
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 arachni/arachni
Web Application Security Scanner Framework
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 d4vinci/scrapling
Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 deepbluedynamics/grubcrawler
The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.
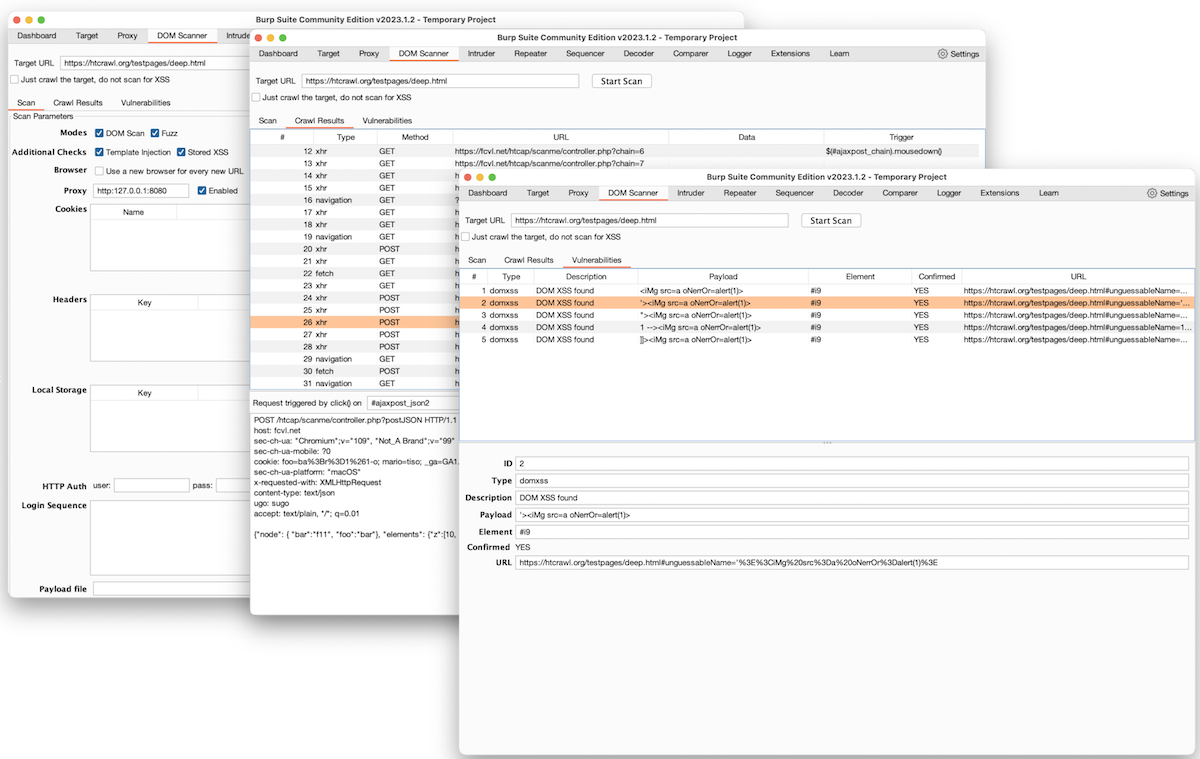 fcavallarin/burp-dom-scanner
Burp Suite's extension to scan and crawl Single Page Applications
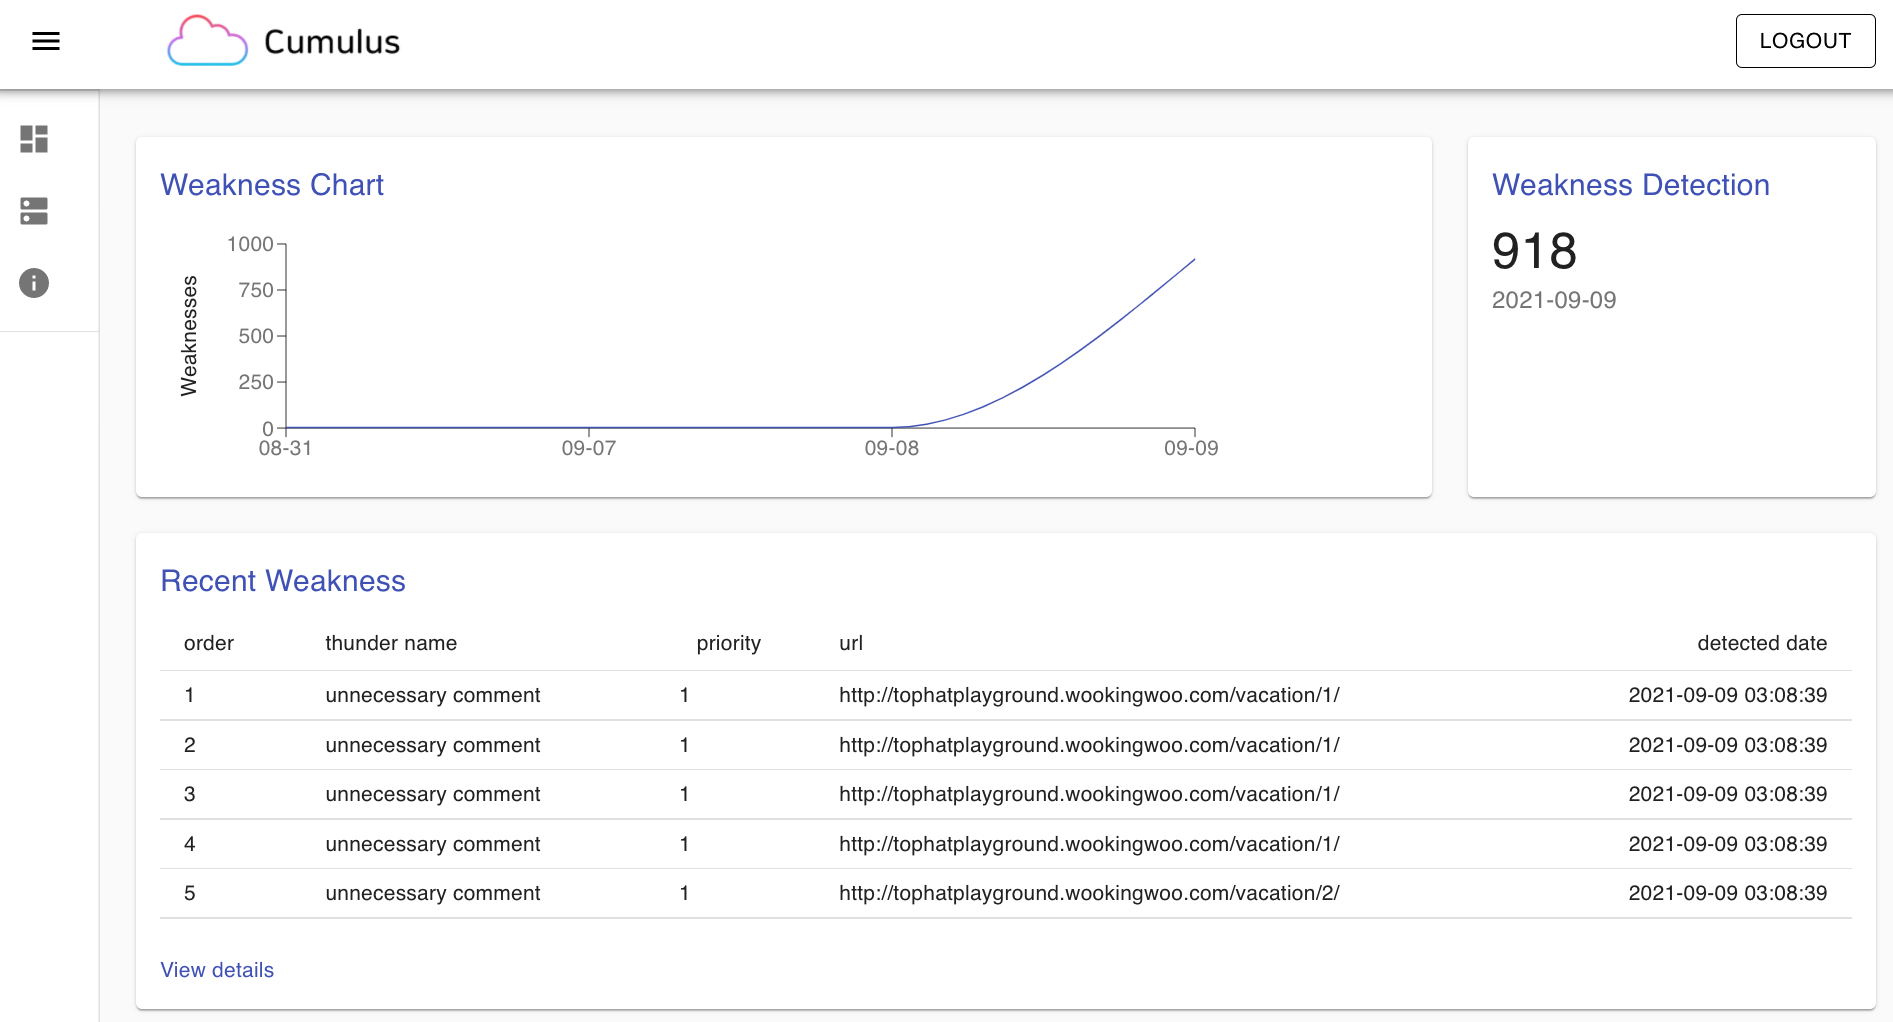 tophat-cloud/cumulus
Real-time web application weakness monitoring SDK and scanner. Detects XSS, SQL injection, sensitive payloads, and code vulnerabilities via dynamic…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 ashishb/android-security-awesome
A collection of android security related resources