

Archived
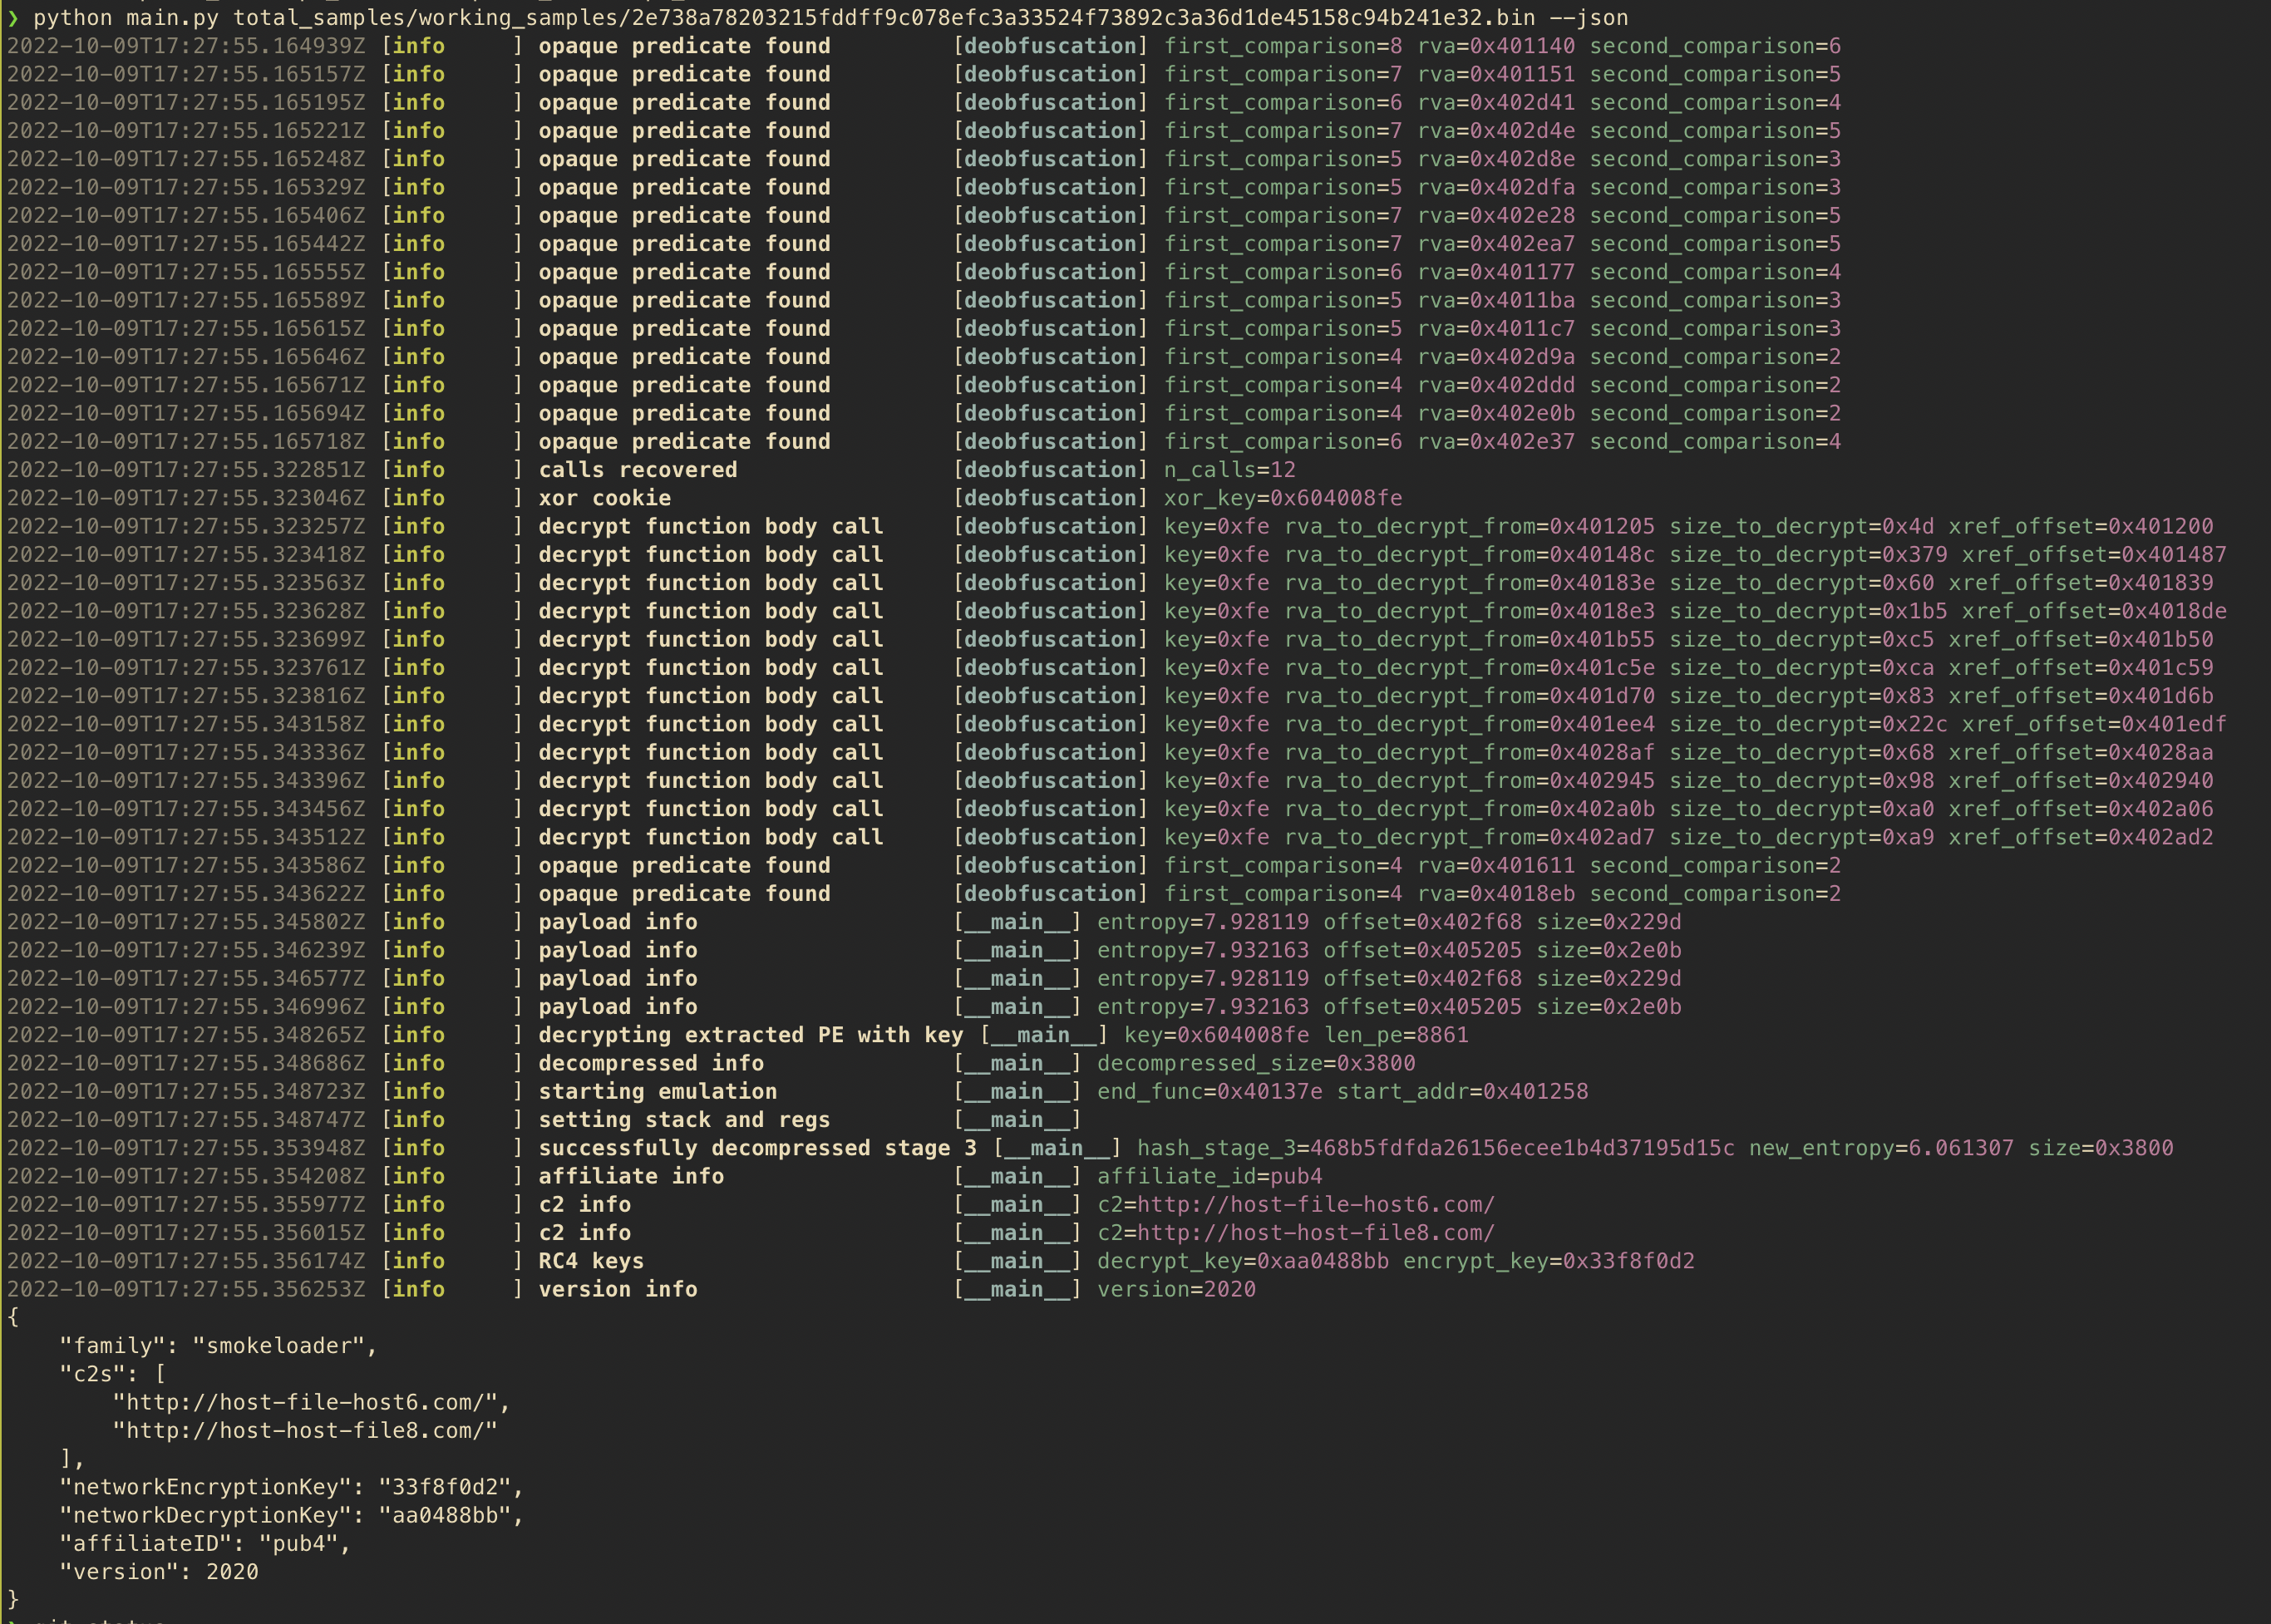
 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ideaslocas/adll
Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
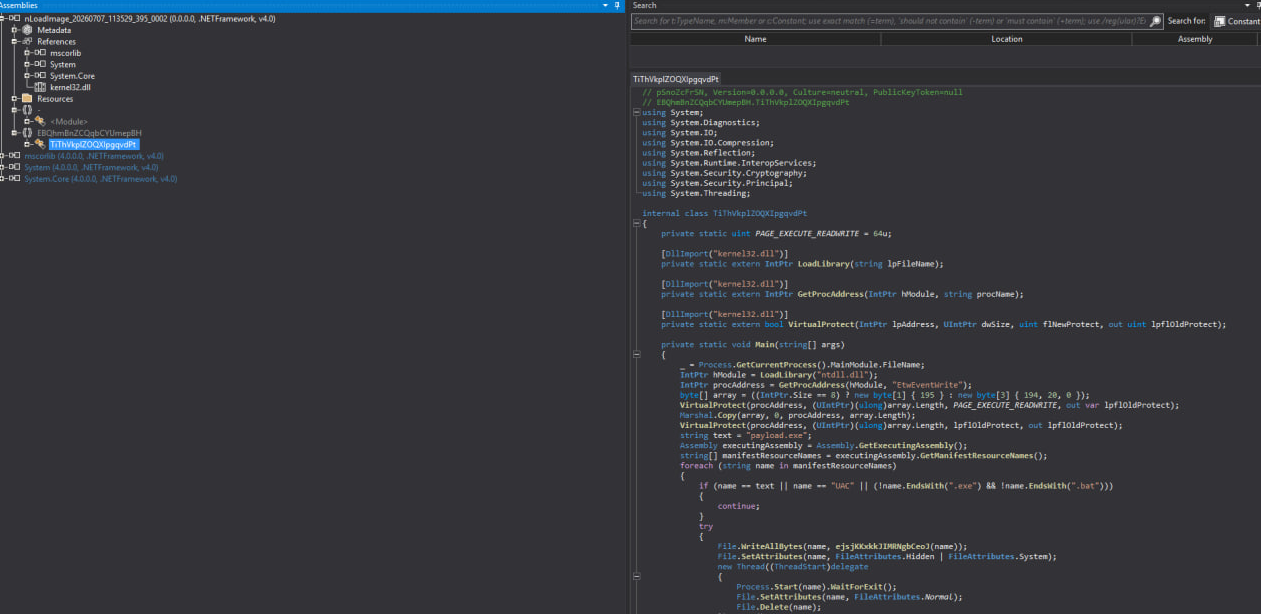 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
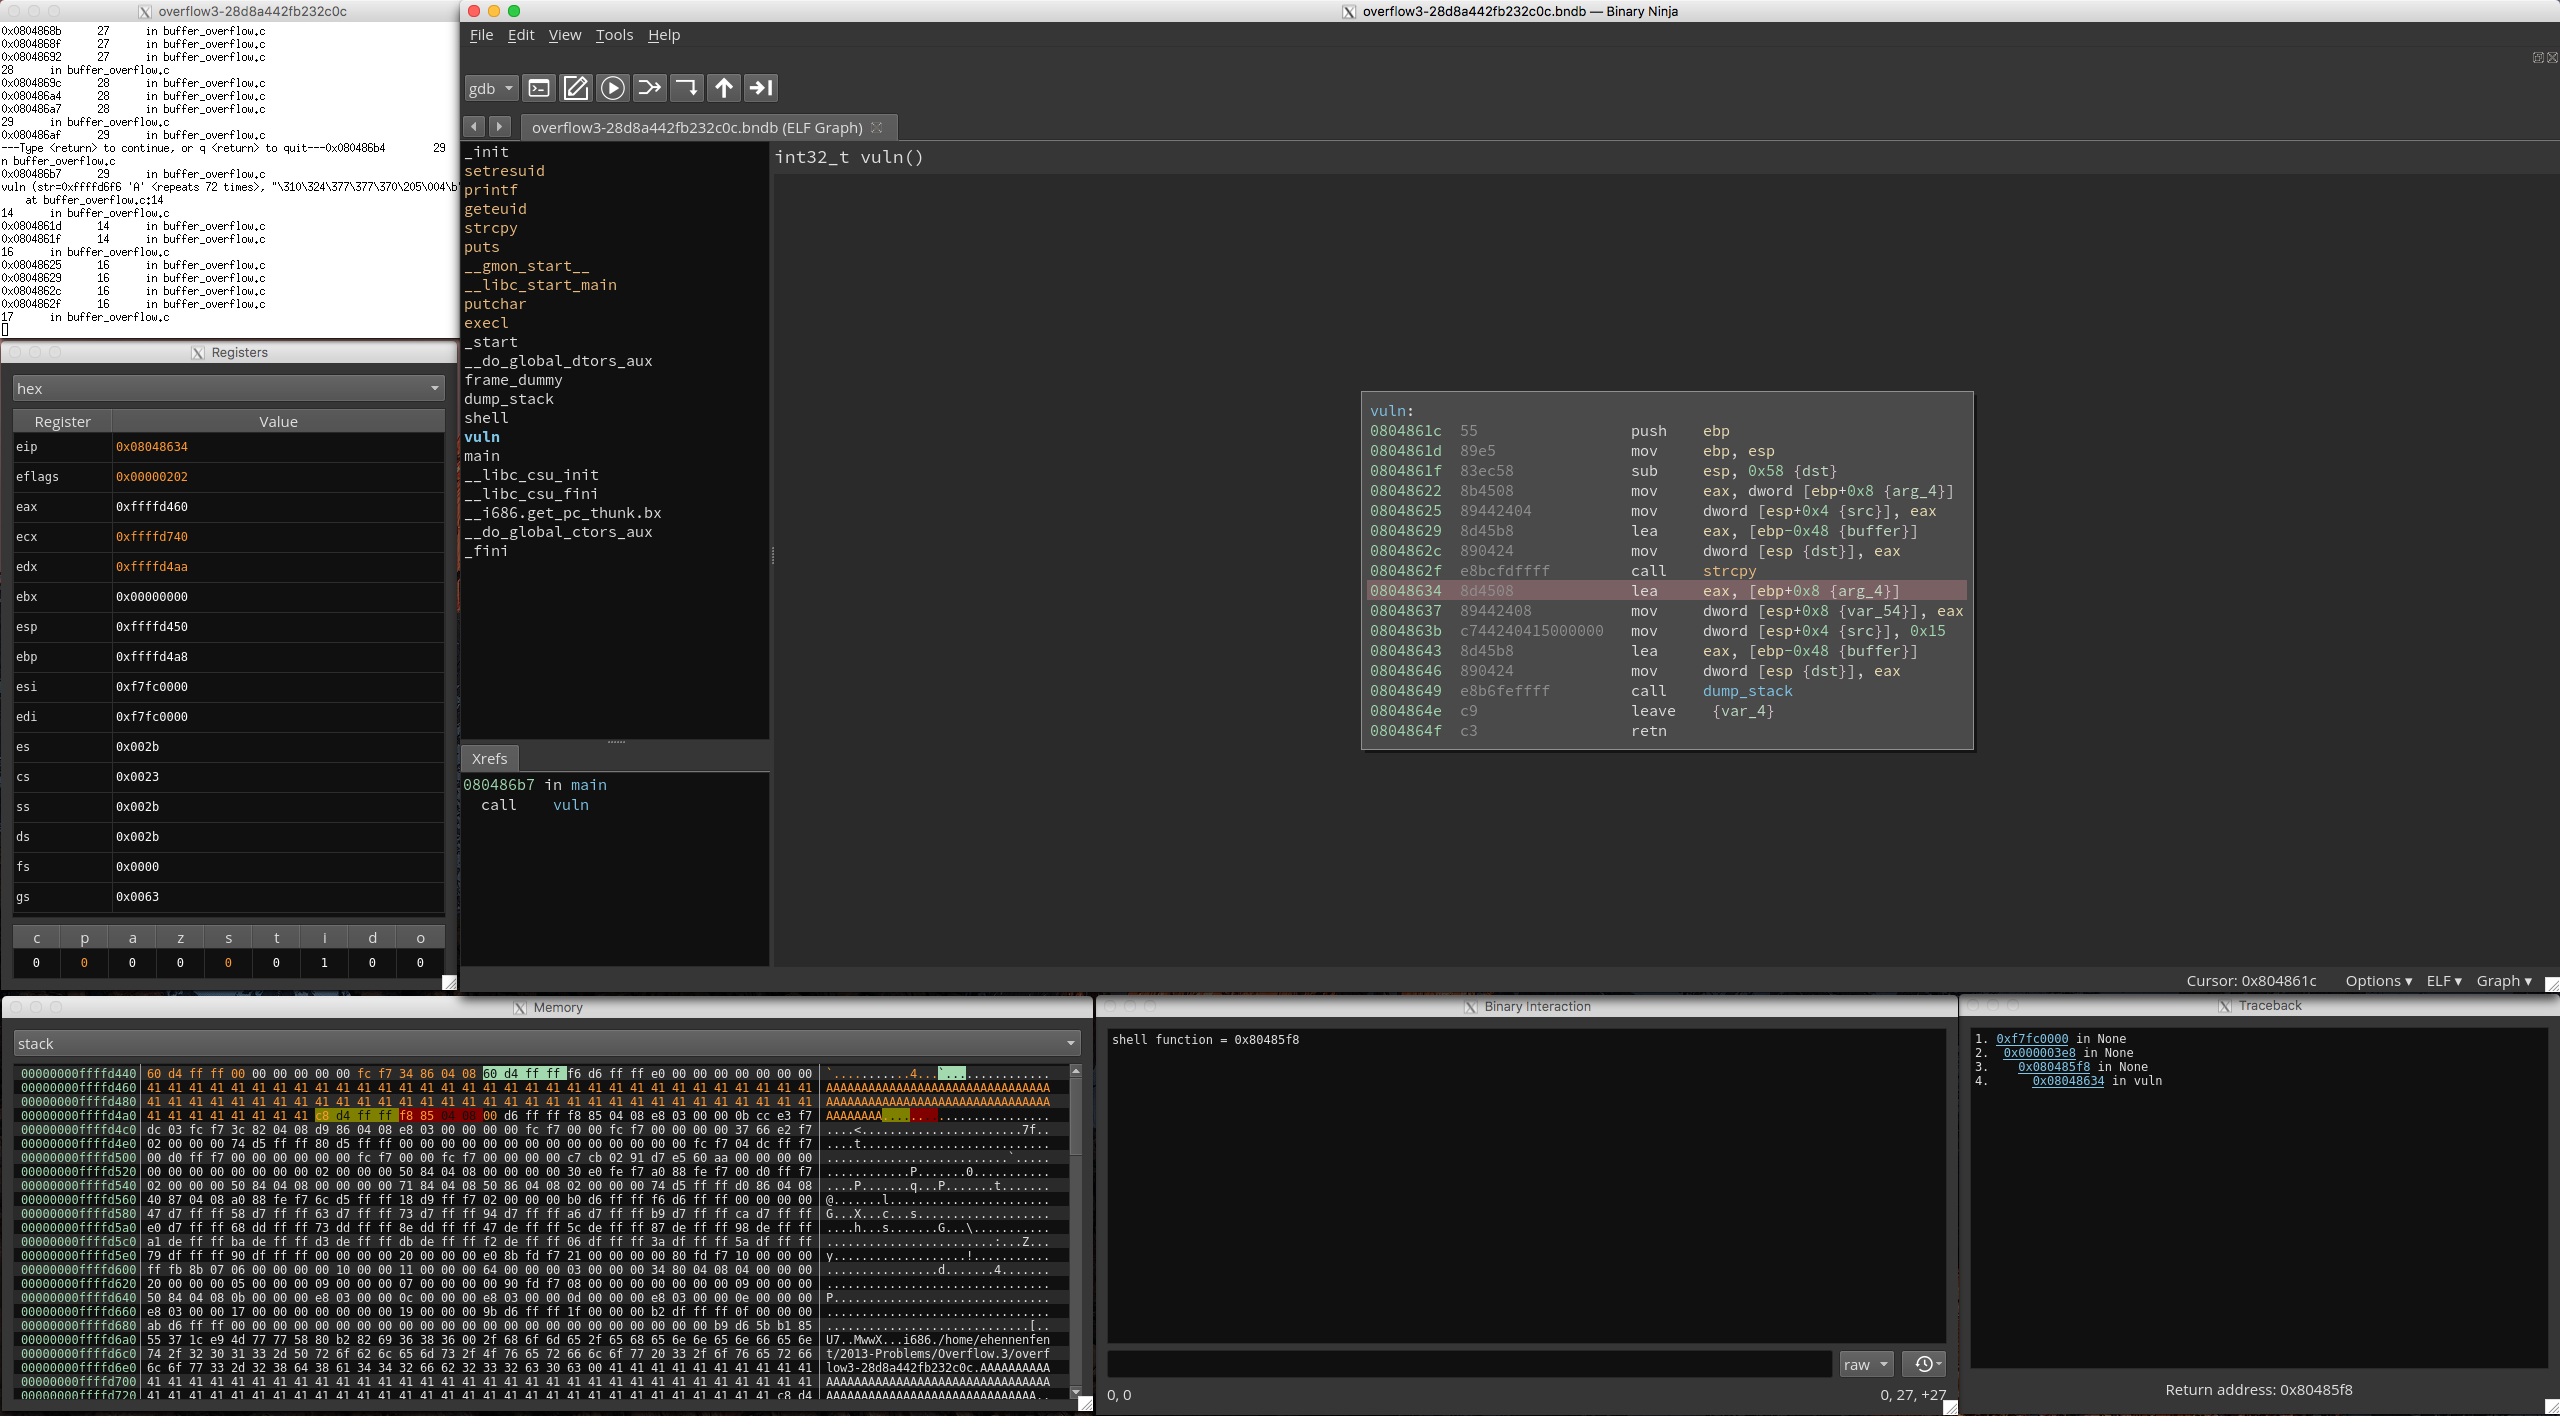 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
 atgreen/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) — blocks authencesn AF_ALG binds at runtime without rebooting
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
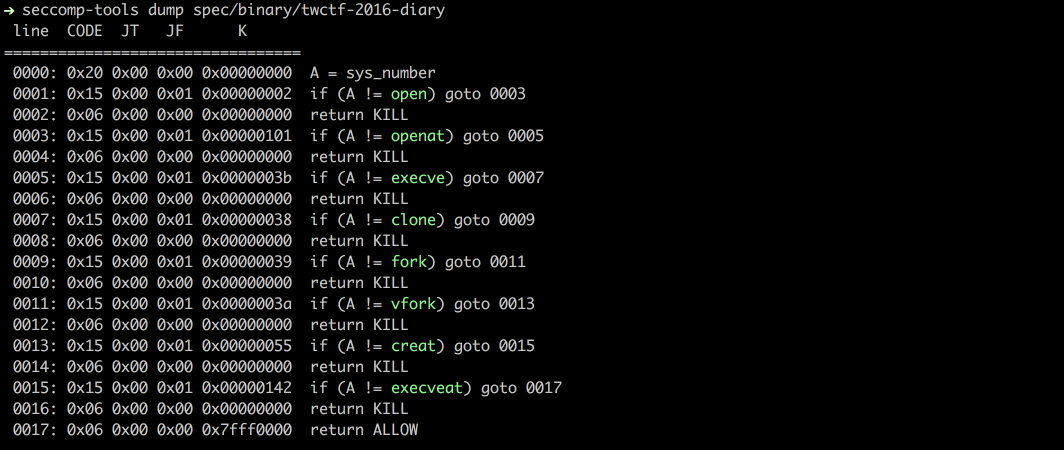 david942j/seccomp-tools
Provide powerful tools for seccomp analysis
 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers