
Archived
Obfuscapk
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
android-securitydynamic-analysis-sandboxingeducation+4
 h1nayoshi/smalien
Information flow analysis tool for Android applications
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
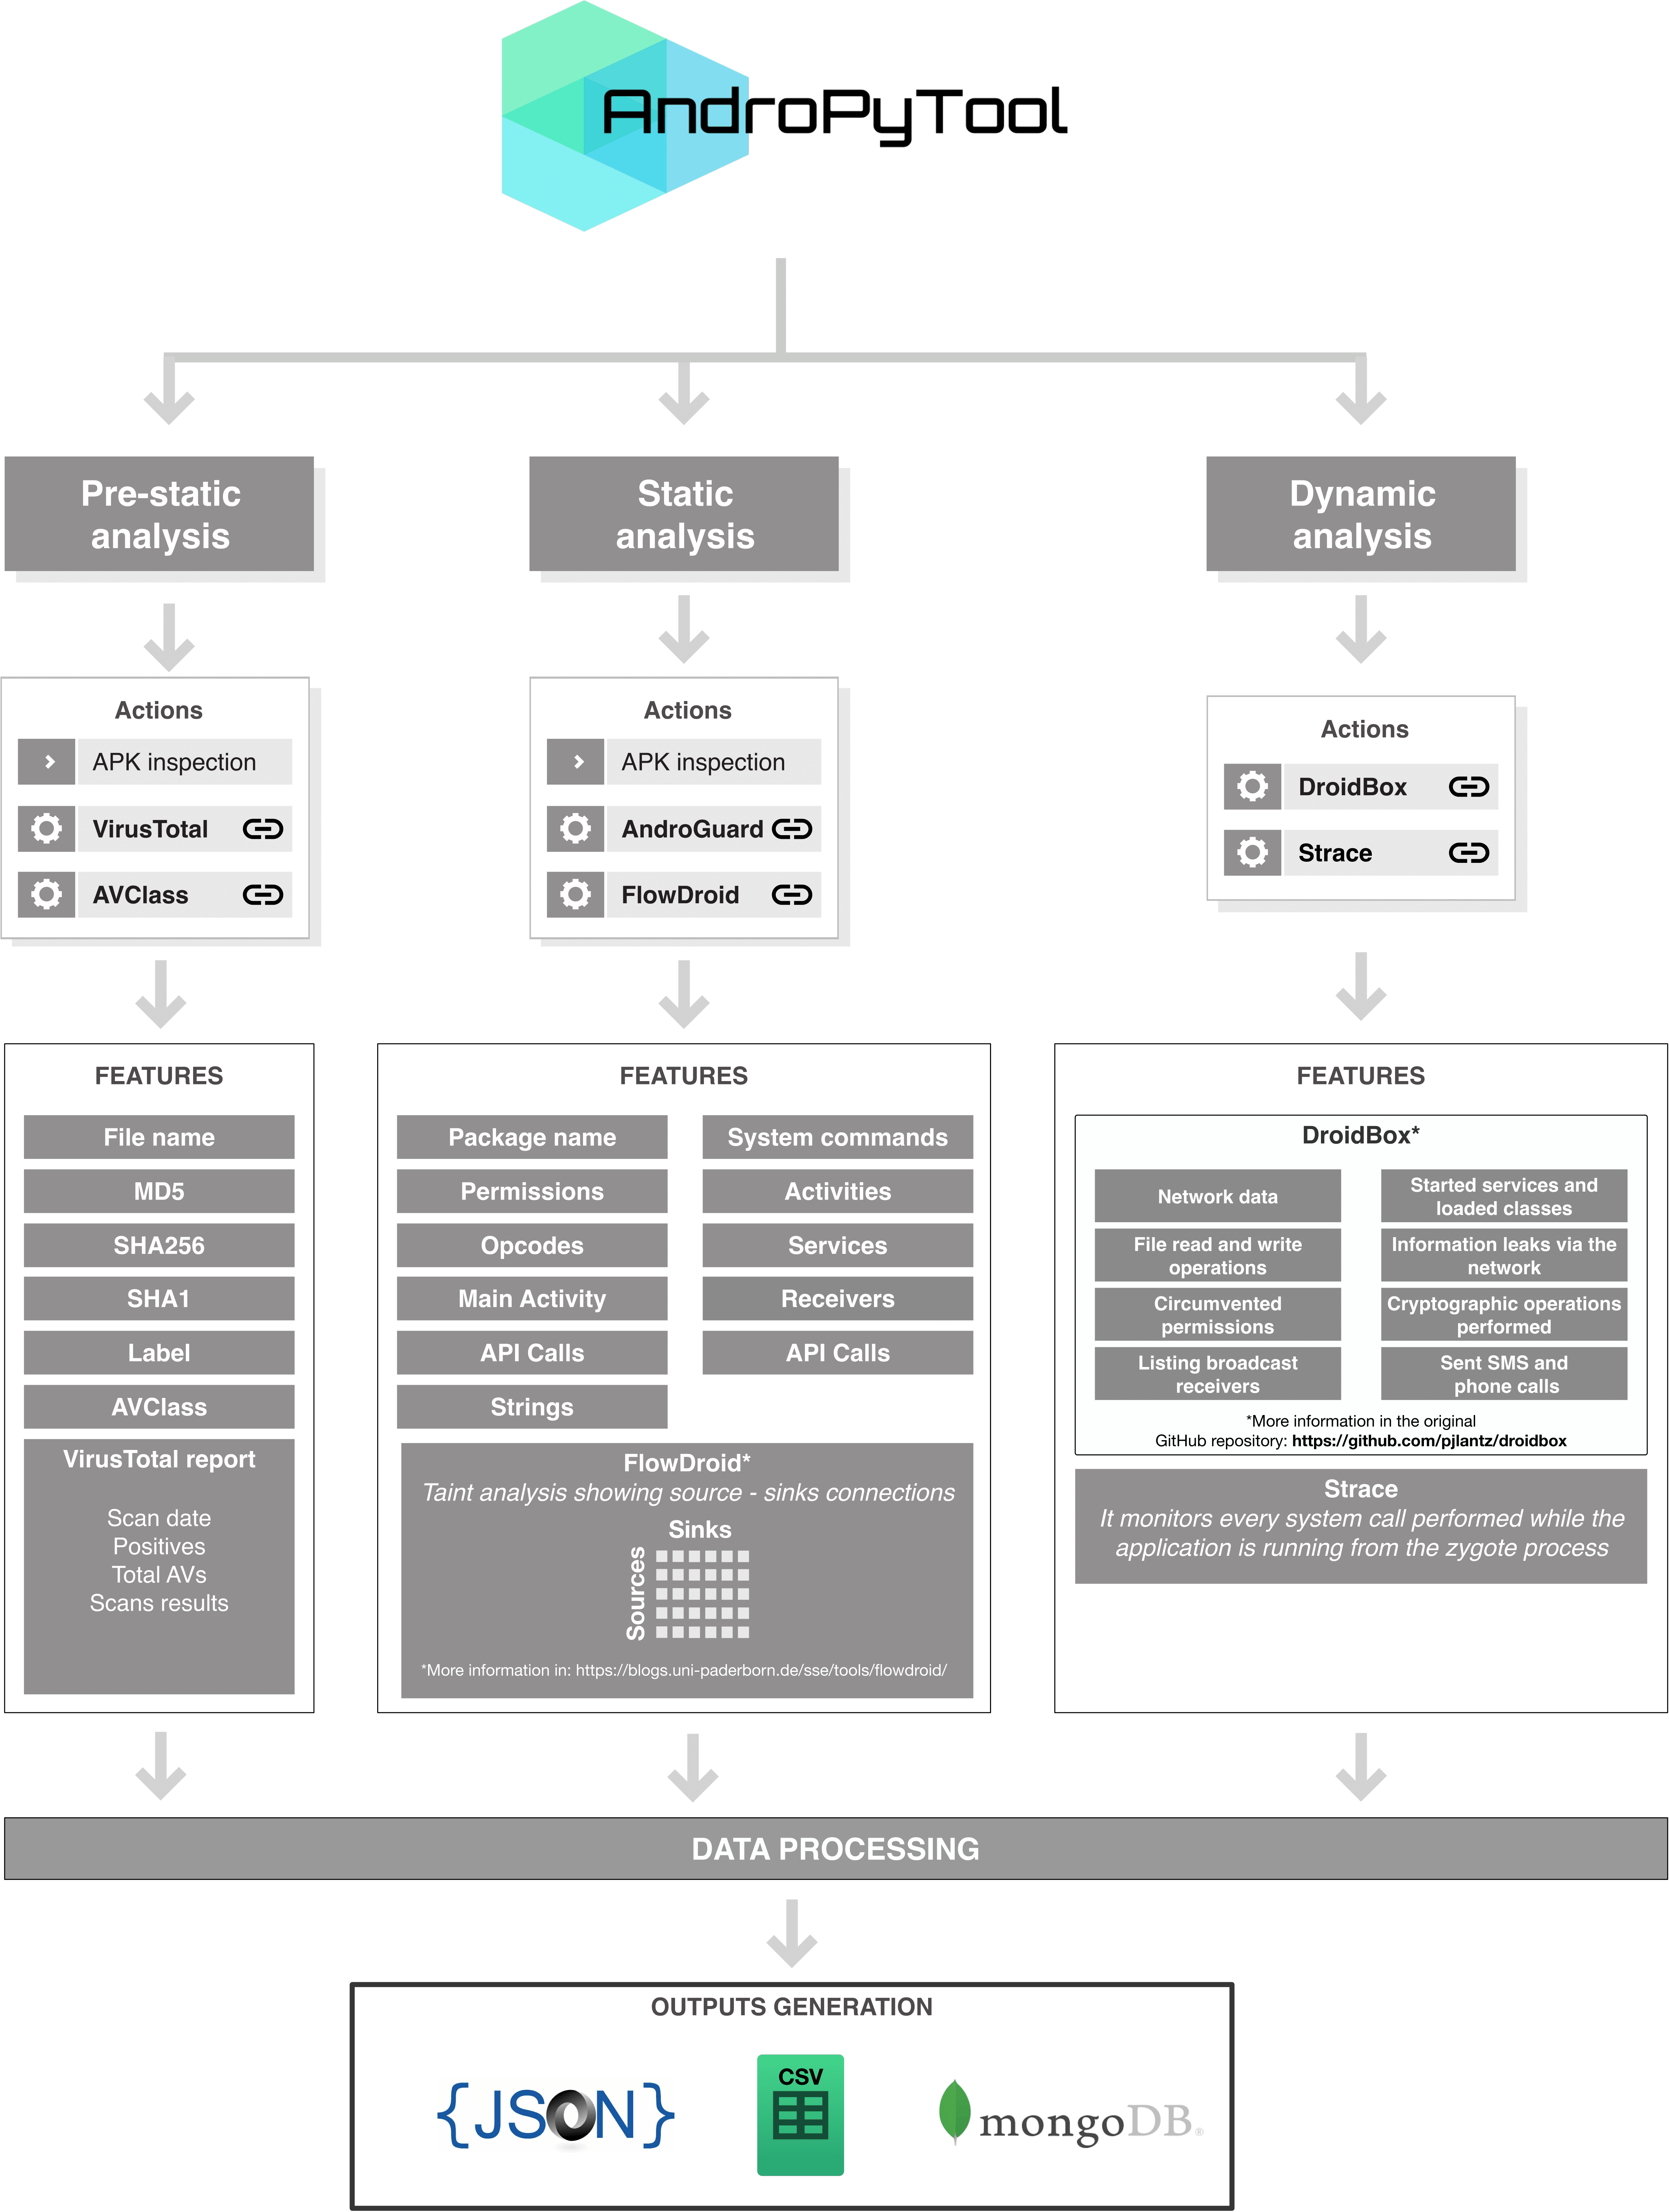 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
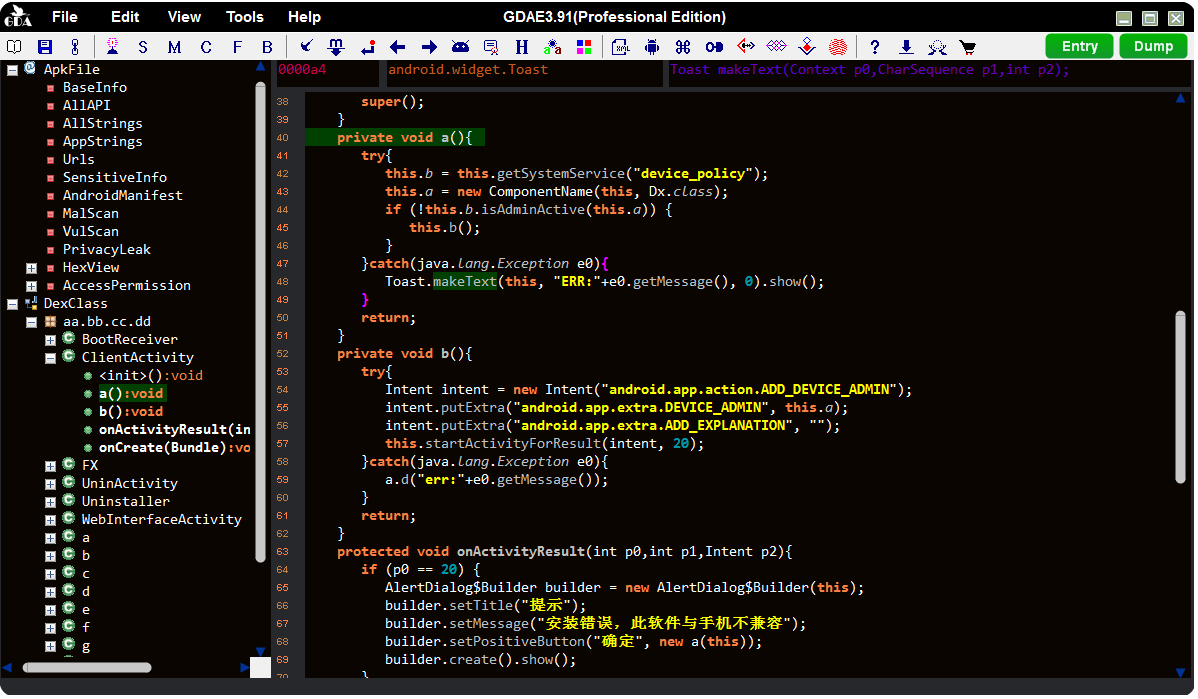 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
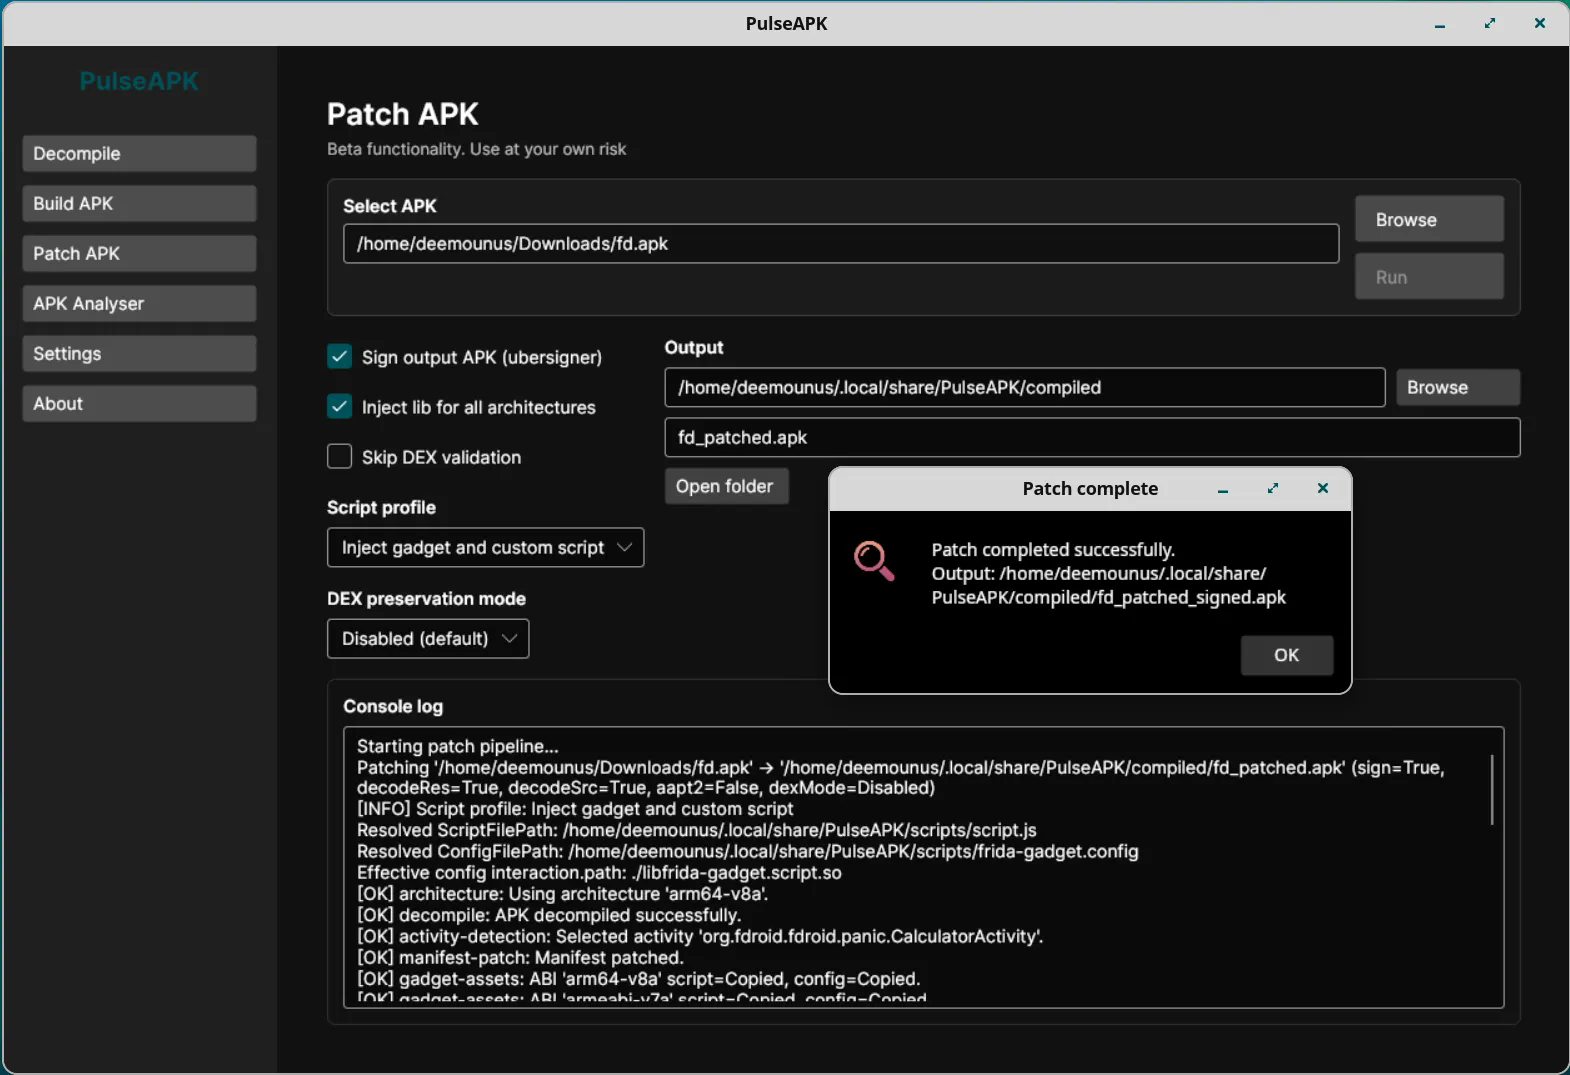 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.