VMProtect-devirtualization

Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.

Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.

Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…

Web application security scanner created by lcamtuf for google - Unofficial Mirror

Secure multithreaded packet sniffer

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis

Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…

A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)

AFL/QEMU fuzzing with full-system emulation.

A reverse engineering framework written in Python.

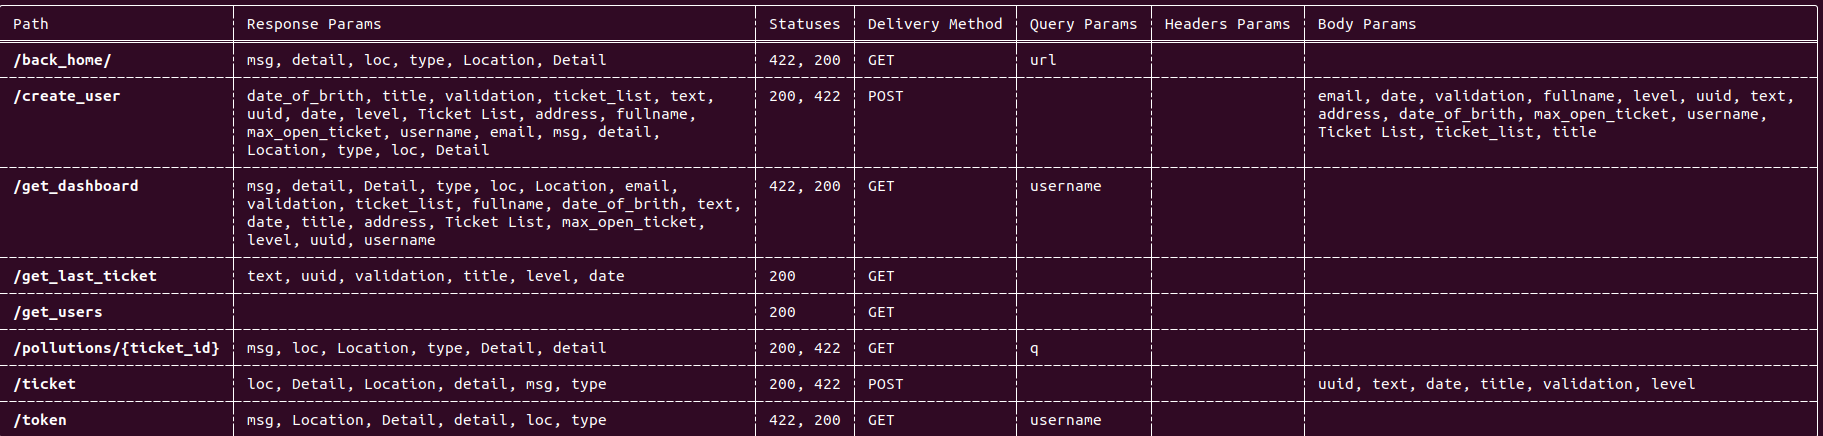
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

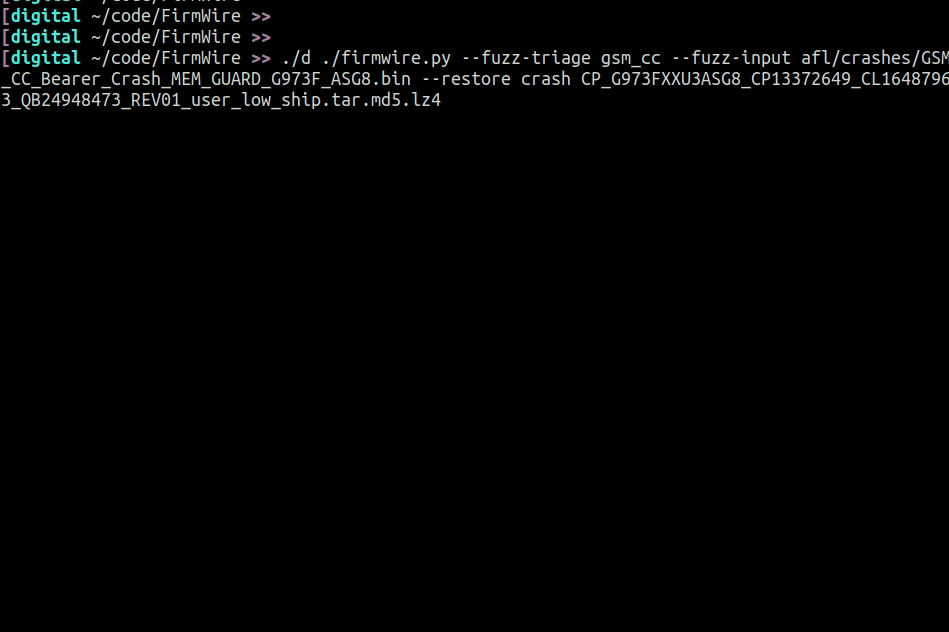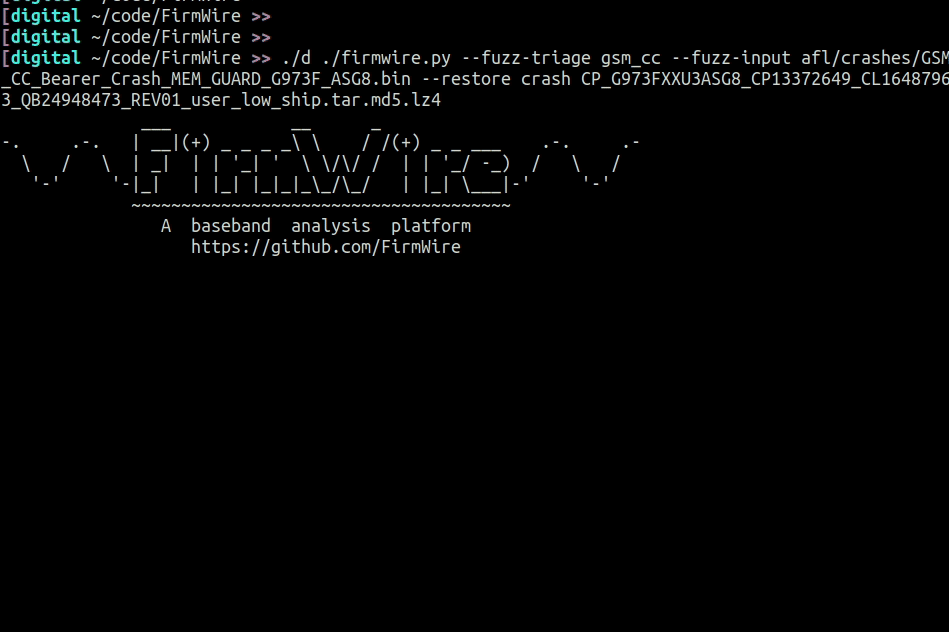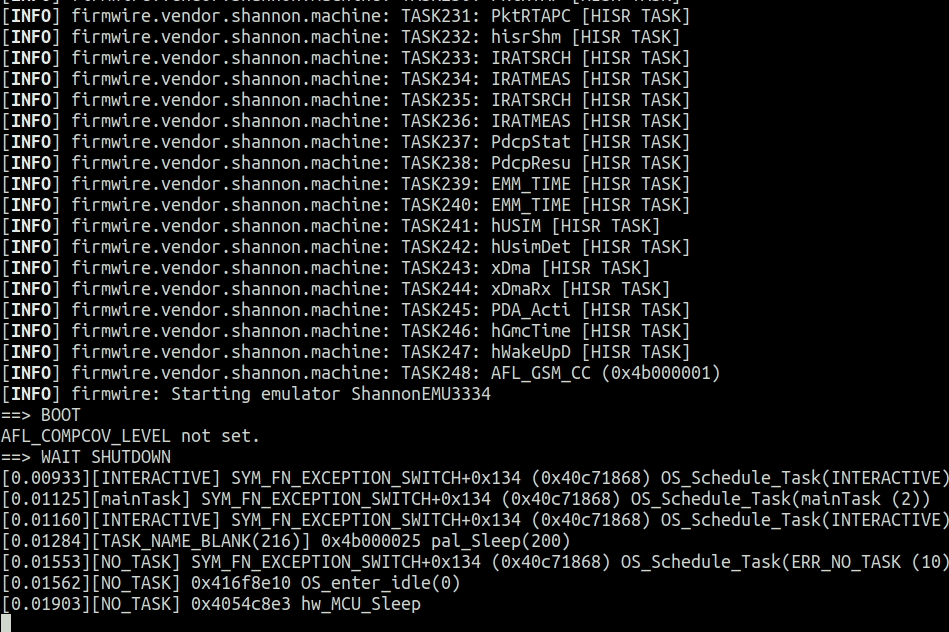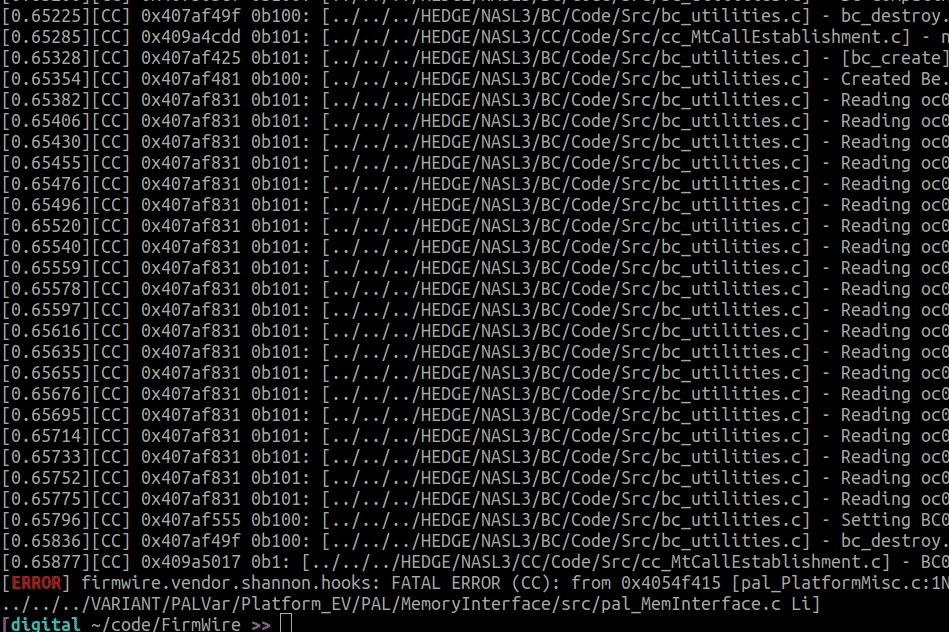
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares

A tool that is used to hunt vulnerabilities in x64 WDM drivers

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

Reverse engineering software using a full system simulator

A hypervisor for fuzzing built with WHVP and Bochs

Fermion, an electron wrapper for Frida & Monaco.