
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
54 results
vmsan preview

vmsan

GitHubangelorc/vmsan

Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.

cloud-infrastructure-securitycontainer-securitydevsecops+3
84
6 months ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

binary-analysisdynamic-analysis-sandboxingeducation+8
2415 days ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
digital-forensicsdynamic-analysis-sandboxingforensics+5
1171 month ago
multiscanner preview

multiscanner

GitHubmitre/multiscanner

Modular file scanning/analysis framework

dynamic-analysis-sandboxingmalware-analysisstatic-analysis+1
6207 years ago
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
79.9k0 days ago
Text4shell--Automated-exploit---CVE-2022-42889 preview

Text4shell--Automated-exploit---CVE-2022-42889

GitHubadarshpv9746/text4shell--automated-exploit---cve-2022-42889

Automated exploit for CVE-2022-42889 (Text4Shell) with a vulnerable Dockerized app for testing and manual exploitation guidance.
dynamic-analysis-sandboxingexploitationpayload-development+3
3 years ago
cve-2026-59827-metabase-cyber-range preview

cve-2026-59827-metabase-cyber-range

GitHubshivammittal2403/cve-2026-59827-metabase-cyber-range

Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…

ctfdynamic-analysis-sandboxingeducation+6
12 days ago
Hypervisor-From-Scratch preview

Hypervisor-From-Scratch

GitHubsinakarvandi/hypervisor-from-scratch

Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
dynamic-analysis-sandboxingeducationlearning-paths-courses+2
2.7k4 months ago
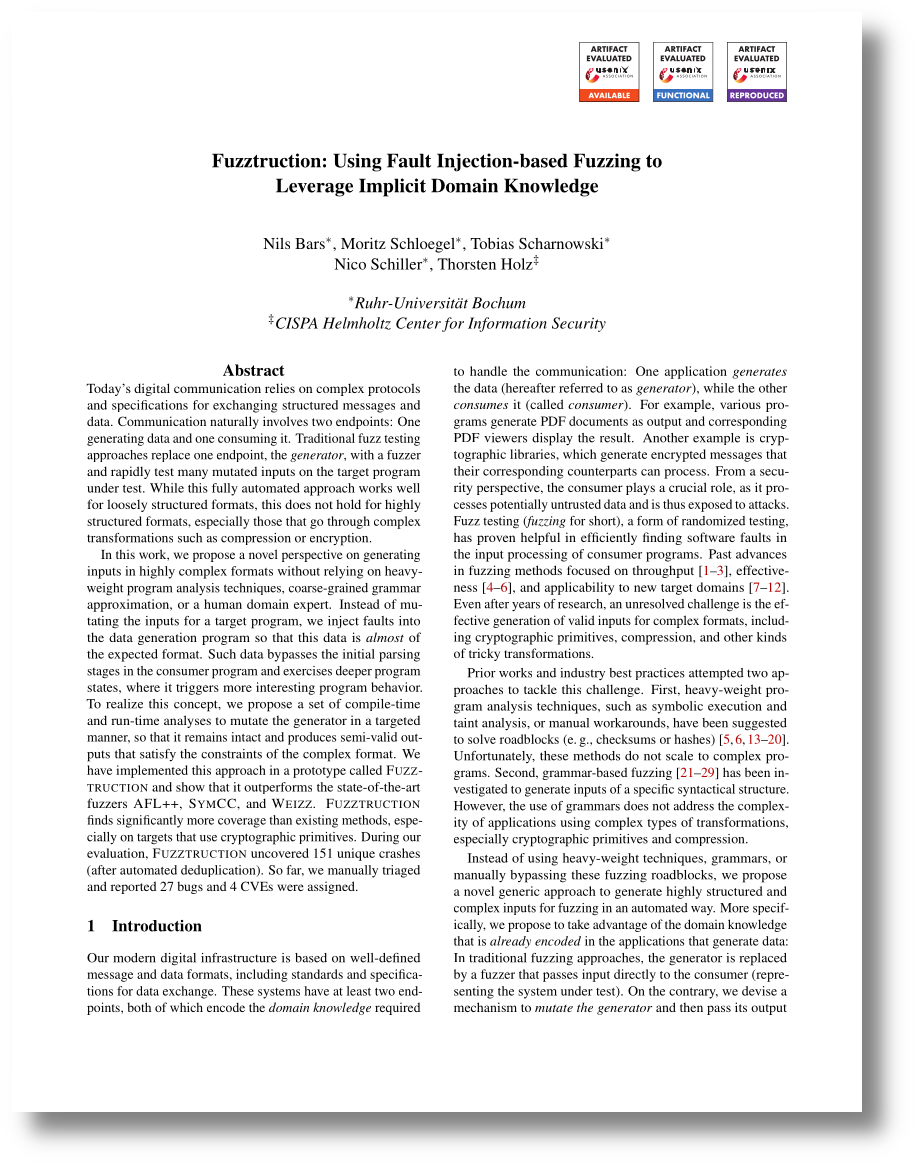
fuzztruction preview

fuzztruction

GitHubfuzztruction/fuzztruction

Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…
binary-analysisdynamic-analysis-sandboxingfuzzing+1
1362 years ago
CVE-2026-34197 preview

CVE-2026-34197

GitHublat-06/cve-2026-34197

Proof-of-concept exploit for CVE-2026-34197, demonstrating authenticated remote code execution in Apache ActiveMQ via Jolokia JMX-HTTP bridge and…

code-analysisdynamic-analysis-sandboxingeducation+5
4 months ago
snapchange preview

snapchange

GitHubawslabs/snapchange

Lightweight fuzzing of a memory snapshot using KVM
debuggersdynamic-analysis-sandboxingdynamic-code-analysis+3
4712 years ago
ReClass.NET preview

ReClass.NET

GitHubreclassnet/reclass.net

More than a ReClass port to the .NET platform.
binary-analysiscode-analysisdebuggers+4
2.2k3 years ago
rex preview

rex

GitHubrex-rs/rex

Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
dynamic-analysis-sandboxingembedded-systems-securitysecurity-virtualization
5582 months ago
chimera preview

chimera

GitHubpenberg/chimera

Sandbox untrusted code with safe access to the host.
binary-analysiscode-analysisdynamic-analysis-sandboxing+3
1358 days ago
hyperpom preview

hyperpom

GitHubimpalabs/hyperpom

AArch64 fuzzer based on the Apple Silicon hypervisor

binary-analysisdynamic-analysis-sandboxingfuzzing+2
2042 years ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

ai-assisted-reversingandroid-securitybinary-analysis+8
372 days ago
Insular preview

Insular

GitLabsecure-system/insular

Isolate your big brother apps https://secure-system.gitlab.io/Insular/
android-securitycontainer-escapedynamic-analysis-sandboxing+3
22117 days ago
CaptainHook preview

CaptainHook

GitHubsynacktiv/captainhook

Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.

binary-analysiscode-analysisdebuggers+2
94 years ago
Previous123Next