
ravage
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
ai-securityctfdynamic-analysis-sandboxing+7
55
duriantaco/ravageEvidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
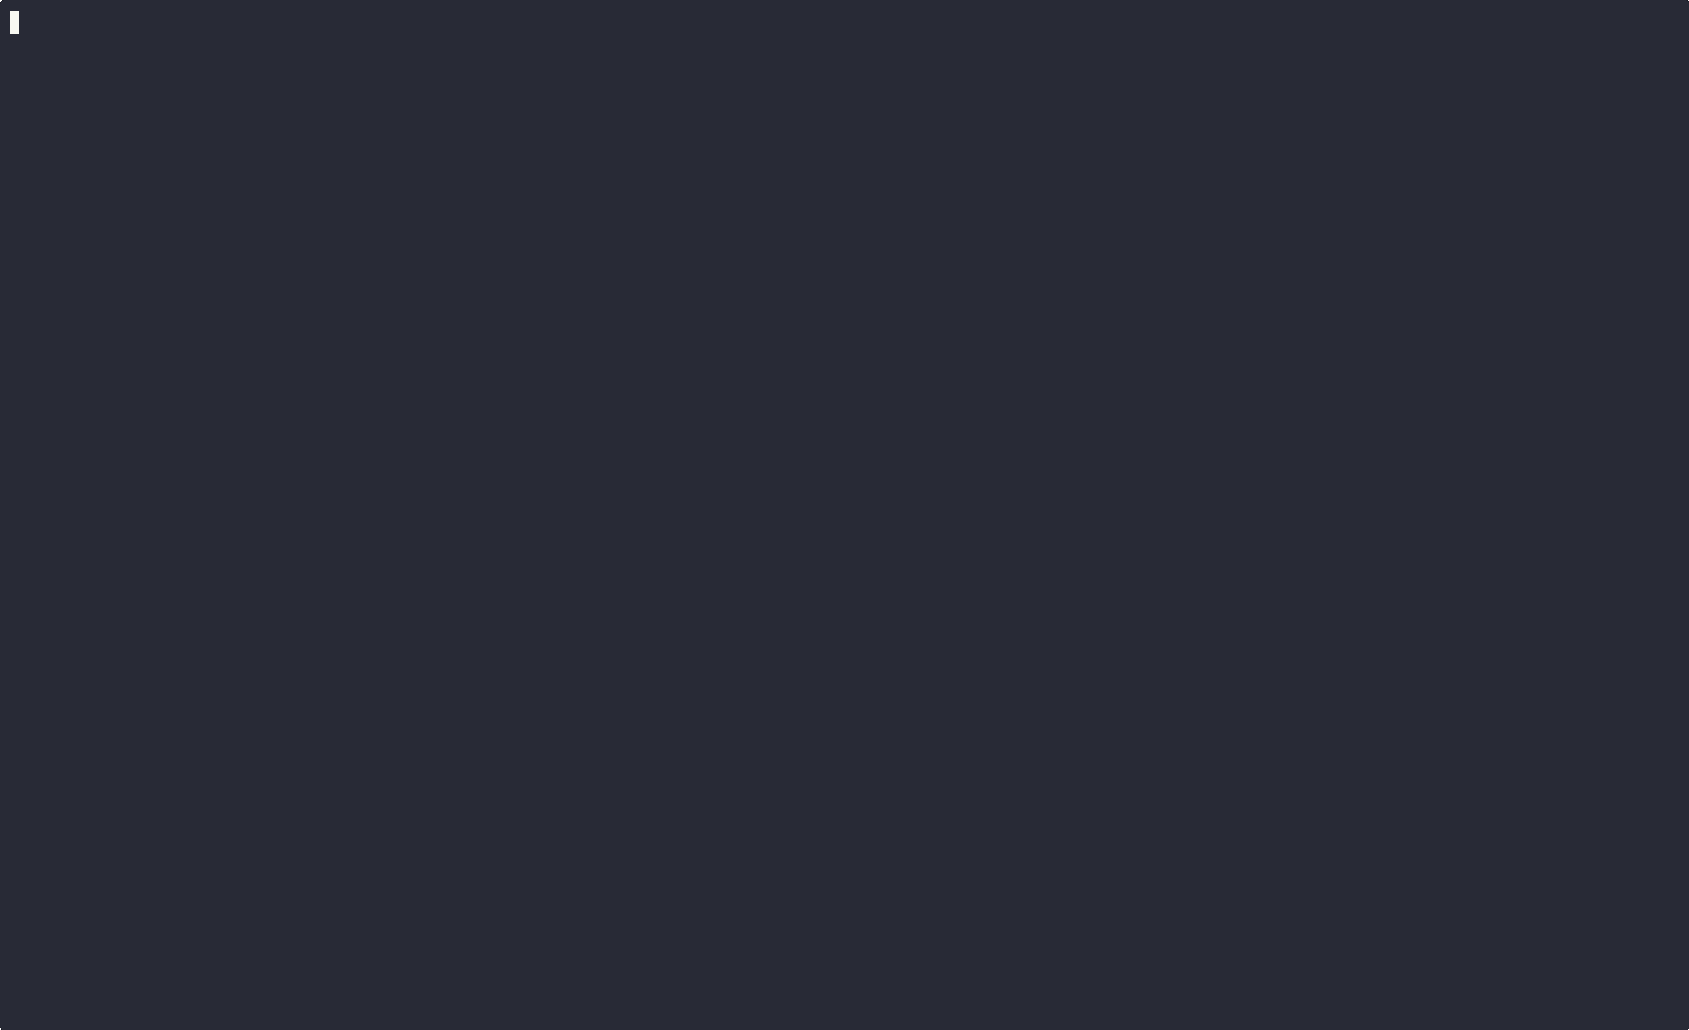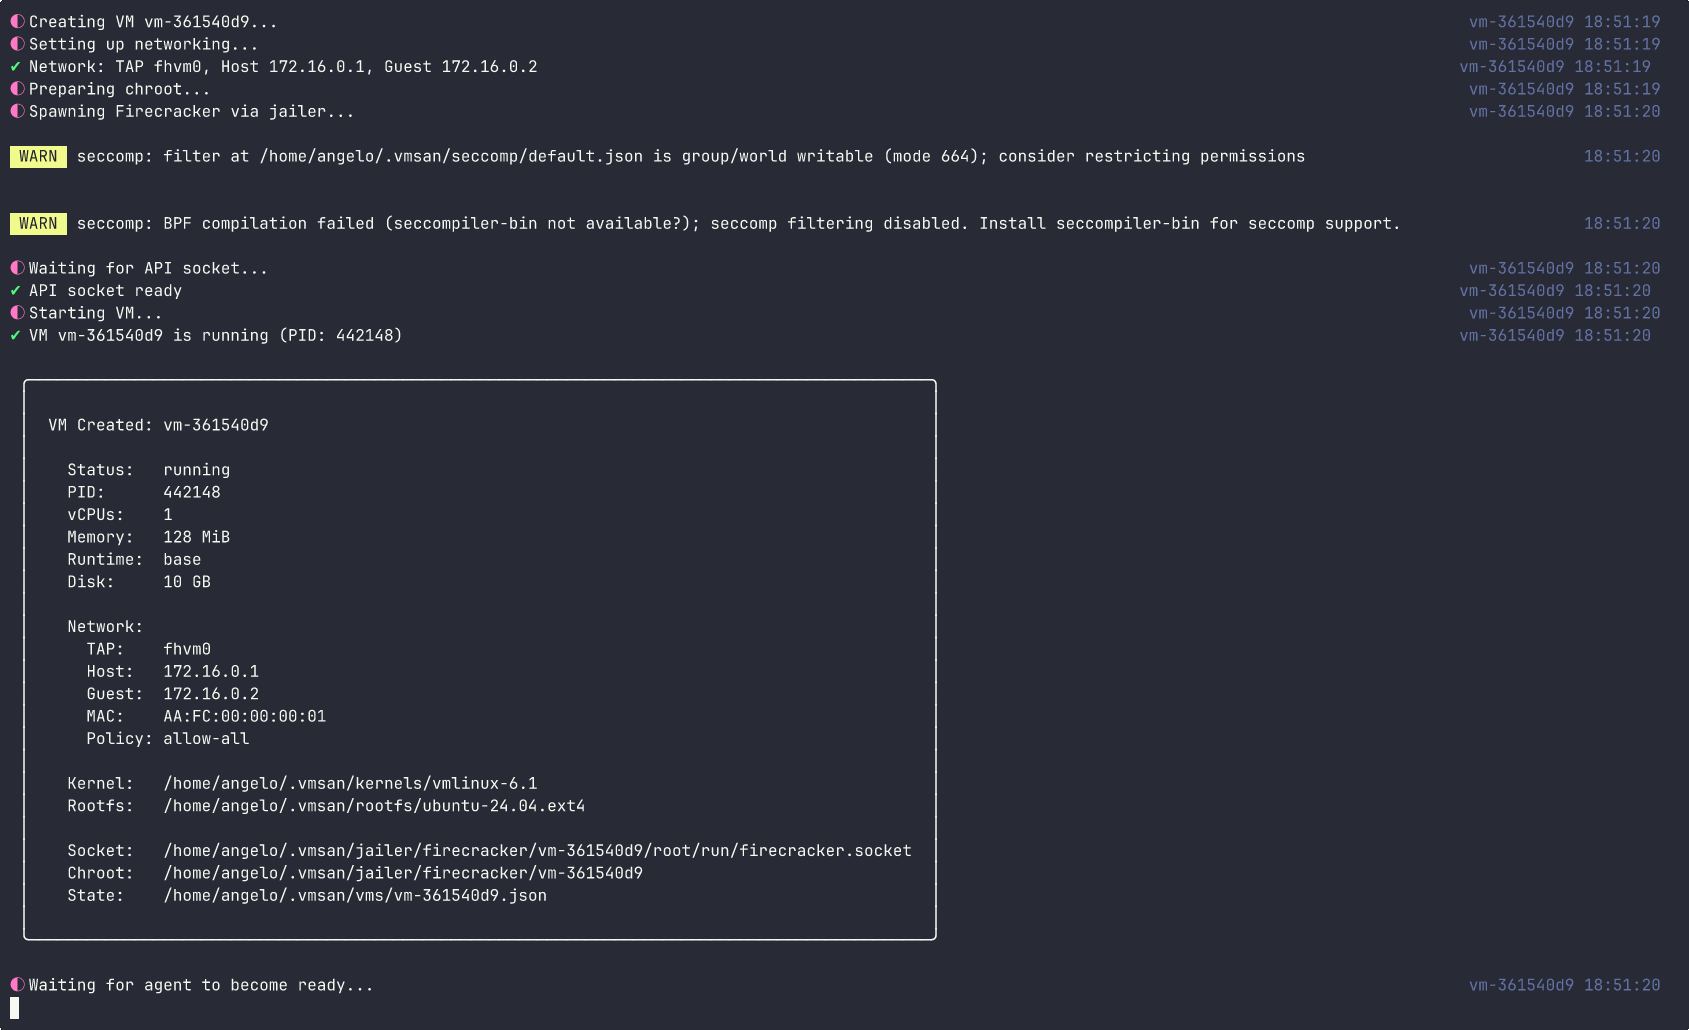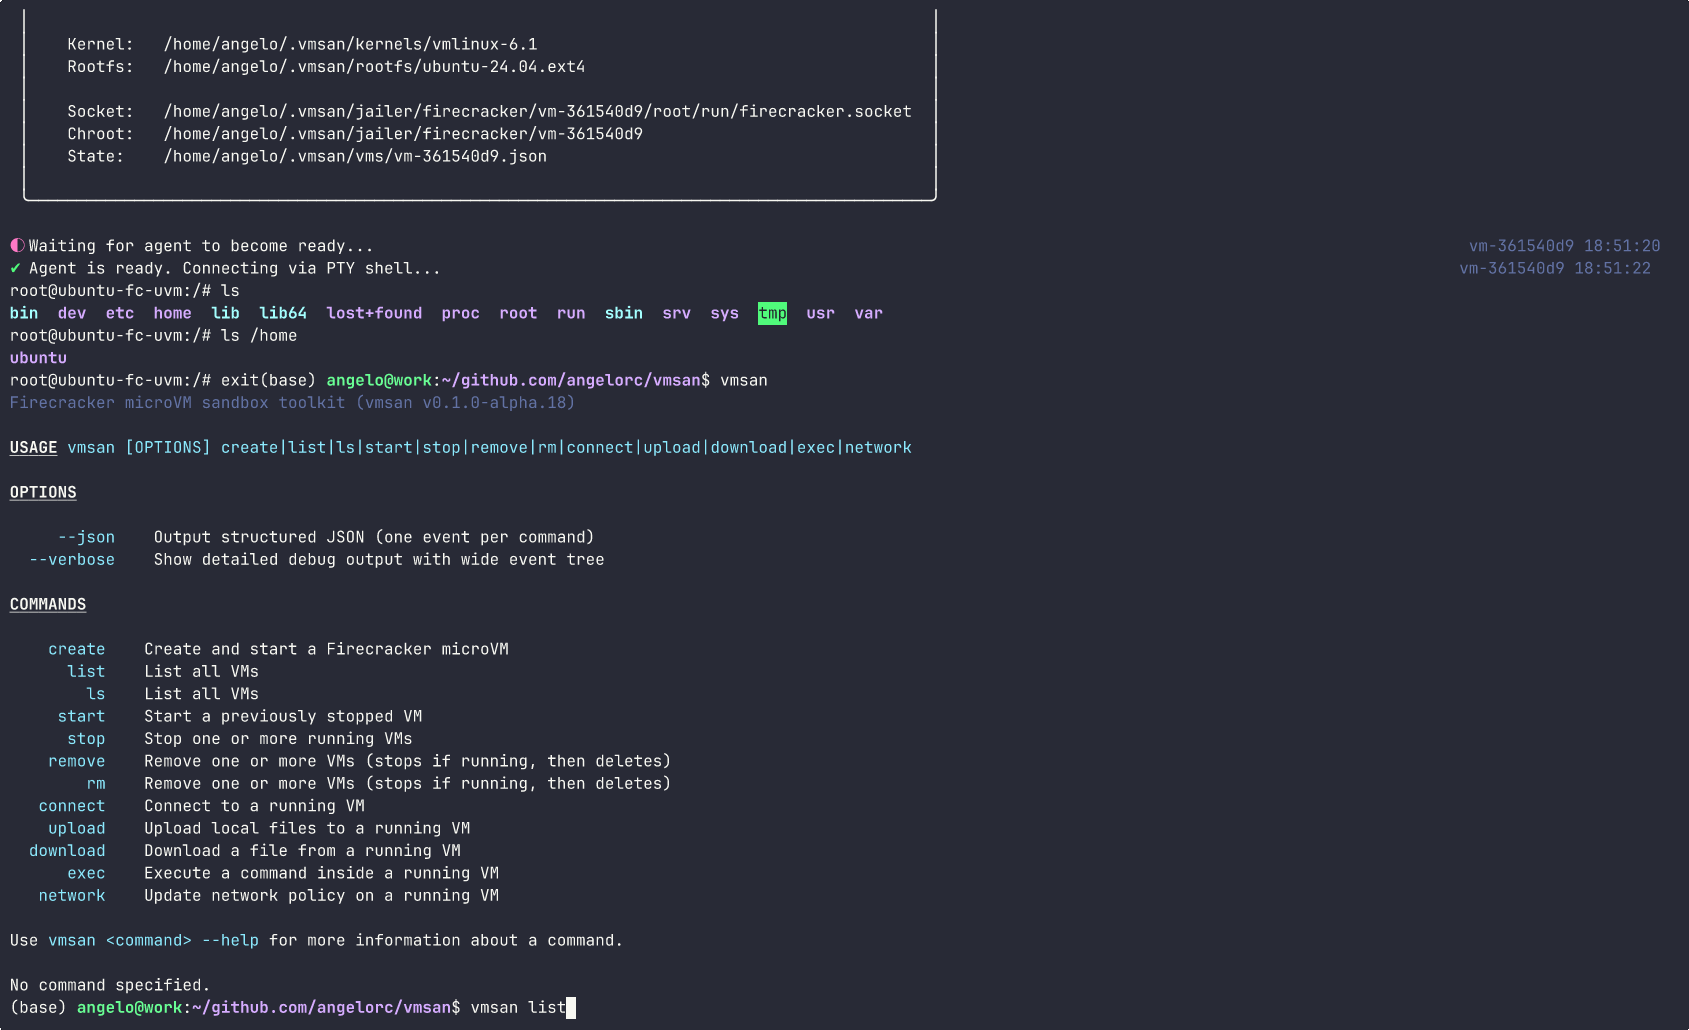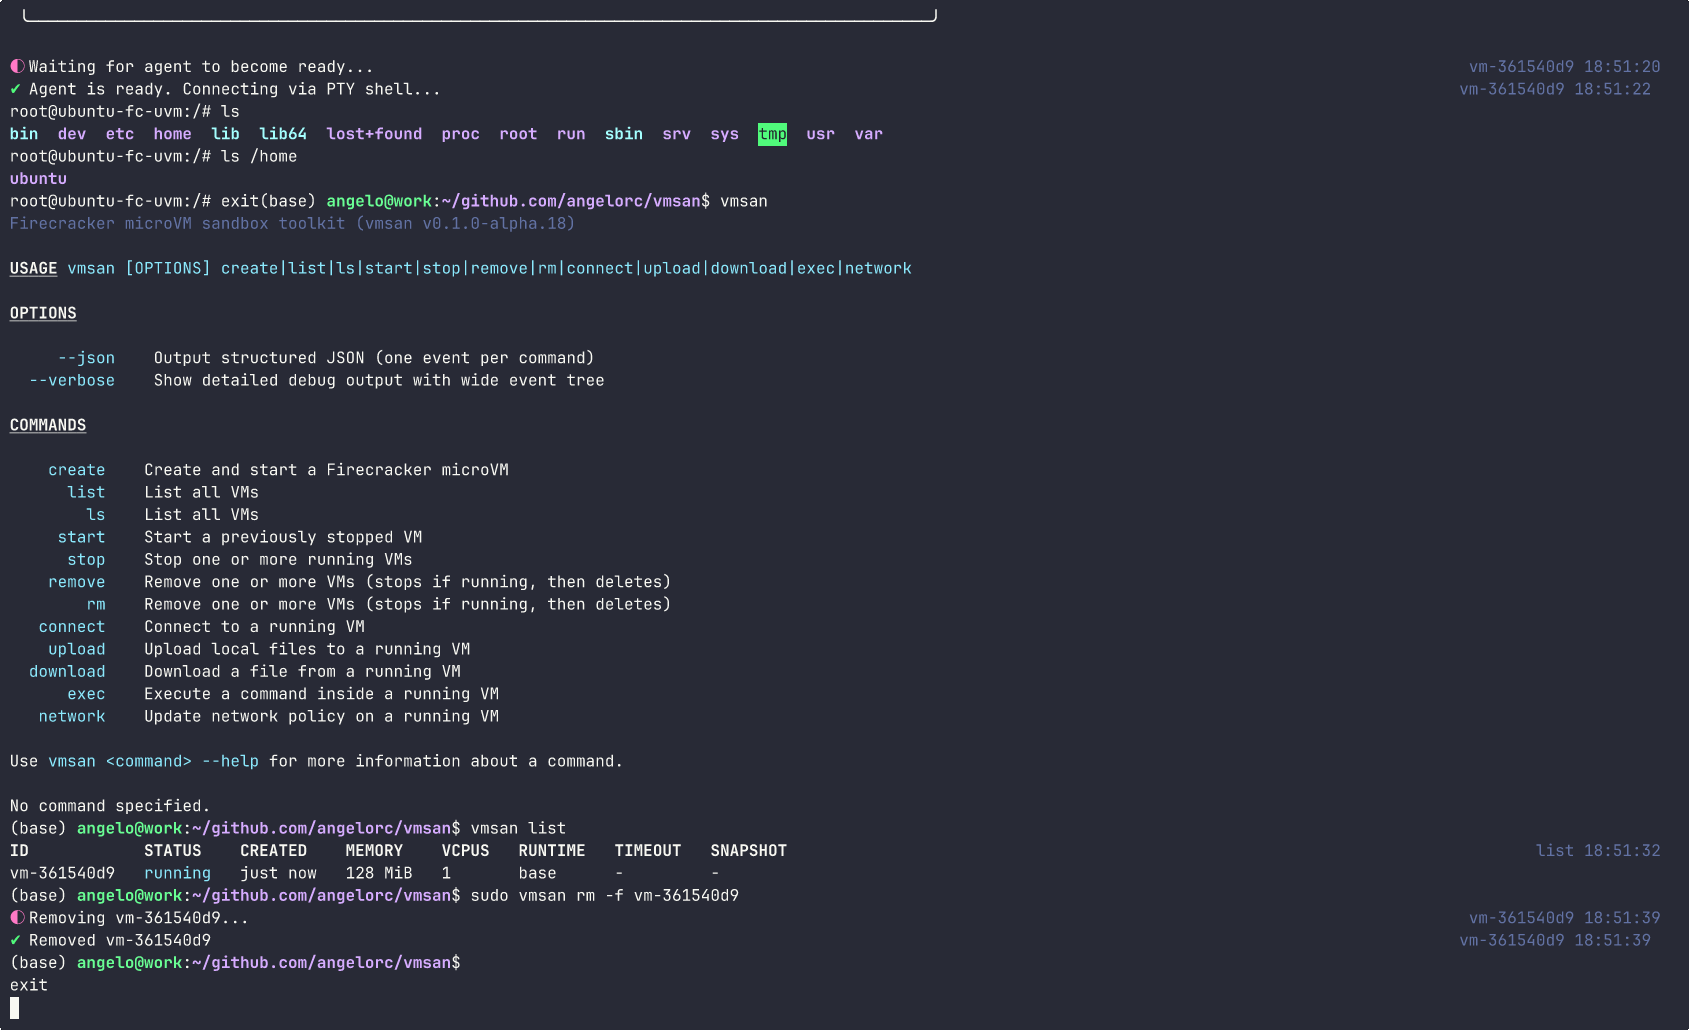 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
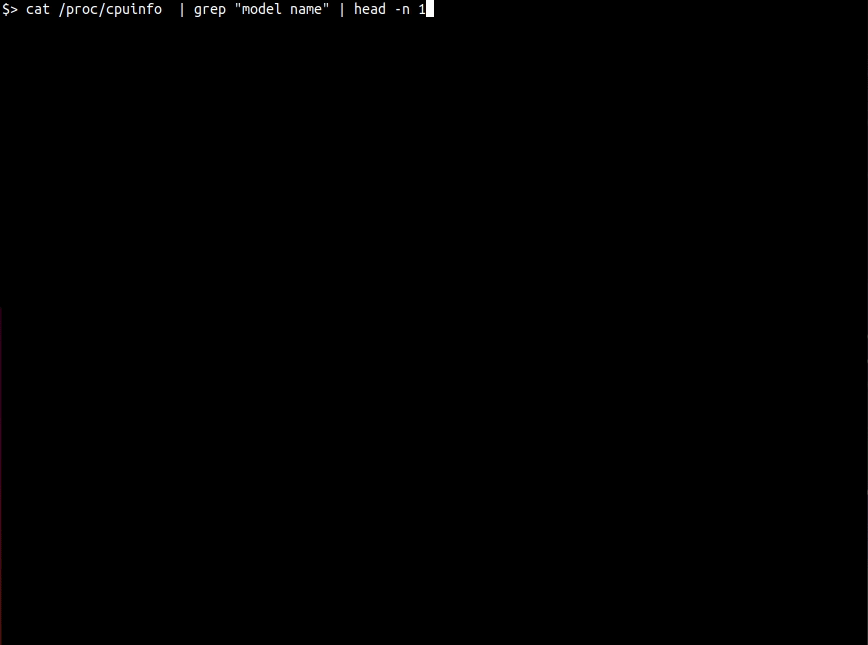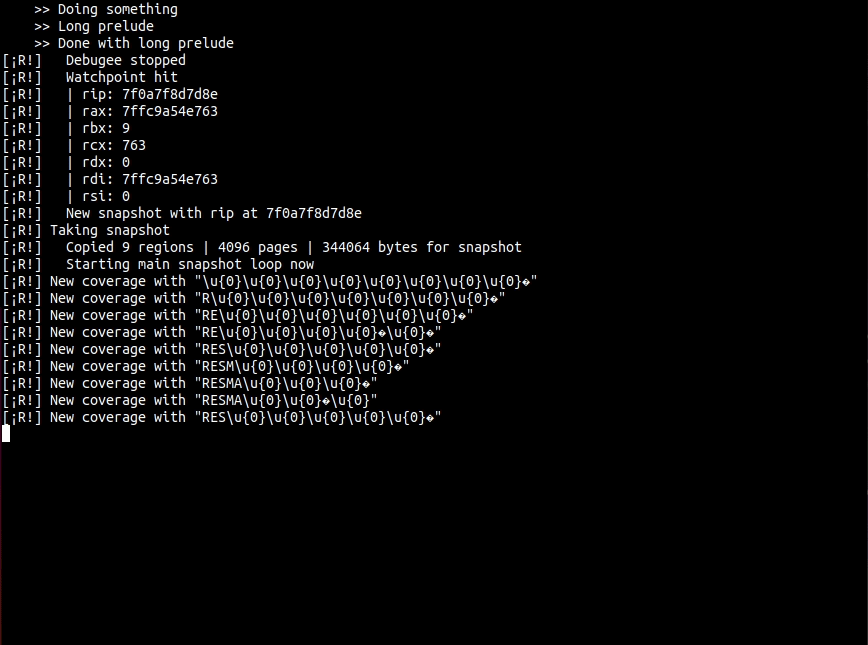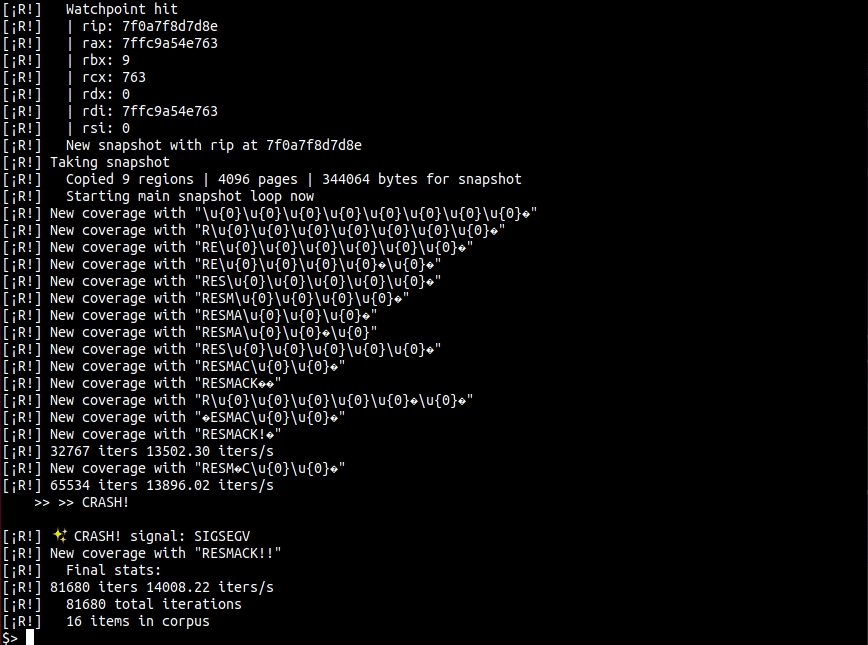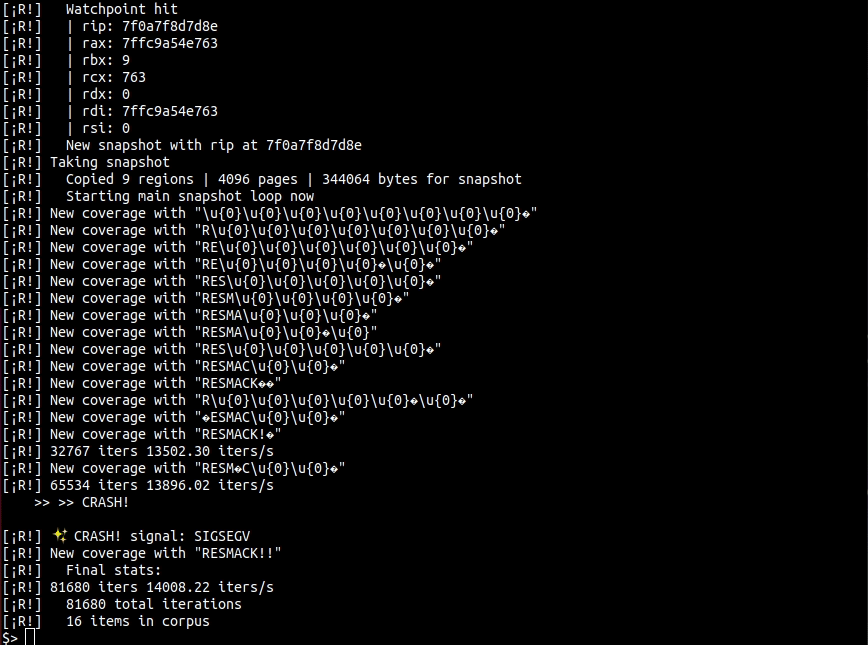
 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
 trailofbits/manticore
Symbolic execution tool
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
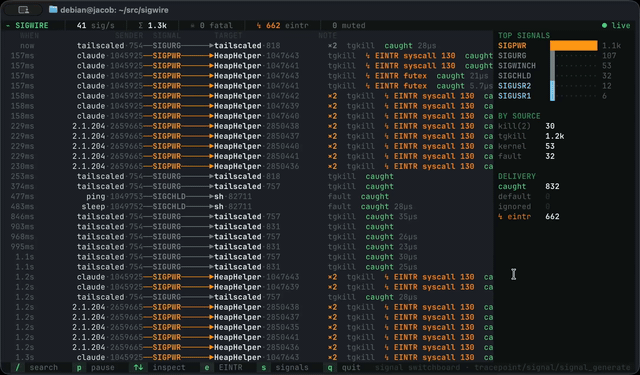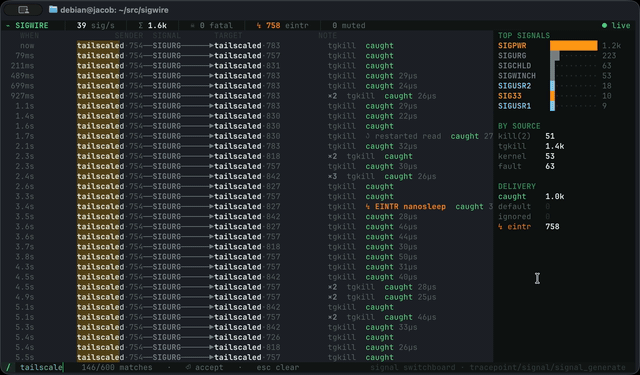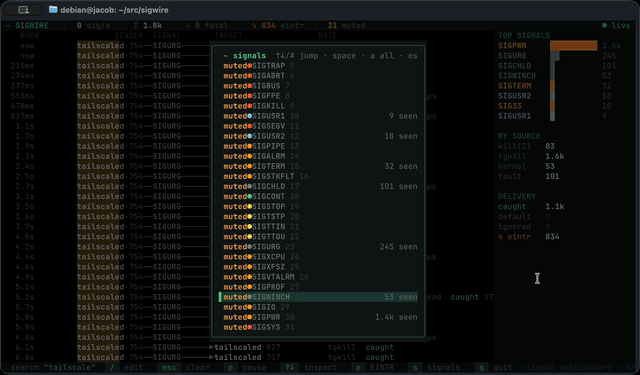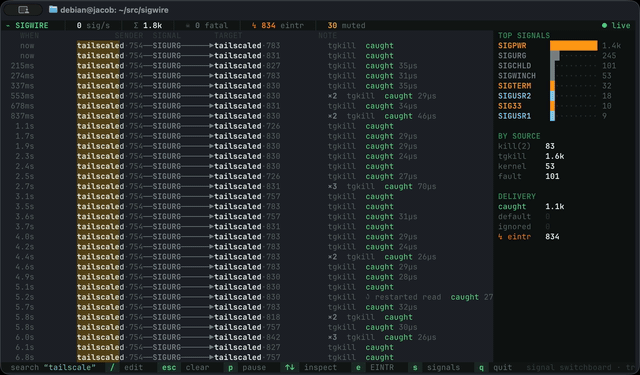 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 catern/rsyscall
Process-independent interface to Linux system calls
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...