

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
152 results
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k
15 days ago
cherrybomb preview

cherrybomb

GitHubblst-security/cherrybomb

CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

api-securityapi-security-testingdynamic-analysis-sandboxing+3
1.2k1 year ago
cuckoo3 preview

cuckoo3

GitHubcert-ee/cuckoo3

Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.

dynamic-analysis-sandboxingmalware-analysissecurity-virtualization
82110 months ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ai-securitybinary-analysisdebuggers+5
4927 months ago
nah preview

nah

GitHubmanuelschipper/nah

a guard that blocks catastrophic agent actions
ai-securitycode-analysiscommand-and-control+8
4913 days ago
incarcero preview

incarcero

GitHub0x48piraj/incarcero

Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
cloud-securitycurated-resourcesdynamic-analysis-sandboxing+4
942 years ago
TraceTree preview

TraceTree

GitHubtejasprasad2008-afk/tracetree

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…

container-securitydevsecopsdynamic-analysis-sandboxing+6
431 month ago
dae preview

dae

GitHubejfkdev/dae

Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…

android-securitybinary-analysisdebuggers+6
1119 days ago
Cusimanse preview

Cusimanse

GitHubopposum0112/cusimanse

Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute

ai-securitydefensive-toolsdynamic-analysis-sandboxing+9
1 month ago
process-watcher preview

process-watcher

GitHubneo23x0/process-watcher

A process monitoring tool that tries to detect exploitation

defensive-toolsdynamic-analysis-sandboxingincident-response+4
132 days ago
certfuzz preview
Archived

certfuzz

GitHubcertcc/certfuzz

This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).

binary-analysisdynamic-analysis-sandboxingexploitation+3
2741 year ago
sandbox-runtime preview

sandbox-runtime

GitHubanthropic-experimental/sandbox-runtime

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
configuration-auditingcontainer-securitydefensive-tools+4
5.7k1 day ago
Triton preview

Triton

GitHubjonathansalwan/triton

Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
binary-analysisdynamic-analysis-sandboxingfuzzing+1
4.3k5 months ago
Brida preview

Brida

GitHubfedericodotta/brida

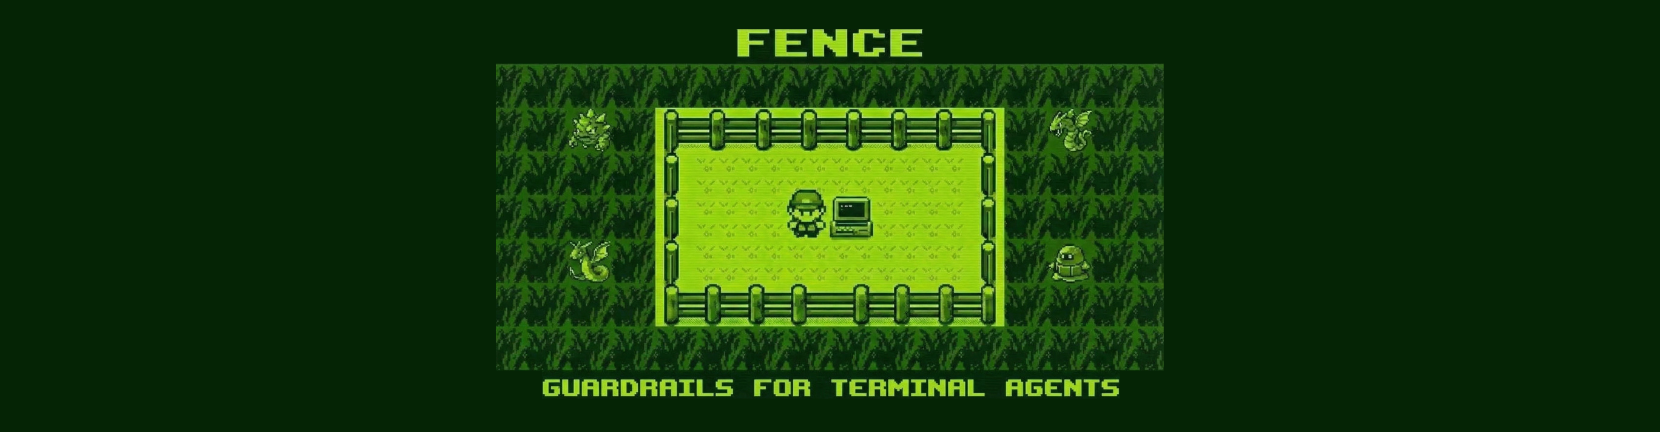
The new bridge between Burp Suite and Frida!
android-securitybinary-analysisdynamic-analysis-sandboxing+5
1.9k11 months ago
fence preview

fence

GitHubfencesandbox/fence

Lightweight, container-free sandbox for running commands with network and filesystem restrictions
container-securitydefensive-toolsdevsecops+5
9981 month ago
cuckooautoinstall preview

cuckooautoinstall

GitHubbuguroo/cuckooautoinstall

Auto Installer Script for Cuckoo Sandbox
dynamic-analysis-sandboxingmalware-analysisscripting-automation+1
1648 years ago
MCPwner preview

MCPwner

GitHubpigyon/mcpwner

Model Context Protocol server for autonomous vulnerability discovery

devsecopsdynamic-analysis-sandboxingfuzzing+6
562 months ago
spectrIDA-Reverse_Engineering_Stack preview

spectrIDA-Reverse_Engineering_Stack

GitHubggfuchsi-oss/spectrida-reverse_engineering_stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

ai-assisted-reversingbinary-analysisctf+8
643 months ago
Previous123…9Next