
DexLoader
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
android-securitybinary-exploitationdynamic-analysis-sandboxing+3
2
bend0us/dexloaderA demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 almkuznetsov/cve-2024-1441
Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 hzqst/unicorn_pe
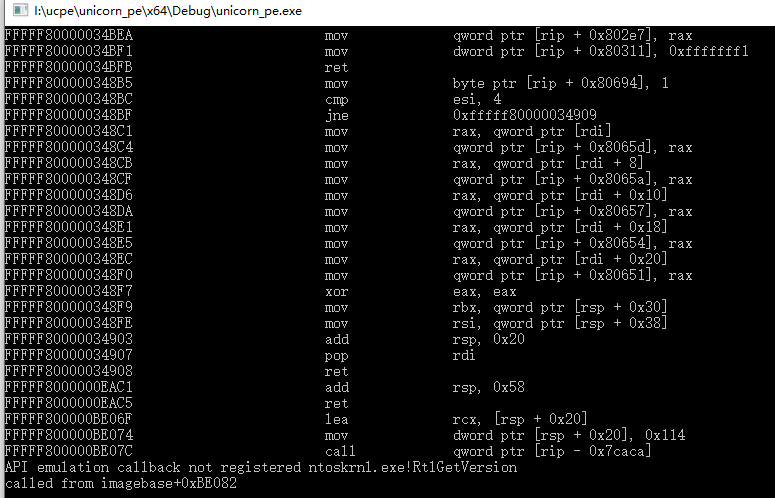
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 1ultimat3/badintent
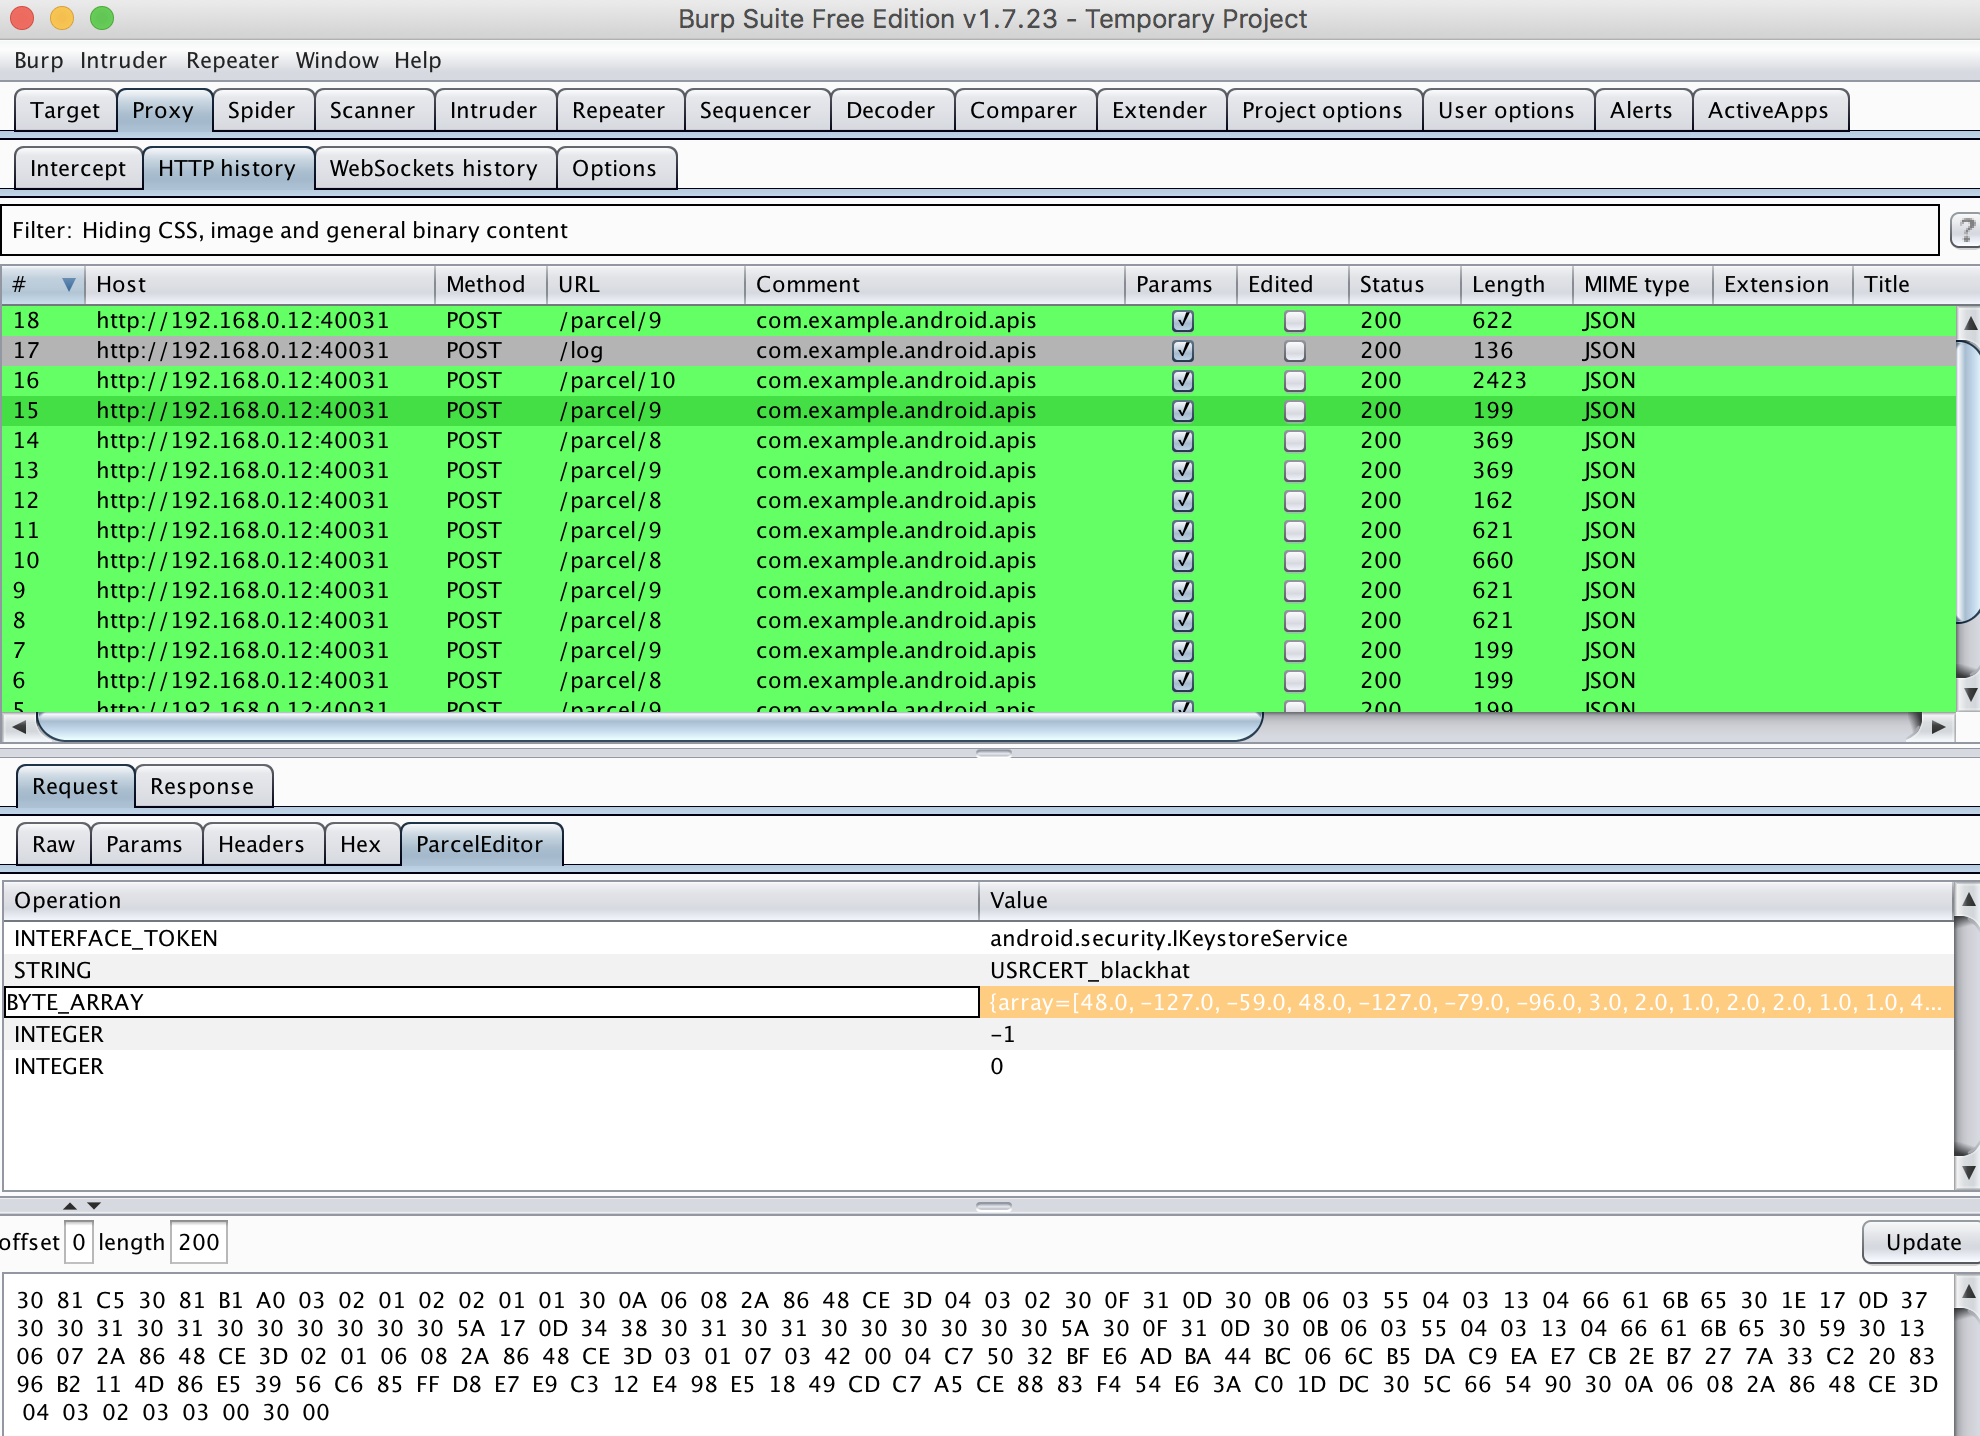
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 nowsecure/r2frida
Radare2 and Frida better together.
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 security-prince/resources-for-application-security
Some good resources for getting started with application security
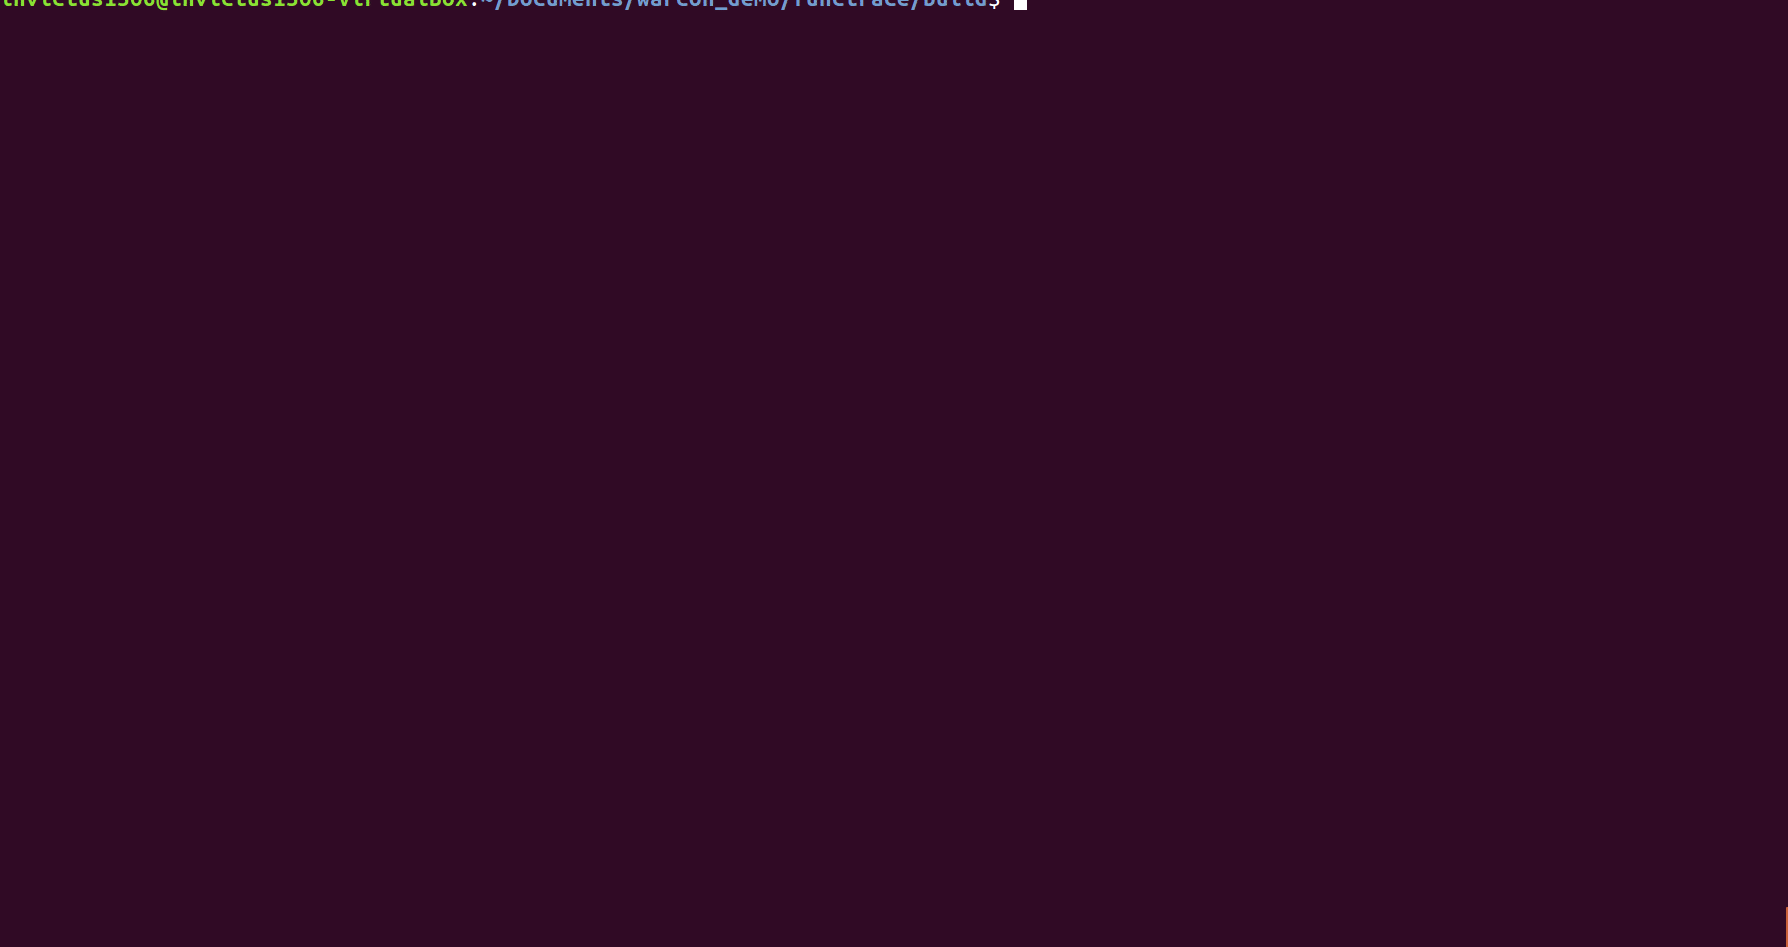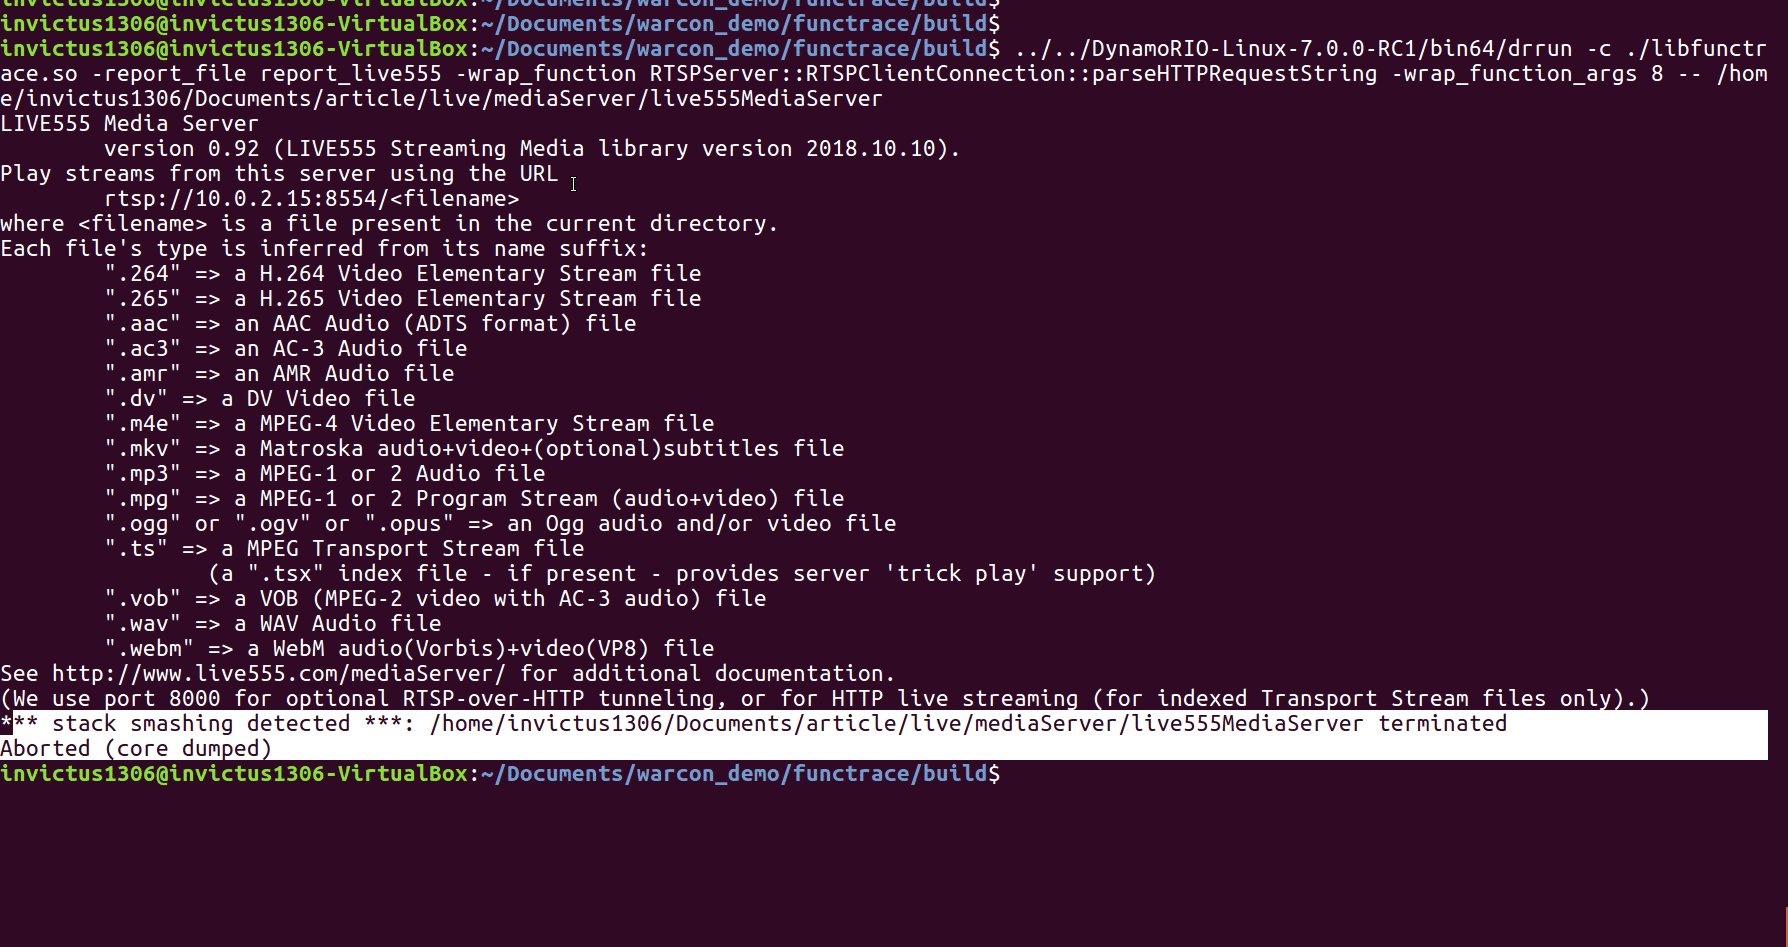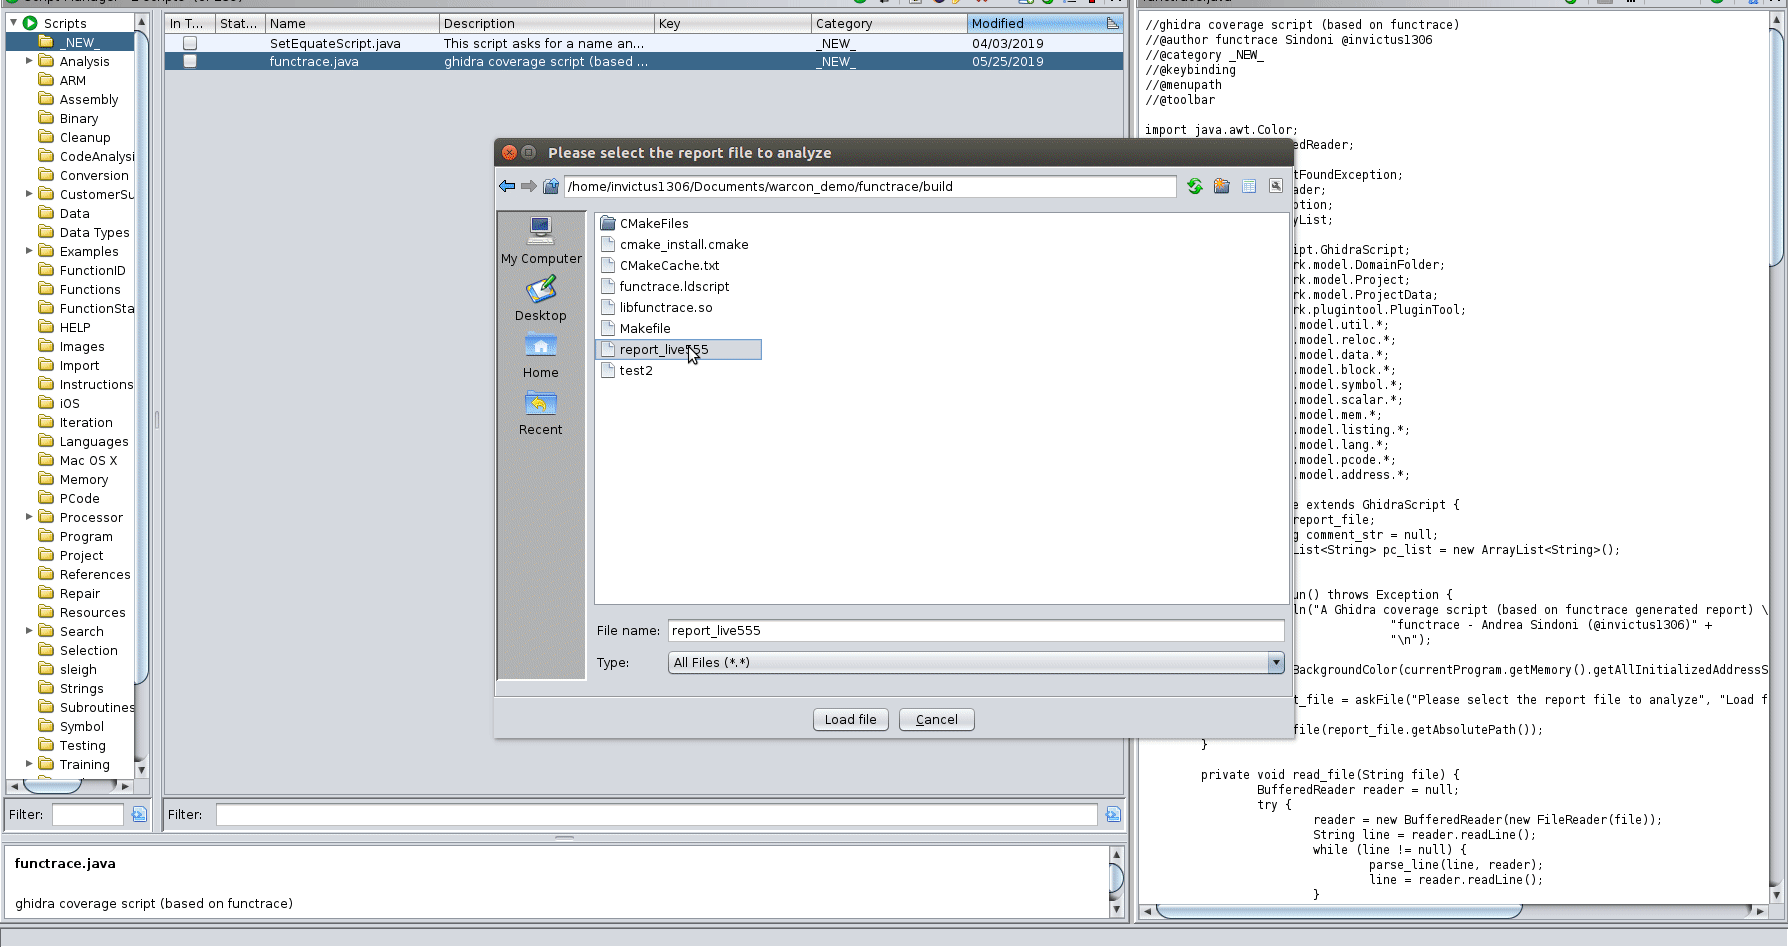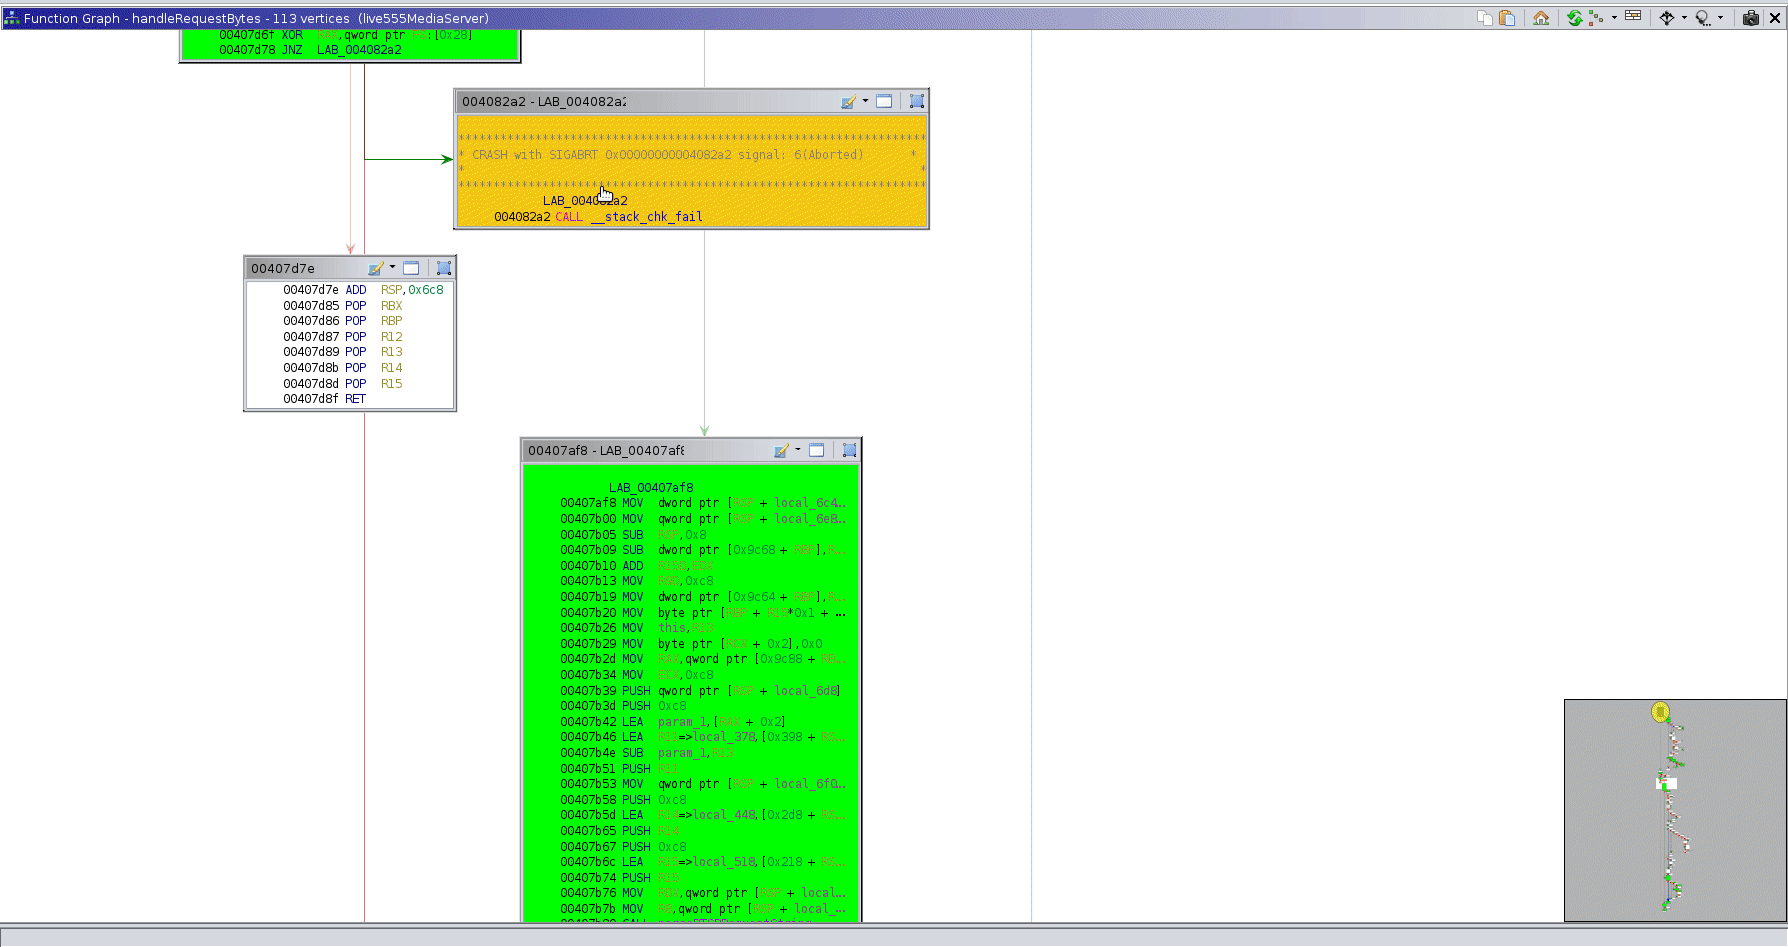 invictus1306/functrace
A function tracer
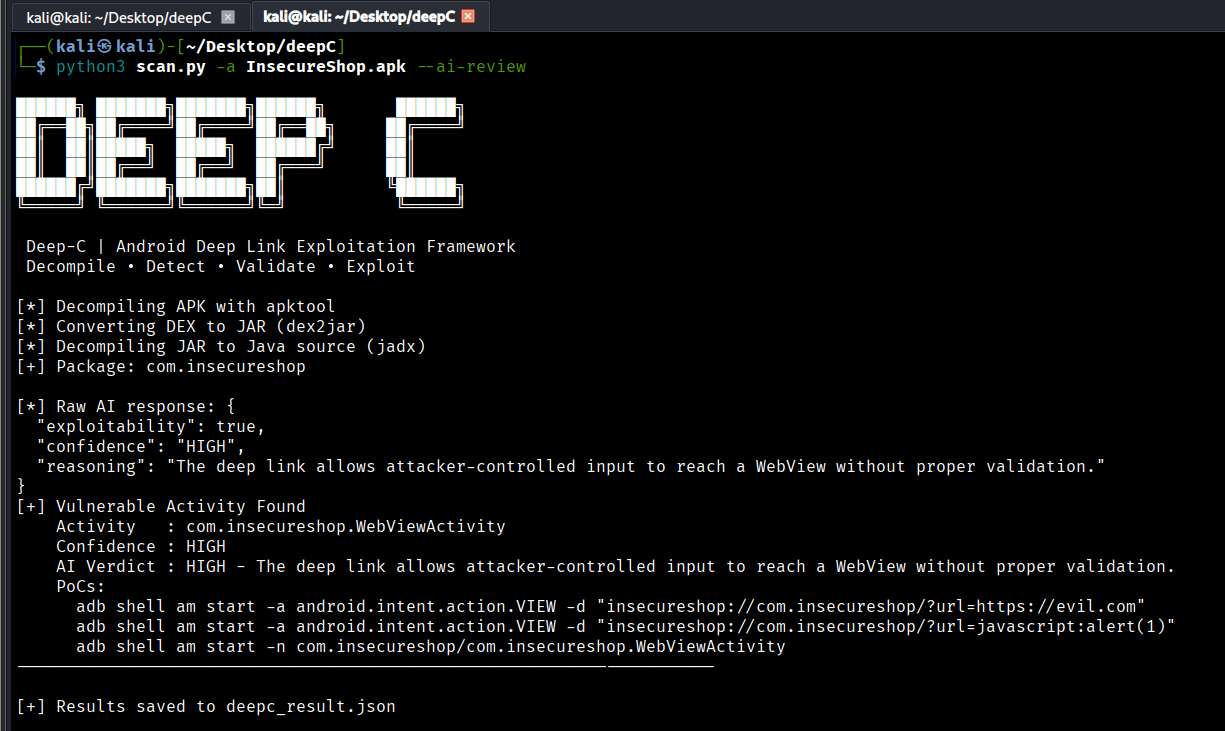 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
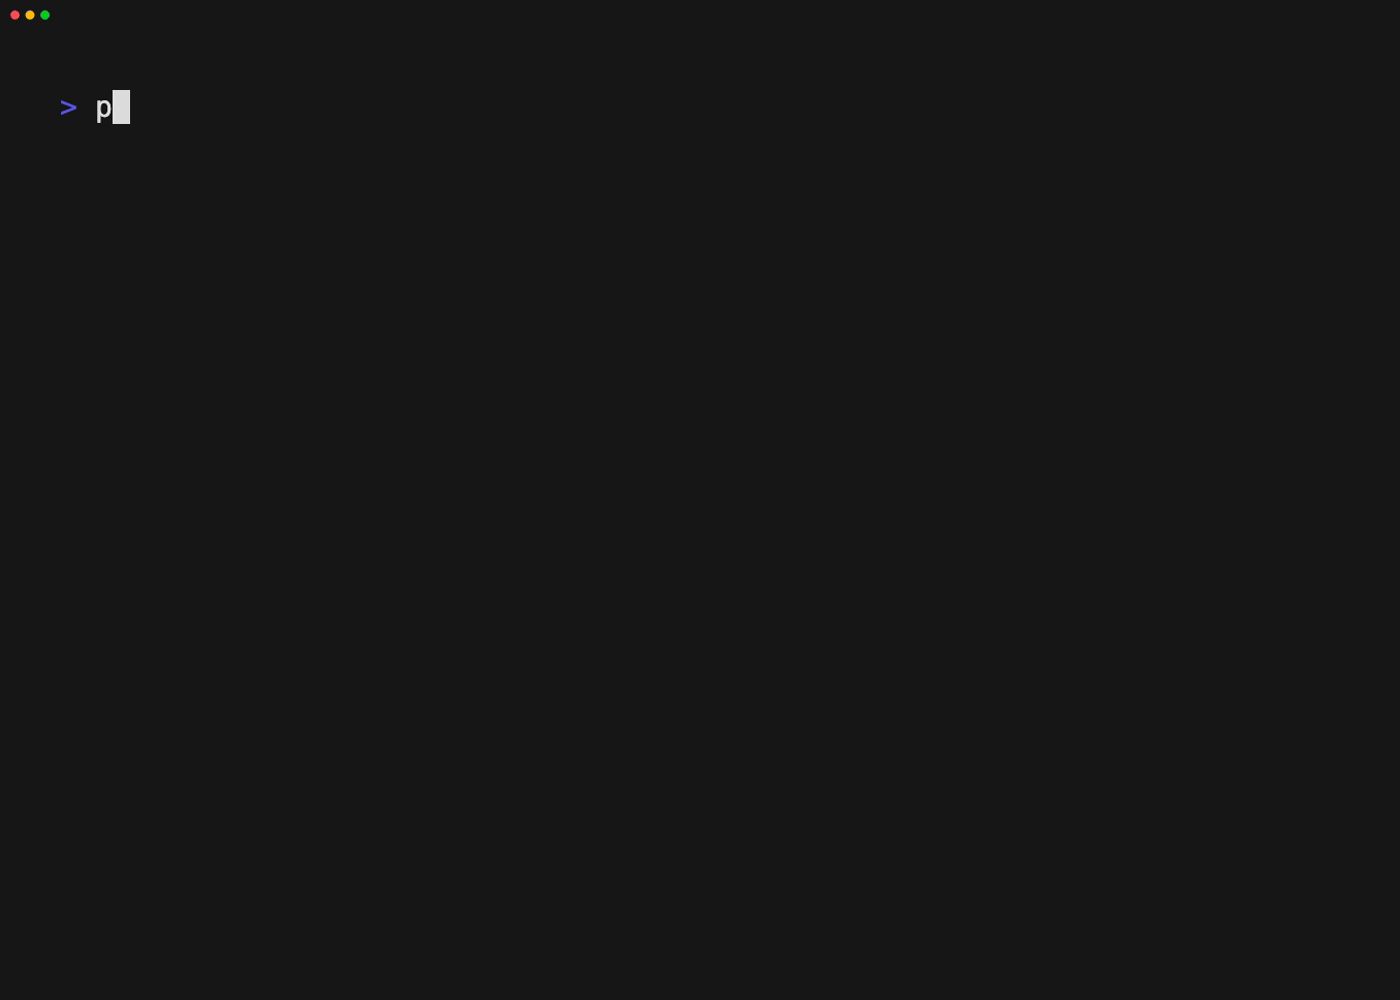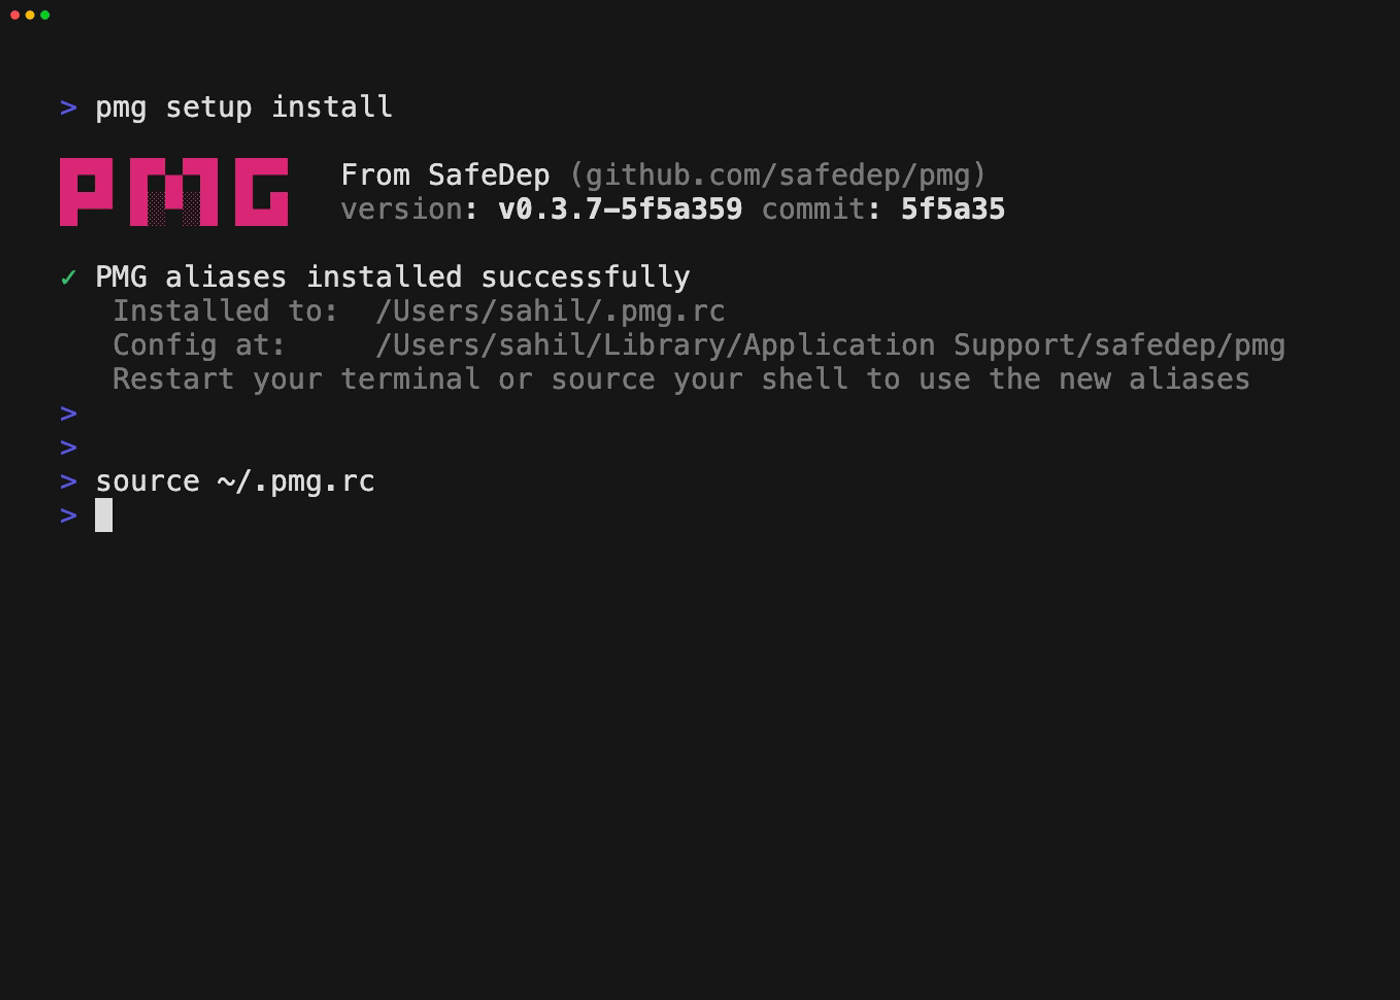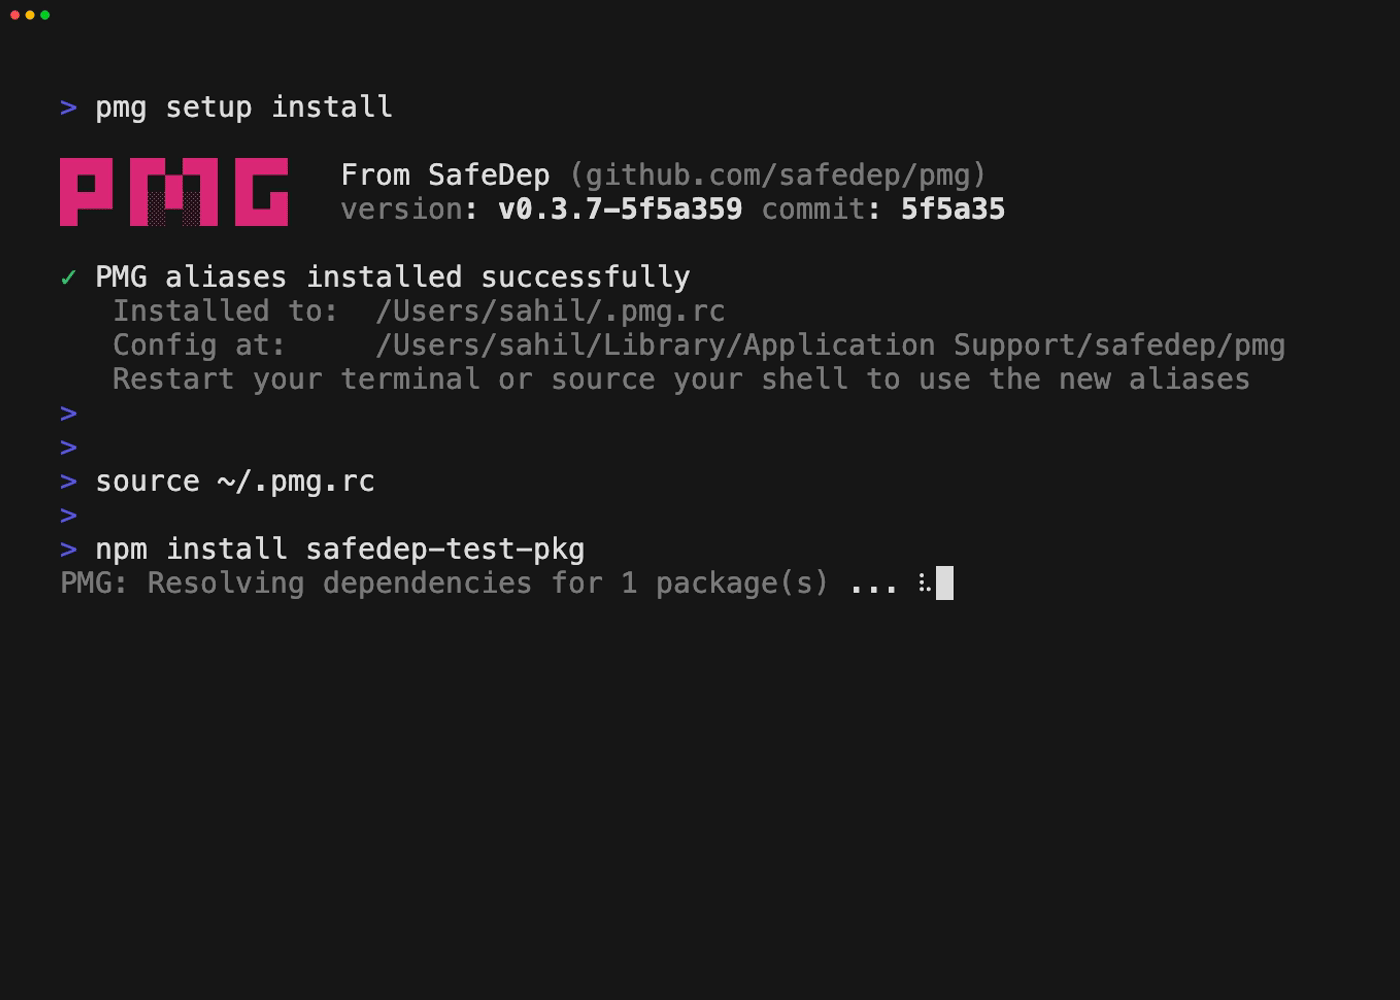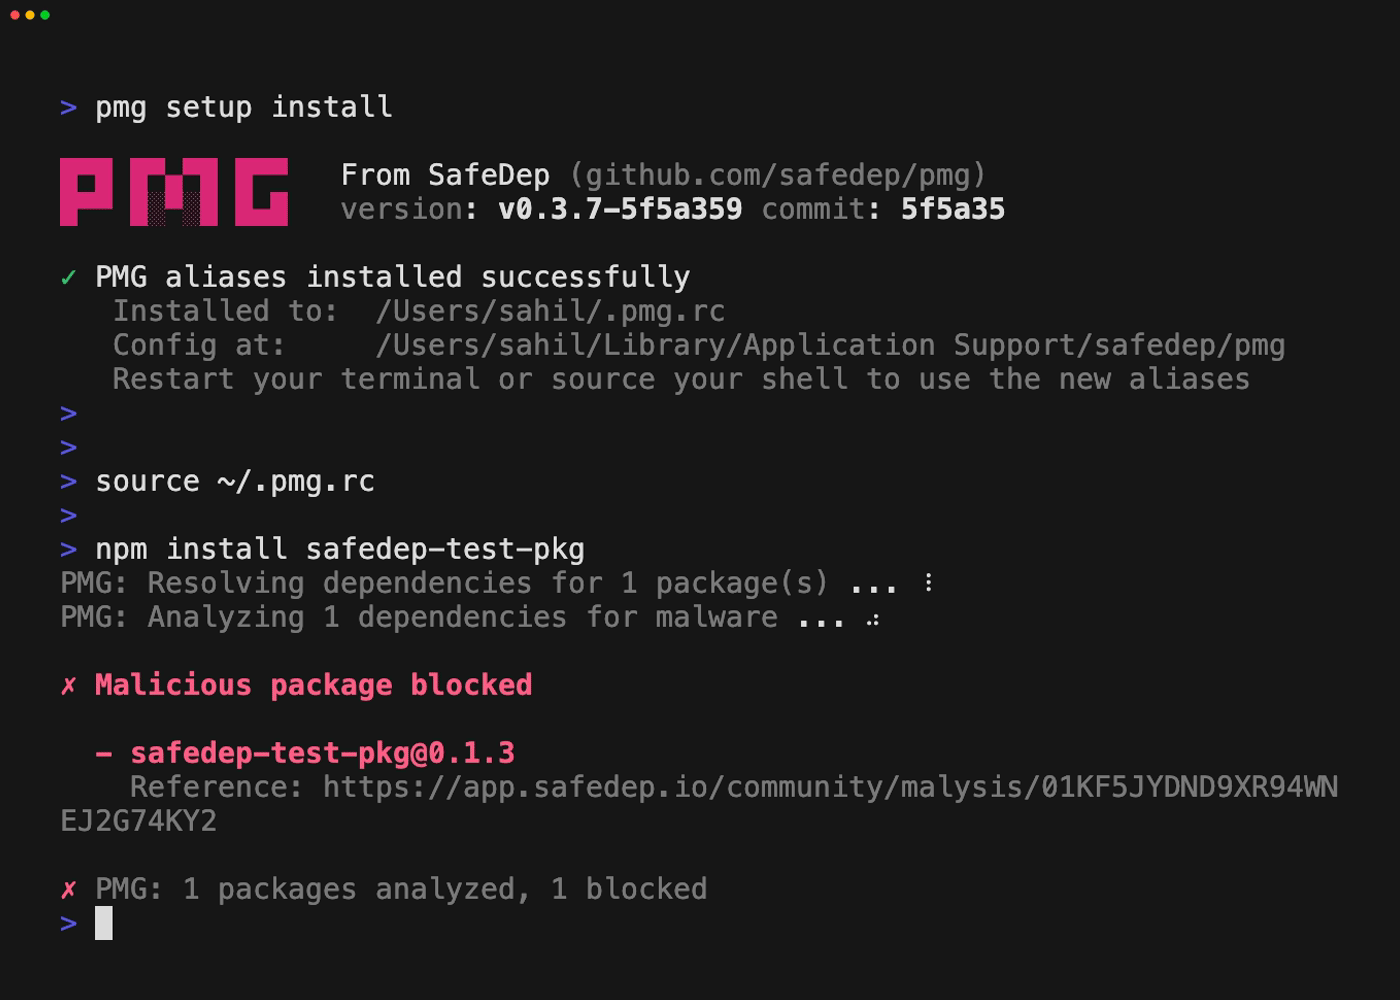 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 nccgroup/triforcelinuxsyscallfuzzer
A linux system call fuzzer using TriforceAFL