
DrSemu
 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
280
secrary/drsemuDrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 amossys/memitm
Tool to make in memory man in the middle
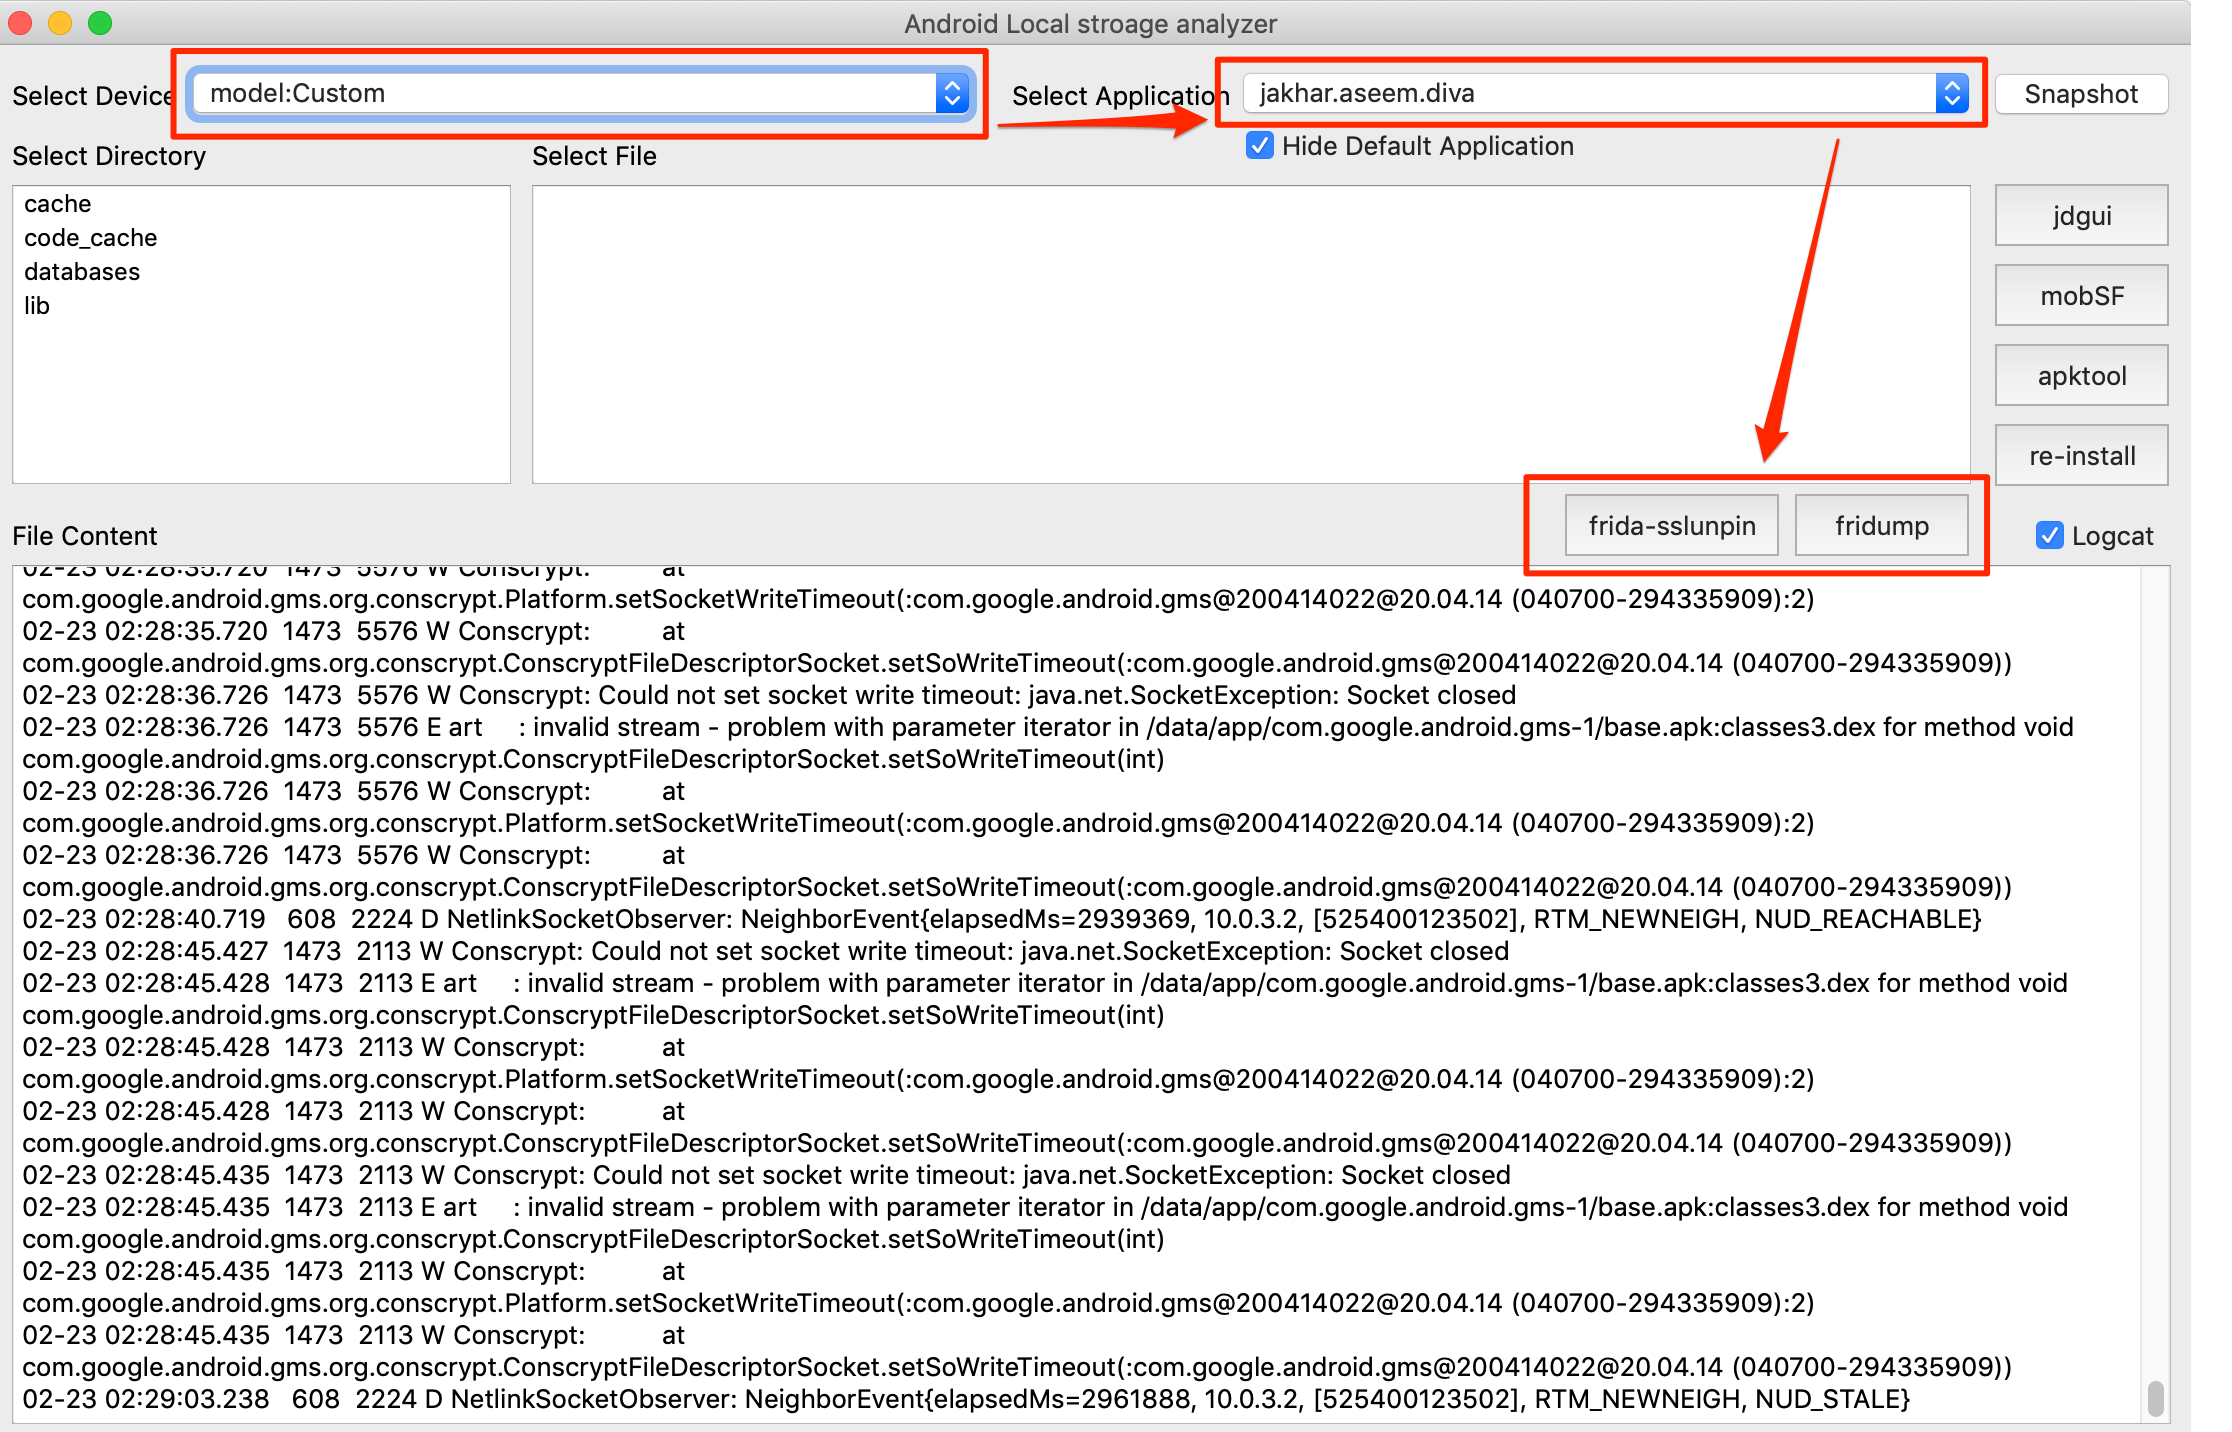 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
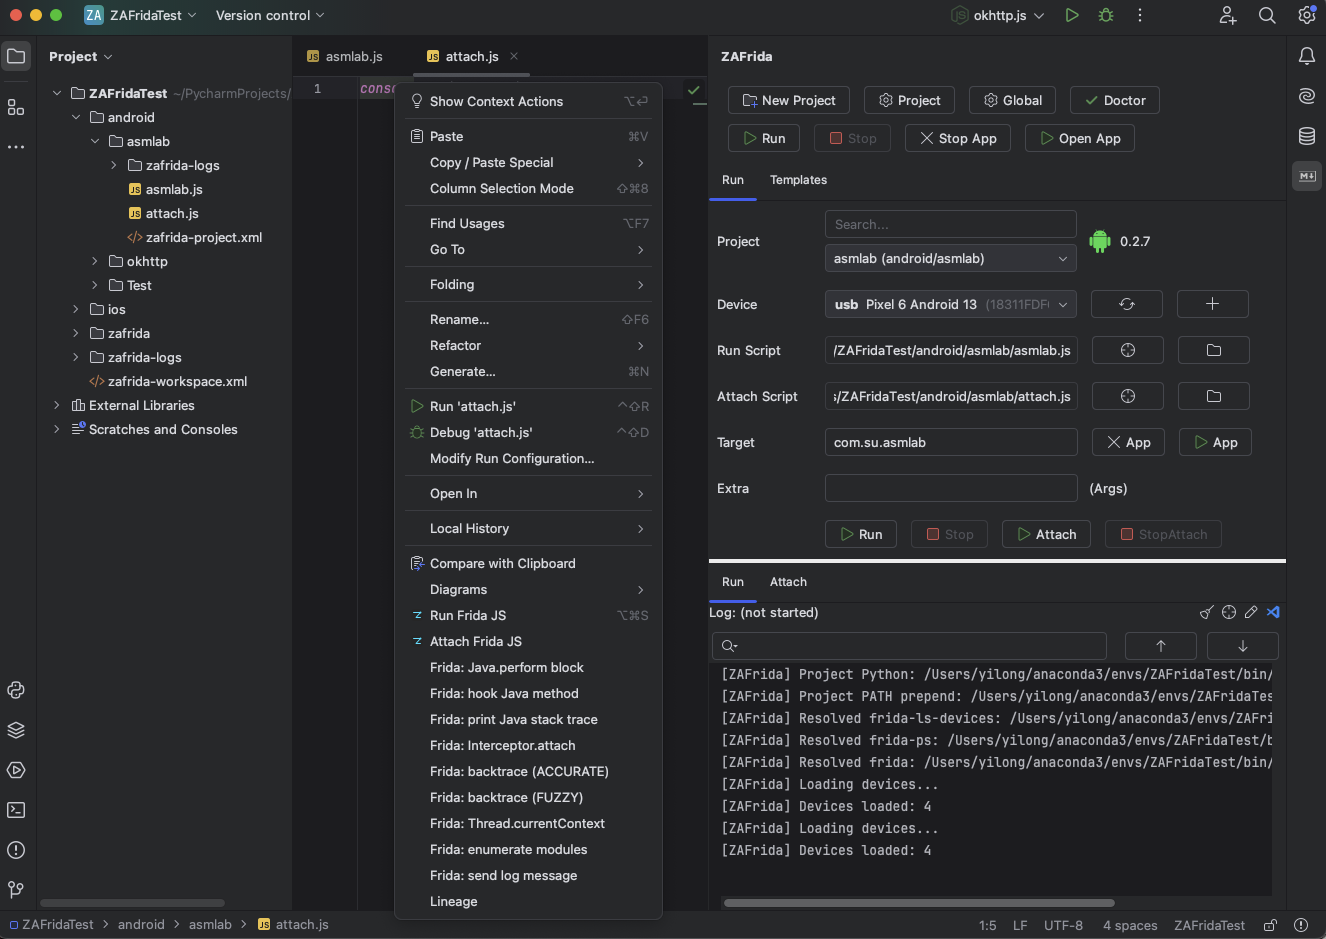 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
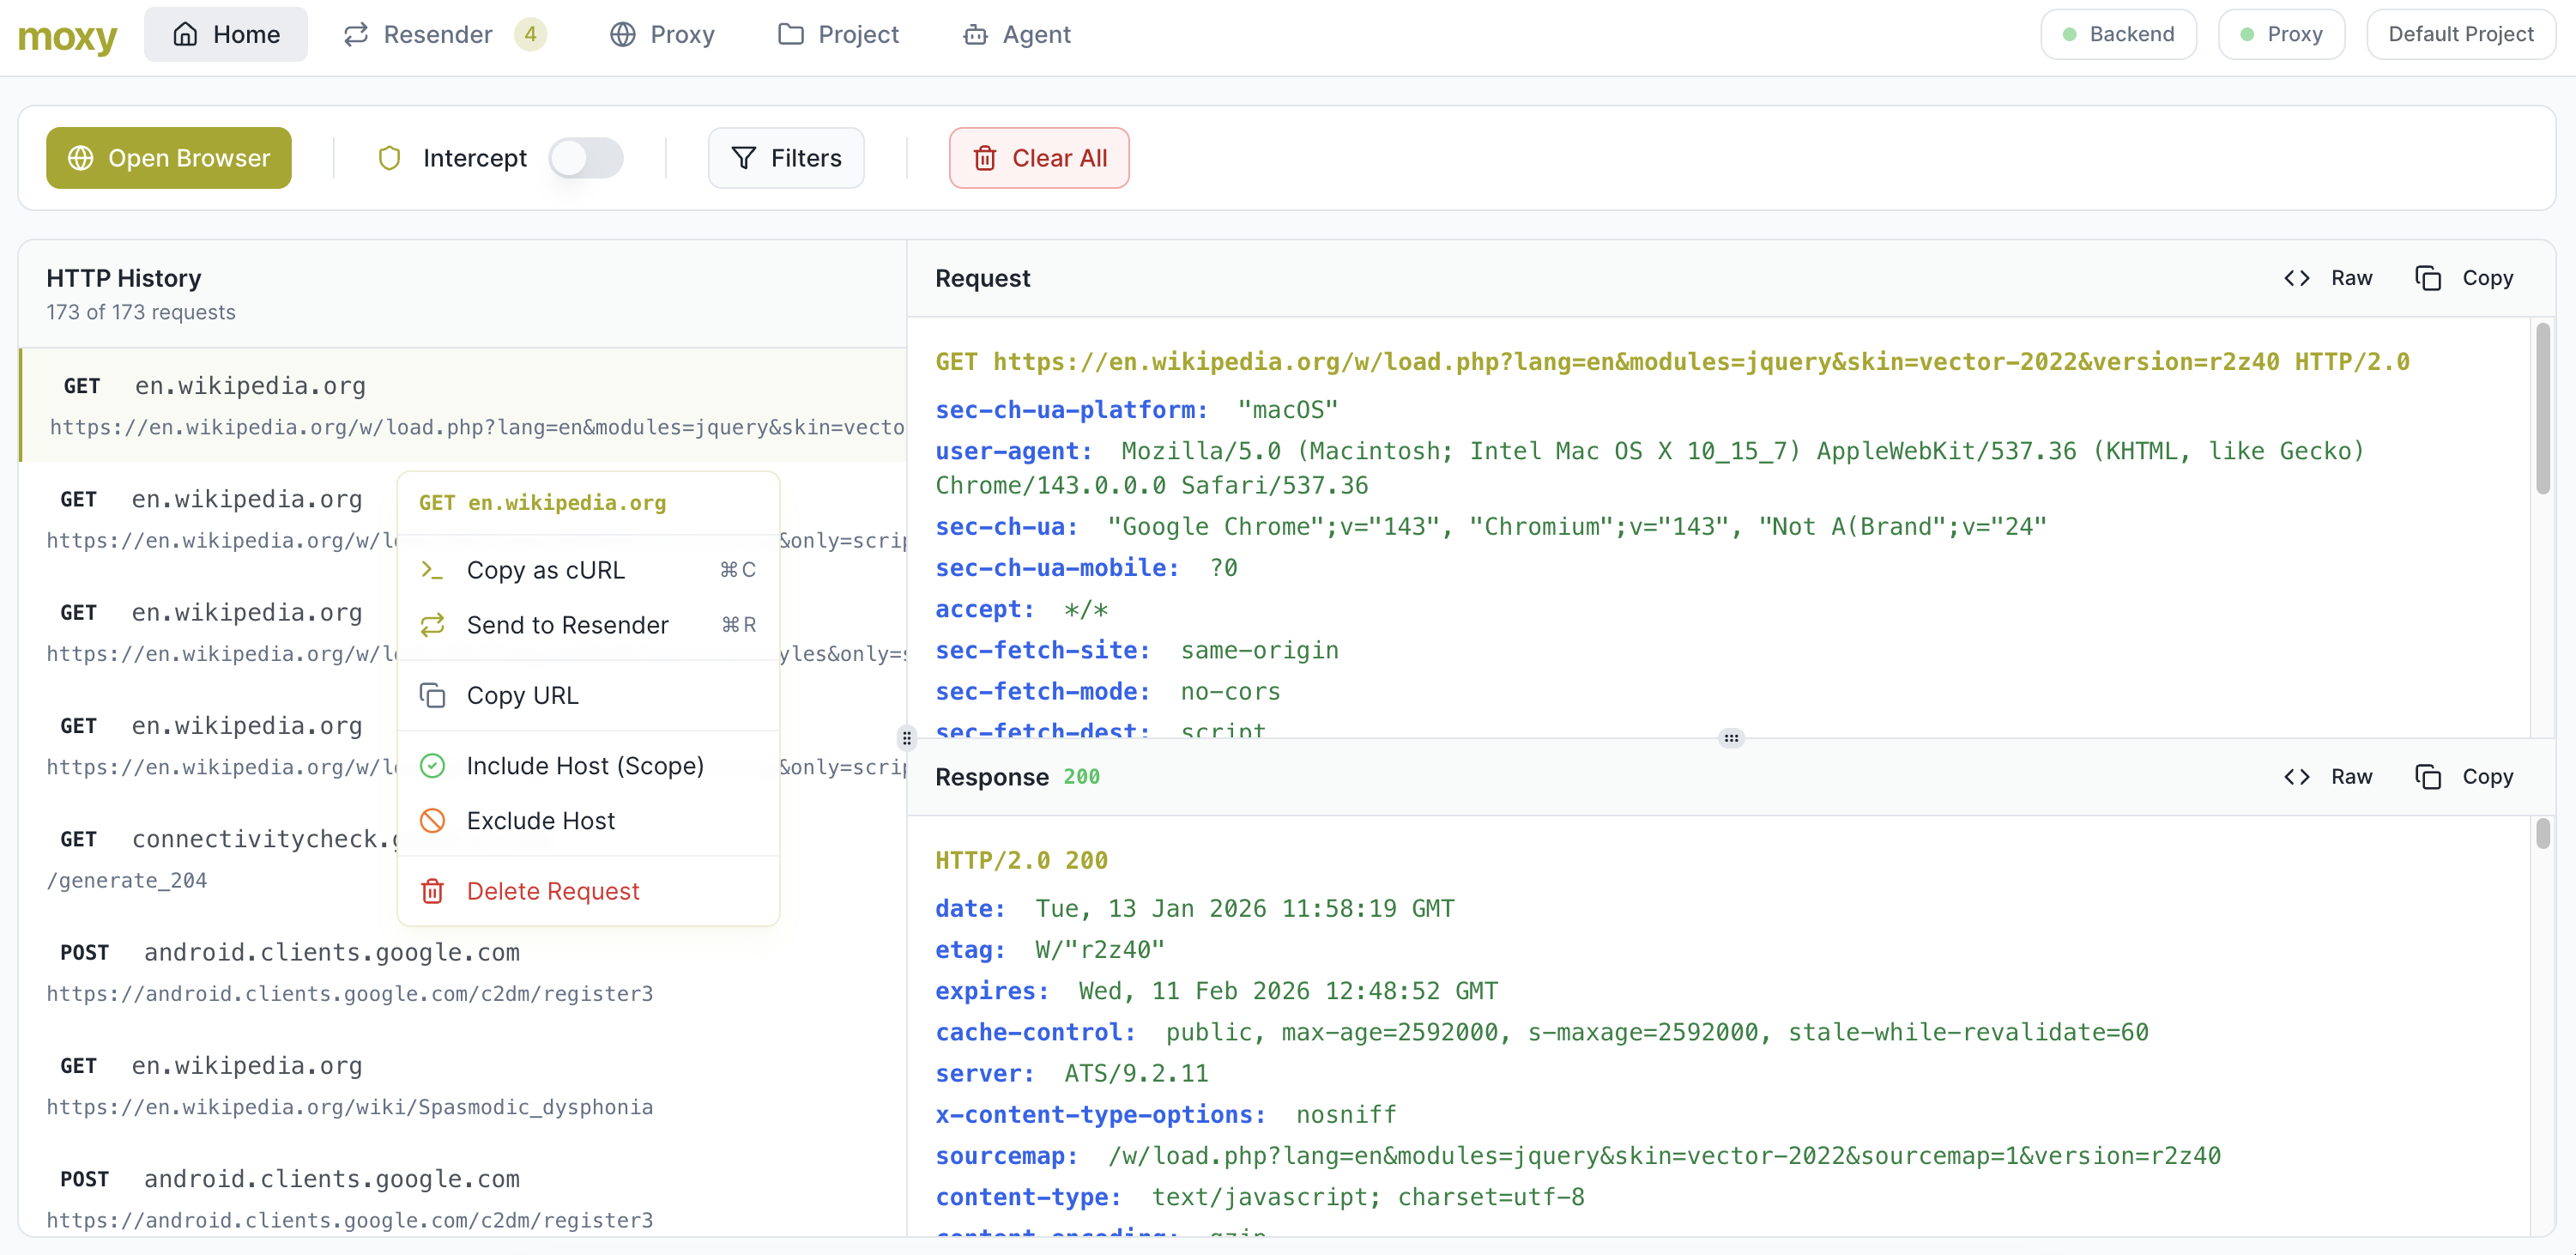 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
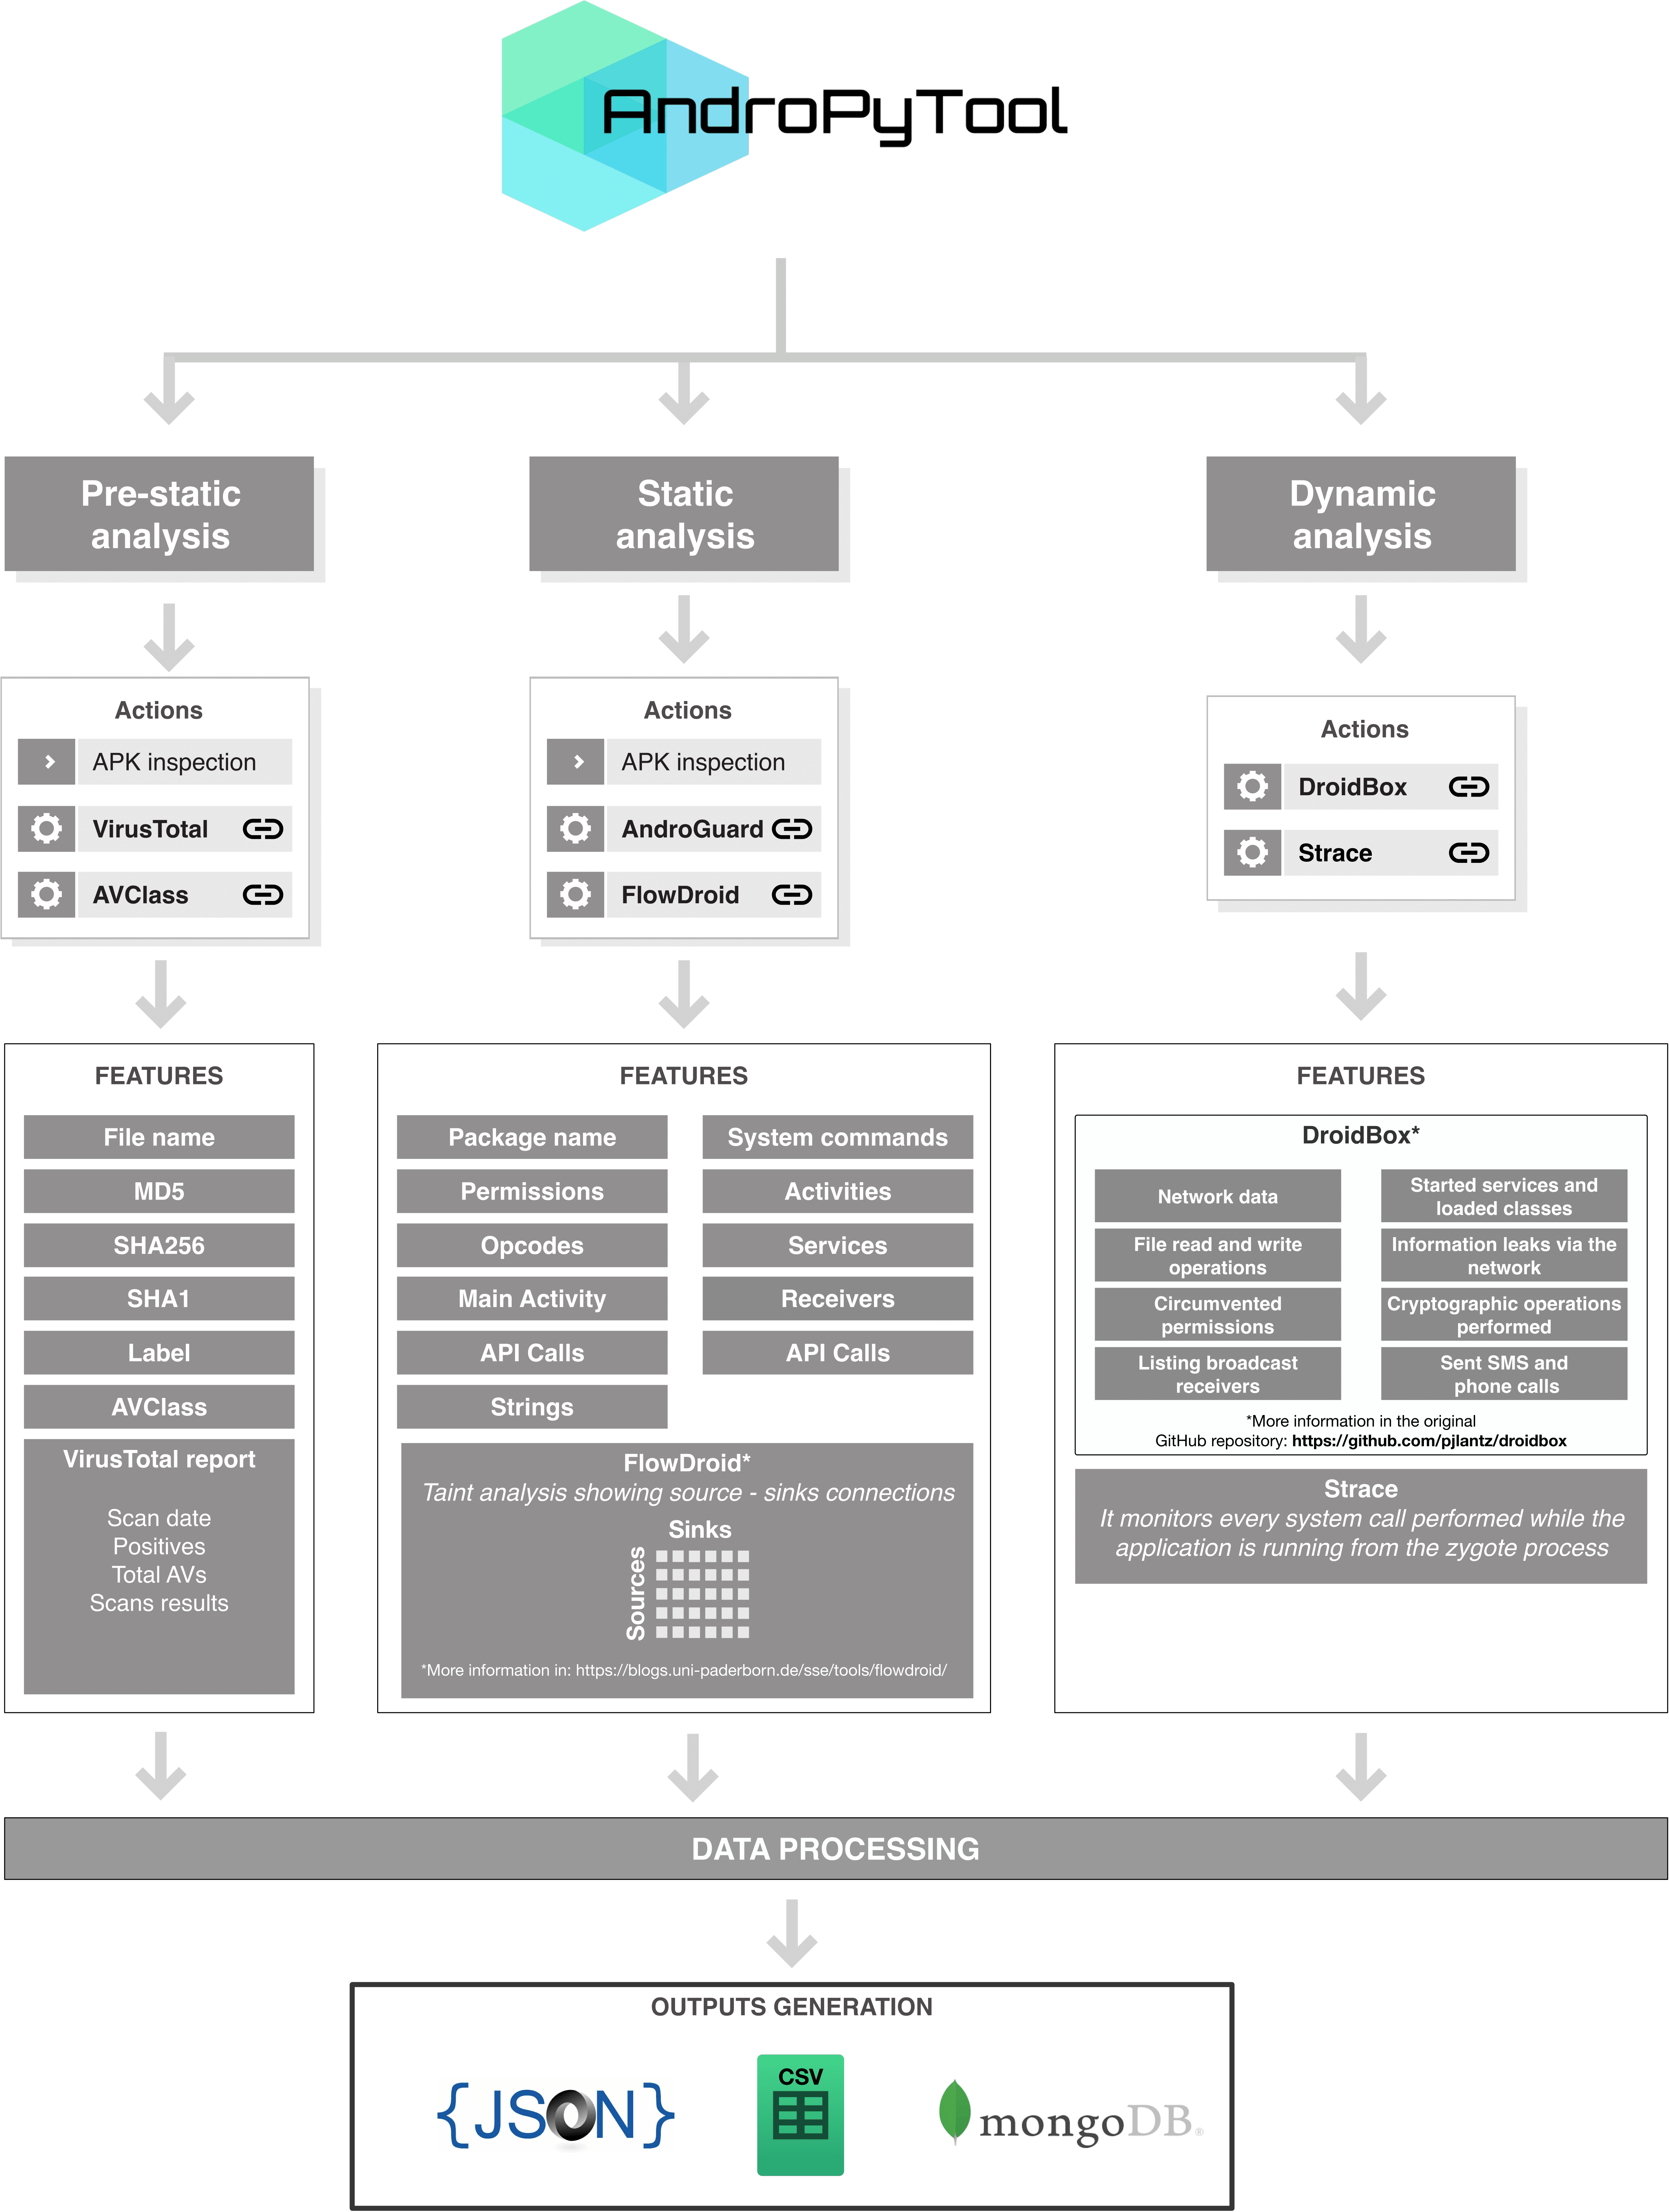 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
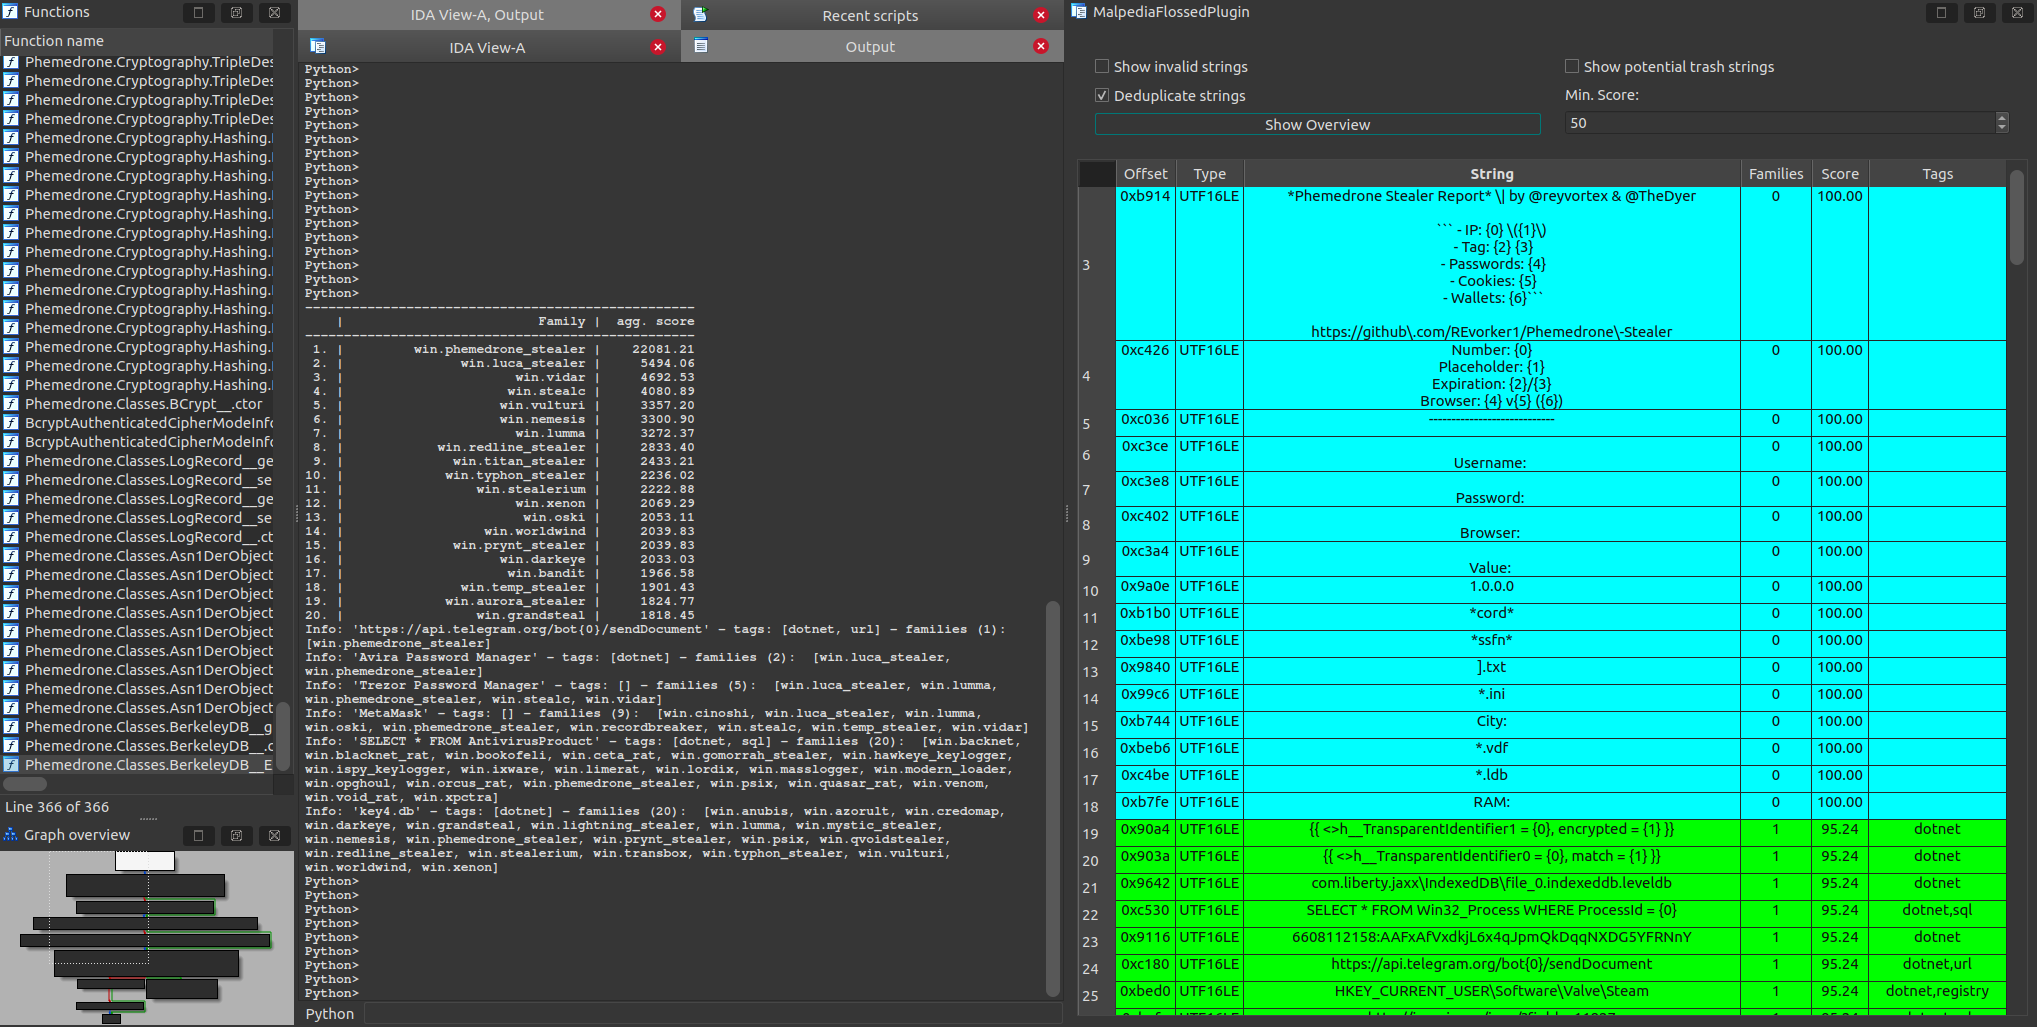 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
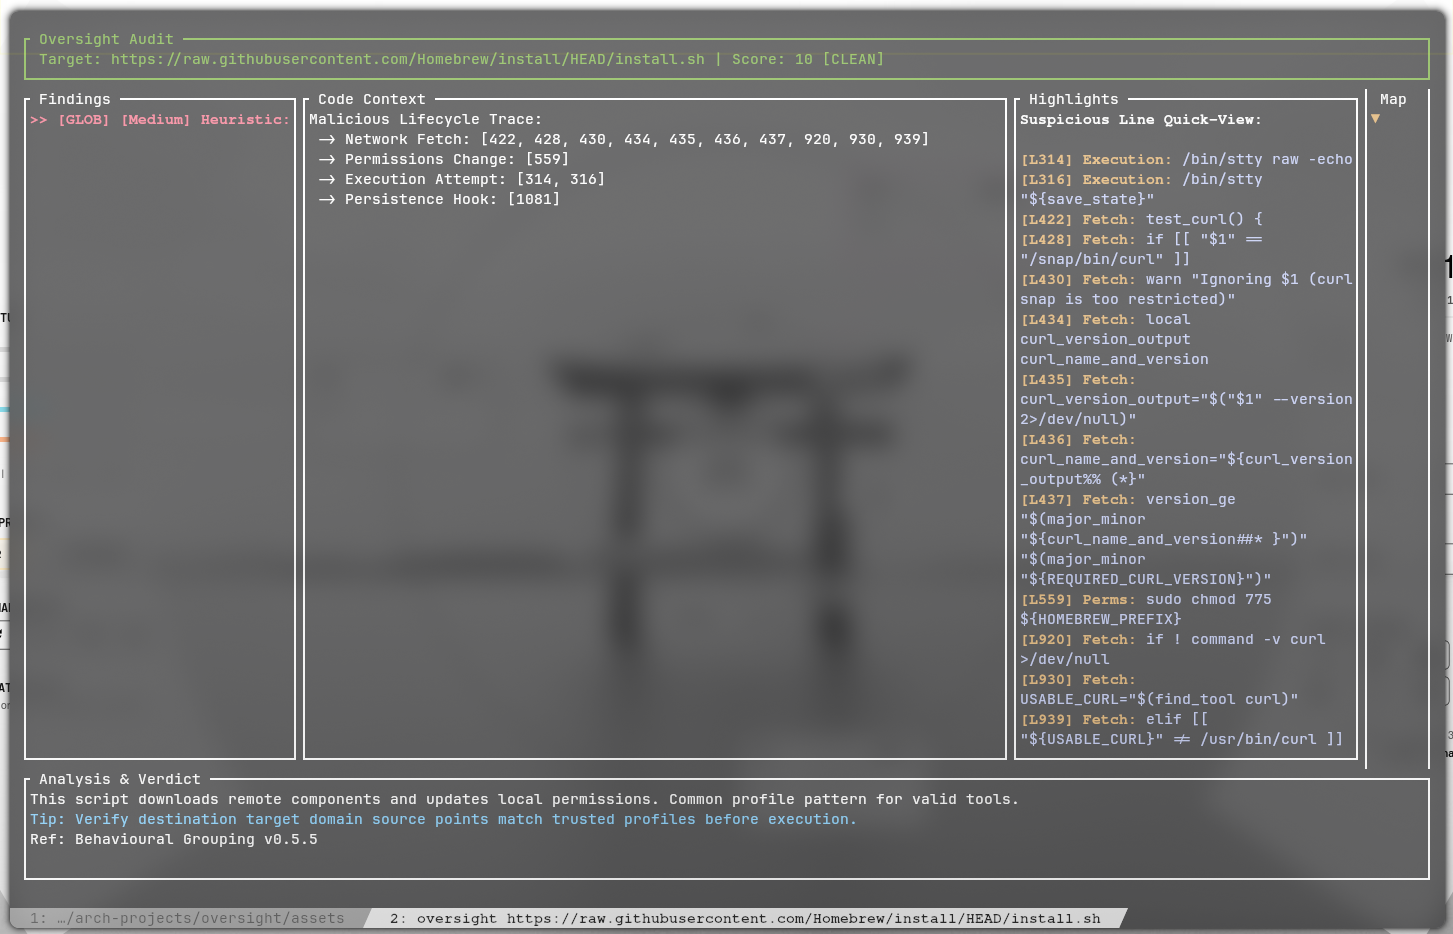 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…