

B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
552
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
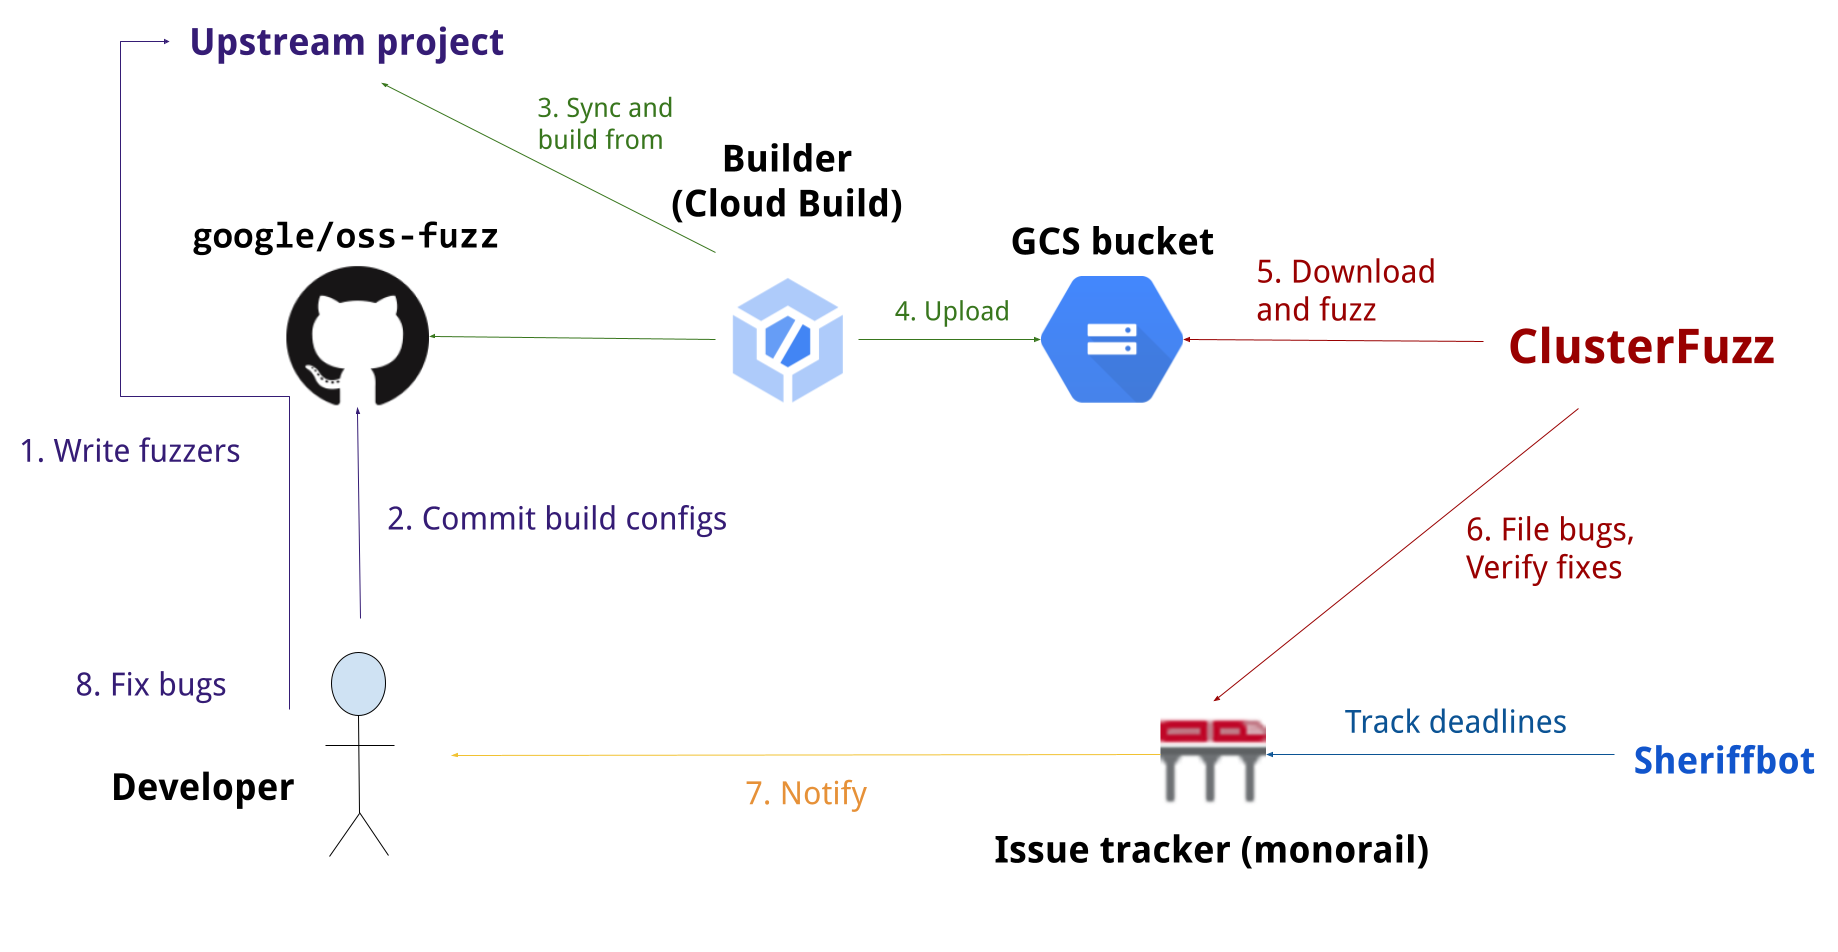 google/oss-fuzz
OSS-Fuzz - continuous fuzzing for open source software.
 google/clusterfuzz
Scalable fuzzing infrastructure with coverage-guided engines (libFuzzer, AFL, Honggfuzz), automated crash deduplication, bug filing, and regression…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
 angr/angr
A powerful and user-friendly binary analysis platform!
 ashishb/android-security-awesome
A collection of android security related resources
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
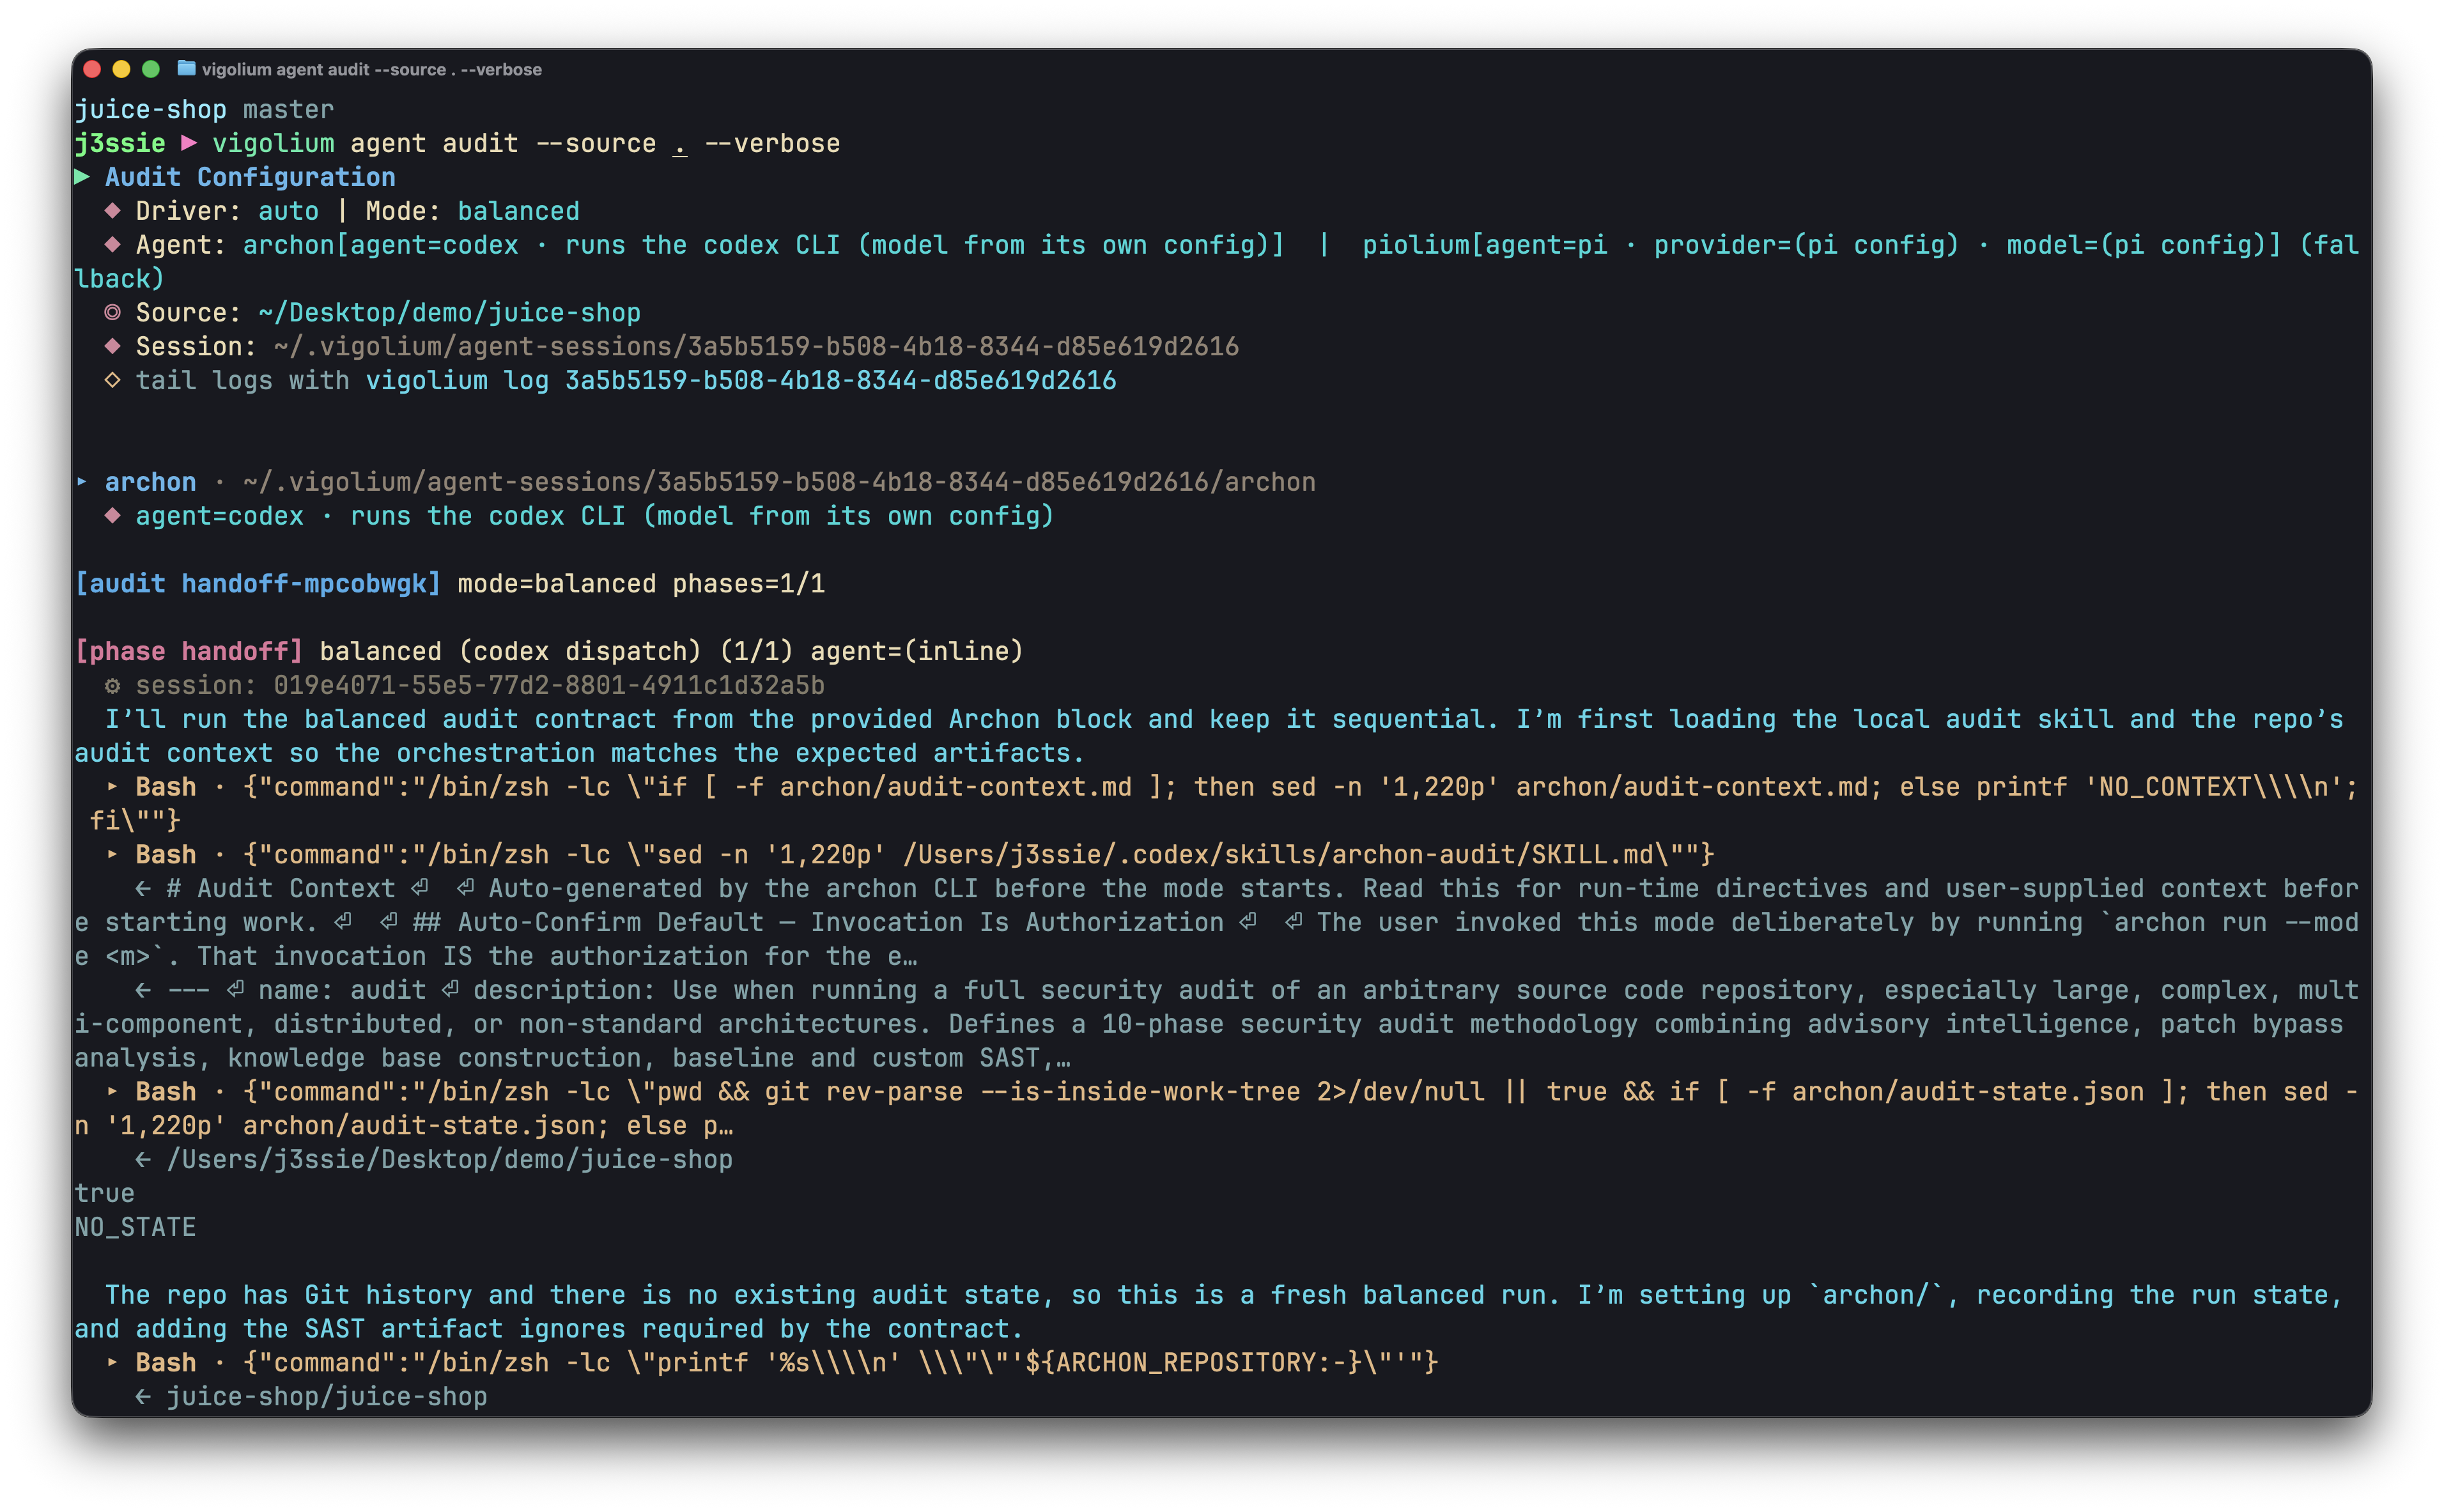 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…