

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
89 results
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.7k
11h 16m ago
sogen preview

sogen

GitHubmomo5502/sogen

🪅 Windows & Linux userspace emulator
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3.7k12h 11m ago
FACT_core preview

FACT_core

GitHubfkie-cad/fact_core

Firmware Analysis and Comparison Tool

binary-analysisdynamic-analysis-sandboxingembedded-systems-security+9
1.5k16h 52m ago
bromure preview

bromure

GitHubrderaison/bromure

Proper sandboxing for agentic coding and web browsing
ai-securitycontainer-securitydynamic-analysis-sandboxing+6
29818h 32m ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1651 day ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
digital-forensicsdynamic-analysis-sandboxingforensics+5
1191 day ago
raptor preview

raptor

GitHubgadievron/raptor

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
3.9k2 days ago
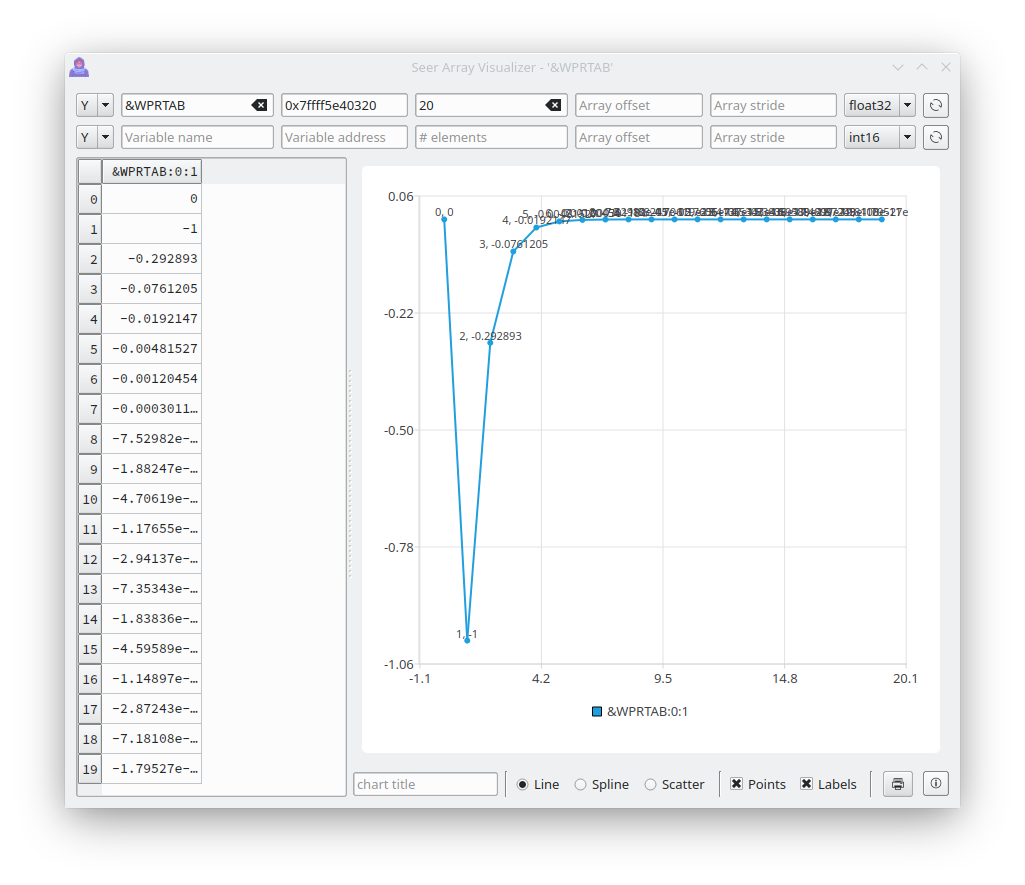
seer preview

seer

GitHubepasveer/seer

Seer - a gui frontend to gdb

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3.5k3 days ago
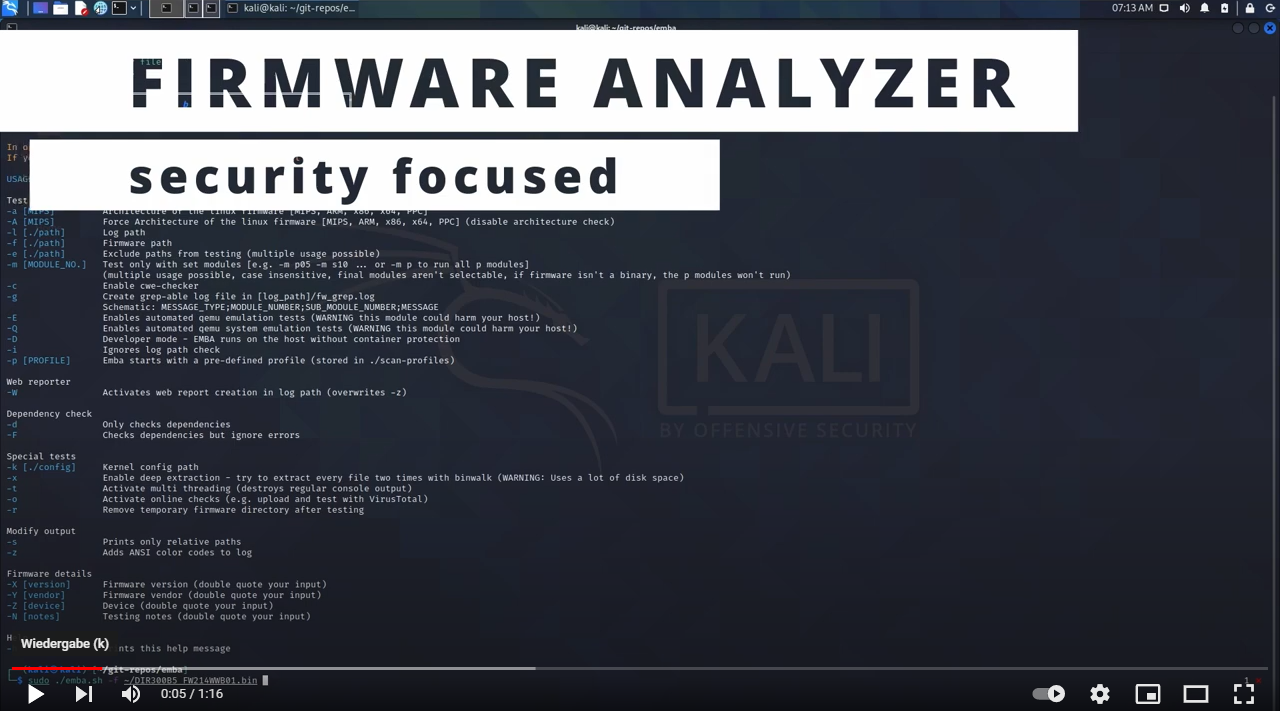
emba preview

emba

GitHube-m-b-a/emba

EMBA - The firmware security analyzer
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+8
3.7k3 days ago
litebox-seccomp-open-rdonly preview

litebox-seccomp-open-rdonly

GitHubabraxas/litebox-seccomp-open-rdonly

High local file read: LiteBox v0.1.0 linux-userland seccomp SYS_open O_RDONLY has no host path check
container-securitydynamic-analysis-sandboxingexploitation+4
4 days ago
rsyscall preview

rsyscall

GitHubcatern/rsyscall

Process-independent interface to Linux system calls

binary-analysisdebuggersdynamic-analysis-sandboxing+3
966 days ago
AetherVM preview

AetherVM

GitHubaethervm/aethervm

LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
binary-analysisbinary-exploitationcode-analysis+8
157 days ago
unidbg preview

unidbg

GitHubzhkl0228/unidbg

Allows you to emulate an Android native library, and an experimental iOS emulation

ai-assisted-reversingandroid-securitybinary-analysis+5
5.3k8 days ago
GateX preview

GateX

GitHubabraxas/gatex

FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…

binary-analysisbinary-exploitationcryptography+8
19 days ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9 days ago
nah preview

nah

GitHubmanuelschipper/nah

a guard that blocks catastrophic agent actions
ai-securitycode-analysiscommand-and-control+8
48511 days ago
super-trouper preview

super-trouper

GitHubcrissyfield/super-trouper

MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
android-securitybinary-analysisdebuggers+5
5111 days ago
VulnReach preview

VulnReach

GitHubowasp/vulnreach

Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

code-analysisdevsecopsdynamic-analysis-sandboxing+5
1611 days ago
Previous12345Next