
Noriben
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
dynamic-analysis-sandboxingforensicsioc-management+1
1.3k
rurik/noribenPython-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
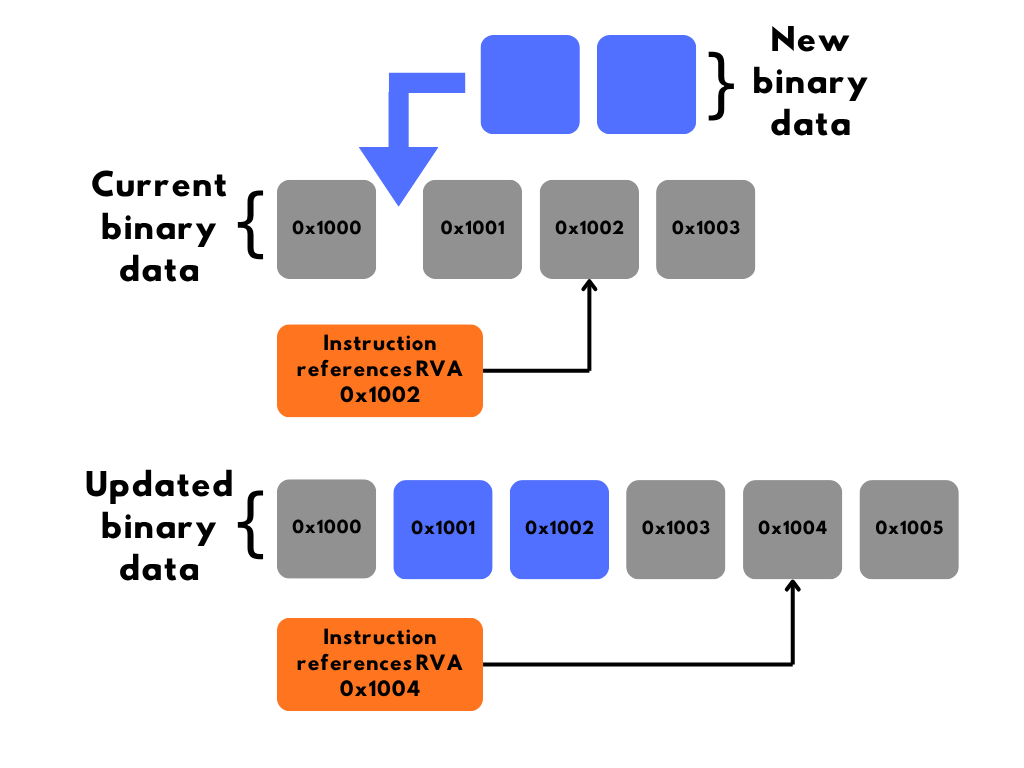 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 dbrumley/extract75-cve-2020-13995
Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.
 fracturelabs/go-scan-spring
Vulnerability scanner for Spring4Shell (CVE-2022-22965)
 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
 h1nayoshi/smalien
Information flow analysis tool for Android applications
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 nccgroup/frisbeelite
A GUI-based USB device fuzzer
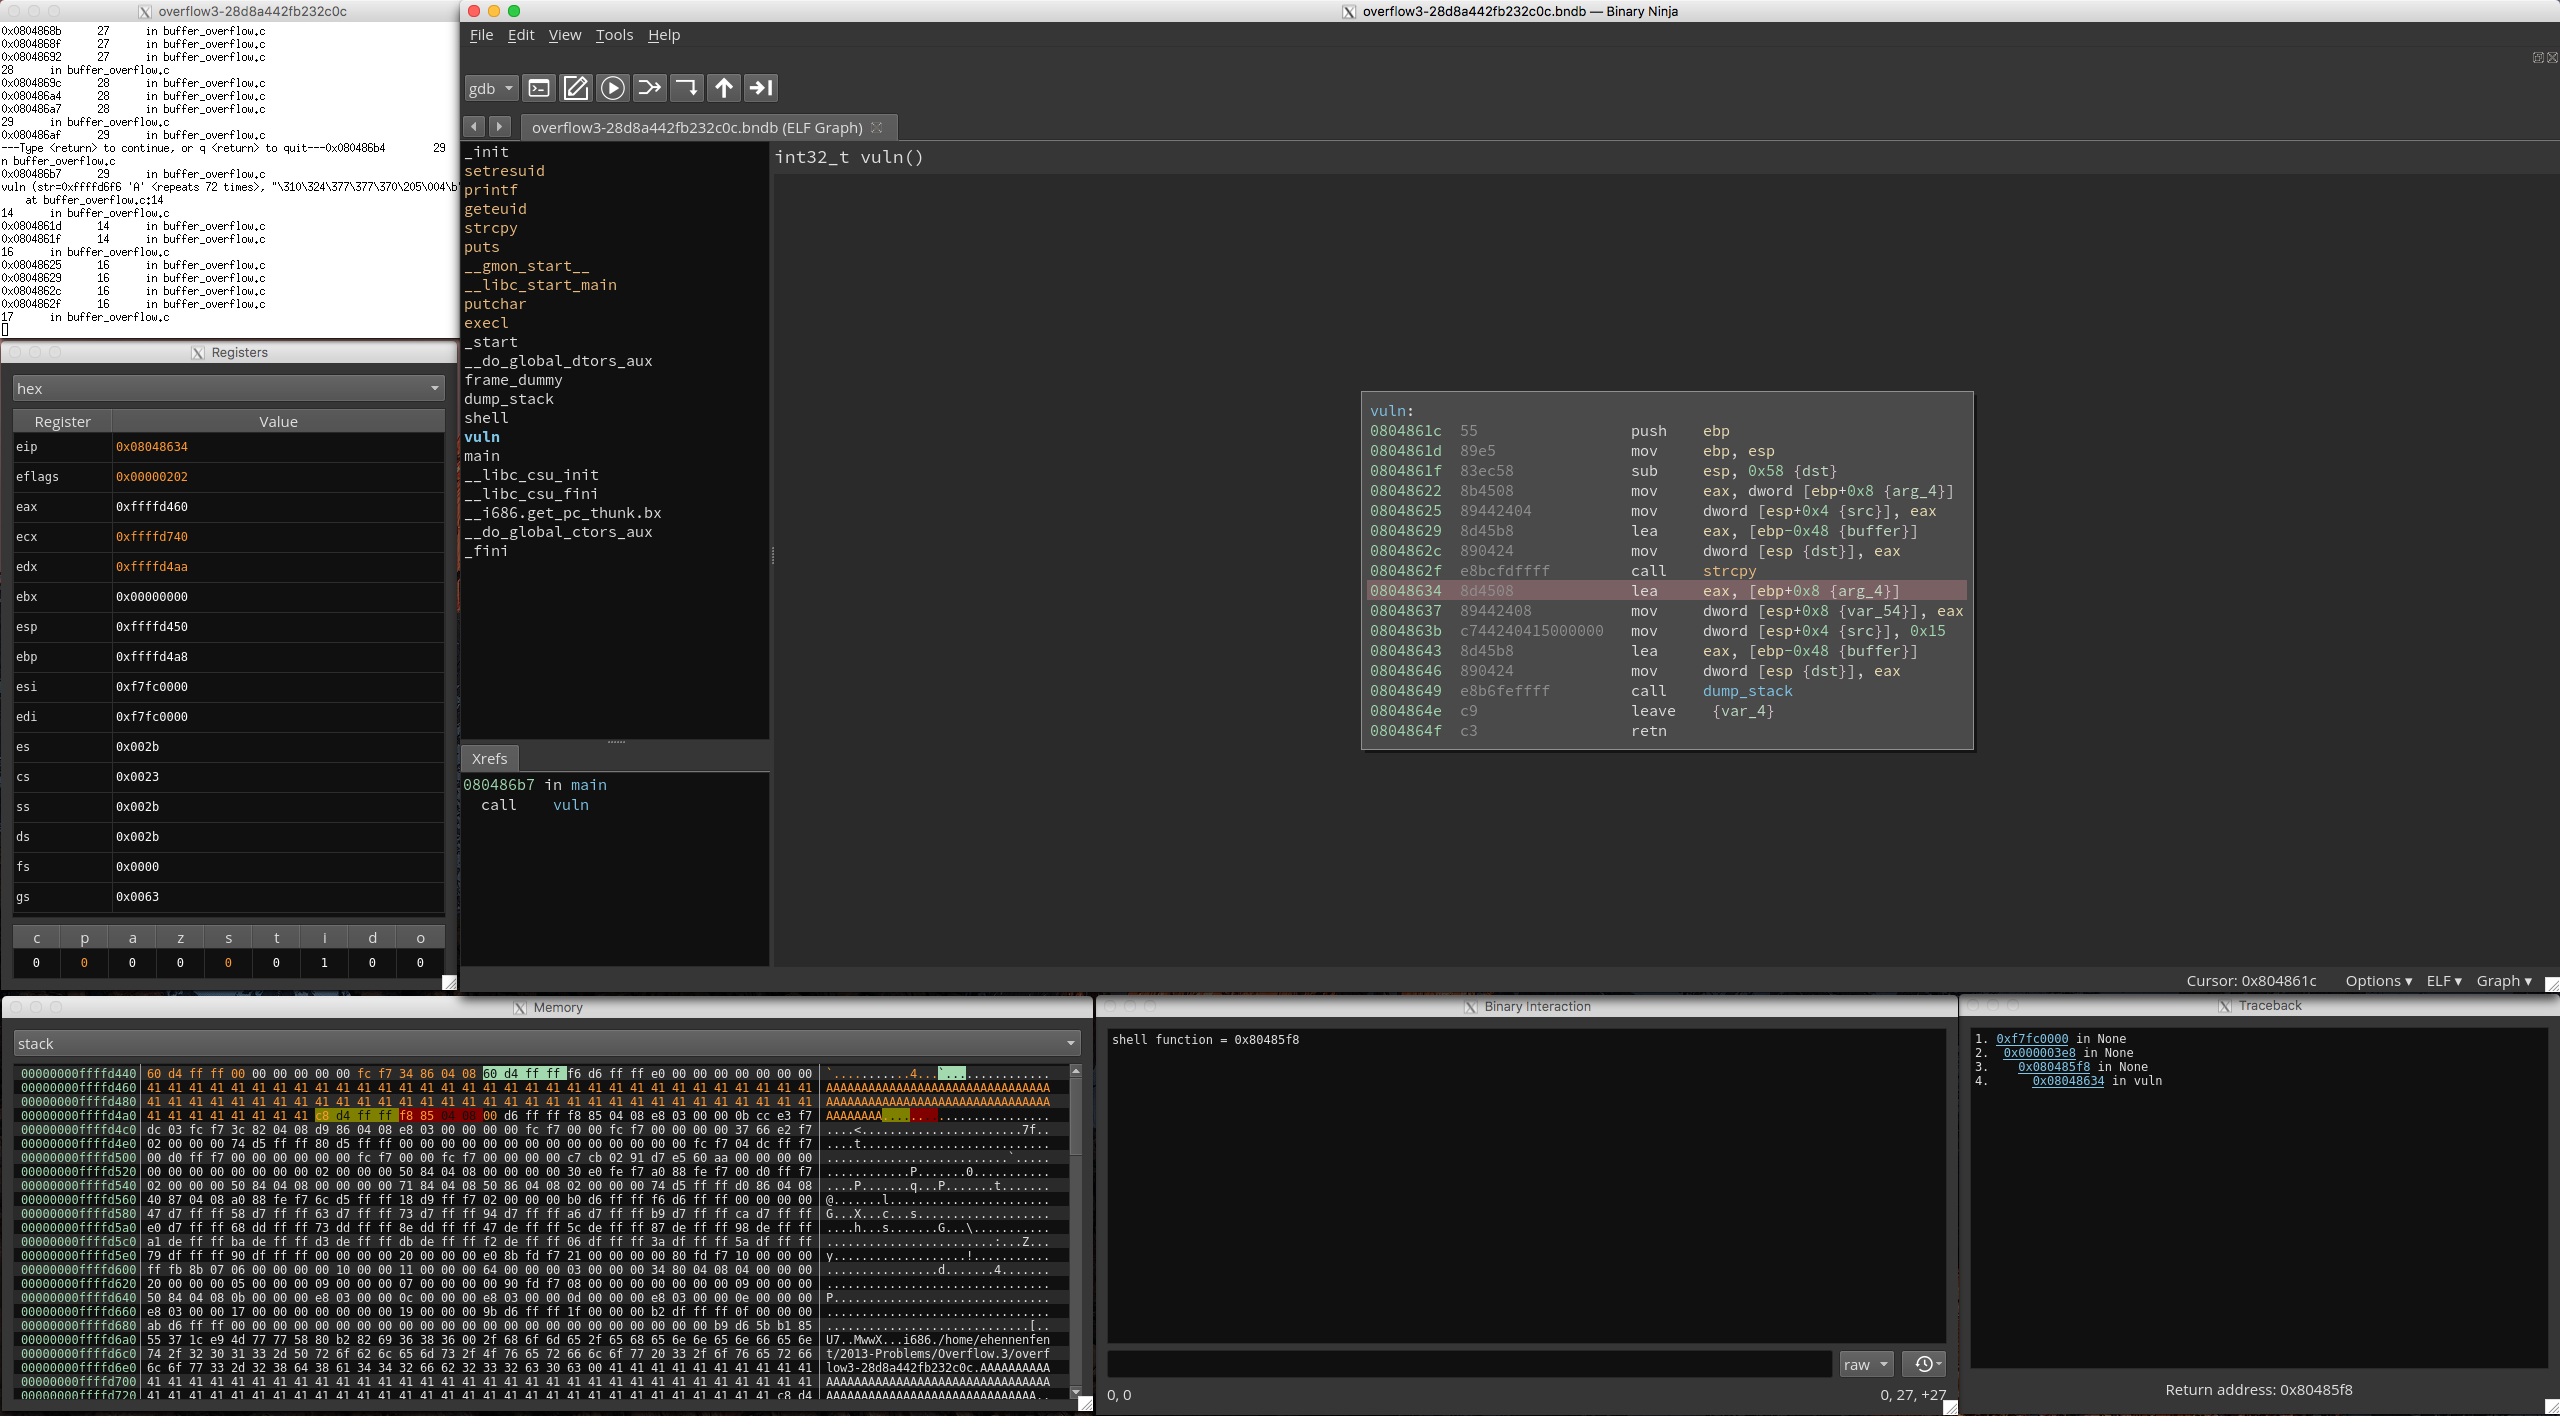 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
