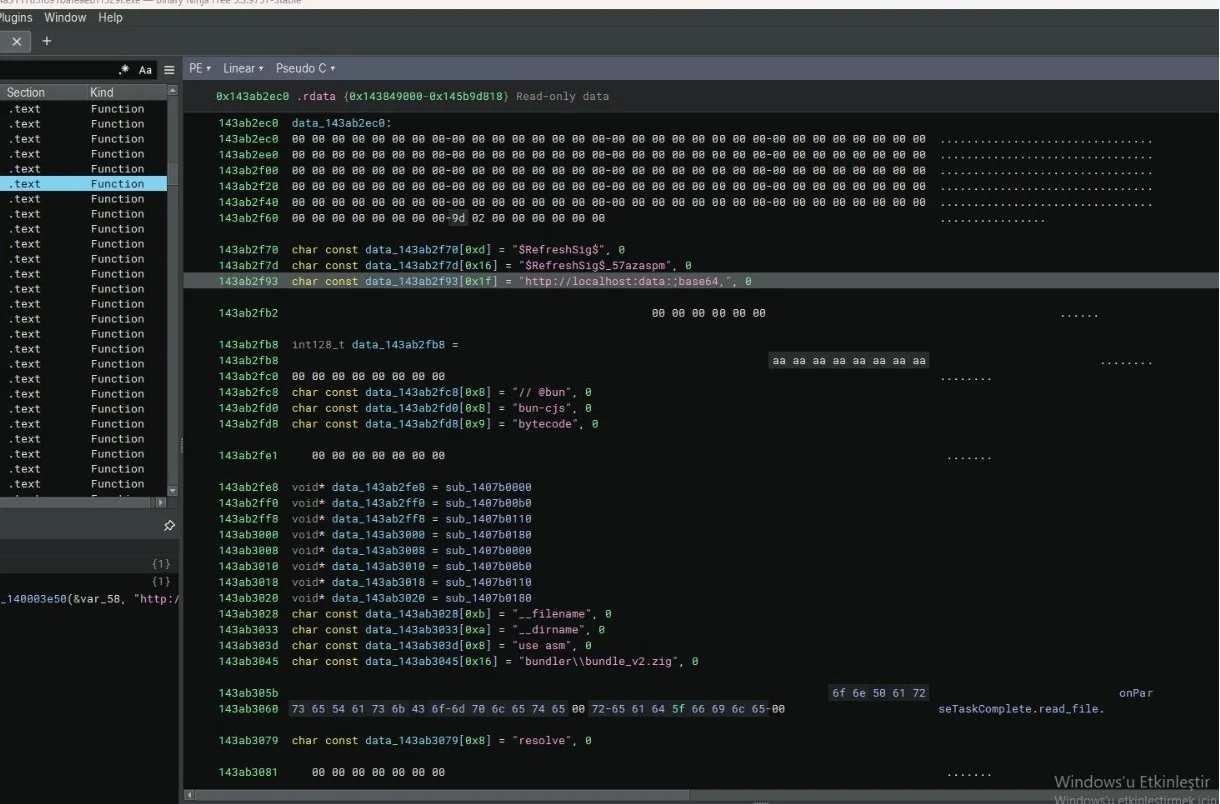
NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

A process monitoring tool that tries to detect exploitation

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

Reverse engineer anything with agents, from app behavior down to native binaries.

Neutralize KEPServerEX anti-debugging techniques

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

A helper script for unpacking and decompiling EXEs compiled from python code.

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…