
nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 apurvsinghgautam/dark-web-osint-tools
OSINT Tools for the Dark Web
 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 j3ers3/searpy
🥀 Search Engine Tookit,URL采集、Favicon哈希值查找真实IP、子域名查找
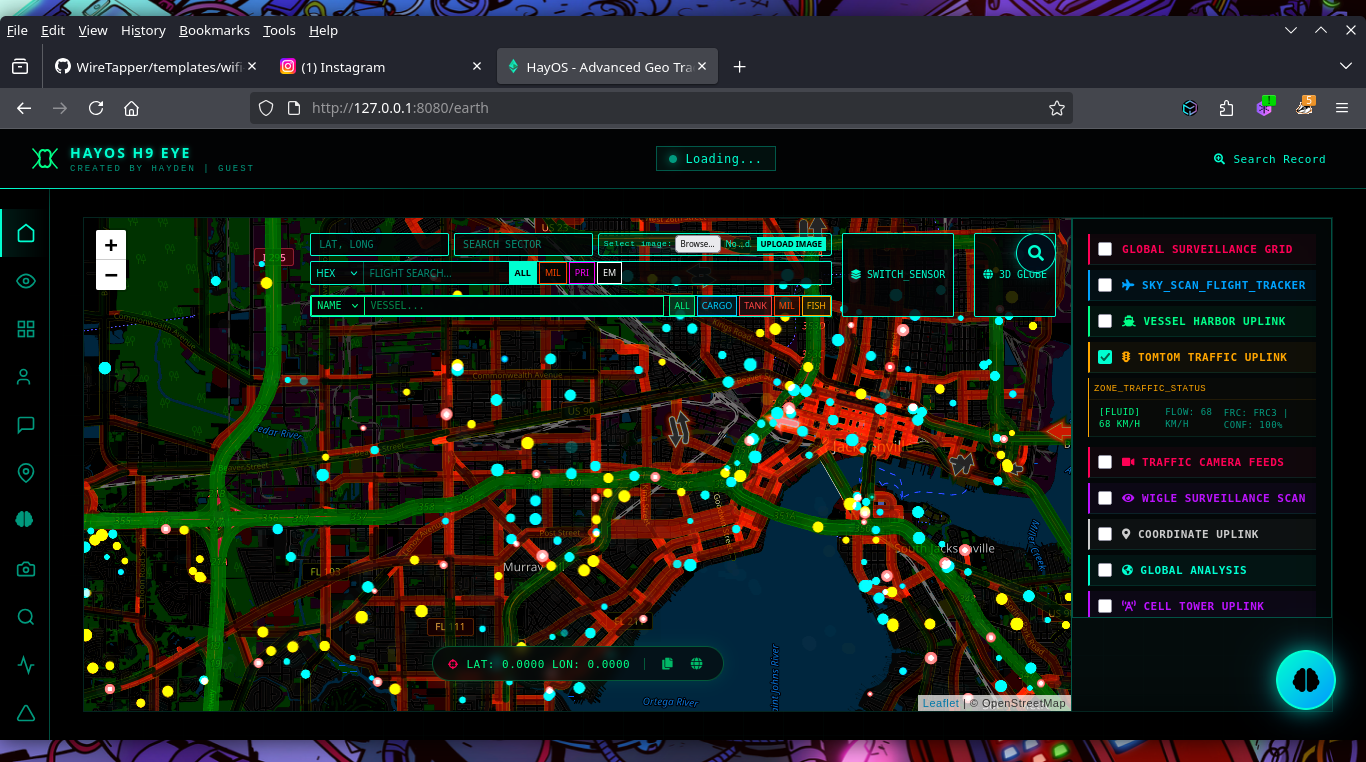 h9zdev/geosentinel
Real-time geospatial OSINT platform aggregating flight, vessel, and satellite data with dark web search, social media dorking, and AI-powered…
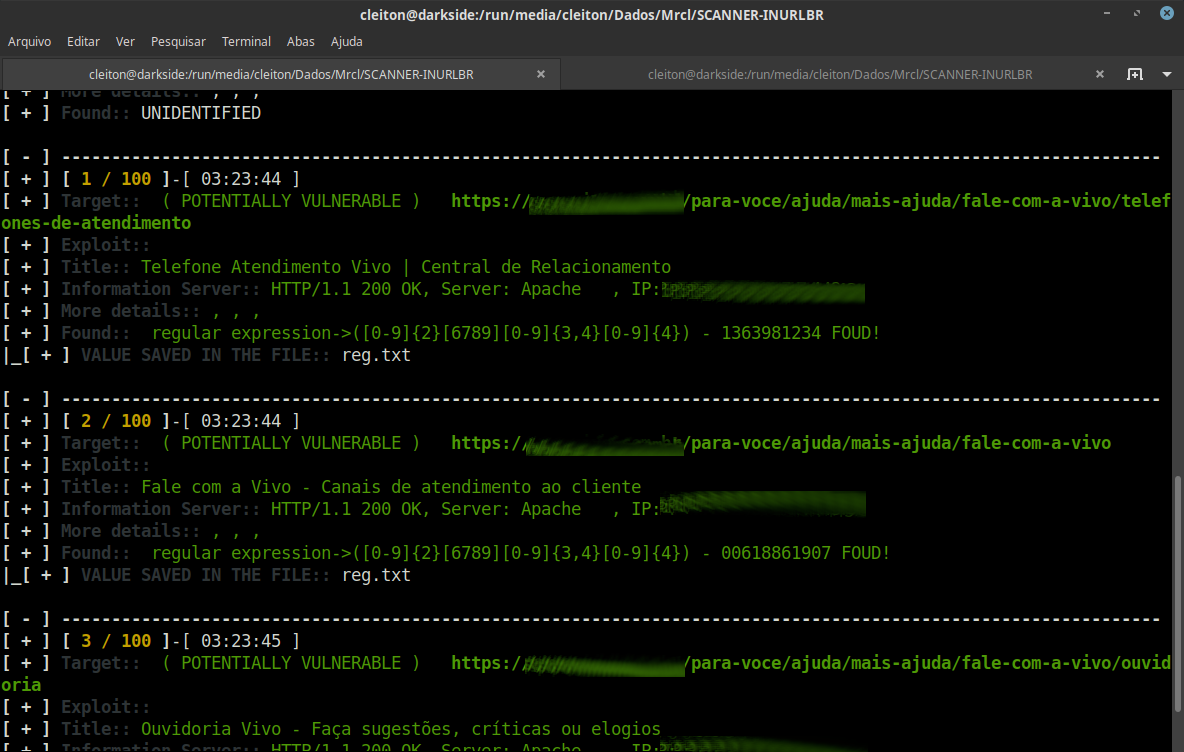 mrcl0wnlab/scanner-inurlbr
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
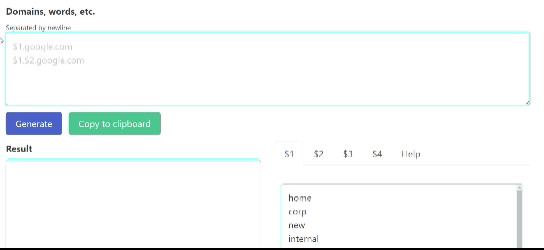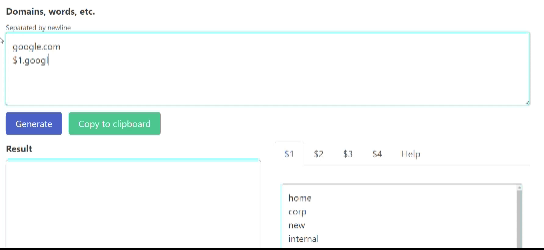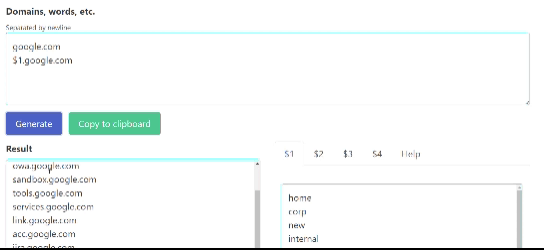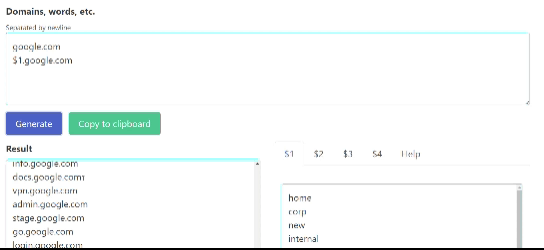 zzzteph/probable_subdomains
Subdomains analysis and generation tool. Reveal the hidden!
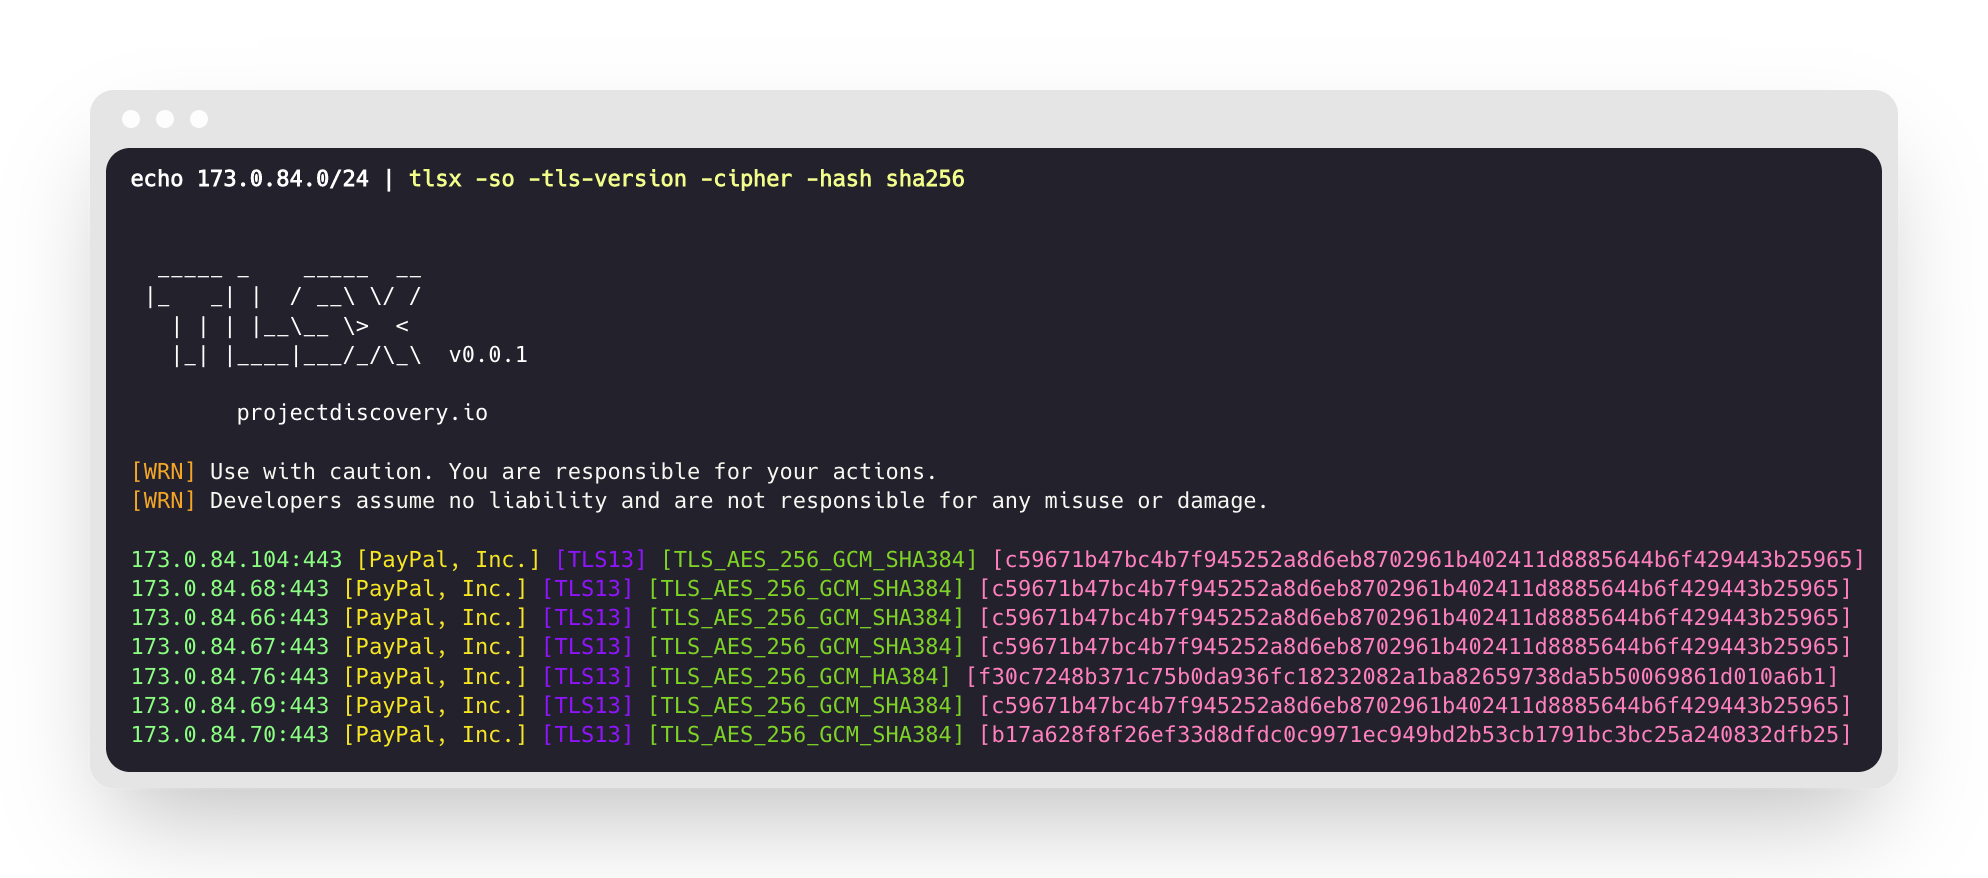 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
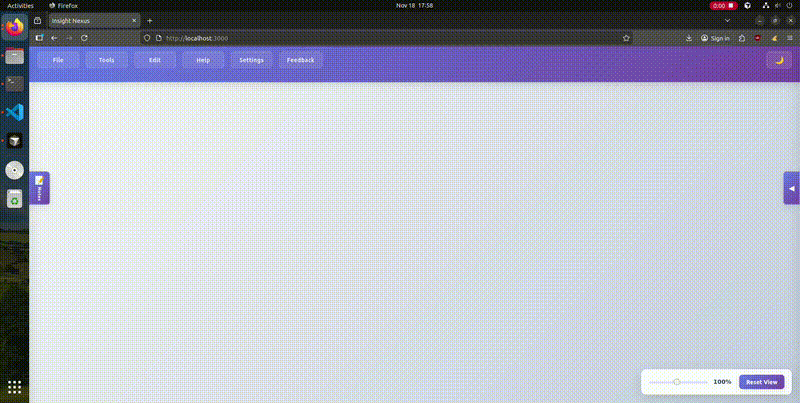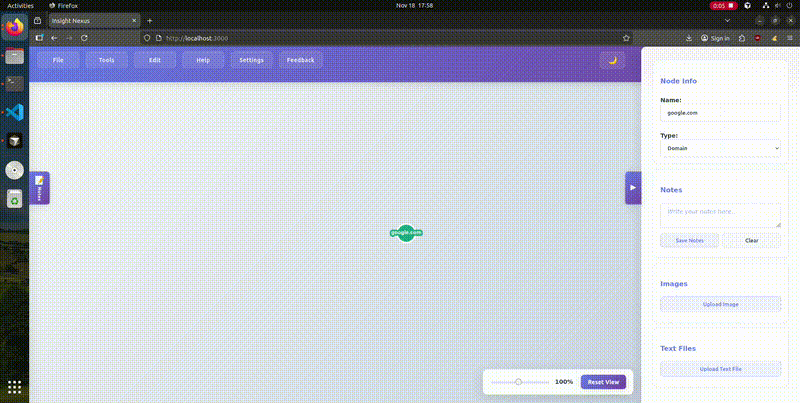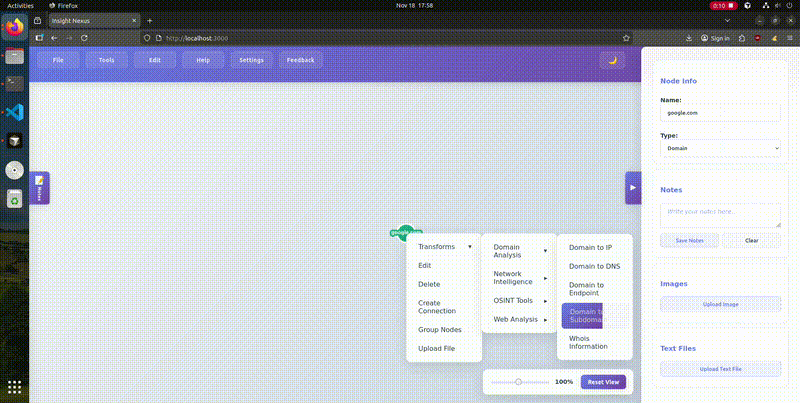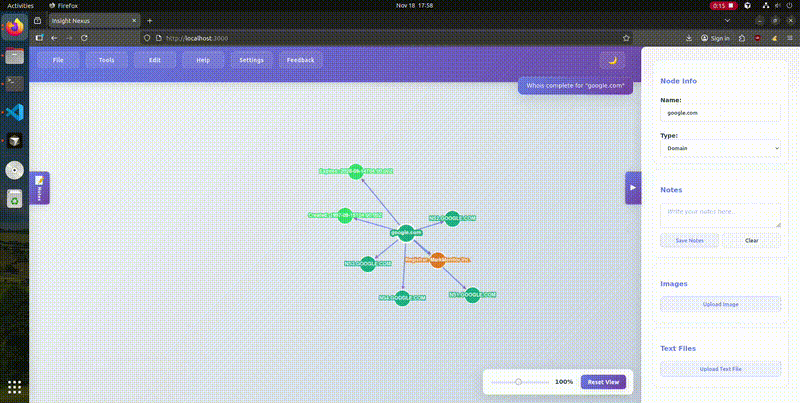 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application
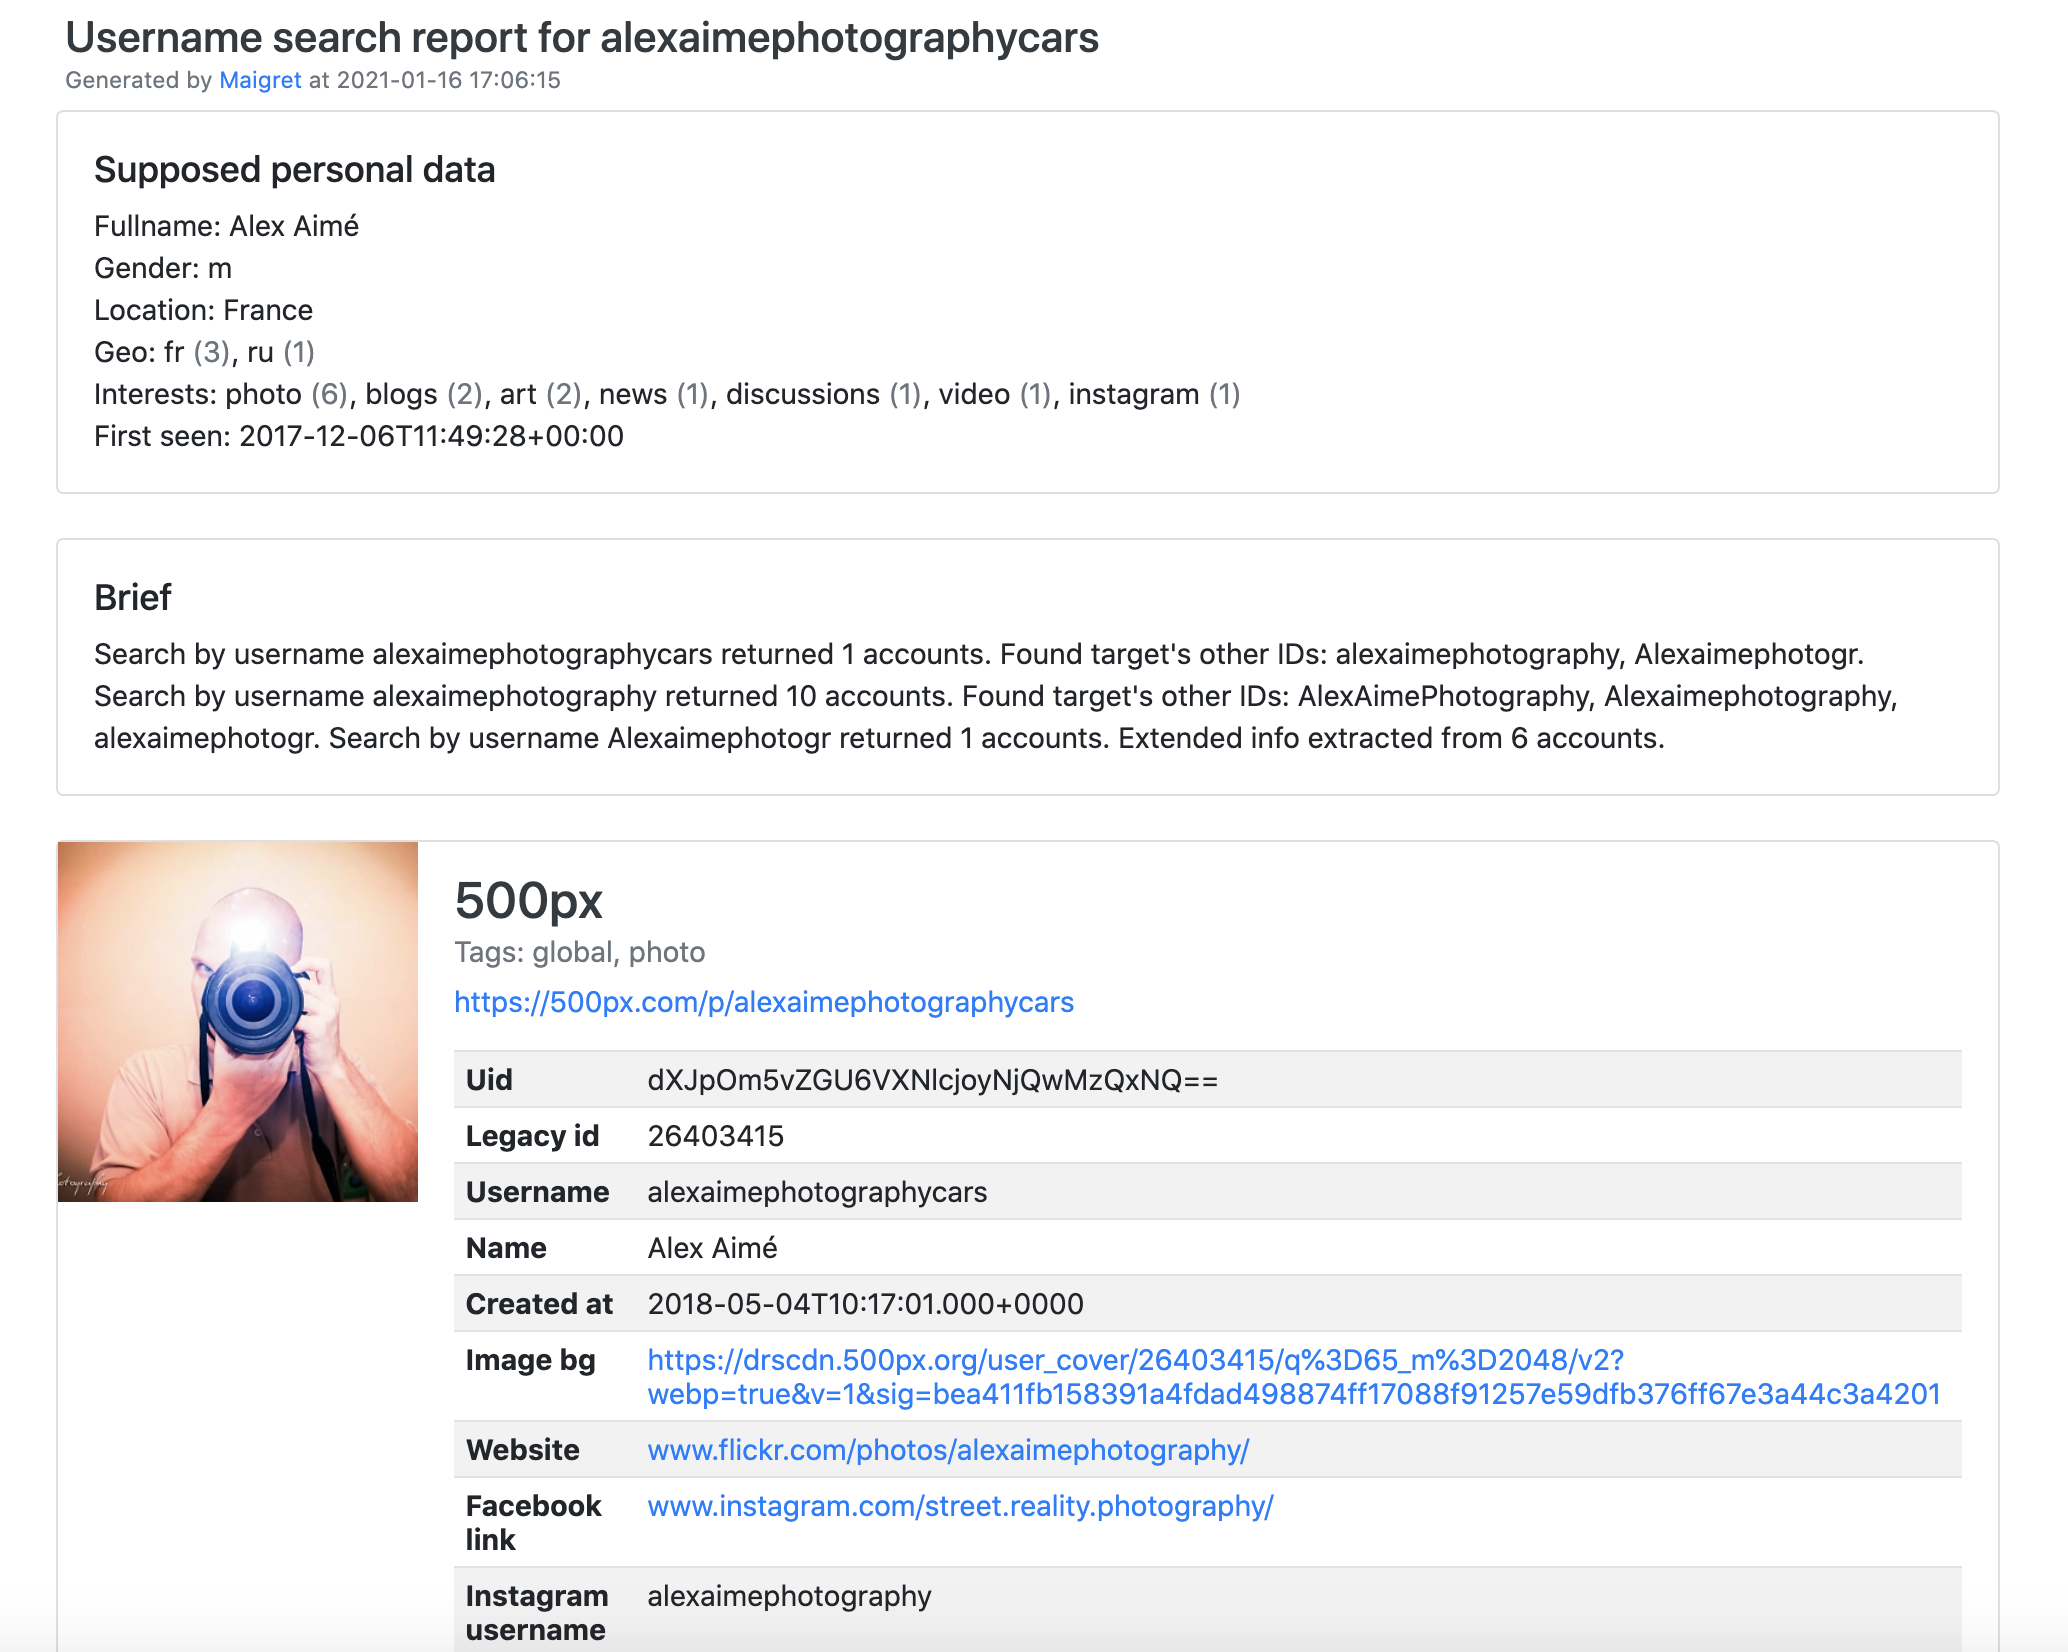 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
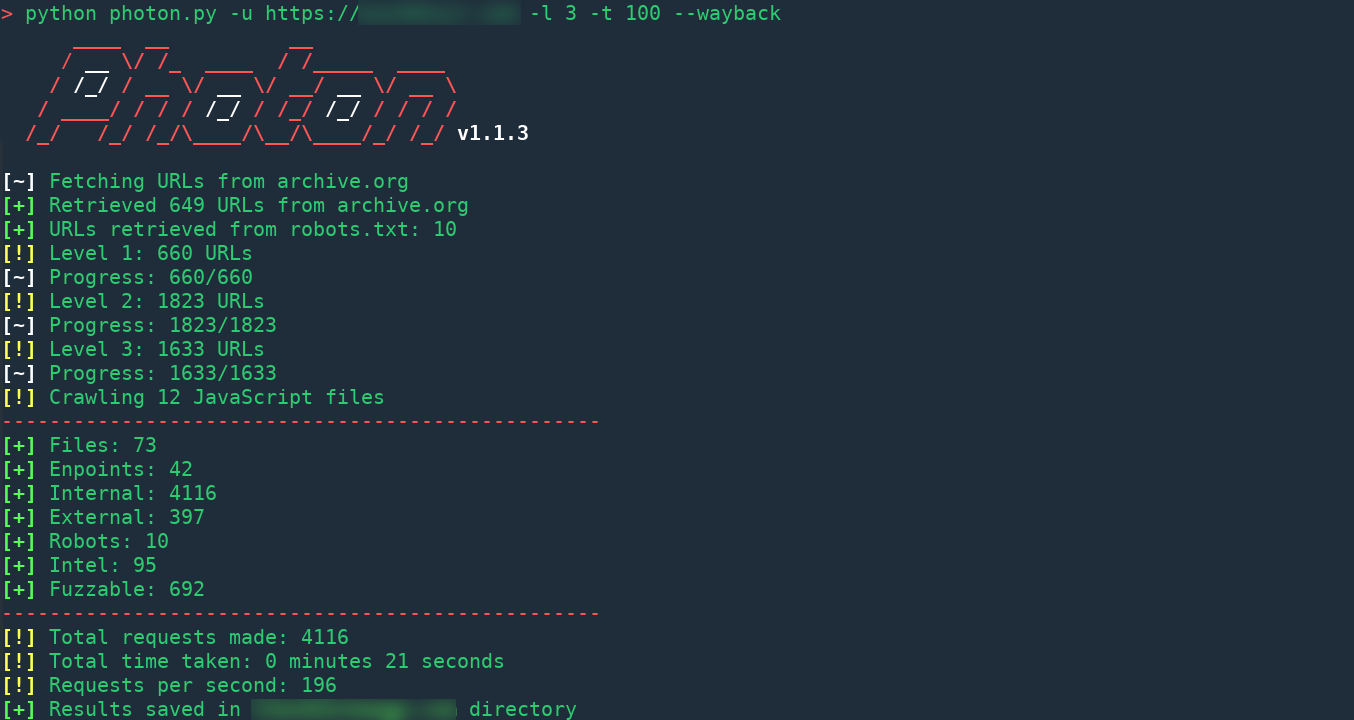 s0md3v/photon
Incredibly fast crawler designed for OSINT.
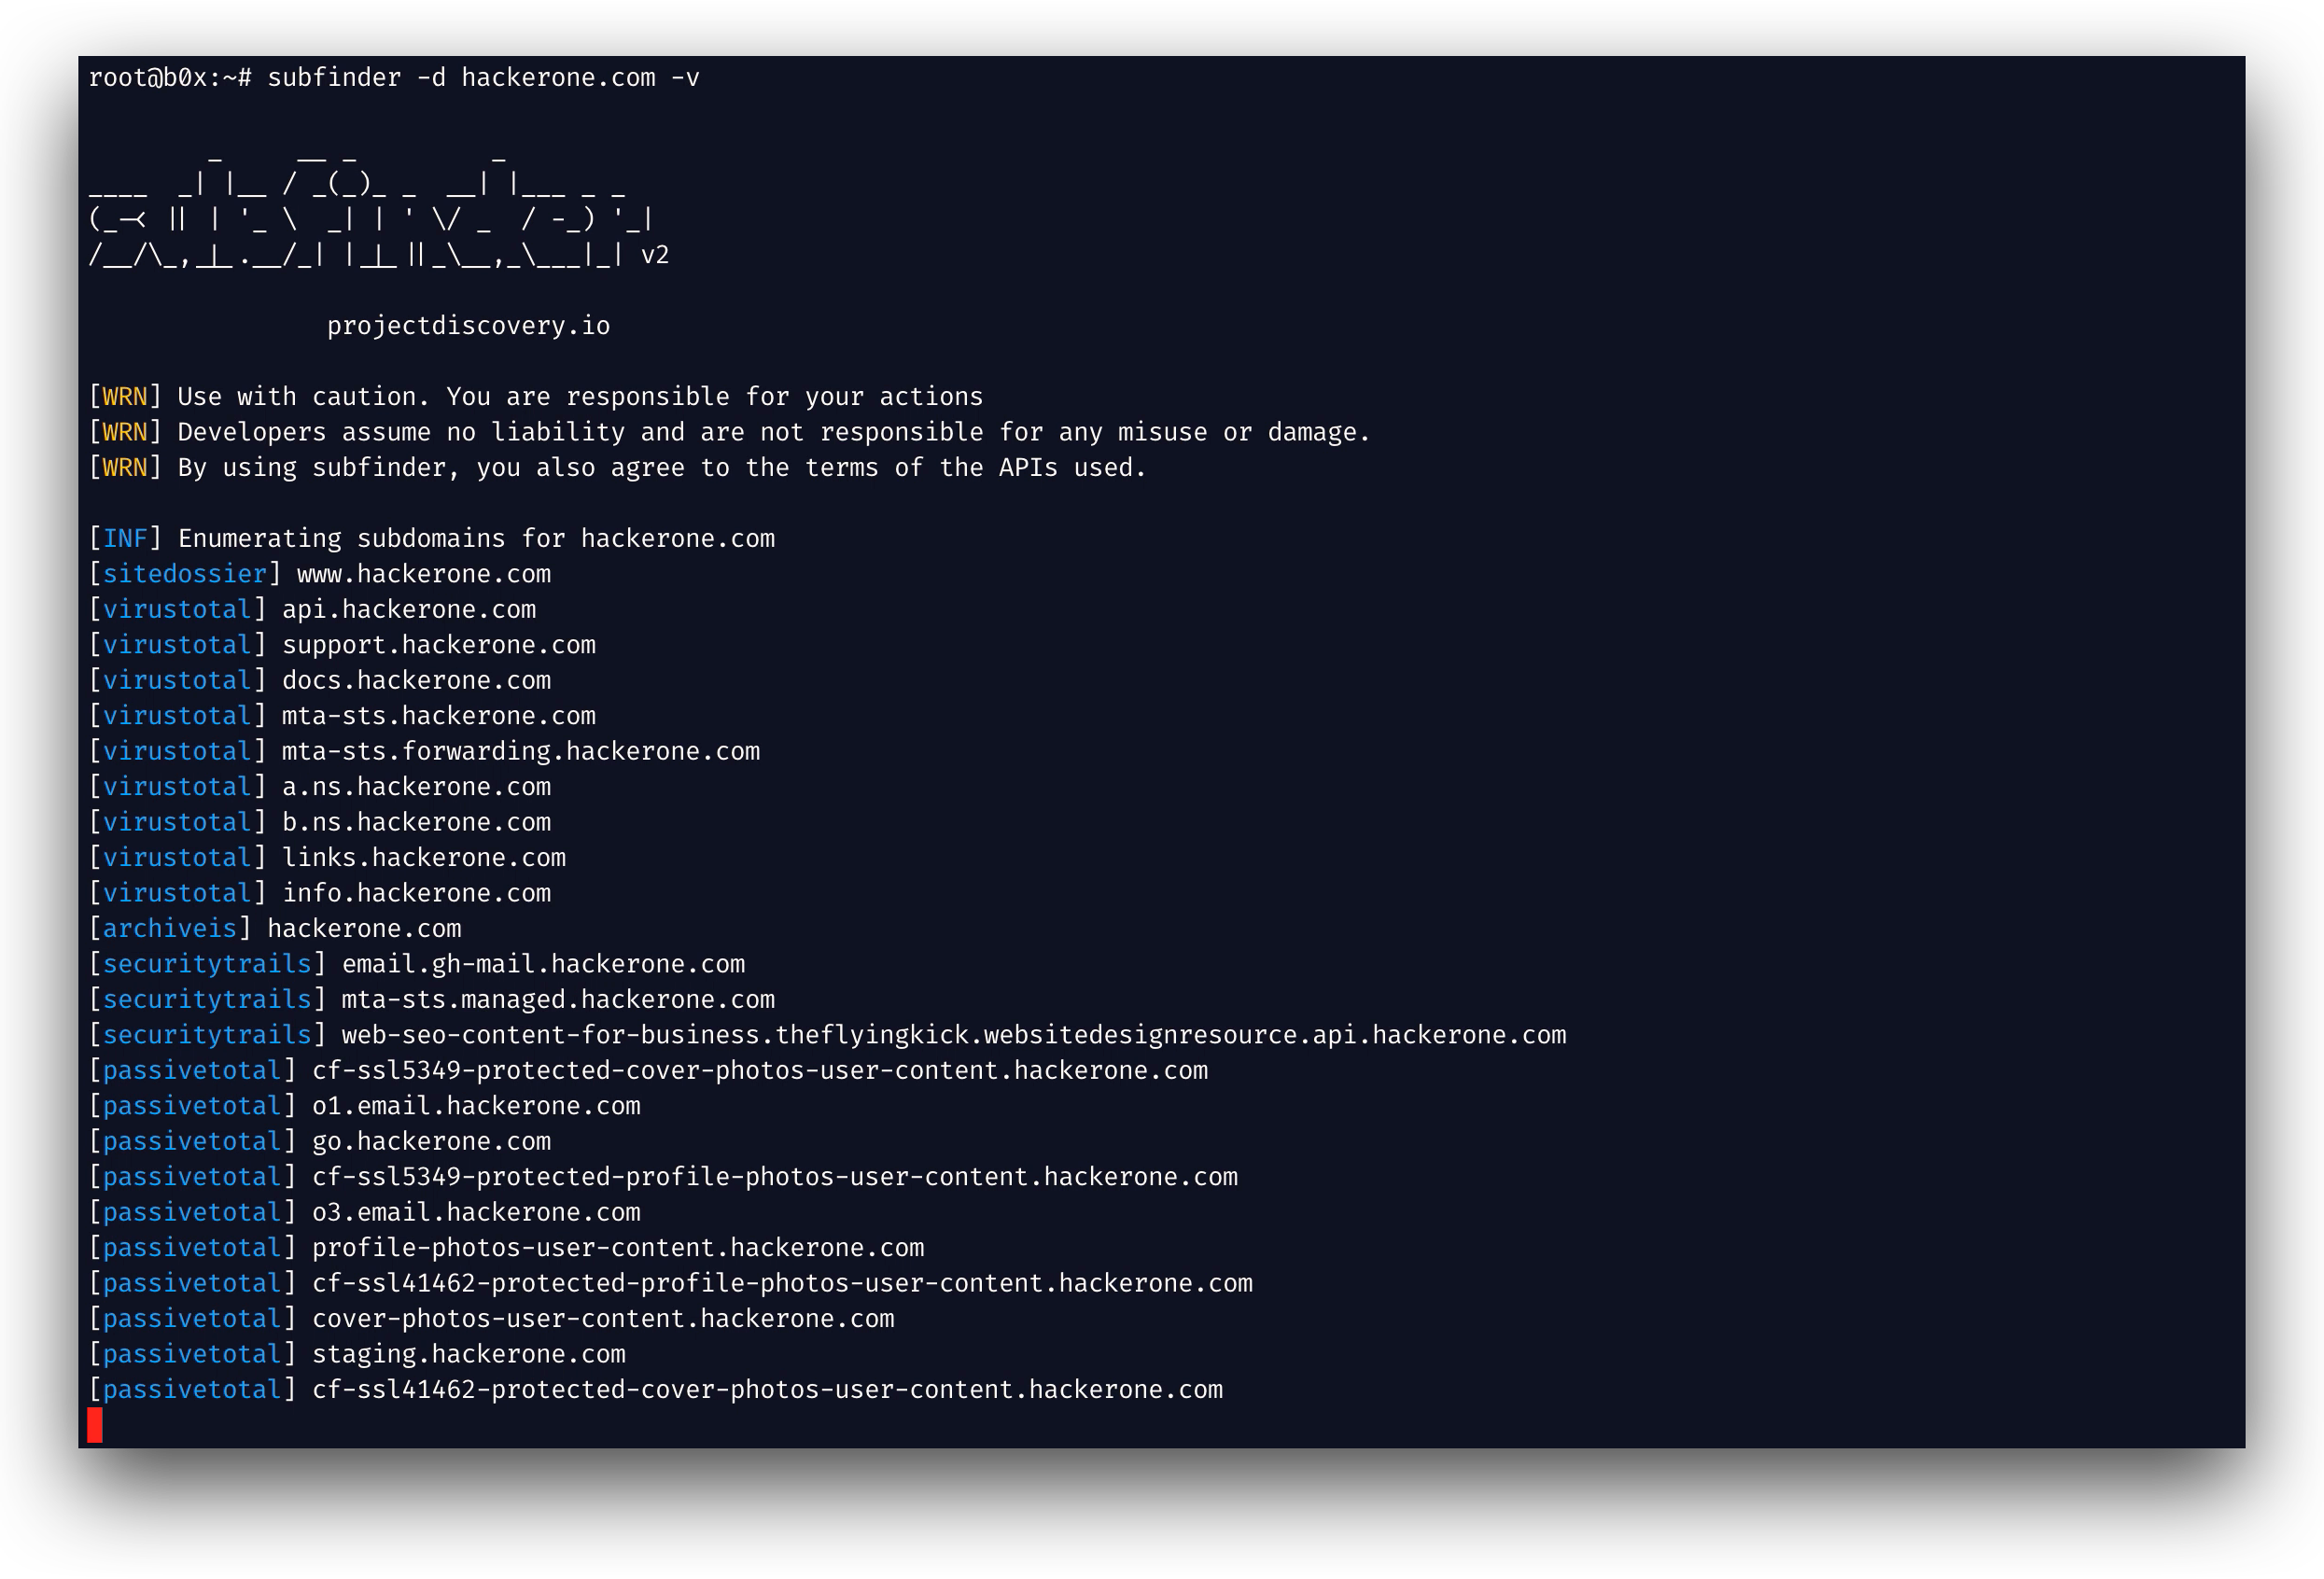 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
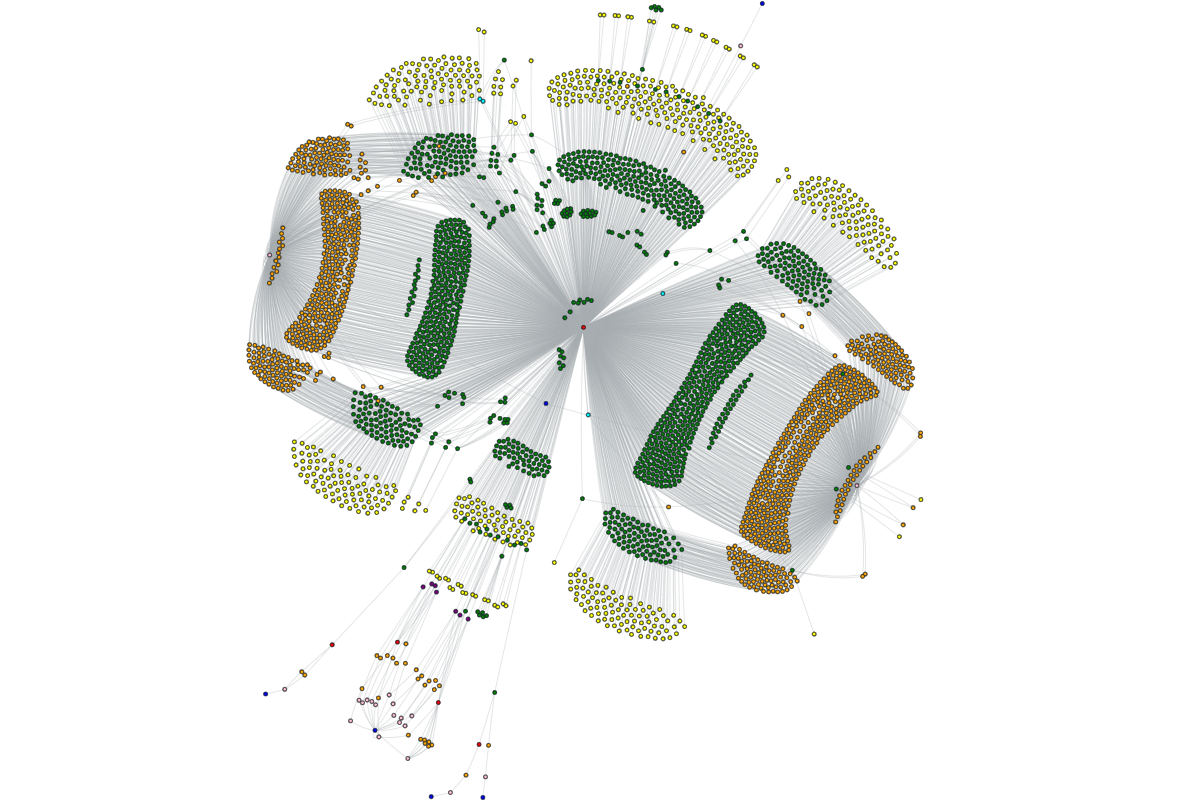 owasp-amass/amass
In-depth attack surface mapping and asset discovery
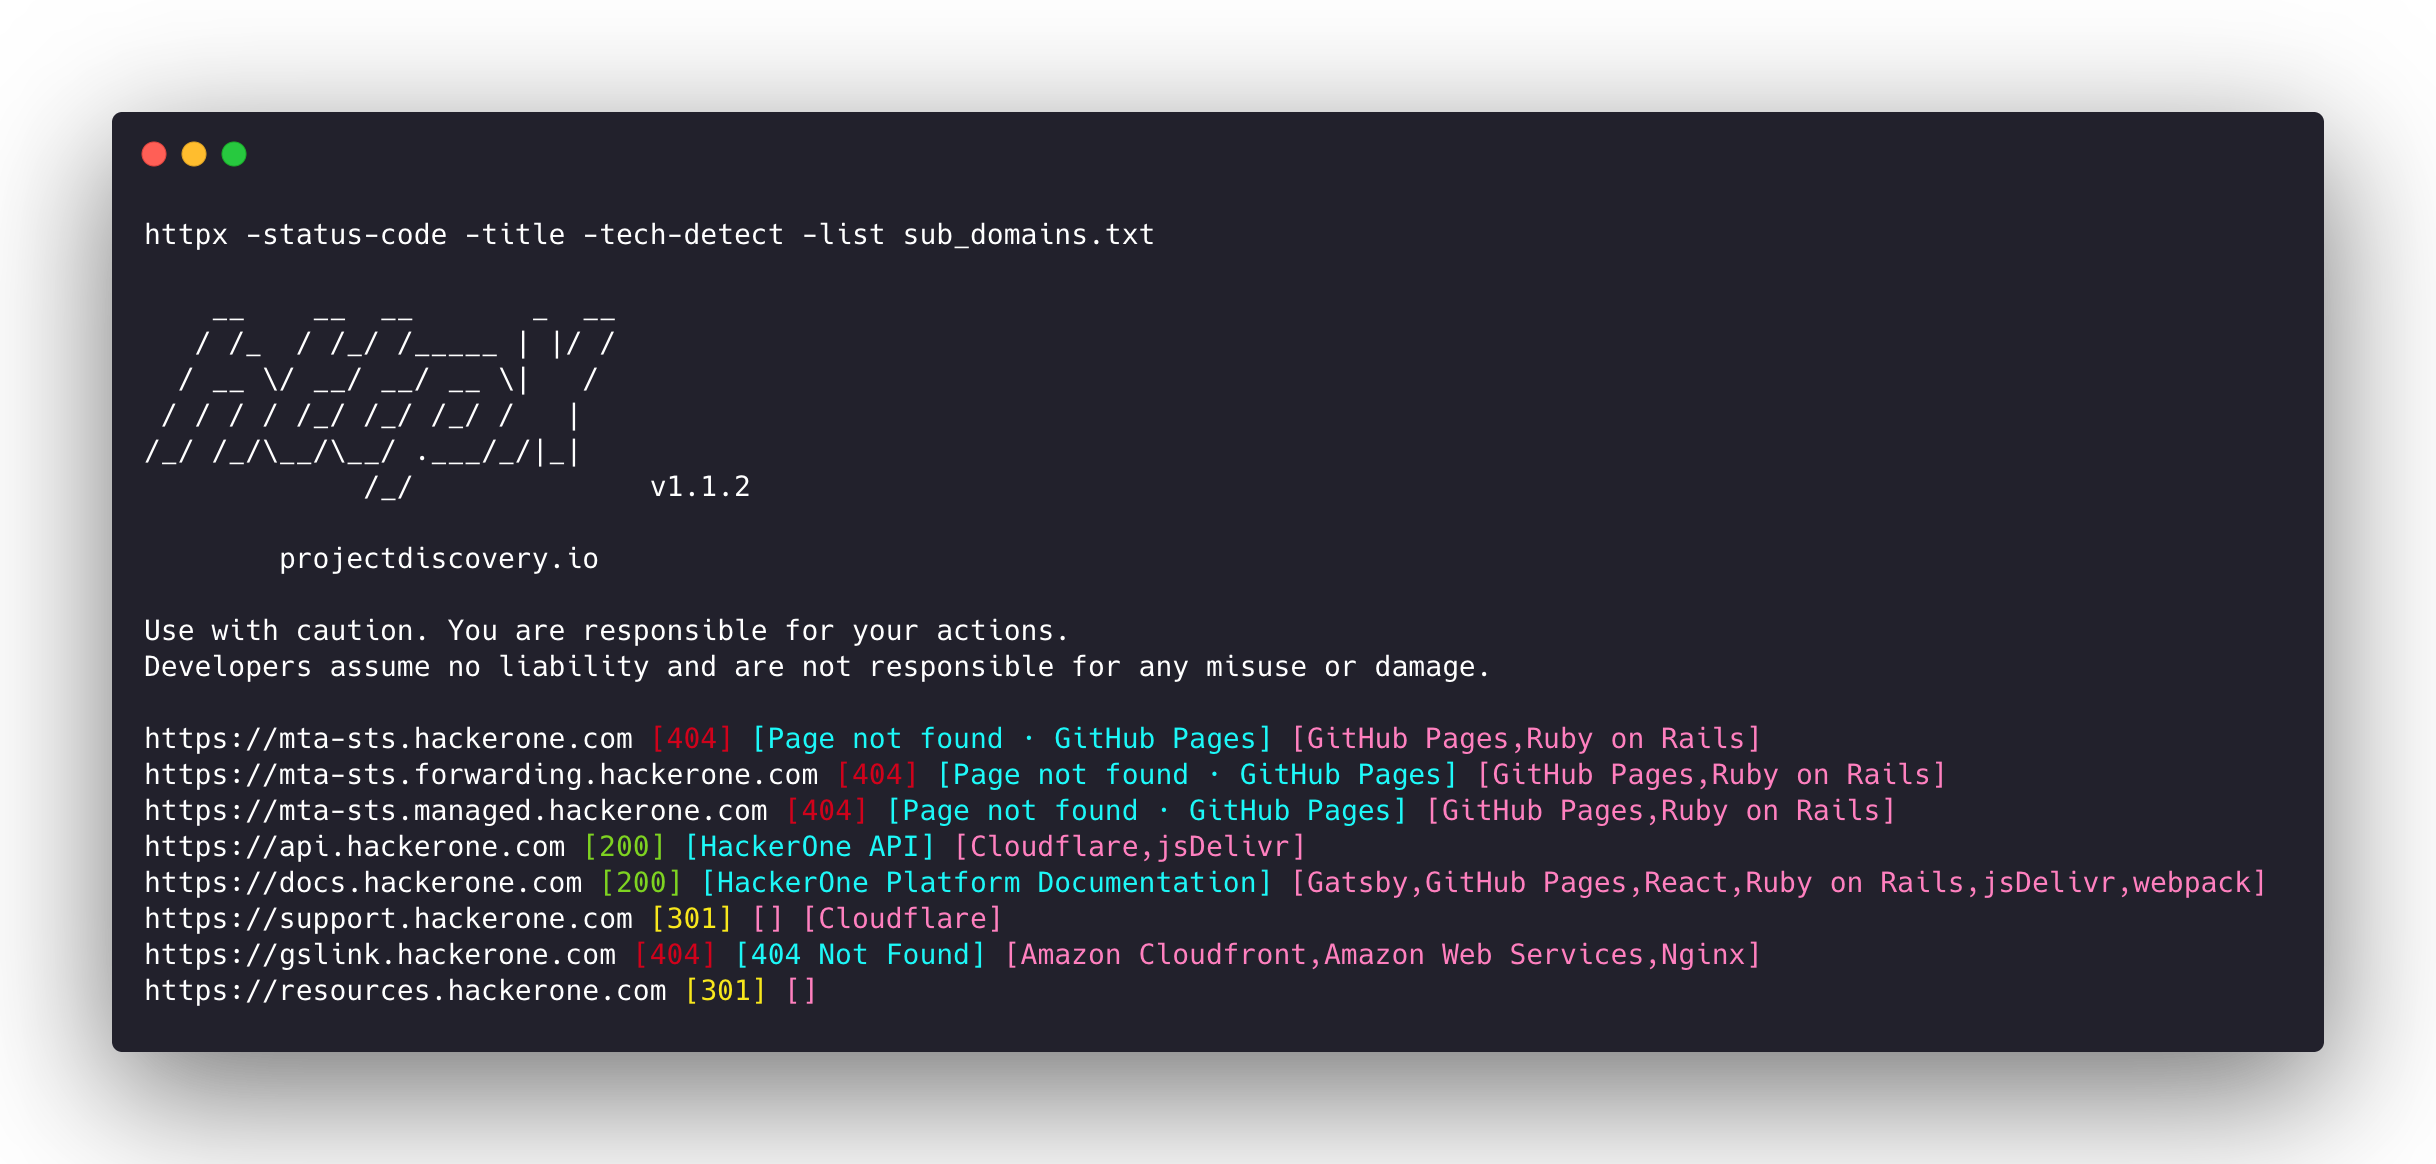 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…