
rengine
 yogeshojha/rengine
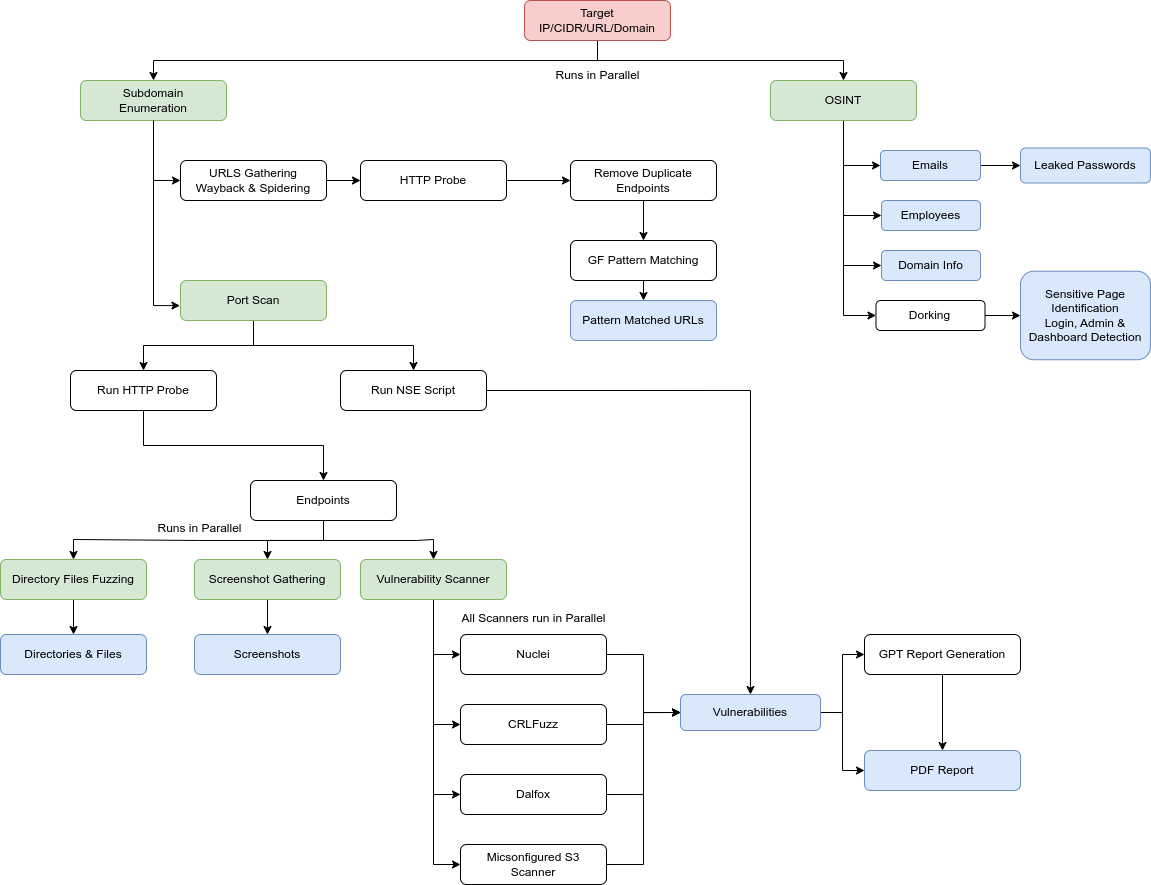
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
crawlerdns-subdomain-enumerationinformation-gathering+9
8.9k
yogeshojha/renginereNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 mhaskar/exchangefinder
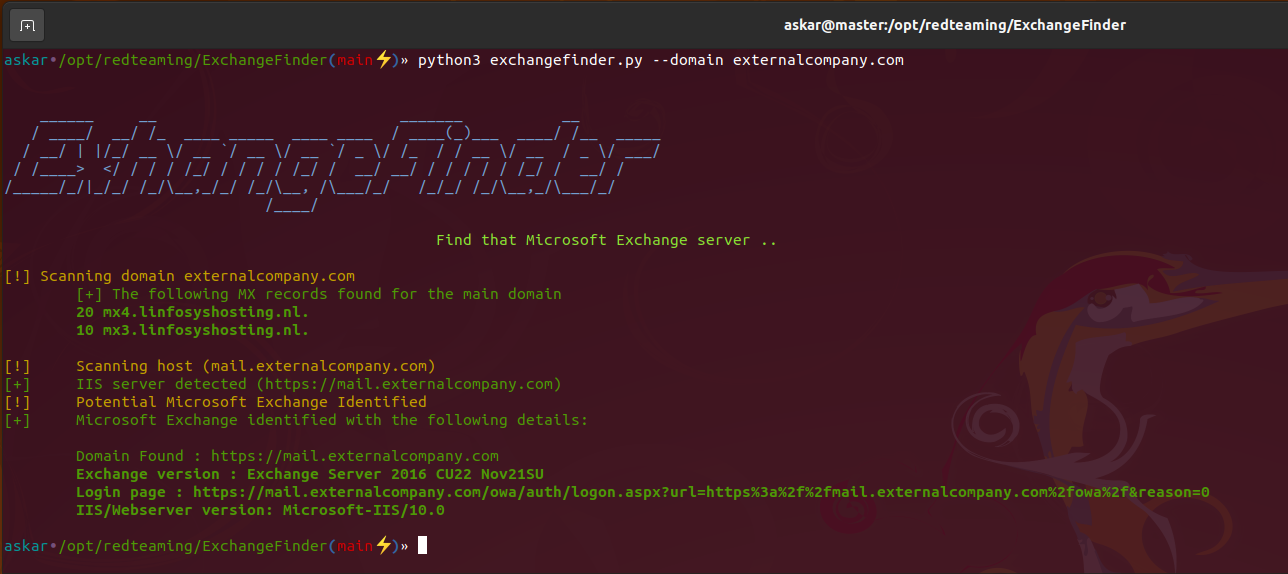
Find Microsoft Exchange instance for a given domain and identify the exact version
 clouedoc/autosqli
An automatic SQL Injection tool which takes advantage of ~DorkNet~ Googler, Ddgr, WhatWaf and sqlmap.
 nullt3r/rapiddns
Rapidly enumerate subdomains and domains using rapiddns.io.
 trimstray/htrace.sh
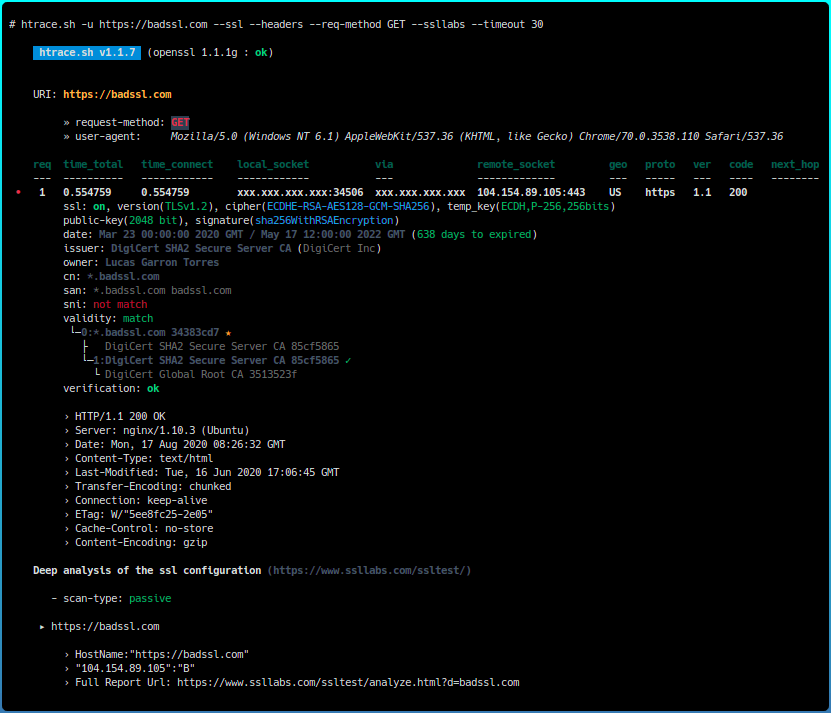
My simple Swiss Army knife for http/https troubleshooting and profiling.
 blechschmidt/massdns
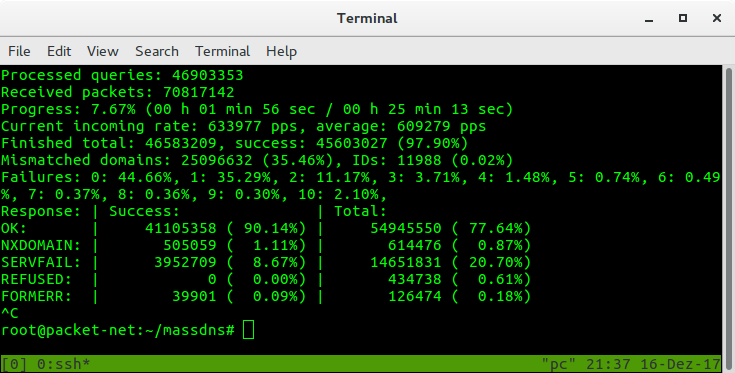
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
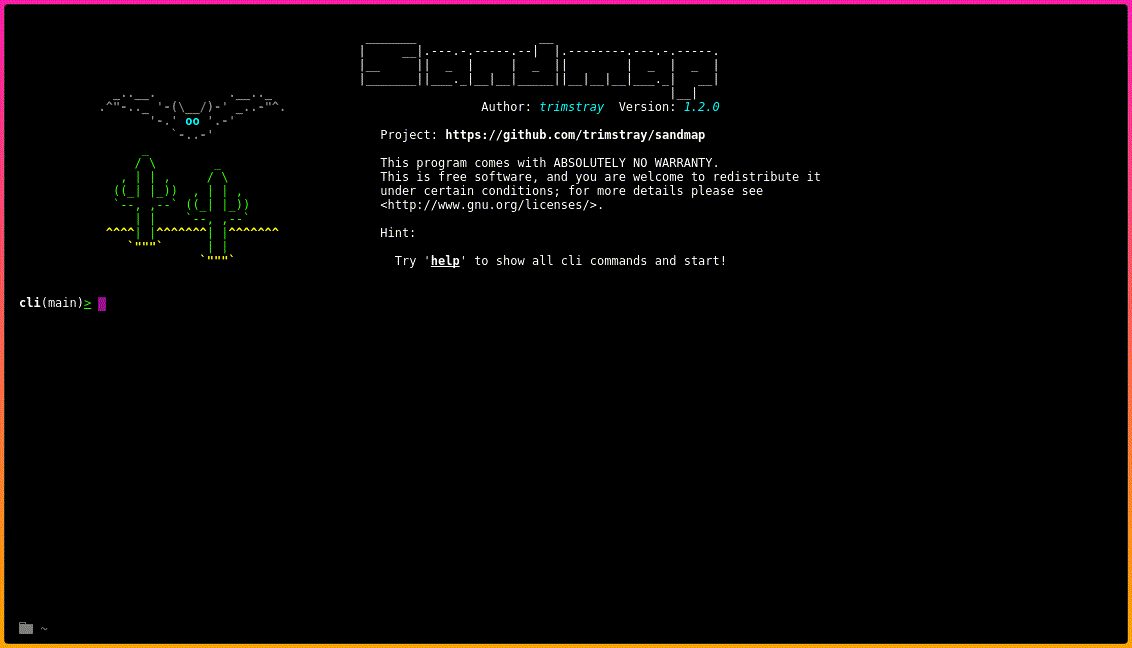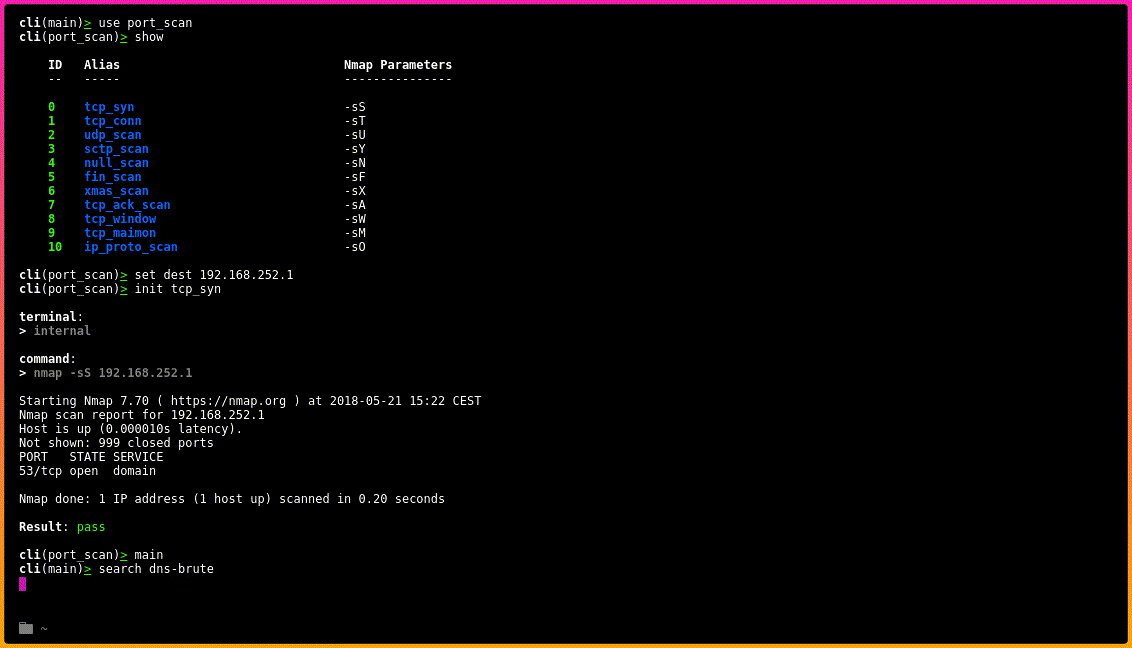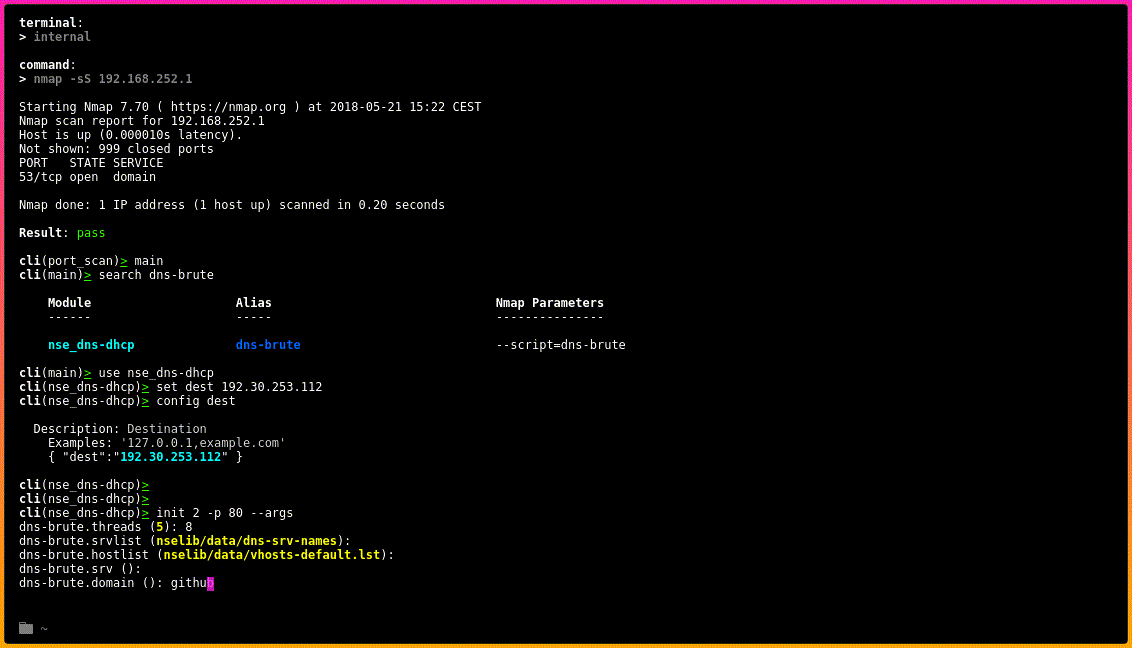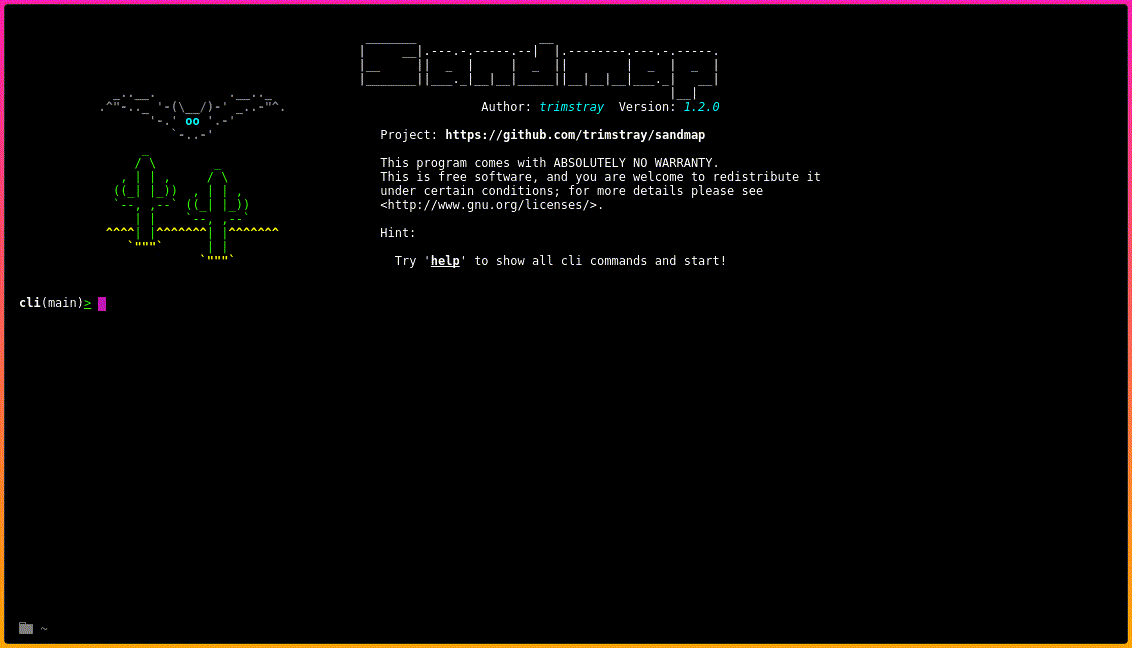 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
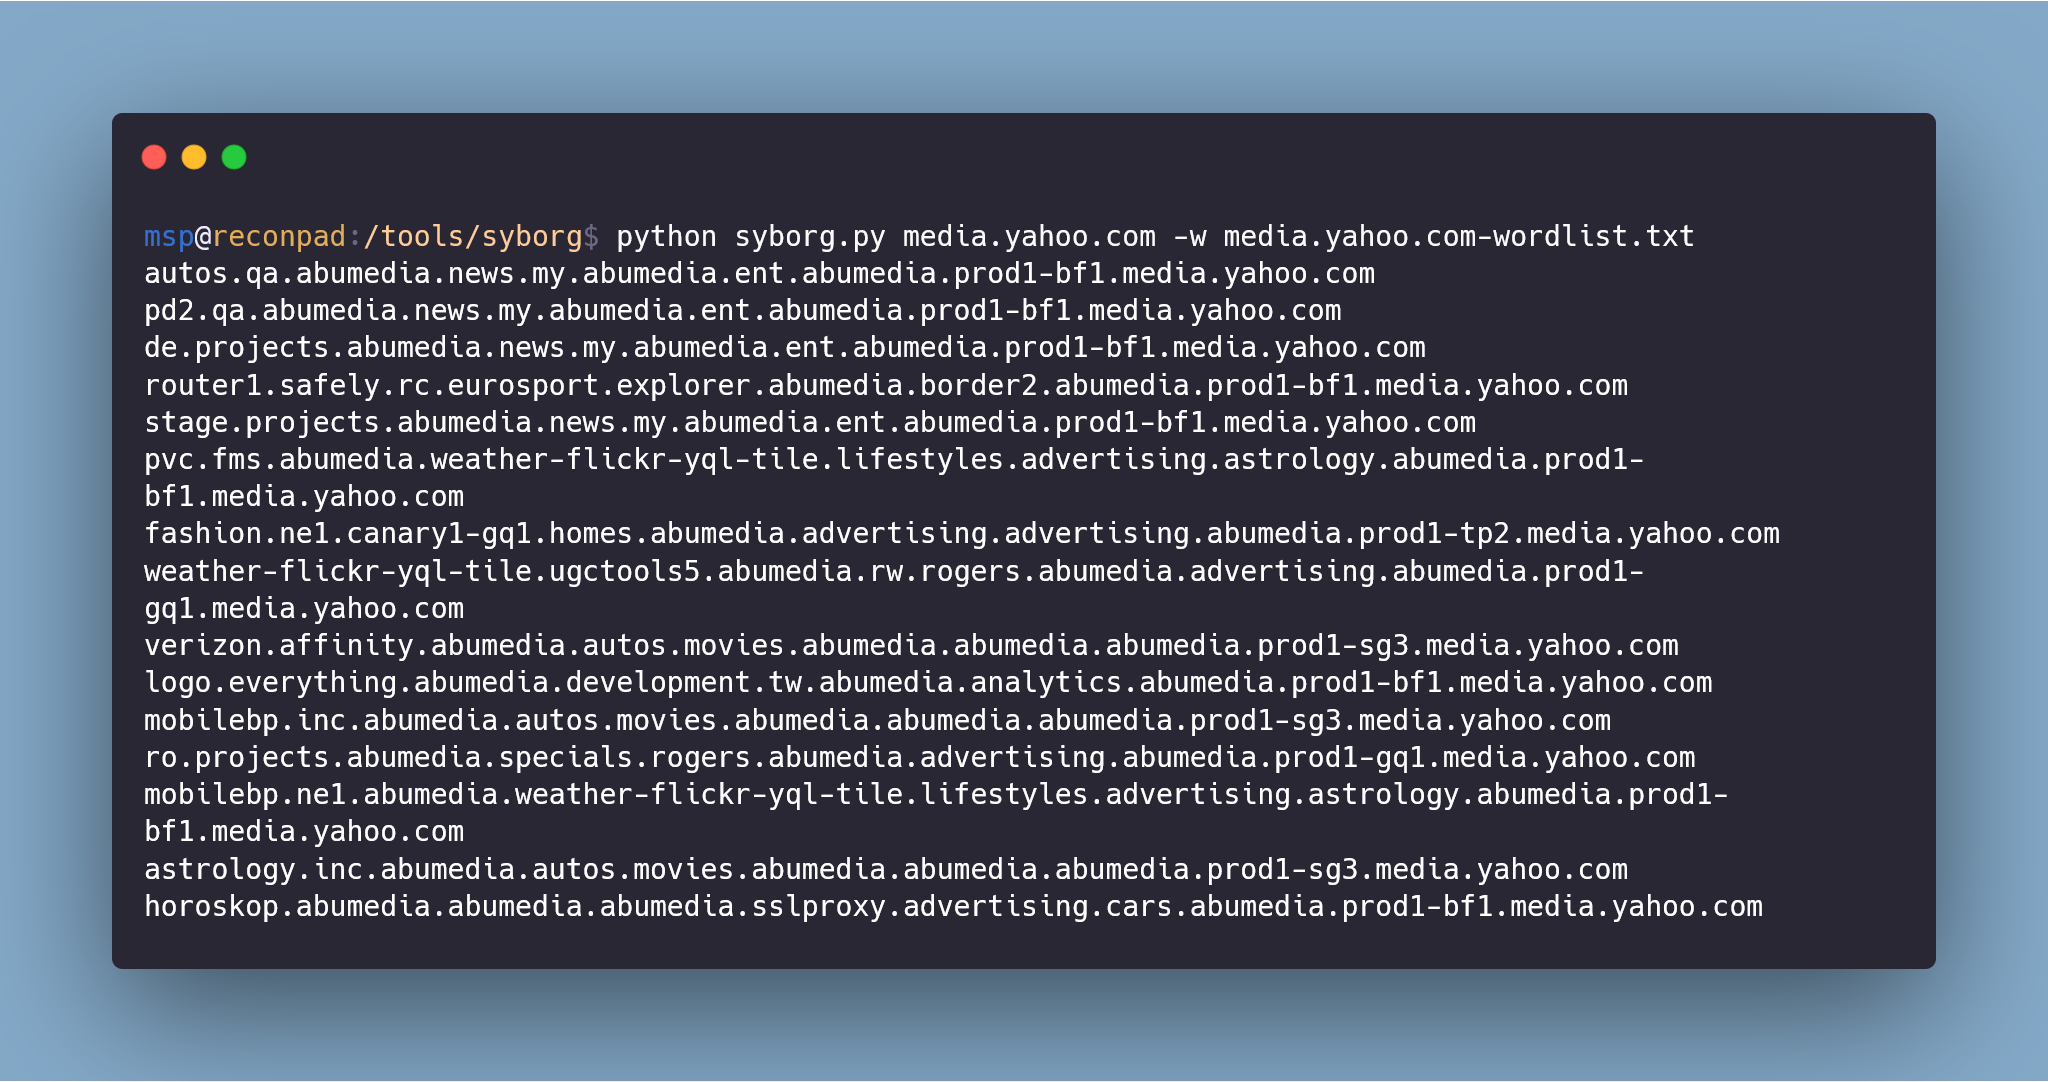 milindpurswani/syborg
Recursive DNS Subdomain Enumerator with dead-end avoidance system (BETA)
 pry0cc/subgen
A really simple utility to concate wordlists to a domain name - to pipe into your favourite resolver!
 hakluke/hakrevdns
Small, fast tool for performing reverse DNS lookups en masse.
 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
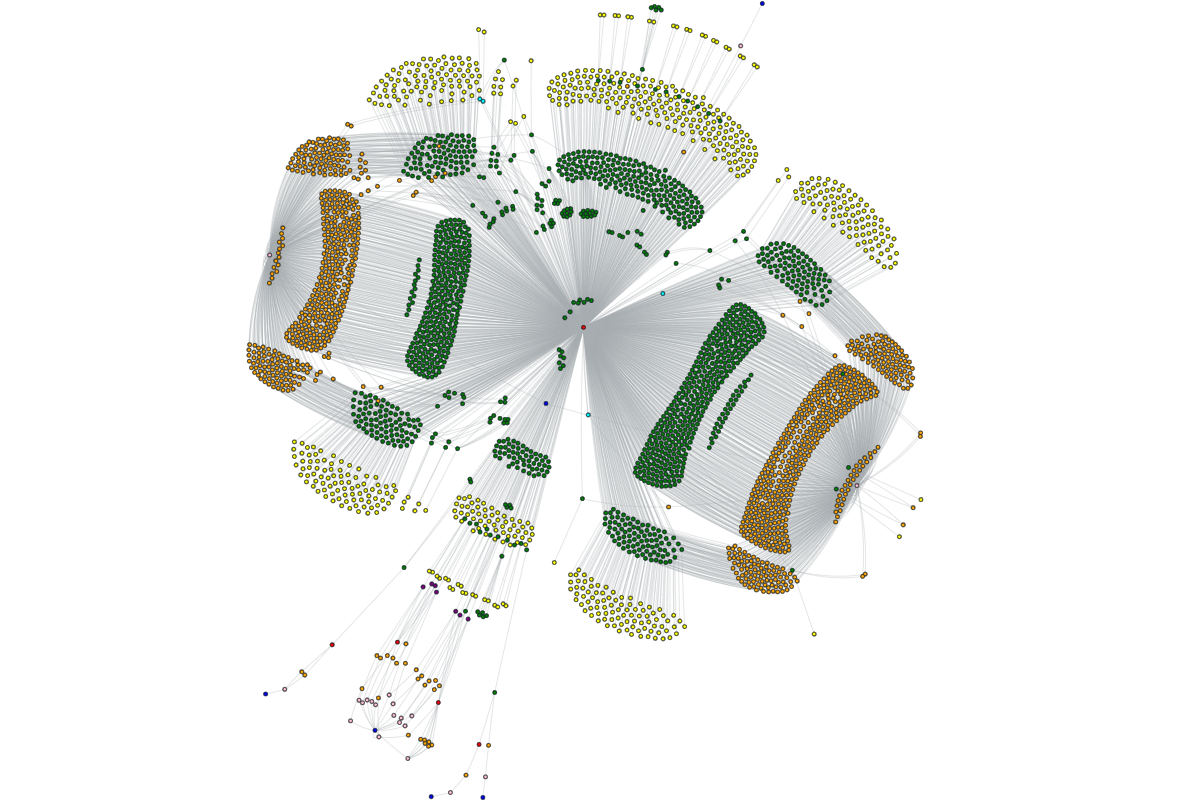 owasp-amass/amass
In-depth attack surface mapping and asset discovery