
Bluto-Old
 darryllane/bluto-old
Recon, Subdomain Bruting, Zone Transfers
dns-analysisdns-subdomain-enumerationemail-harvesting+4
darryllane/bluto-oldRecon, Subdomain Bruting, Zone Transfers
 penafieljlm/inquisitor
Opinionated organisation-centric OSINT footprinting inspired from recon-ng and Maltego
 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
 fricciolosa-red-team/evildork
Automated Google dorking tool for extracting leaked secrets, personal information, and subdomains from a target domain or individual, outputting…
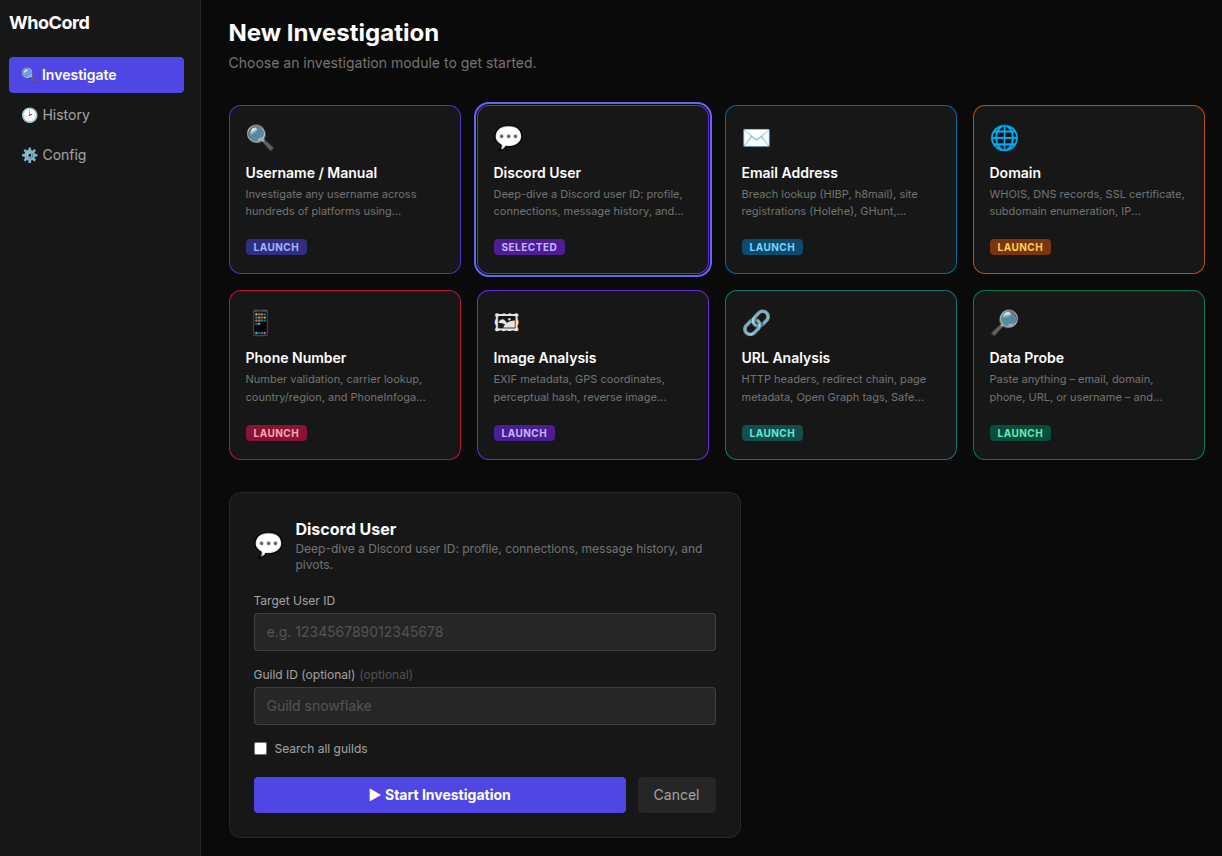 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 leobeosab/sharingan
Offensive Security recon tool
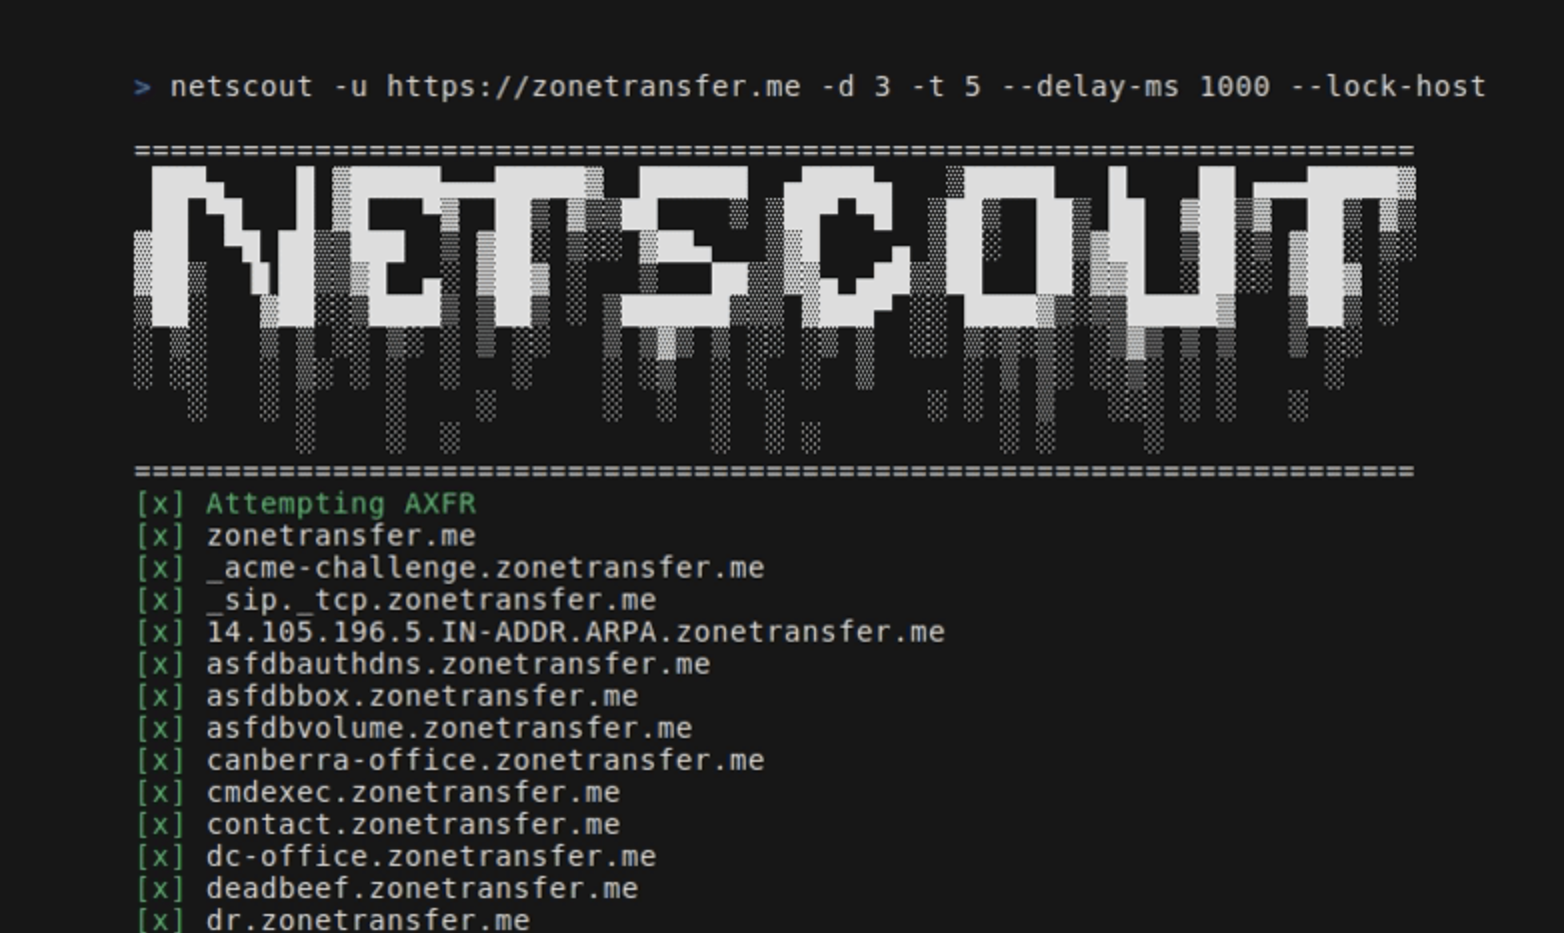 caio-ishikawa/netscout
OSINT tool that finds domains, subdomains, directories, endpoints and files for a given seed URL.
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 makefu/dnsmap
fork of http://code.google.com/p/dnsmap/source/checkout
 researchanddestroy/dorxng
Next Generation DorX. Built by Dorks, for Dorks. 🤓
 mindcrypt/urideep
Unicode encoding attacks with machine learning
 ax-i-om/bitcrook
Centralized OSINT investigation platform with CLI and GUI, integrating email breach checks, domain lookups, phone search, and API key support for…
 a3h1nt/subcert
Passive subdomain enumeration tool that extracts valid subdomains from certificate transparency logs using Python, ideal for reconnaissance and bug…
 in3tinct/taken
Takeover subdomains using AWS dangling elastic ips and have a working POC for Subdomain Takeover.
 zeropwn/dnsdmpstr
Unofficial API & Client for dnsdumpster.com and hackertarget.com
 joda32/certcrunchy
Just a silly recon tool that uses data from SSL Certificates to find potential host names
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results