Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sharingan — Offensive Security recon tool | Kitploit
Tools/GitHubGitHub/leobeosab/sharingan
ReconnaissancePort ScanningDNS & Subdomain EnumerationInformation GatheringPenetration Testing
GitHubleobeosab/sharingan

sharingan

Offensive Security recon tool

View Repository
91141015 years agoReviewed by Kitploit
Share

Sharingan

Sharingan is a recon multitool for offensive security / bug bounty

WIP, will I ever finish? Who knows

Cloning for development

Outside of your gopath git clone https://github.com/leobeosab/sharingan

Installing

go get github.com/leobeosab/sharingan/cmd/sharingancli

Dependencies

  • NMap
  • Go

Usage

Note

Order matters when it comes to flags it must be sharingancli [globalflags] command [commandflags] if this isn't a wanted feature I can change it but I like how clean it is

DNS

bruteforce

DNS busts the target with a wordlist you provide

sharingancli --target targetname dns --dns-wordlist ~/path/to/wordlist --root-domain target.com

dns example gif

addsubs

Adds subdomains to the program's storage from stdin using pipes

cat subs | sharingancli --target targetname dns addsubs

Scan

Scans all hosts available that were stored in target using nmap

sharingancli --target target scan

scan_example_gif

interactive

Scan a single host from list of subdomains stored in target

sharingancli --target target scan interactive
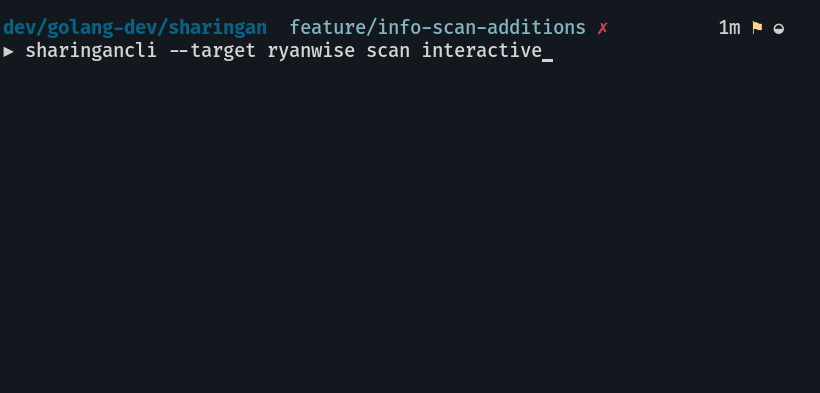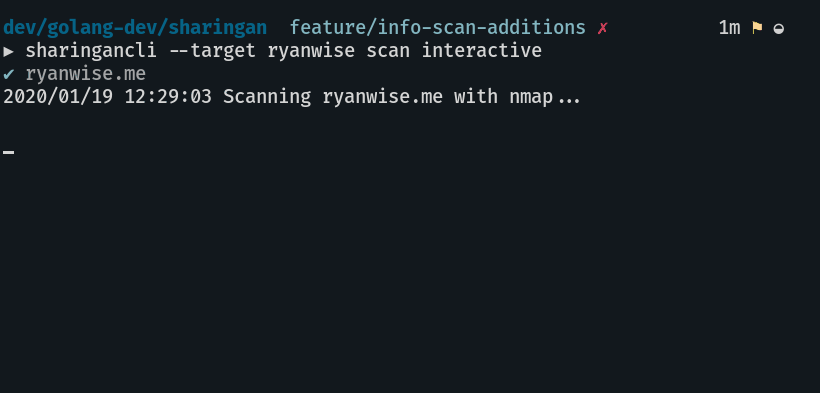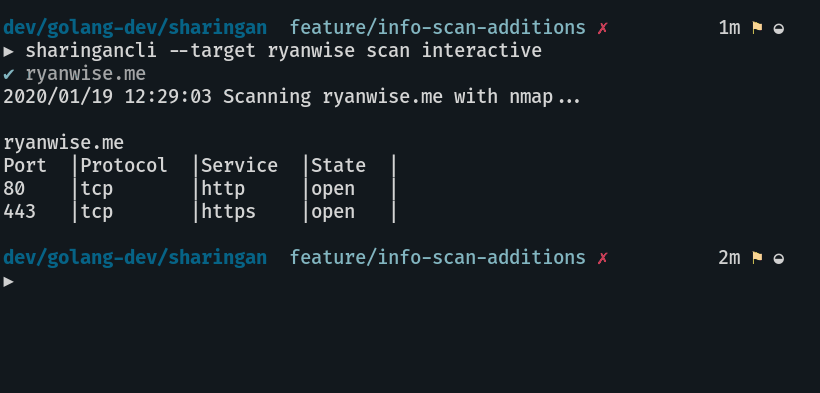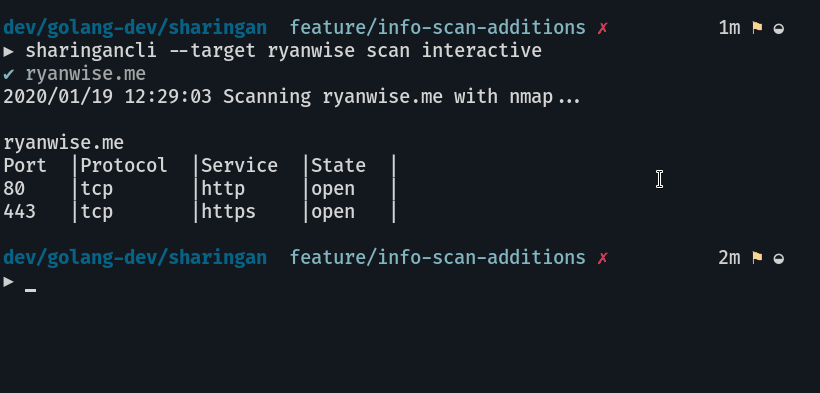
scan interactive_example gif

info

domains

Outputs all domains as a list in stdout

sharingancli --target target info domains

info example

Features to come

  • Dir brute forcing -- Currently being worked on
  • JSON and regular file exports
  • Automated scans through a daemon?
  • add a way to do SYN / -sS scanning [ must be root so it presents a challenge ]
  • Possible Web ui / html export
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →