
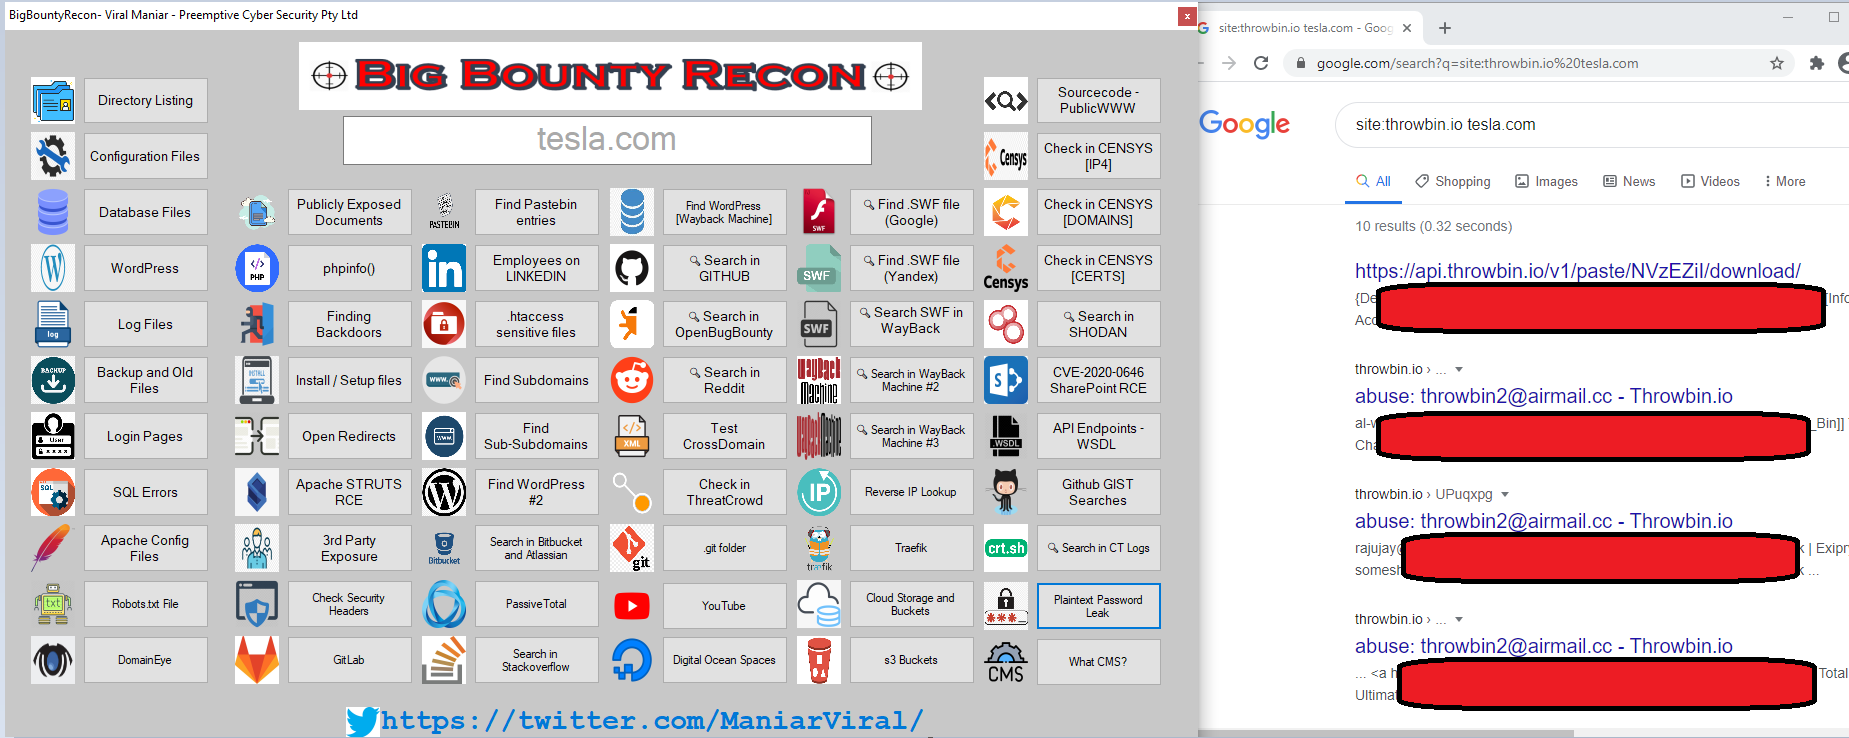
BigBountyRecon
 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
dns-subdomain-enumerationeducationinformation-gathering+6
1.6k
viralmaniar/bigbountyreconBigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 dwisiswant0/go-dork
The fastest dork scanner written in Go.
 frizb/vanquish
Vanquish is Kali Linux based Enumeration Orchestrator. Vanquish leverages the opensource enumeration tools on Kali to perform multiple active…
 chiasmod0n/chiasmodon
Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
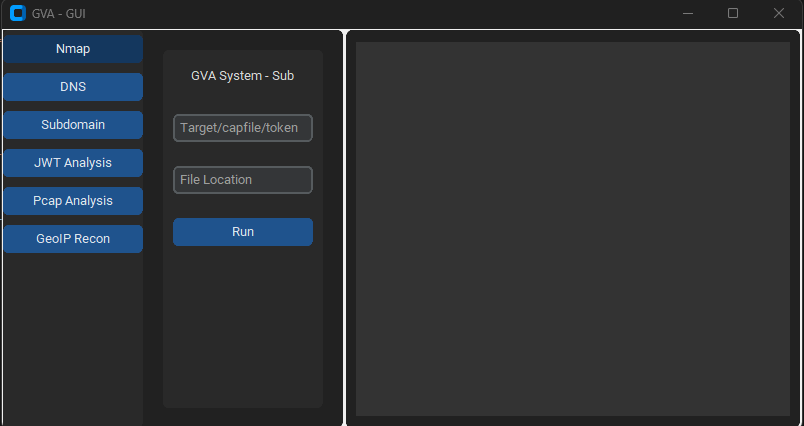 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
 christophetd/censys-subdomain-finder
⚡ Perform subdomain enumeration using the certificate transparency logs from Censys.
 ekultek/pybelt
The hackers tool belt
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
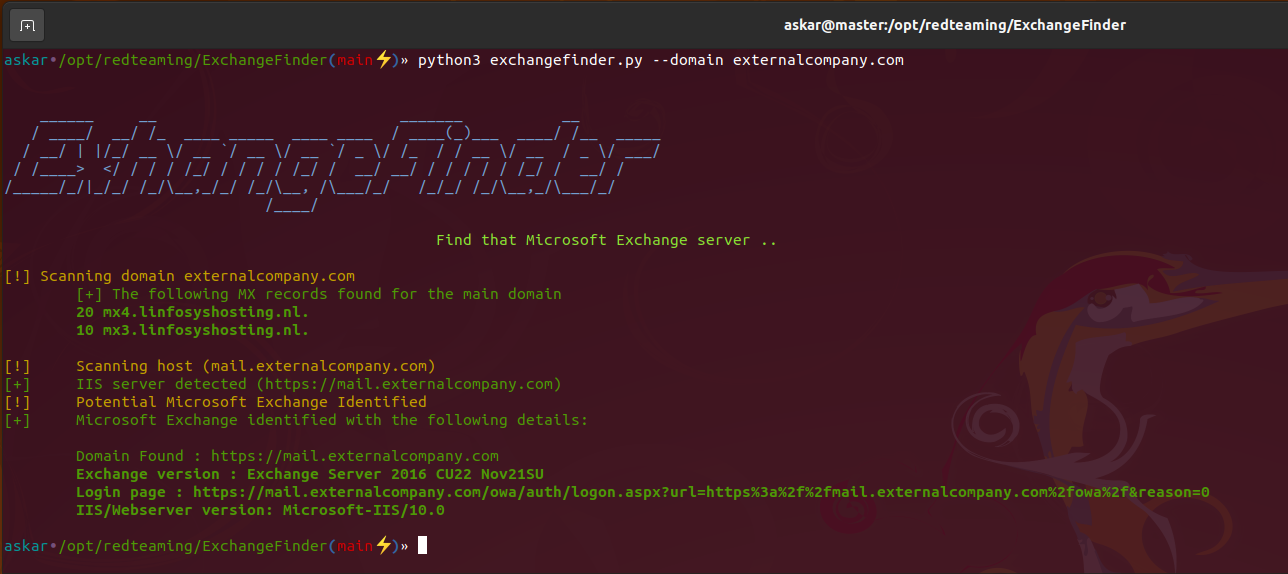 mhaskar/exchangefinder
Find Microsoft Exchange instance for a given domain and identify the exact version
 thebinitghimire/nthim
Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!
 misterch0c/twitterbftd
Twitter Back From The Dead looks in a user tweets history for domain names that are available for registration
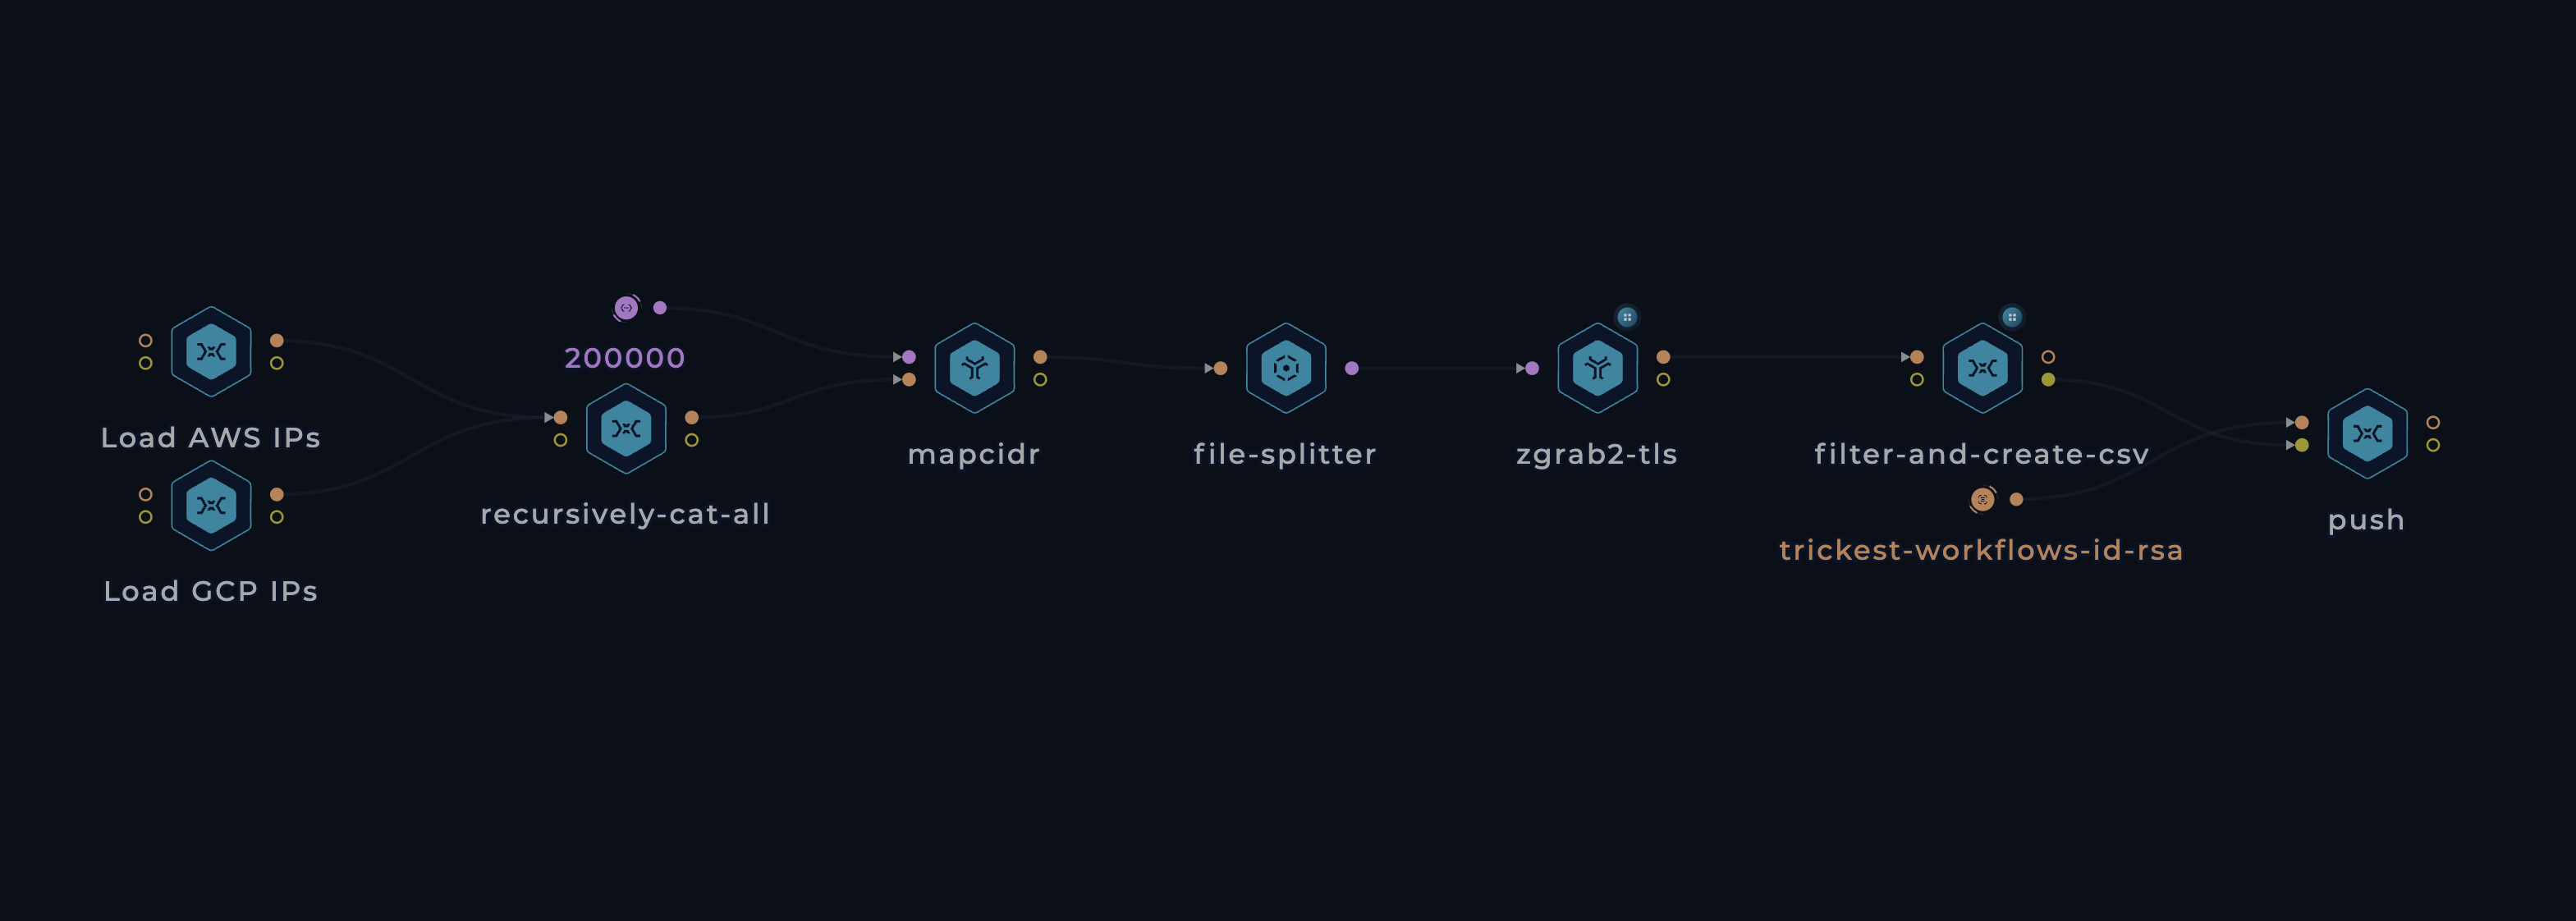 trickest/cloud
Monitoring the Cloud Landscape
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
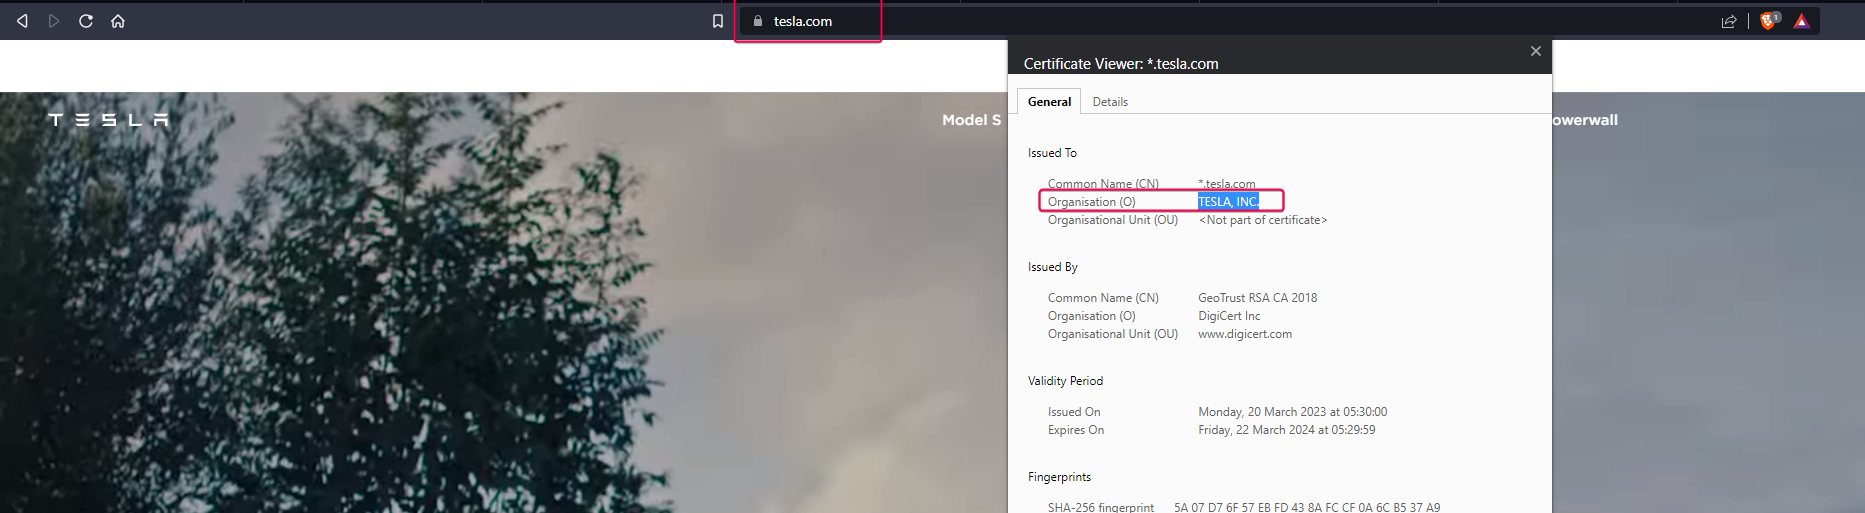 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 hackplayers/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…