

subfinder
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
dns-analysisdns-fuzzingdns-subdomain-enumeration+9
projectdiscovery/subfinderFast passive subdomain enumeration tool.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
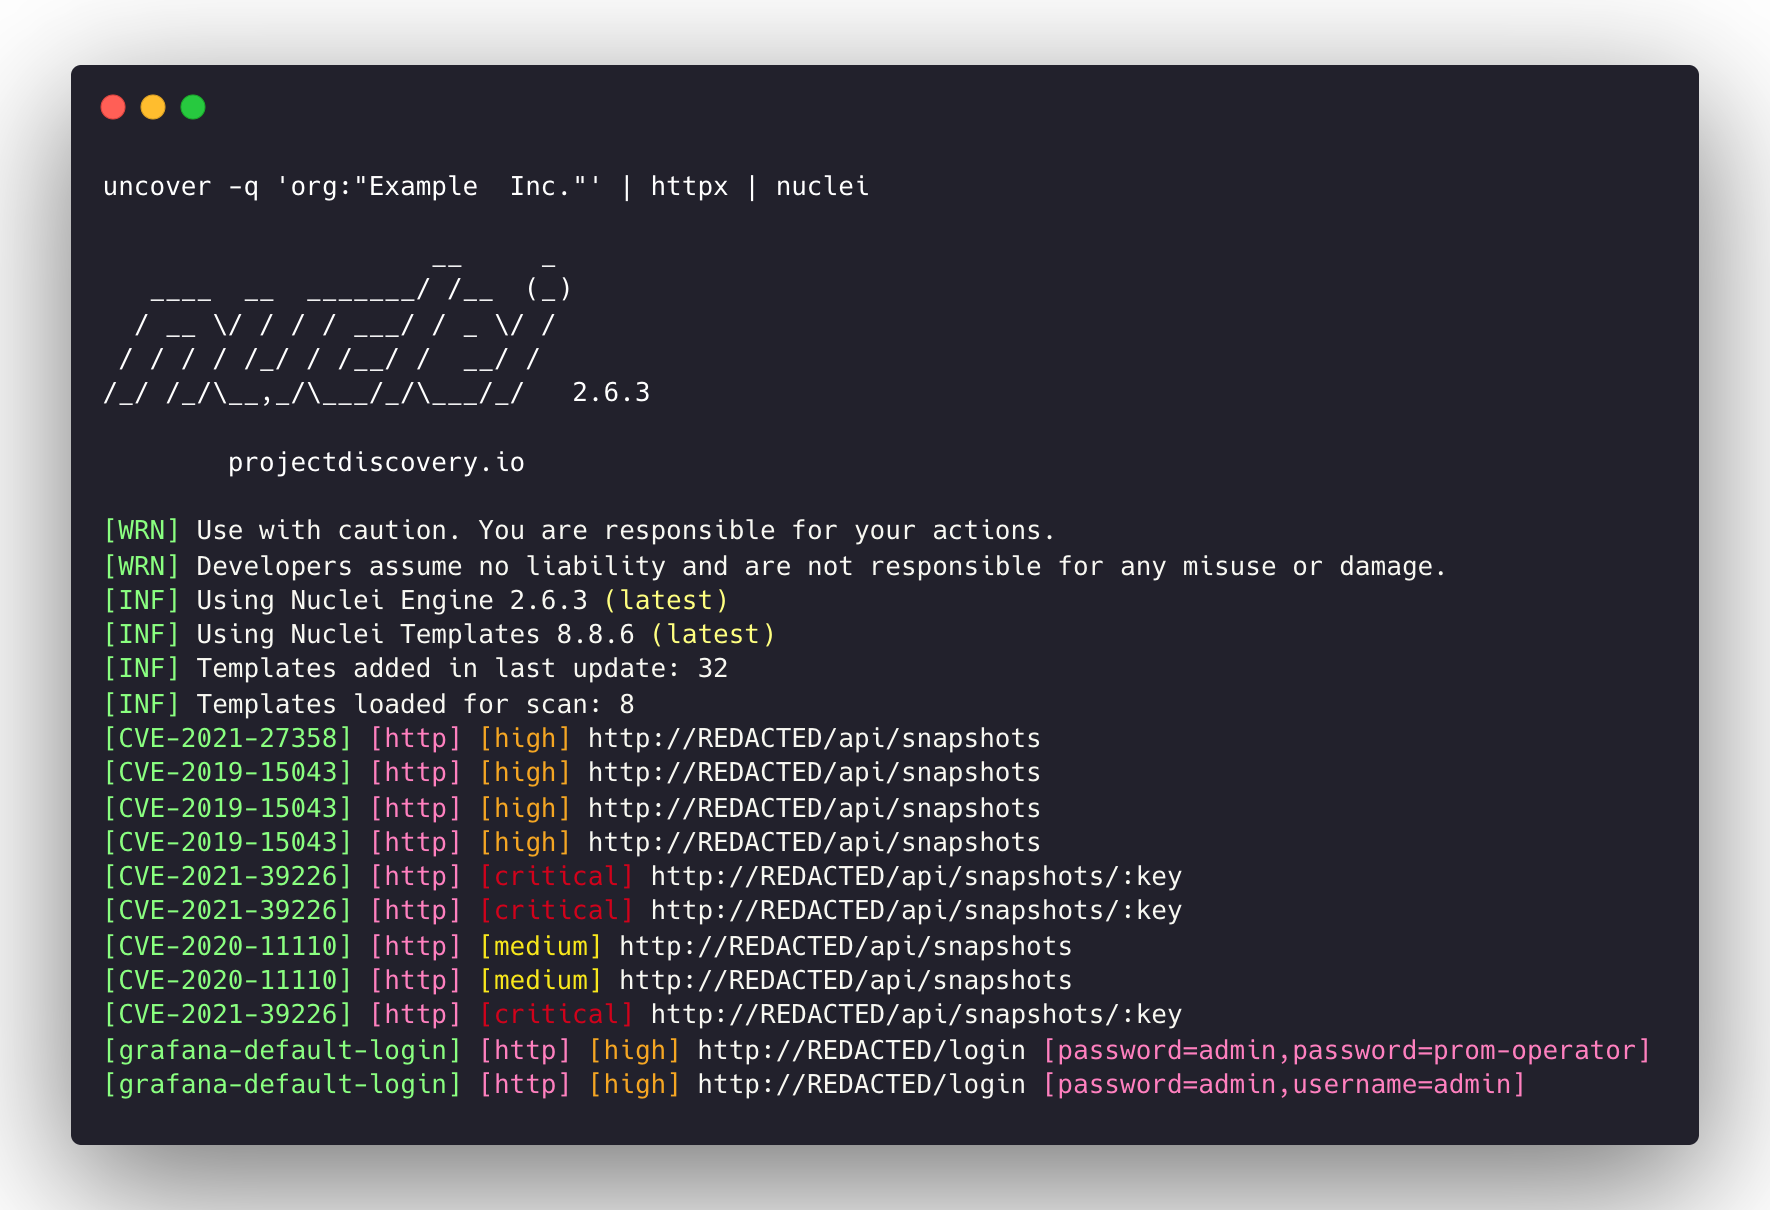 projectdiscovery/uncover
Quickly discover exposed hosts on the internet using multiple search engines.
 deadshot0x7/007-thebond
This Script will help you to gather information about your victim or friend.
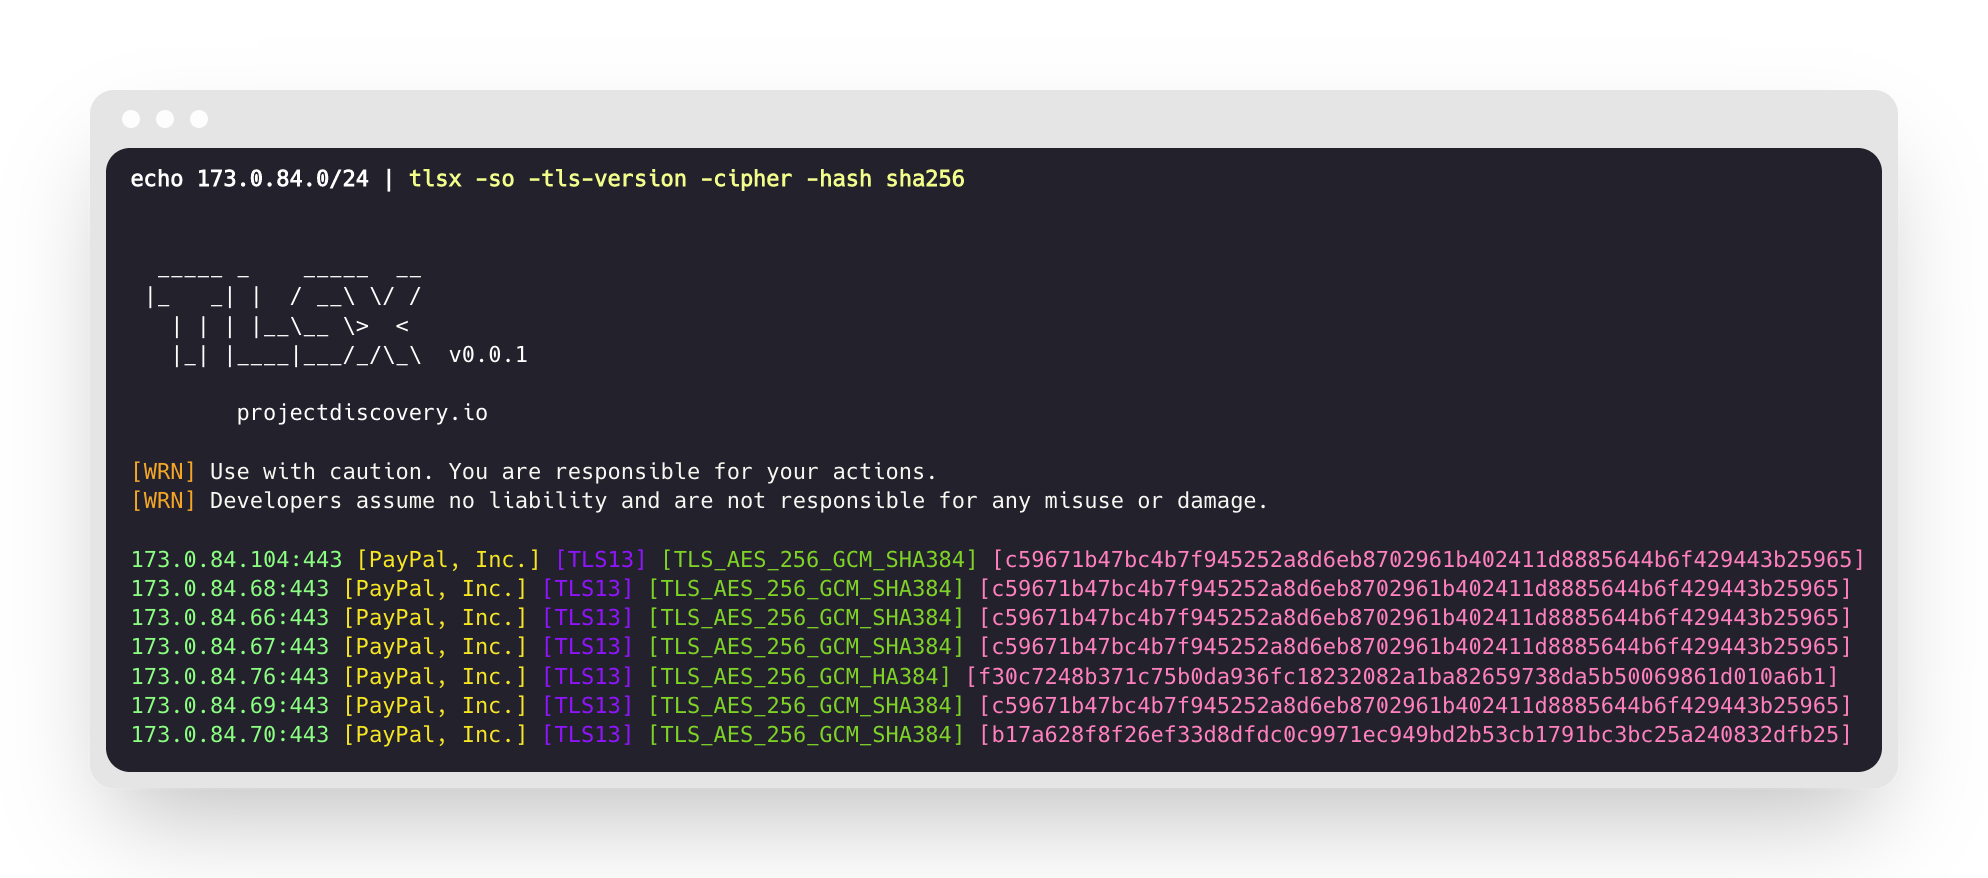 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
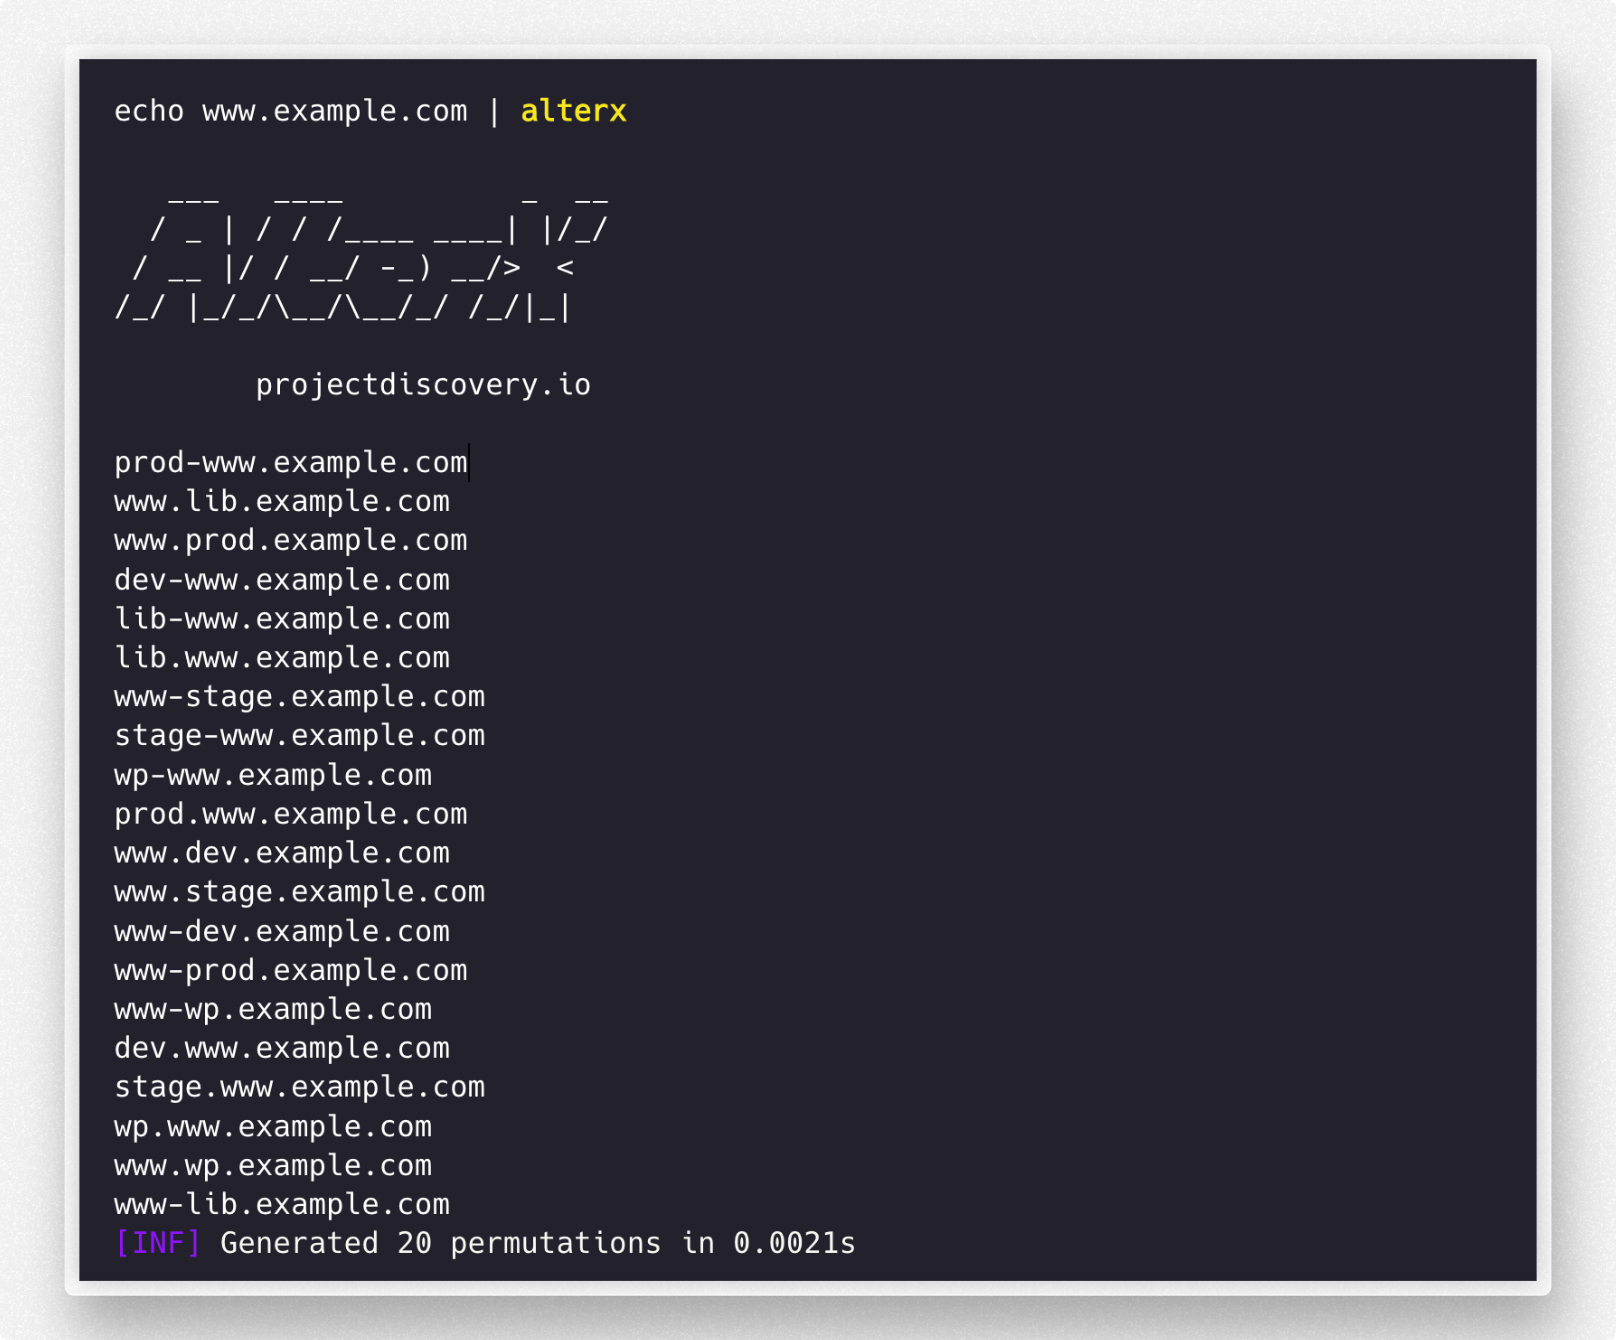 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 zarcolio/sitedorks
Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…
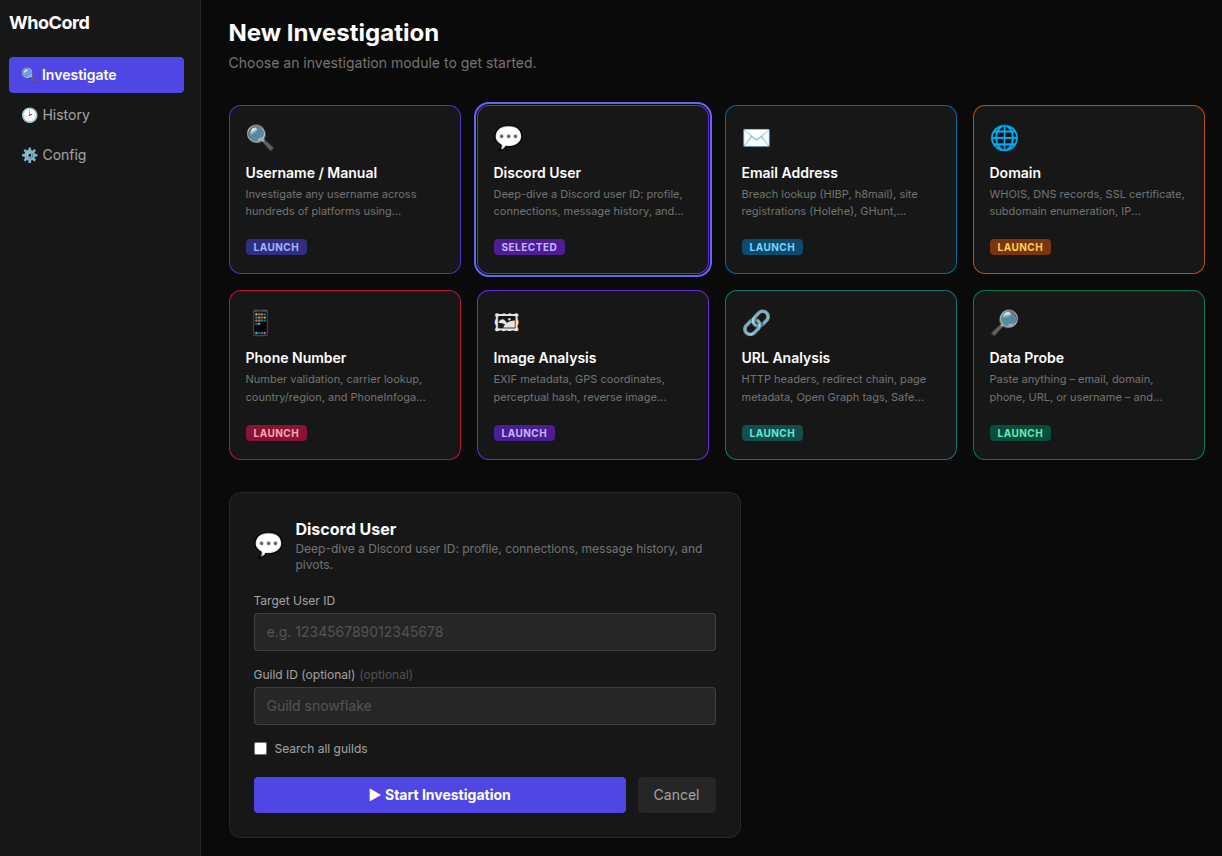 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…