
WordList
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
dns-subdomain-enumerationfuzzinginformation-gathering+6
153
rix4uni/wordlistCurated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 0xshe/fuck-cdn
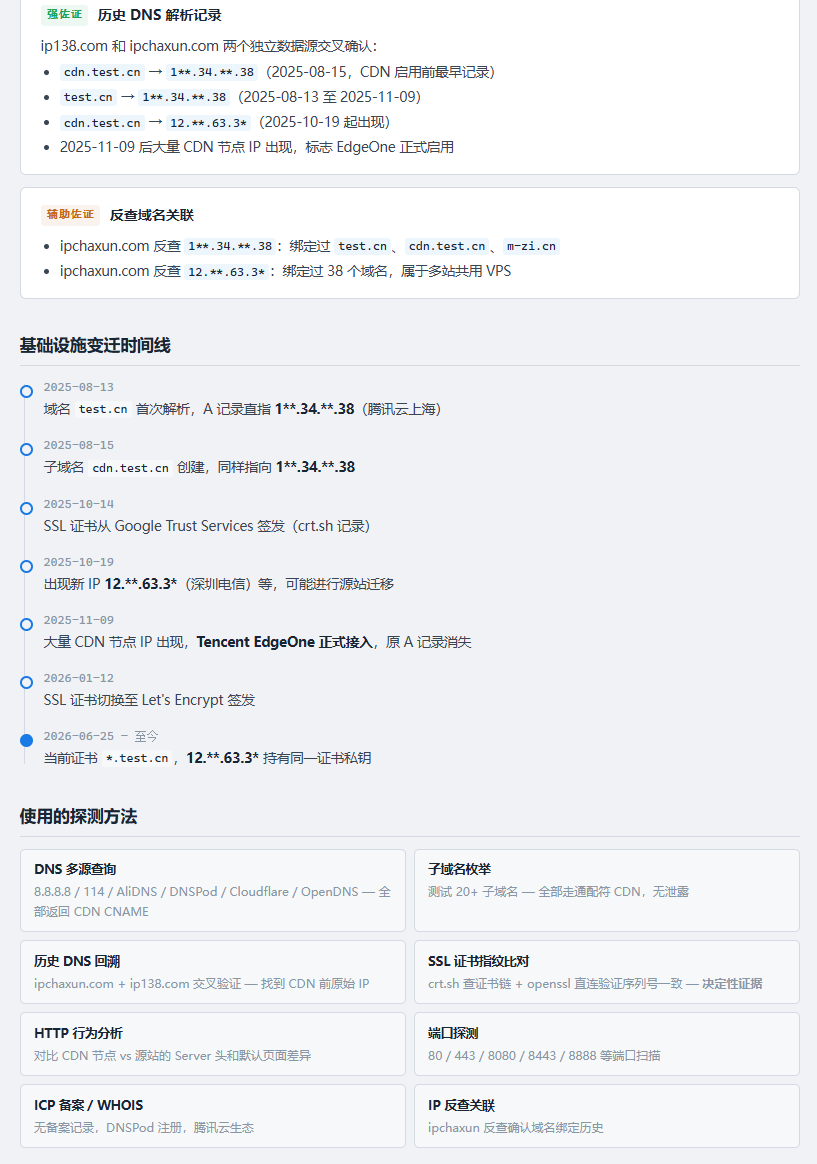
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 rthalley/dnspython
Python DNS toolkit supporting queries, zone transfers, dynamic updates, TSIG, EDNS0, DNSSEC, DNS-over-HTTPS, and DNS-over-QUIC with high- and…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 gmh5225/domain-enumeration-sicarius
Another tool for subdomain enumeration with some magics 🧙🏻♂️
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers
 ethicalhackingplayground/dnsresolver
A Lightning-Fast DNS Resolver written in Rust 🦀
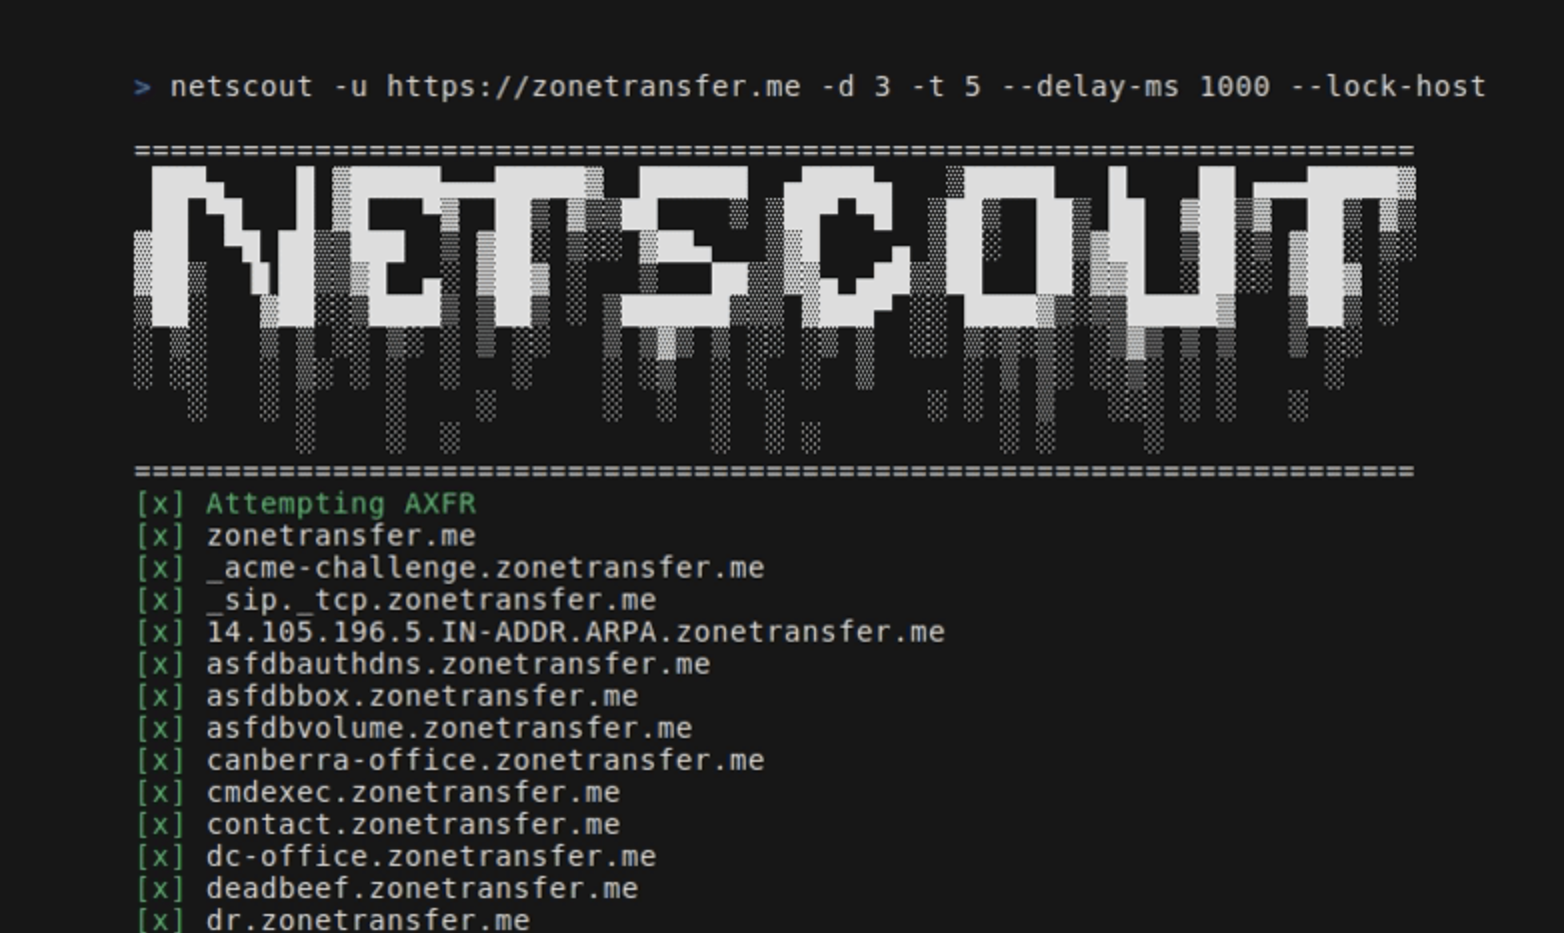 caio-ishikawa/netscout
OSINT tool that finds domains, subdomains, directories, endpoints and files for a given seed URL.
 k3ystr0k3r/dnsplit
Fast subdomain enumeration tool written in python.
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
 darryllane/bluto-old
Recon, Subdomain Bruting, Zone Transfers
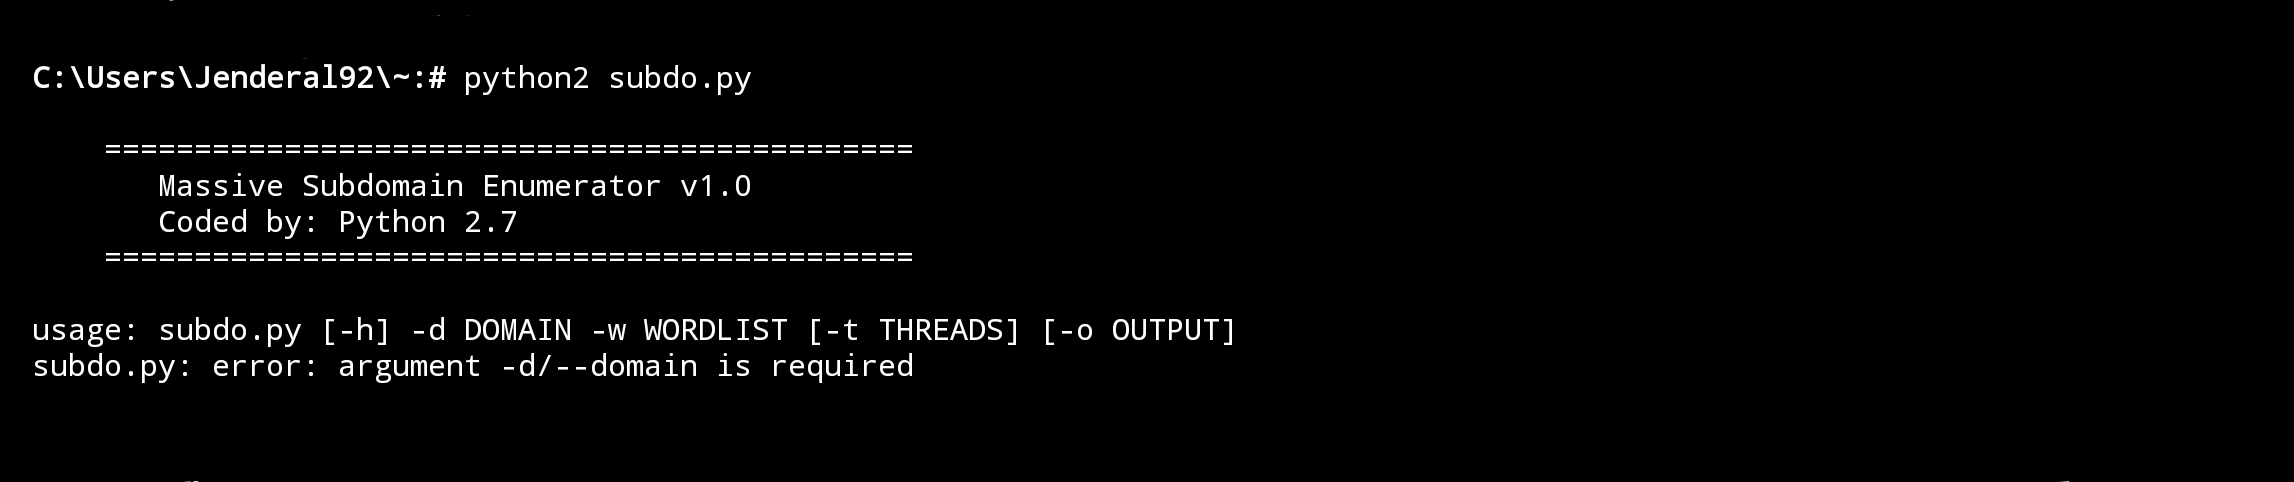 jenderal92/massive-subdomain-enumerator
This tool uses a combination of dictionary-based wordlists (brute-force) and DNS resolution checks to verify the existence of subdomains.