
RXScan
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
defensive-toolsdns-analysisdns-subdomain-enumeration+8
1
darkrx1/rxscanRust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…

 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
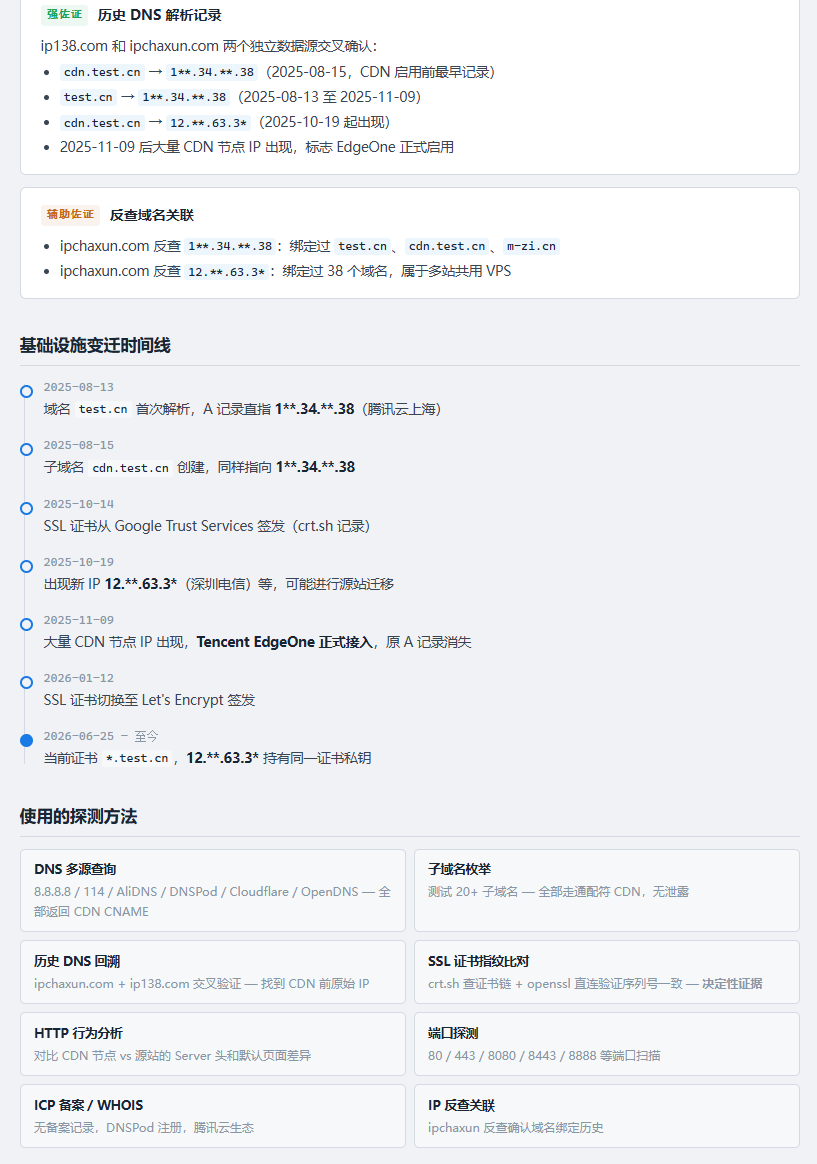 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 rthalley/dnspython
Python DNS toolkit supporting queries, zone transfers, dynamic updates, TSIG, EDNS0, DNSSEC, DNS-over-HTTPS, and DNS-over-QUIC with high- and…
 gmh5225/domain-enumeration-sicarius
Another tool for subdomain enumeration with some magics 🧙🏻♂️
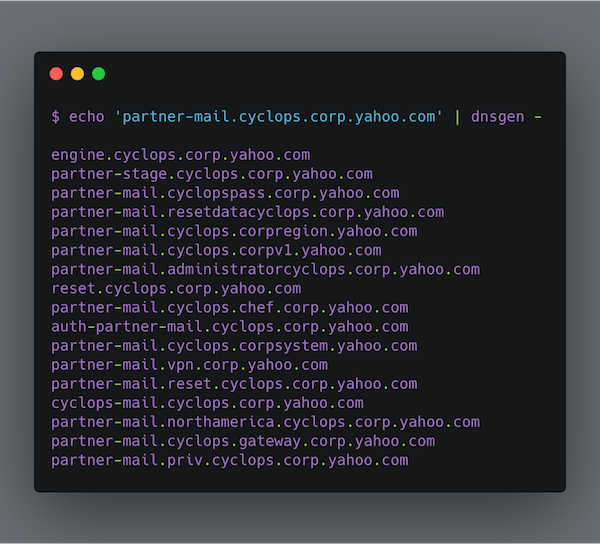 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 hakluke/hakrevdns
Small, fast tool for performing reverse DNS lookups en masse.
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers
 ethicalhackingplayground/dnsresolver
A Lightning-Fast DNS Resolver written in Rust 🦀
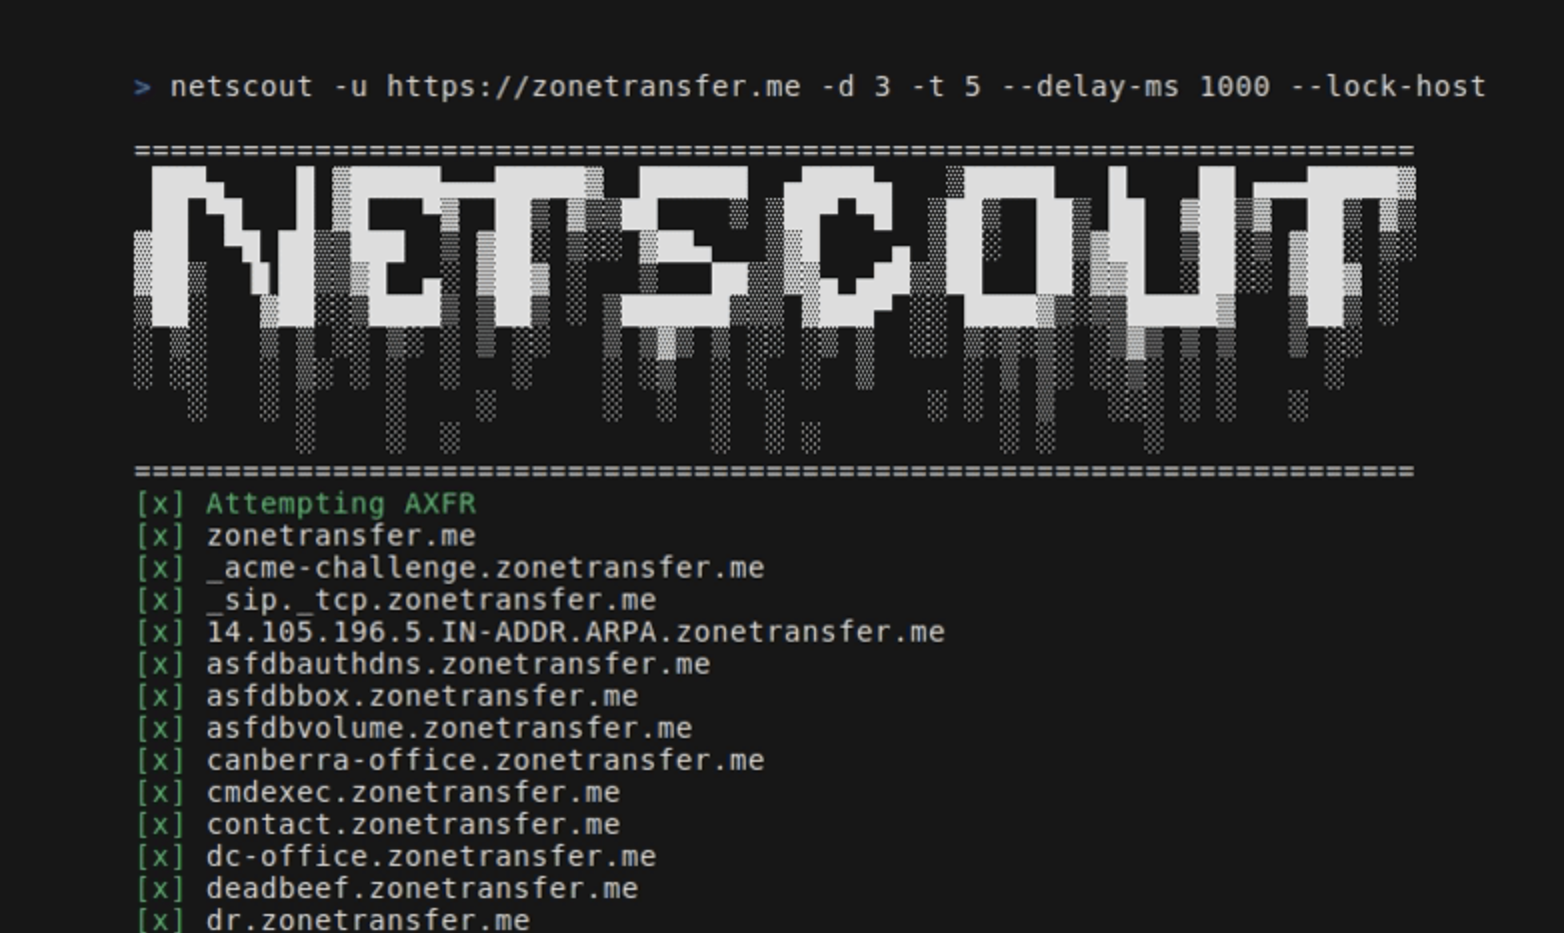 caio-ishikawa/netscout
OSINT tool that finds domains, subdomains, directories, endpoints and files for a given seed URL.
 nccgroup/hostresolver
A Windows application to help out with external infrastructure scans.