

yowie
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
defensive-toolsdns-analysisdns-subdomain-enumeration+9
2
joda32/yowieFinds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration
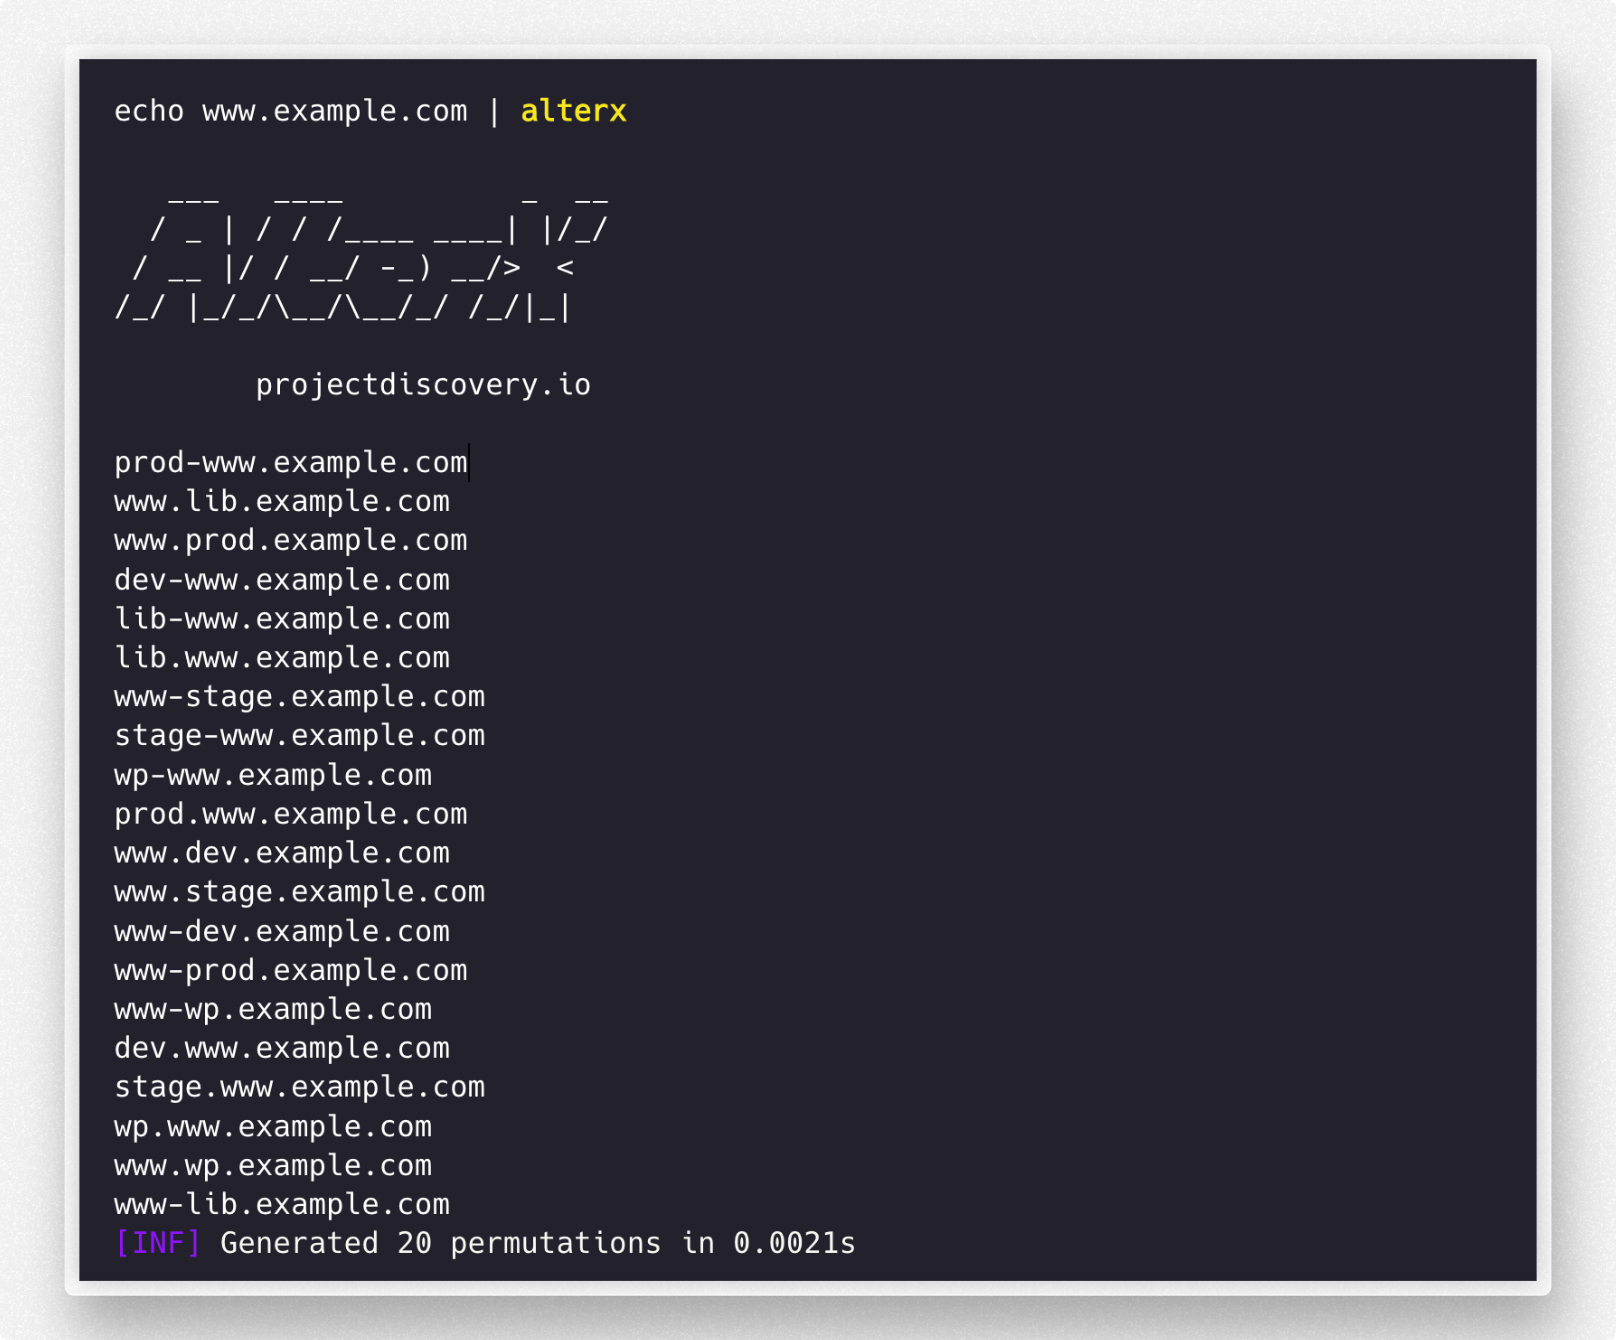 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL
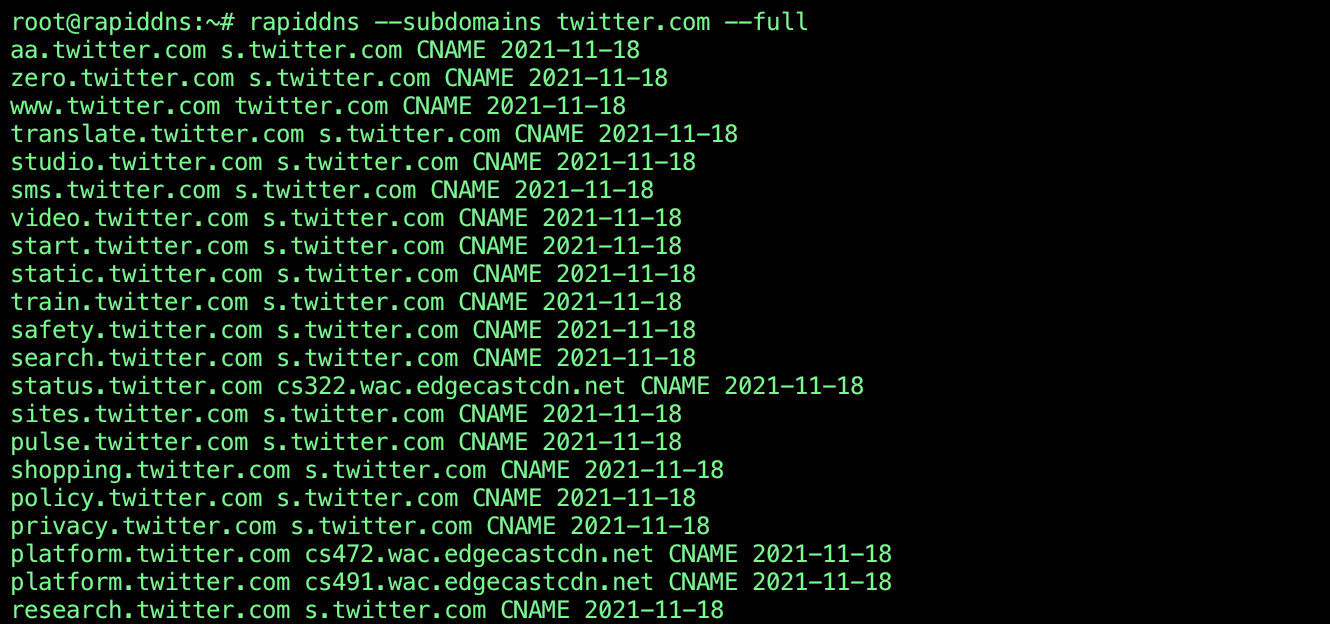 nullt3r/rapiddns
Rapidly enumerate subdomains and domains using rapiddns.io.
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
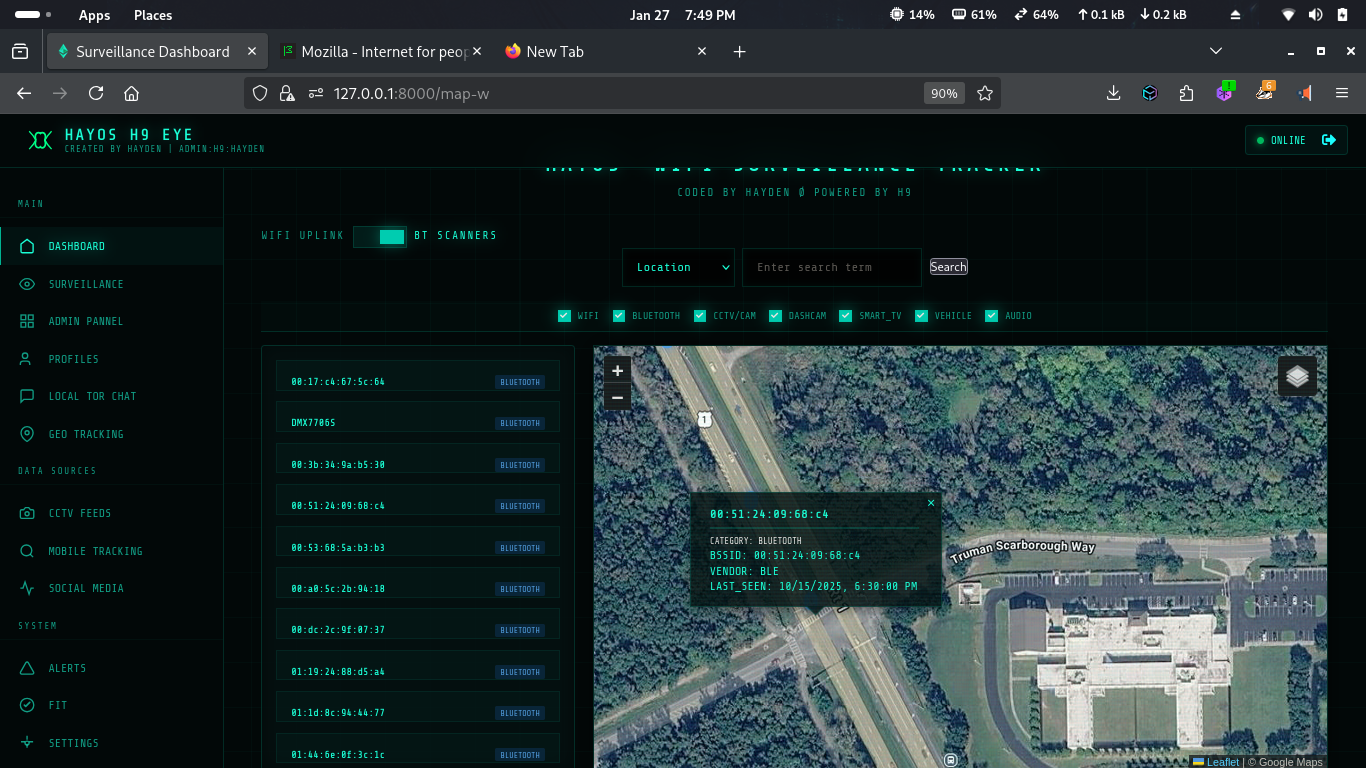 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.
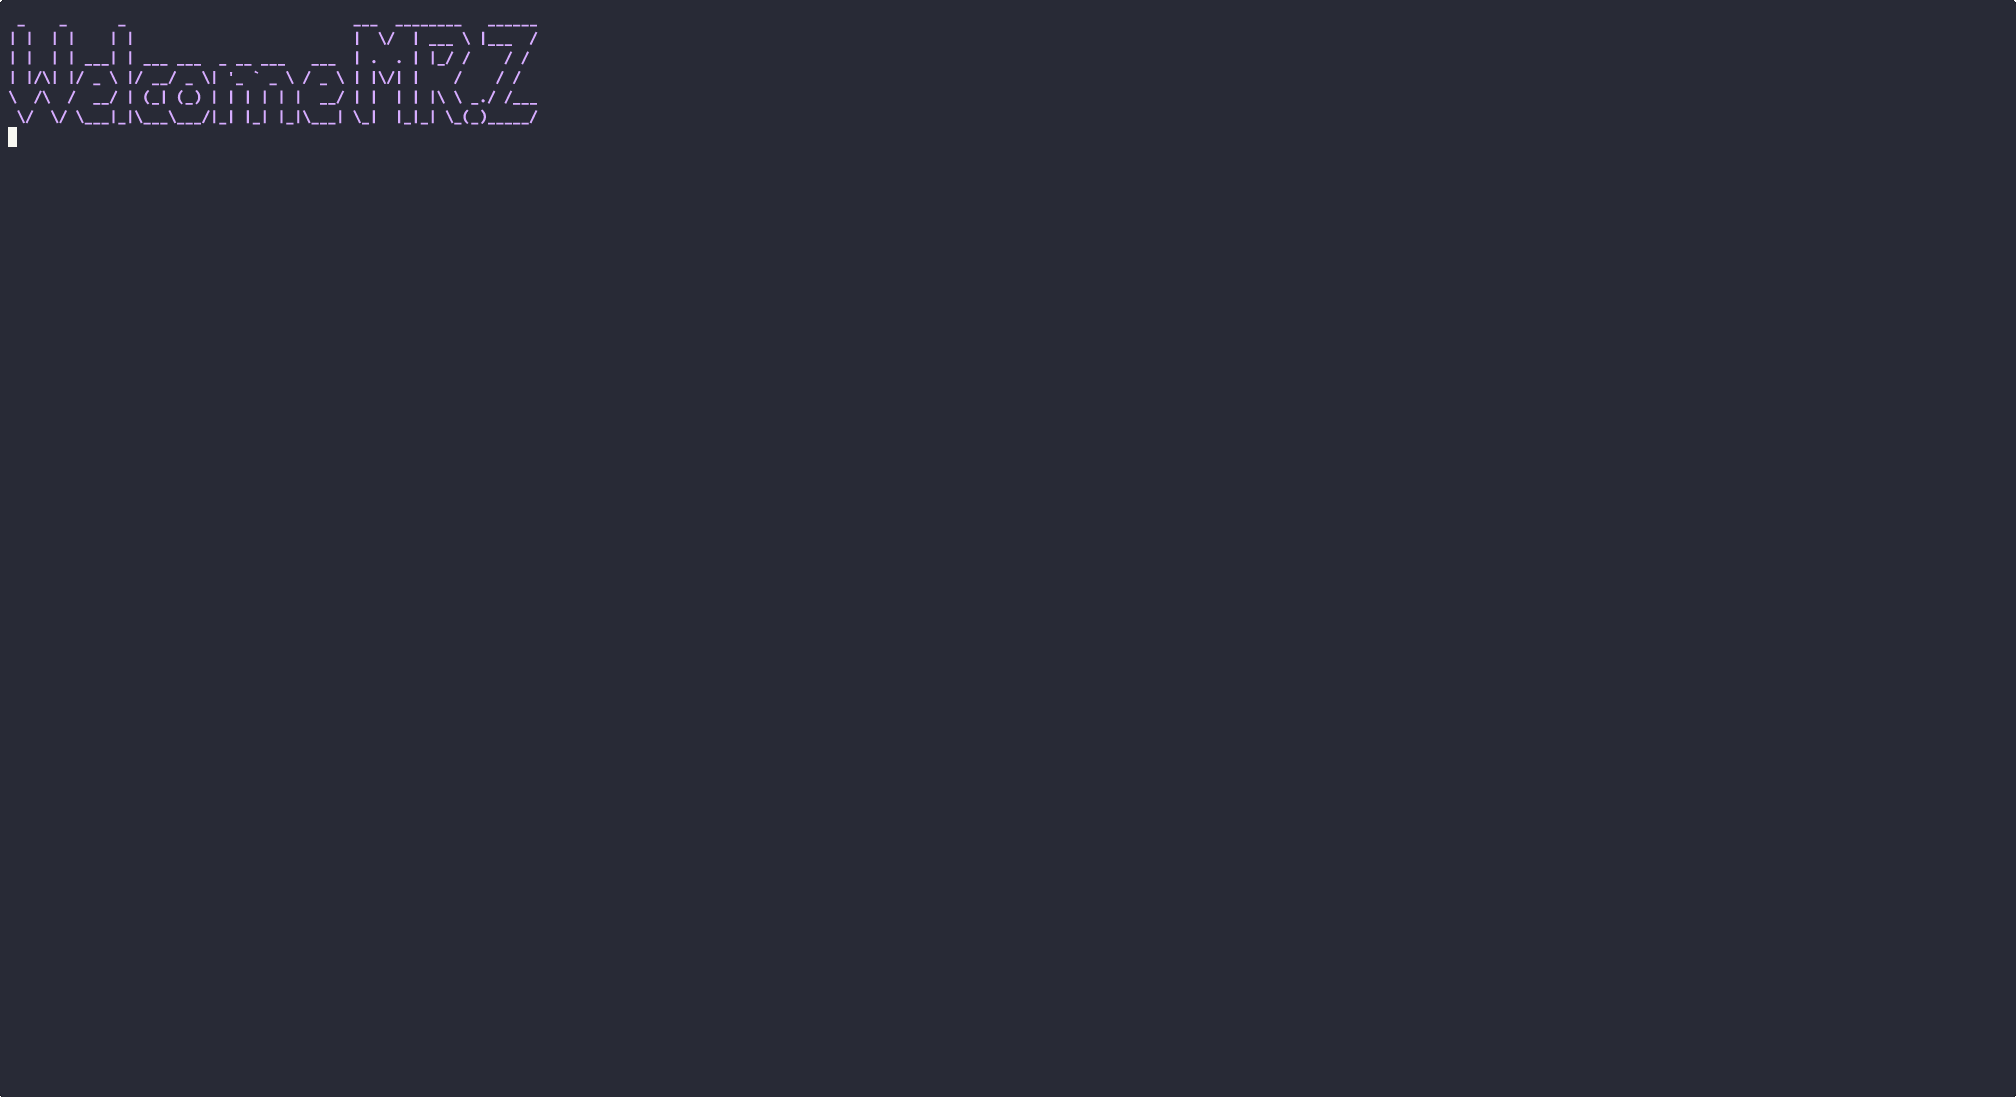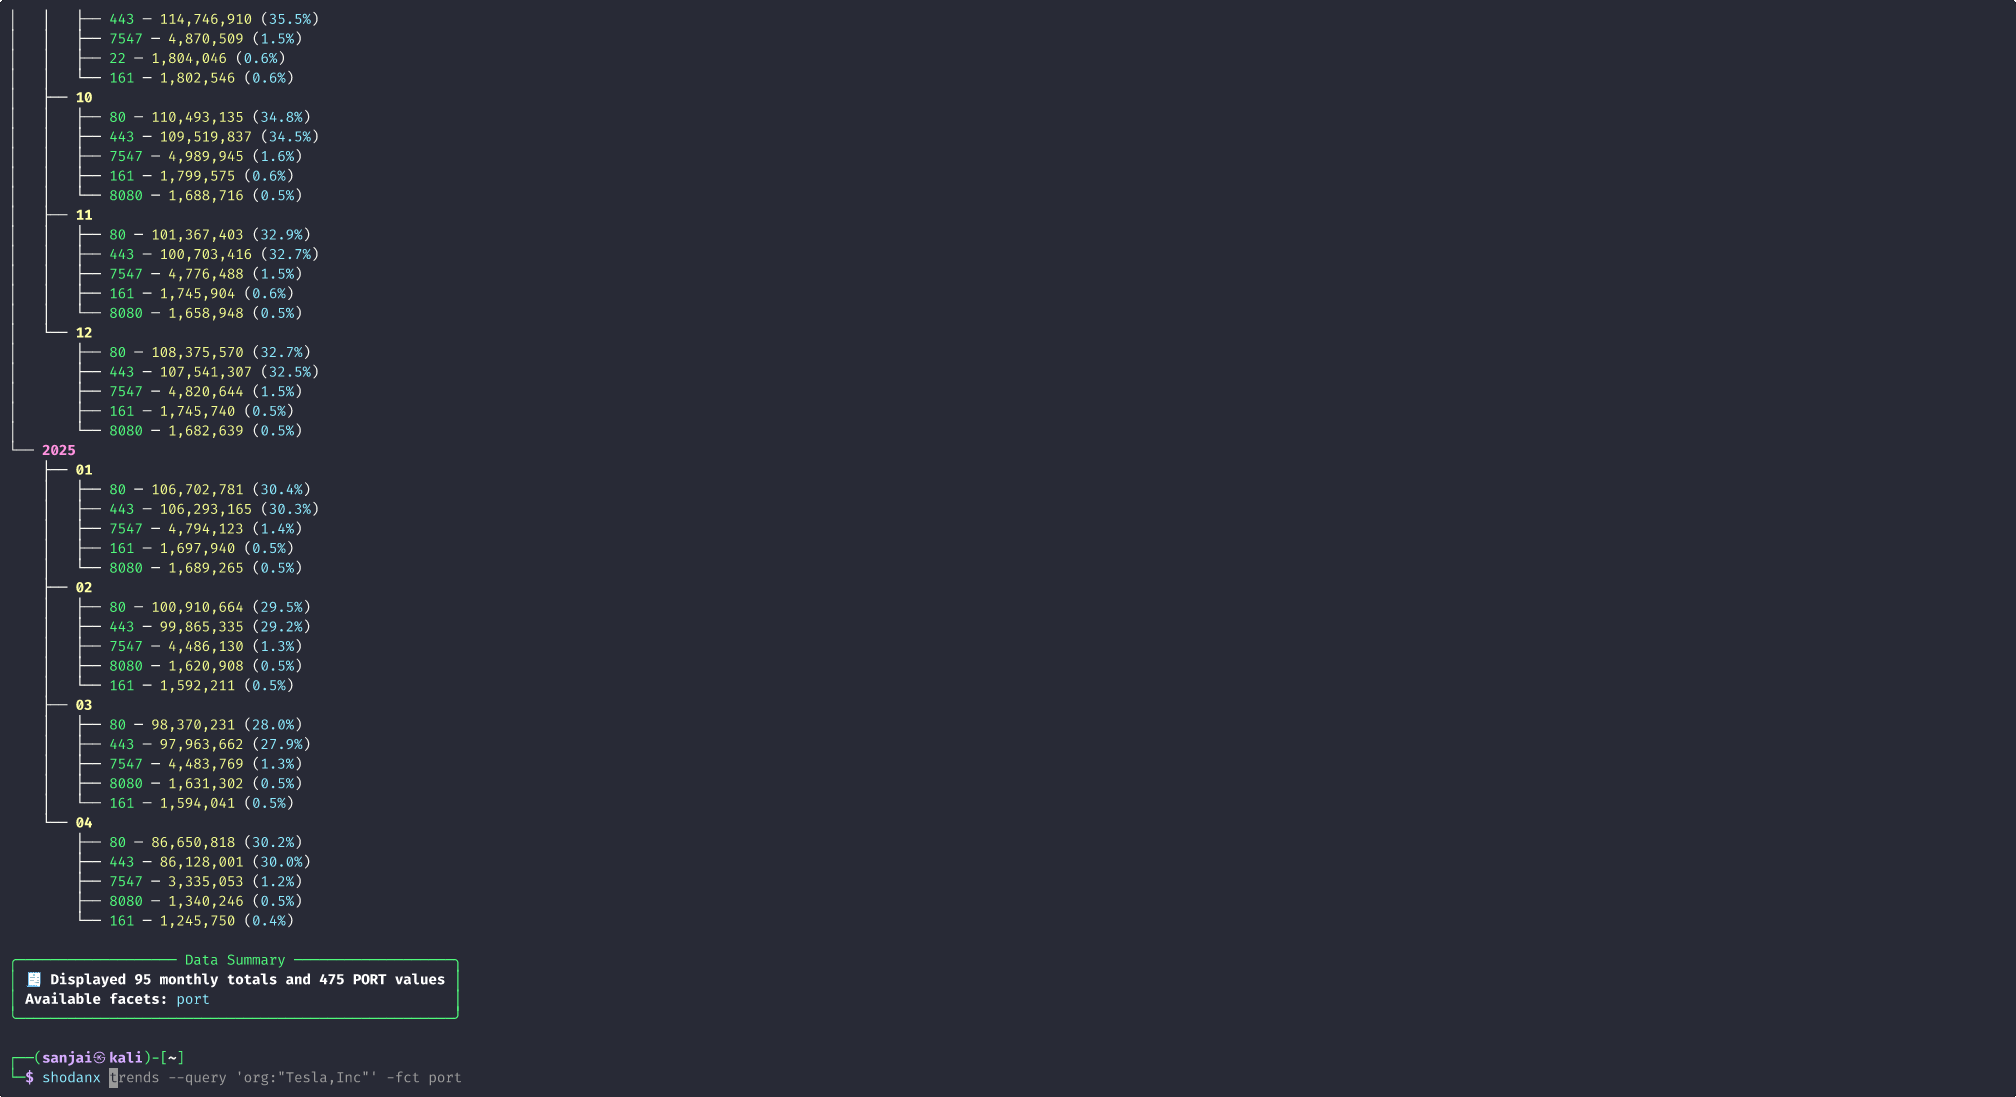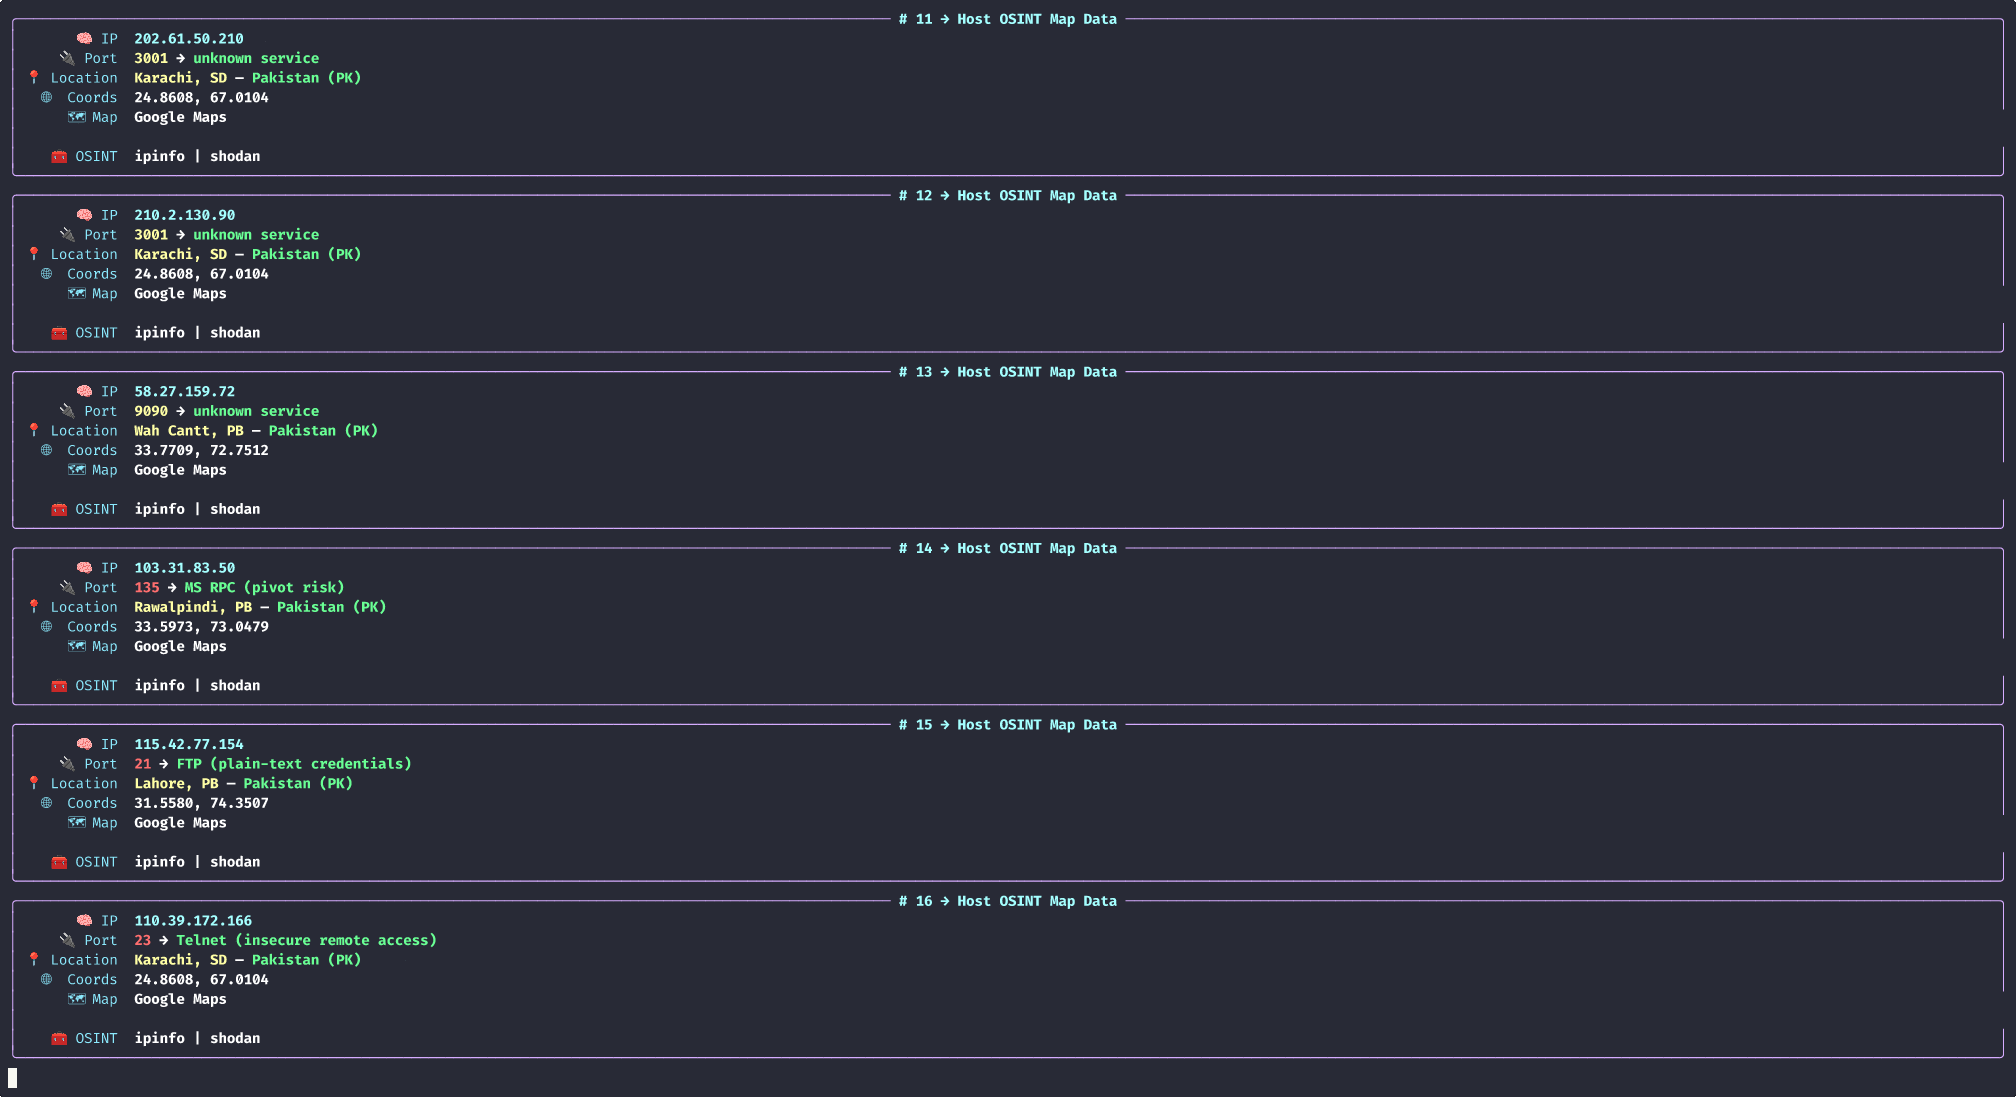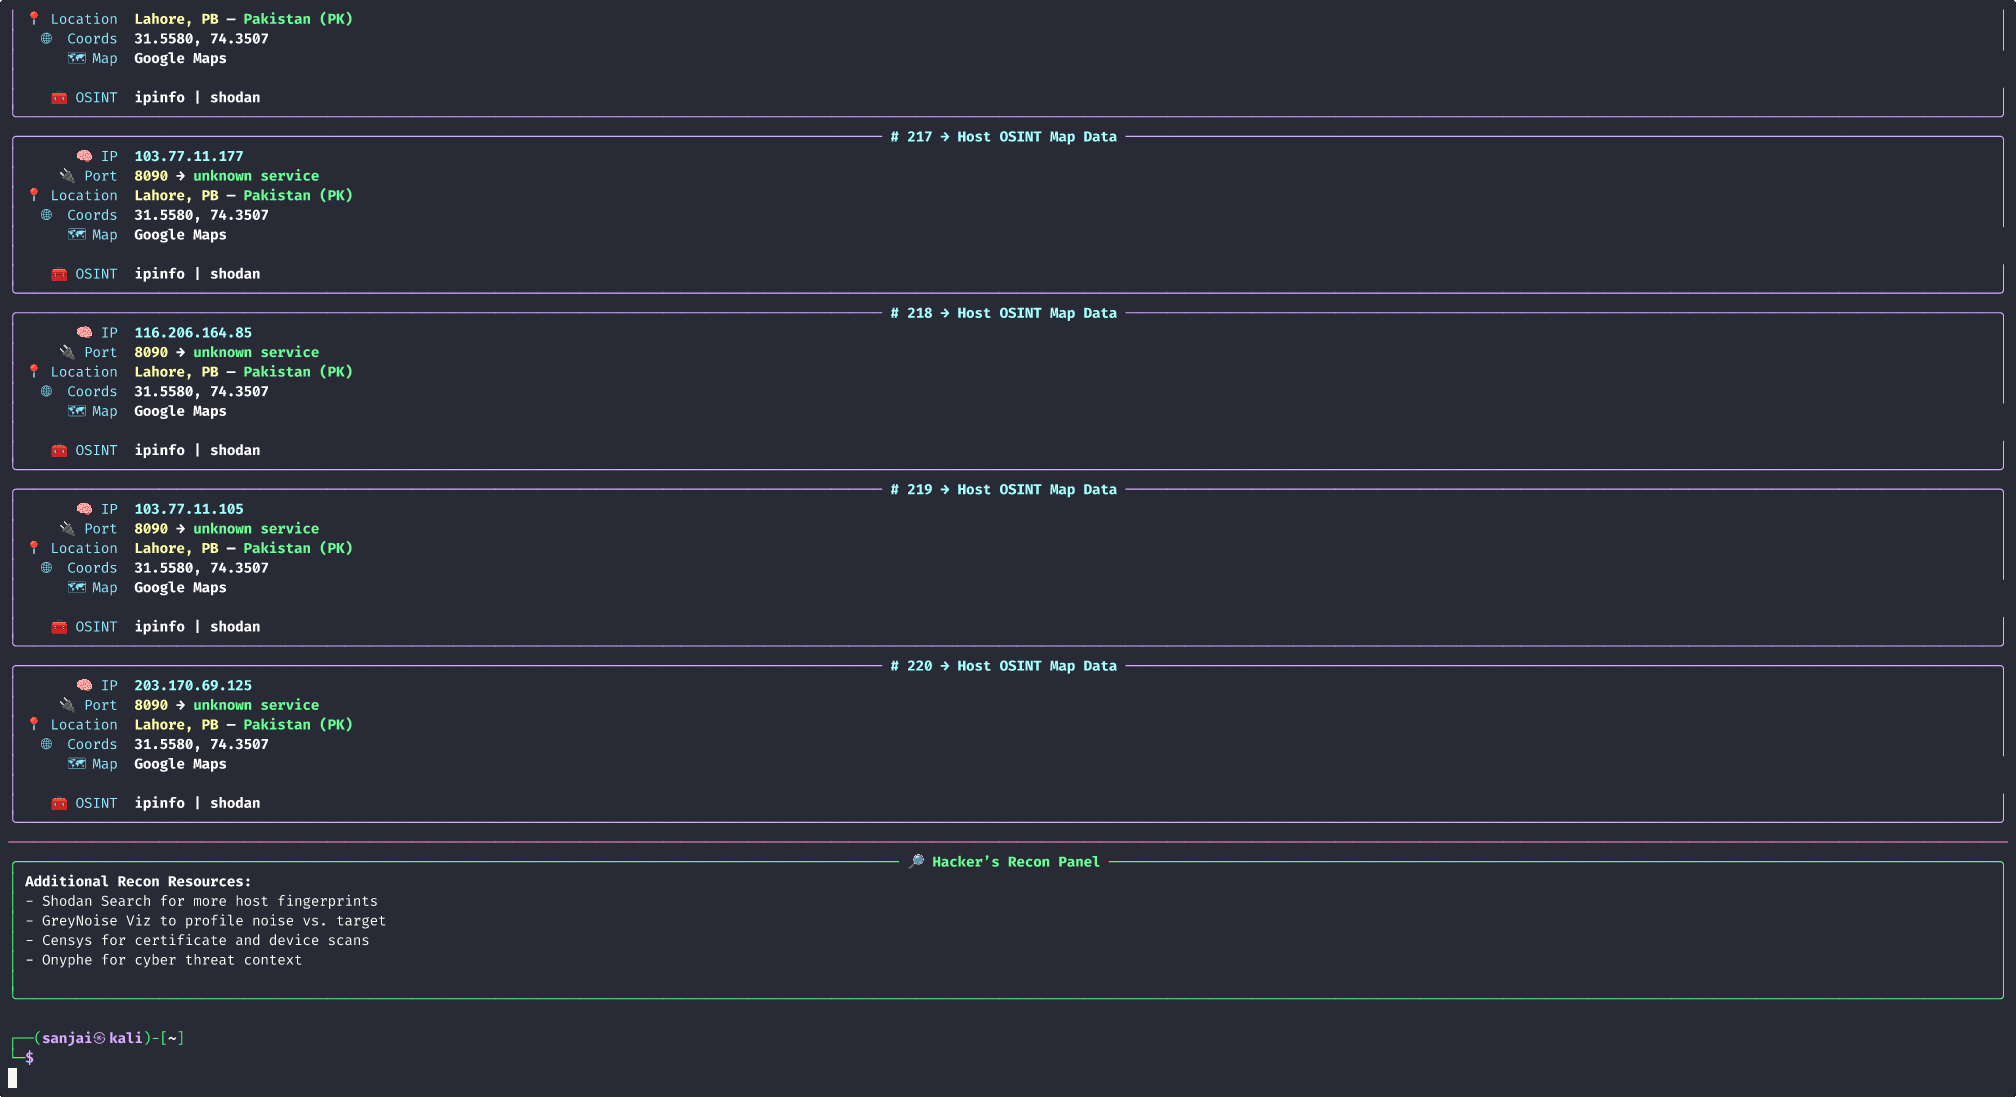 revoltsecurities/shodanx
ShodanX is a tool to gather information of targets using shodan dorks⚡.
 hackplayers/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
 aboul3la/sublist3r
Fast subdomains enumeration tool for penetration testers
 christophetd/censys-subdomain-finder
⚡ Perform subdomain enumeration using the certificate transparency logs from Censys.
 spiderlabs/hosthunter
HostHunter a recon tool for discovering hostnames using OSINT techniques.
 am0nt31r0/osint-search
Useful for digital forensics investigations or initial black-box pentest footprinting.
 evilsocket/dnssearch
A subdomain enumeration tool.