

DNSStager
 mhaskar/dnsstager
Hide your payload in DNS
command-and-controldns-analysisexploitation+3
6223 years ago
mhaskar/dnsstagerHide your payload in DNS
 sensepost/godoh
🕳 godoh - A DNS-over-HTTPS C2
 mananjain61/php-cgi-internal-rce
Delivering PHP RCE (CVE-2024-4577) to the Local Network Servers
 ascotbe/medusa
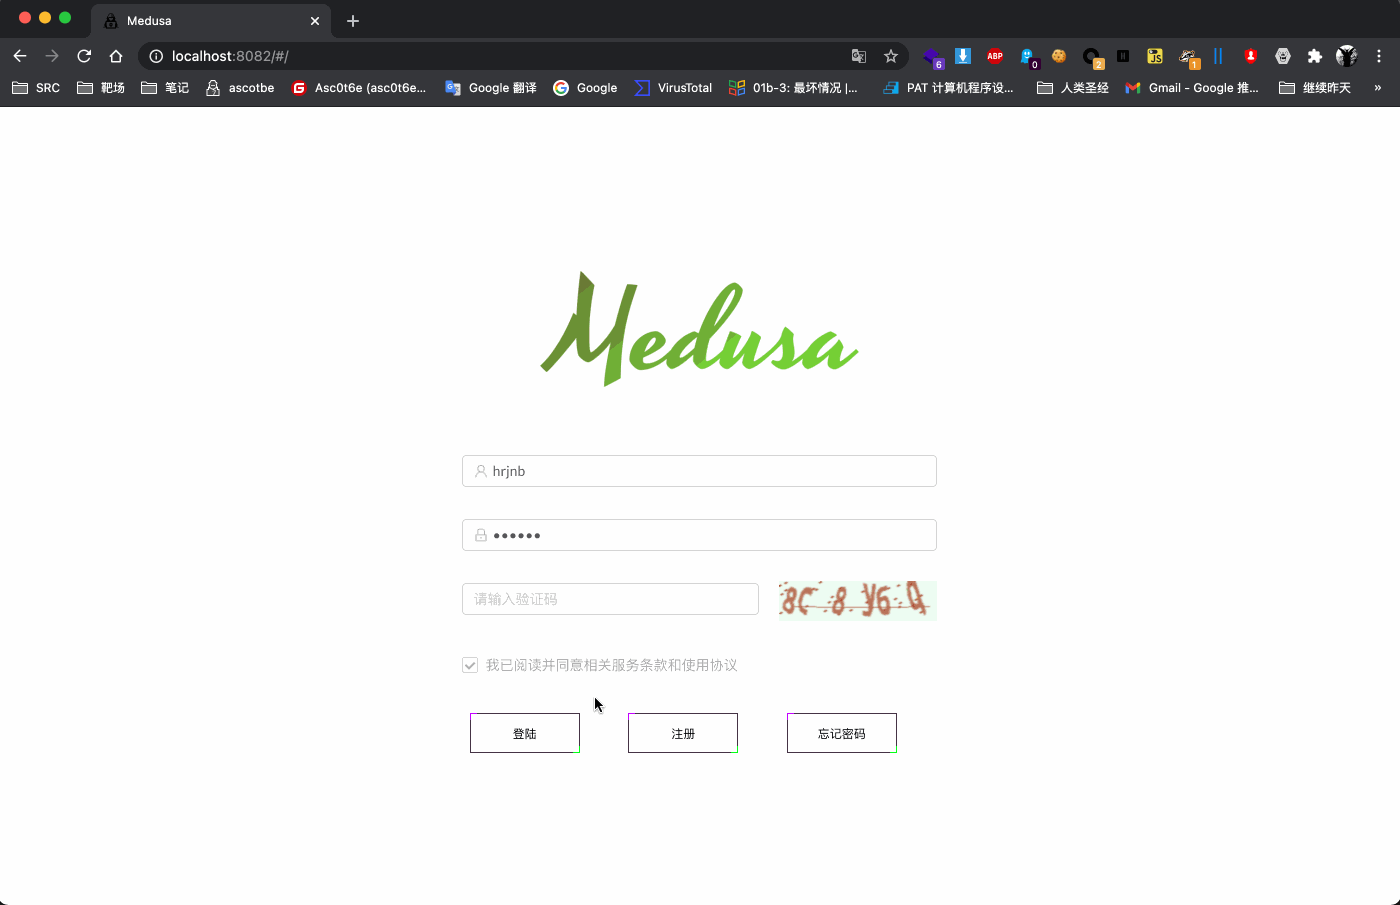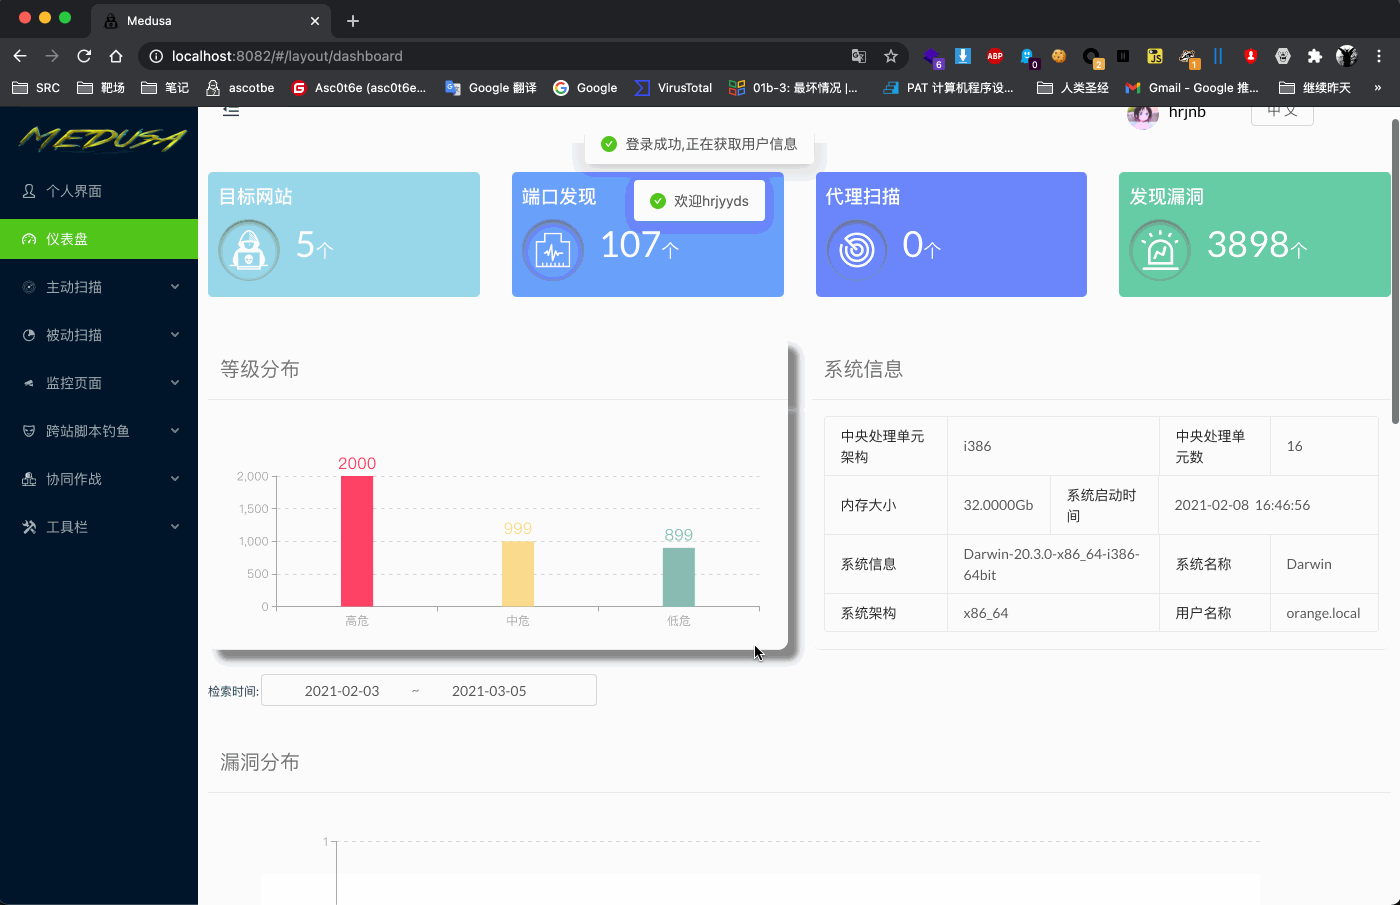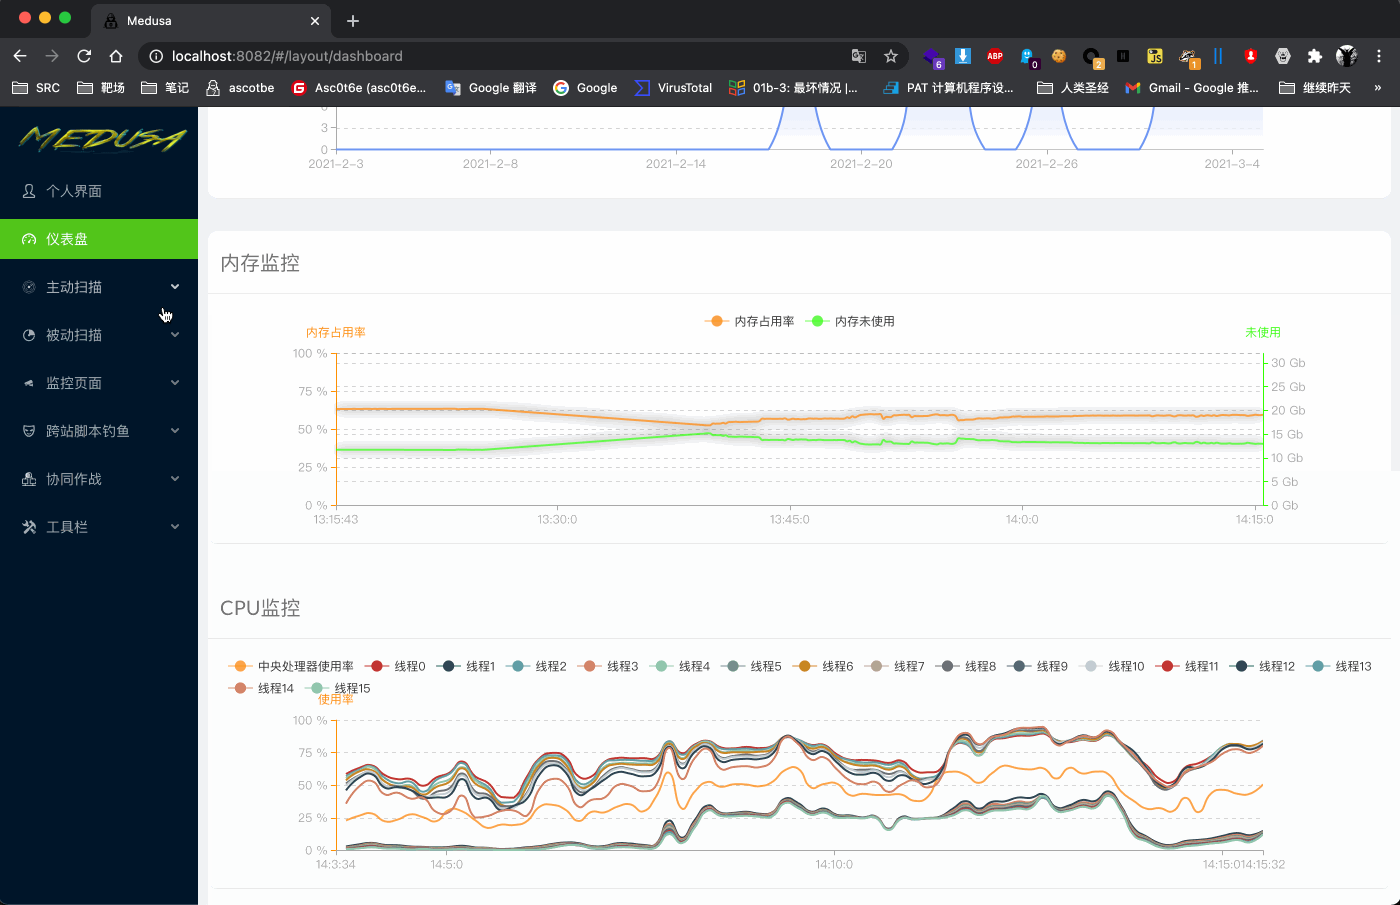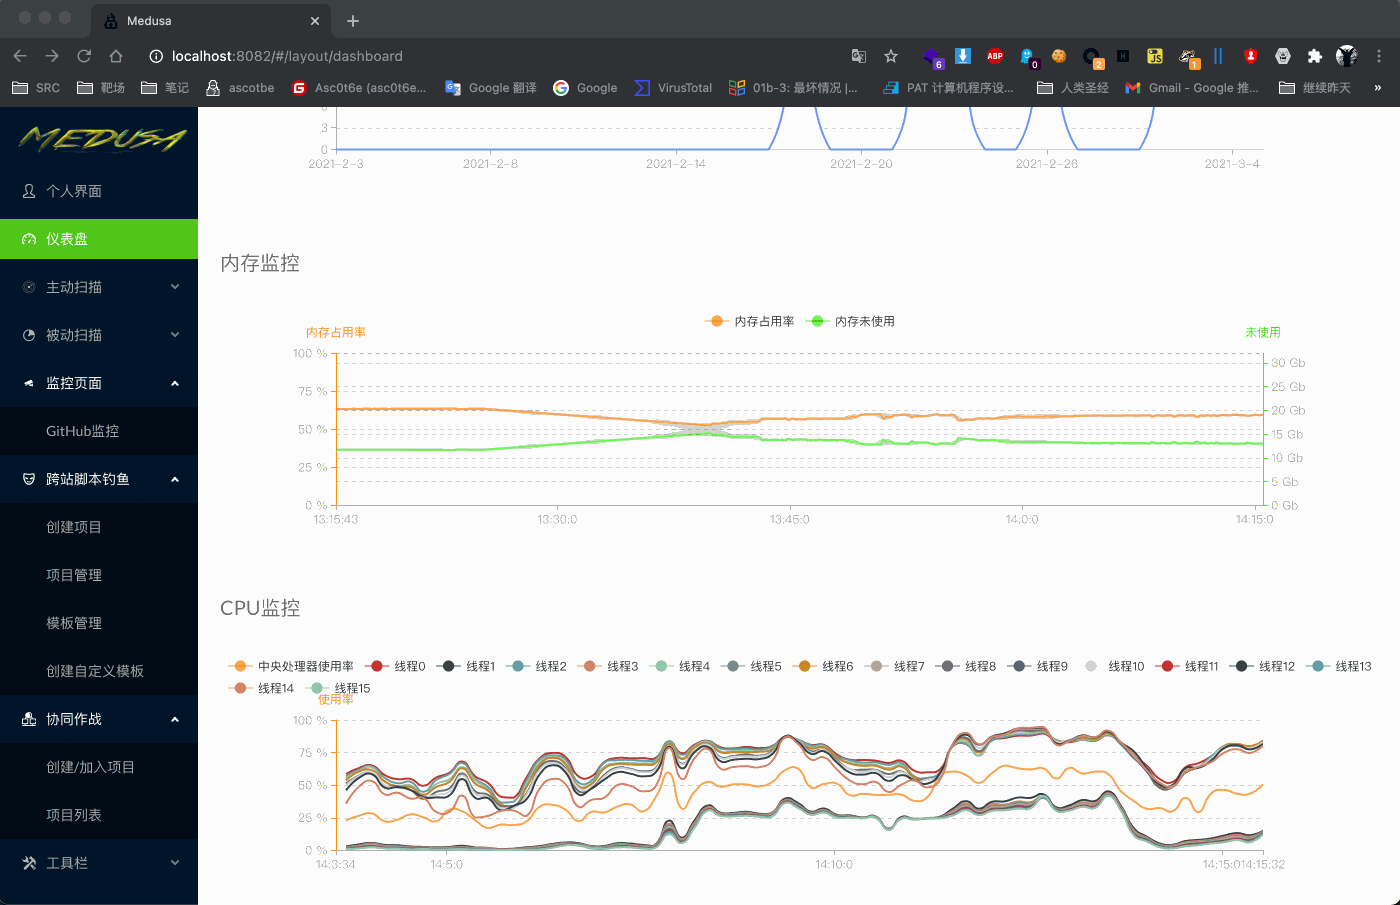
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
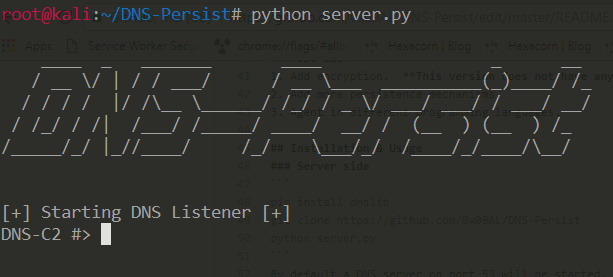 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
 besimorhino/powercat
netshell features all in version 2 powershell
 f0ng/log4j2burpscanner
CVE-2021-44228 Log4j2 BurpSuite Scanner,Customize ceye.io api or other apis,including internal networks
 rtfmkiesel/goldig
Execute commands on Windows via malicious TXT DNS records
 sensepost/dns-shell
DNS-Shell is an interactive Shell over DNS channel
 ahhh/reverse_dns_shell
A python reverse shell that uses DNS as the c2 channel
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
 bigsizeme/log4j-check
log4J burp被扫插件、CVE-2021-44228、支持dnclog.cn和burp内置DNS、可配合JNDIExploit生成payload
 satchfunky/cve-2026-41096-poc
windows api bug