

Hodometer
 gary23w/hodometer
A single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
defensive-toolsdns-analysisforensics+5
1
gary23w/hodometerA single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
 activecm/passer
Passive service locator, a python sniffer that identifies servers, clients, names and much more
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 cisagov/findcdn
Scans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
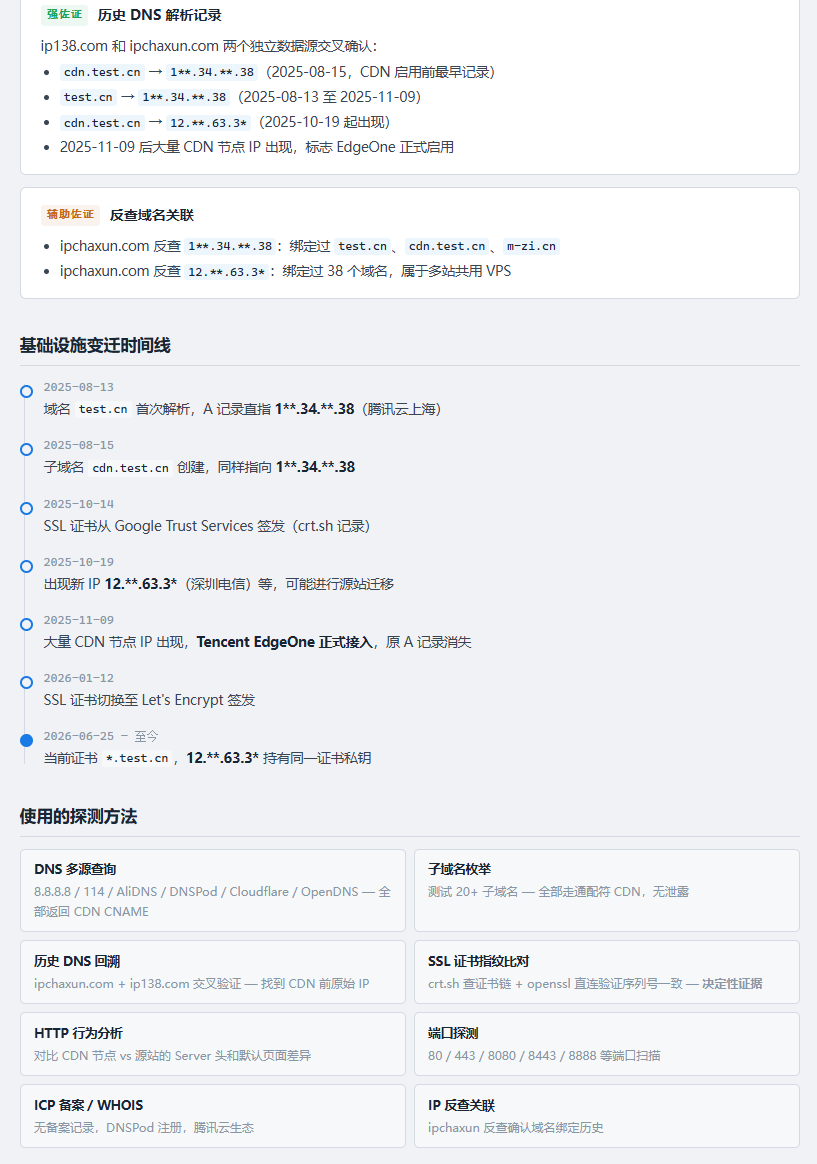 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
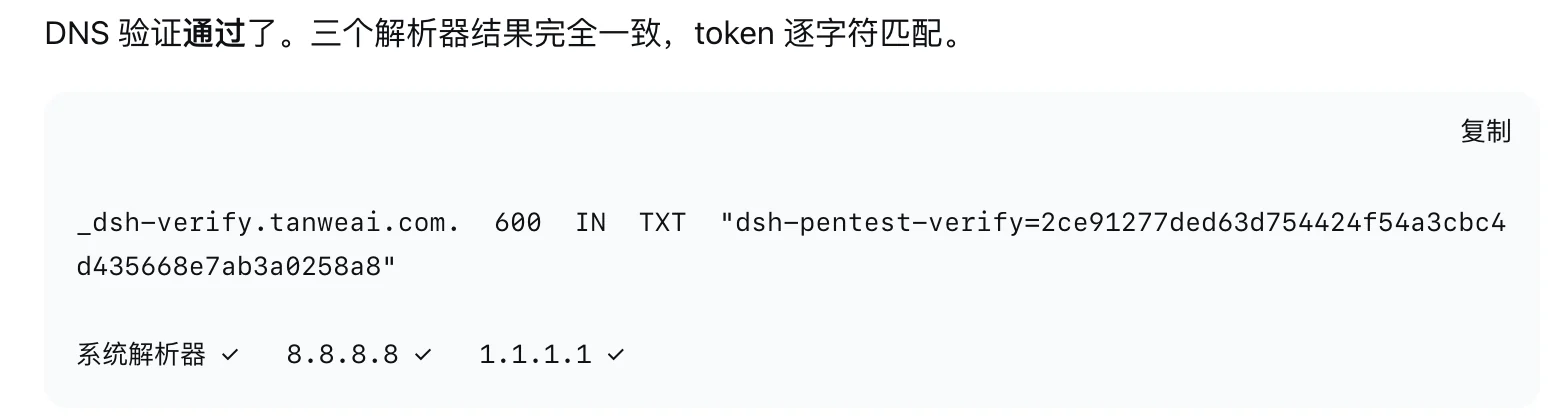 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 nicmx/fort-validator
RPKI Relying Party and RTR server that validates BGP route origin authorizations and serves validated data to routers over the RTR protocol.
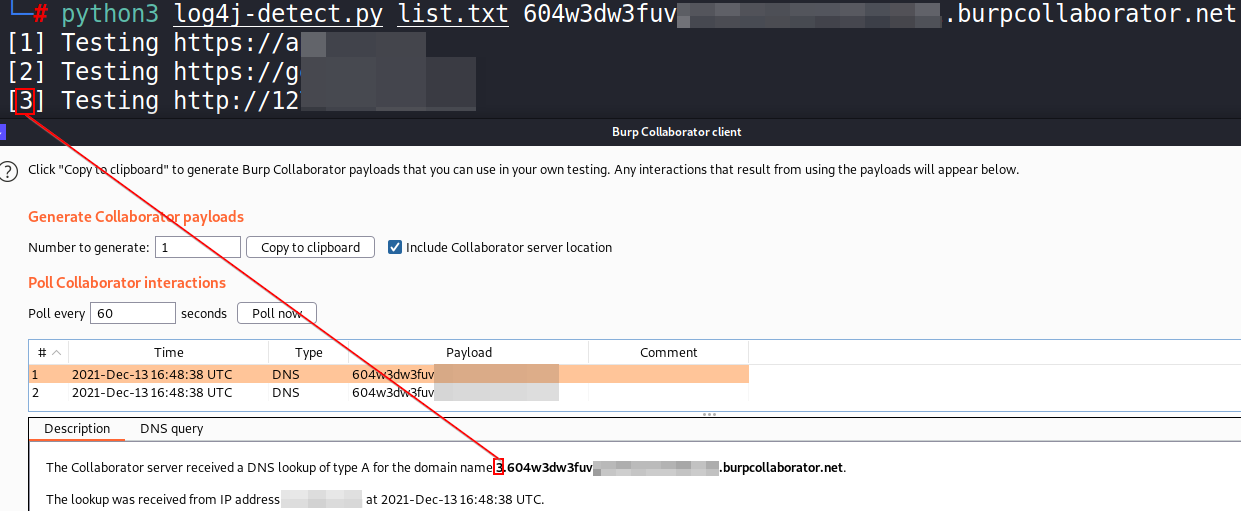 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 bluedragonsecurity/cve-2026-27831-poc
Poc Exploit for CVE-2026-27831 - vulnerability discovered by : Antonius
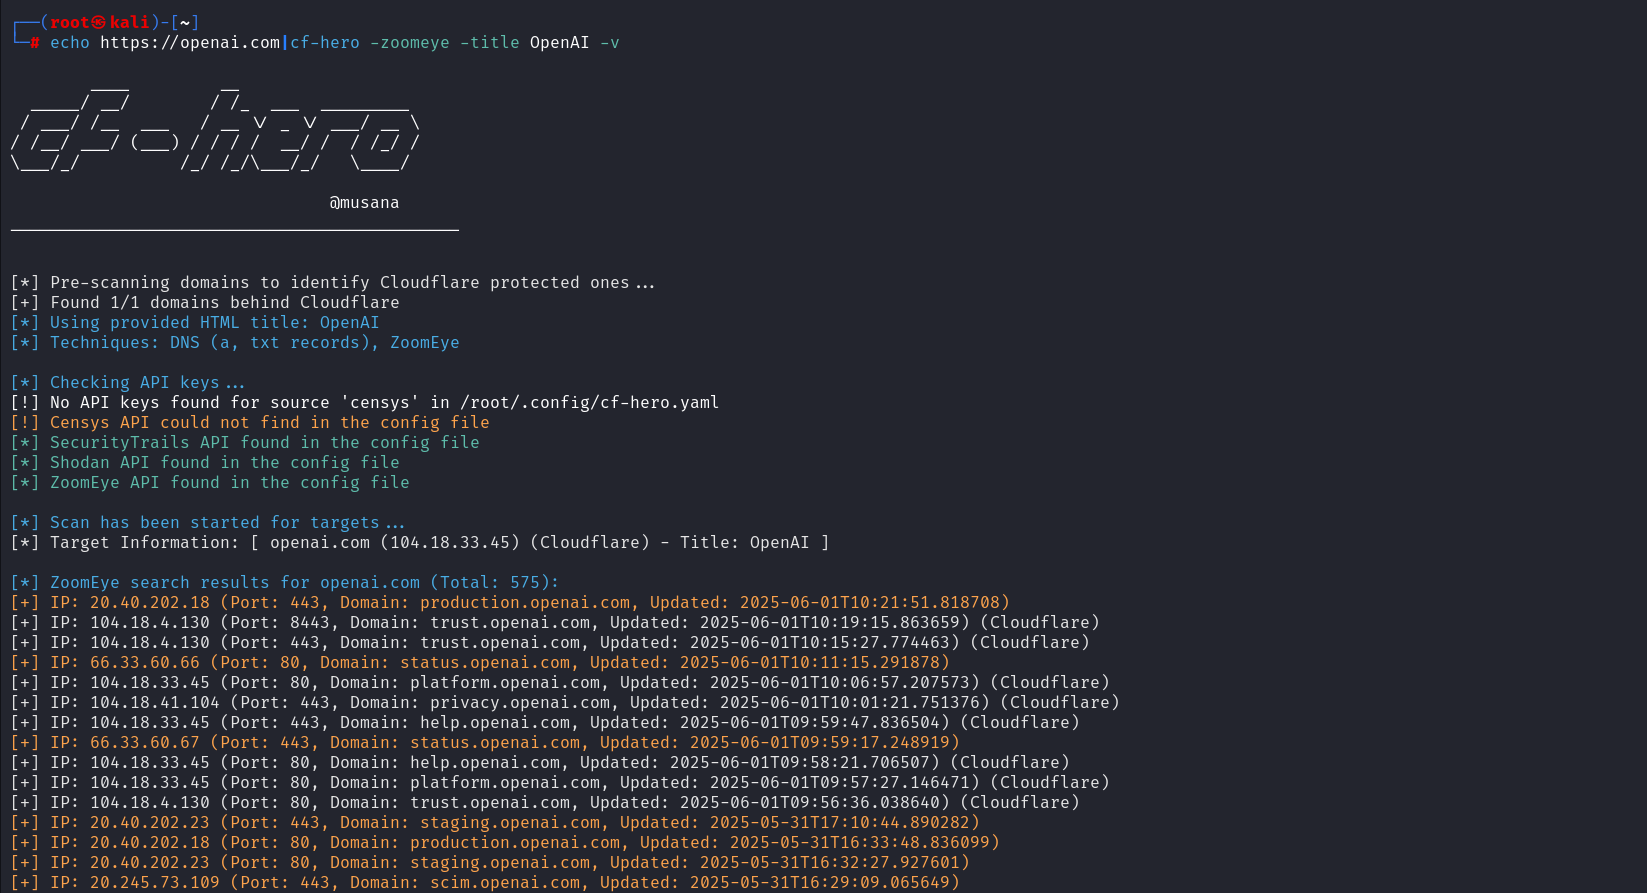 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 bishopfox/spoofcheckselftest
Web application that lets you test if your domain is vulnerable to email spoofing
 haad/proxychains
proxychains - a tool that forces any TCP connection made by any given application to follow through proxy like TOR or any other SOCKS4, SOCKS5 or…