

Dshell
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
usarmyresearchlab/dshellDshell is a network forensic analysis framework.

 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
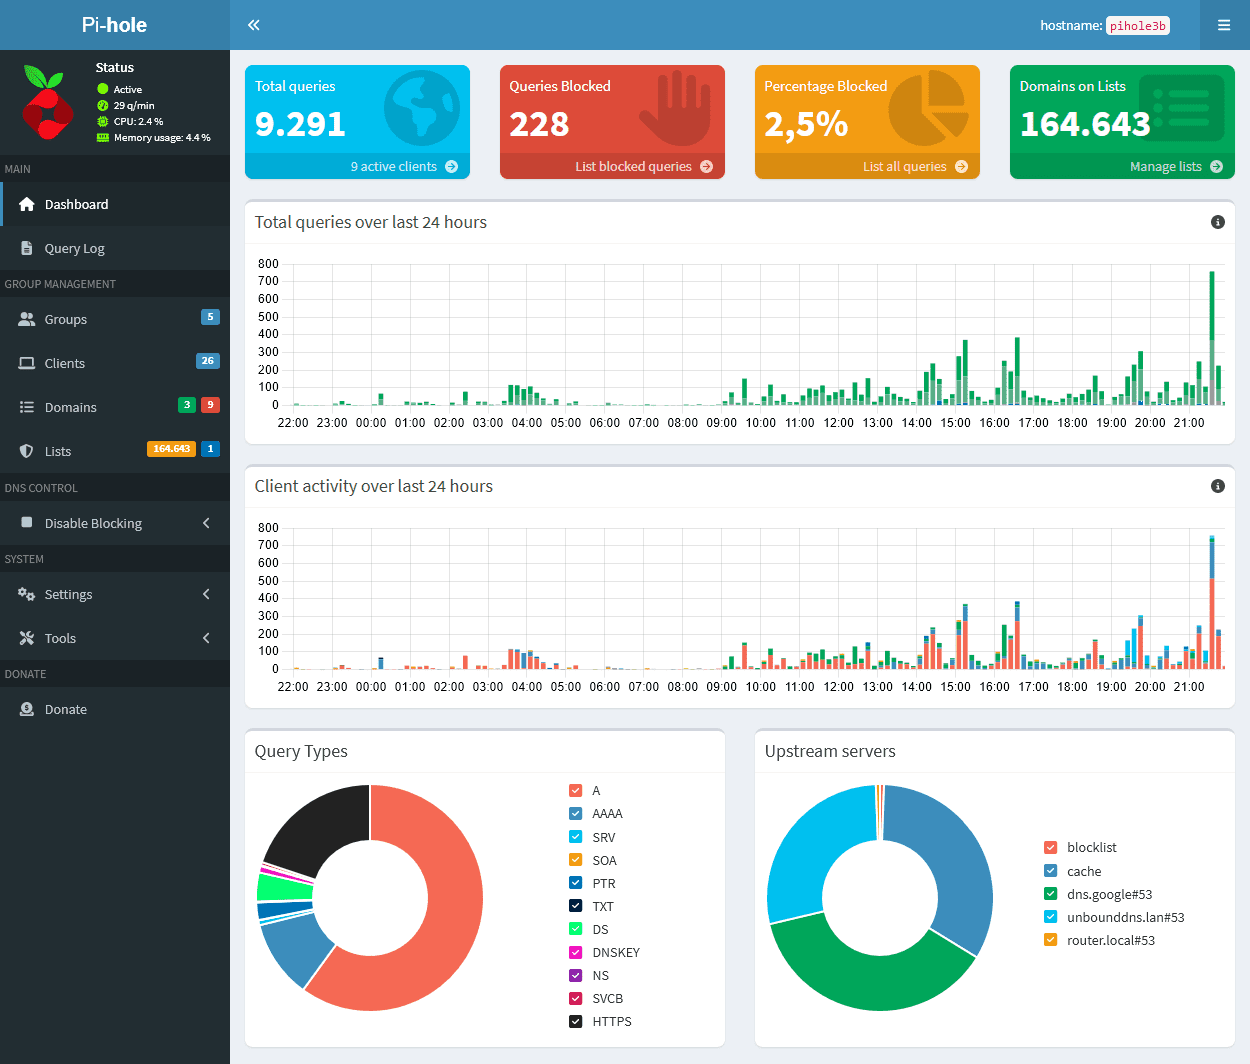

 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
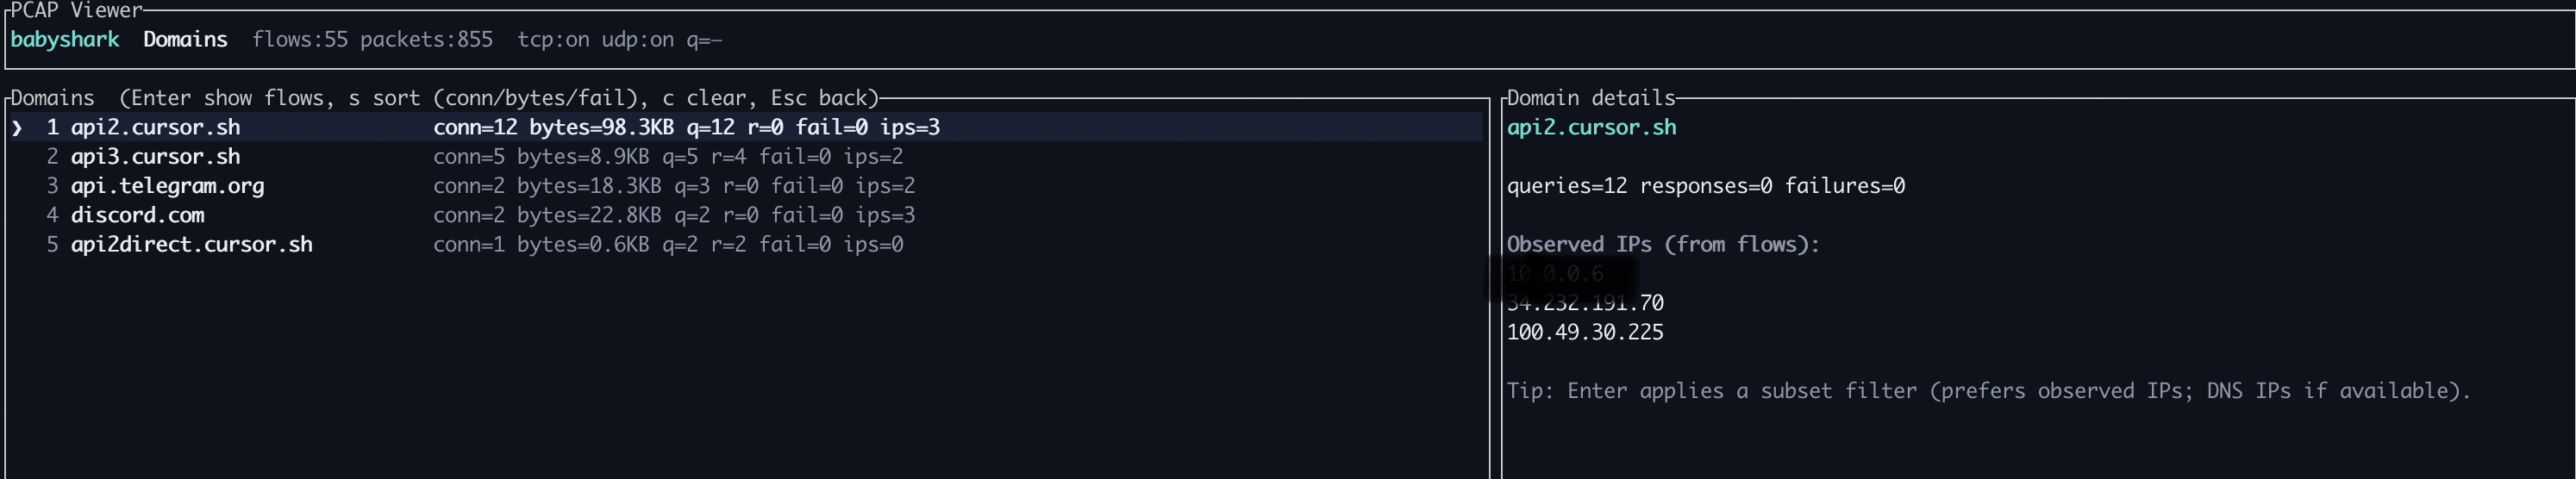 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
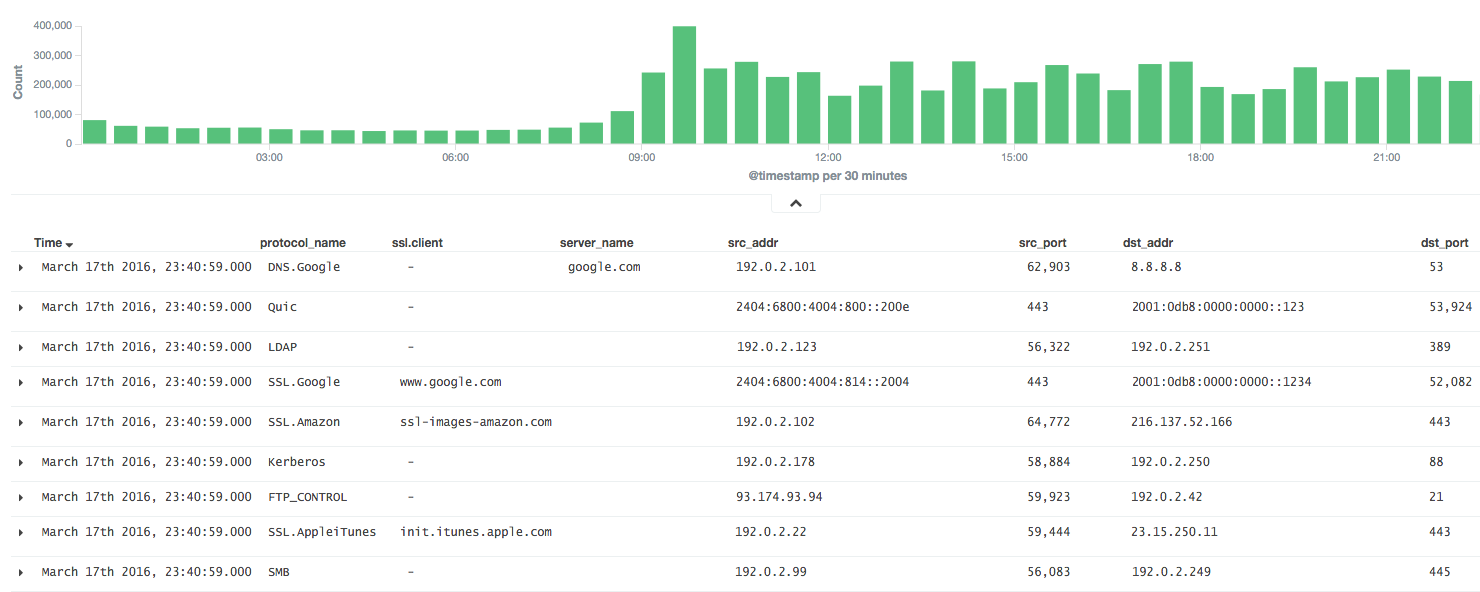 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 trinadh465/external_tcpdump_cve-2018-14880
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14469
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14879
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 korc/pr-dnsd
Passive-recursive DNS daemon that logs all DNS queries and responses, enabling network visibility, EDR/IR log enrichment, and passive DNS data…