Judge-Jury-and-Executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.

PoC, IOCs, and detection logic for the SharePoint /_trust WS-Federation BinaryFormatter deserialization chain. Lab reconstruction covering…

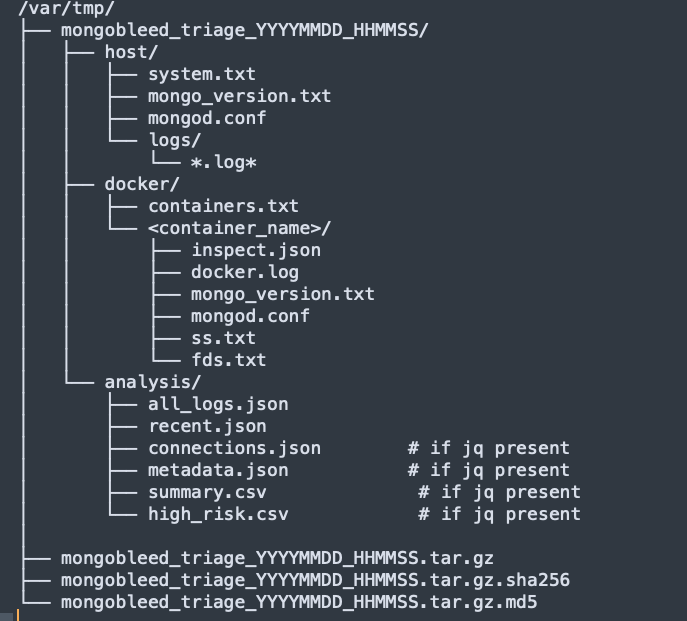
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

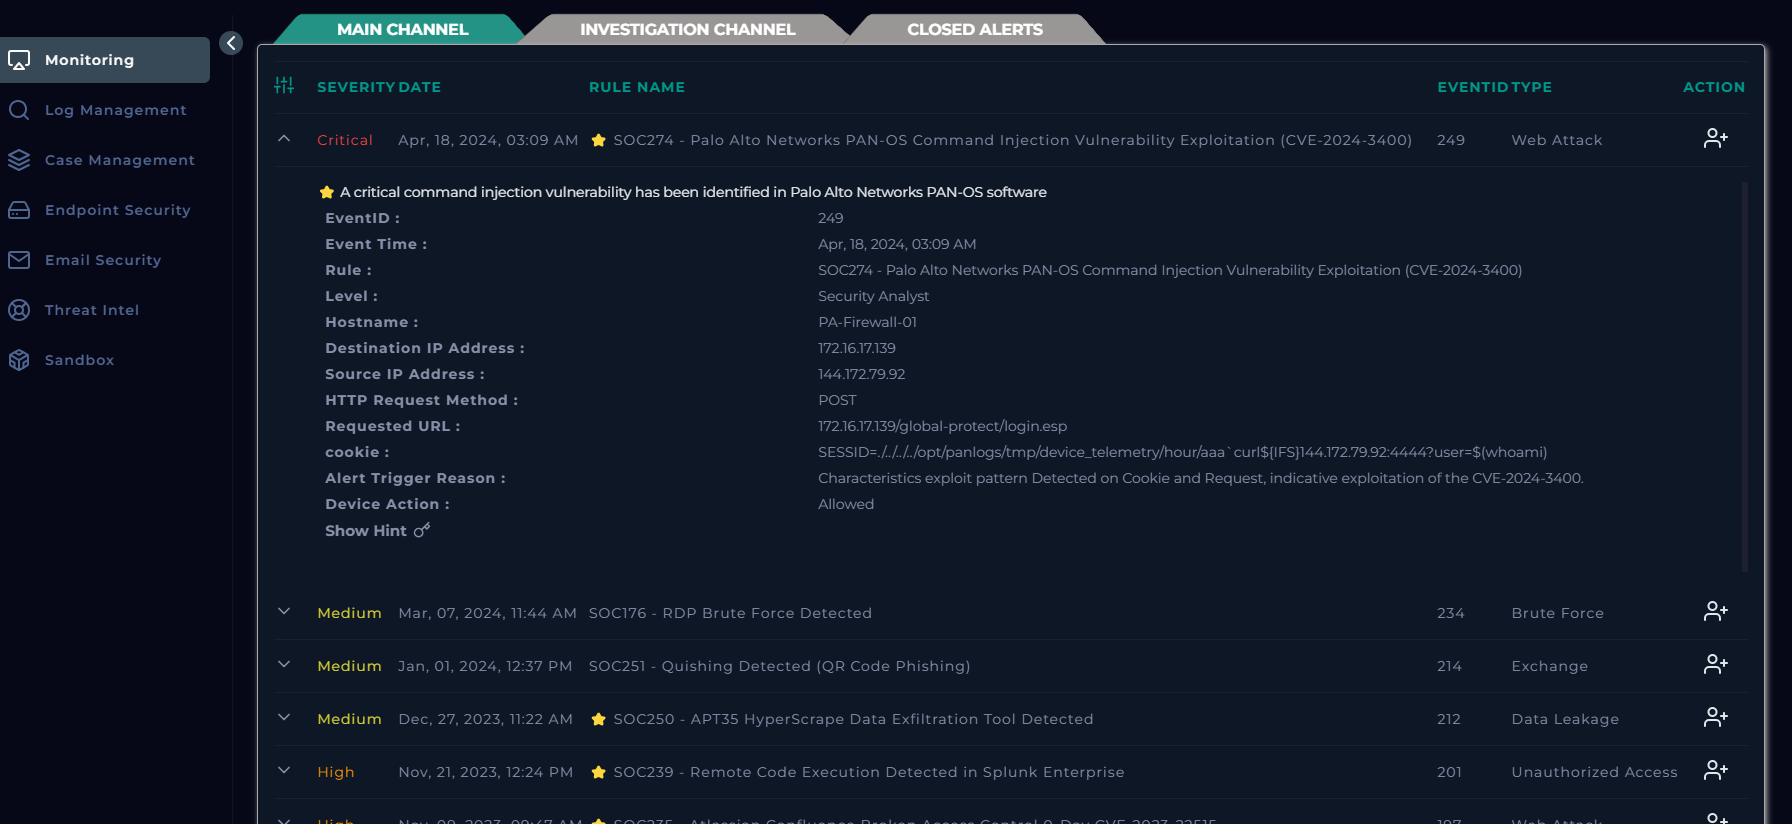
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)

This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819

Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack

Exploit for Joomla CVE-2015-8562 combined with Linux forensic analysis capabilities for post-exploitation investigation and evidence collection.

TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…


Detection Script for MongoBleed Exploitation

Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database