Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
337 results
CitrixNetscalerAnalysis preview

CitrixNetscalerAnalysis

GitHubl4r1k/citrixnetscaleranalysis

🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781
curated-resourcesdigital-forensicseducation+5
6 years ago
rip_raw preview
Archived

rip_raw

GitHubcado-security/rip_raw

Rip Raw is a small tool to analyse the memory of compromised Linux systems.
data-recoverydigital-forensicsforensics+3
133
androidqf preview

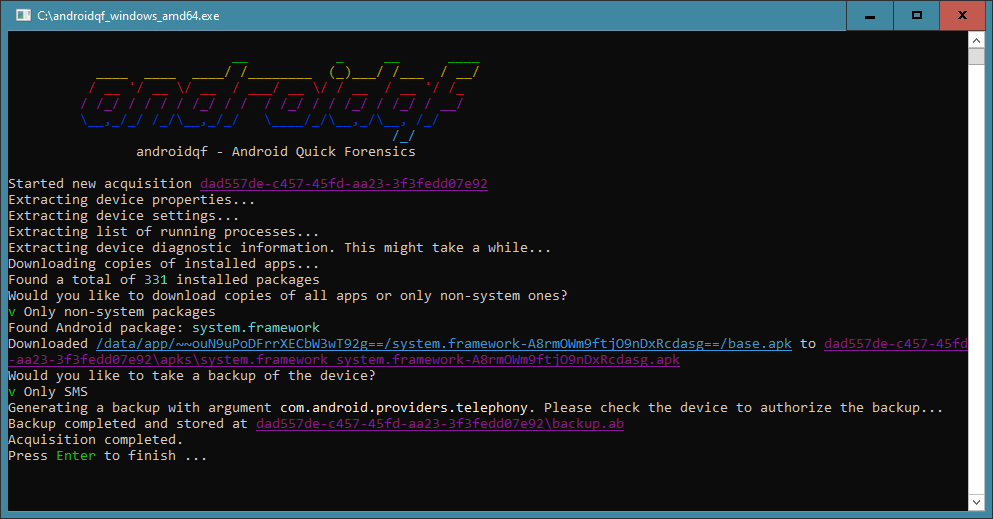
androidqf

GitHubmvt-project/androidqf

androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
27314 days ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8462 months ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1211 year ago
mailMeta preview

mailMeta

GitHubgr33nm0nk2802/mailmeta

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
1755 years ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
SnipRecover-CLI preview

SnipRecover-CLI

GitHubm31r0n/sniprecover-cli

Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303

binary-analysisdata-recoverydigital-forensics+3
21 year ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

digital-forensicsforensicsincident-response+4
2188 years ago
CVE-2025-57819-ioc-check preview
Archived

CVE-2025-57819-ioc-check

GitHubsucuri-labs/cve-2025-57819-ioc-check

This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819

digital-forensicsforensicsincident-response+3
1 year ago
FACT preview

FACT

GitHubunicornunicode/fact

Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
cloud-securitydigital-forensicsforensics
173 years ago
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.

digital-forensicsforensicsincident-response+1
3472 years ago
ForensicMiner preview

ForensicMiner

GitHubsecurityjoes/forensicminer

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.

digital-forensicsdisk-forensicsforensics+2
1651 year ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8492 years ago
KNX-Bus-Dump preview

KNX-Bus-Dump

GitHubchrism09/knx-bus-dump

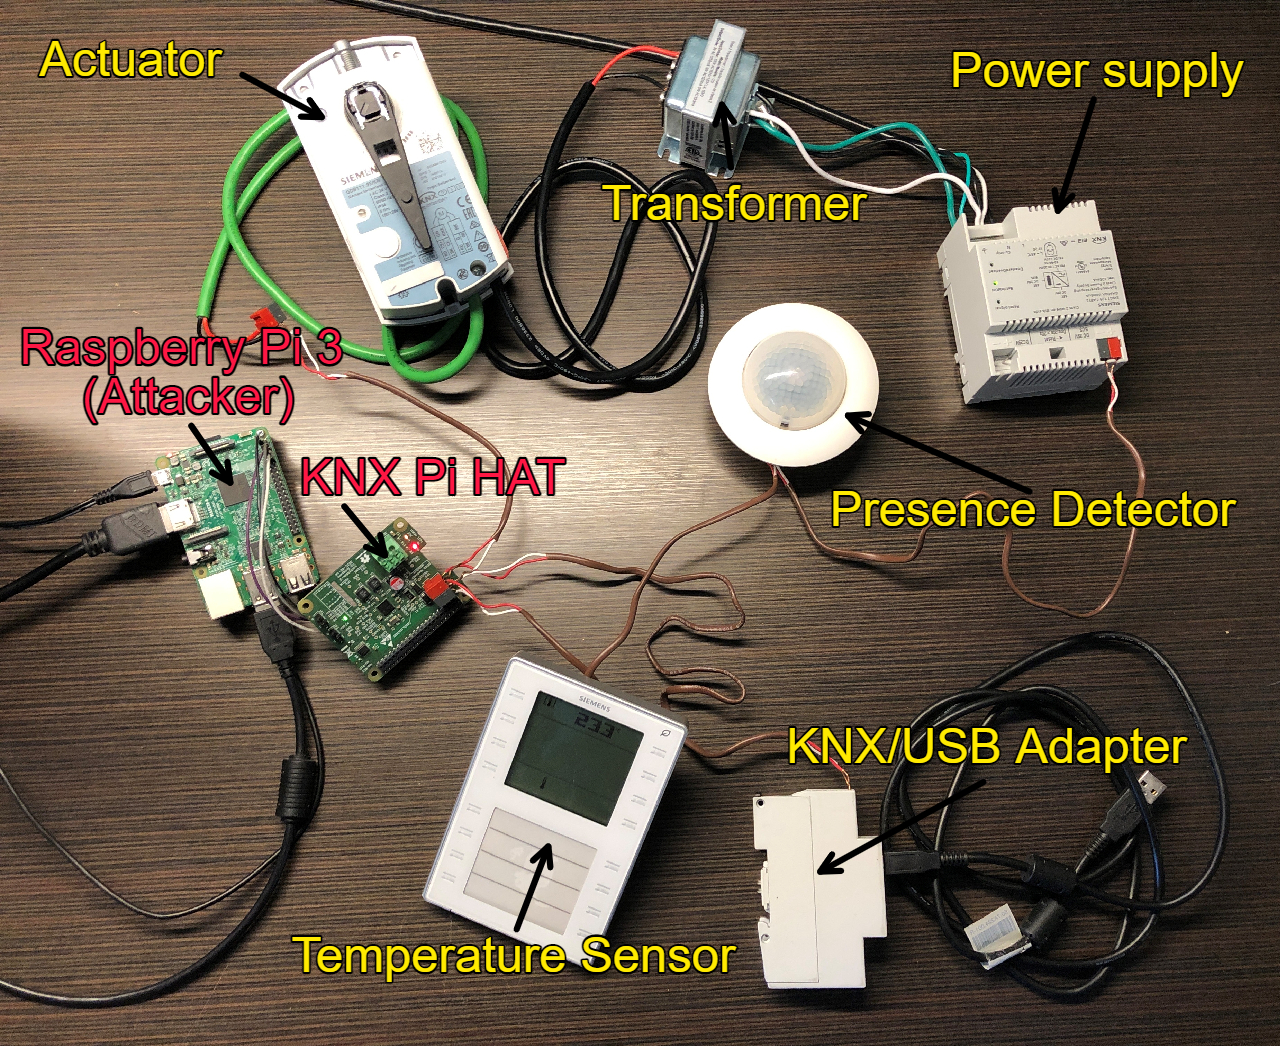
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
digital-forensicsforensicshardware-iot-security+3
124 years ago
XWFAcropalypse preview

XWFAcropalypse

GitHubpolitoinc/xwfacropalypse

X-Ways Acropalypse extension detects CVE-2023-21036 in common images
data-recoverydigital-forensicsexploitation+2
4 months ago
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

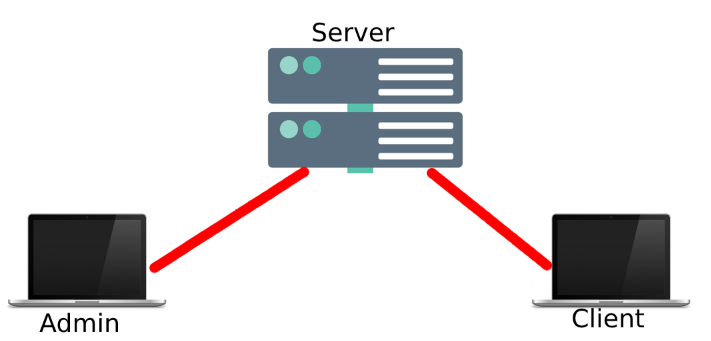
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
digital-forensicsforensicsincident-response+1
225 years ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

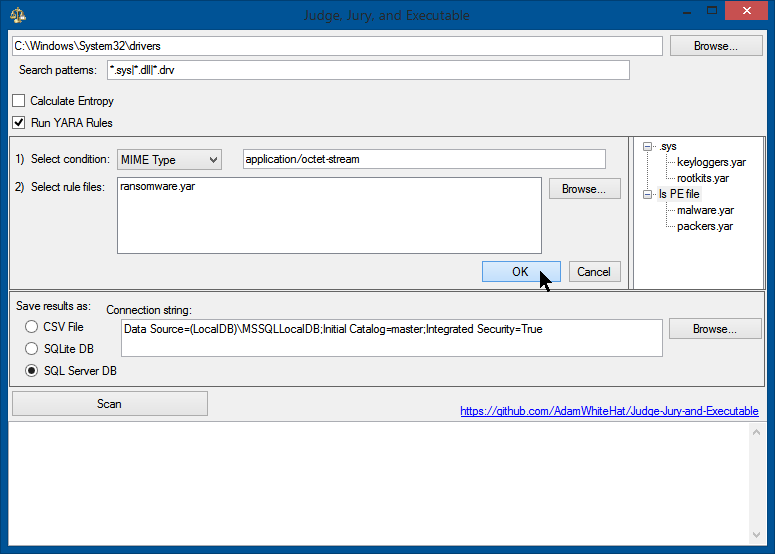
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
855 months ago
Previous12…19Next
4 years ago