Judge-Jury-and-Executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

Detection Script for MongoBleed Exploitation

Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…

Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…

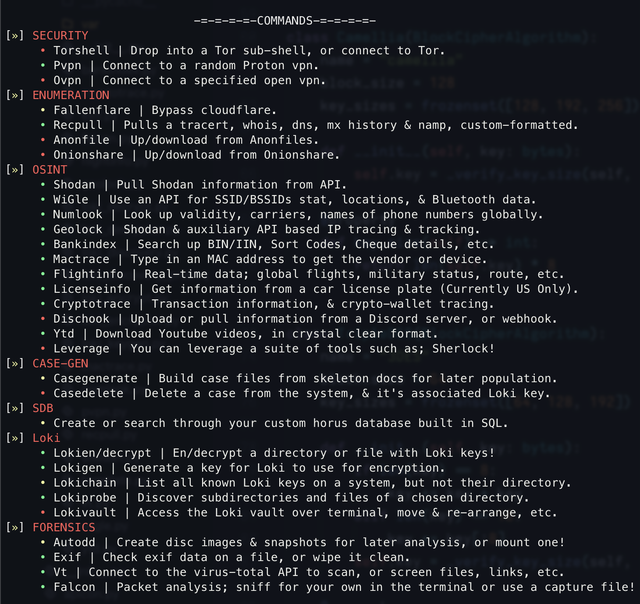
An OSINT / digital forensics tool built in Python

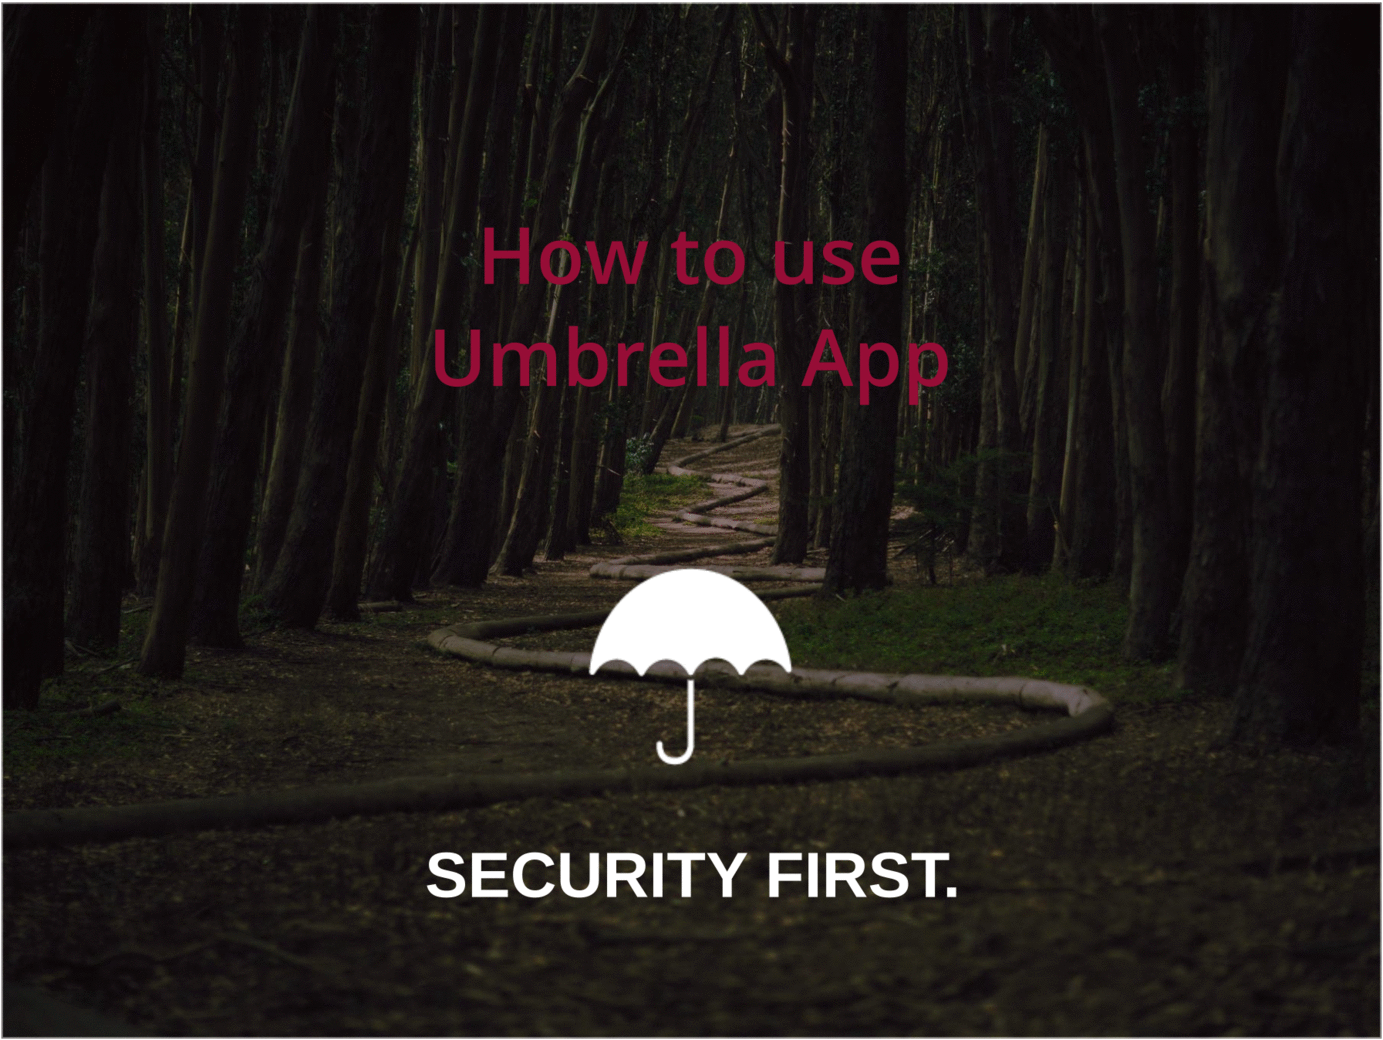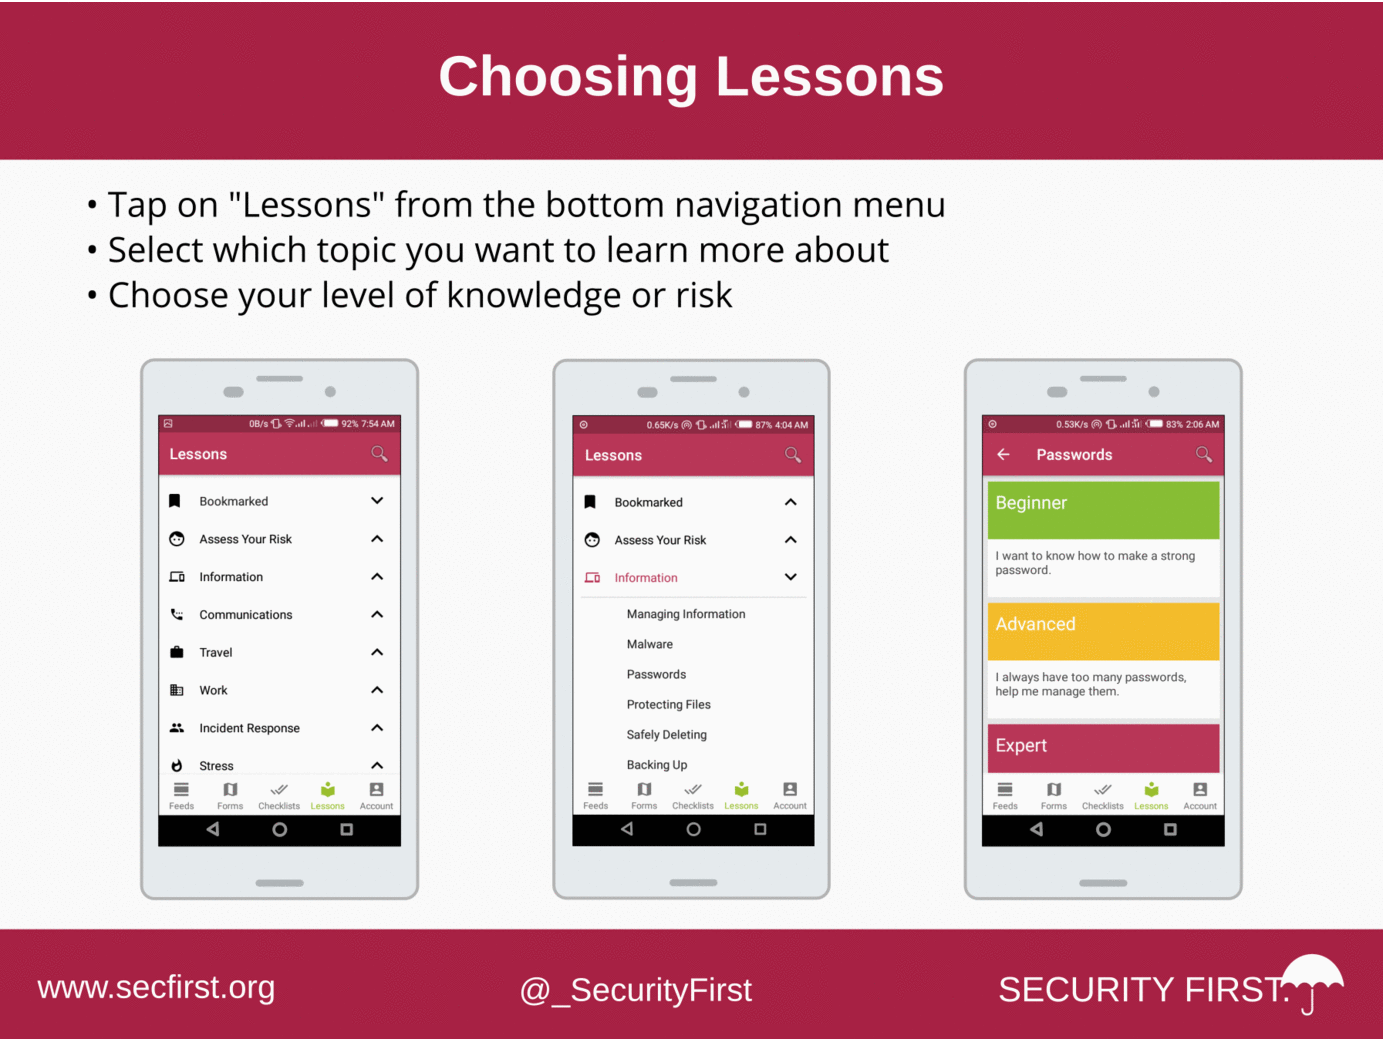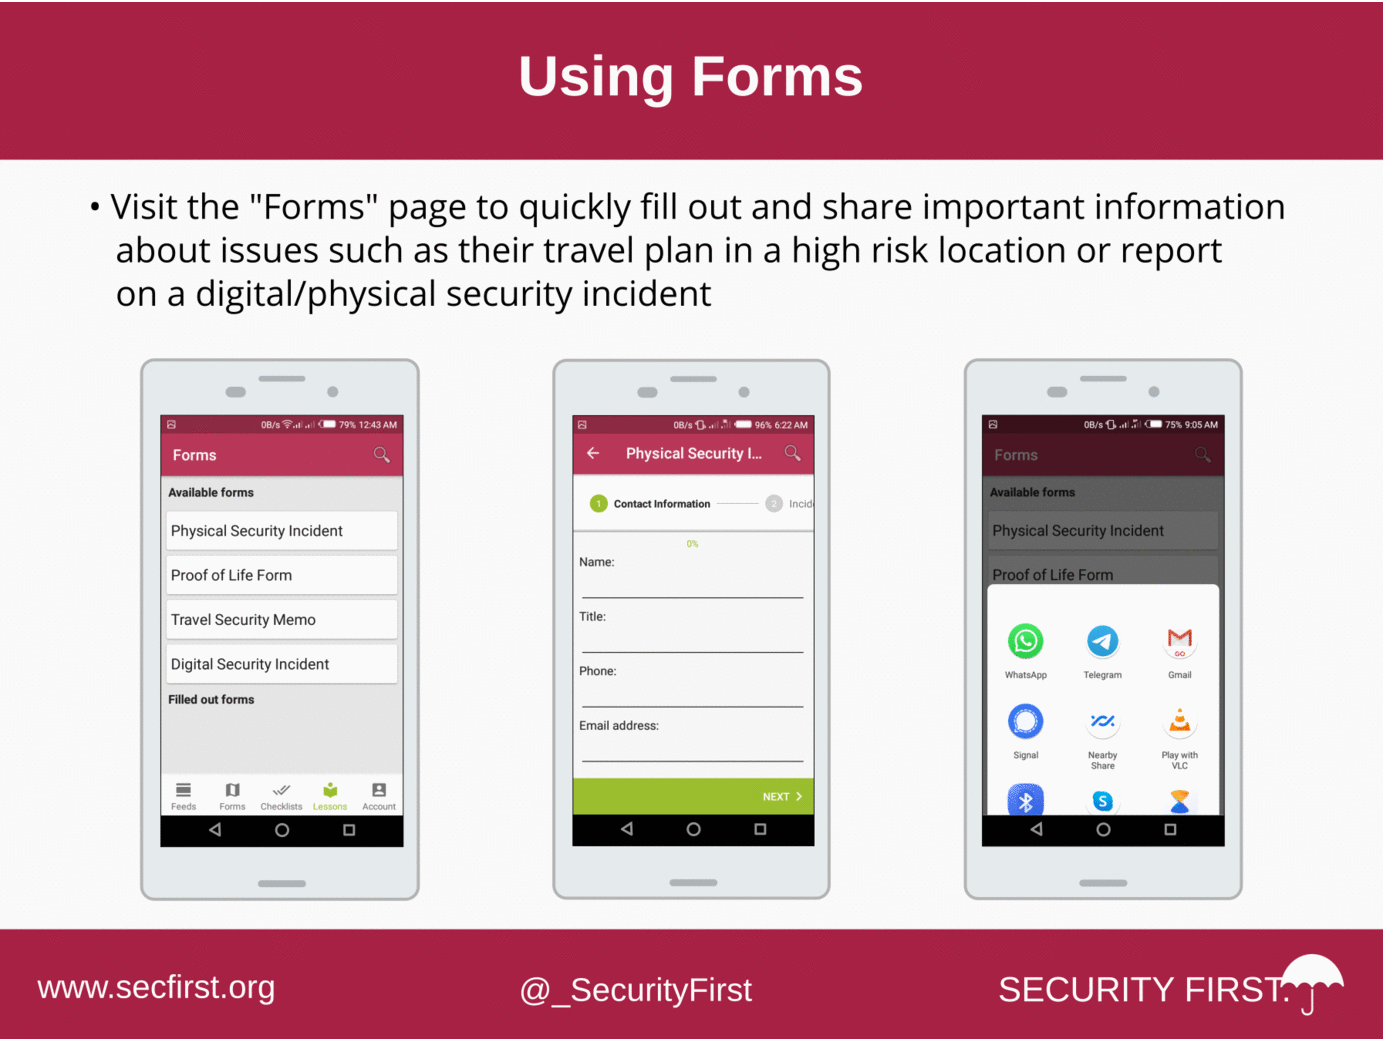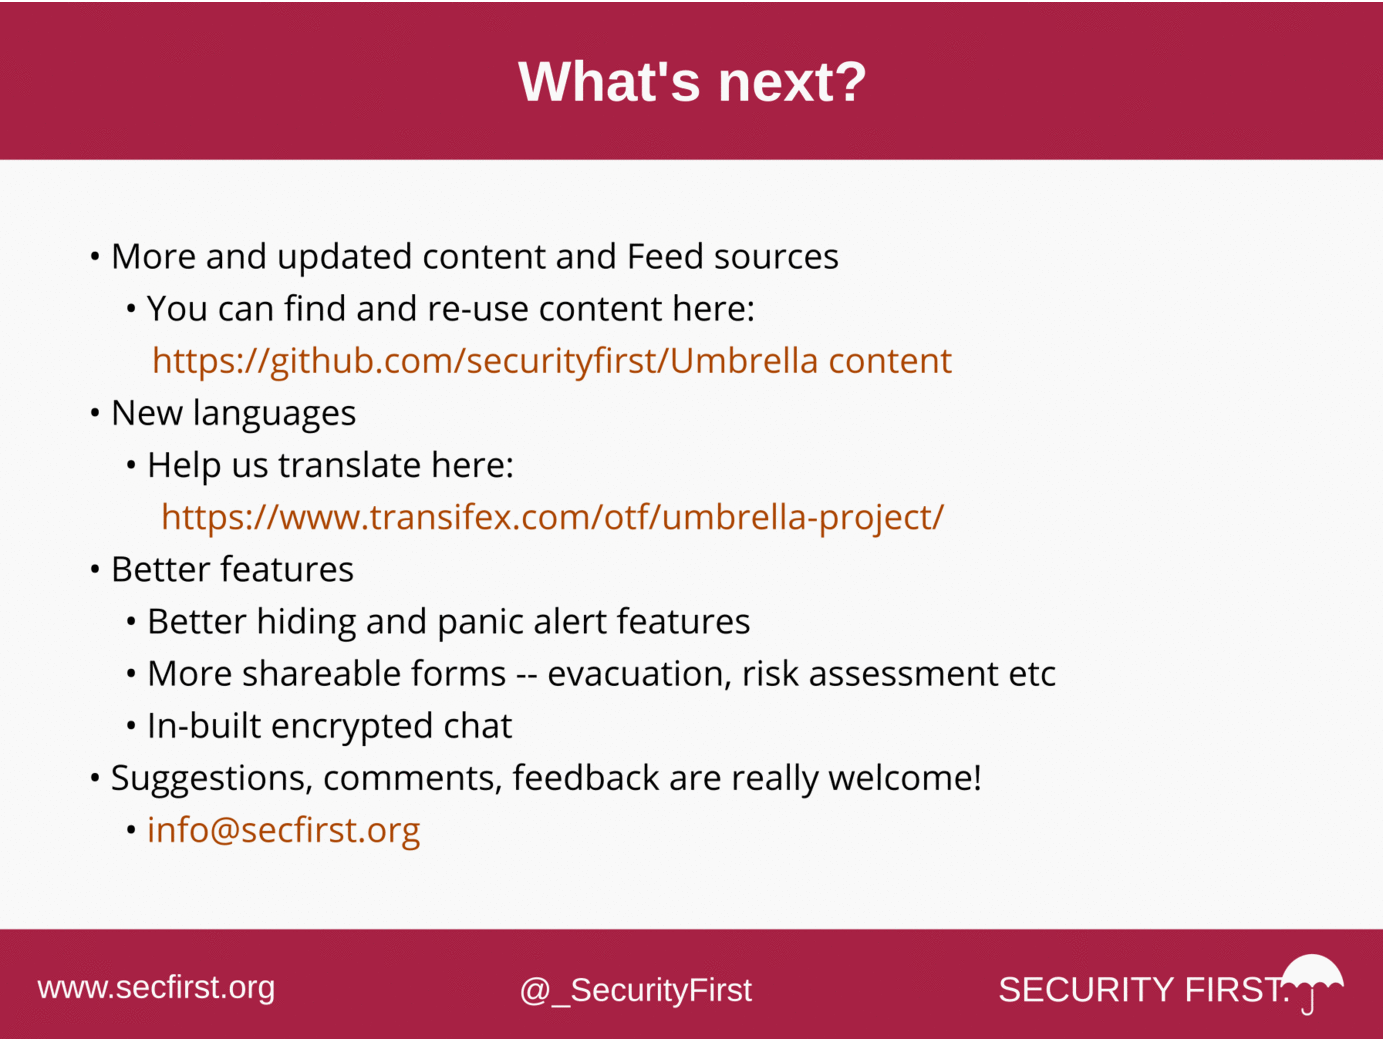
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…

Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…

Python DPAPI NG Decryptor for non-Windows Platforms

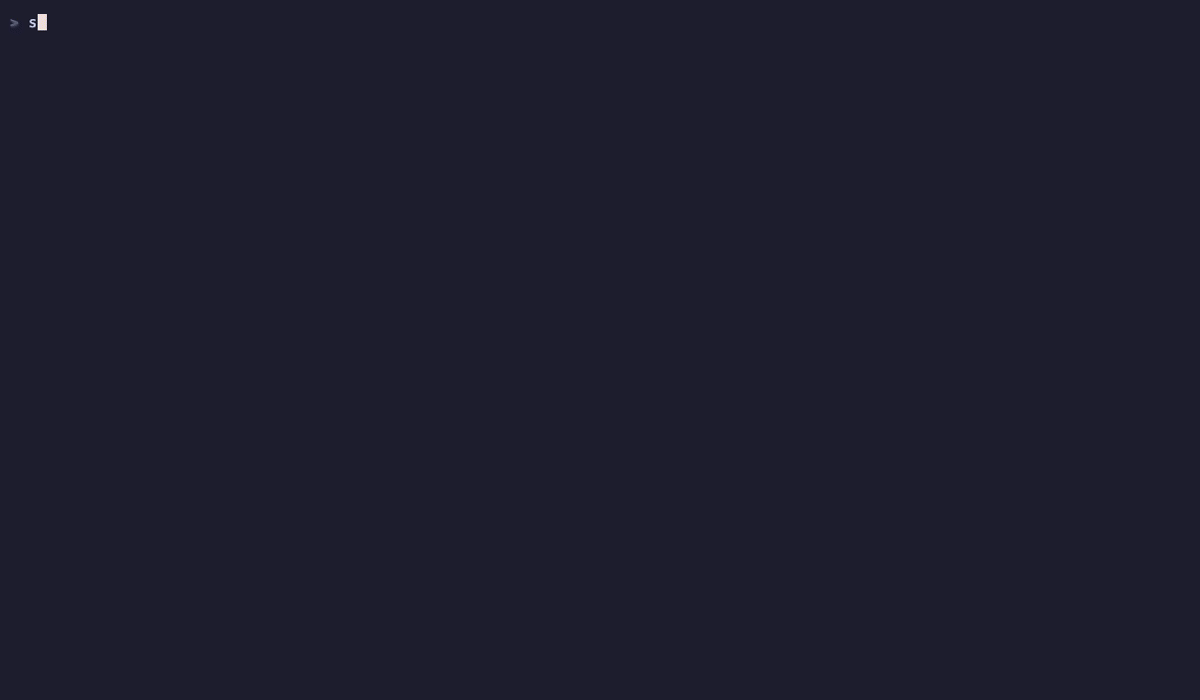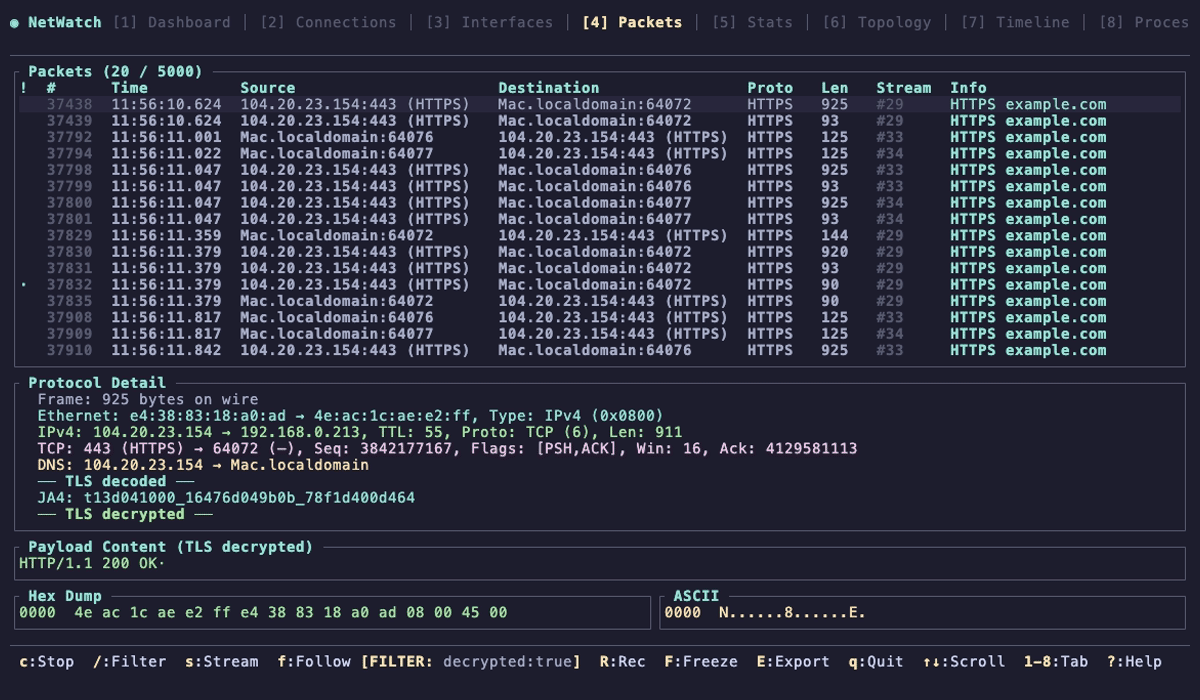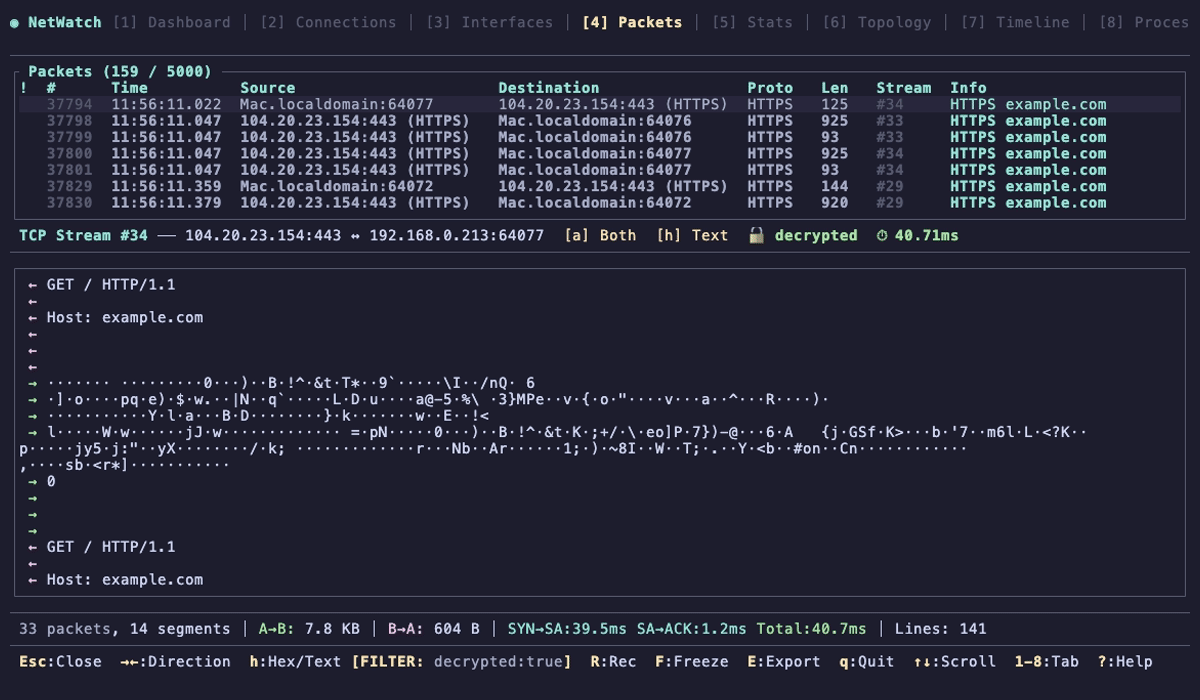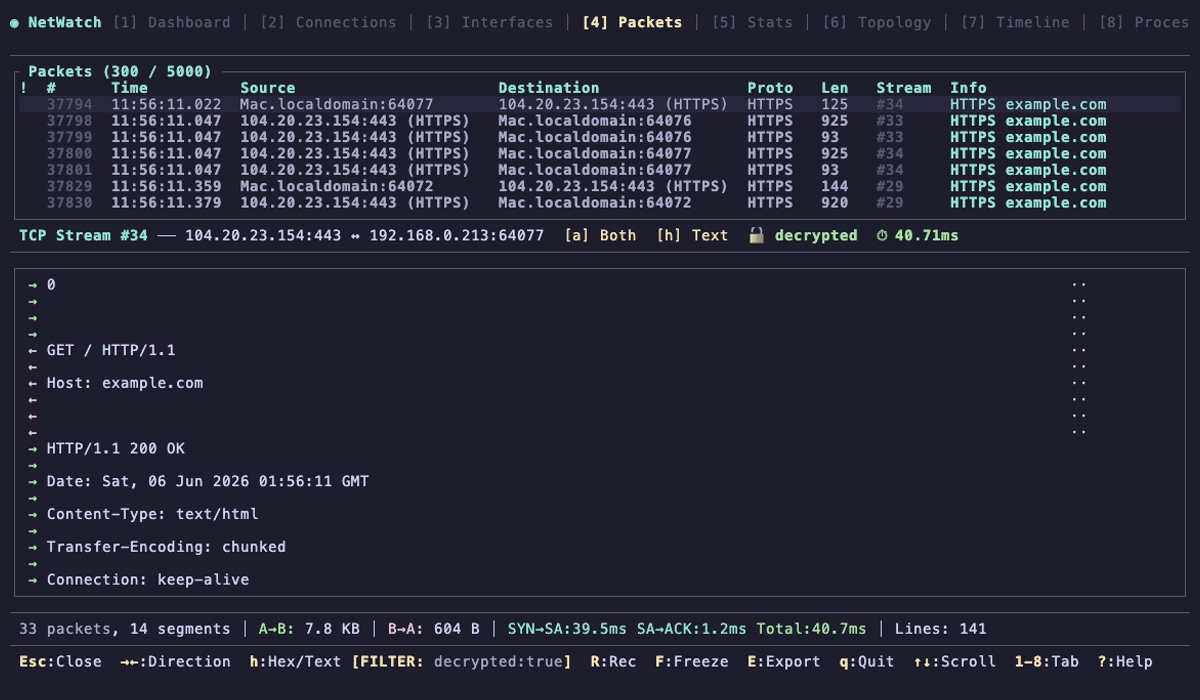
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.

Mimikatz implementation in pure Python

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.

OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…

Windows passwords decryption from dump files