MemProcFS-Analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

Incident Response collection and processing scripts with automated reporting scripts

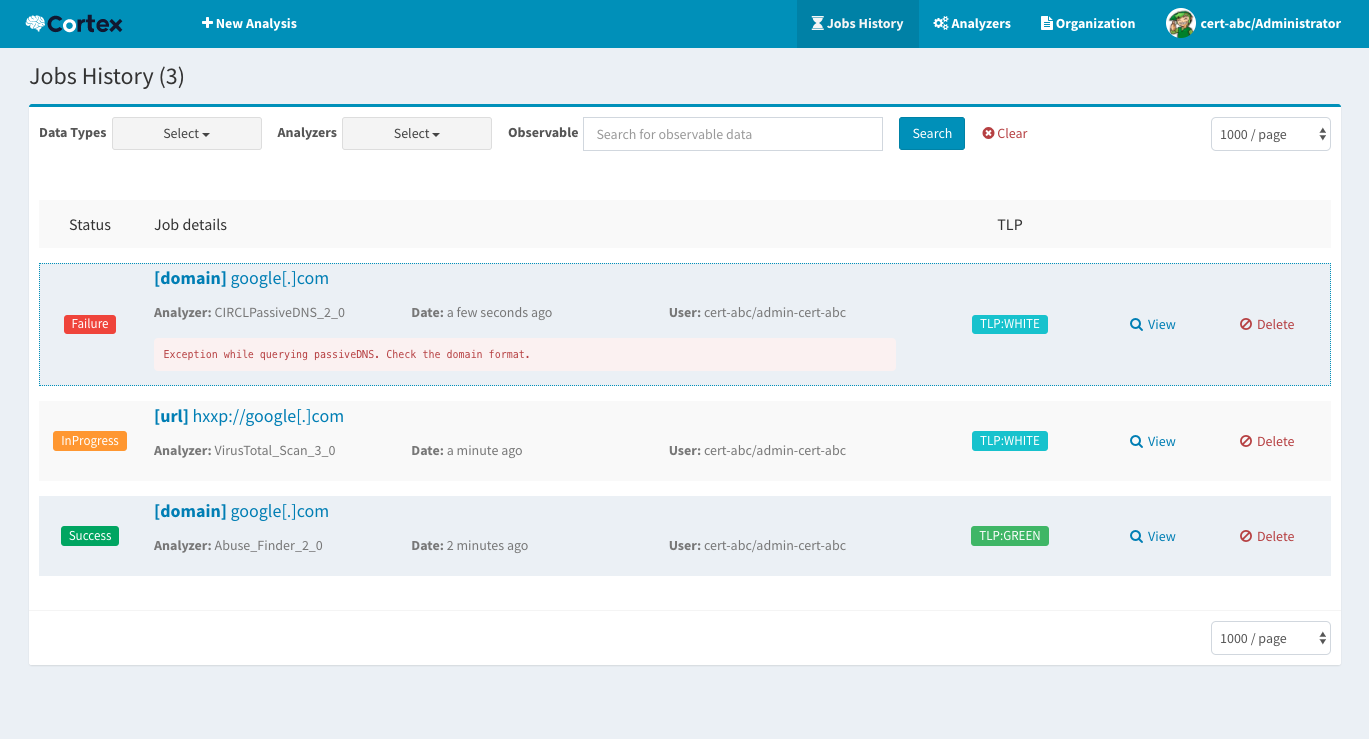
Cortex: a Powerful Observable Analysis and Active Response Engine

Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality

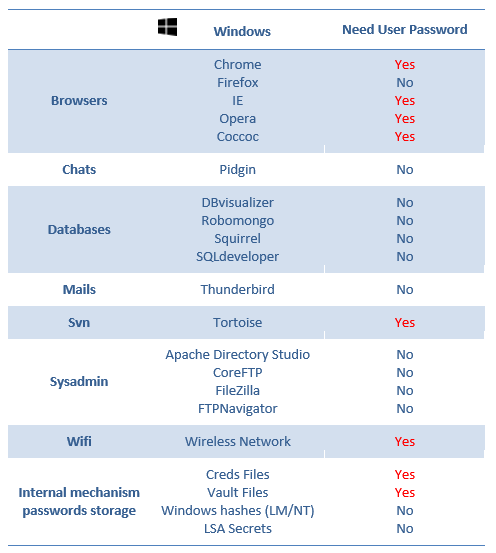
Windows passwords decryption from dump files

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Technical analysis of a multi-stage Adobe Acrobat PDF JavaScript sample, detailing environment triage, Acrobat API abuse, and in-memory payload…

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Credential and sensitive-data exposure triage for file shares

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

A collection of awesome software, libraries, documents, books, resources and cools stuffs about security.

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

YARA signature and IOC database for my scanners and tools

Investigate malicious Windows logon by visualizing and analyzing Windows event log

Android Logs Events And Protobuf Parser

Automation and Scaling of Digital Forensics Tools

Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.