
imaginaryC2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

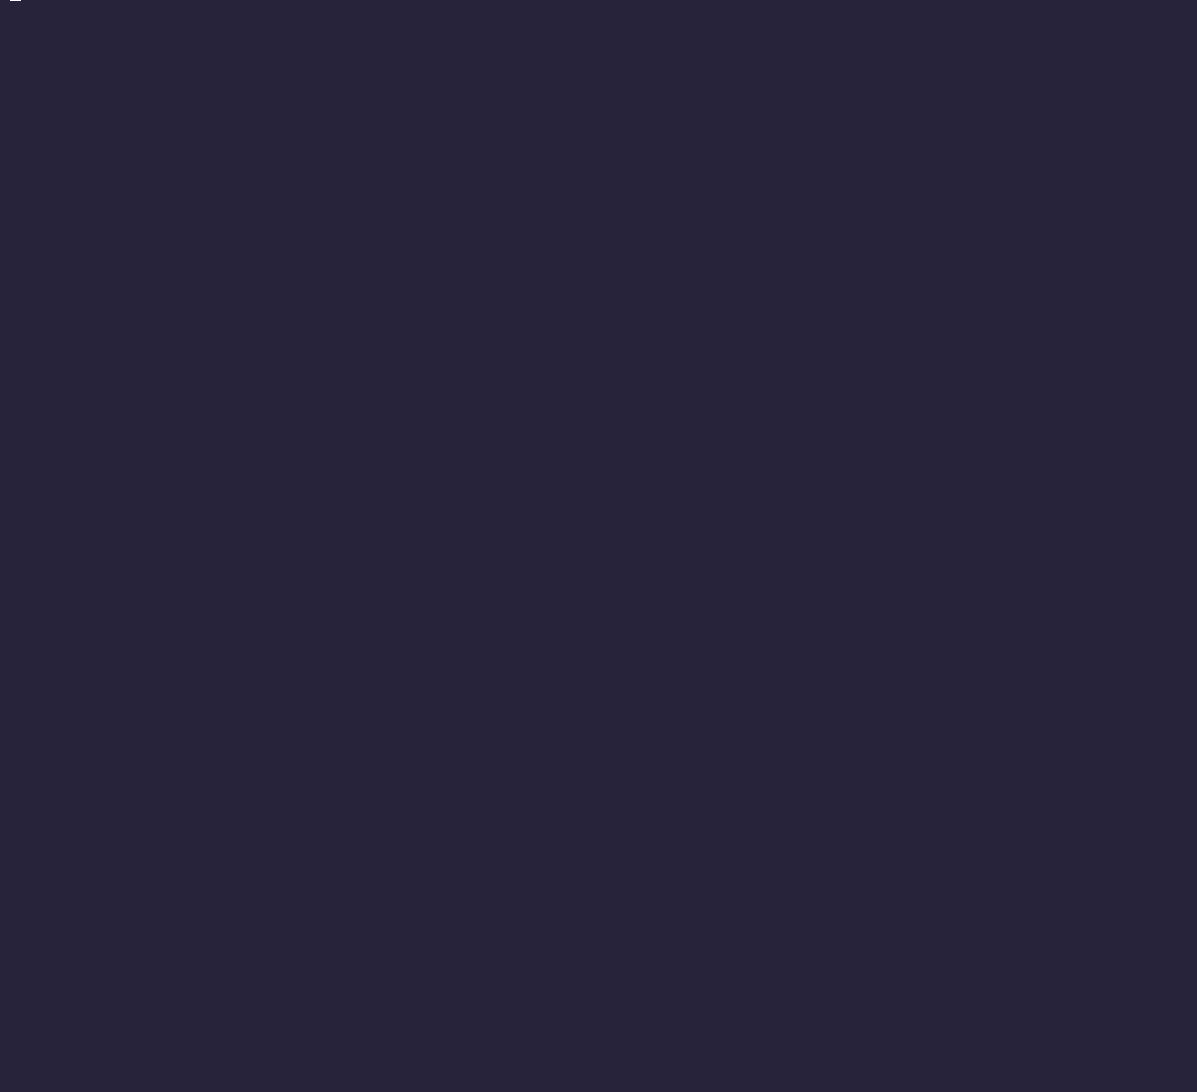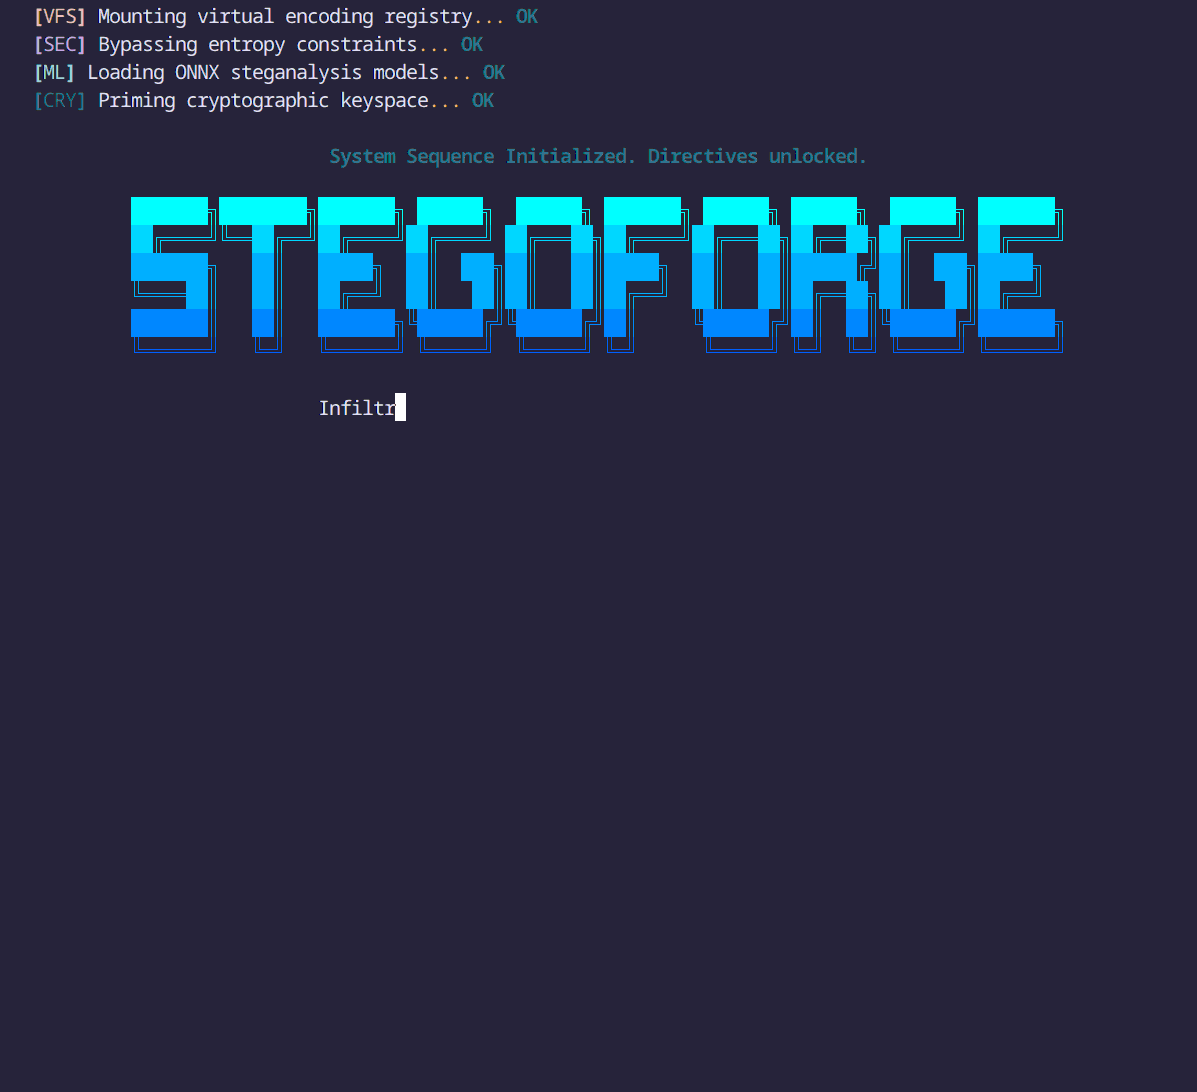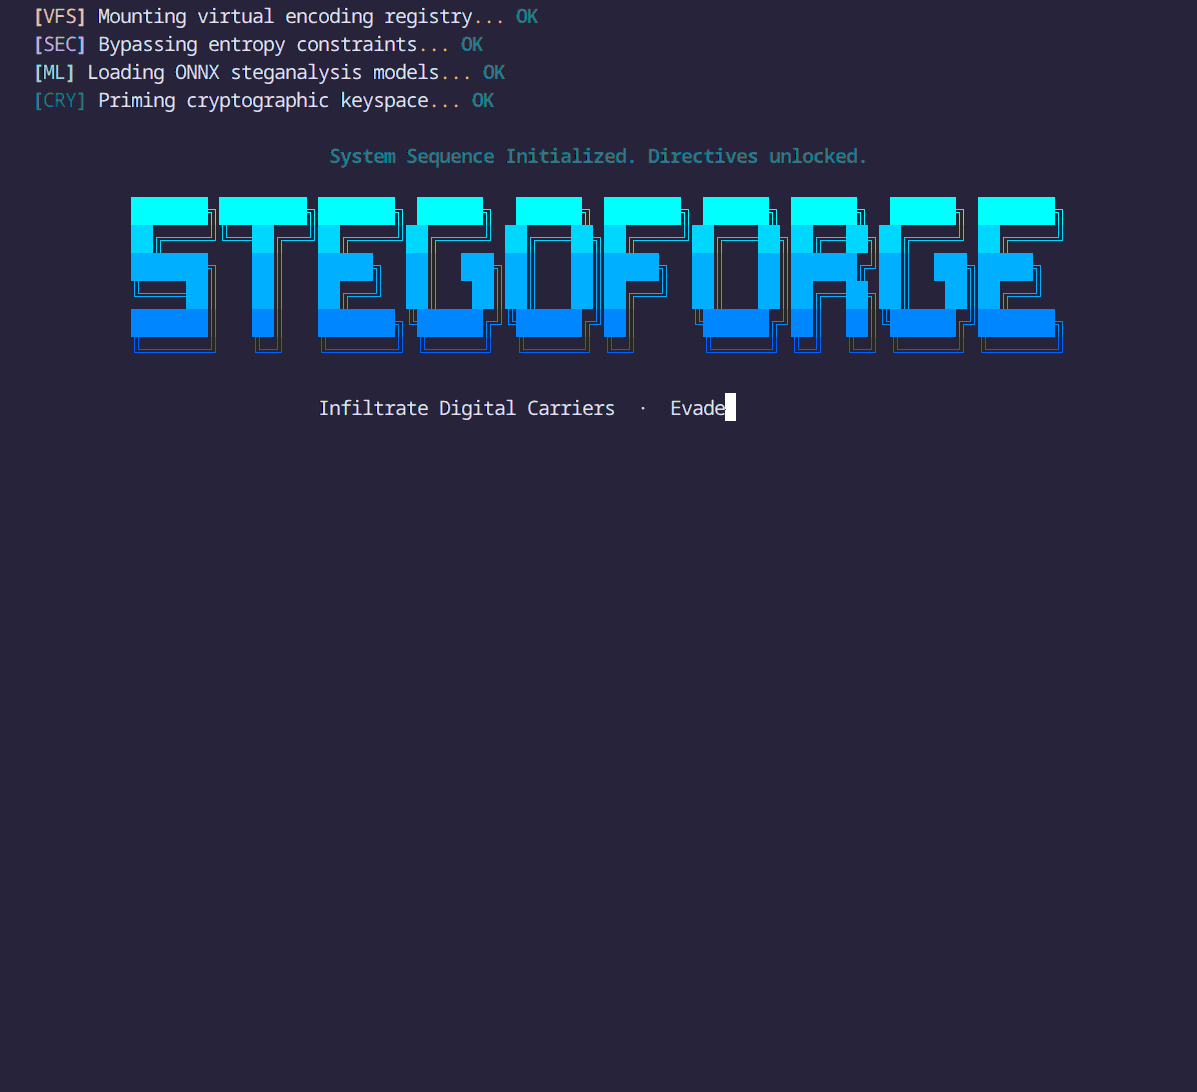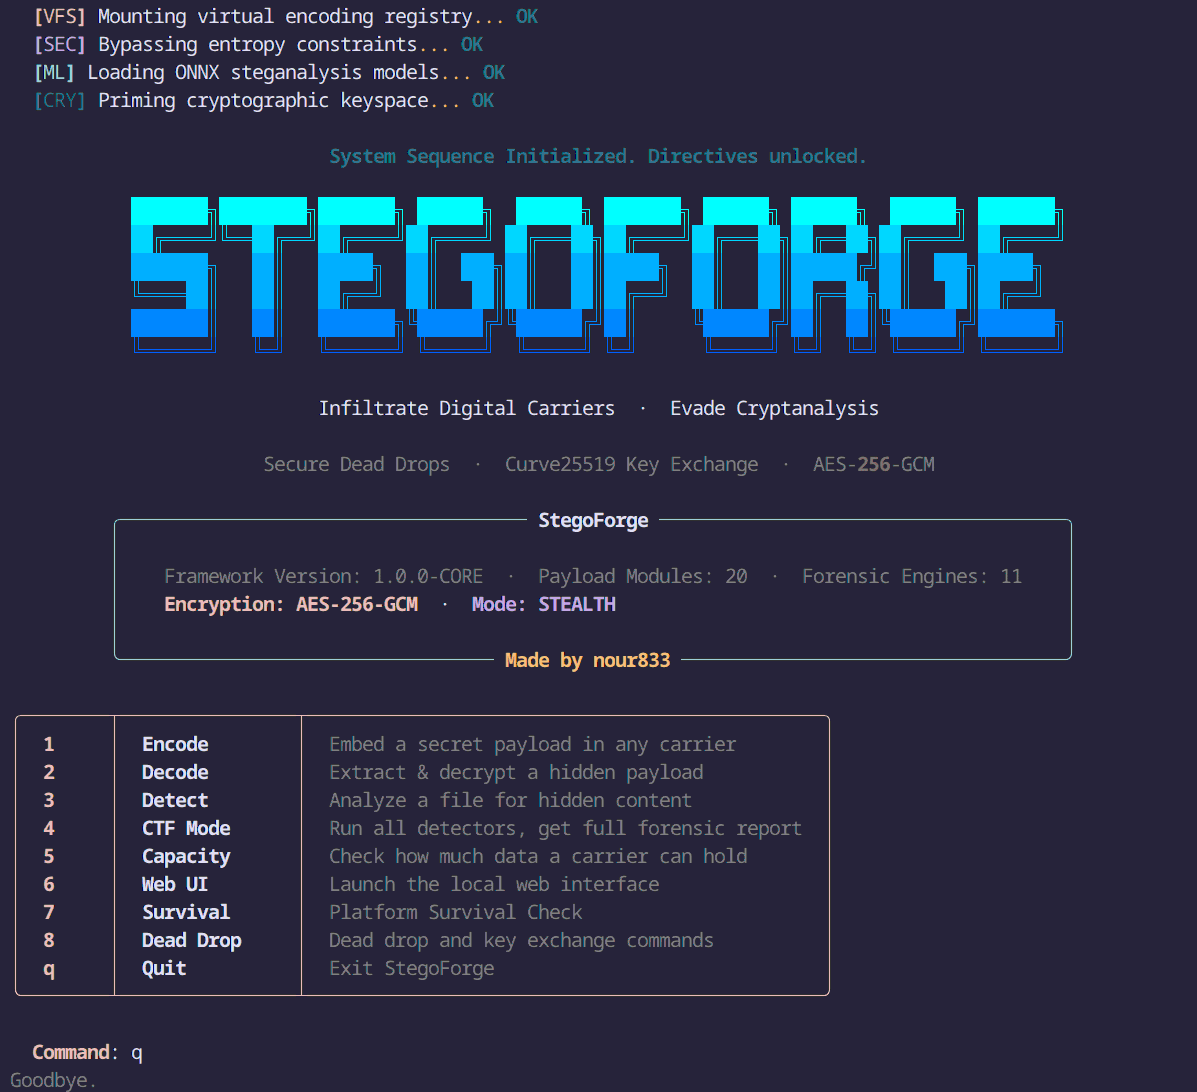
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…

Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine