follina-msdt-threat-investigation

🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…

🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…

Sources of Synacktiv's challenge for leHack 2026

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…

This repository is to demonstrate and practice my forensic/vulnerability analysis skills by reproducing a web-related CVE in a safe environment.

Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.

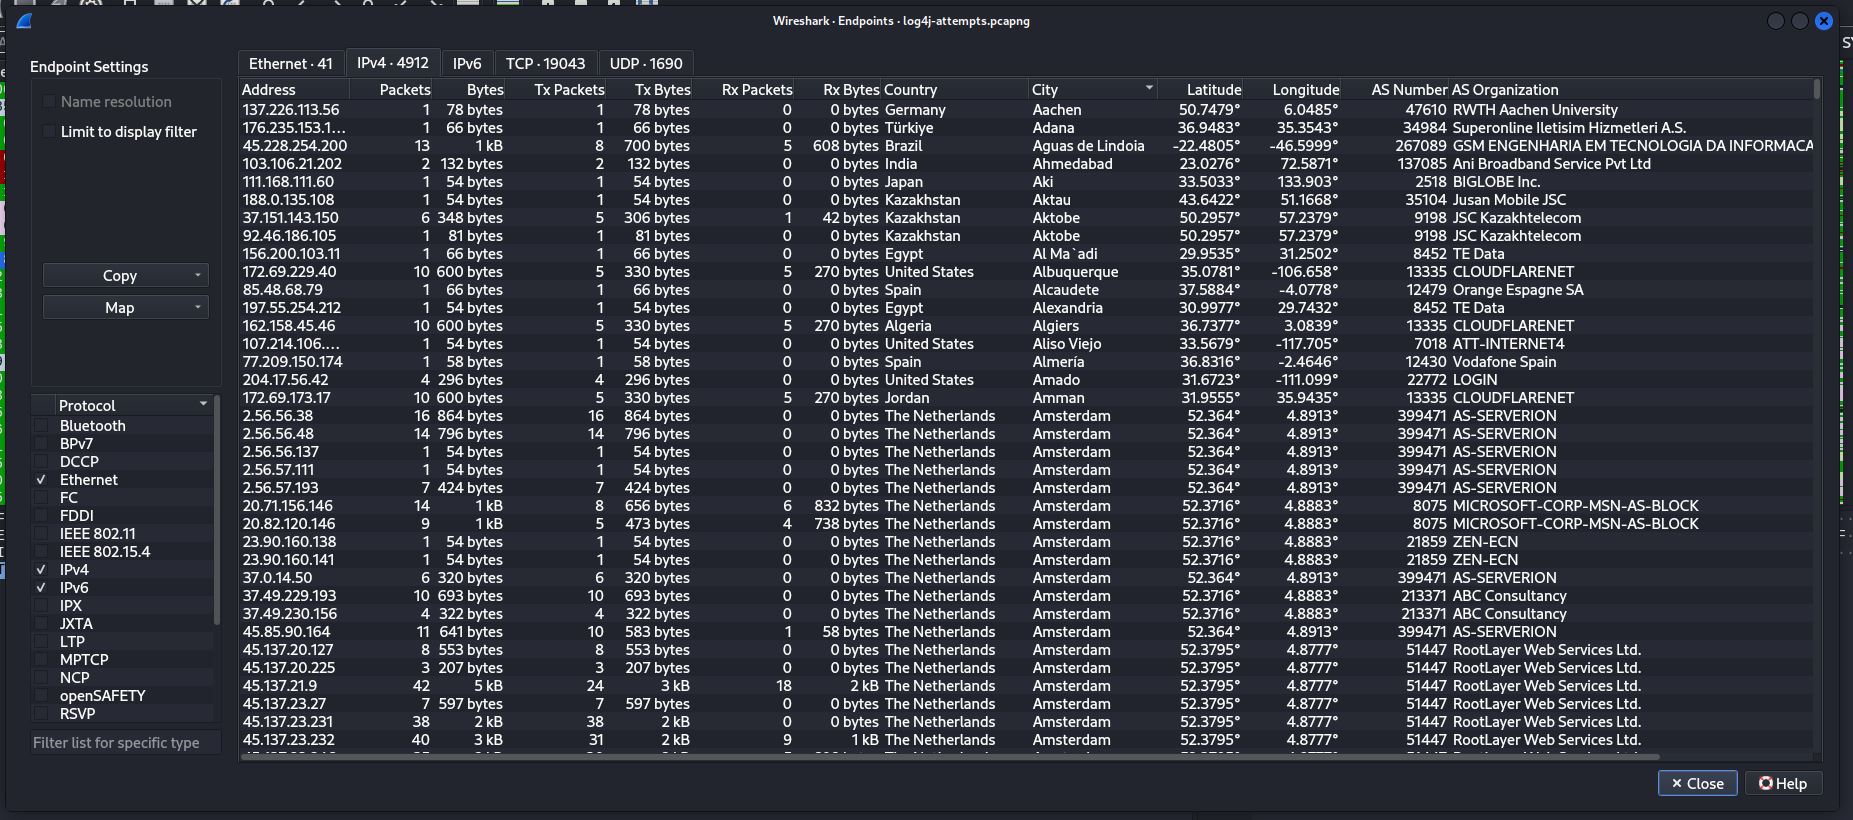
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…

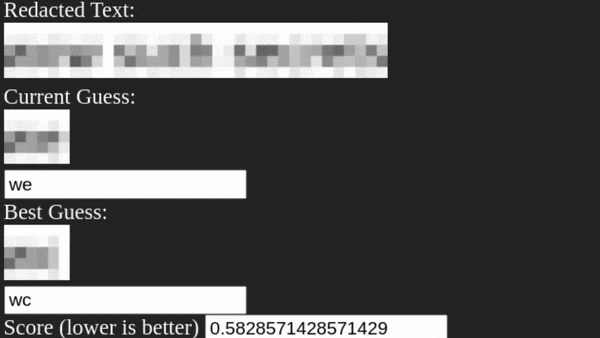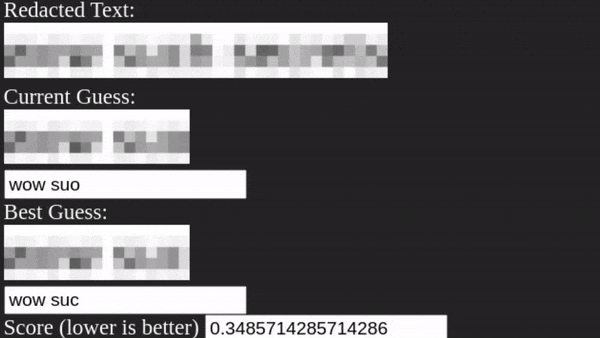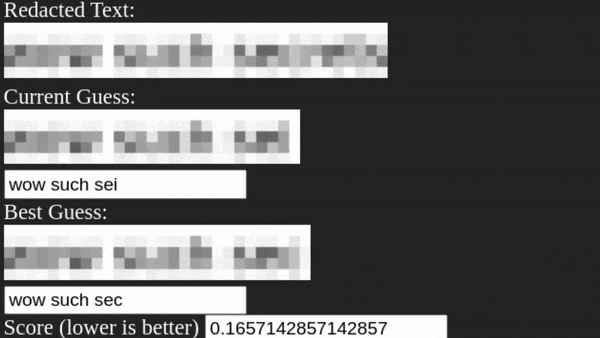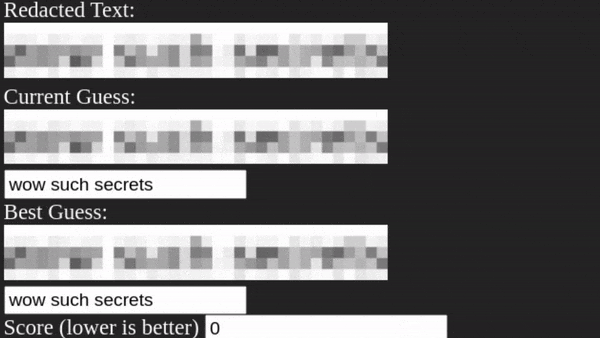
Never ever ever use pixelation as a redaction technique

An open-source digital image forensic toolset


Re-play Security Events

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…


Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…

Labs for Practical Malware Analysis & Triage

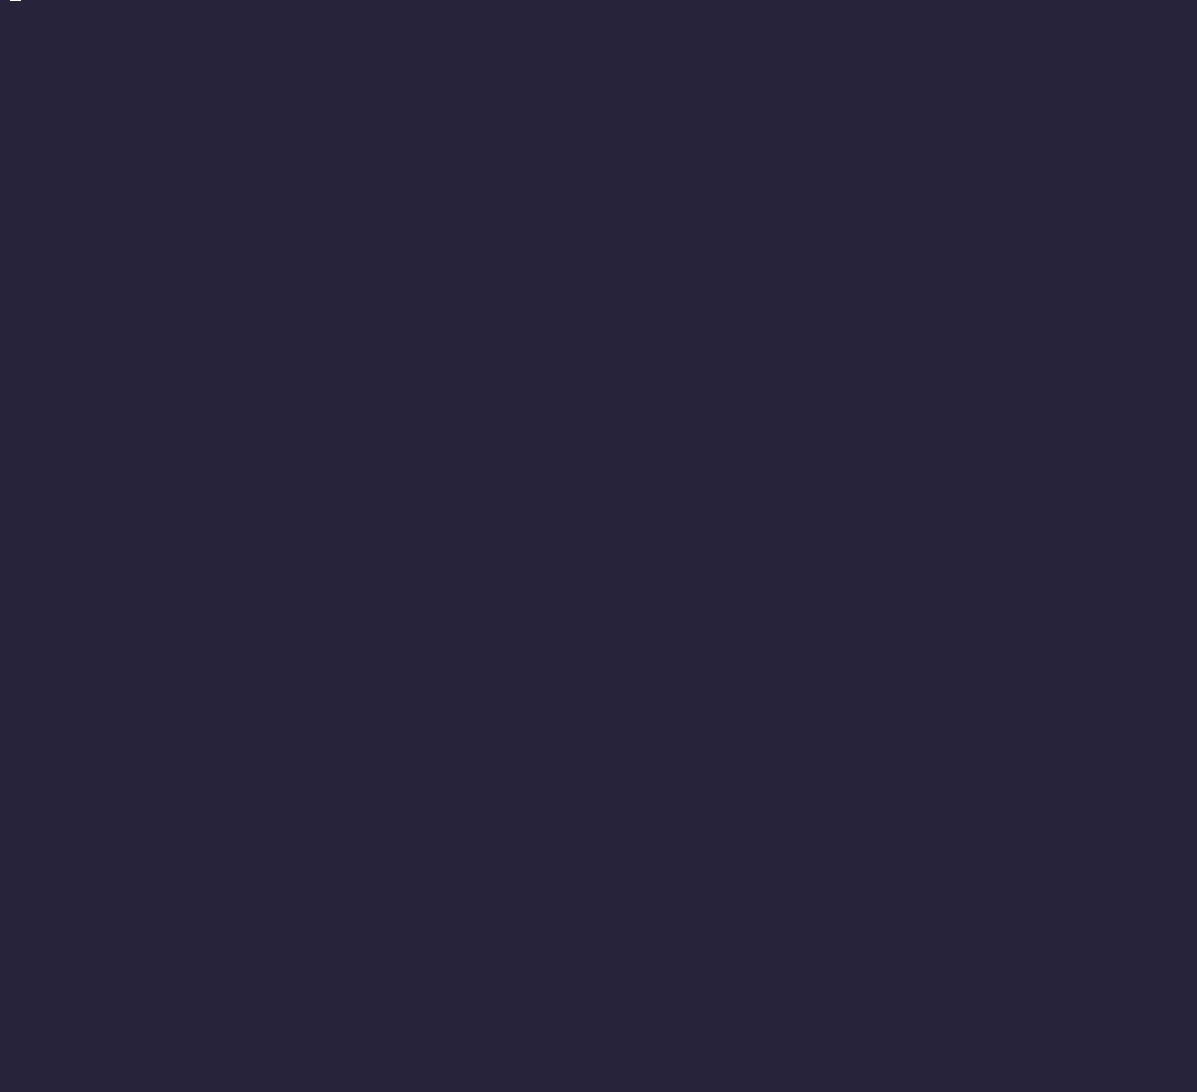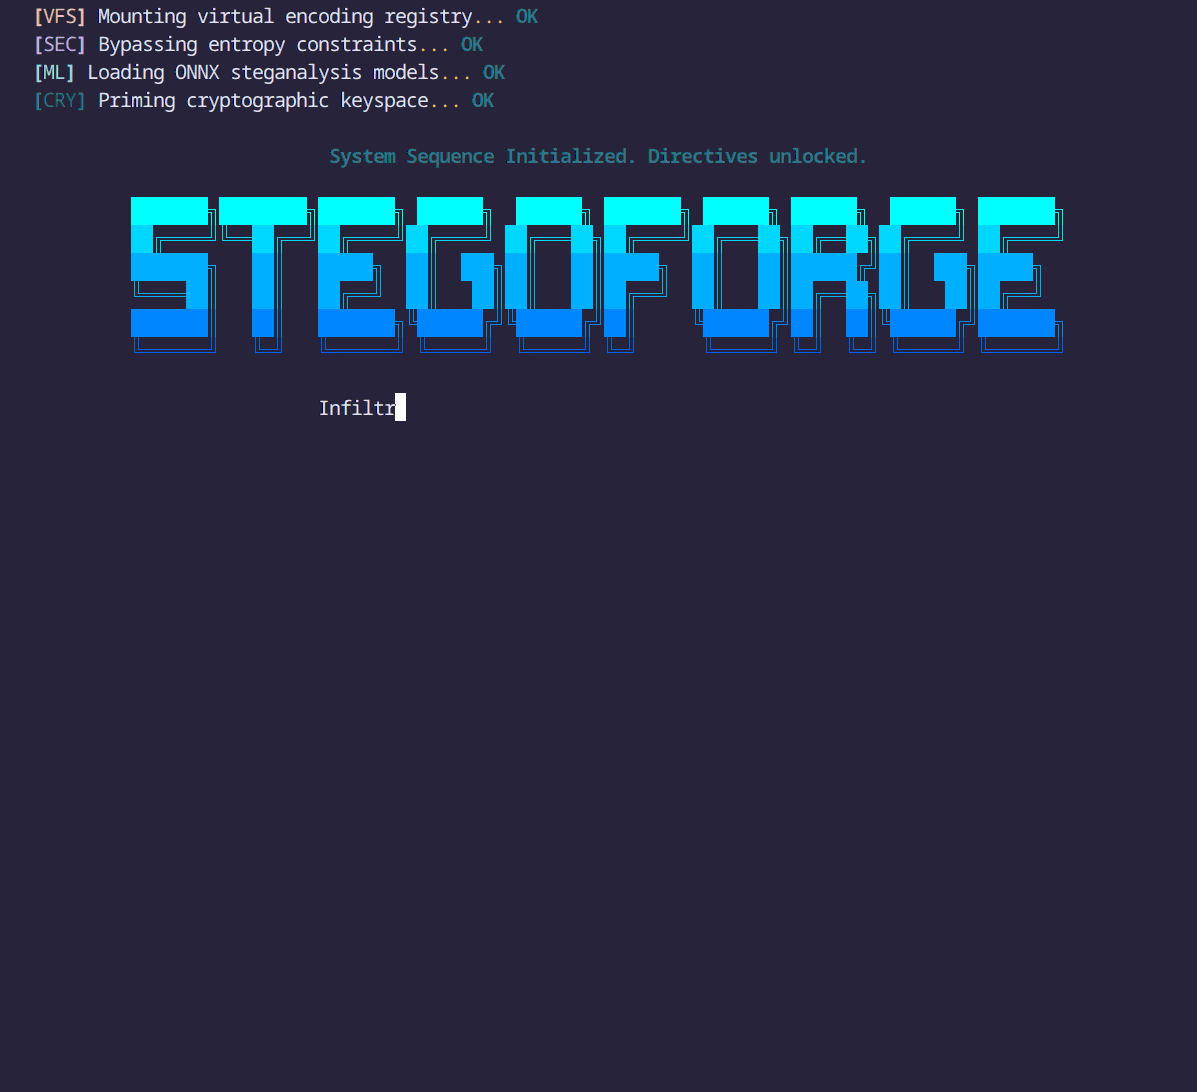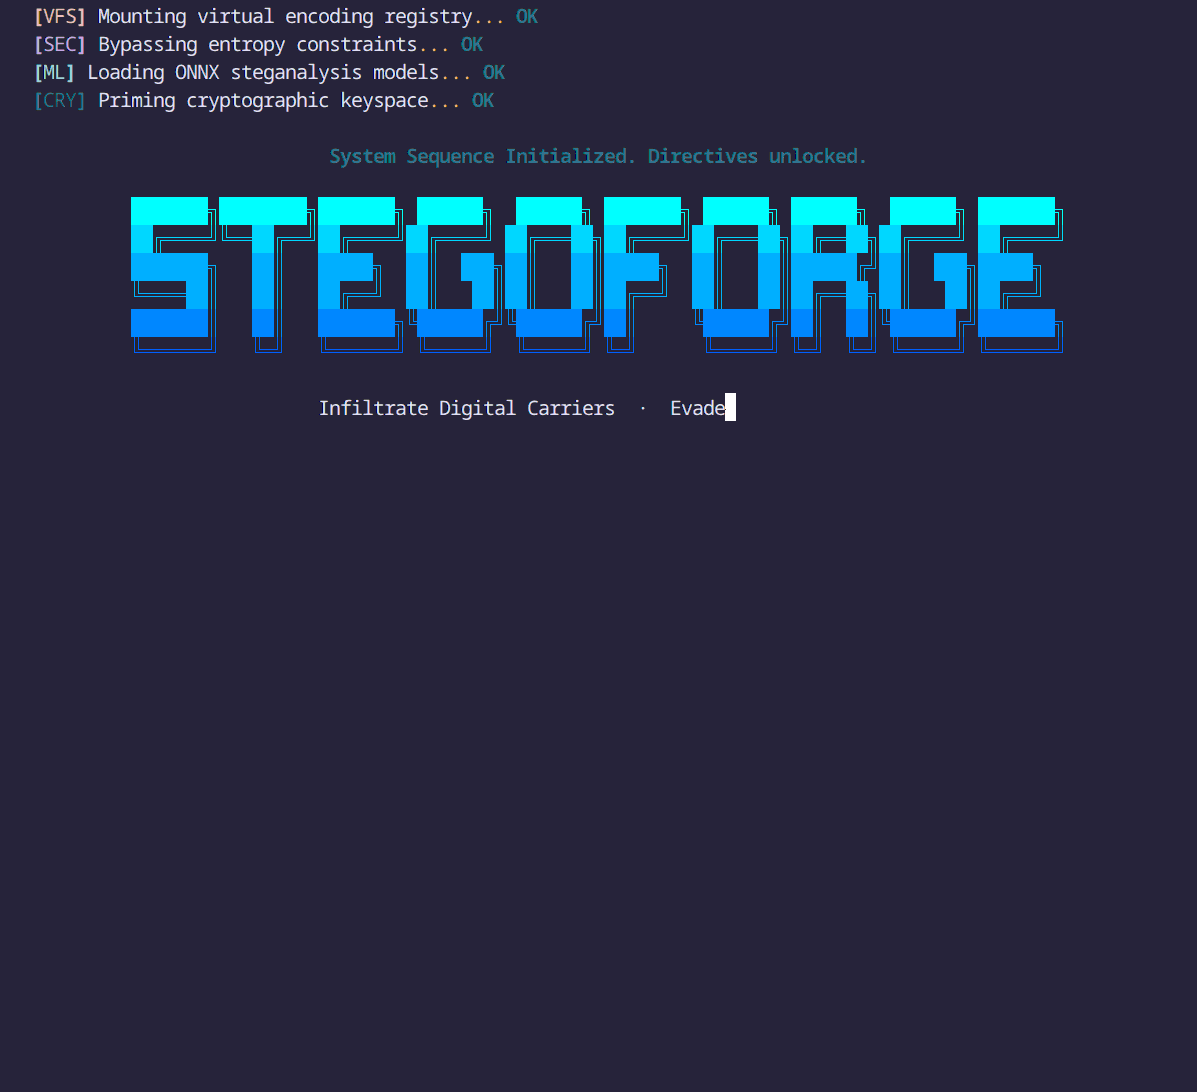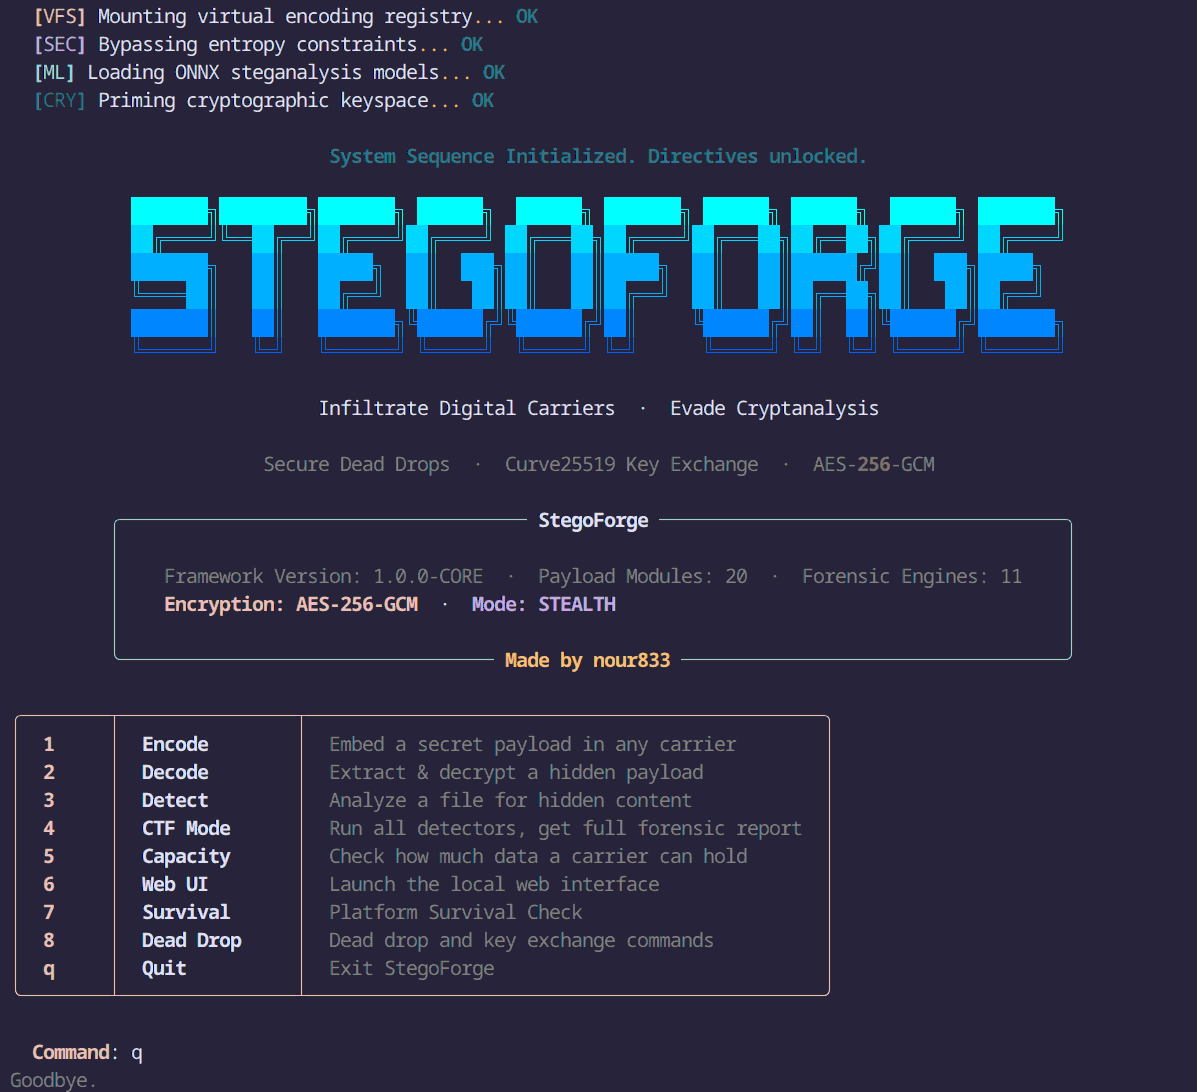
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…