
TCPViewer
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
digital-forensicsforensicsinformation-gathering+3
442
proxymanapp/tcpviewerThe best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project

 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
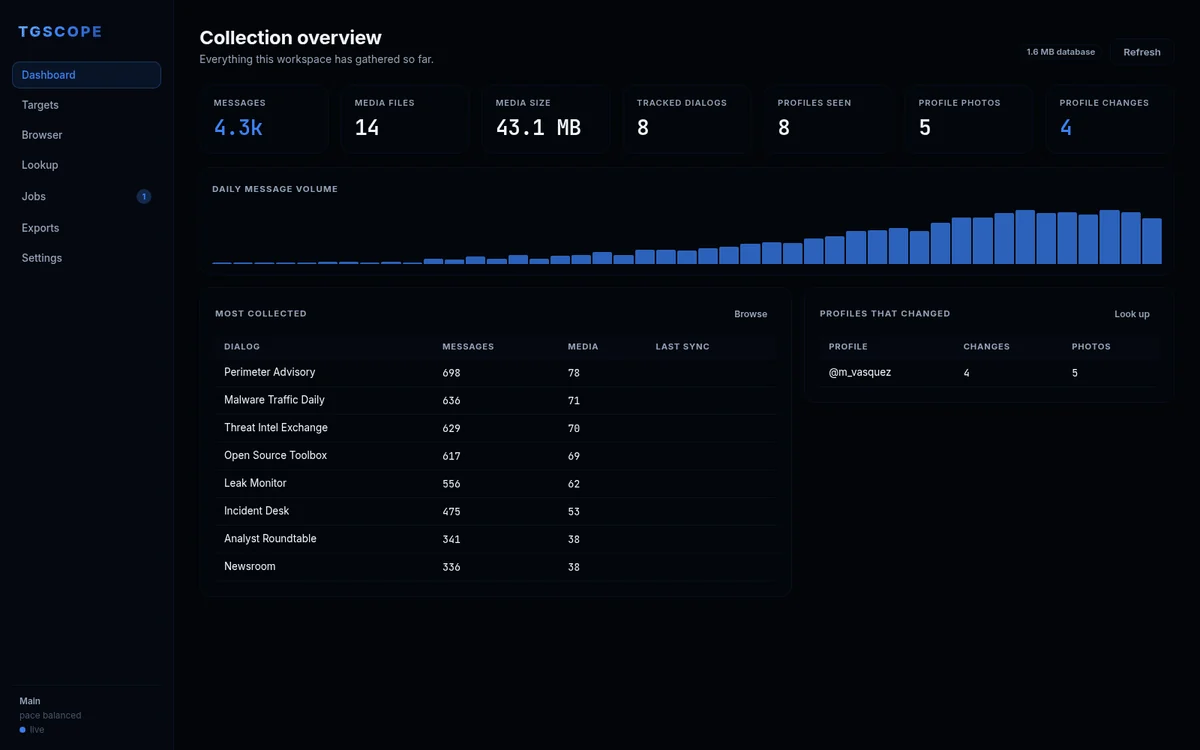 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
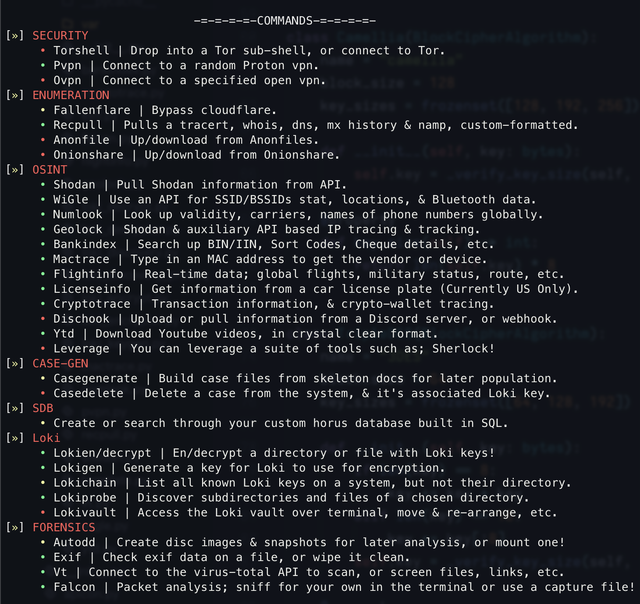 6abd/horus
An OSINT / digital forensics tool built in Python
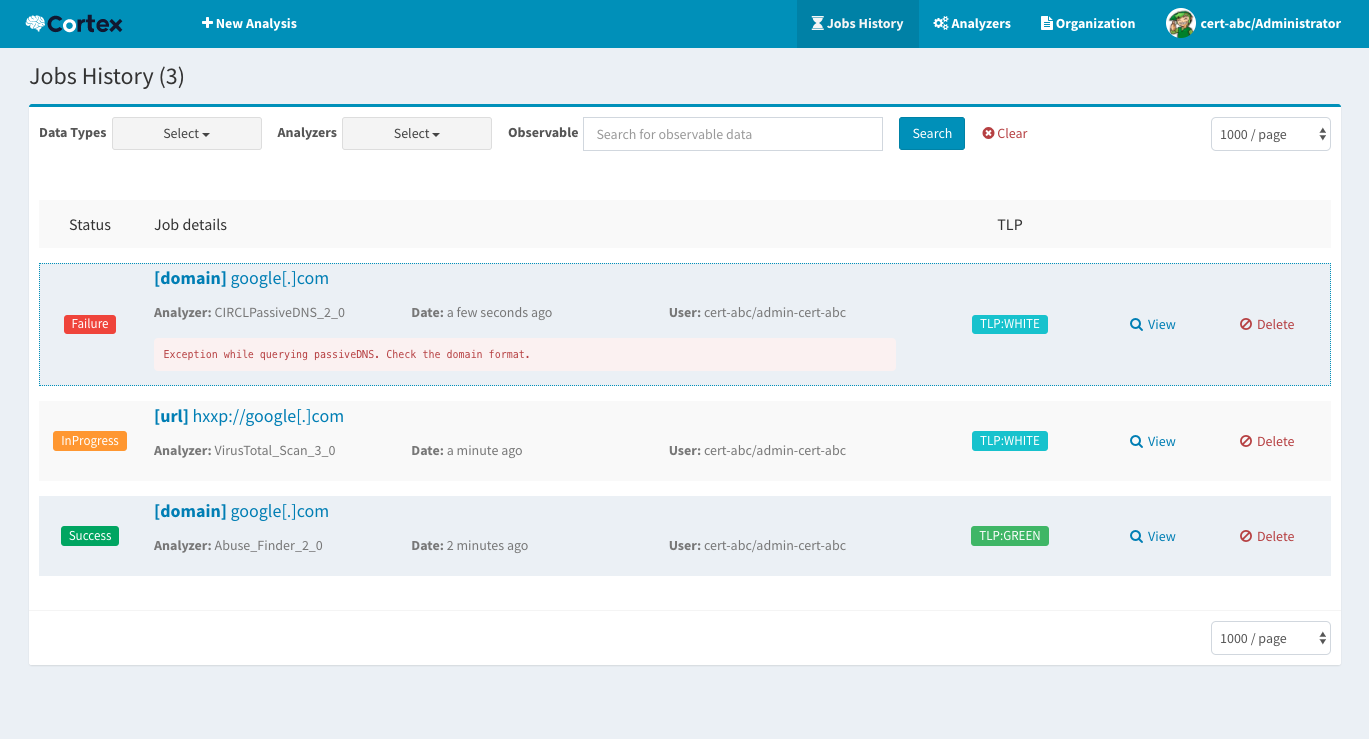 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine