
iLEAPP
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.3k
abrignoni/ileappParses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
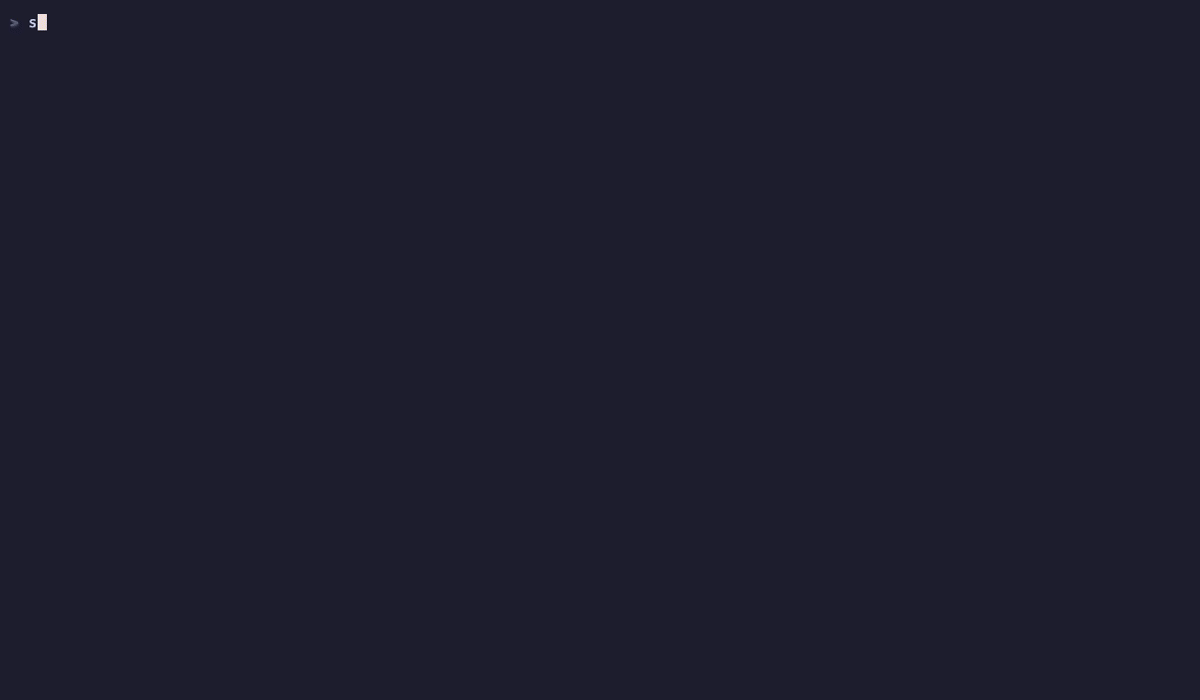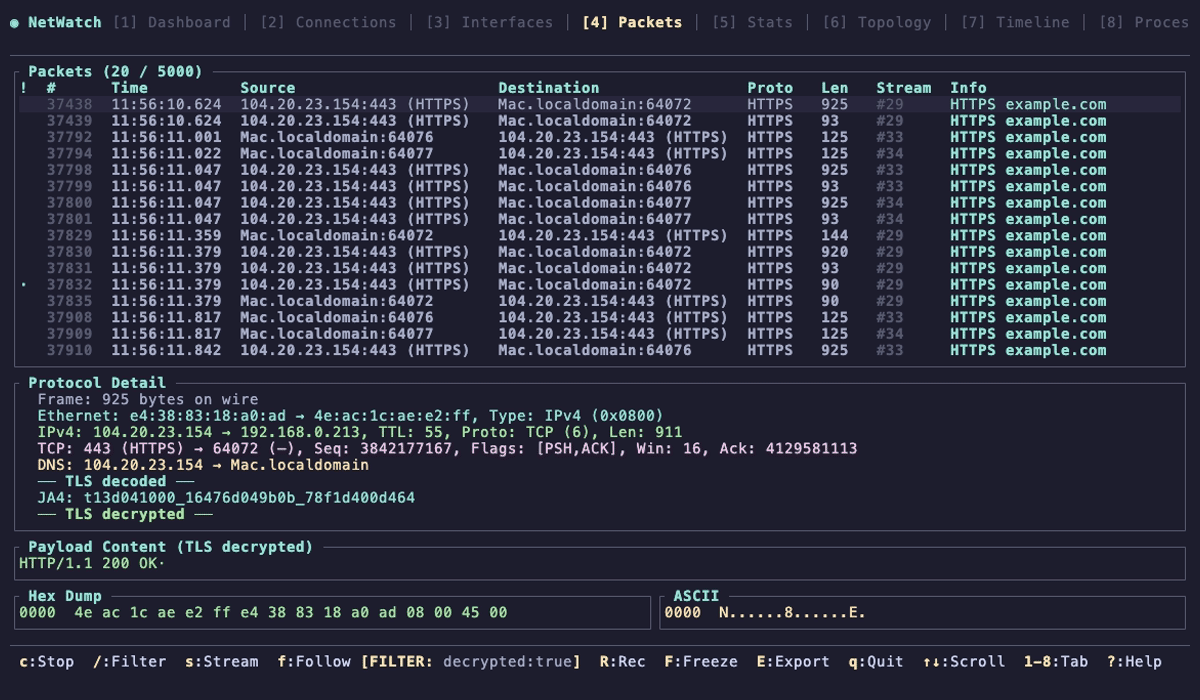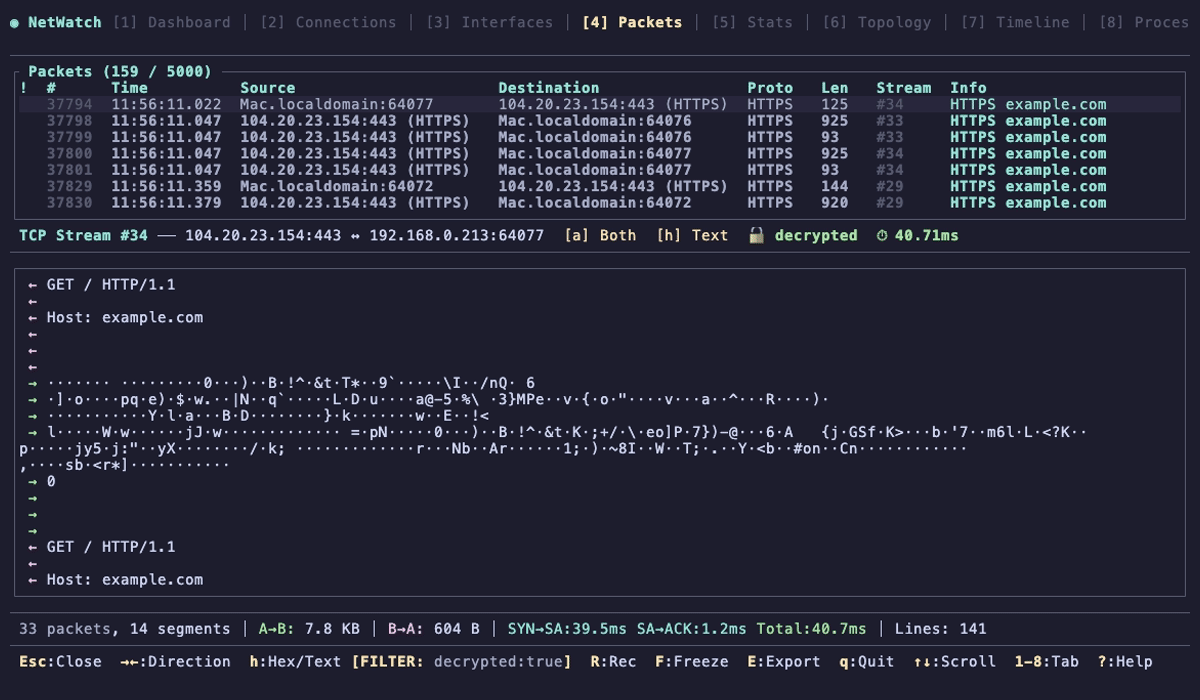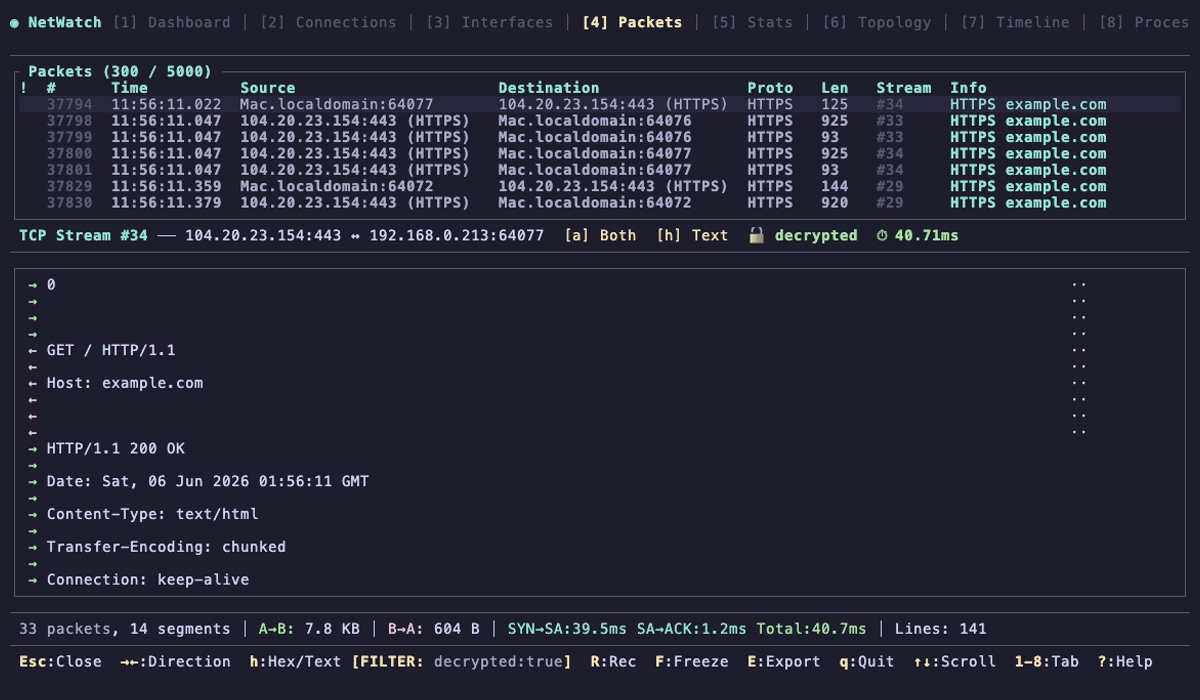 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
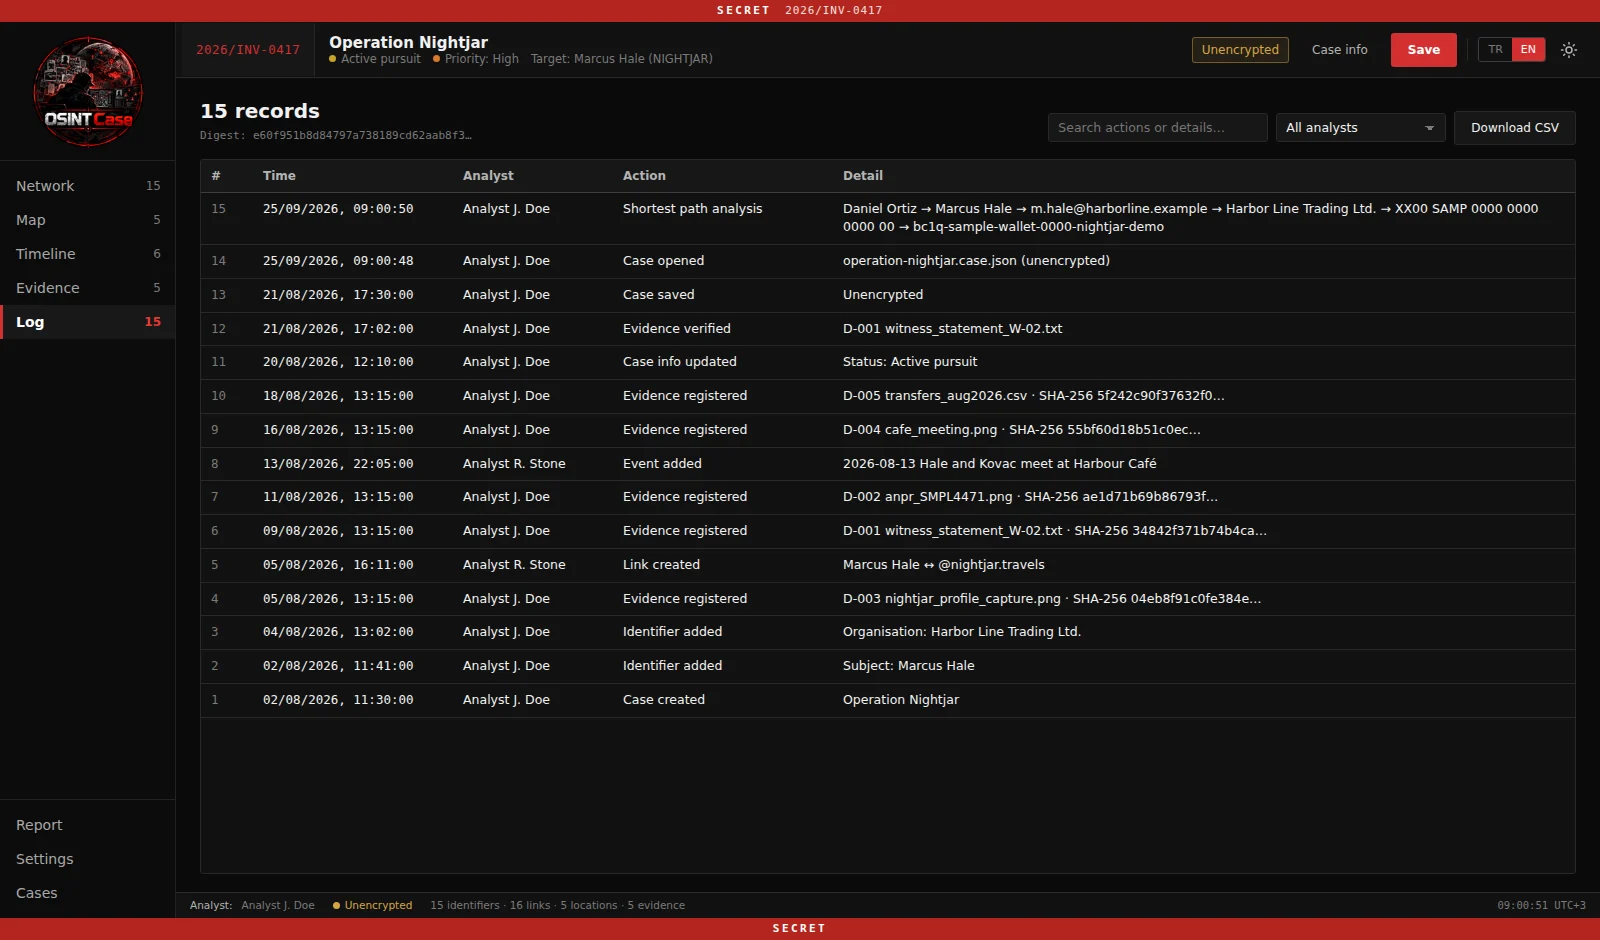 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 trunkrecorder/trunk-recorder
Records calls from a Trunked Radio System (P25 & SmartNet)
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.