

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
SOCMIntelligence preview

SOCMIntelligence

GitHubemrekybs/socmintelligence

A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
crawlerdigital-forensicsidentity-management+8
3
13 days ago
watermarks-remover preview

watermarks-remover

GitHubguillaumemeyer/watermarks-remover

A privacy-first app that strips AI watermarks from content you own.

adversarial-attackai-securitydigital-forensics+5
25.6k8 days ago
badbox-h713-projector preview

badbox-h713-projector

GitHubflorentineprinzessinzusachsen/badbox-h713-projector

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

android-securitydigital-forensicsembedded-systems-security+8
31 month ago
awesome-lists preview

awesome-lists

GitHubmthcht/awesome-lists

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.

curated-resourcesdigital-forensicseducation+4
2.0k40 minutes ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1212 years ago
Disk-Arbitrator preview

Disk-Arbitrator

GitHubaburgh/disk-arbitrator

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

data-recoverydigital-forensicsdisk-forensics+2
7151 year ago
ztewaste preview

ztewaste

GitHubjoshatticus/ztewaste

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
android-securitydata-exfiltrationdigital-forensics+6
44 months ago
dumpscan preview
Archived

dumpscan

GitHubdaddycocoaman/dumpscan

Finding secrets in kernel and user memory
cryptographydigital-forensicsencryption-decryption-tools+4
1183 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3053 years ago
php2shell-check preview

php2shell-check

GitHubbrentmartinmiller/php2shell-check

Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
configuration-auditingdefensive-toolsdigital-forensics+6
36 days ago
Mandiant-Azure-AD-Investigator preview
Archived

Mandiant-Azure-AD-Investigator

GitHubmandiant/mandiant-azure-ad-investigator

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
cloud-securitydigital-forensicsidentity-access-management+4
6473 years ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

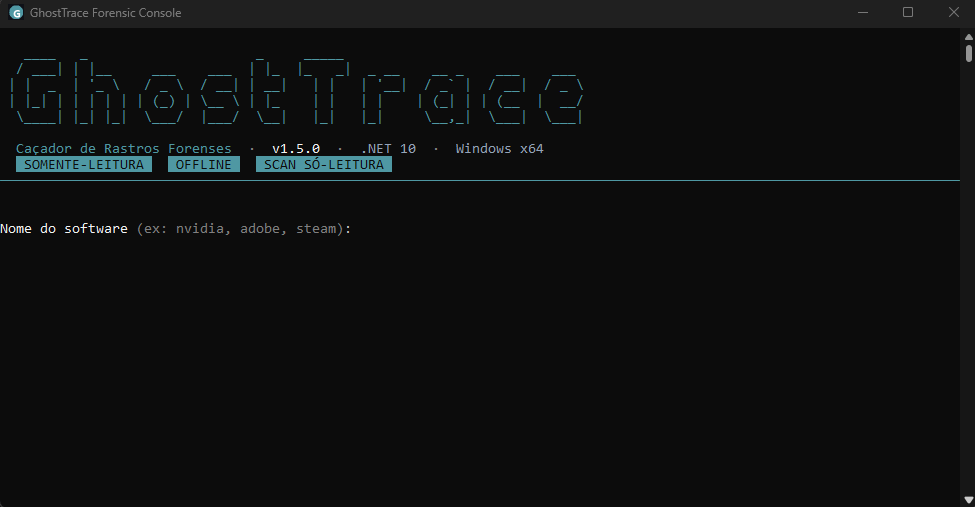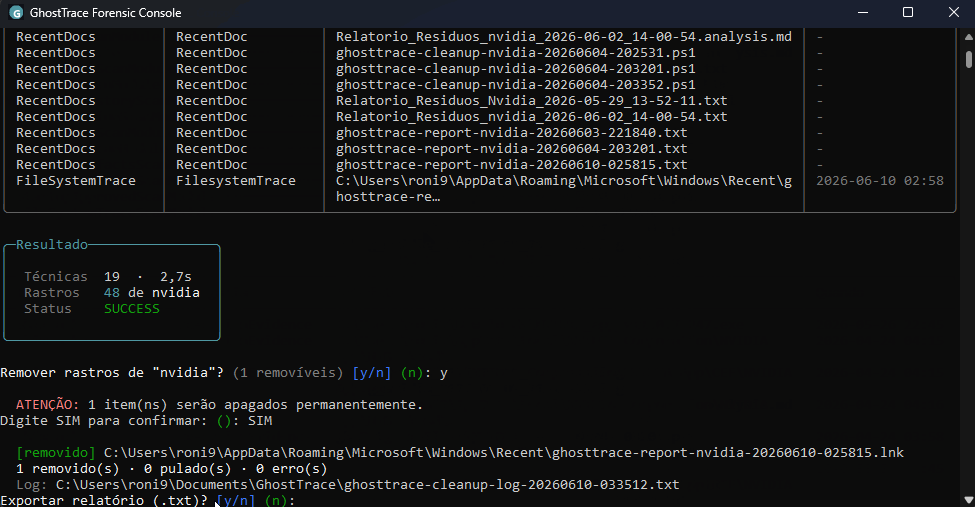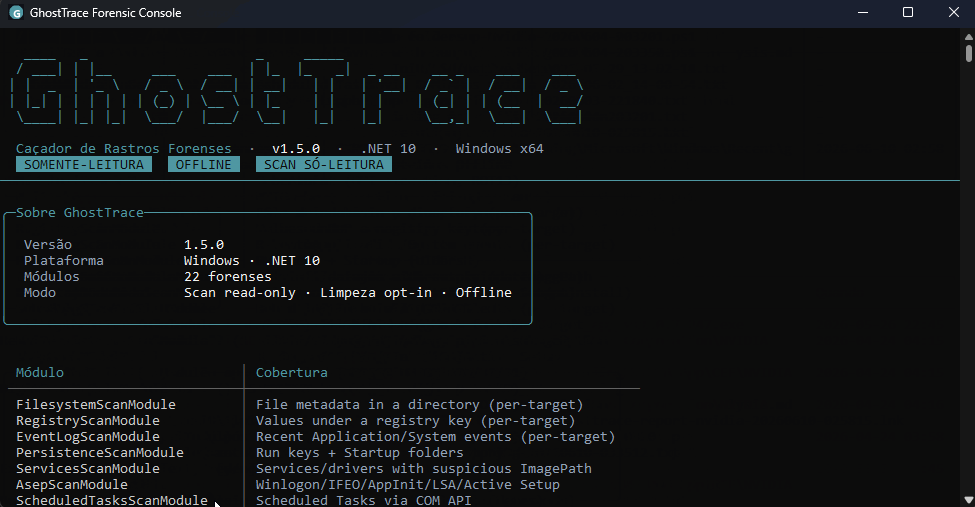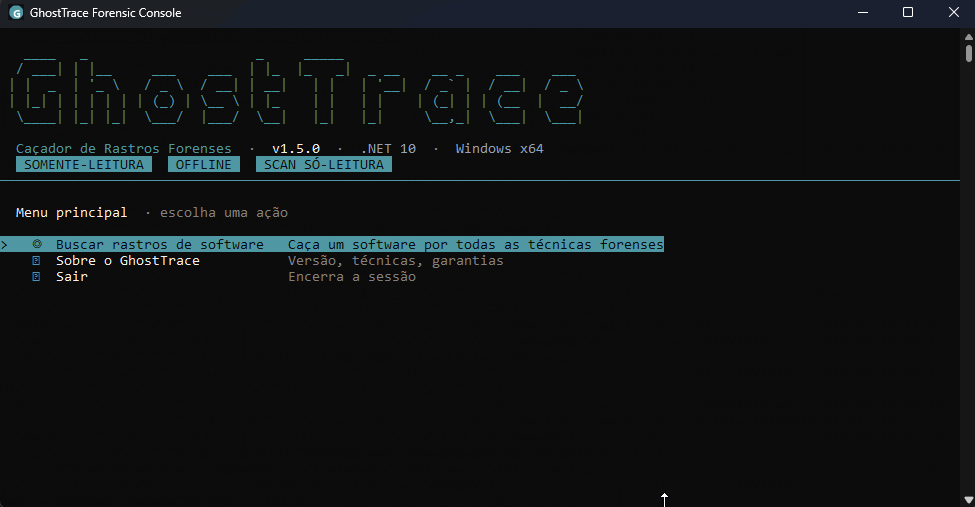
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
digital-forensicsforensicsincident-response+3
3 months ago
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

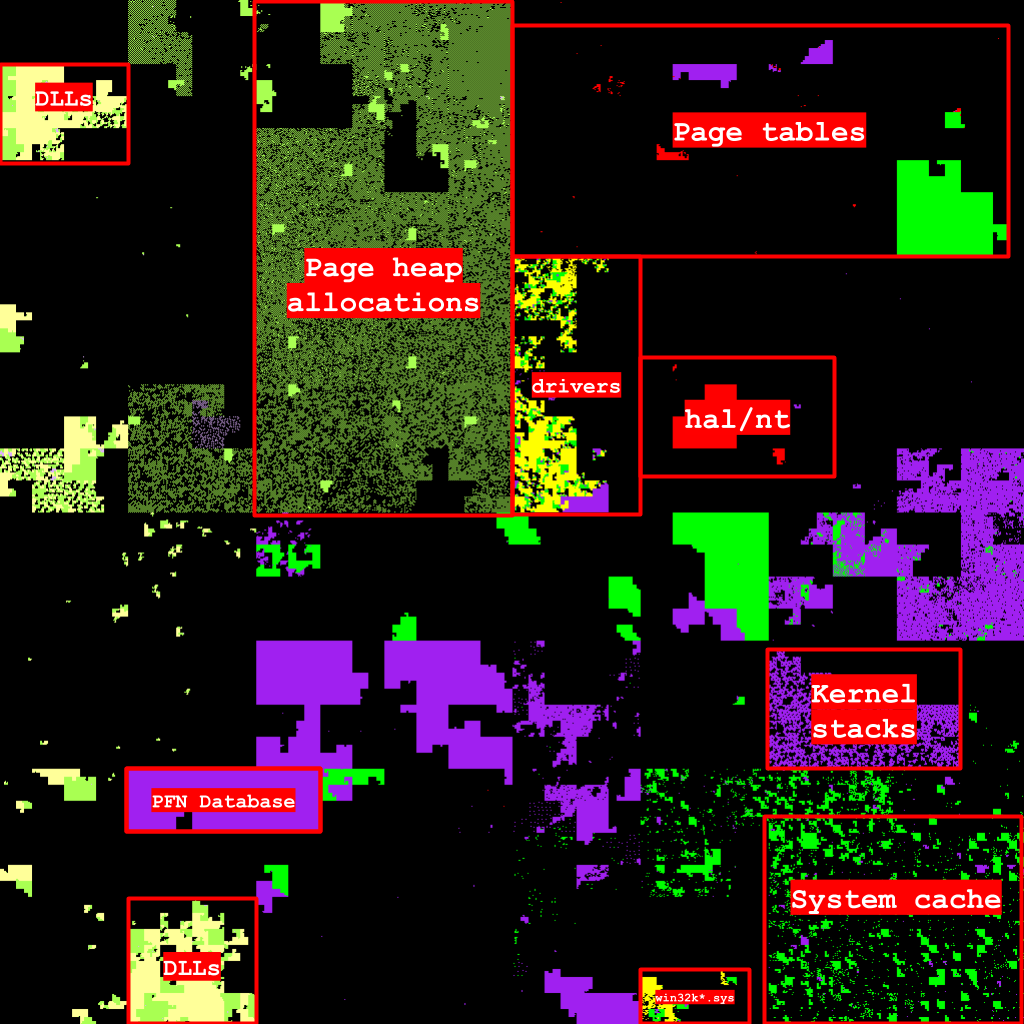
Visualize the virtual address space of a Windows process on a Hilbert curve.
digital-forensicsforensicsmemory-forensics
3125 years ago
VolExp preview

VolExp

GitHubmemoryforensics1/volexp

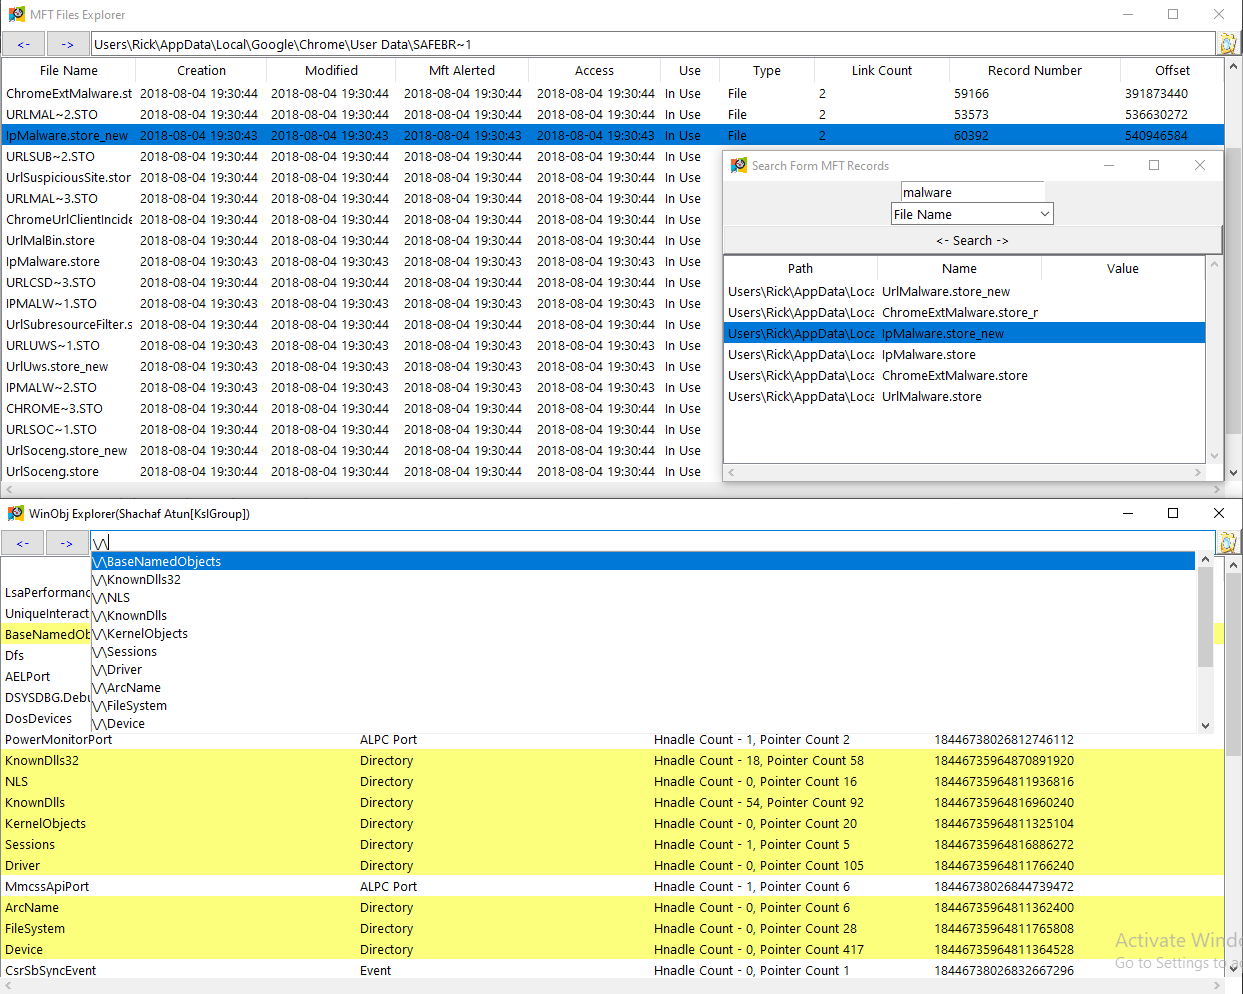
volatility explorer (volatility 2)
digital-forensicsforensicsincident-response+2
955 years ago
swap_digger preview

swap_digger

GitHubsevagas/swap_digger

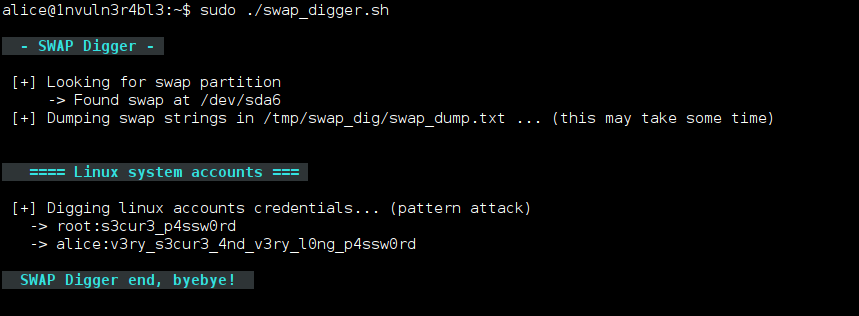
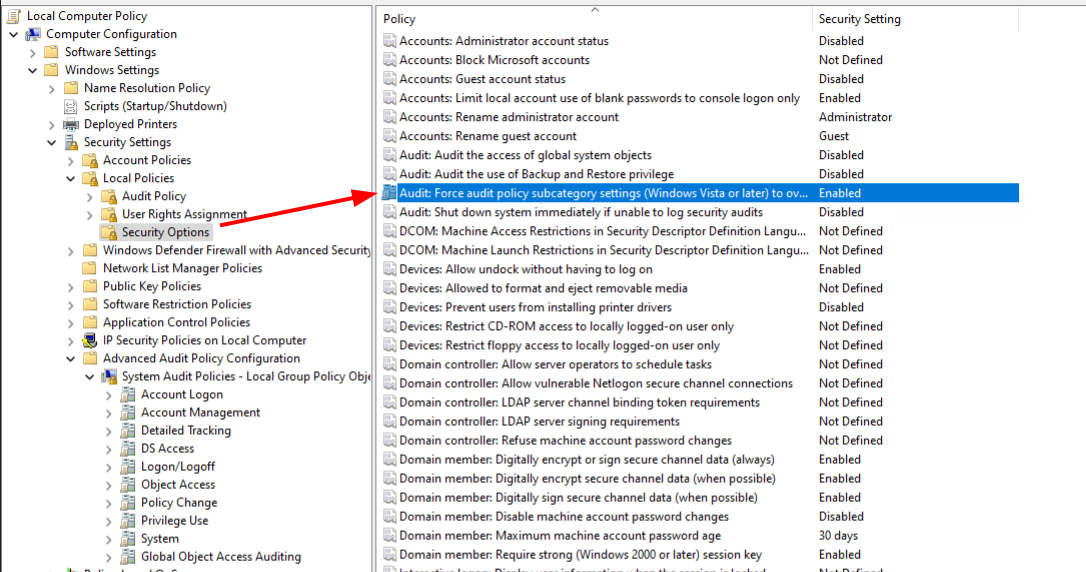
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
digital-forensicsforensicsinformation-gathering+2
5355 years ago
evtx-baseline preview

evtx-baseline

GitHubnextronsystems/evtx-baseline

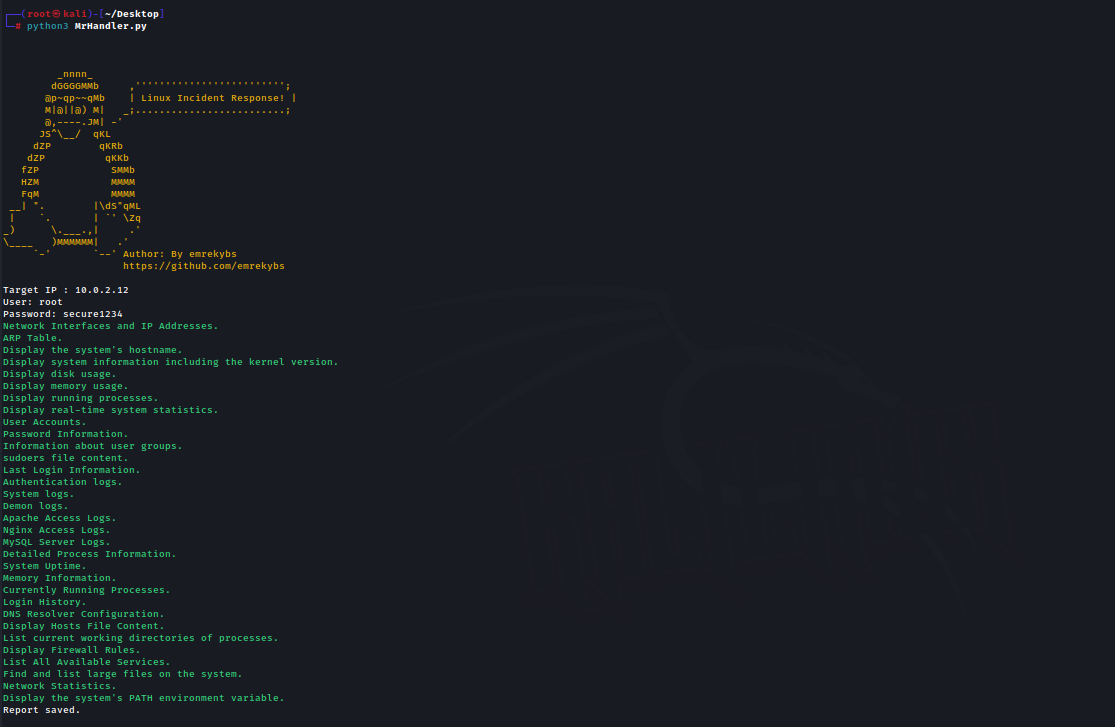
A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
curated-resourcesdigital-forensicseducation+2
932 years ago
MrHandler preview

MrHandler

GitHubemrekybs/mrhandler

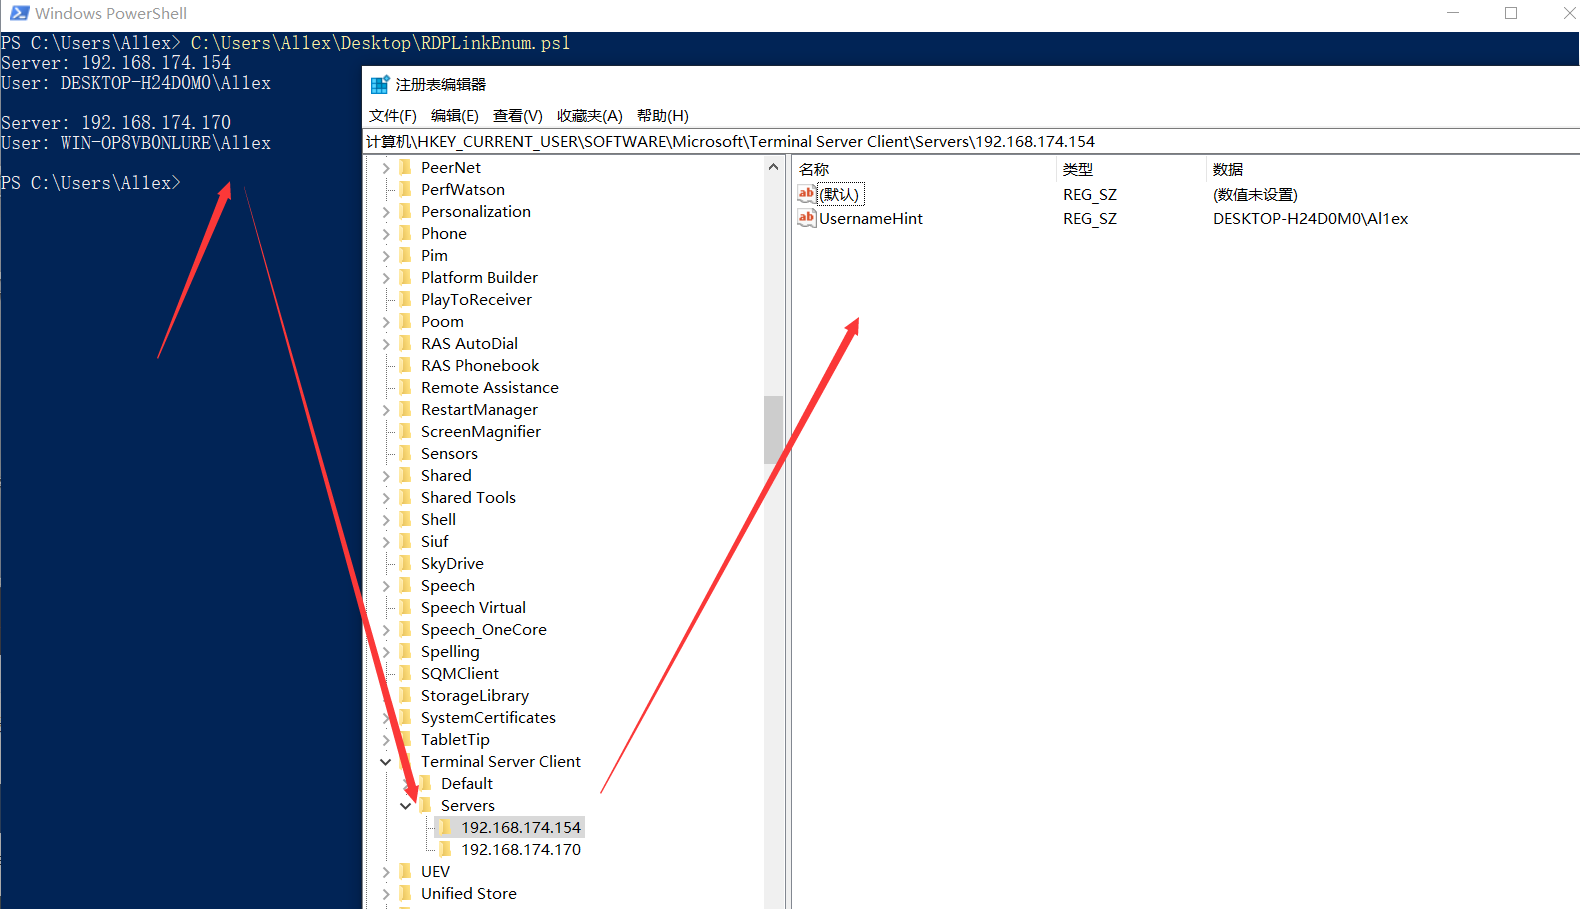
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
digital-forensicsforensicsincident-response+1
857 months ago
RDPLinkEnum preview

RDPLinkEnum

GitHubal1ex/rdplinkenum

RDPLinkEnum

digital-forensicsforensicsincident-response+3
55 years ago
Previous12Next