
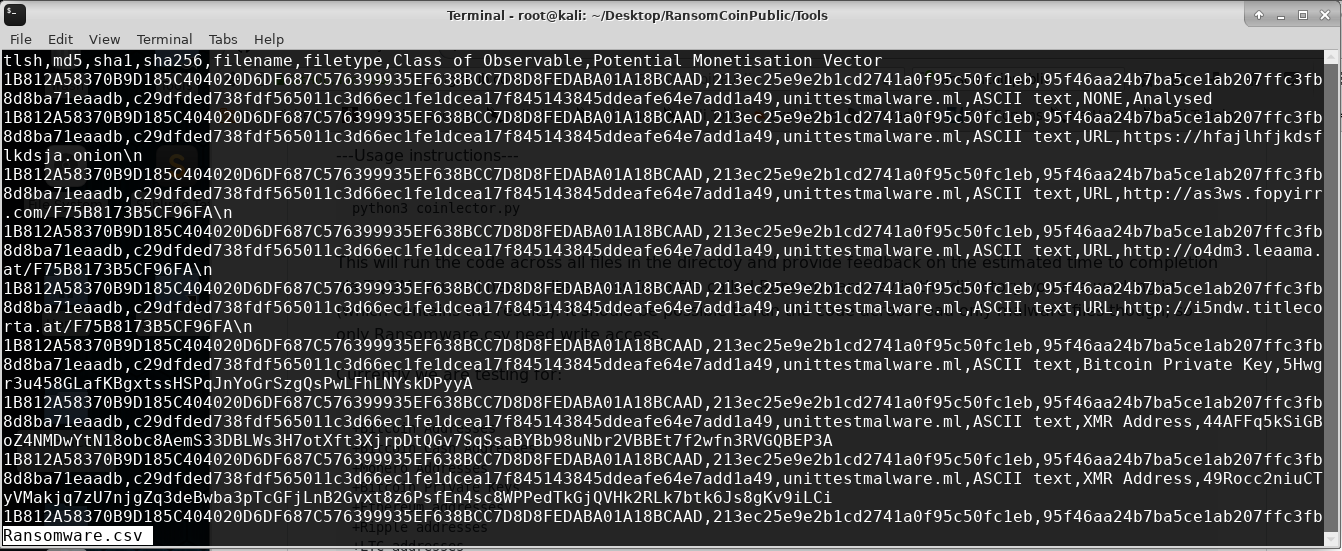
RansomCoinPublic
 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
ioc-managementforensicsmalware-analysis+3
56
concinnity-risks/ransomcoinpublicA DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
 slaughterjames/excelpeek
Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
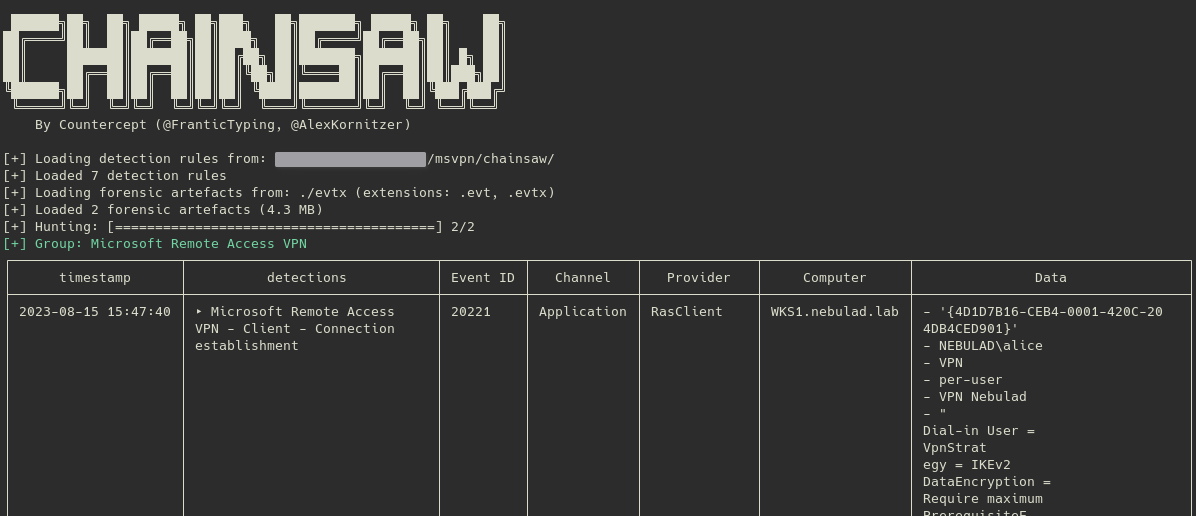 synacktiv/forensic-msvpn
This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity
 synacktiv/lehack-2026-challenge
Sources of Synacktiv's challenge for leHack 2026
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
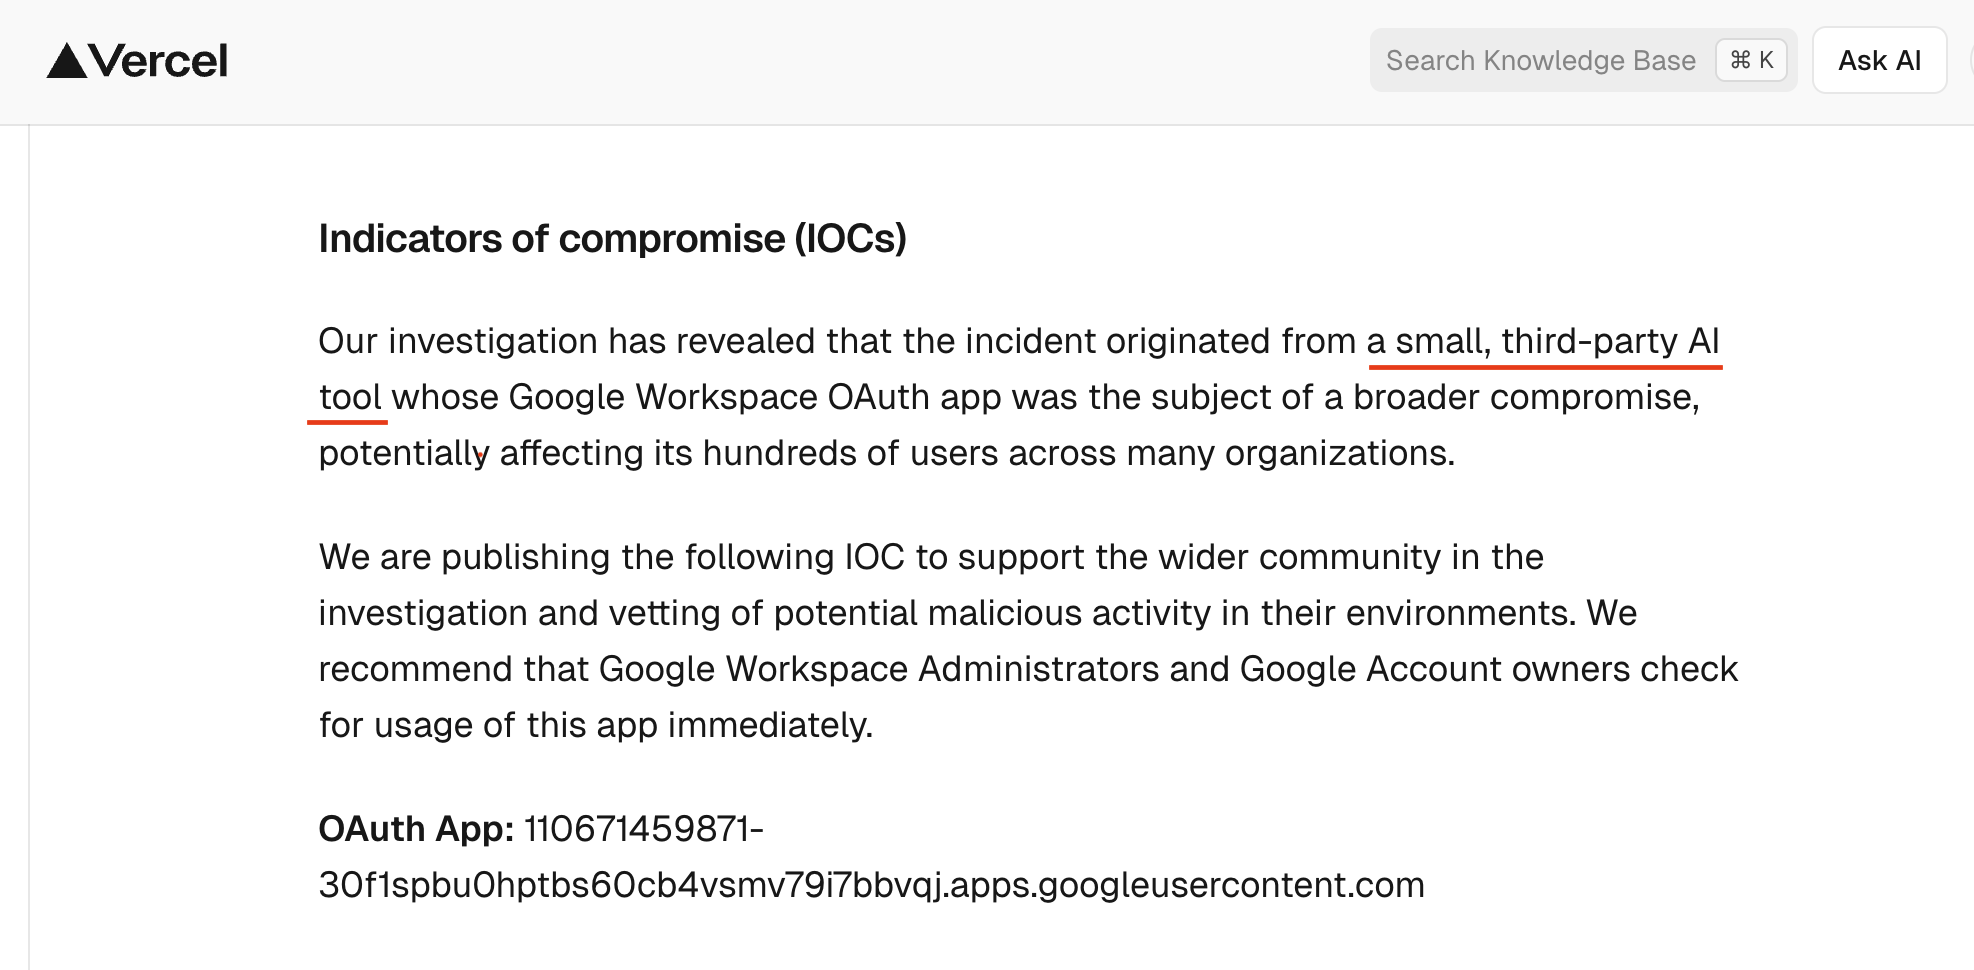 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 uthrasri/openssl_g2.5_cve-2014-8275
General-purpose cryptography library and SSL/TLS toolkit implementing ciphers, digests, public key algorithms, and X.509 certificates for secure…
 synacktiv/cachedata_decrypt
A simple Toolkit to BF and decrypt Windows EntraId CacheData
 azeemering/cve-2021-44228-dfir-notes
CVE-2021-44228 DFIR Notes
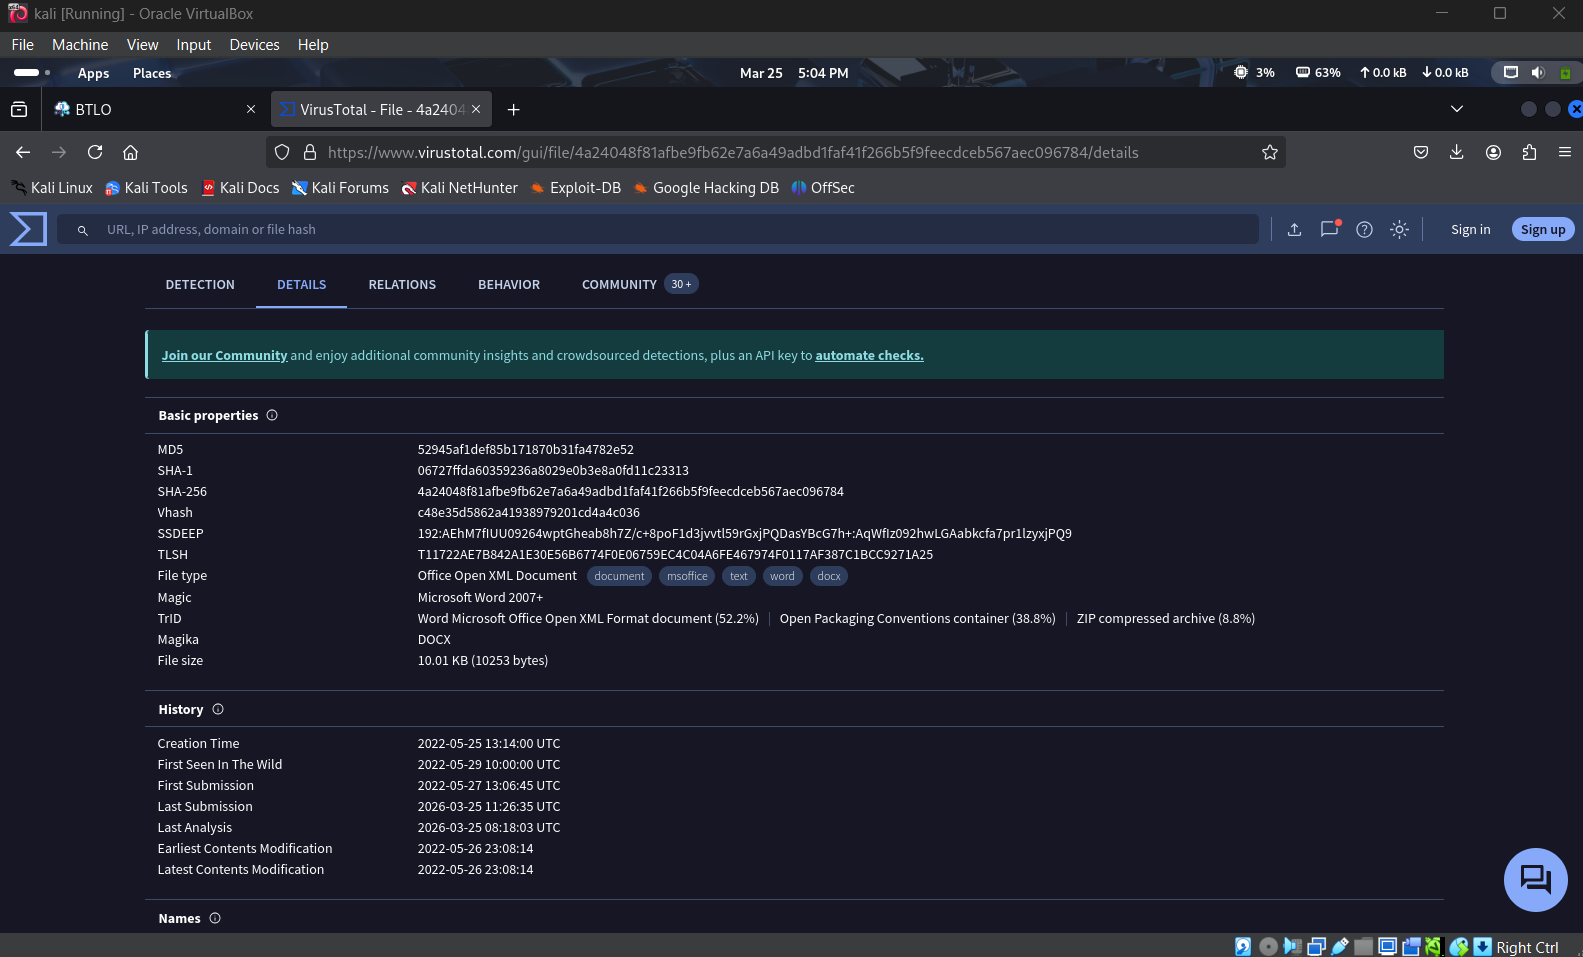 imvihanga03/static-malware-analysis-follina-cve-2022-30190
Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 busindre/mozcache
Simple shell script to perform forensic analysis of the Mozilla-Browsers cache (Firefox, Iceweasel and Seamonkey).
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
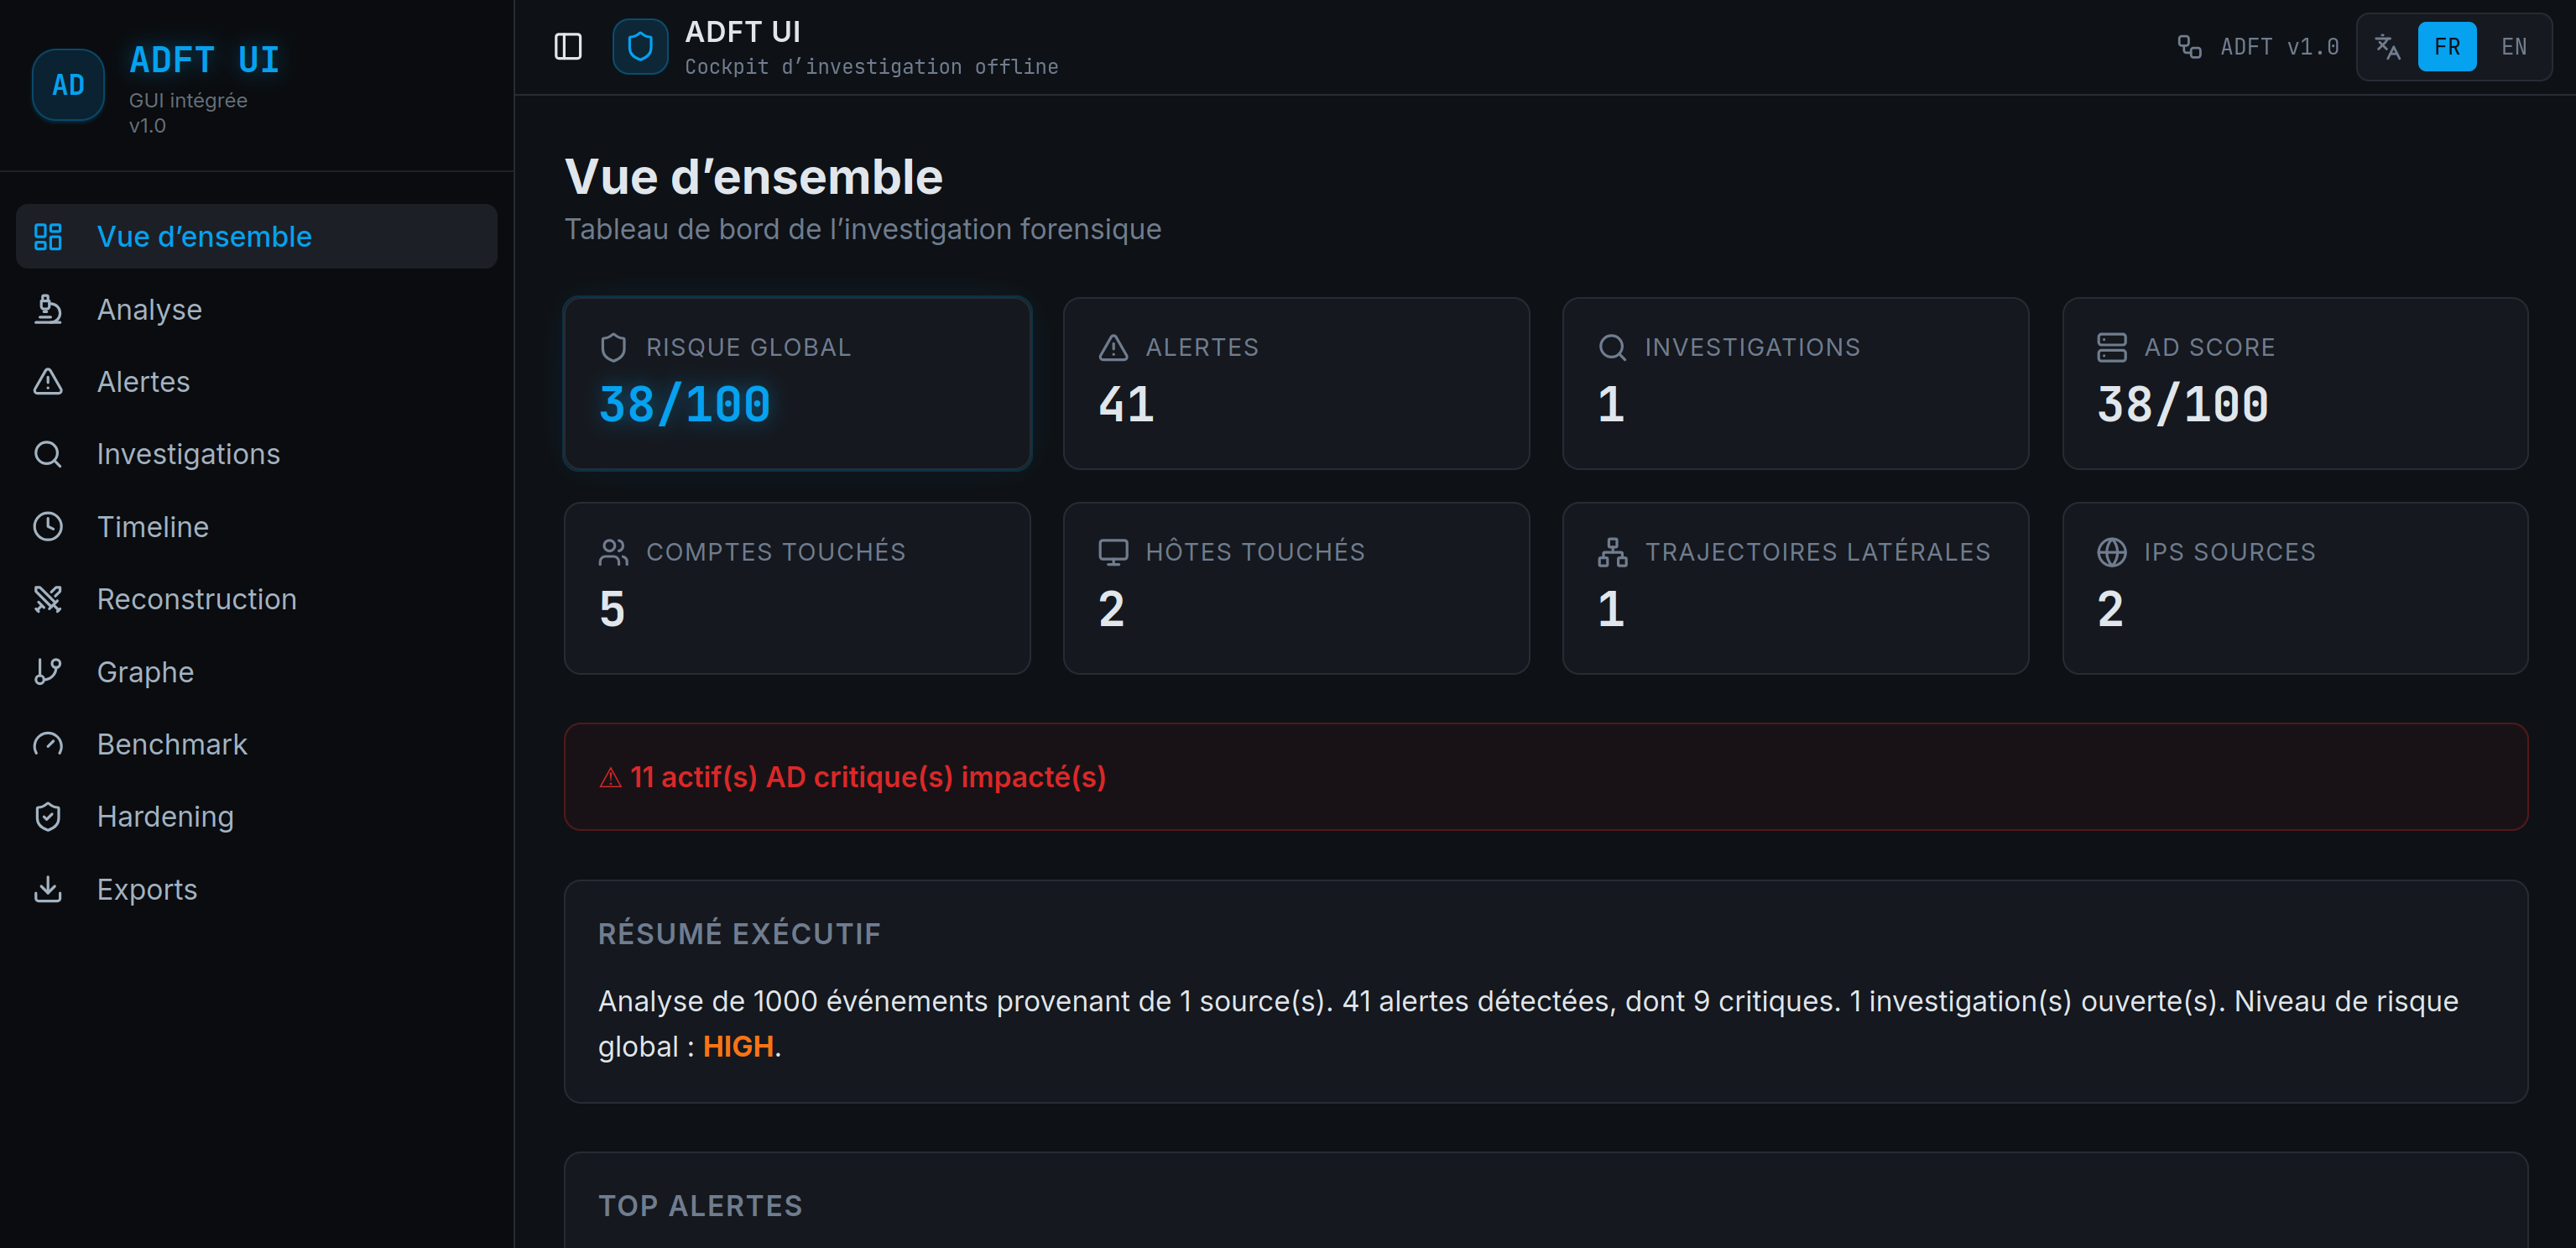 kjean13/adft
Active Directory Forensic Toolkit : Detect & reconstruct AD attacks from Windows event logs (EVTX)
 leandrofroes/malware-research
General malware analysis stuff