

Log4ShellAuditor
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
devsecopsexploitationlabs-practice+6
1
c00ln3t/log4shellauditorAn autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 cider-security-research/cicd-goat
A deliberately vulnerable CI/CD environment. Learn CI/CD security through multiple challenges.
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
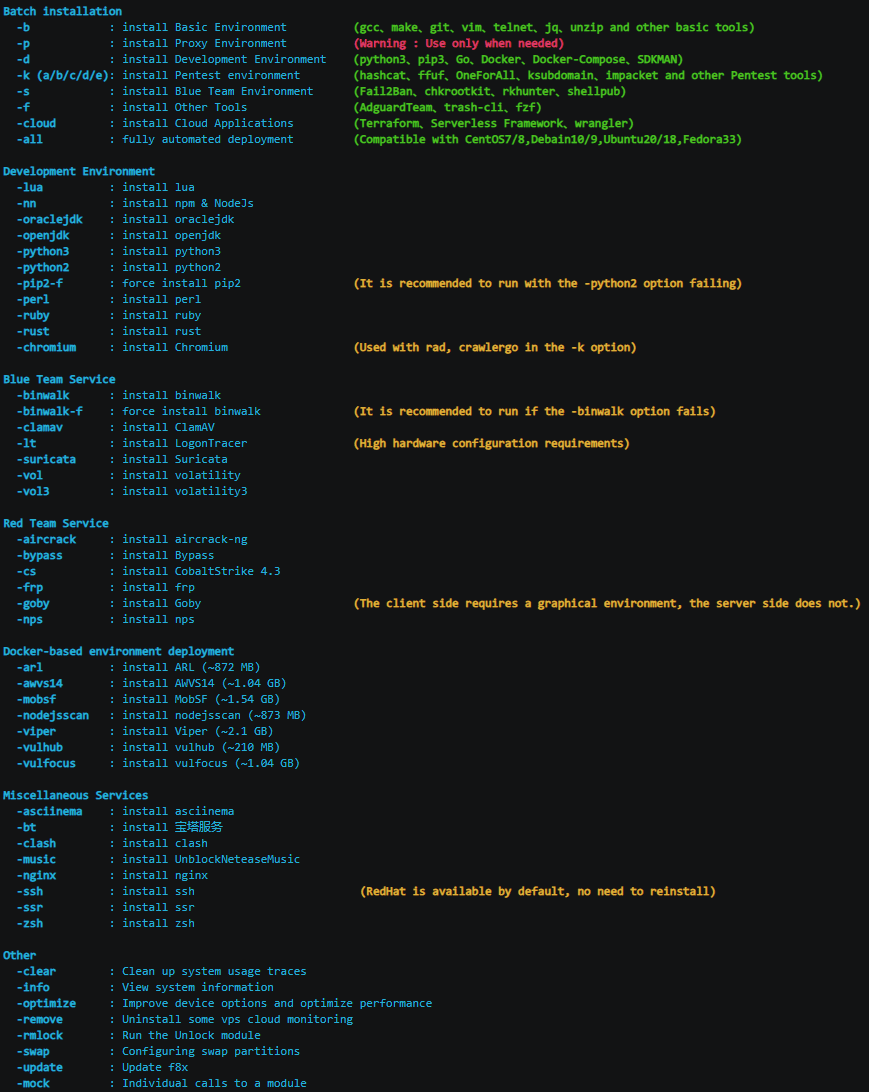 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 devsecops/awesome-devsecops
An authoritative list of awesome devsecops tools with the help from community experiments and contributions.
 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 npm/ansible-bashpocalypse
Patch for CVE-2014-6271
 terra-nova83/cve-2026-0915-json-patch.-v2.0
Provides a security patch for CVE-2026-0915, adding strict JSON schema validation, input sanitization, and rate limiting to prevent injection and DoS…
 gui/legacy-rails-cve-2020-5267-patch
Patch CVE-2020-5267 for Rails 4 and Rails 3
 drkbcn/lblfixer_cve_2023_30839
PrestaShop <1.7.8.9 Fix for CVE-2023-30839 and CVE-2023-30545
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
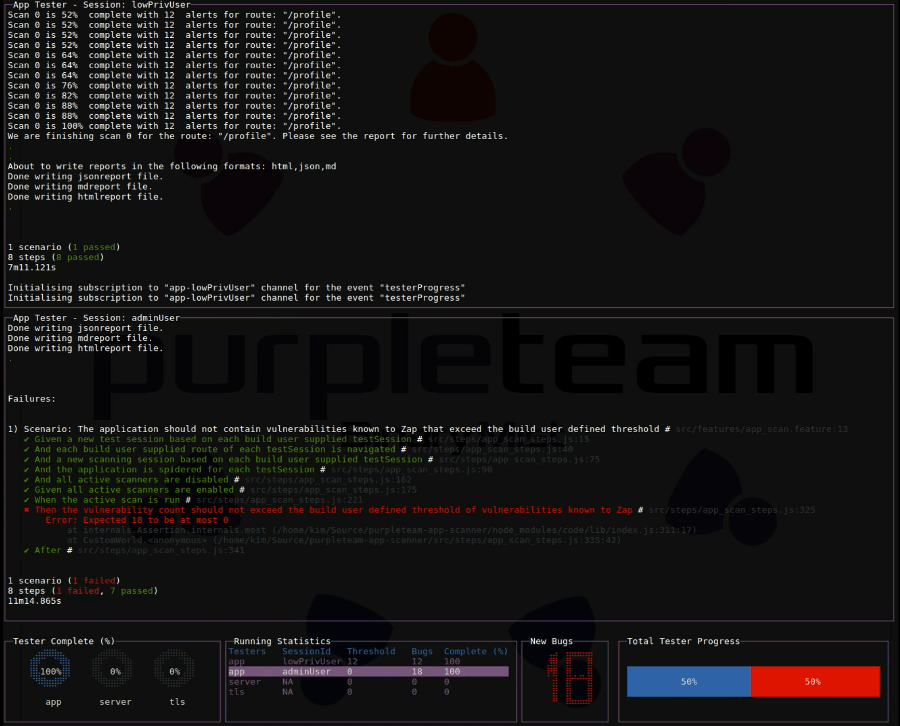 purpleteam-labs/purpleteam
CLI component of purpleteam