

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
16.0k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
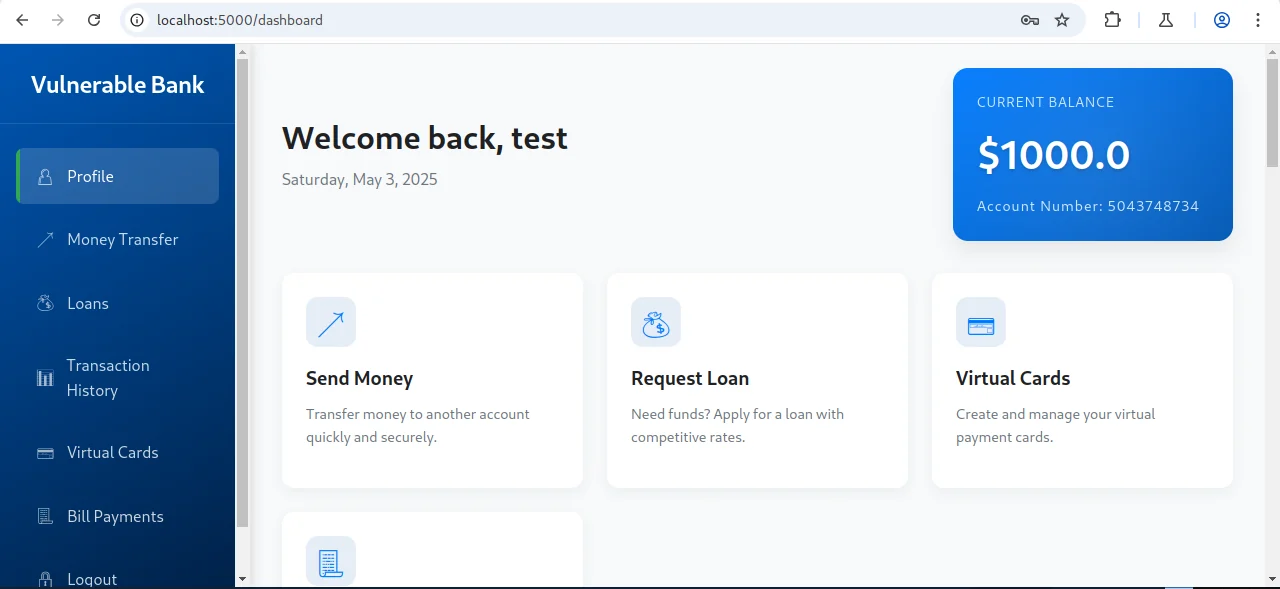 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
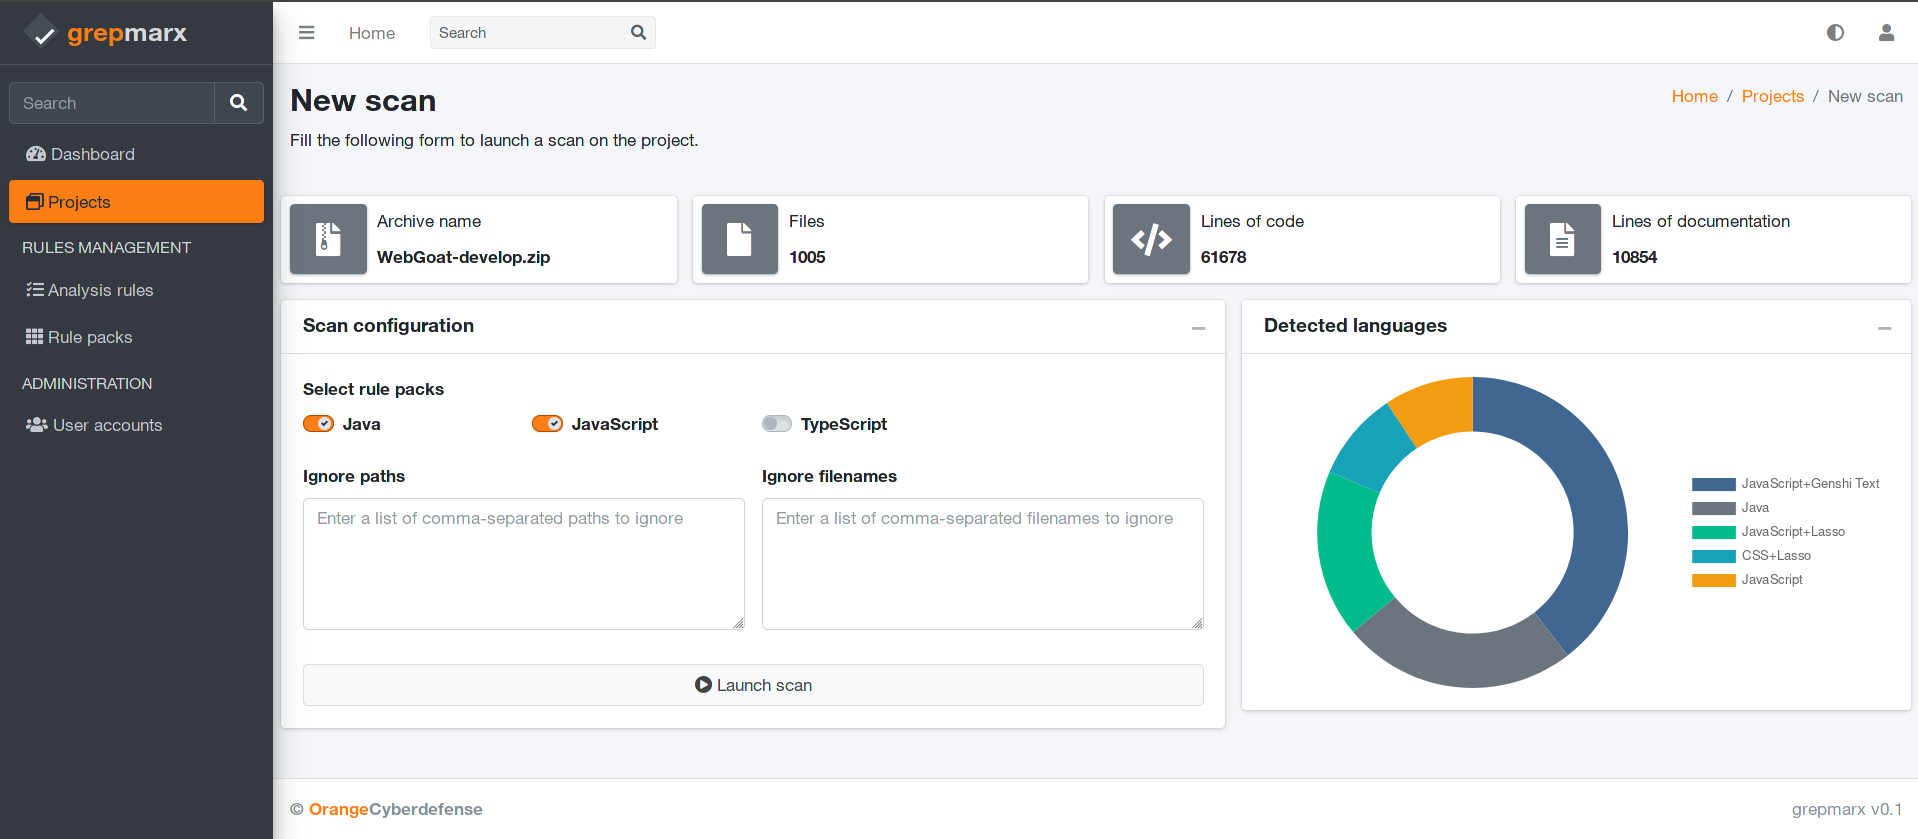 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
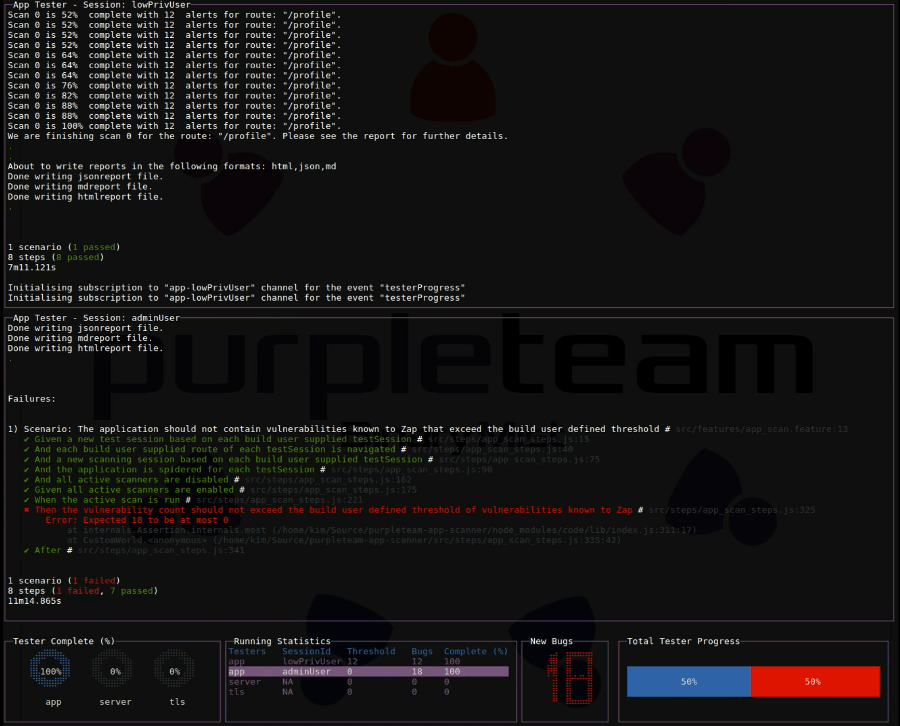 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam