

bearer
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
code-analysisdevsecopsprivacy+3
2.7k3 days ago
bearer/bearerCode security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
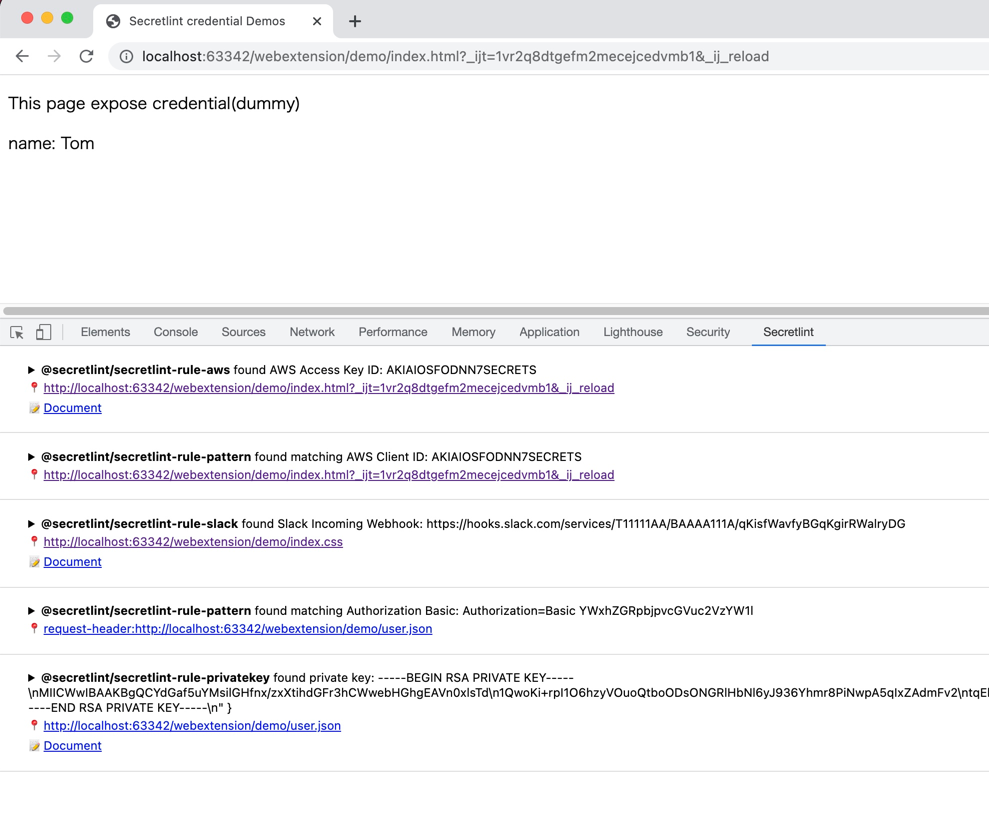 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 faloker/purify
All-in-one tool for managing vulnerability reports from AppSec pipelines
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…