
CVE-2026-24733
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
configuration-auditingdefensive-toolsdevsecops+4
darabium/cve-2026-24733Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 danielmadsendk/servicenow-cve-2025-11449-cve-2025-11450-mitigation-script
Automated detection and remediation of ServiceNow UI Macro vulnerabilities (CVE-2025-11449, CVE-2025-11450) by encoding sysparm_ parameters to…
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 jenkinsci-cert/security-3314-3315
Workaround for disabling the CLI to mitigate SECURITY-3314/CVE-2024-23897 and SECURITY-3315/CVE-2024-23898
 nomograph/kit
Verified tool registry manager. Manages developer toolchains from git-based registries.
 opnsense/core
OPNsense GUI, API and systems backend
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.

 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
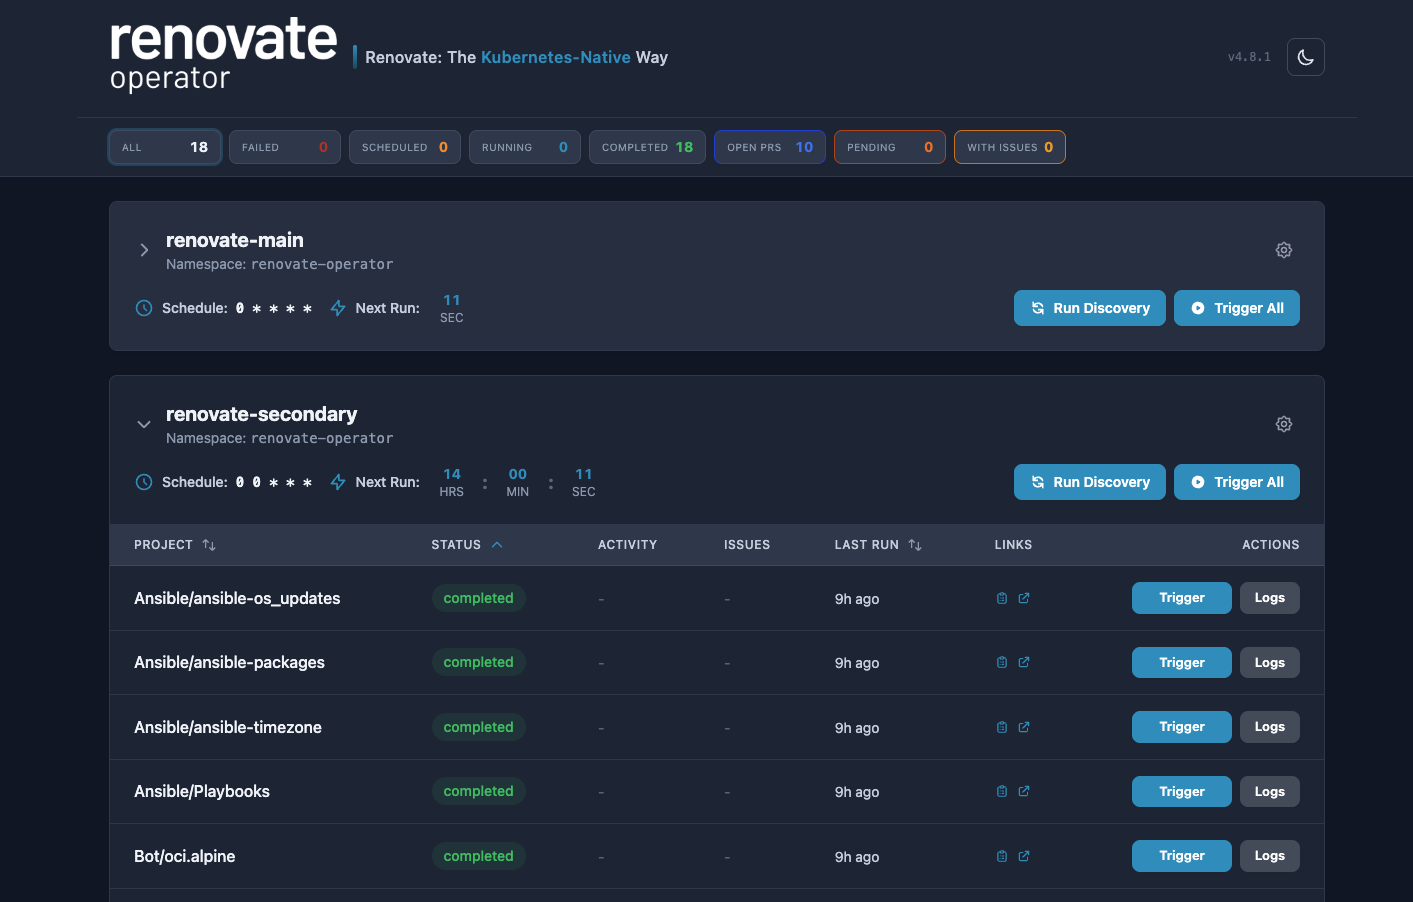 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 ajf8729/blacklotus
BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use
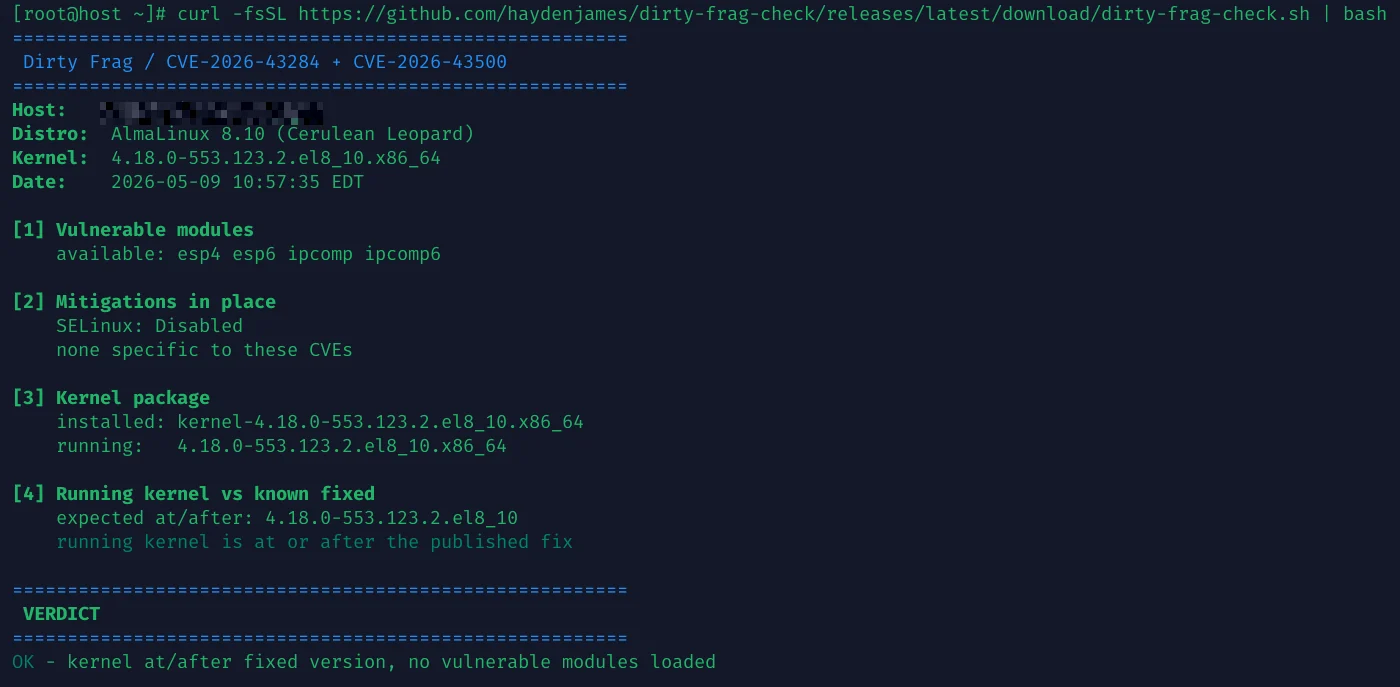 haydenjames/dirty-frag-check
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns