httpx-action
 projectdiscovery/httpx-action
HTTP Web Server probing
devsecopsinformation-gatheringnetwork-mapping+3
142 years ago
projectdiscovery/httpx-actionHTTP Web Server probing
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
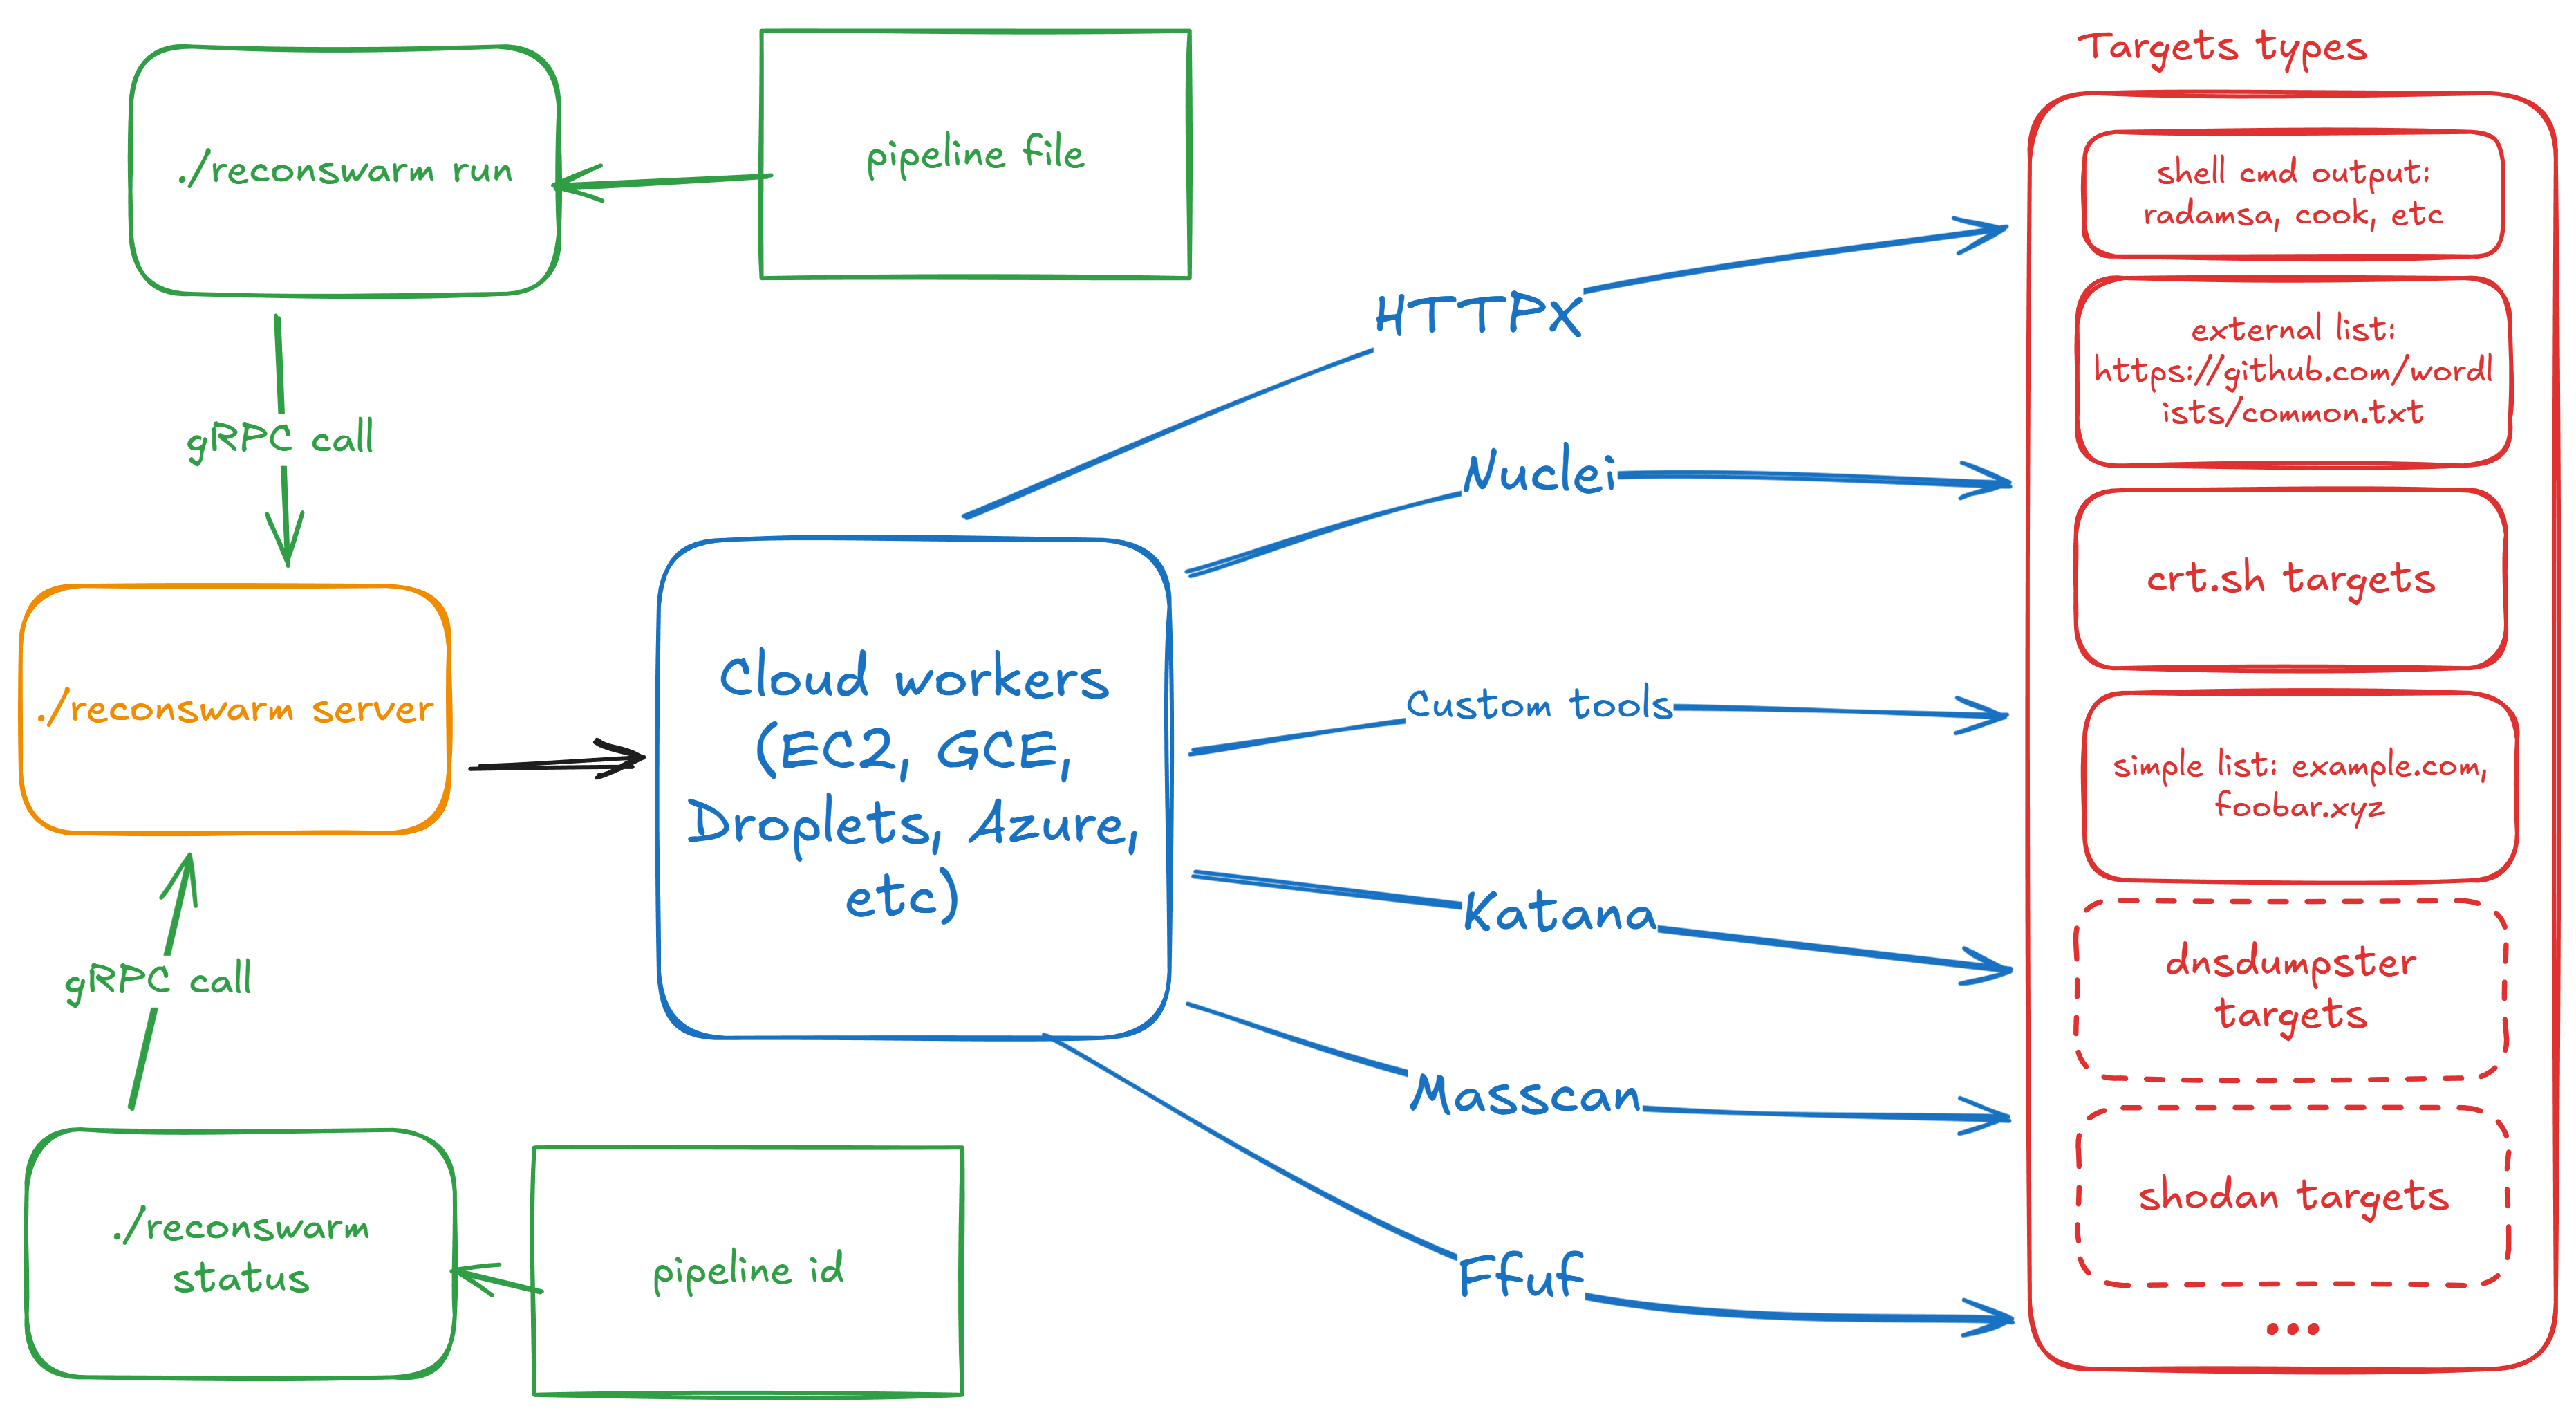 renatus-cartesius/reconswarm
Extend your recon with cloud power
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
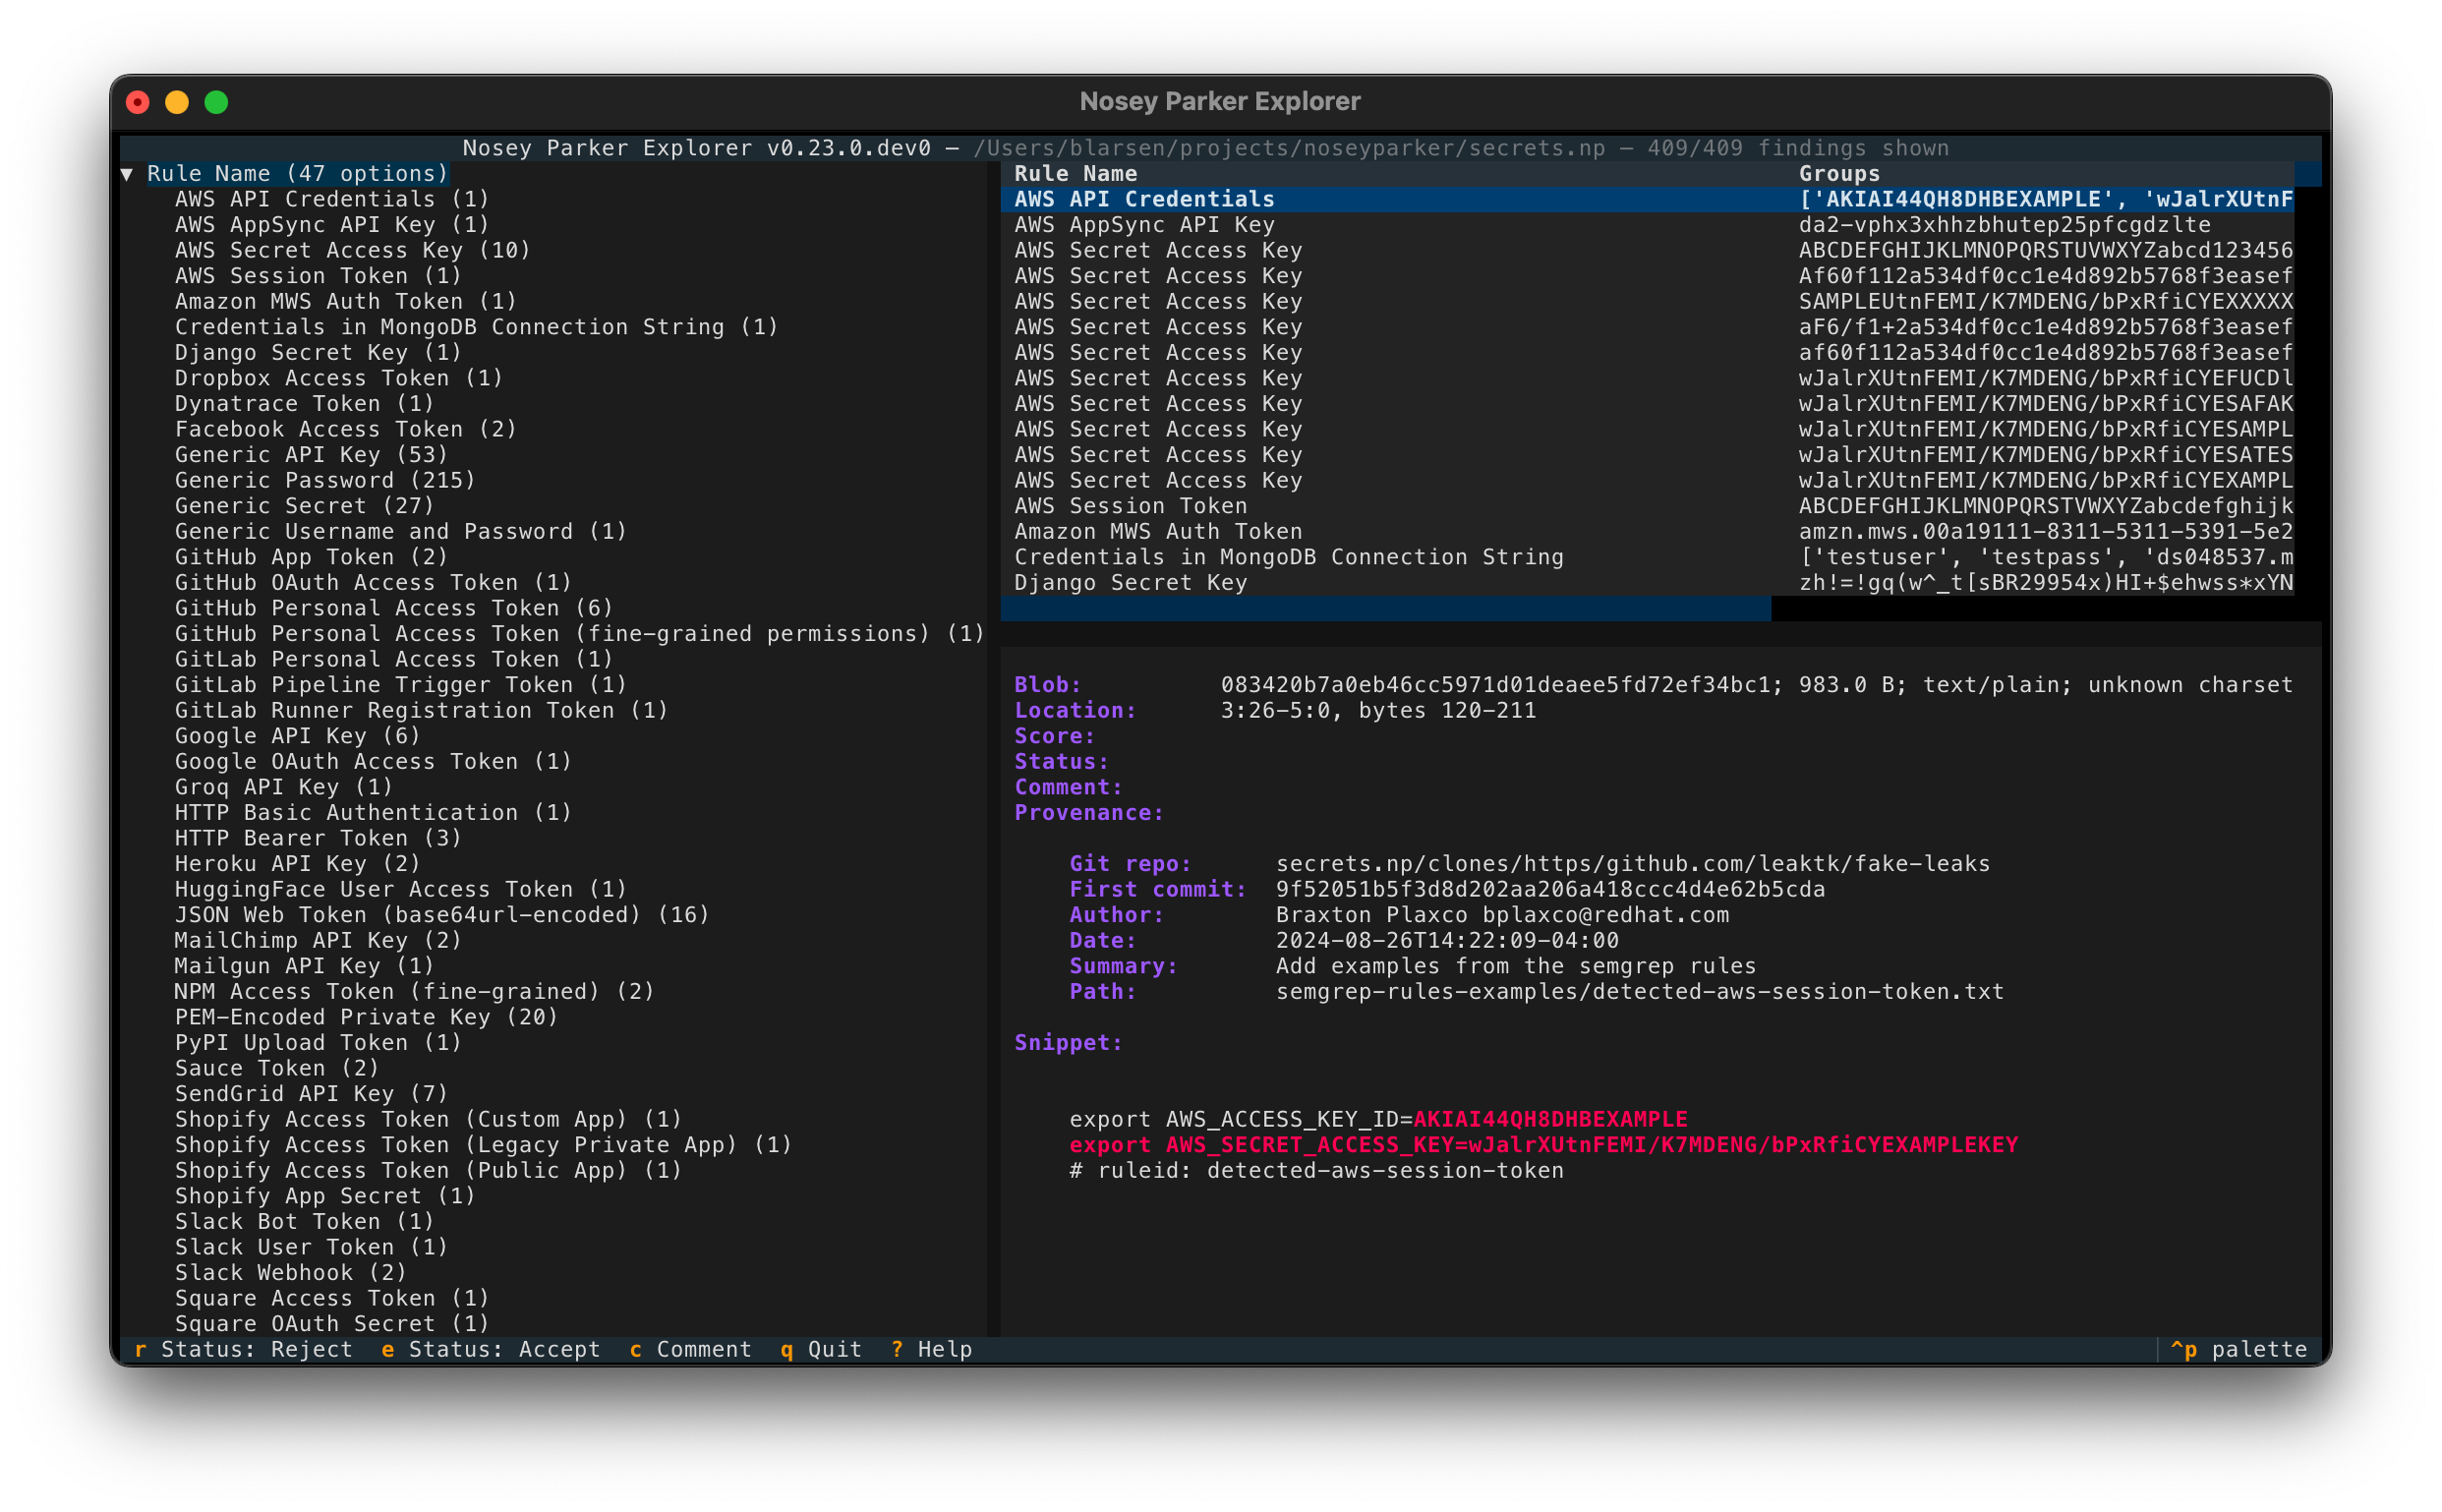 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover