
Archived
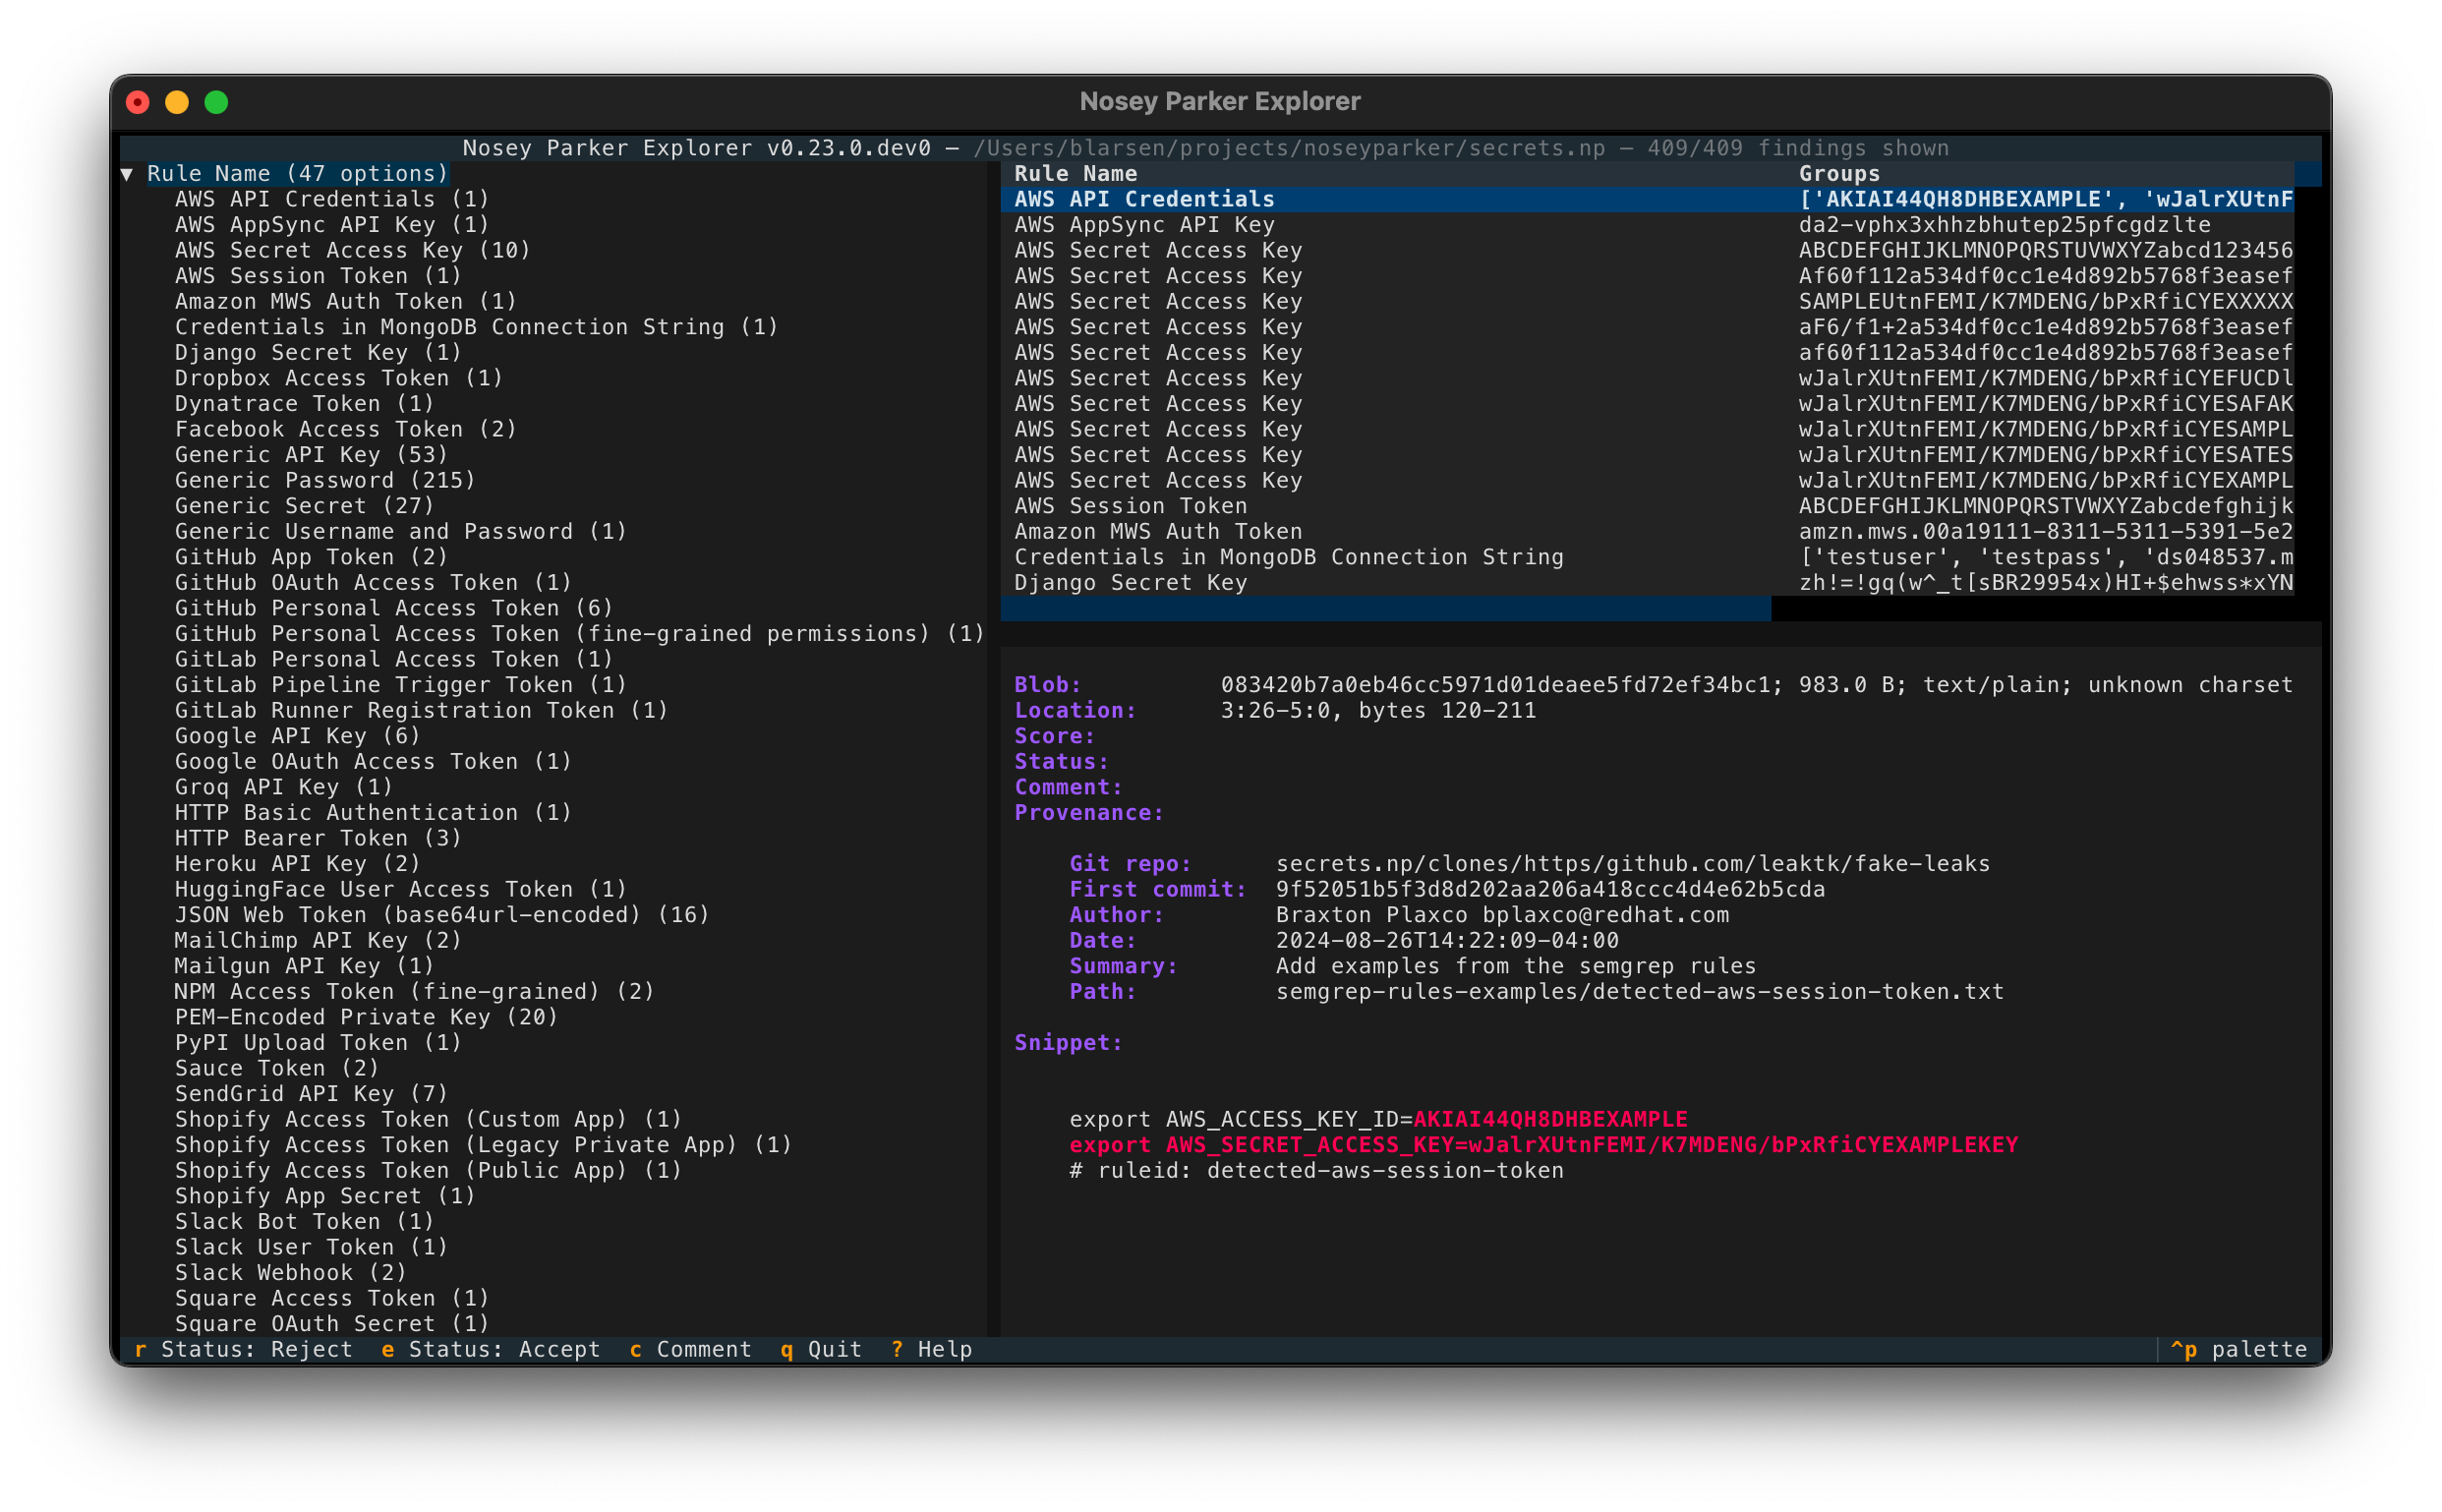
 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 ansvar-systems/eu_compliance_mcp
EU focused compliance MCP server
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 guilherme-grimm/graph-go
simply nodes and graphs
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 projectdiscovery/httpx-action
HTTP Web Server probing
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 nu11secur1ty/kali-linux-docker
kali-linux-docker
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 papermtn/gitlab-watchman
Finding exposed secrets and personal data in GitLab
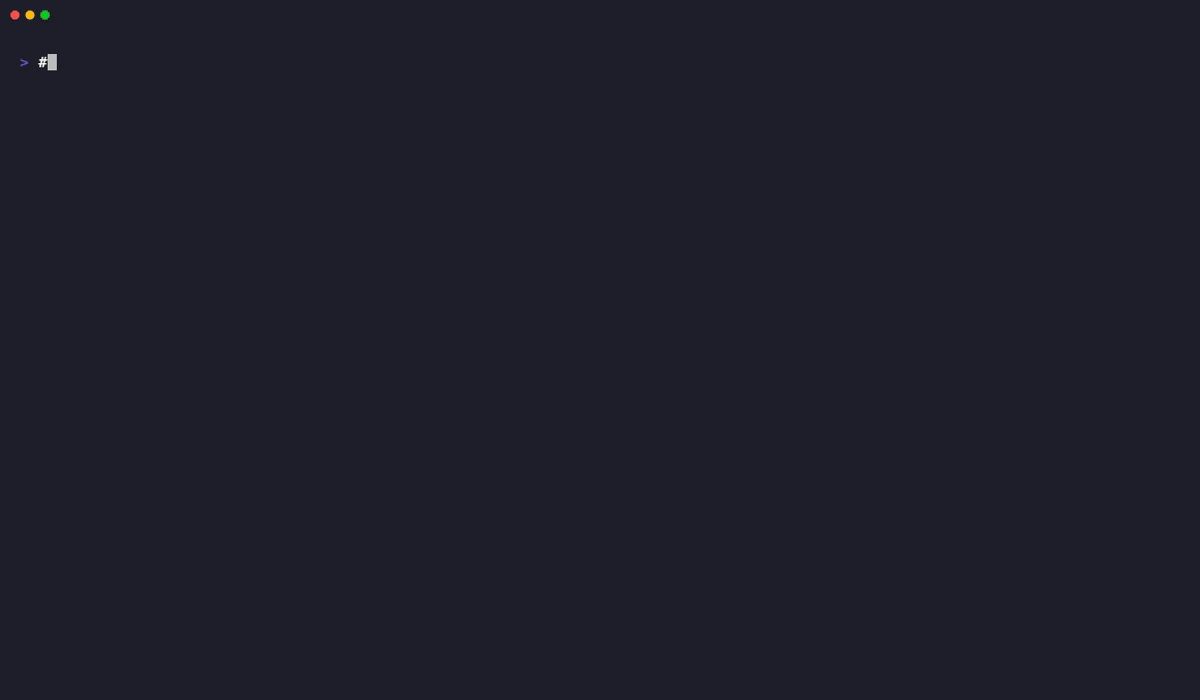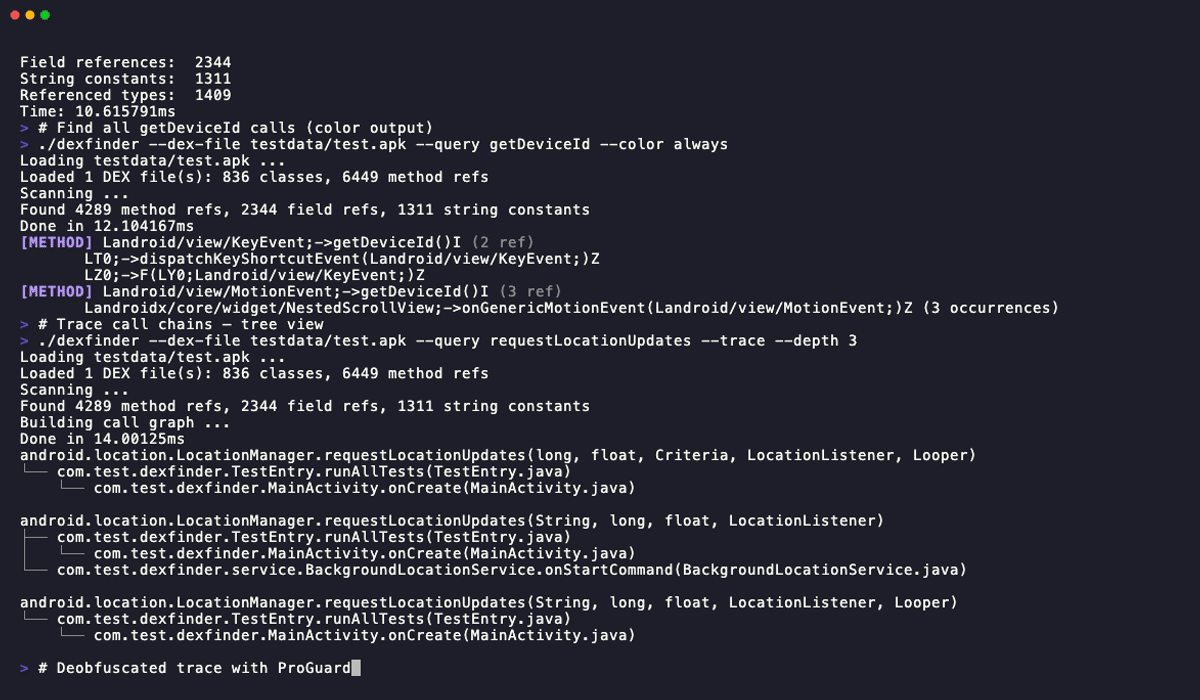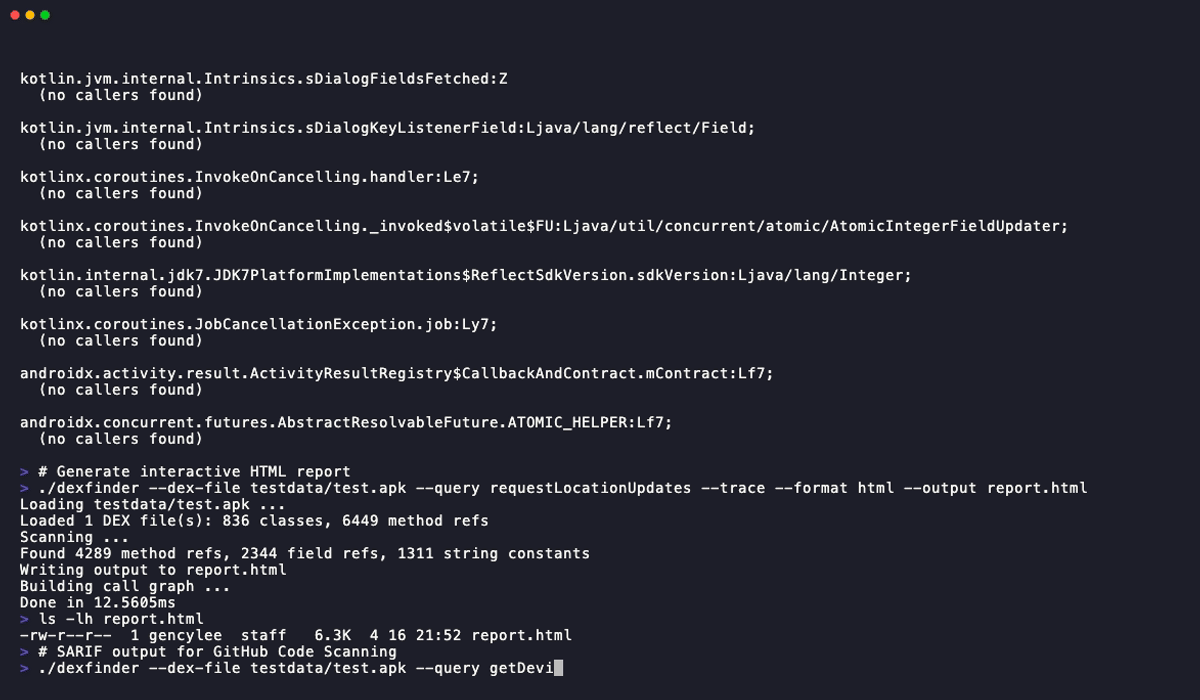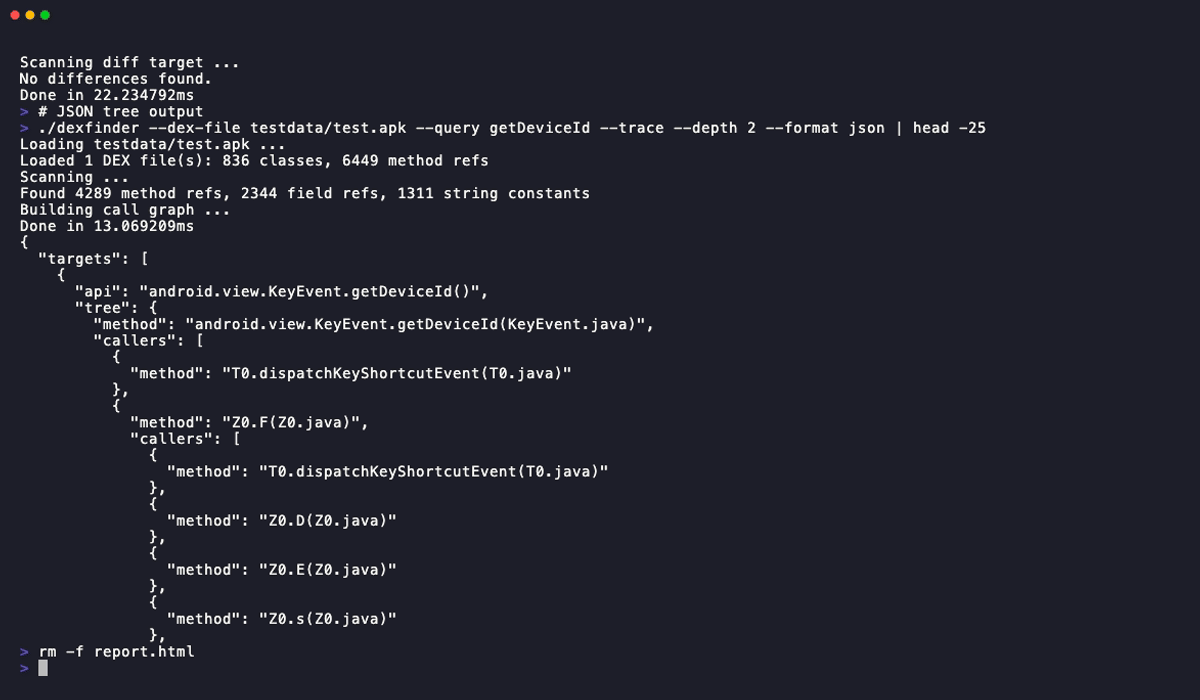 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection