seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

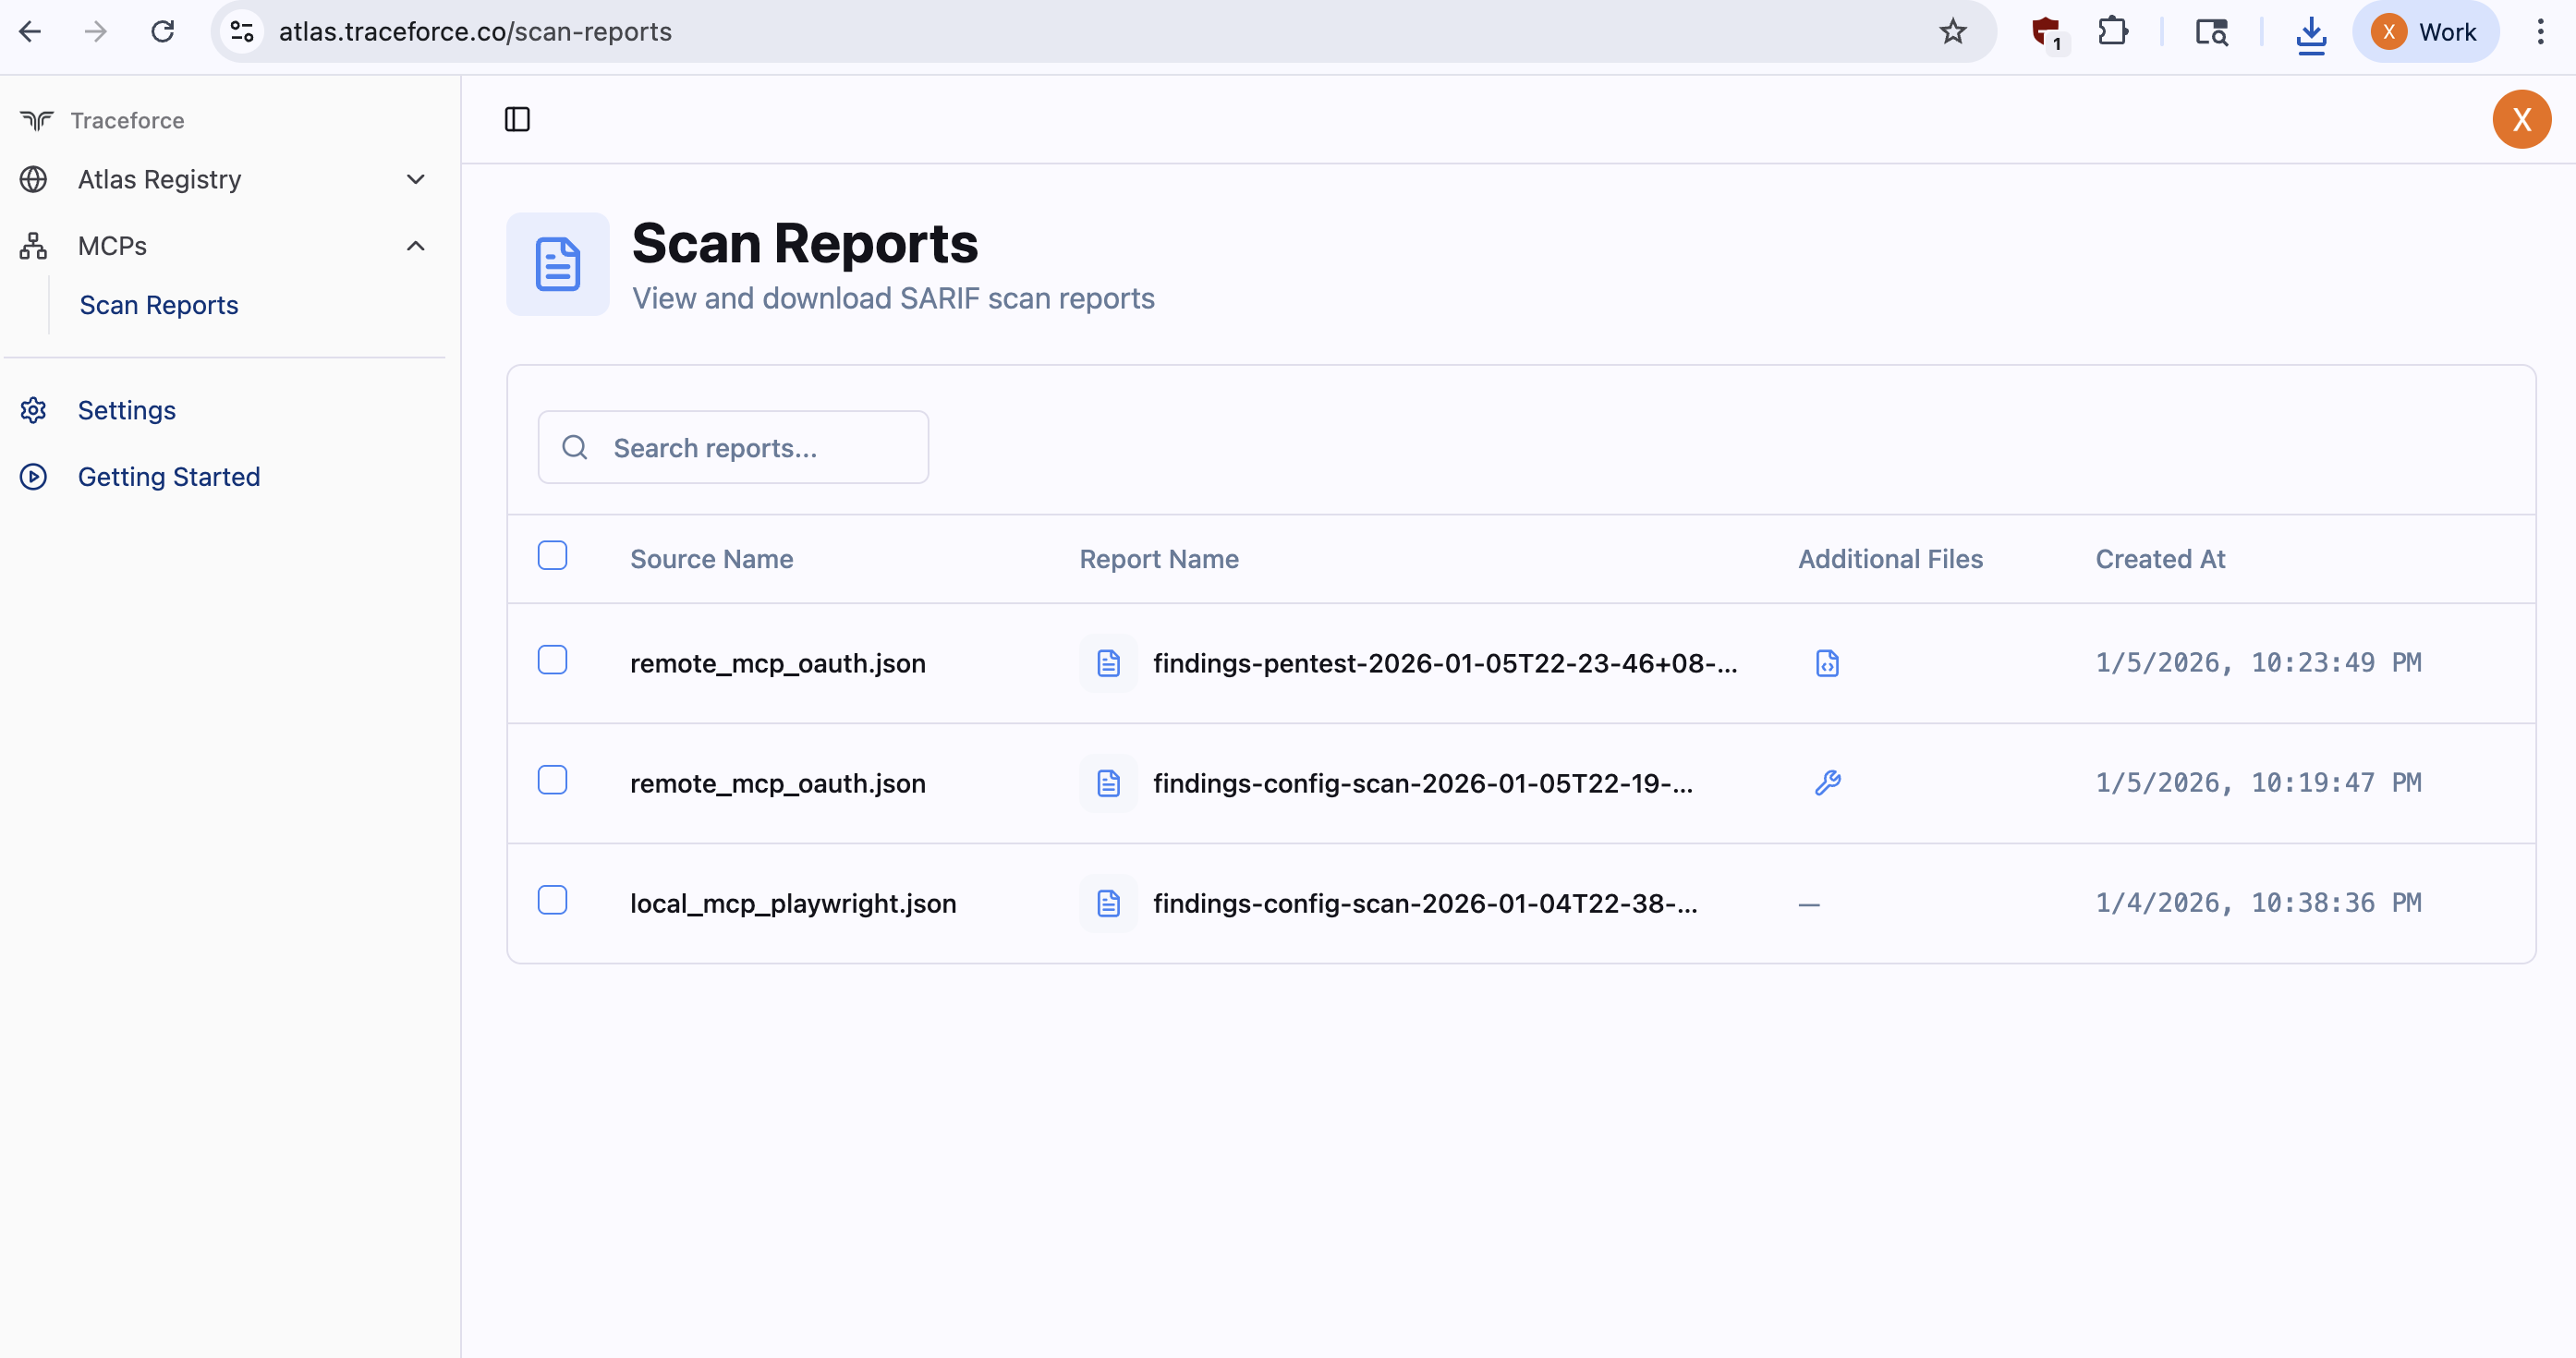
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

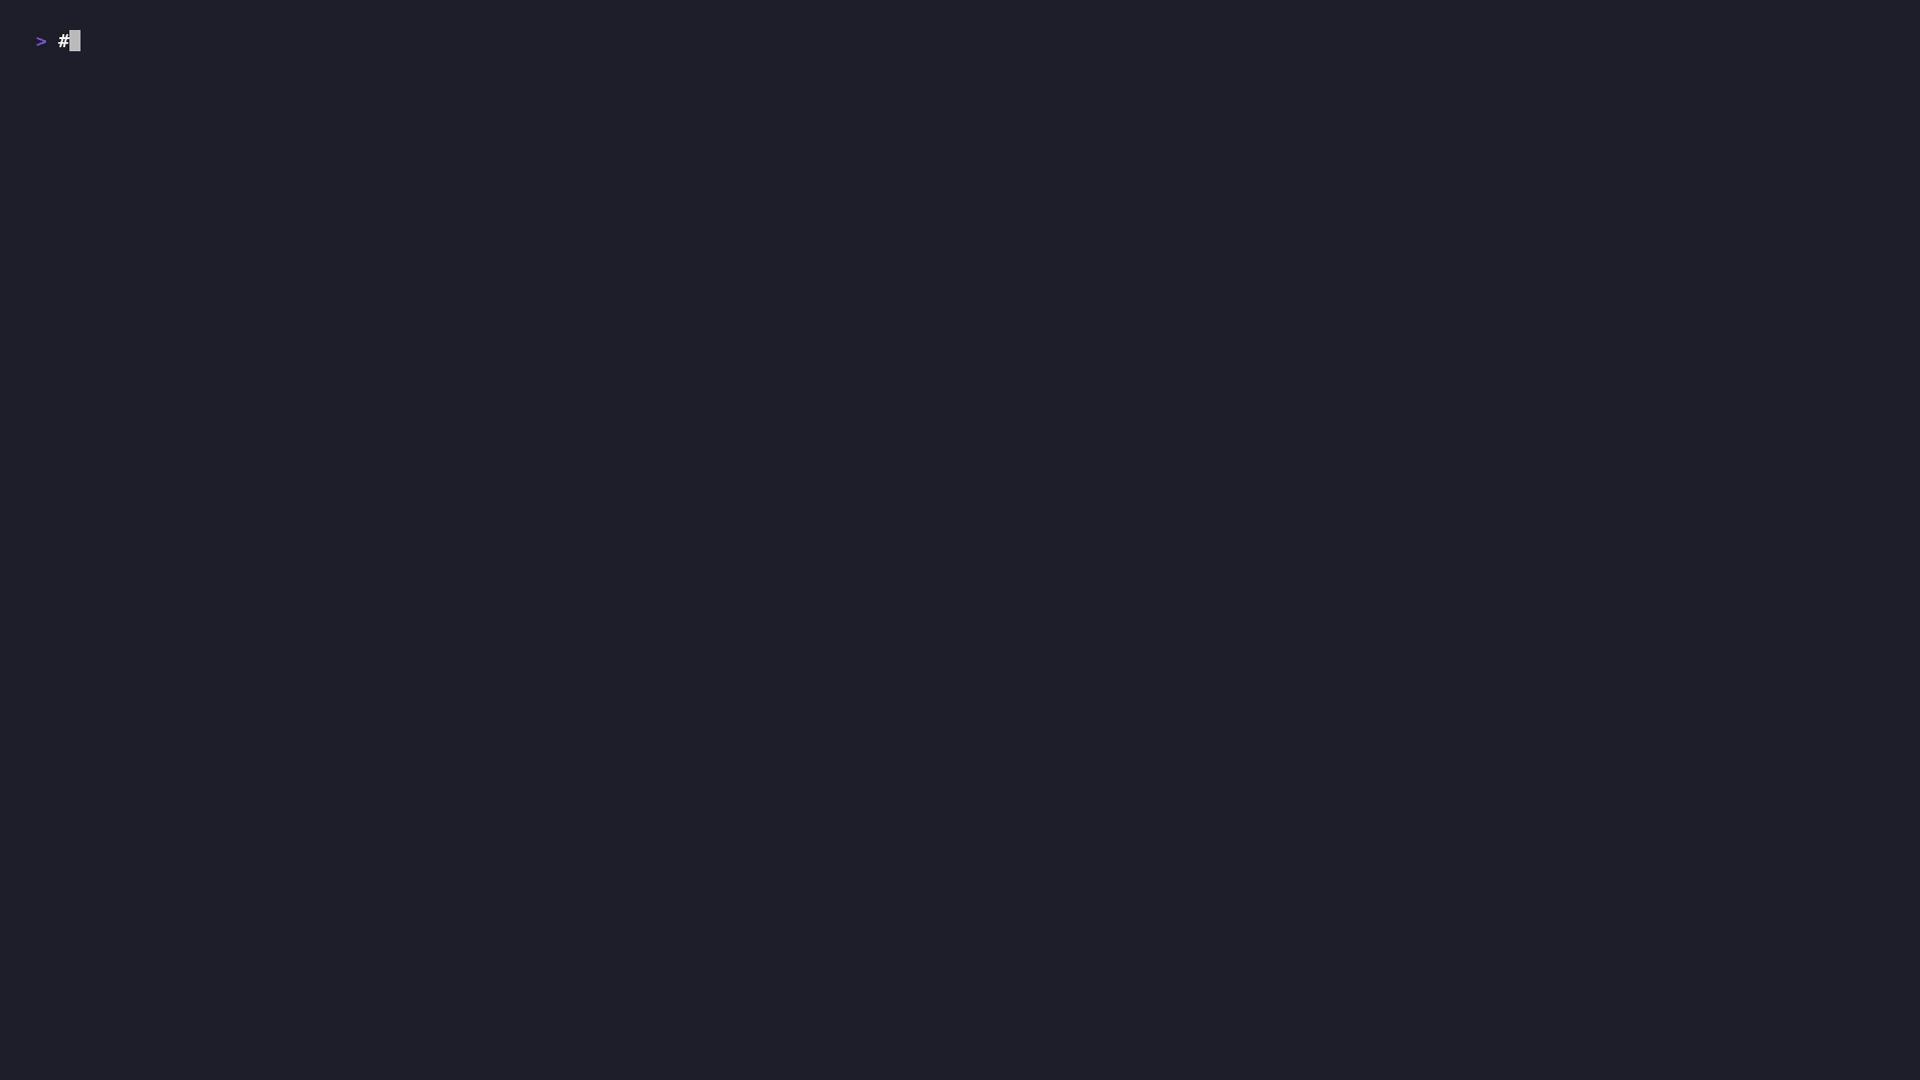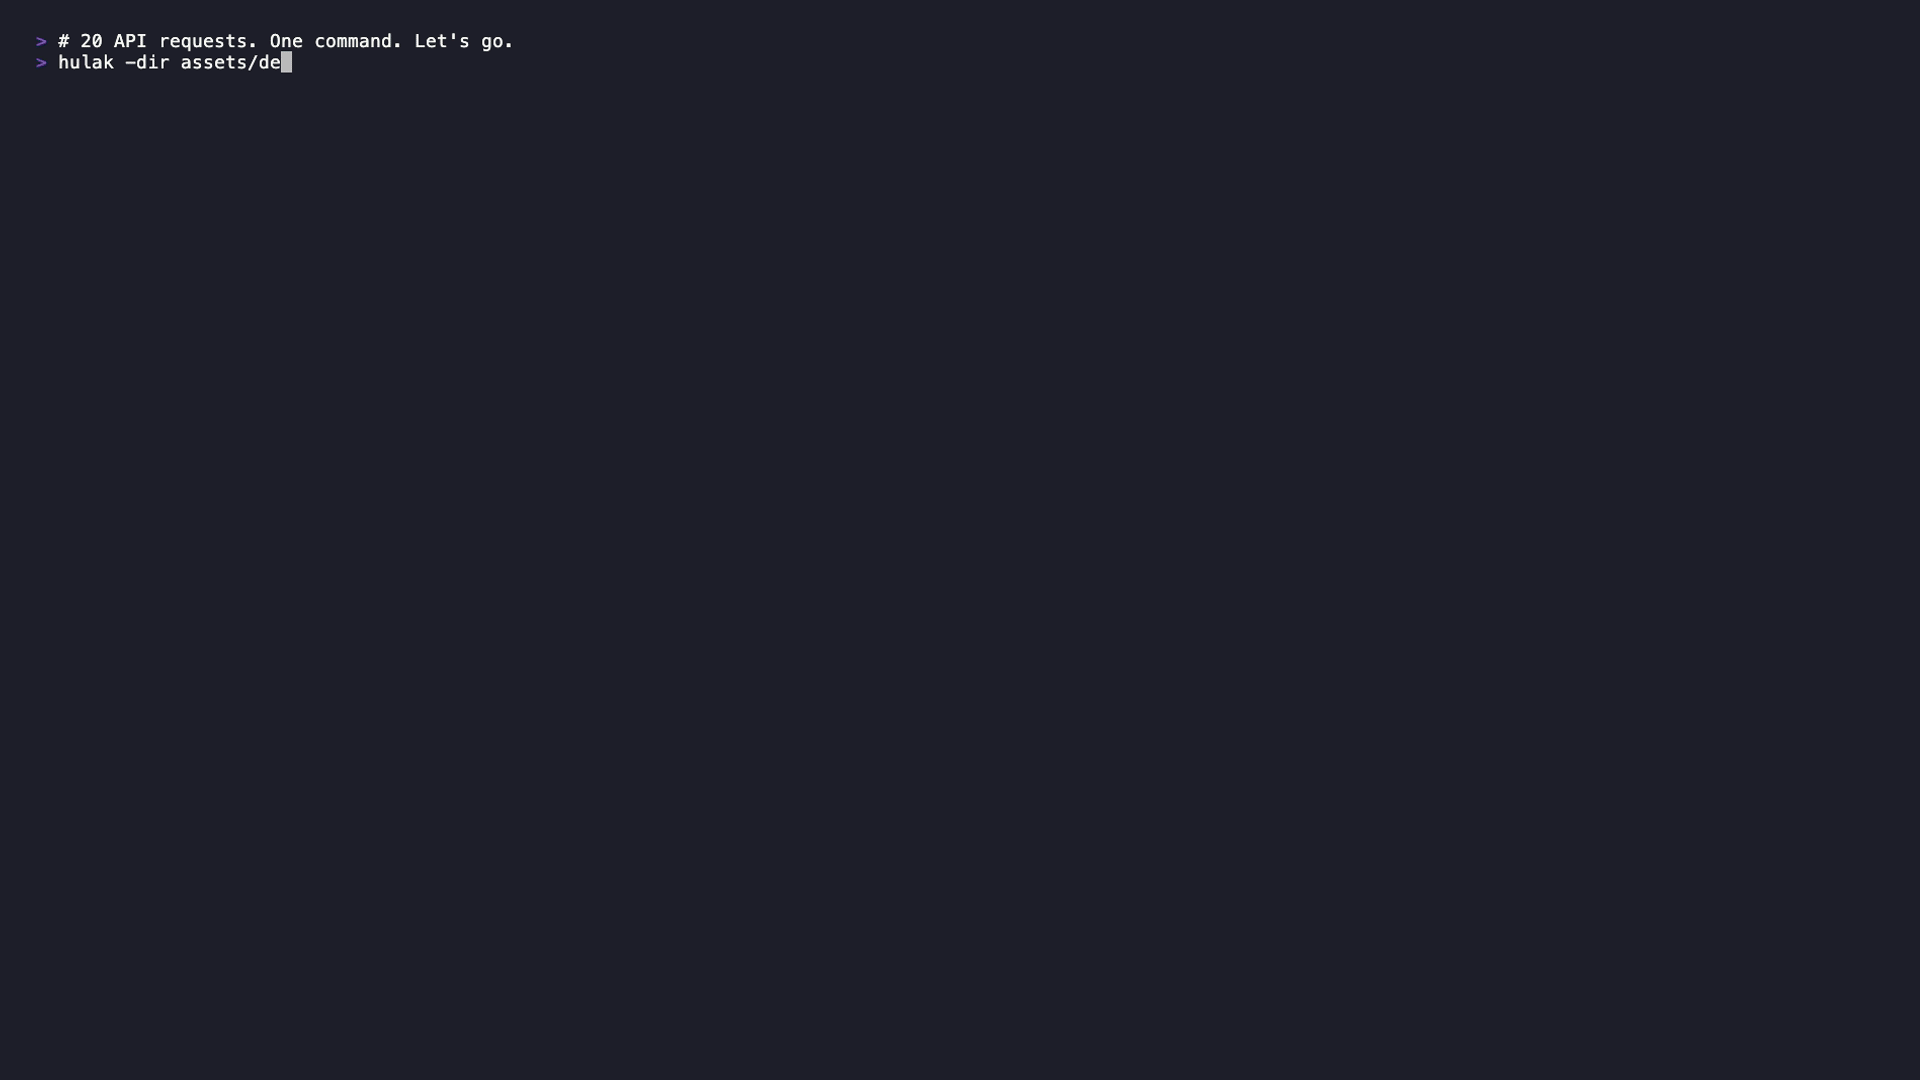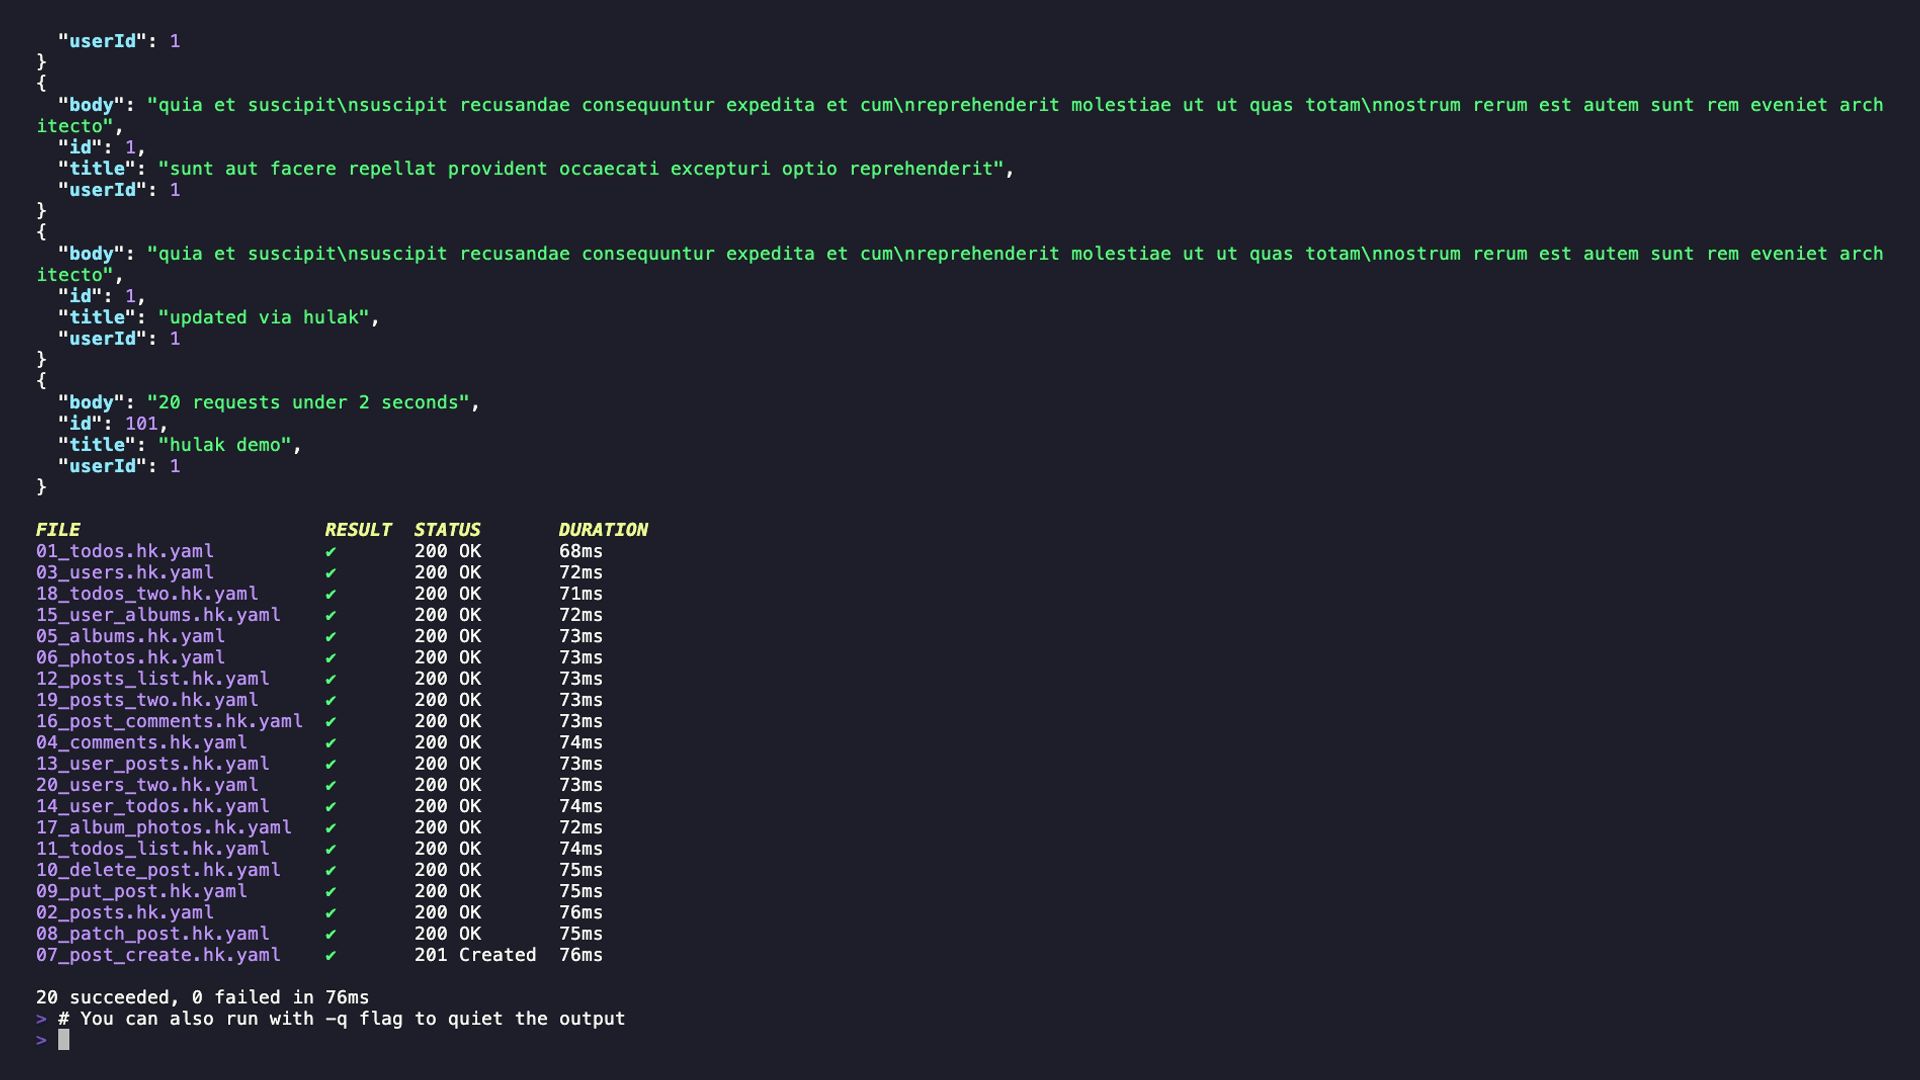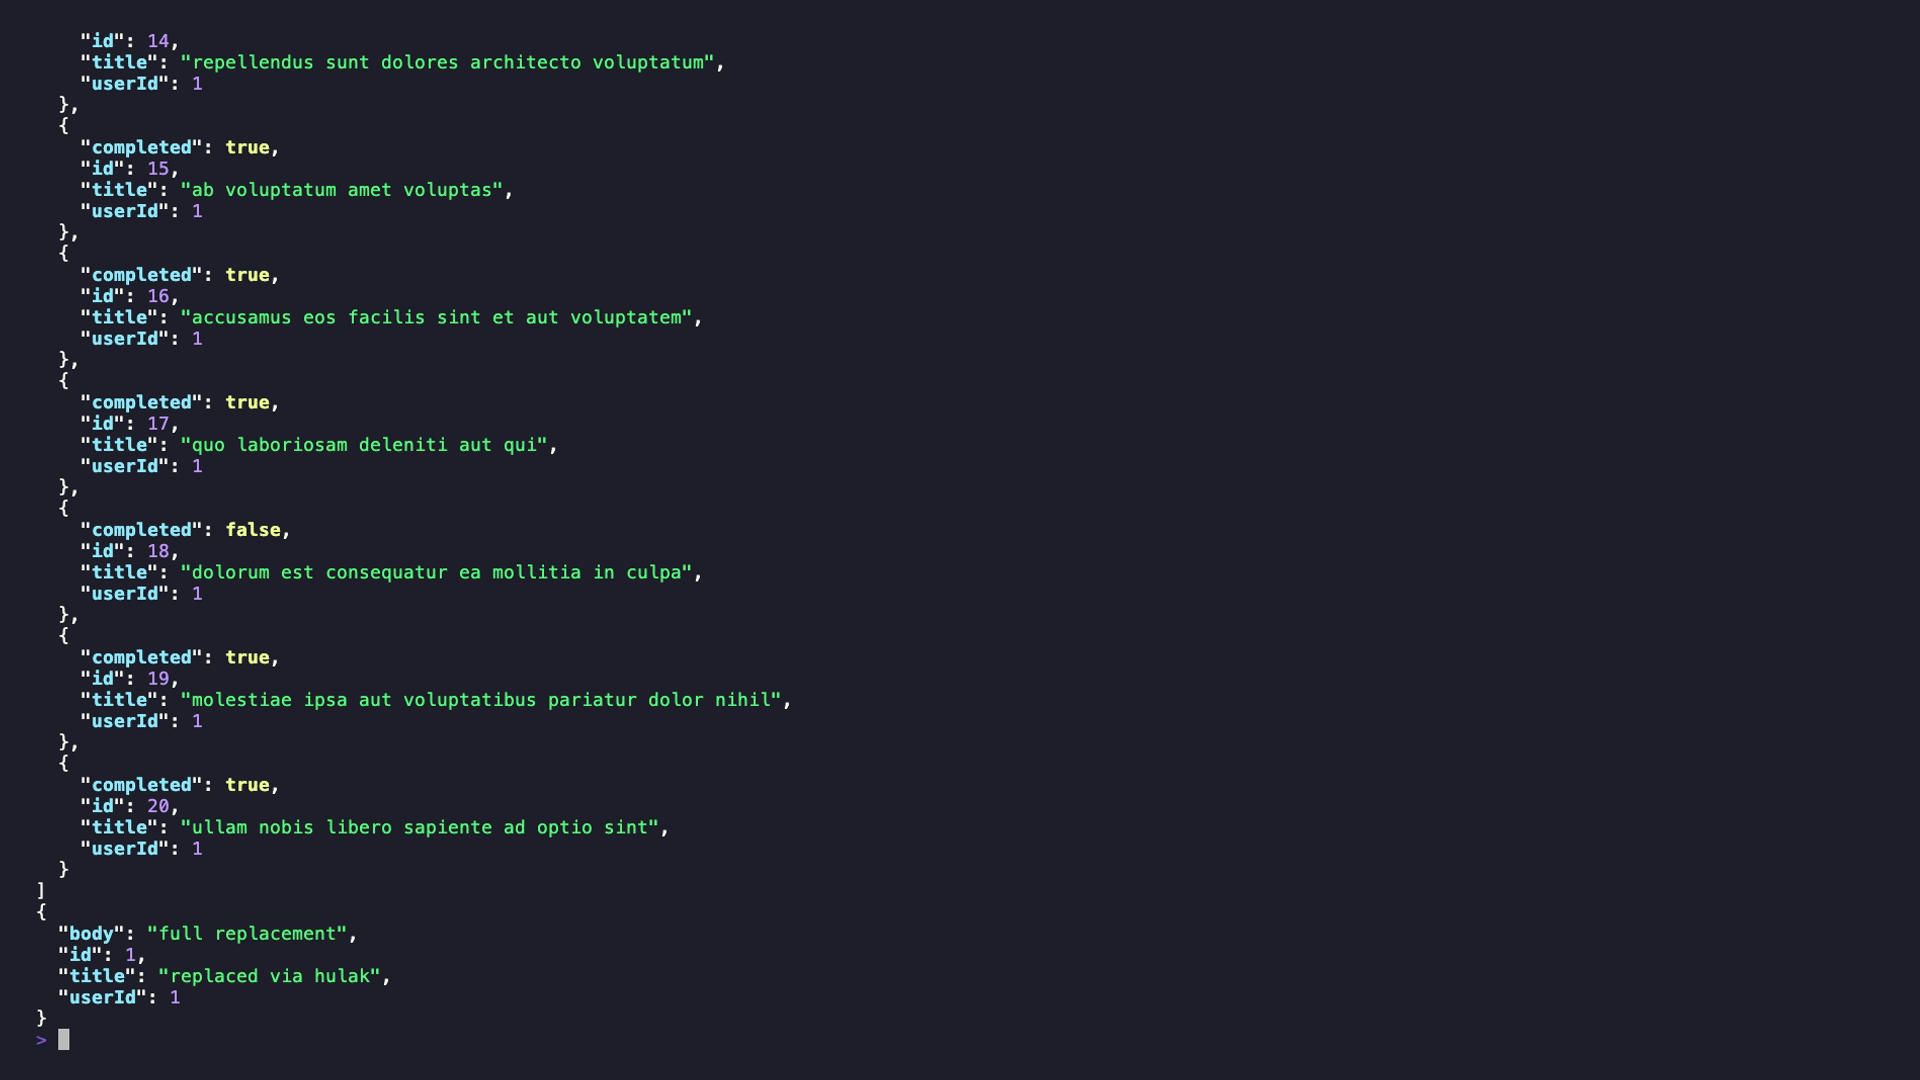
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.

Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

MCP server for Slither static analysis of Solidity smart contracts

Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection

CLI tool for the Horizon3.ai API

A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.

Vulnerability Assessment Scanner with Report Generation

Burp Extension for collaboration in Faraday

Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…