

windows-security-cve-2017-8543
 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543
cloud-securityconfiguration-auditingdevsecops+1
americanhanko/windows-security-cve-2017-8543InSpec profile to verify a node is patched and compliant for CVE-2017-8543
 shoucheng3/apache__dolphinscheduler_cve-2023-51770_3_2_1_fixed
Exploit for CVE-2023-51770 targeting Apache DolphinScheduler versions 3.2.1 and earlier, enabling remote code execution via crafted workflow…
 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
 moisei-dev/go-dbmigrate
Go library and CLI for managing database schema migrations with support for PostgreSQL, MySQL, SQLite, and Cassandra, including up/down migration…
 renanvicente/puppet-shellshock
This module determine the vulnerability of a bash binary to the shellshock exploits (CVE-2014-6271 or CVE-2014-7169) and then patch that where…
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 nickanderson/cfengine-cve-2016-2118
An example detection and remediation policy.
 mrmahile/massscanning-cve-2025-55182
A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…
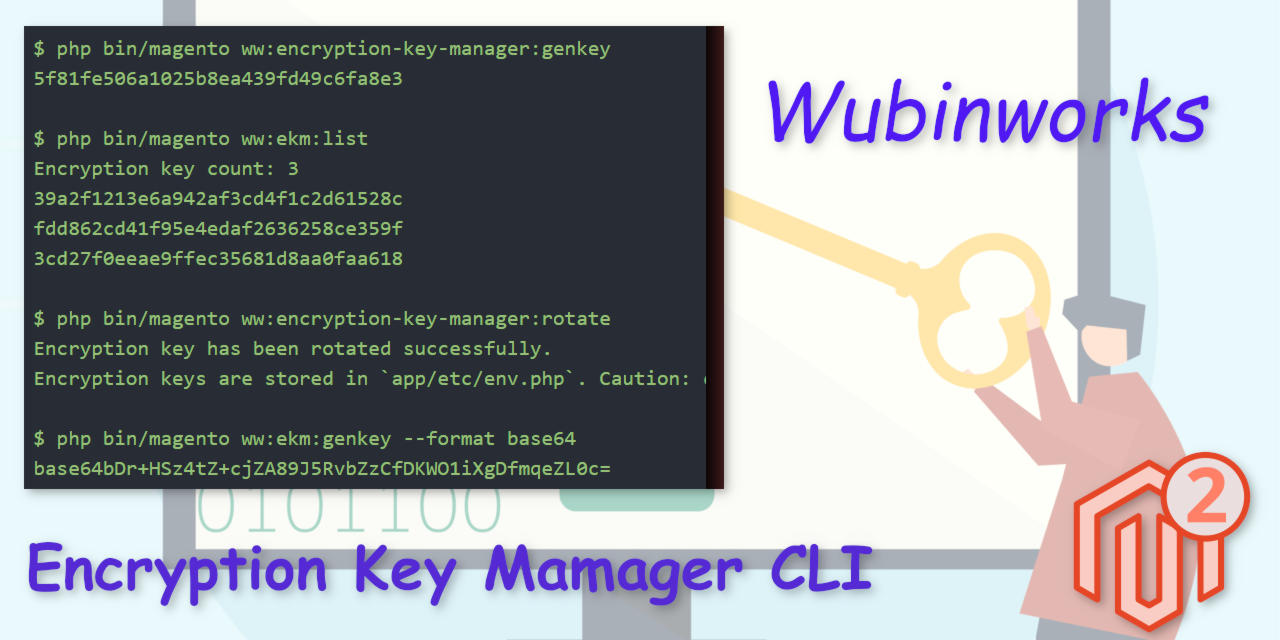 wubinworks/magento2-encryption-key-manager-cli
A utility for Magento 2 encryption key rotation and management. CVE-2024-34102(aka Cosmic Sting) victims can use it as an aftercare.
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 gina-alaska/bash-cve-2014-7169-cookbook
Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.
 shoucheng3/payara__payara_cve-2022-37422_5-2022-2
Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 konstantin-kelemen/mysqld_safe-cve-2016-6662-patch
Ansible playbook that applies the Percona patch for CVE-2016-6662 to the mysqld_safe file on CentOS and FreeBSD systems.
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…