
Archived
raptor
 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
android-securitycode-analysisdevsecops+6
356
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 lintsinghua/deepaudit
DeepAudit:人人拥有的 AI 黑客战队,让漏洞挖掘触手可及。国内首个开源的代码漏洞挖掘多智能体系统。小白一键部署运行,自主协作审计 + 自动化沙箱 PoC 验证。支持 Ollama 私有部署 ,一键生成报告。支持中转站。让安全不再昂贵,让审计不再复杂。
 devsecops/awesome-devsecops
An authoritative list of awesome devsecops tools with the help from community experiments and contributions.
 cider-security-research/cicd-goat
A deliberately vulnerable CI/CD environment. Learn CI/CD security through multiple challenges.
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 owasp/security-culture
OWASP Security Culture repository
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
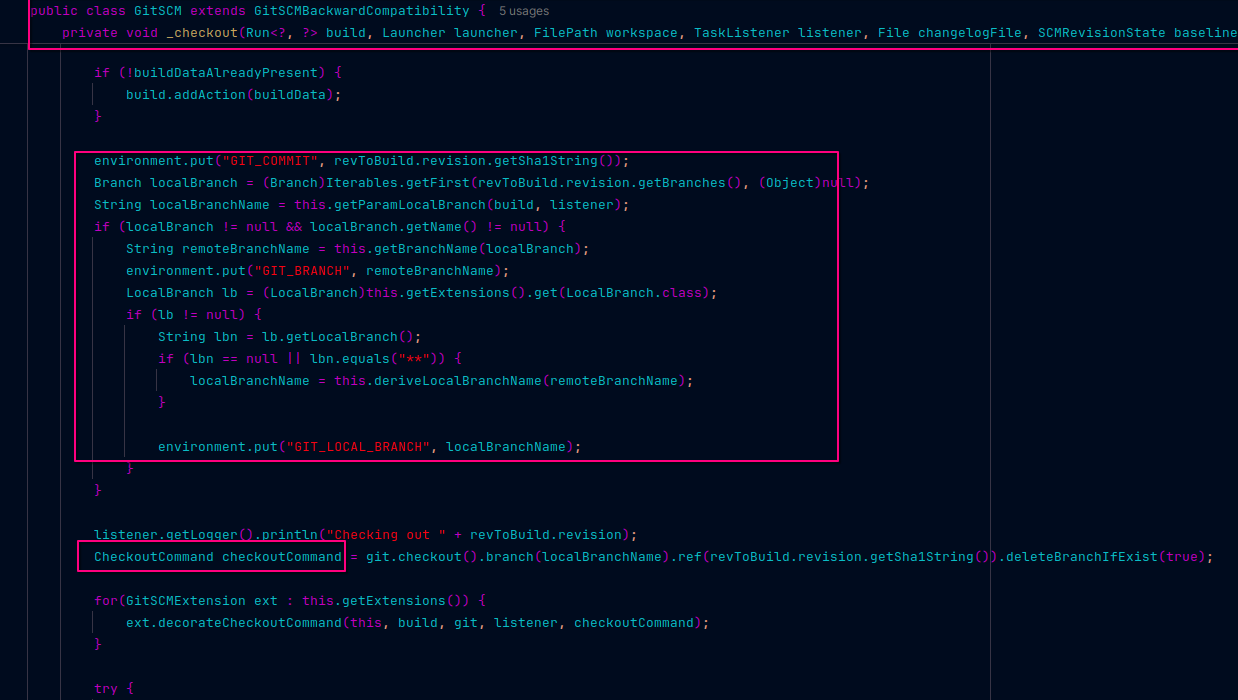 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 bhimsekhar/vulnerable-java-app
Spring Boot app with log4j 2.14.1 (CVE-2021-44228) — VulnFix agent test target
 delvygonzalez/react2shell-security-toolkit
Security toolkit to detect CVE-2025-55182 (React2Shell) vulnerability
 hamm0nz/react2shell-audit
A lightweight, recursive Bash script to detect Next.js and React Server DOM versions vulnerable to CVE-2025-55182 (React2Shell) in local projects.

 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 jeremylong/dependencycheck
The dependency-check repository has moved: