

NemoClaw
 nvidia/nemoclaw
Run agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
ai-securitycloud-securitycontainer-security+4
nvidia/nemoclawRun agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 ossf/allstar
GitHub App to set and enforce security policies
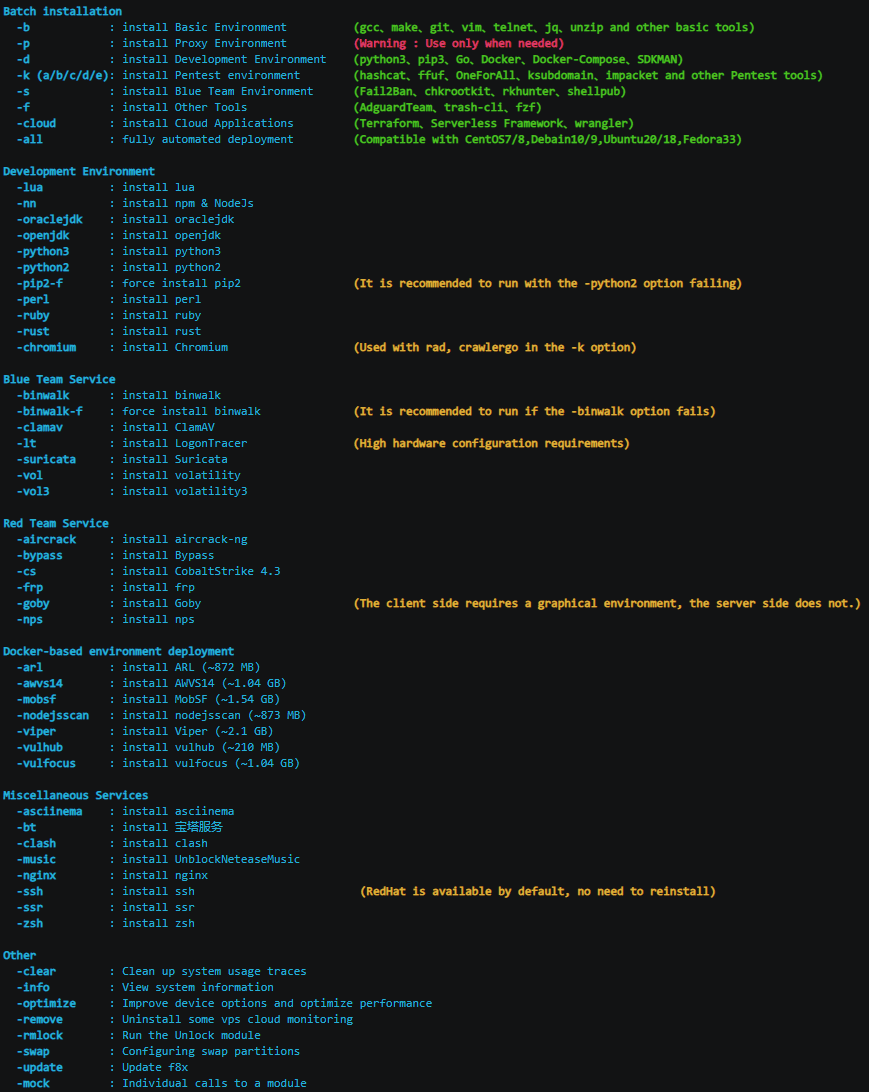 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 safedep/vet
Protect against malicious open source packages 🤖
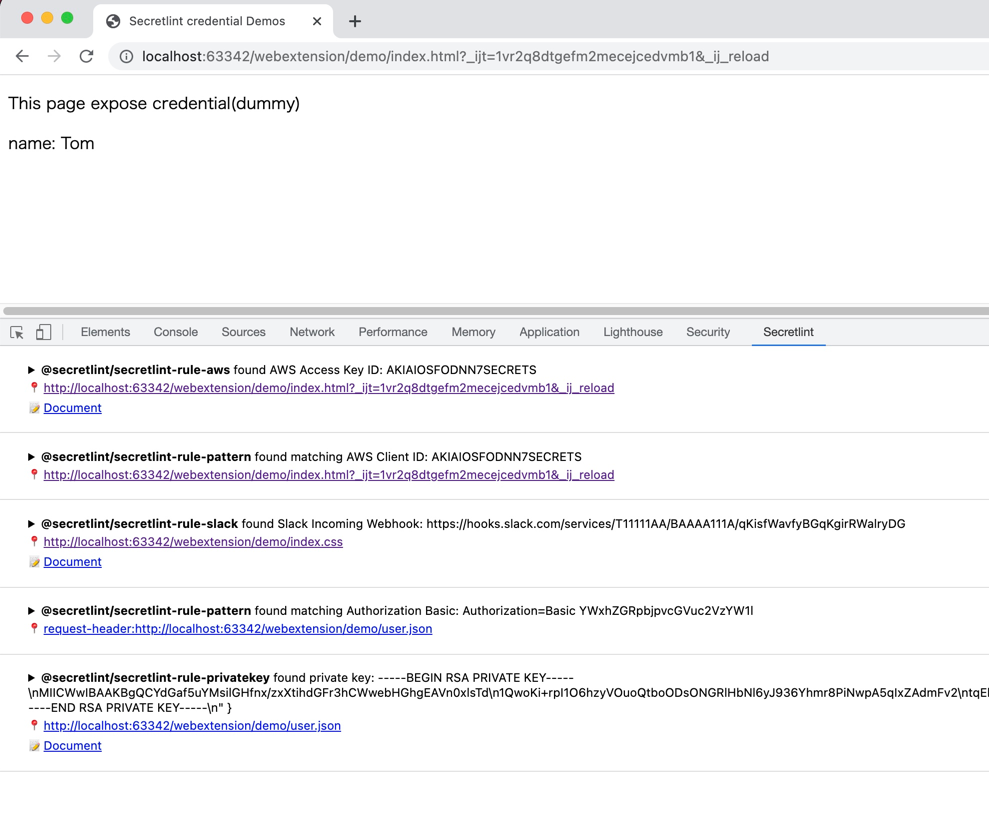 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 tmobile/pacbot
PacBot (Policy as Code Bot)
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.