
contrast
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
cloud-infrastructure-securitycloud-securitycode-analysis+6
20
contrastsecurity/contrastSAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
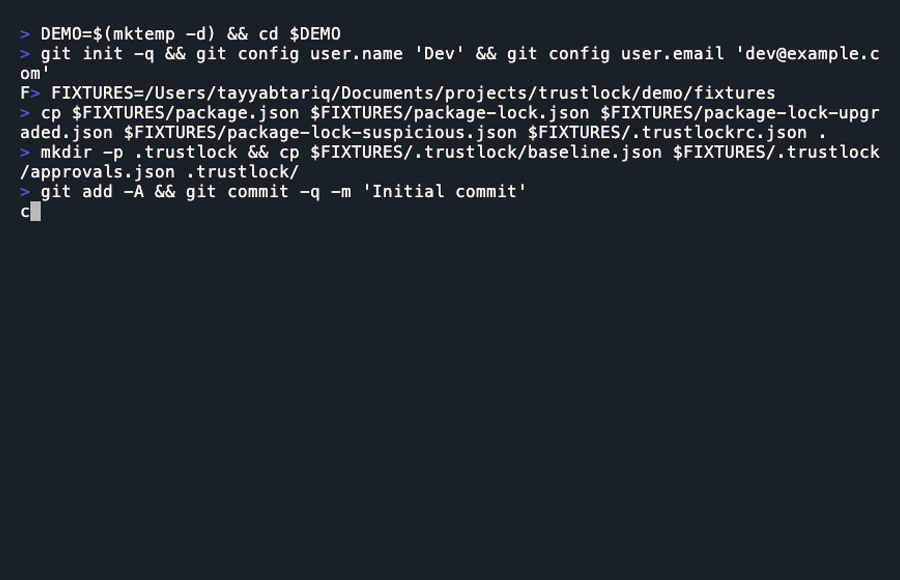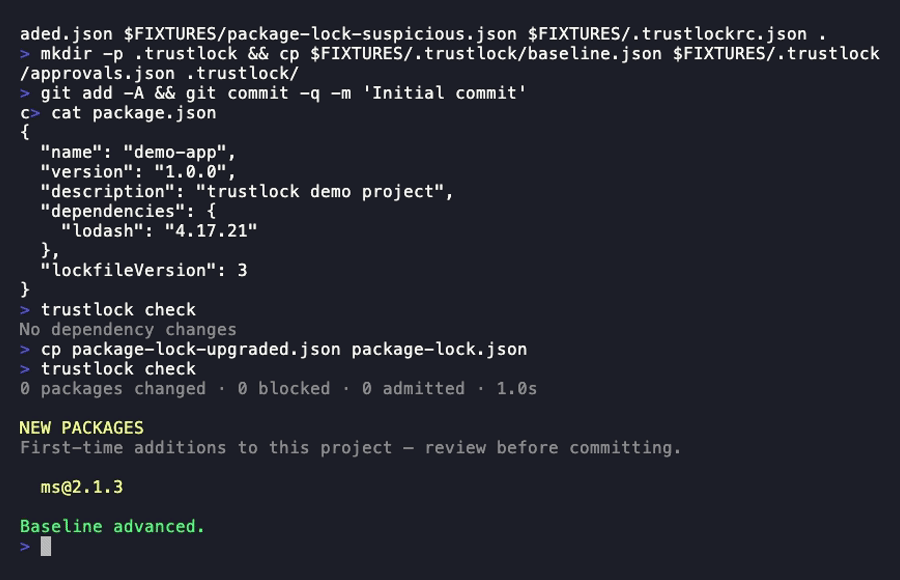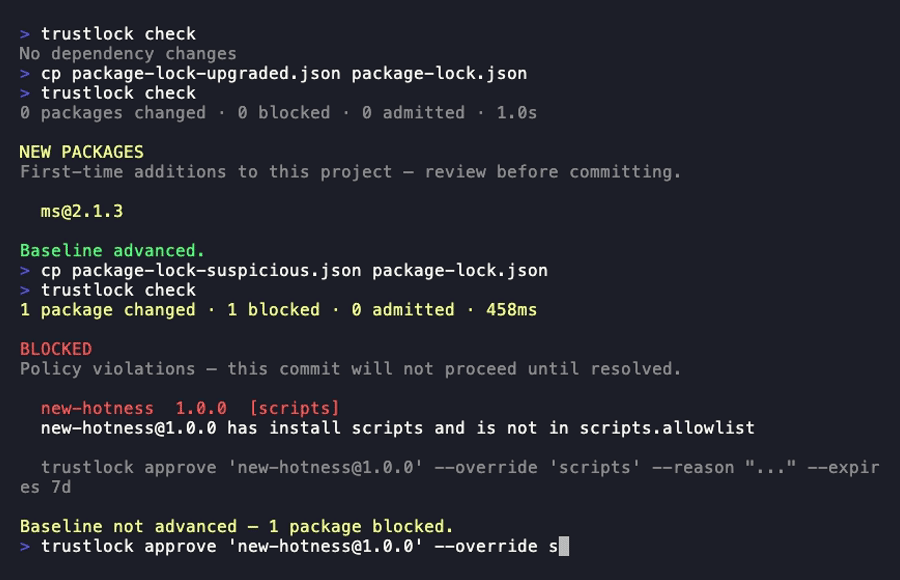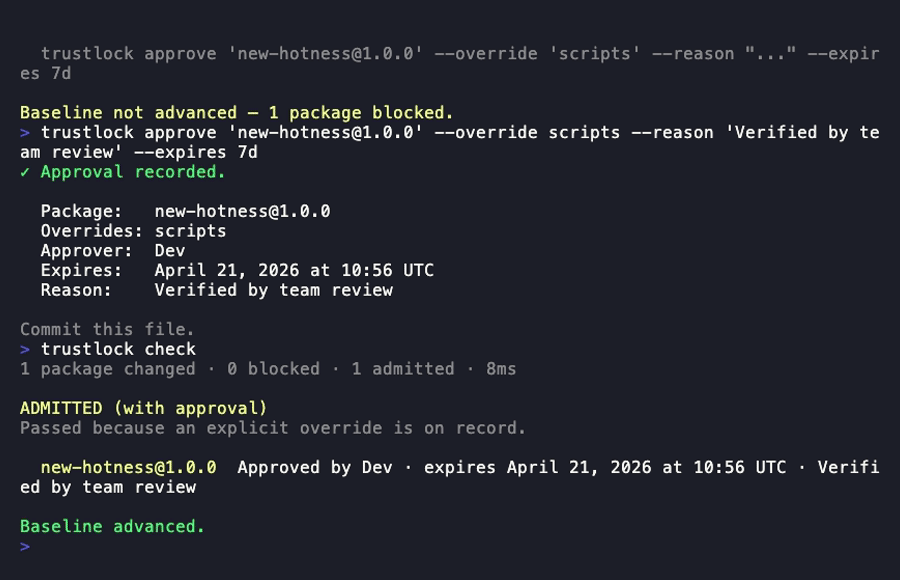 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
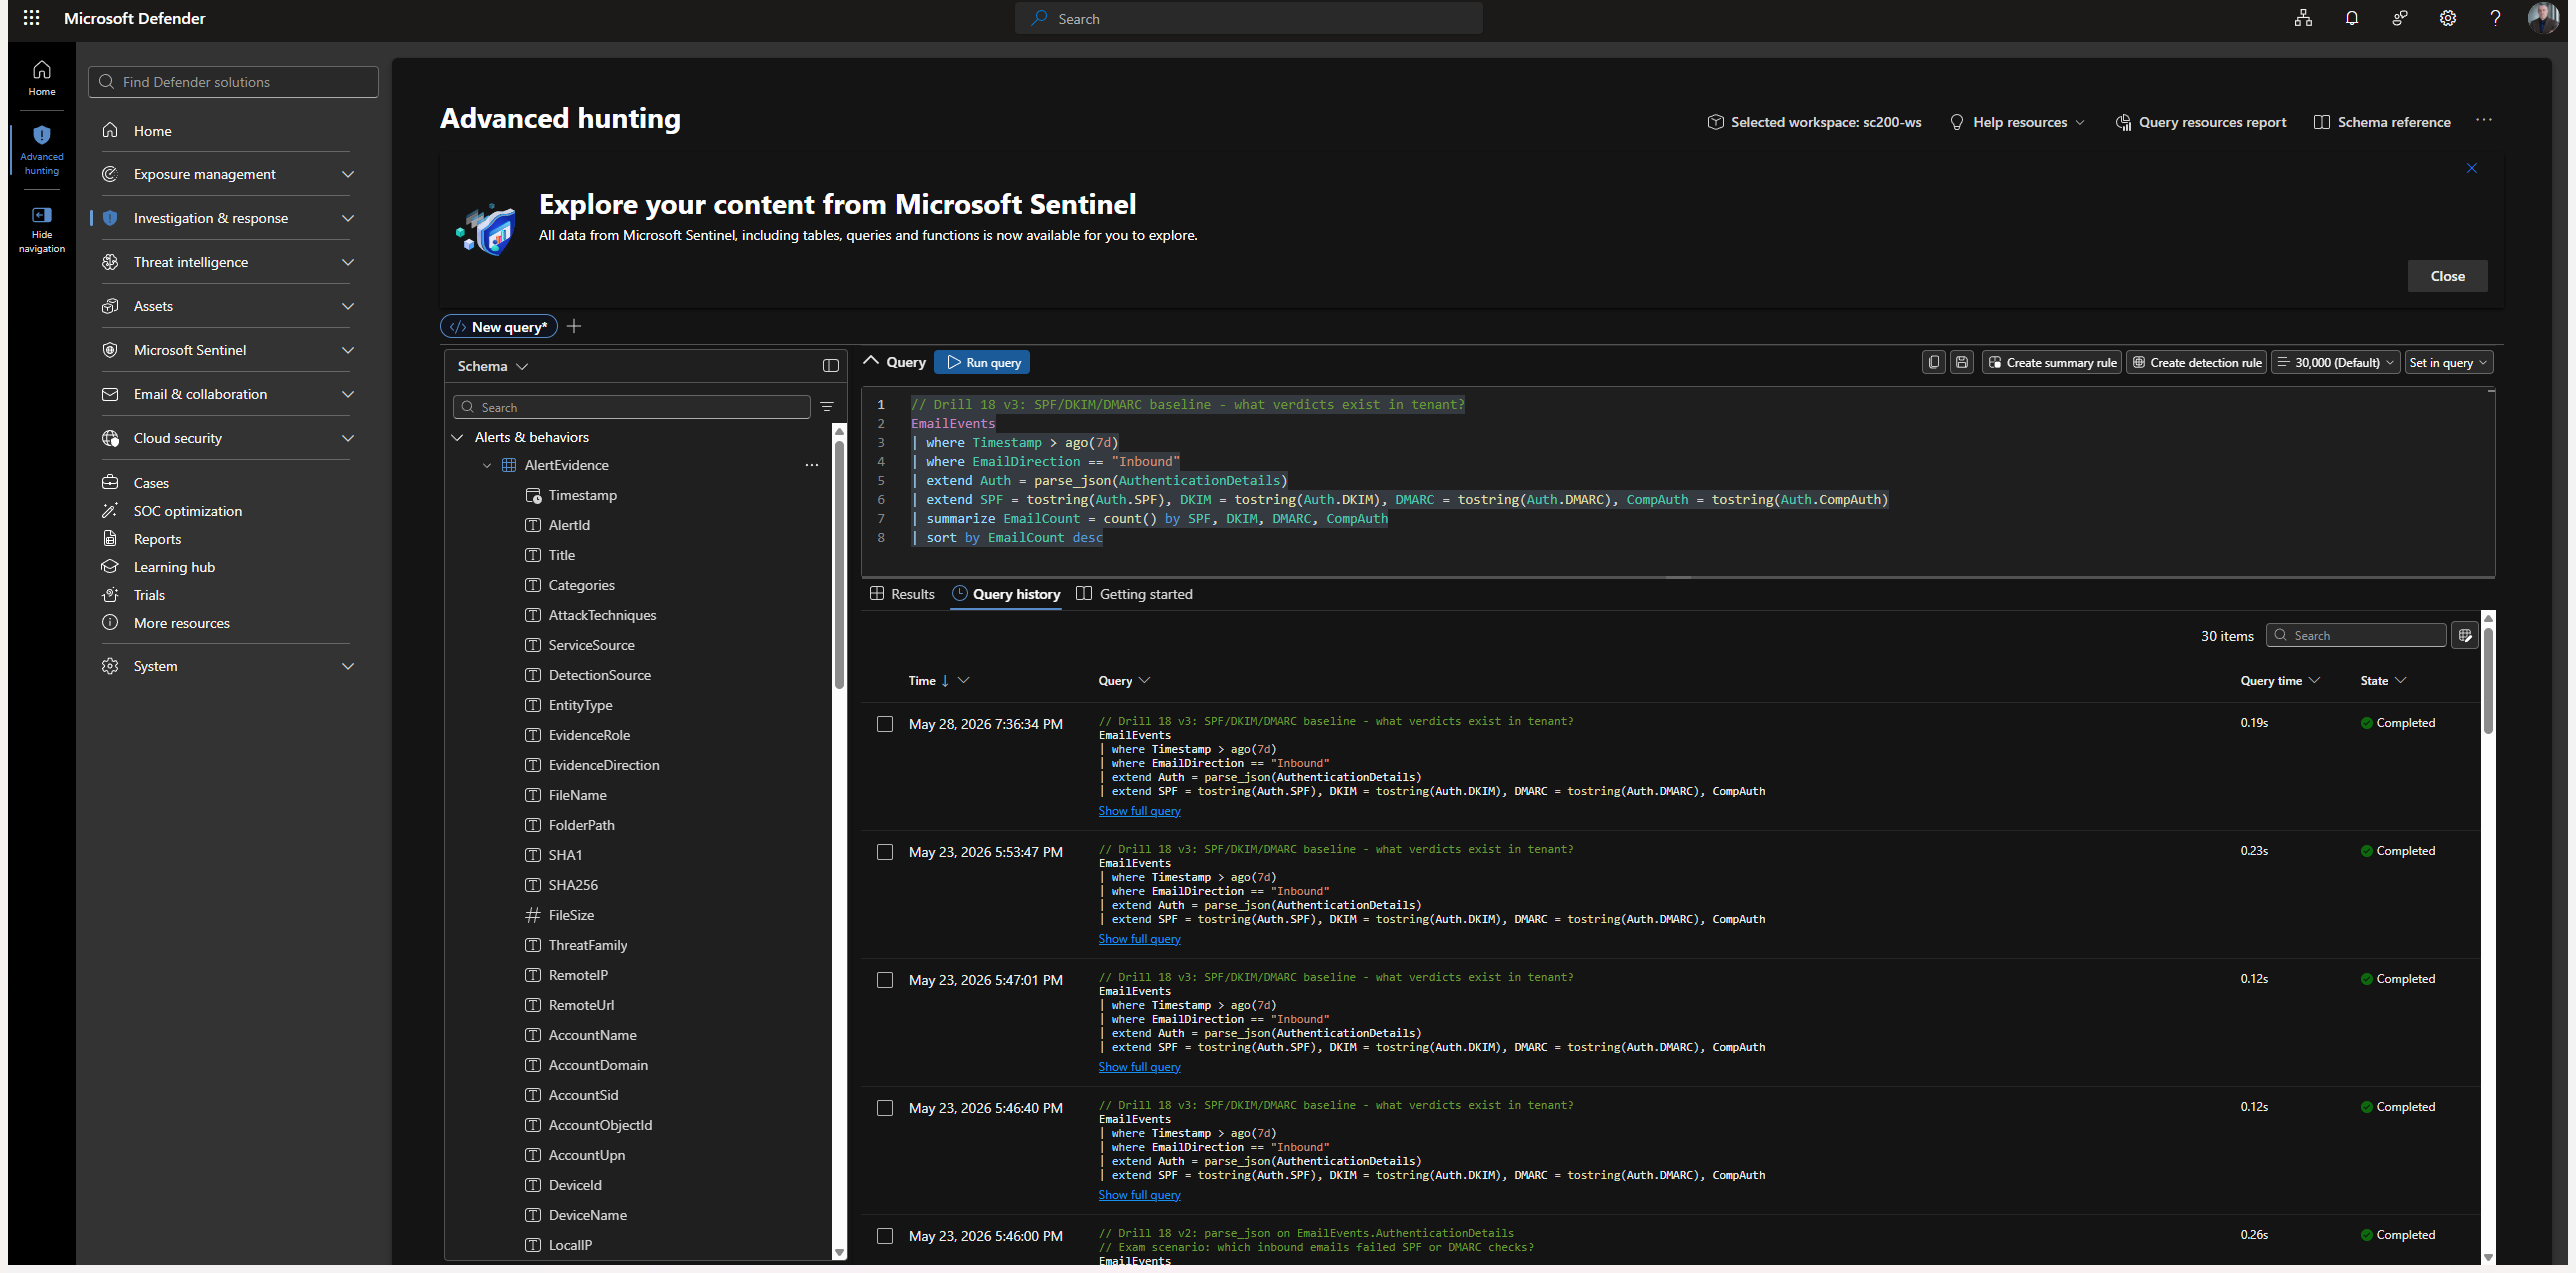 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 elevenpaths/atomshields
Security testing framework for repositories and source code
 haydenjames/dirty-frag-check
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 pvharmo2/gha-lab-f894926966
Authorized security-research reproduction lab for CVE-2025-54415 (GHSA-g5hx-xv45-9whg): astronomer/dag-factory snapshot at 464c75a —…
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
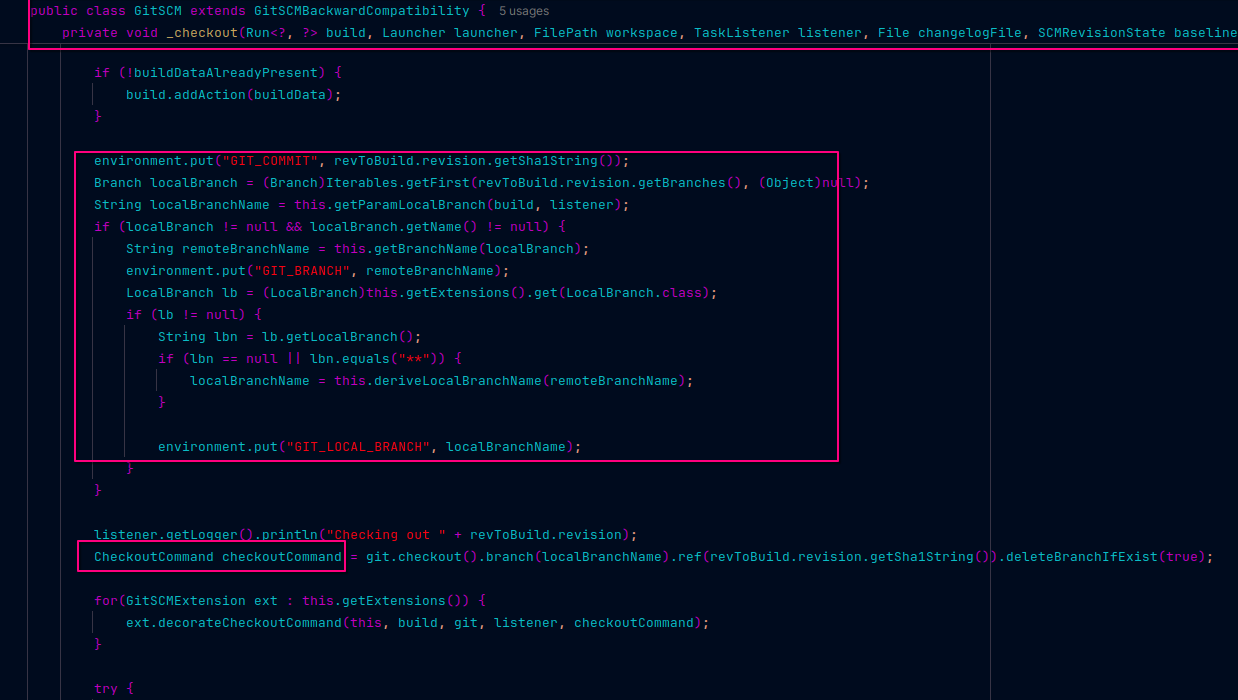 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
 guardia-ai/gitlab-component
EU AI Act compliance scanner for GitLab CI/CD pipelines — detects AI/ML libraries and posts risk classification as MR comments.