

HybridTestFramework
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
api-security-testingcloud-securitycontainer-security+3
153
dipjyotimetia/hybridtestframeworkEnd to End testing of Web, API, Cloud, Events and Security
 xaaha/hulak
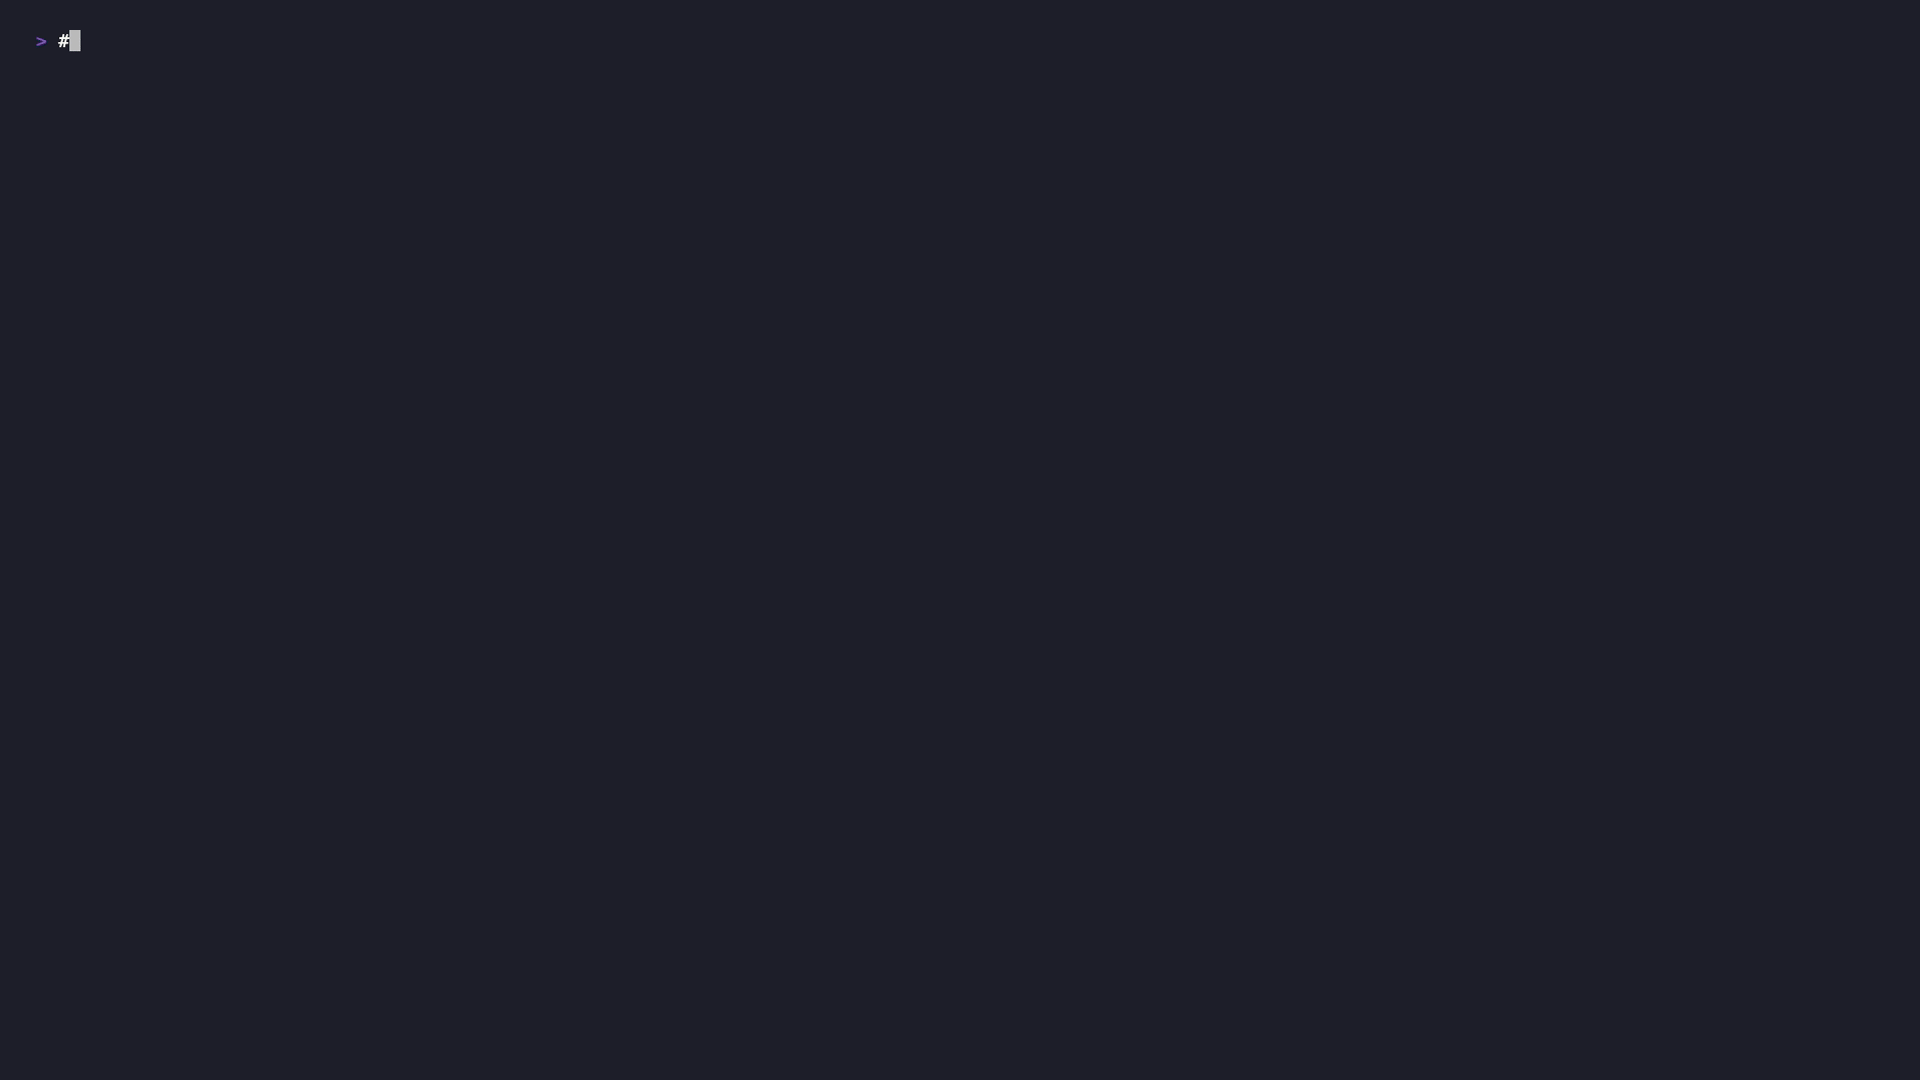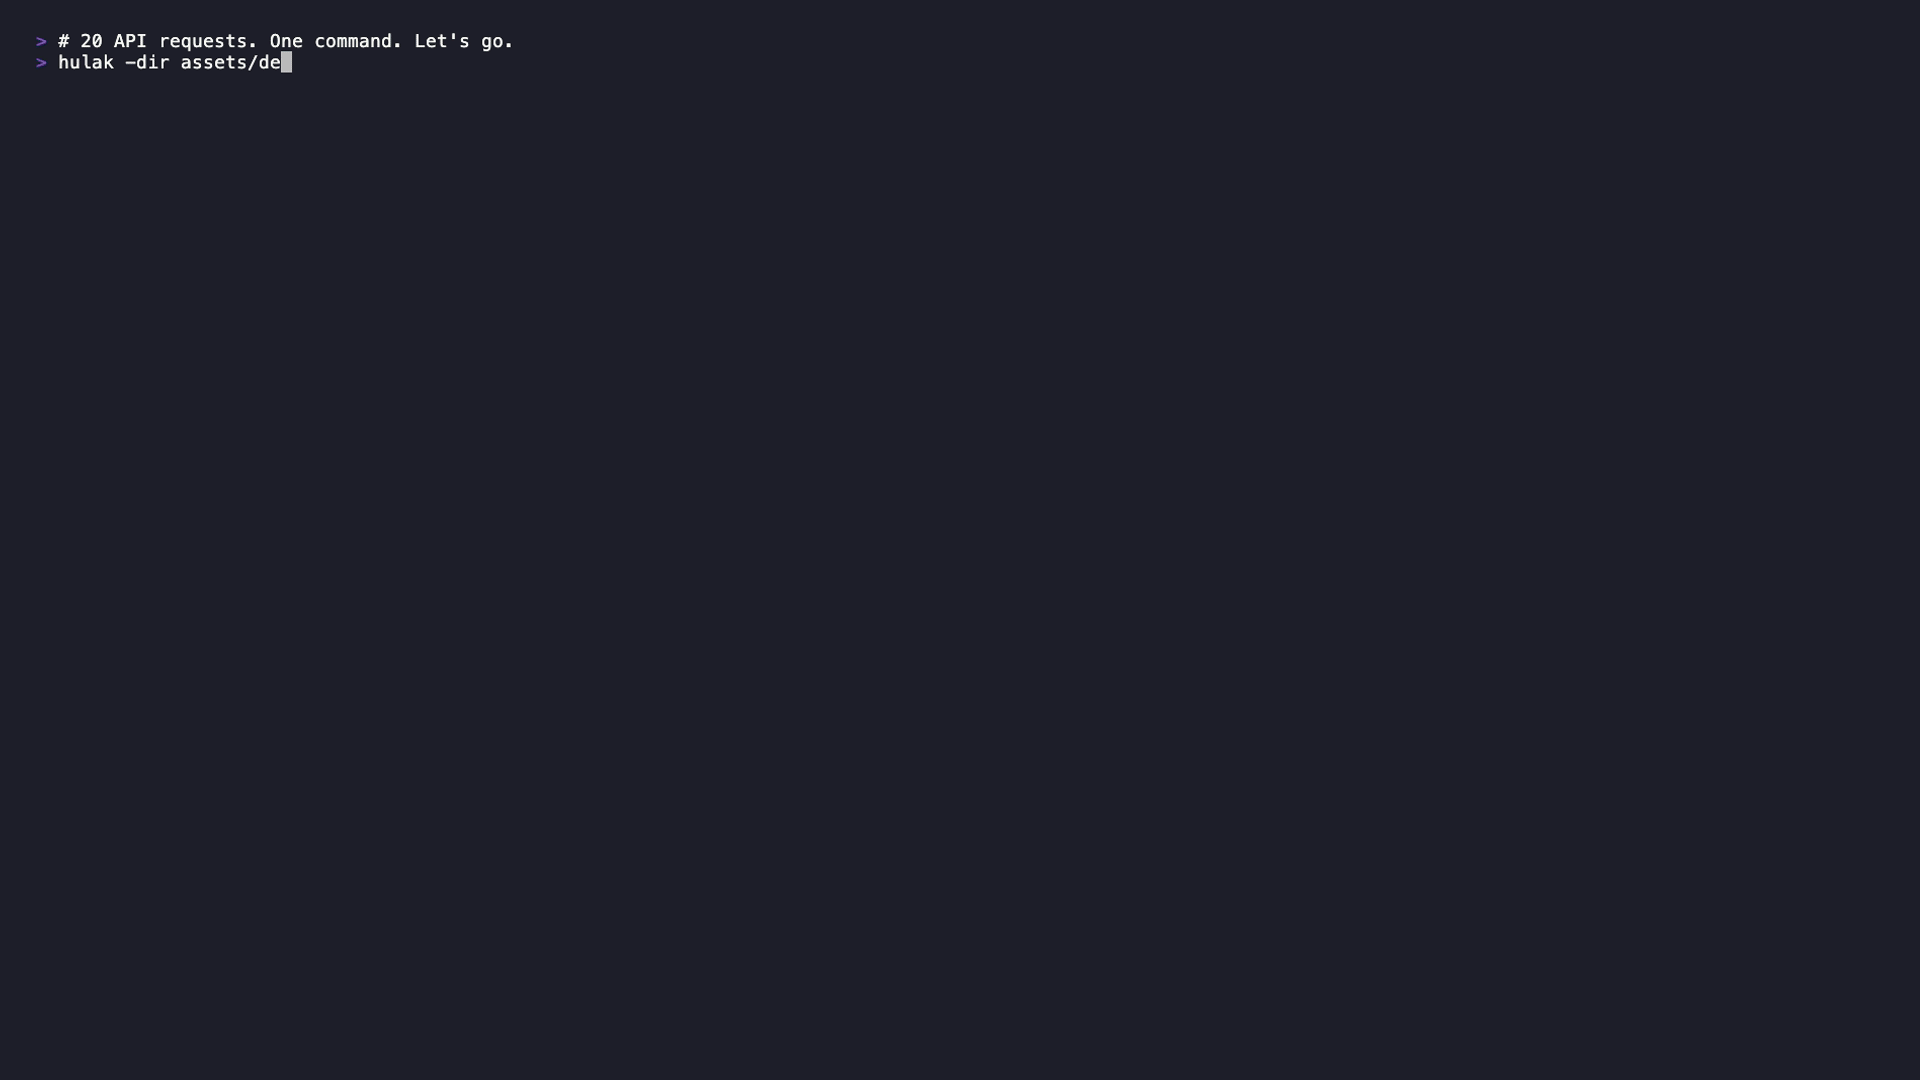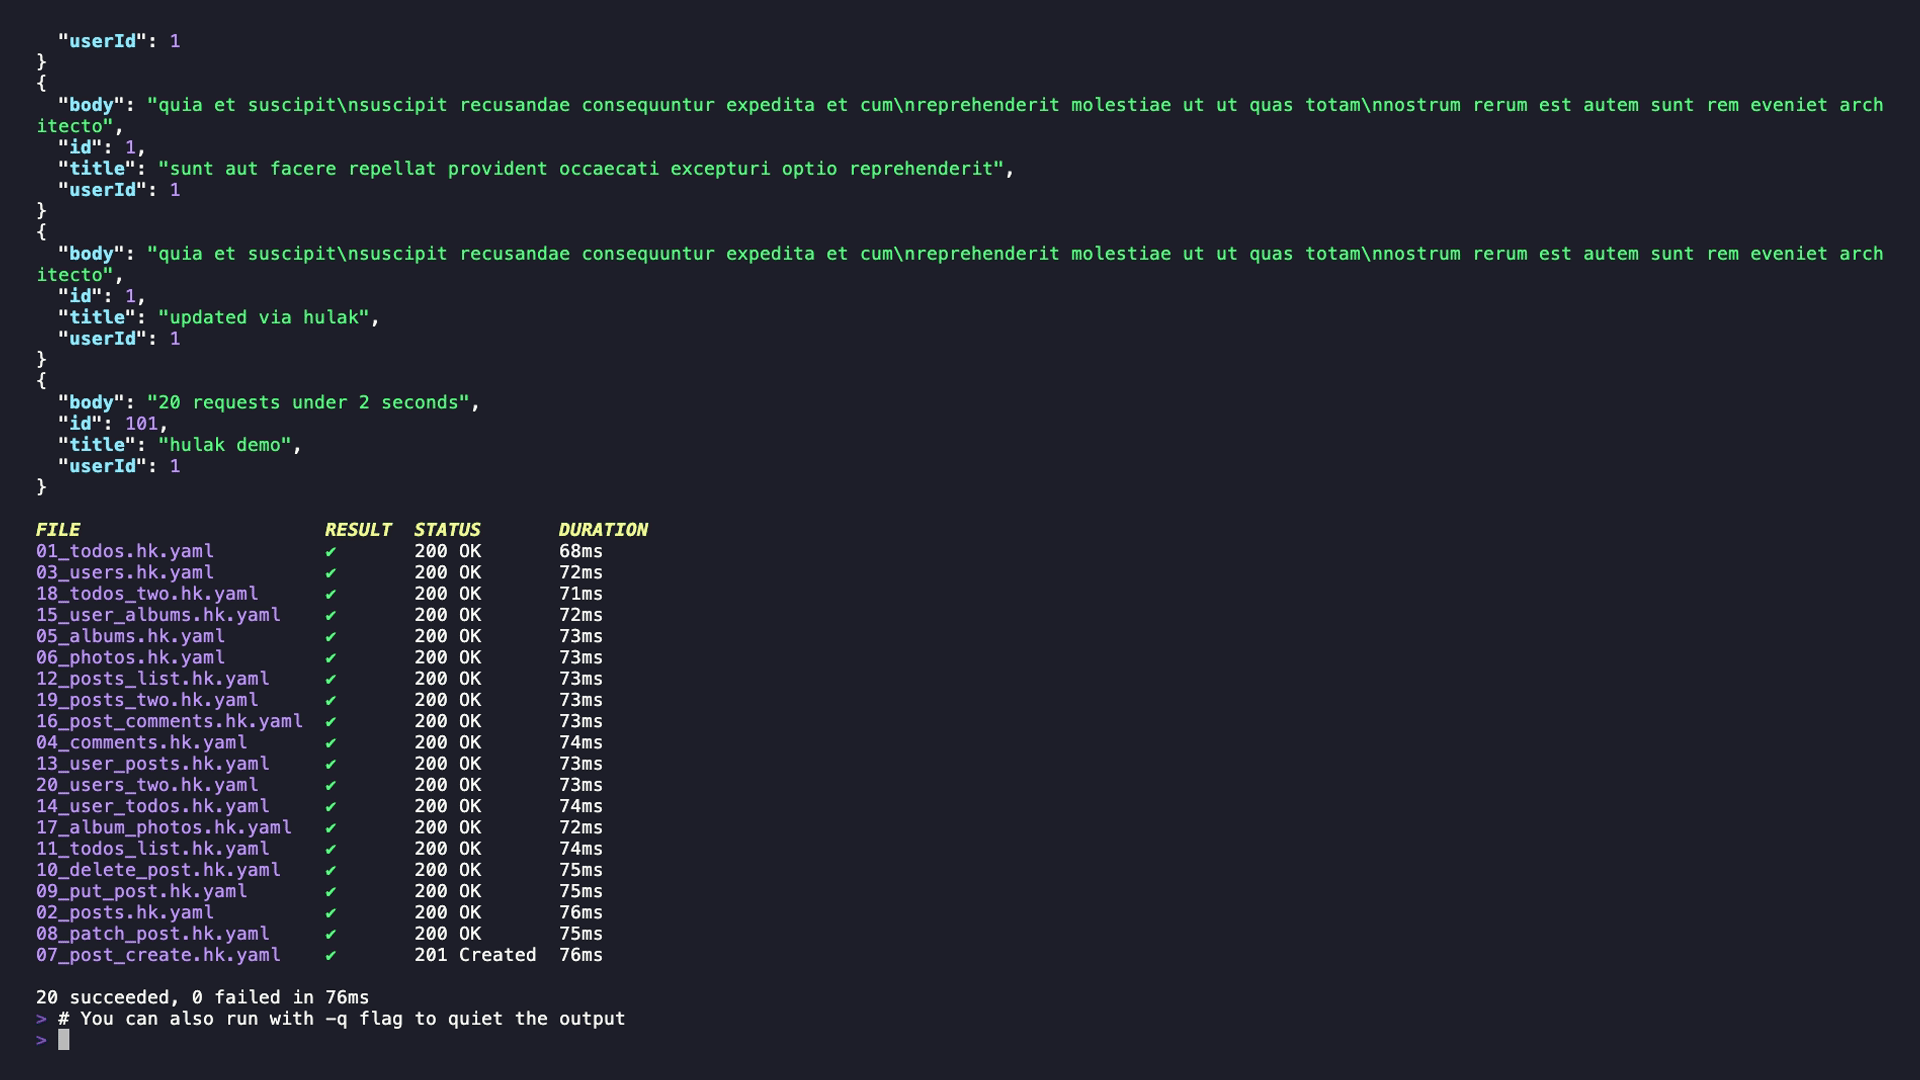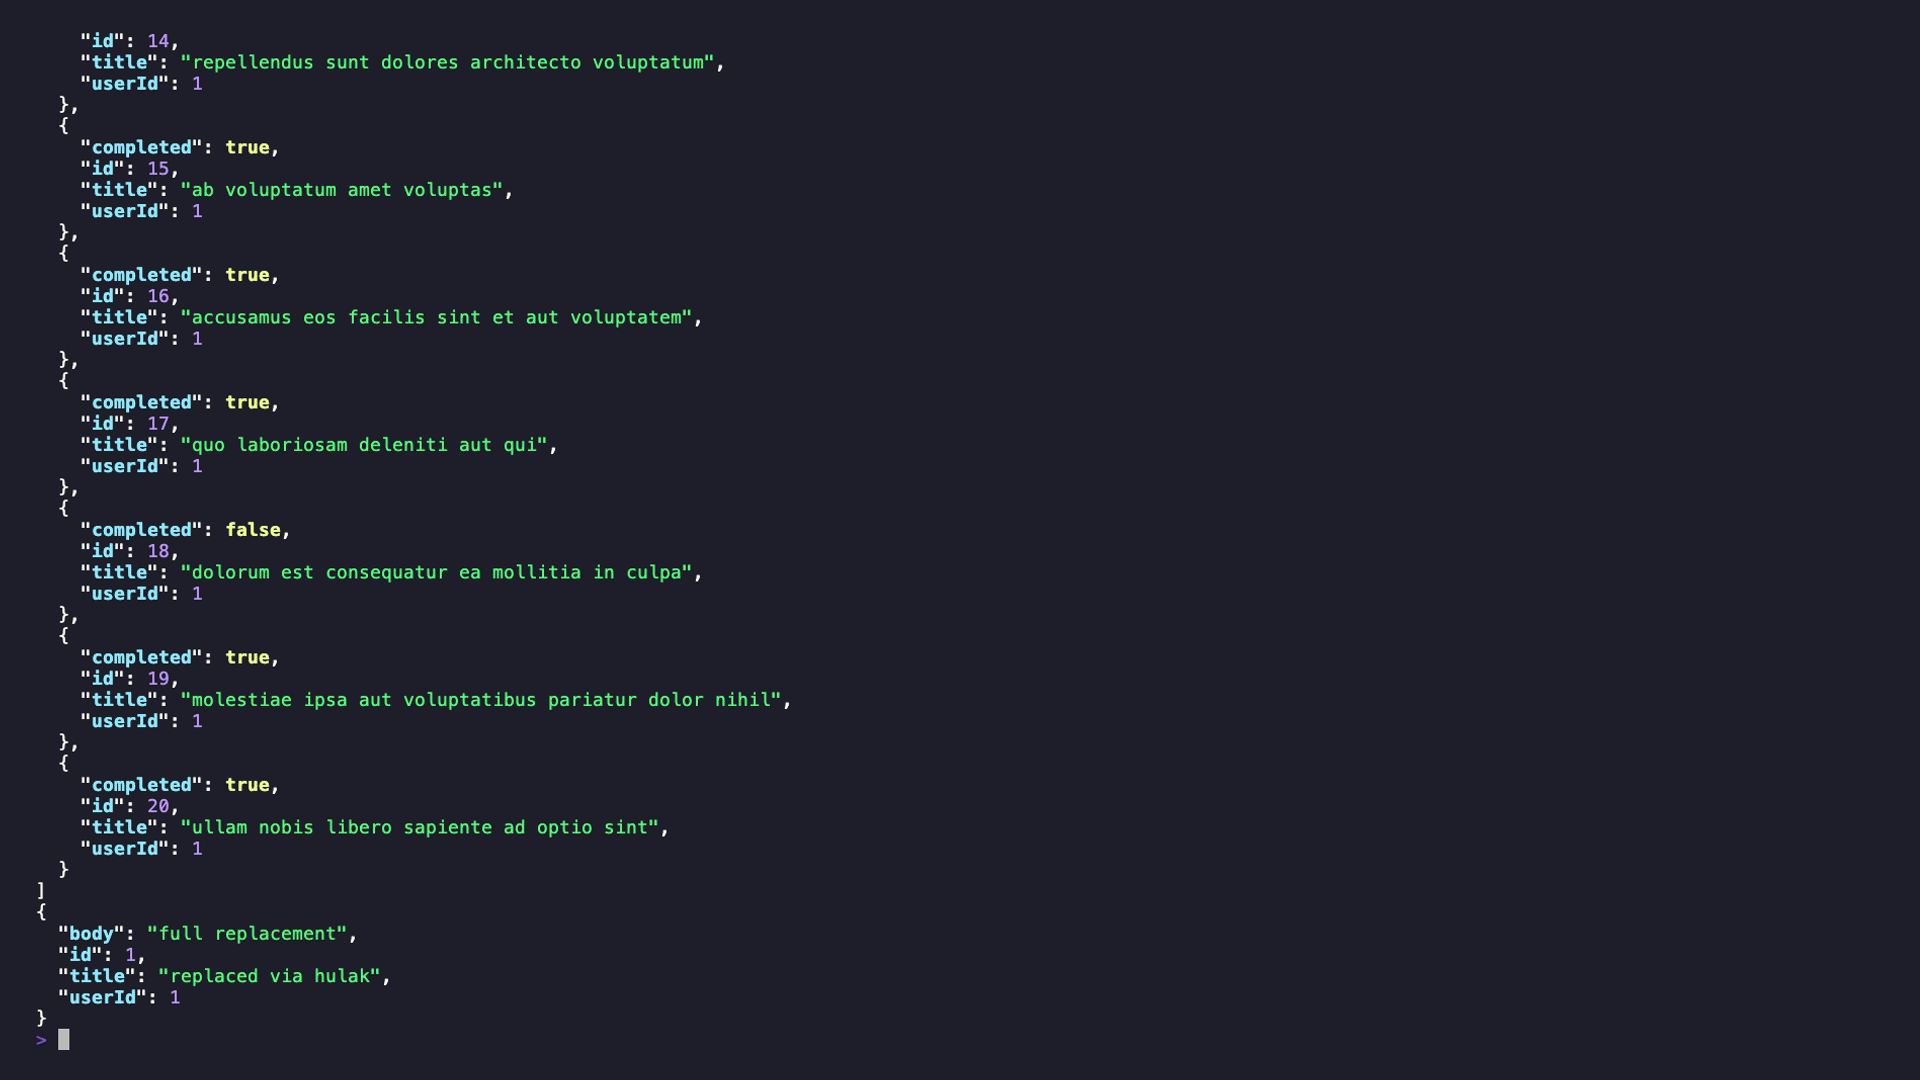
Lightweight file-based CLI API client with age-encrypted secrets, first-class GraphQL support and MCP server for agentic workflow.
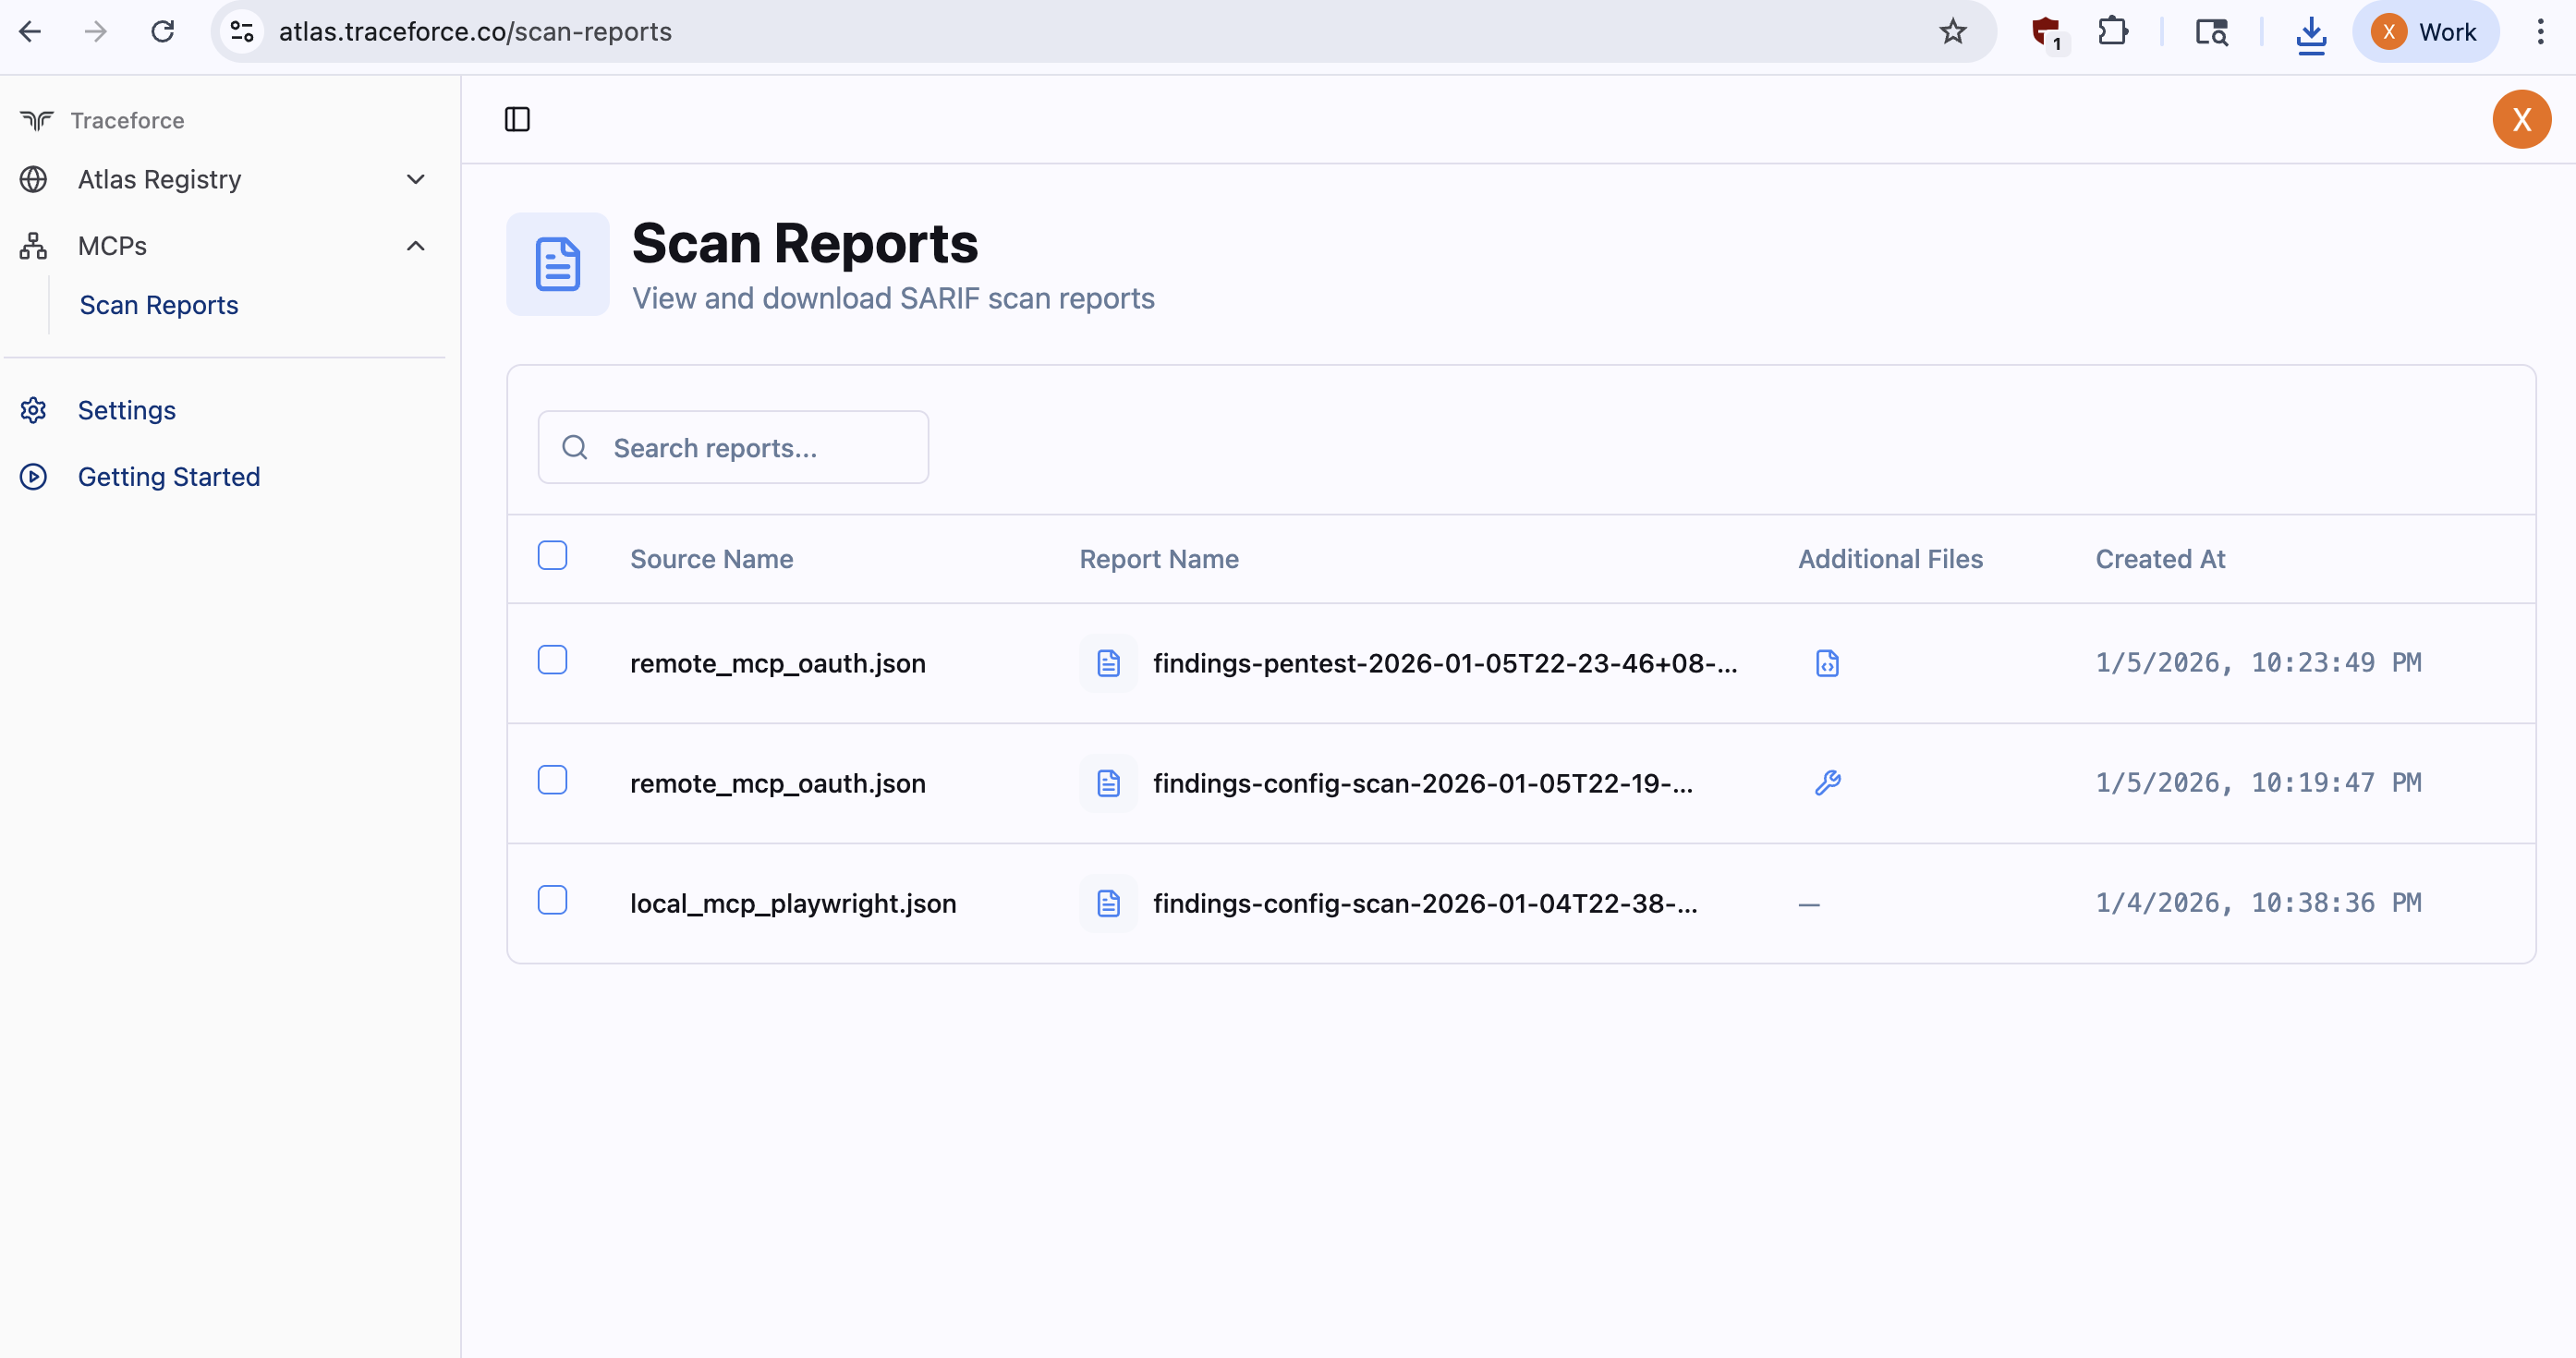 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 opnsense/core
OPNsense GUI, API and systems backend
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
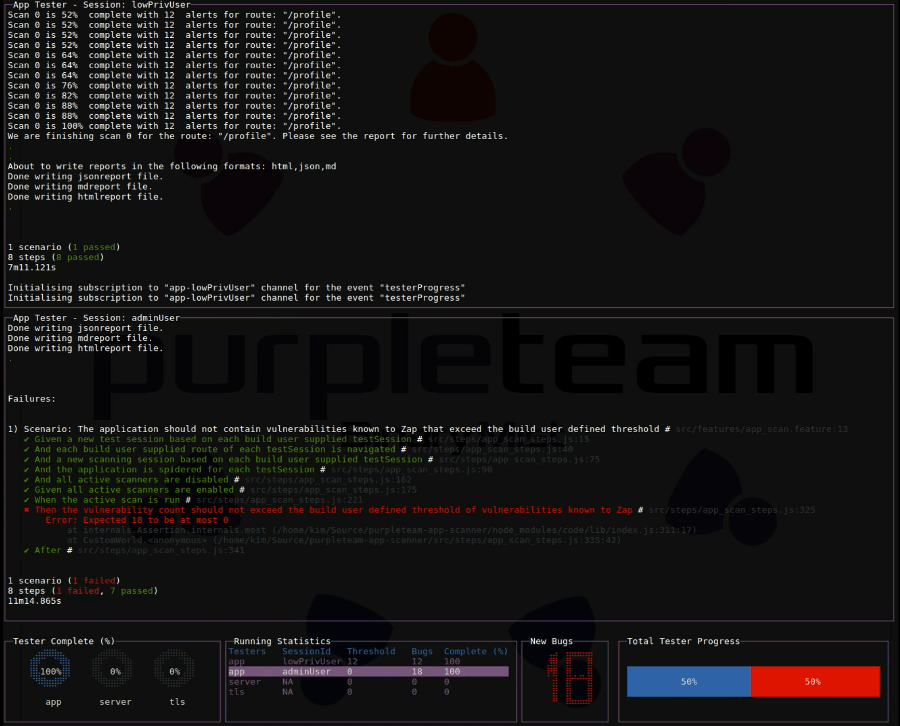 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
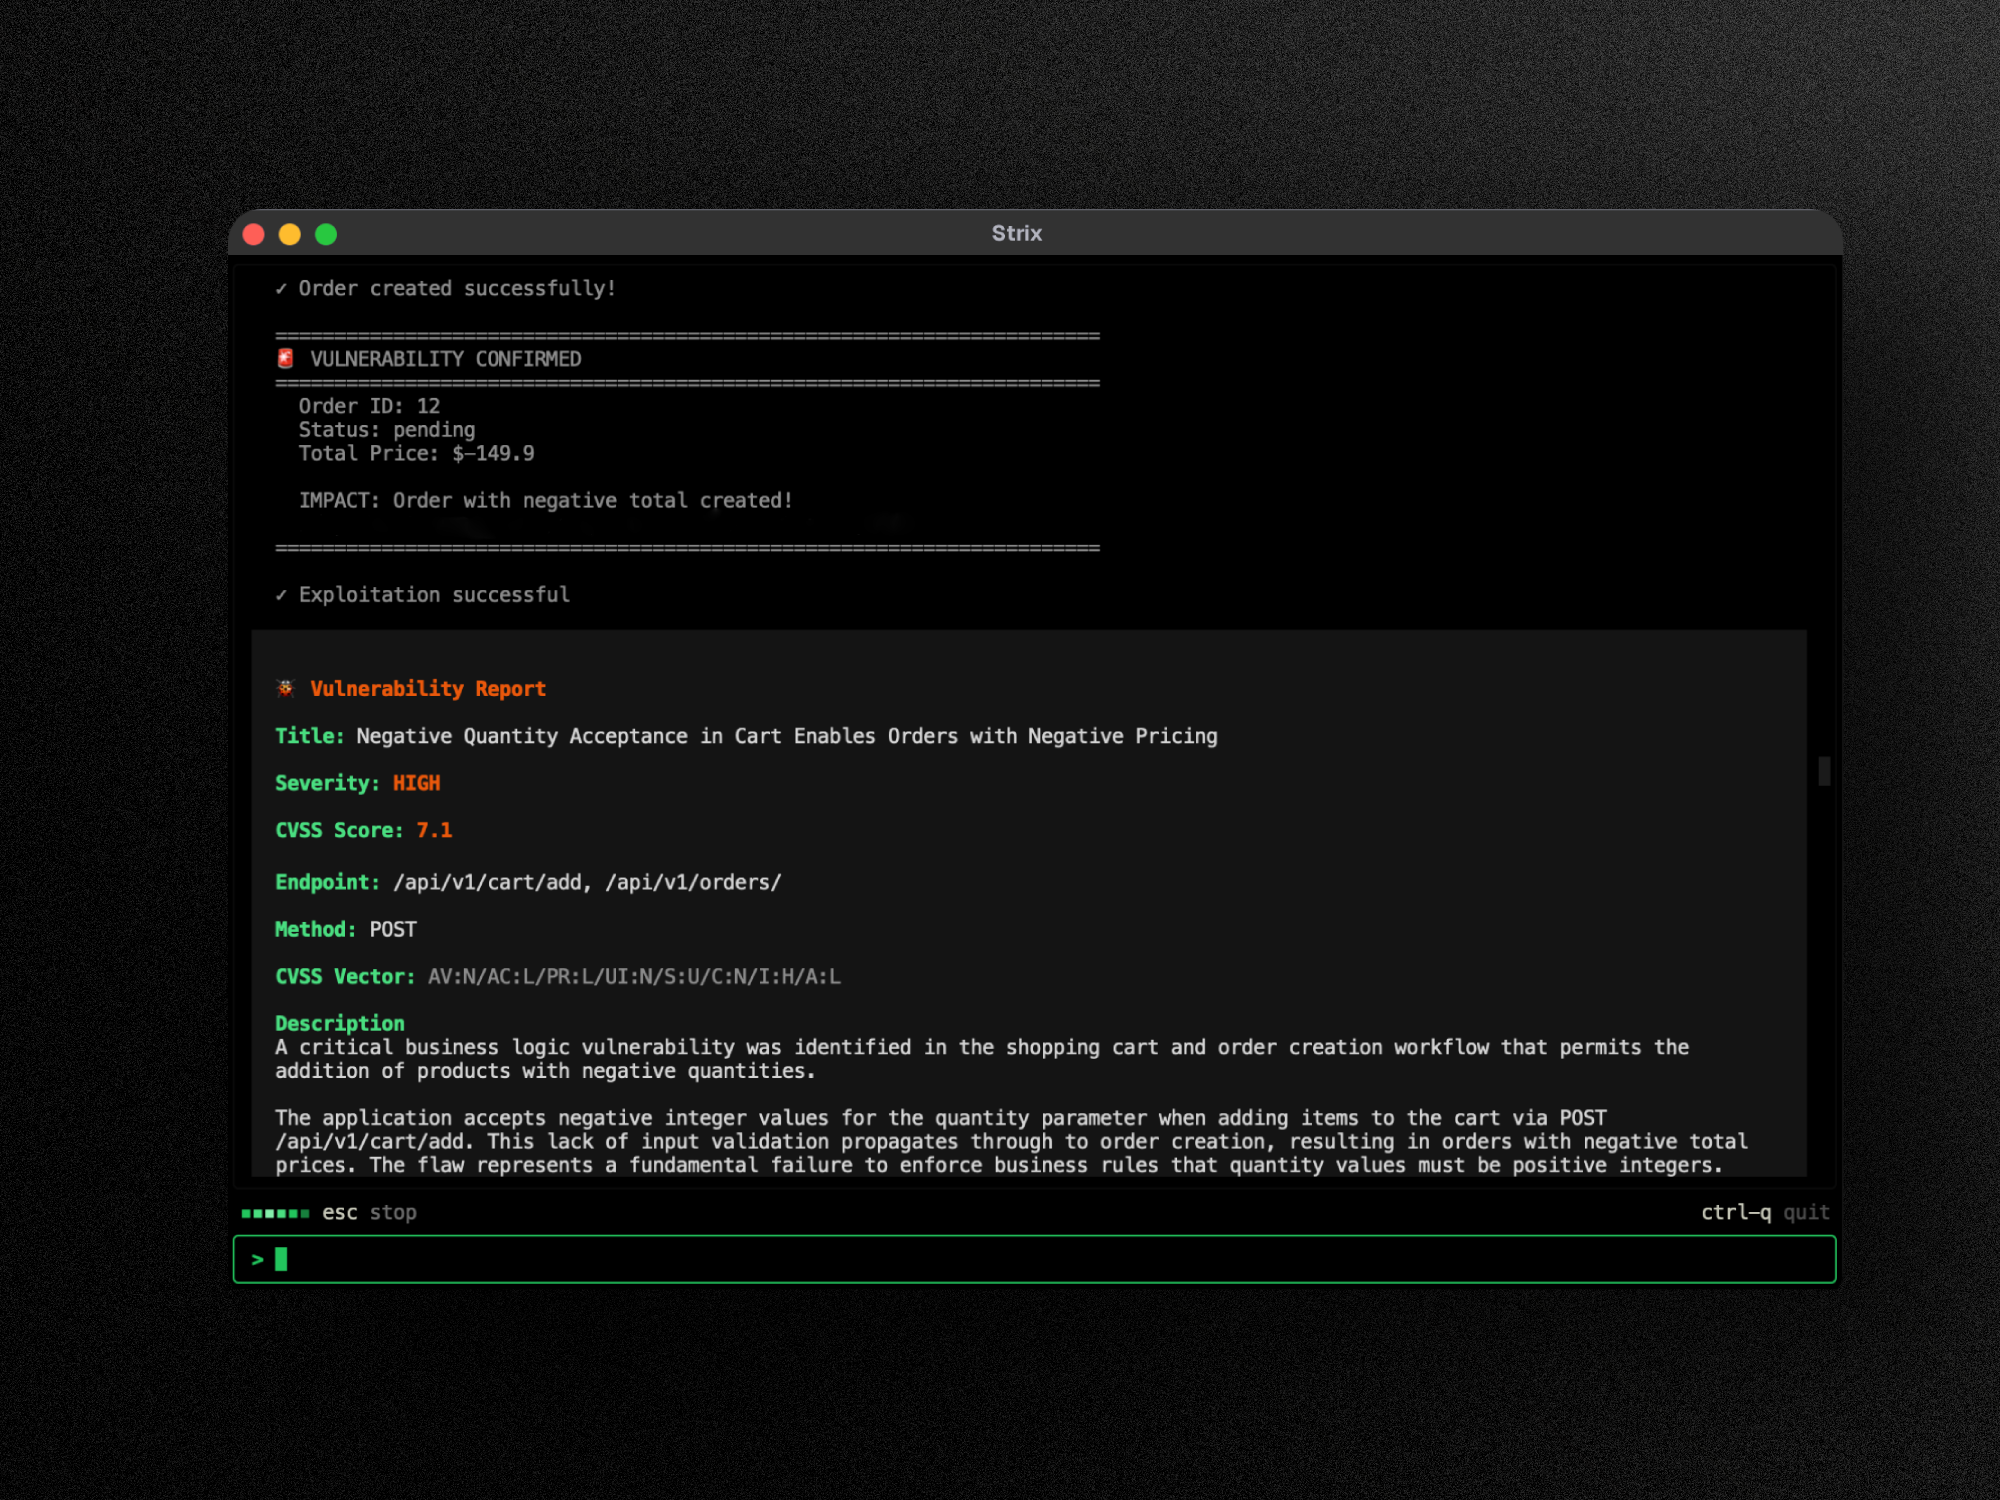 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.