

 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 cloud-gouv/securix
SécurixOS is a NixOS-based secure operating system tailored for small to medium-sized teams. It provides a minimal, hardened environment with strong…
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 dev-sec/chef-ssh-hardening
This chef cookbook provides secure ssh-client and ssh-server configurations.
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
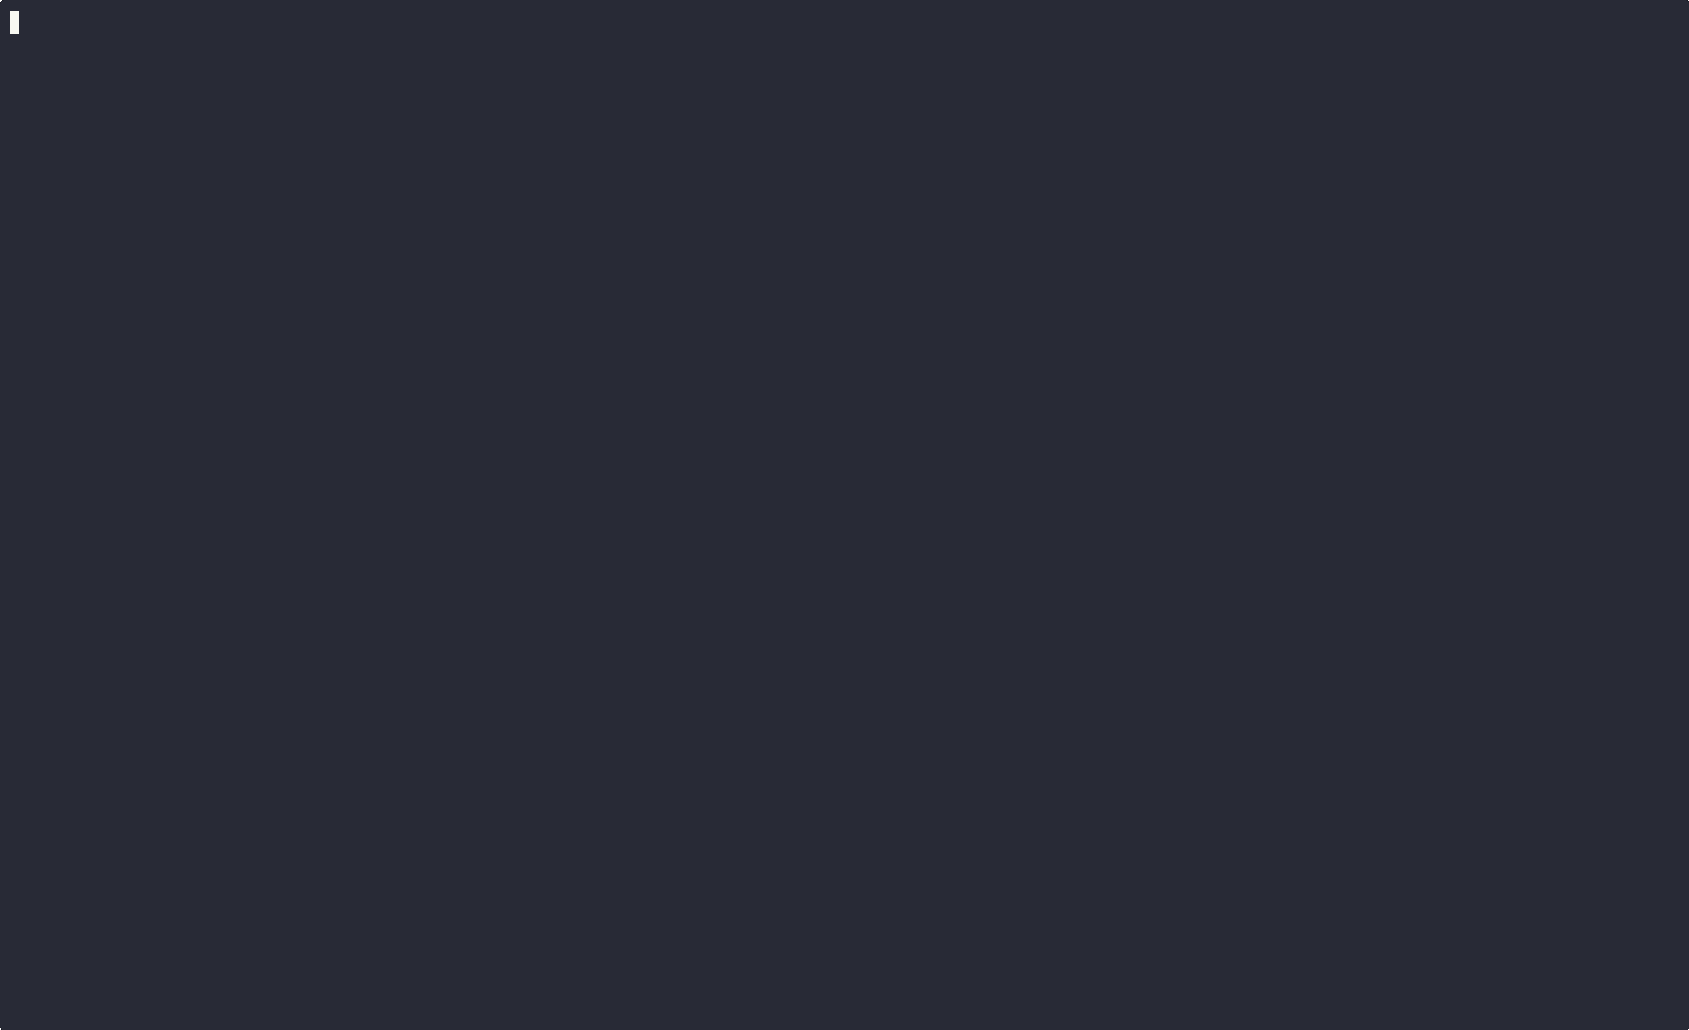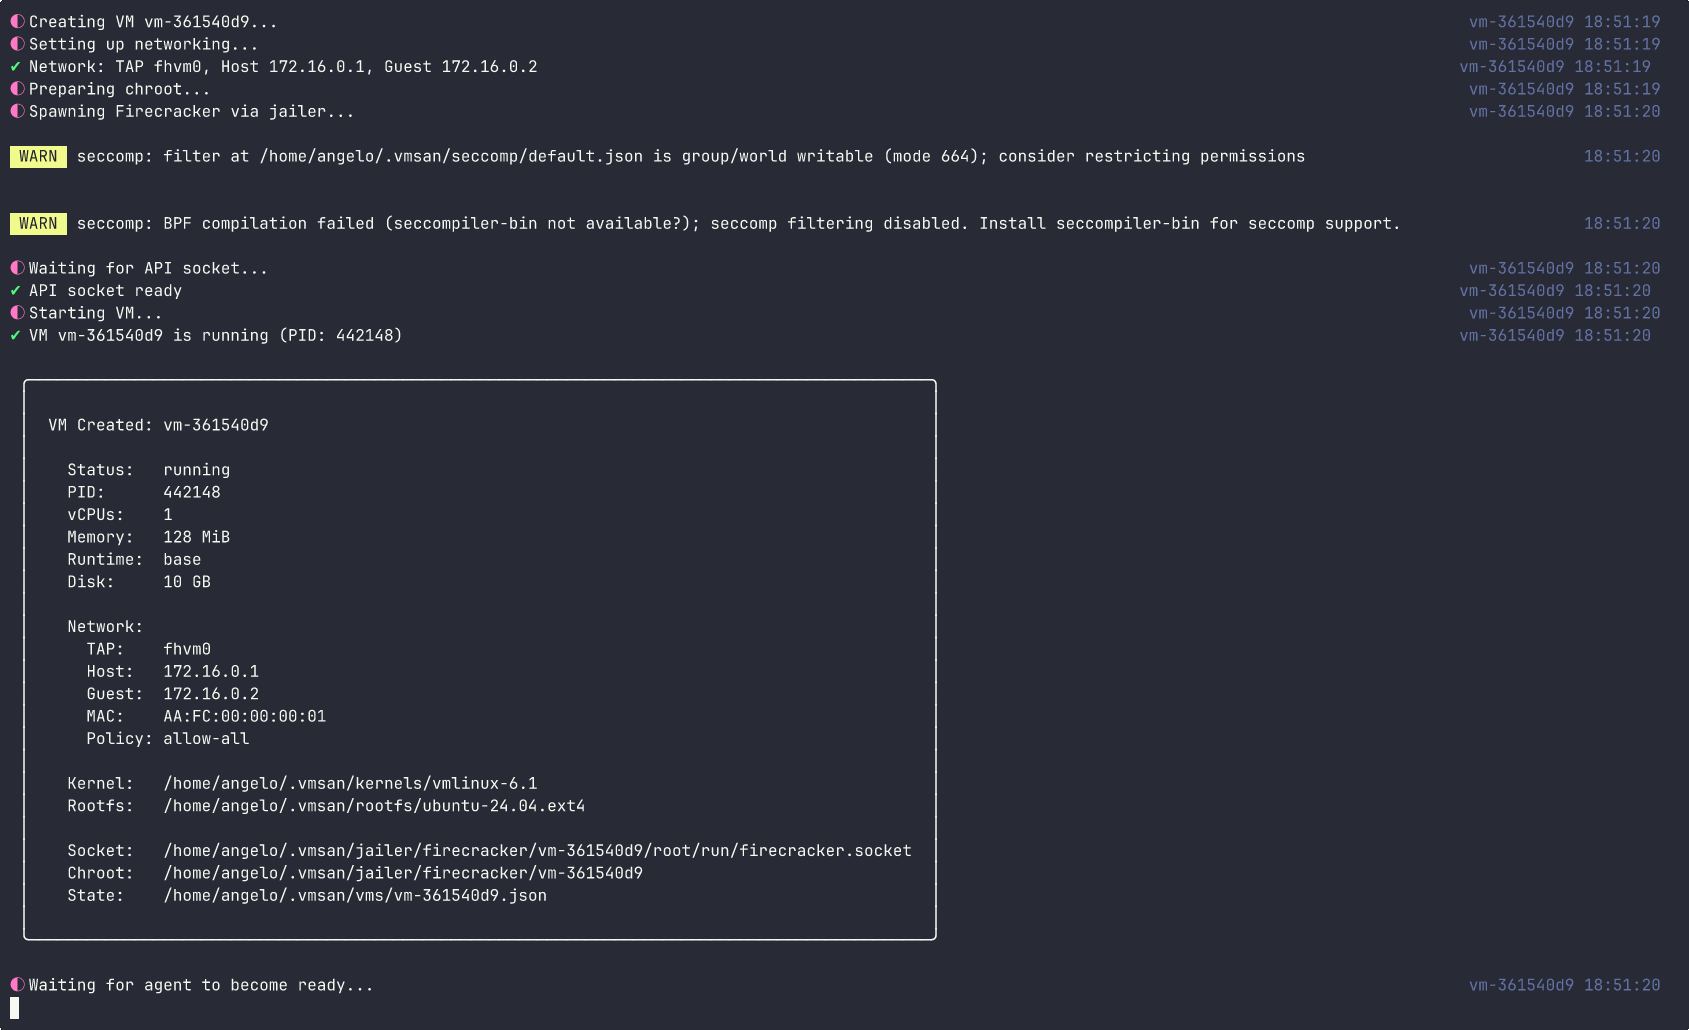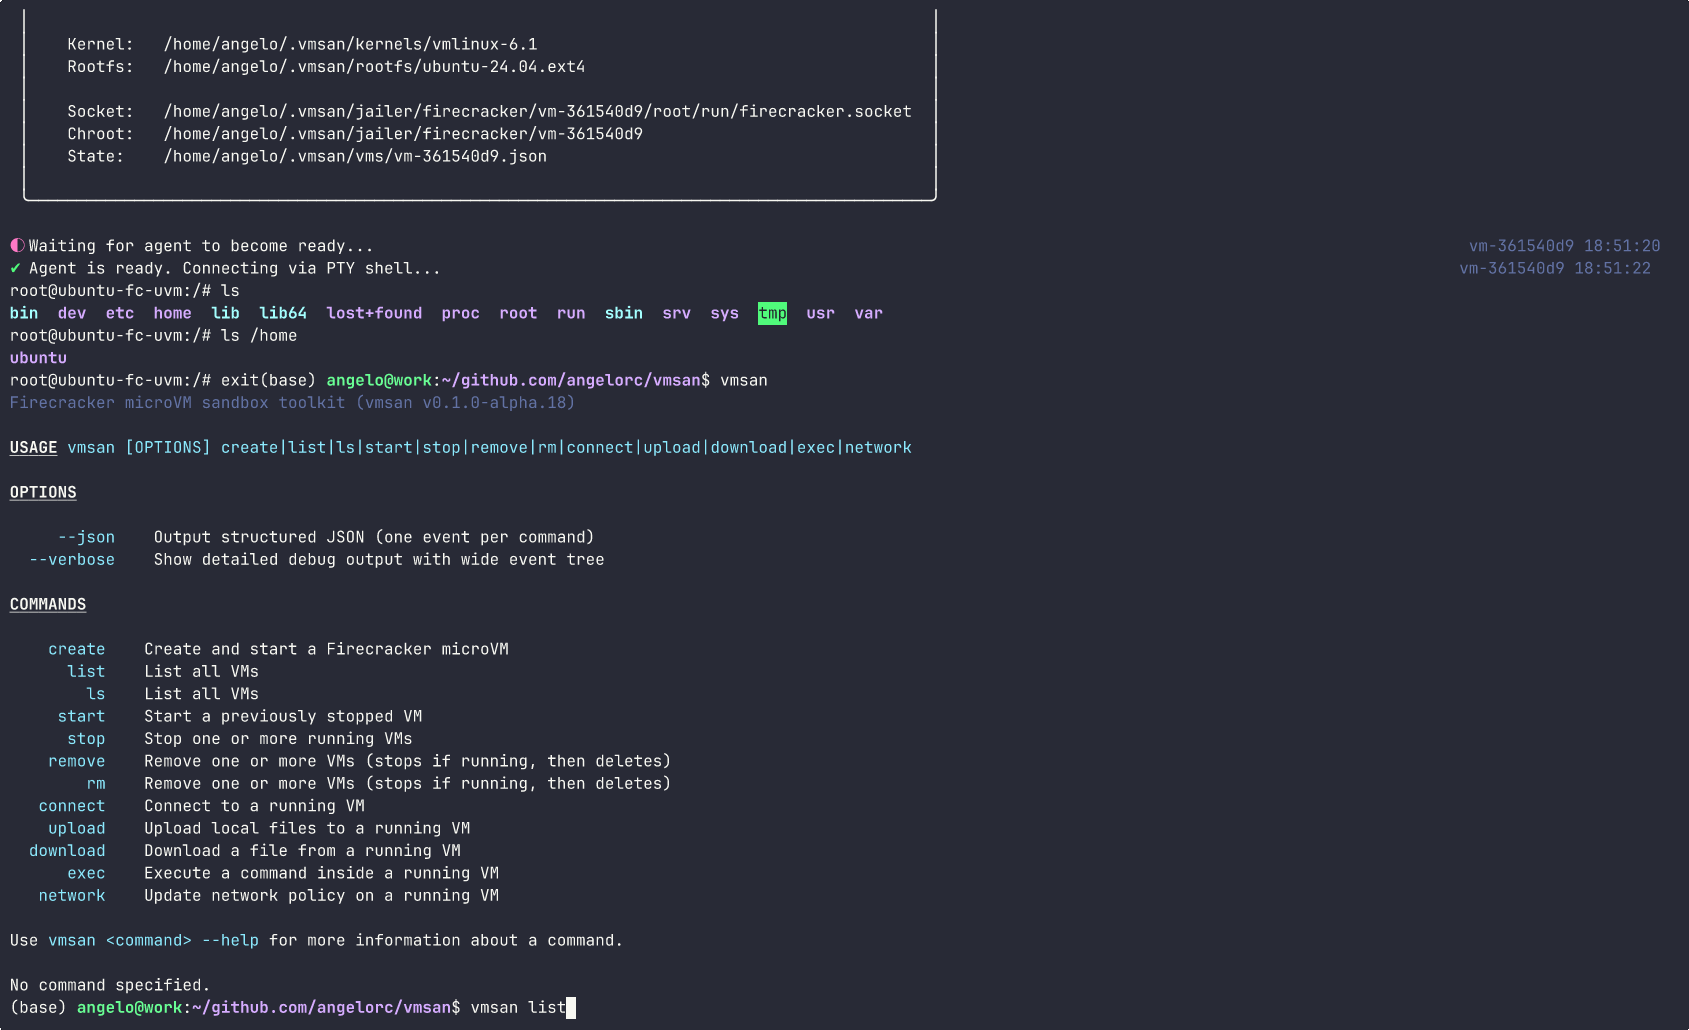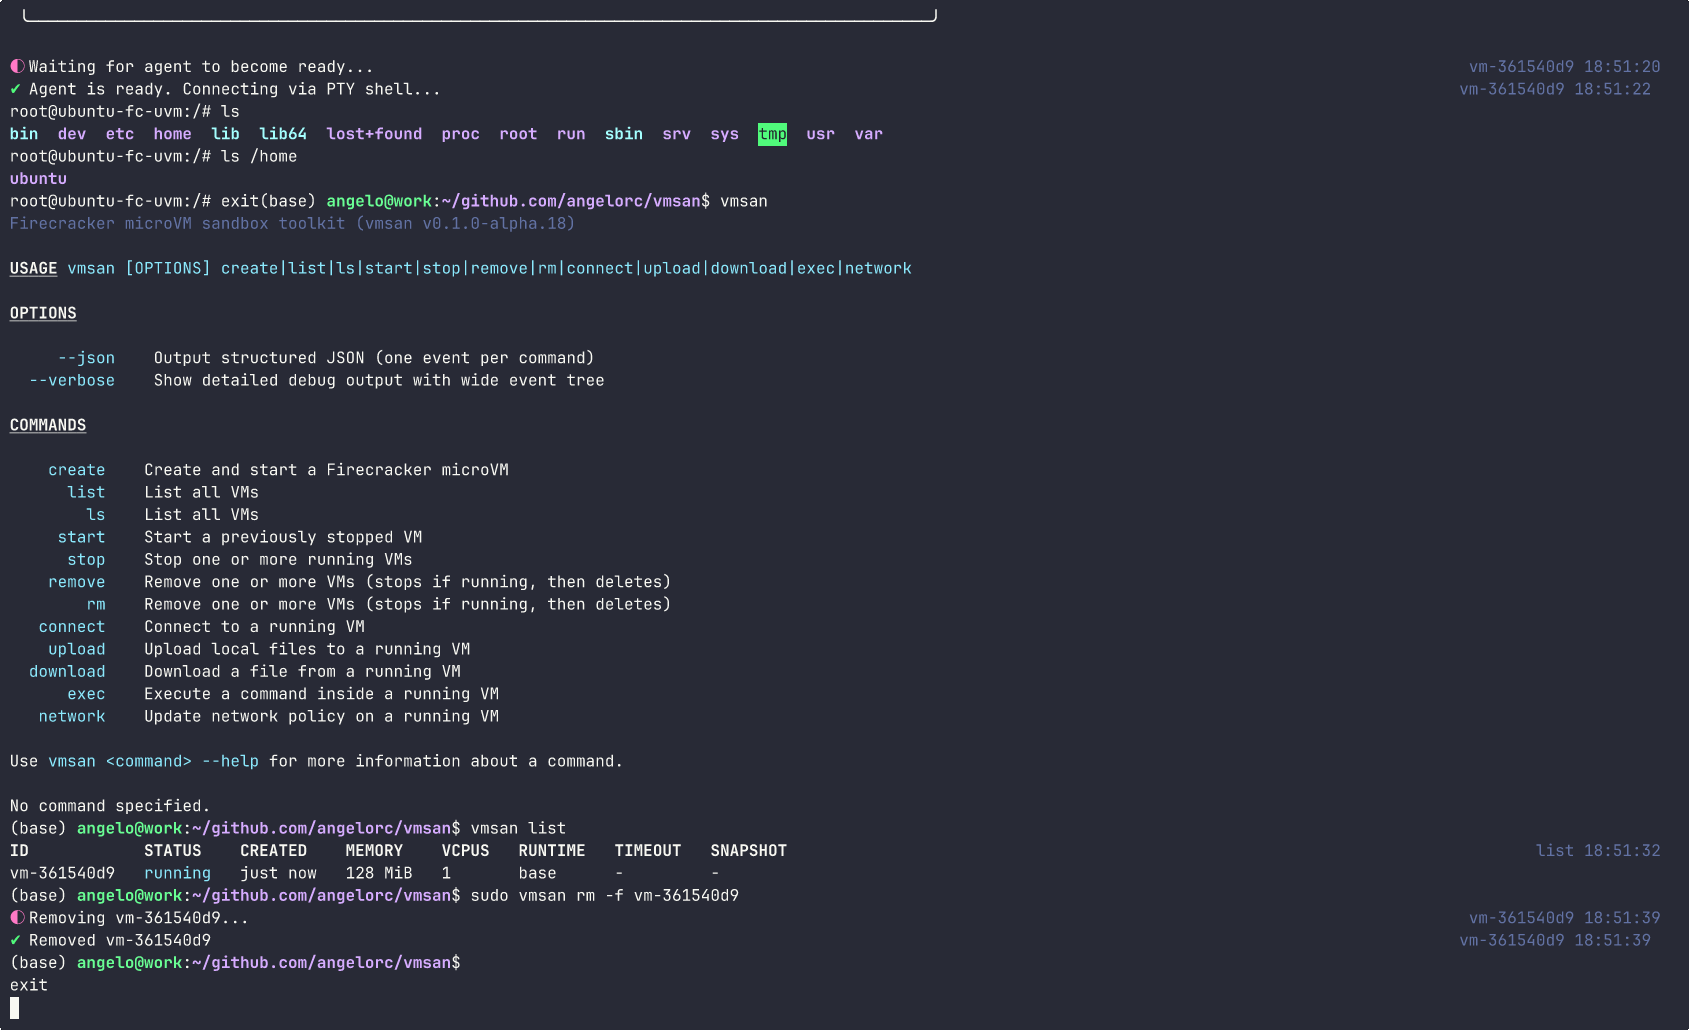 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
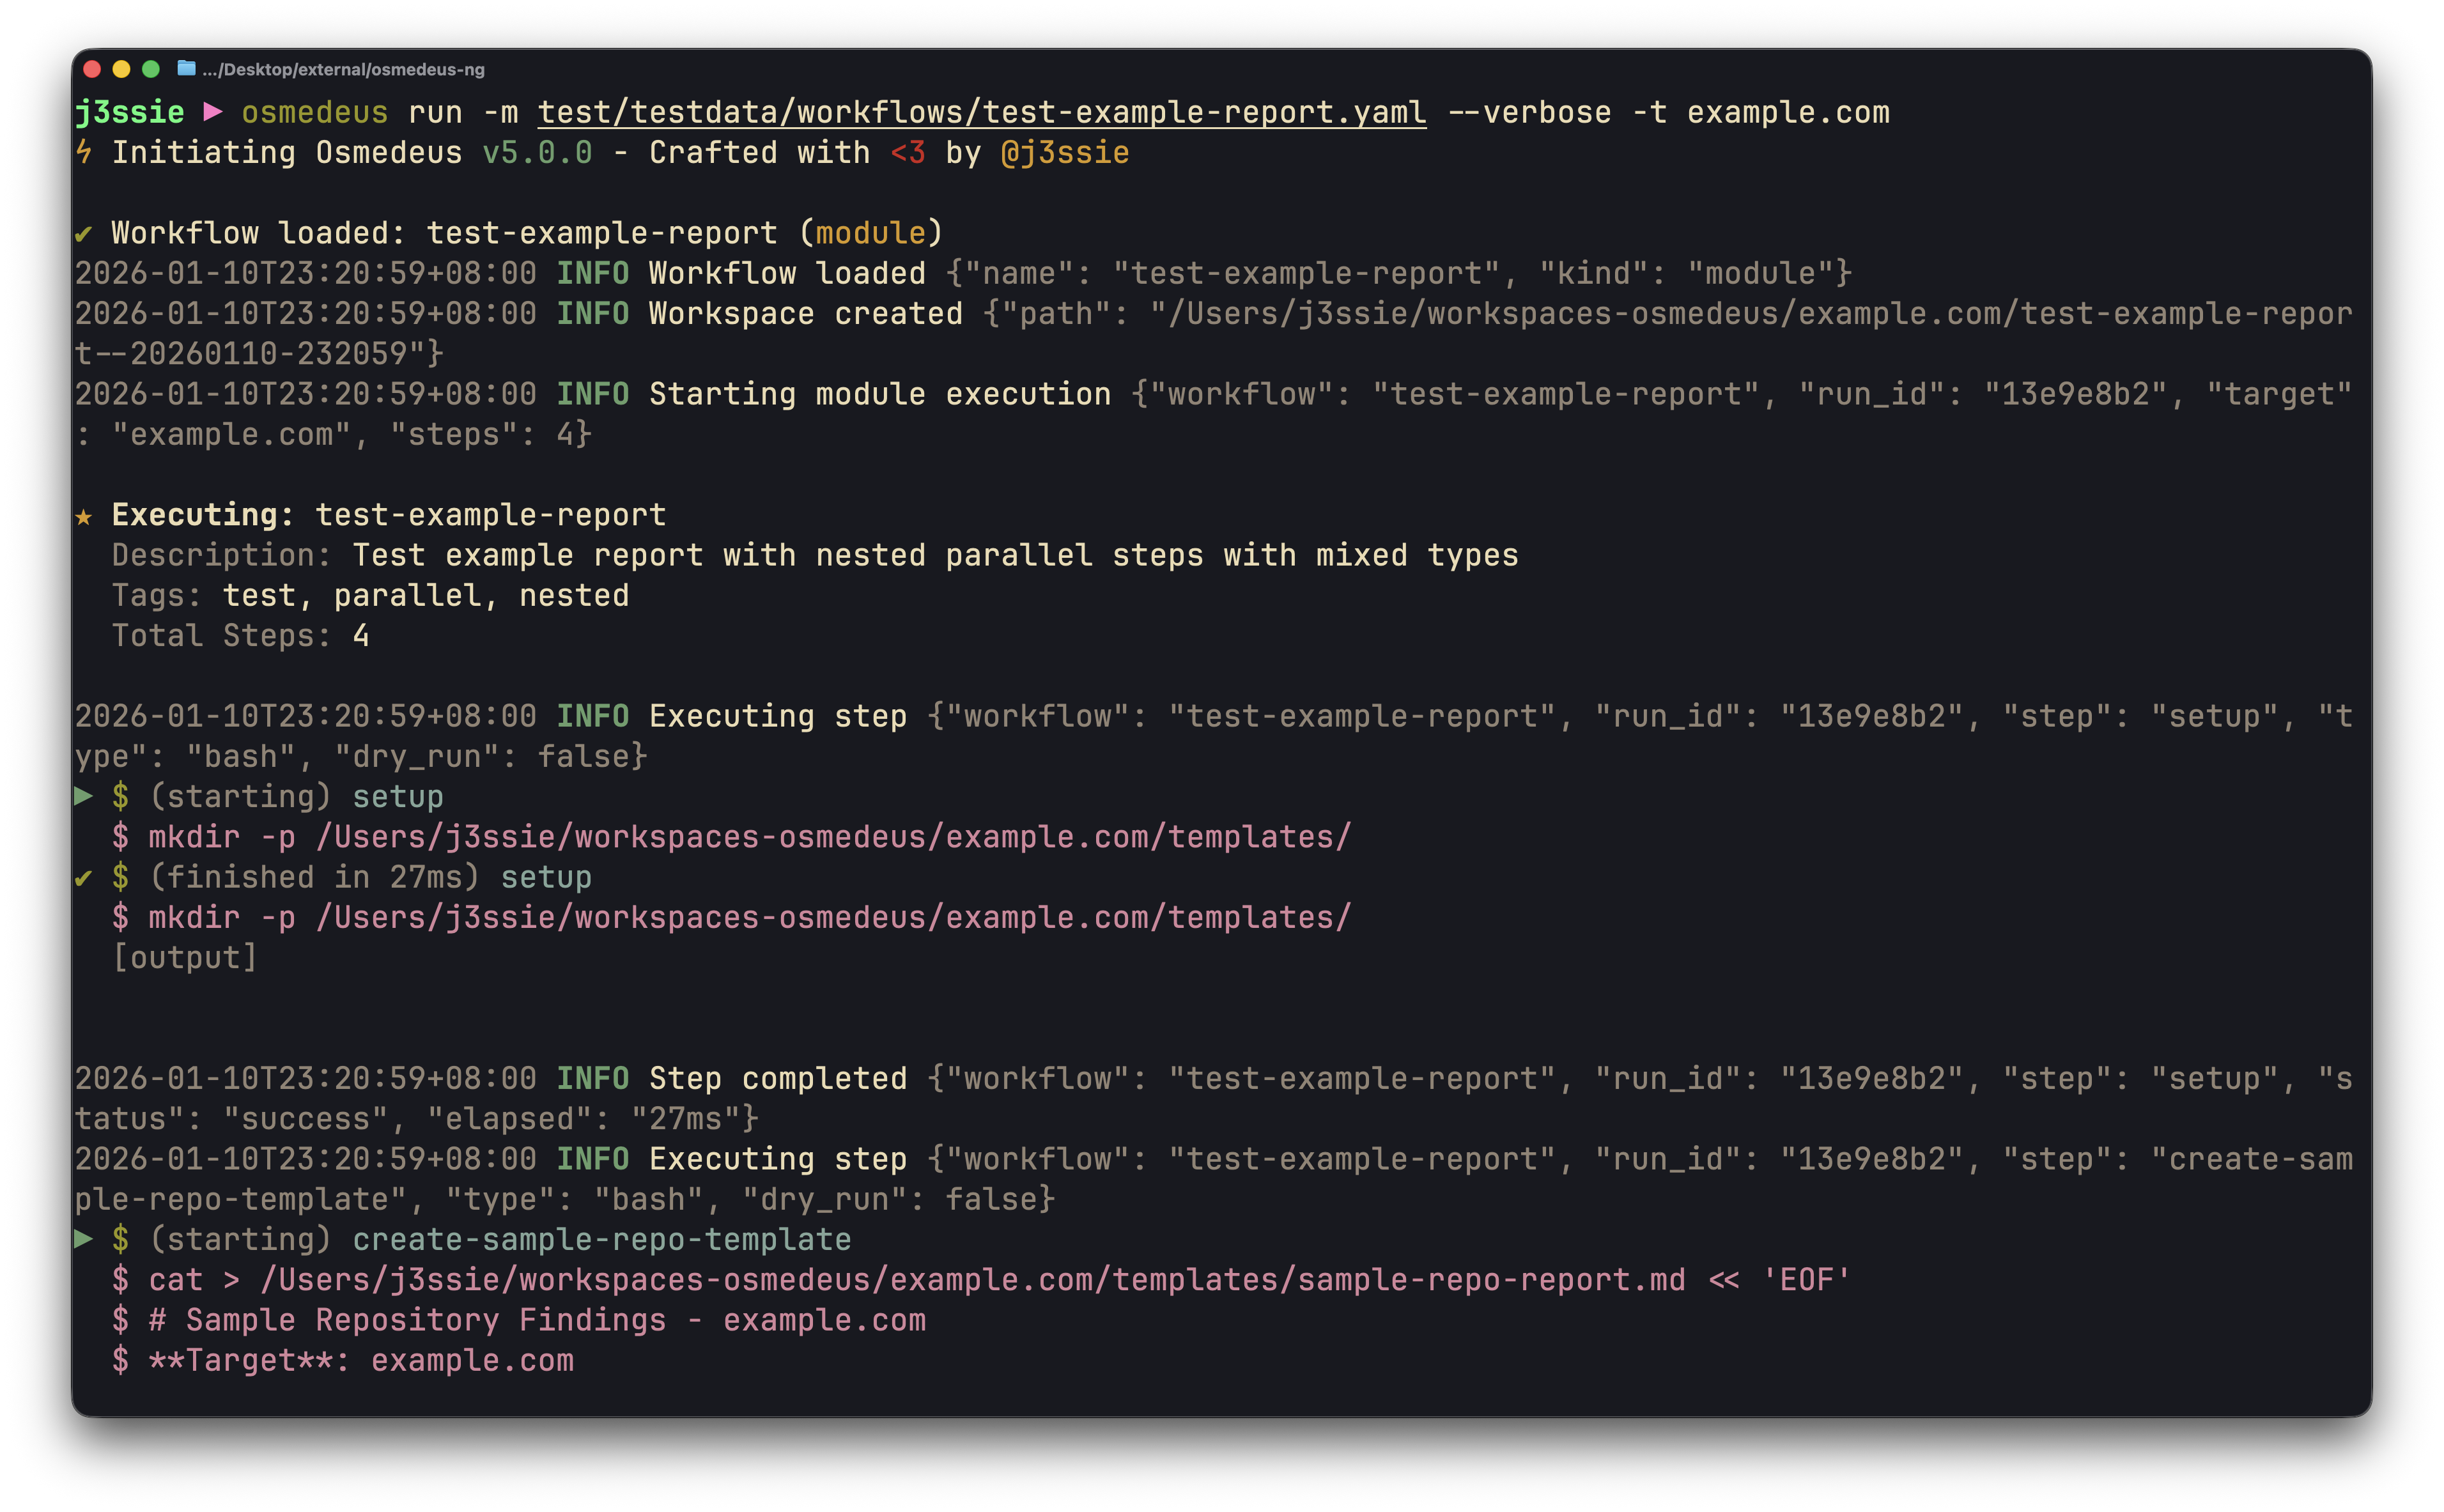 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 dev-sec/ansible-collection-hardening
This Ansible collection provides battle tested hardening for Linux, SSH, nginx, MySQL
 dev-sec/linux-baseline
InSpec-based compliance profile for auditing Linux system hardening against security baselines, ensuring consistent configuration across…
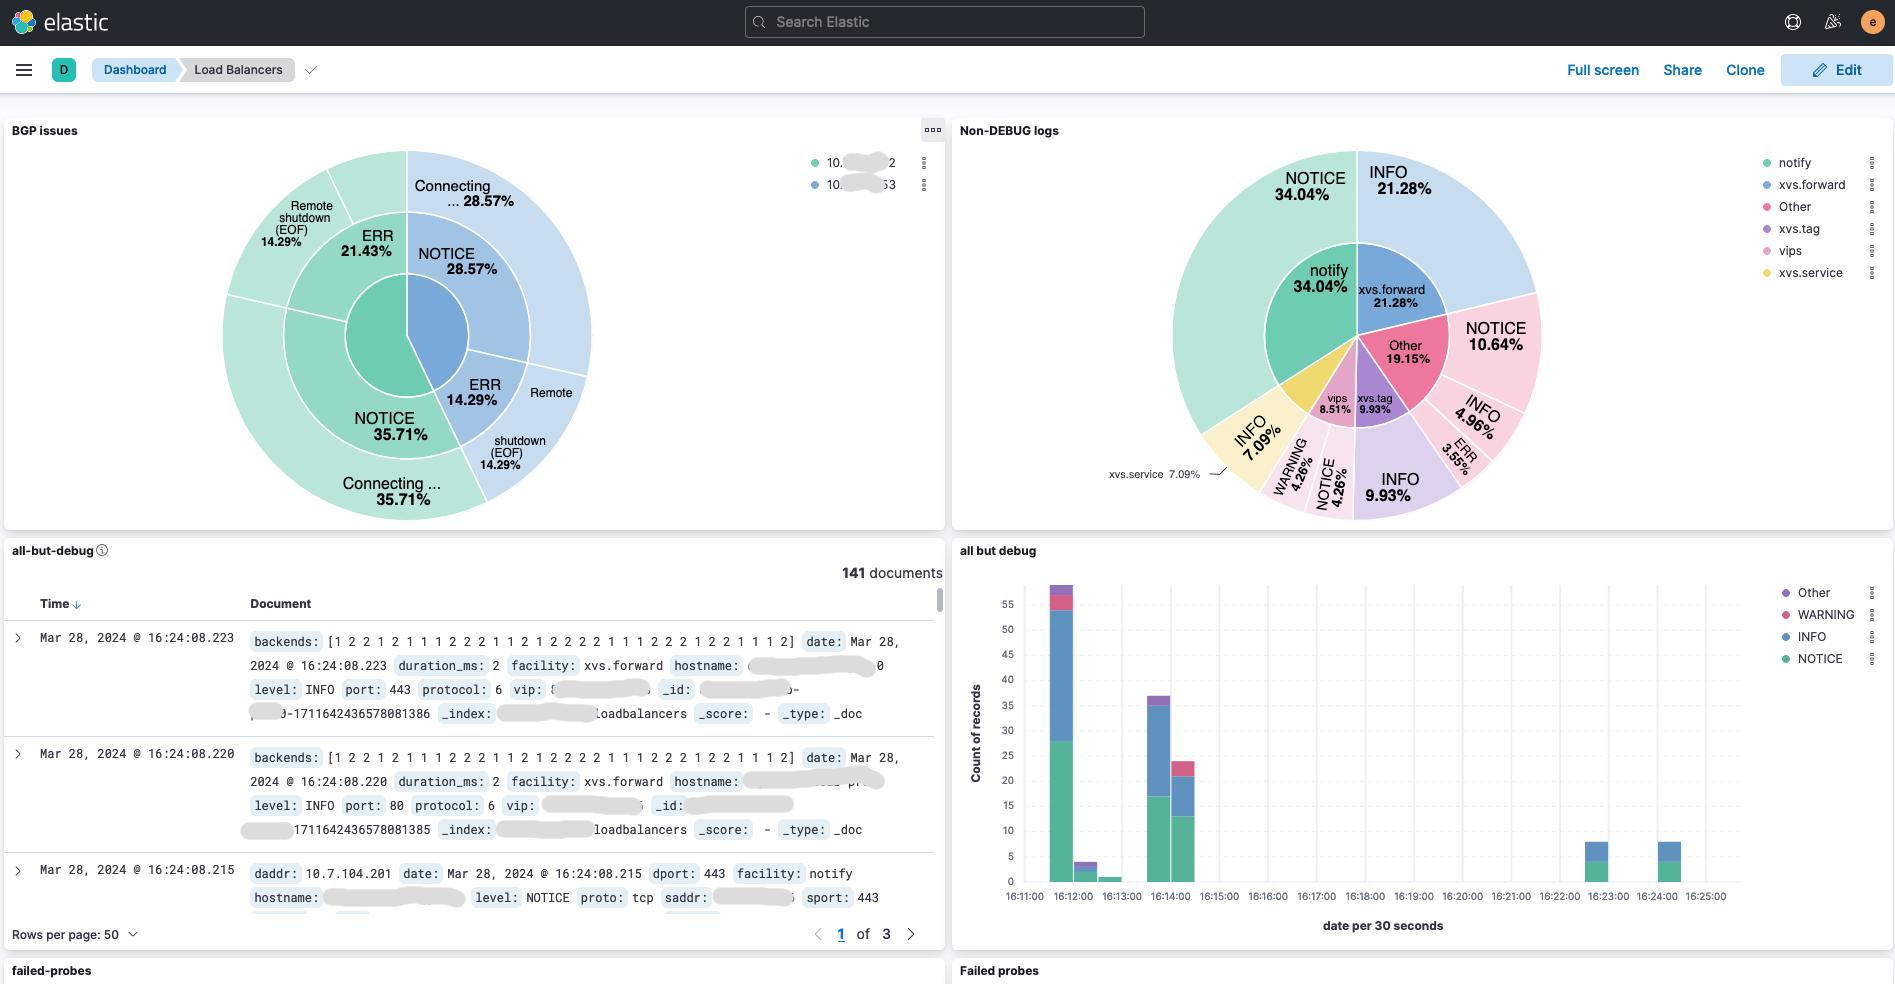 davidcoles/vc5
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
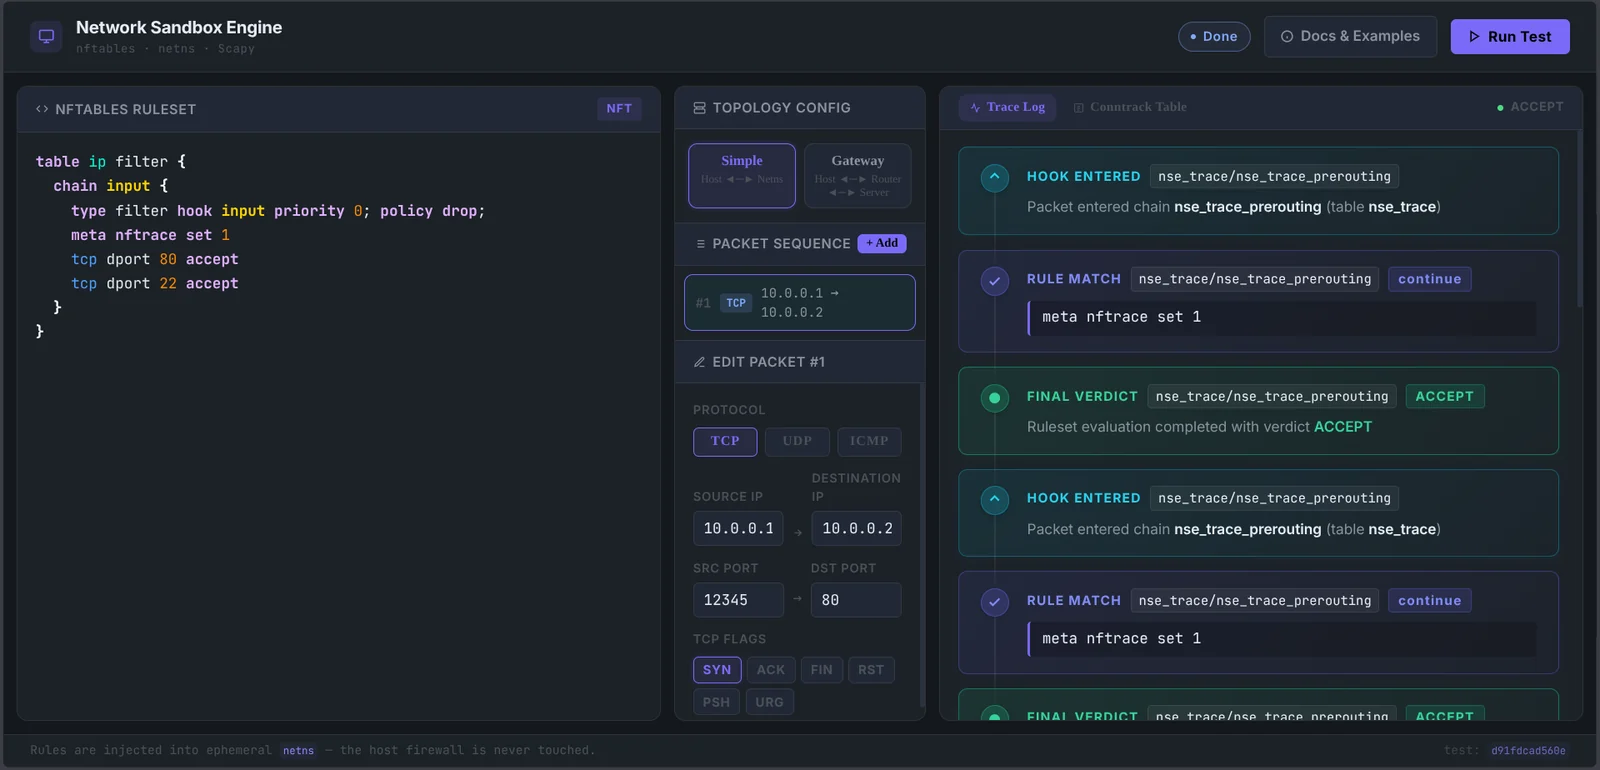 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.